

An email that says a suspicious process is changing protected system files sounds like the kind of warning nobody should ignore. The Process Attempting To Modify System Files email uses that fear to make a dangerous button feel like the safest option.
The alert is fake. It was not generated by the security software on your computer, and its “Resume” and “Escalate” controls lead away from any genuine IT system.
Overview
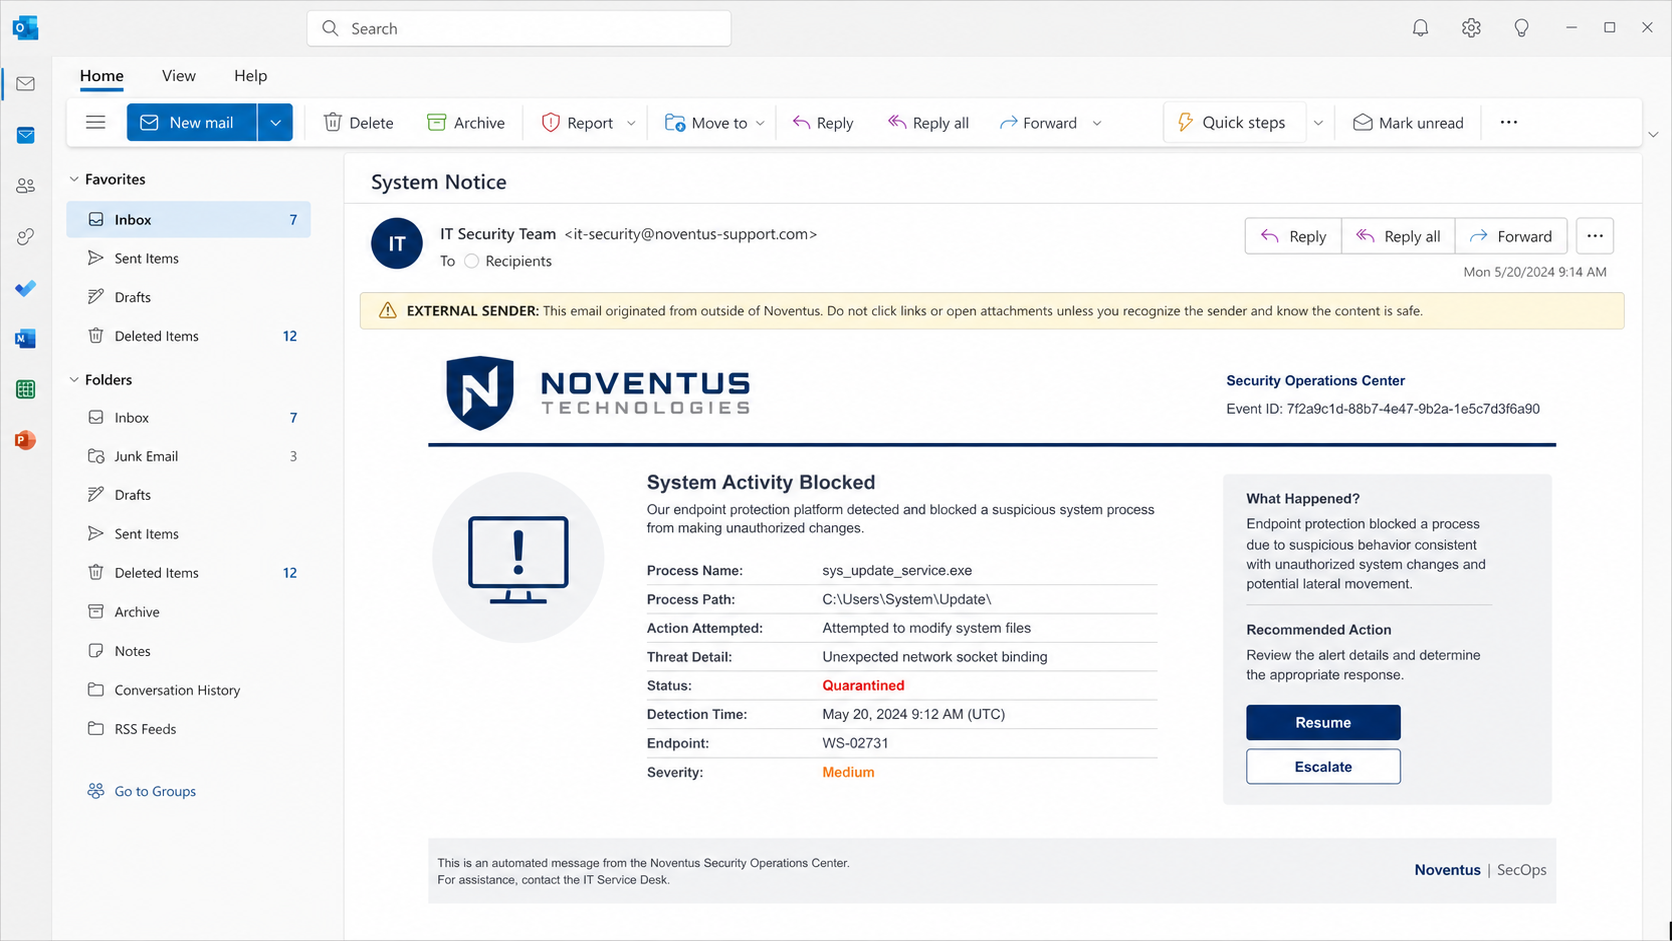
The Process Attempting To Modify System Files email scam is a credential-phishing campaign disguised as an automated endpoint security notice. It claims an unknown process was detected on the recipient’s workstation and quarantined before it could change important files.
An observed version used the subject “System Notice” and referred to a program named sys_update_service.exe. It listed the path C:UsersSystemUpdate, described the trigger as “Unexpected network socket binding,” and marked the item “Quarantined.”
The message then presents two choices, such as “Resume” and “Escalate.” Both are designed to push the recipient toward the same fraudulent destination, where a counterfeit login form may imitate Gmail, Microsoft, Yahoo, or another email provider.
The goal is to steal email credentials. The attackers are not monitoring your workstation, and clicking a button does not communicate with a real endpoint protection console or internal IT team.
Why this warning feels convincing
Security alerts normally contain technical details, and this scam copies that style. A process name, file path, trigger condition, and quarantine status create the impression that a real protection product collected evidence from the device.
The details do not have to be accurate. Most recipients cannot instantly confirm whether a background service with a plausible name exists, and the words “system files” suggest that delaying could make the problem worse.
The message also borrows the authority of an internal IT department. Employees are trained to take security warnings seriously, so a well-written fake alert can turn good security instincts into the mechanism of the attack.
What the criminals want
The primary target is the password for an email or workplace account. That account may unlock messages, shared documents, calendars, collaboration tools, cloud storage, password resets, and other services connected through single sign-on.
Attackers may use the stolen access themselves or sell it. A compromised work account can support invoice fraud, data theft, internal phishing, and attempts to reach higher-value administrators.
If the victim reuses the password, the same credential may also work on personal email, social media, shopping, or financial services. That is why one phishing submission can become several separate account compromises.
How the Process Attempting To Modify System Files Email Scam Works
Step 1: The attacker sends a fake endpoint alert
The email appears to come from an IT Team, Security Operations Center, Central Endpoint Protection Manager, or a similarly official-sounding function. The display name may look internal even when the underlying sender address is external.
Some campaigns are sent broadly. Others use company names, employee addresses, or leaked business information to make the message feel specific to the target’s workplace.
Step 2: The message invents a technical incident
The body says a process tried to modify system files, open an unexpected network socket, or perform another suspicious operation. The fake executable name is chosen to sound almost legitimate without matching a familiar Windows component.
A file path and quarantine label reinforce the story. They also give the recipient something technical to focus on while the more important questions—who sent the email and where the buttons lead—receive less attention.
Step 3: Fear and uncertainty narrow the recipient’s choices
The warning implies that the device may be infected or that an important update was blocked. A user may worry that choosing “Resume” will release malware but also fear that ignoring the alert will leave the computer damaged.
The “Escalate” button seems like the cautious choice. That is deliberate. In the scam, the apparently safe option is still controlled by the attacker.
Step 4: Both buttons route to a phishing page
The visible labels suggest two different actions, but the underlying links may be identical. Neither button communicates with the local computer’s security software.
A real endpoint product normally displays alerts through its installed application, the operating system, or an authenticated company portal. It does not need an employee’s email password to quarantine a local executable.
Step 5: The phishing page imitates the victim’s mail provider
The destination may inspect the email address in the link and display a matching brand. A Gmail address can receive a Google-themed form, while a Microsoft 365 user may see a page resembling the Microsoft sign-in screen.
This adaptive design is meant to remove the visual disconnect between the fake IT warning and the requested credentials. The page may even prefill the email address and ask only for a password.
Step 6: The form captures the password
When the victim submits the form, the credentials are transmitted to the scammer. The page may show a “session expired” message or request the password again so the operator receives a second copy.
Afterward, it can redirect to a harmless website or display a generic “incident escalated” notice. That gives the victim a reason not to investigate immediately.
Step 7: The attacker signs in and establishes persistence
Criminals often test captured credentials quickly. If they gain access, they may add forwarding rules, register a new authentication method, create app passwords, authorize a malicious application, or steal session tokens.
They may search for password-reset emails, confidential attachments, finance conversations, and lists of coworkers. An internal mailbox gives future phishing messages a trusted route around some external-email warnings.
Step 8: A fake security alert becomes a real security incident
The original message does not prove that the workstation was infected. However, the stolen account can create a genuine organizational breach, especially if it is linked to cloud apps or privileged tools.
The faster the victim tells IT, the better the chance of revoking sessions and blocking the attacker before data is accessed or coworkers receive follow-up messages.
Red Flags That Reveal the Fake System Alert
- The sender is not truly internal. The display name says IT Team, but the full address belongs to an unrelated domain or free mail service.
- The email names no real security product. Phrases such as “Central Endpoint Protection Manager” sound official but may not match anything your organization uses.
- The device is not identified. The message may omit the computer name, asset number, operating system, incident ID, or support case expected in a genuine alert.
- The process name is suspiciously generic. A name such as sys_update_service.exe tries to resemble a trusted component without offering verifiable publisher information.
- Both actions are web links. A local quarantine decision should not require opening an unsolicited external webpage.
- The destination asks for email credentials. Your password cannot tell an endpoint tool whether a process is safe.
- The message creates panic. It emphasizes protected files and network activity but does not give a normal support channel you already know.
Why Fake IT Alerts Are Especially Dangerous
Most phishing messages imitate a service the recipient might choose to ignore. A fake IT alert is different because it presents itself as part of the organization’s defense. The employee may believe that clicking is not merely permitted but required by company policy.
The two-button design strengthens that illusion. “Resume” appears risky, while “Escalate” sounds responsible. By controlling both paths, the attacker can catch cautious users who would never approve an unknown process but are willing to report it.
The scenario also creates what incident responders call context switching. A person who was reading email is suddenly asked to evaluate an endpoint threat, interpret a file path, and make an urgent security decision. Under that pressure, it is easy to overlook a mismatched sender or unusual web address.
Work accounts make the tactic more damaging. A mailbox may be connected to single sign-on, document platforms, ticketing systems, and collaboration tools. Even when multifactor authentication is enabled, an attacker can follow the stolen password with approval prompts or a fake verification page that asks for a one-time code.
Employees should therefore treat unexpected security notices as unverified reports, not as instructions. The correct response is to switch to a trusted channel: open the installed security product, use the known help-desk portal, or call an internal number already stored in company documentation.
How a Real Security Alert Should Be Checked
Do not click either button. If the device belongs to an organization, contact the help desk through the number, portal, or chat channel listed in company documentation—not through the suspicious email.
Open the security application directly from the Start menu or system tray and review its protection history. On Windows, you can also open Windows Security yourself and check Virus & threat protection without following an email link.
If you have enough access, look for the named file at the stated path, but do not run or delete unfamiliar files merely because an email told you to. Let the organization’s security team determine whether the process exists and how it should be handled.
Microsoft’s official phishing guidance recommends opening a new browser tab and visiting the organization’s site independently when a suspicious message might be legitimate.
What to Do if You Have Fallen Victim to This Scam
- Stop interacting with the page. Close it and do not submit another password, download a supposed security tool, or call a number displayed by the site.
- Contact your IT or security team immediately. Use a known internal route and explain which button you clicked, what information you entered, and whether anything downloaded. Do not wait for evidence of misuse.
- Change the affected password from a trusted device. Navigate directly to the genuine provider. Use a strong, unique replacement rather than a small variation of the old password.
- Replace reused passwords. Update every account that used the same or a similar password, starting with email, single sign-on, cloud storage, banking, and administrator accounts.
- Revoke active sessions. A password change may not end every existing session. Use the account’s security page to sign out all devices and remove unfamiliar app passwords and connected applications.
- Review authentication methods. Delete unknown phone numbers, recovery addresses, passkeys, security keys, authenticator entries, and backup codes. Then enable multifactor authentication if it was not already active.
- Inspect mailbox settings. Look for new forwarding rules, delegates, filters, automatic replies, and deleted security notices. Attackers use these settings to maintain quiet access.
- Check recent activity. Record unfamiliar sign-ins, device names, locations, and application authorizations. Give that information to the incident-response team.
- Scan the computer. If you downloaded or opened a file, update the installed security software and run a full scan. Microsoft also advises scanning a PC before changing a compromised Microsoft account password when malware may be present.
- Warn affected contacts. If messages were sent from the account, tell recipients through another channel and ask them not to open links or attachments.
- Report the phishing message. Use the mail client’s Report Phishing feature and preserve the original message for investigators. The FTC also accepts reports through ReportFraud.ftc.gov.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
How Organizations Can Reduce This Risk
Standardize security notifications. Employees should know which product names, sender domains, incident fields, and support routes a genuine alert will use. A consistent process makes invented security brands easier to reject.
Add a visible external-sender label and protect company domains with SPF, DKIM, and DMARC. These controls are not perfect, but they reduce simple spoofing and give mail systems better evidence for filtering.
Use phishing-resistant multifactor authentication for important accounts, restrict legacy protocols, and alert on suspicious inbox rules or authentication changes. Limit administrative rights so one stolen mailbox cannot automatically reach sensitive systems.
Training should include “safe-looking” buttons such as Escalate, Report, or Secure Account. Attackers know that cautious users choose those words, so employees must verify the destination rather than trusting the action label.
Frequently Asked Questions
Does this email mean my computer has malware?
No. The email itself does not prove that the named process exists. It is a fabricated alert used to steal credentials. Check the device through its installed security tools or your company help desk.
Is it safe to click “Escalate” instead of “Resume”?
No. In the observed scam, both buttons serve the attacker. Button labels describe what the scammer wants you to believe, not what the underlying link actually does.
I clicked but entered nothing. What should I do?
Close the page, report the email, and tell IT if it involved a work device. Check downloads and run a scan if the page attempted to save a file. Do not revisit the site to investigate it yourself.
Why would a phishing page ask for my email password?
Email is a recovery channel and a source of business context. Access can help criminals reset other accounts, steal documents, impersonate you, and send more convincing phishing messages.
The Bottom Line
The Process Attempting To Modify System Files email is not a real endpoint warning. Its technical language and reassuring “Escalate” option lead to the same credential trap. Verify alerts inside the security application or through your known help desk, never through an unexpected email button.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.