

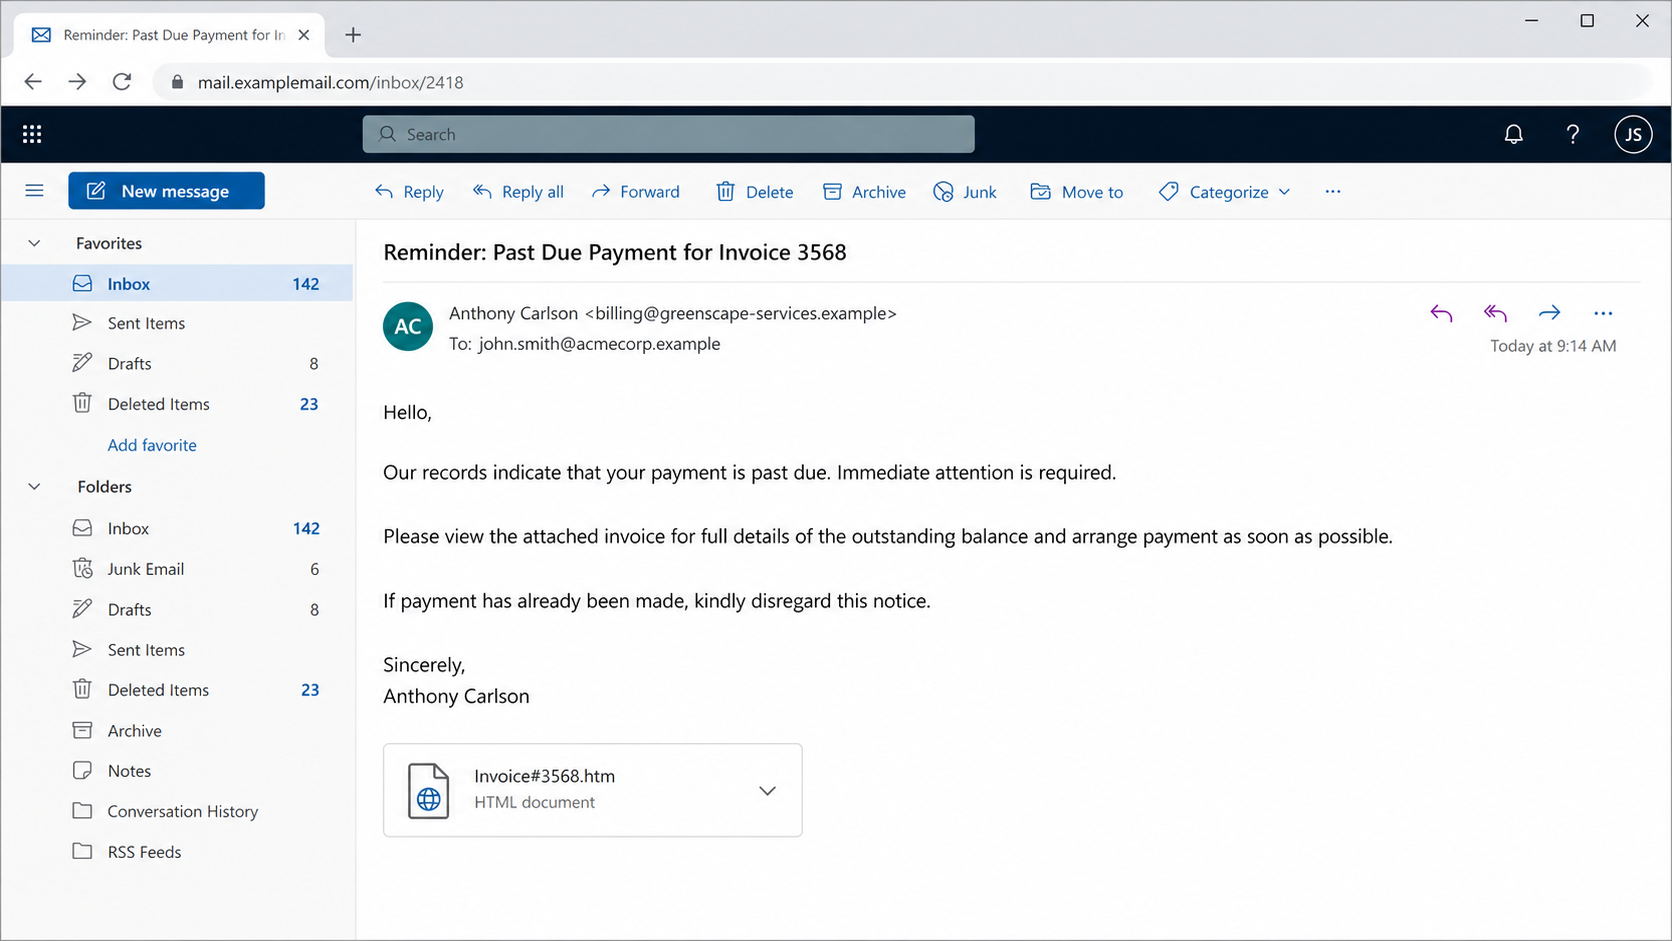
An unexpected billing reminder says Invoice 3568 is past due and requires immediate attention. There is no balance in the message, no recognizable vendor, and no useful account detail, only an attached file that promises the full invoice.
The attachment looks like a simple HTML document. When opened, it displays an invoice and places a Microsoft-style password prompt over the page, making the request feel like a protected business file.
The Invoice Payment Is Past Due email scam is not collecting an overdue balance. It is using an invoice story and a local HTML attachment to steal Microsoft or email account credentials.
Overview
The message creates urgency without identifying a real debt
The email uses the subject “Reminder: Past Due Payment for Invoice 3568.” Its short body states that payment is overdue and tells the recipient to review the attached invoice before arranging payment.
No company relationship, purchase order, service date, contract, amount, customer number, or previous reminder is provided. The sender signs the message as “Anthony Carlson,” but a name alone does not establish who issued the invoice.
The absence of details is intentional. The attachment must be opened to answer the questions the email creates, and curiosity becomes the route into the phishing page.
The attached HTML file is the phishing page
The observed attachment is named Invoice#3568.htm. An HTML file can contain the same code used to build a webpage, including text, images, forms, and scripts.
When the file opens in a browser, it can display a convincing invoice locally. A Microsoft-branded overlay then claims the connection is verified and encrypted and asks for a password to view the document.
A local file can still send entered data across the internet. The address bar may begin with file://, but scripts inside the attachment can transmit the password to a remote server controlled by criminals.
The target is a valuable business login
Invoice lures are often sent to accounting, purchasing, sales, and administrative addresses because those employees routinely handle documents from outside organizations. Opening an invoice is part of their normal work.
A stolen Microsoft or webmail login can expose:
- Email conversations with customers and suppliers
- Files stored in OneDrive, SharePoint, or other connected services
- Contact lists and internal company directories
- Real invoices, purchase orders, and bank details
- Single sign-on access to additional workplace applications
- Information criminals can use for business email compromise
Microsoft is not involved in this campaign. Its visual identity is copied to make a password request inside an unrelated attachment appear routine.
Why an HTML Invoice Attachment Deserves Extra Caution
HTML files can behave like small websites
People often associate dangerous attachments with executable programs or macro-enabled Office files. An HTML attachment may look less threatening because a browser opens it, but it can still contain interactive forms and remote connections.
The file does not need to install malware to cause harm. If it persuades a recipient to enter a password and sends that password away, the attack has already succeeded.
The invoice background is visual misdirection
The attacker can render itemized services, totals, logos, and payment rows behind the login box. The visible document reassures the viewer that a real invoice exists, even though it may be nothing more than decorative code.
Because the login overlay blocks the document, the recipient cannot inspect whether the supposed vendor or charges make sense until after submitting credentials. That order is the reverse of a safe verification process.
“Encrypted connection” does not authenticate the sender
Security language is easy to place inside an image or HTML panel. A statement saying a document is verified, trusted, protected, or encrypted is only text unless it comes from a known service whose domain and session can be independently confirmed.
Even HTTPS on a remote site would protect the connection to that particular site. It would not prove that the operator is Microsoft, the alleged vendor, or anyone authorized to collect a workplace password.
How the Invoice Payment Is Past Due Email Scam Works
Step 1: Attackers send a generic overdue-invoice reminder
The campaign reaches business and personal addresses with a brief payment warning. It avoids naming a recognizable company or balance, allowing the same template to be sent to recipients in many industries.
Some people will assume it relates to a forgotten order, a supplier, a subscription, or another department’s purchase. That uncertainty is exactly what the message exploits.
Step 2: The numbered invoice gives the story a record-like quality
“Invoice 3568” sounds as though it belongs to an accounting system. A number makes the message easier to treat as a misplaced business record rather than unsolicited mail.
The instruction to disregard the notice if payment was already made also imitates normal collection language. It softens the tone while preserving the pressure to inspect the attachment.
Step 3: The recipient opens Invoice#3568.htm
The attachment launches in the default browser. Unlike a link, the file initially loads from the device, which may prevent the recipient from seeing an obviously suspicious web domain in the address bar.
Security tools may still block or flag the attachment, but the file format itself is not proof of safety. Legitimate HTML files exist, and attackers abuse that familiarity.
Step 4: A fabricated invoice appears behind a password prompt
The file renders a professional-looking payment document and immediately covers it with a sign-in box. The overlay may use Microsoft colors, a familiar logo, and claims about an encrypted connection.
The recipient is told to enter a password and choose “View Document.” The design suggests that authentication is the normal final step before opening a shared corporate file.
Step 5: The form sends the password to attacker infrastructure
The credential field is connected to code chosen by the scammer. When the form is submitted, the entered information can be posted to a remote collection endpoint or sent through another hidden request.
No legitimate Microsoft login session is created. The invoice remains inaccessible, or the page may show a generic error and request another attempt.
Step 6: Criminals attempt to access the real account
The stolen username and password may be tested against Microsoft 365, webmail, or other likely services. Automated tools can act within minutes, so victims should not wait for visible misuse before changing credentials.
If multi-factor authentication is active, attackers may generate repeated approval prompts or impersonate support staff to request the code. Approving a prompt can complete the takeover.
Step 7: A compromised mailbox reveals authentic financial context
Inside a business account, criminals can search for supplier names, expected payments, invoice formats, executive travel, and active projects. That information supports highly convincing follow-up messages.
They may create forwarding rules or delete security alerts to remain unnoticed. The next fraudulent invoice can then arrive from the victim’s real account inside an existing conversation.
Step 8: The attack develops into payment or identity fraud
A hijacked mailbox may be used to replace bank details, request a wire transfer, send more phishing attachments, or reset passwords on connected services. The initial fake invoice is often valuable because of the access it opens, not the payment it mentions.
The FBI identifies business email compromise as a financially damaging crime and advises independent verification of payment changes. A known telephone number or in-person check is safer than any contact information supplied in a questionable email.
How to Verify an Unexpected Invoice Safely
Check the business relationship before the attachment
Search internal purchasing records, known supplier accounts, and earlier correspondence. A real invoice should connect to an order, agreement, delivery, or person who can confirm it.
Contact the vendor through an established channel
Use a number from a signed contract, an existing vendor profile, or the company’s independently located website. Do not use the phone number or reply address in the suspicious message.
Inspect the complete sender address and attachment type
A familiar display name can hide an unrelated domain. Treat unexpected HTML, HTM, ZIP, ISO, and script attachments as high risk, especially when they request a workplace login.
Use the real document portal directly
If a vendor normally shares invoices through Microsoft 365 or another platform, open that platform from a bookmark or known app. A legitimate shared document should appear in the authenticated account without relying on the attachment.
What a Compromised Microsoft Account May Expose
The inbox can reveal the next believable target
Criminals can search for words such as invoice, payment, bank, payroll, contract, and purchase order. Real conversations show who has authority, which suppliers are active, and when a payment request will attract less suspicion.
Cloud files can supply documents and identities
A workplace account may open OneDrive, SharePoint, Teams, or other connected resources. Contact lists, signature blocks, templates, and stored documents help an intruder reproduce the organization’s normal language and formatting.
Single sign-on can widen the incident
Organizations often use one identity to access several business applications. The exact reach depends on permissions, security policy, and multi-factor protection, but a stolen sign-in should be treated as more than an email problem.
Administrators should review authentication logs and connected applications rather than assuming that changing the mailbox password closes every session. Session tokens and granted permissions may require separate revocation.
Warning Signs in the Past-Due Invoice Message
- The recipient was not expecting Invoice 3568.
- No vendor, balance, purchase order, service, or due date is stated.
- The message relies on an HTML attachment for every meaningful detail.
- The attachment asks for a Microsoft password to reveal an unknown invoice.
- Security claims appear inside the document instead of a verified browser session.
- The sender’s identity cannot be connected to an existing business relationship.
- Immediate payment pressure discourages normal accounting checks.
One sign may have an innocent explanation, but this combination is highly suspicious. A real supplier benefits from giving enough information for a customer to verify the charge before opening an unusual file.
What to Do if You Have Fallen Victim to This Scam
- Disconnect from the phishing workflow. Close the browser tab and do not reopen the HTML file. Do not reply to the sender or follow any new instructions that appear after the submission.
- Change the affected password immediately. Navigate to Microsoft, your webmail provider, or the workplace portal independently. Use a clean device if the attachment also downloaded or launched other content.
- Alert your organization’s IT or security team. Provide the original email and attachment without forwarding it casually to coworkers. Administrators may need to revoke sessions, reset tokens, search for similar messages, and block campaign indicators.
- Review account activity and mailbox rules. Remove unknown devices, applications, forwarding addresses, delegates, filters, and recovery methods. Check sent, deleted, and archived mail for activity you did not perform.
- Protect any reused credentials. Change the same or similar password everywhere it appears. Enable multi-factor authentication and reject any unsolicited approval prompt or request for a code.
- Verify financial instructions already sent or received. Call suppliers and colleagues through known numbers. If money was transferred, contact the financial institution immediately and ask whether the transaction can be recalled or frozen, then report the incident to the FBI’s IC3.
- Scan the device. A credential form alone may not install software, but an HTML attachment can connect to remote content or trigger other downloads. Malwarebytes can check the system for malicious files, stealers, and unwanted changes.
- Block repeat malicious destinations. AdGuard can stop many known phishing pages, malicious advertising requests, and tracking connections. Continue checking unexpected files manually because no filter catches every new campaign.
- Preserve evidence. Save the email headers, attachment name, screenshots, login alerts, and transaction records. Avoid paid “recovery agents” who guarantee that they can retrieve funds or accounts for an advance fee.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is Invoice 3568 a real unpaid invoice?
The campaign provides no verifiable vendor, amount, or purchase details. Its HTML attachment presents a fake login form, so the payment reminder should be treated as phishing.
Can an HTML attachment steal a password?
Yes. HTML files can contain forms and scripts that transmit entered information to a remote server, even when the file initially opens from the local device.
Does opening the attachment automatically infect the computer?
Not necessarily. The observed goal is credential theft, but HTML can load remote content or lead to downloads. Close it, remove the file, and scan the device if anything else ran.
Why does the attachment display a Microsoft login?
Microsoft accounts are common in business environments and can unlock email, files, and other services. The copied branding is meant to make the credential request look normal.
What if I entered a password but multi-factor authentication is enabled?
Change the password anyway, revoke sessions, and review the account. Do not approve unexpected prompts, because attackers may use the stolen password to trigger them.
Should an accounts-payable employee delete the email immediately?
Report it according to company procedure first so security staff can examine headers and block related messages. Then remove it as directed without opening the attachment again.
The Bottom Line
The Invoice Payment Is Past Due email scam uses a vague billing reminder to make an HTML attachment feel necessary. The invoice displayed inside is camouflage for a password-collection form.
Verify debts through purchasing records and known vendor contacts, never through an unexpected attachment. If credentials were entered, secure the account and alert the organization quickly, because a stolen business inbox can turn one fake invoice into a much larger payment-fraud operation.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.