

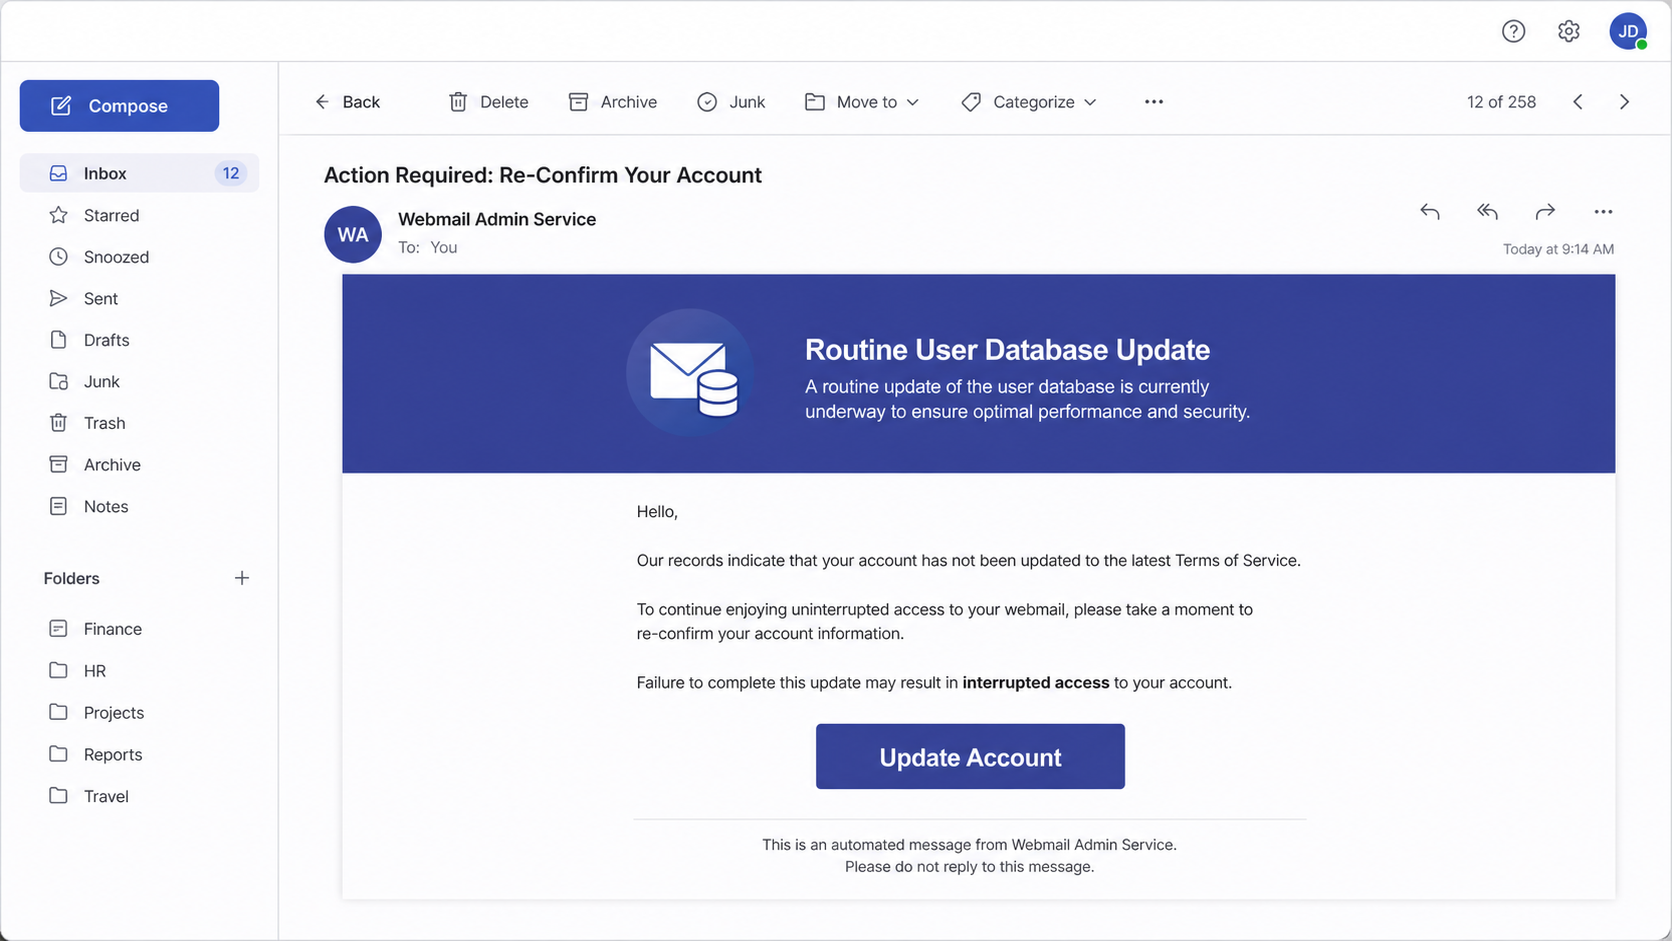
A stark warning arrives with the subject “Action Required: Re-Confirm.” It says your mail account is not updated for new Terms of Service for a user database update and will be suspended within a short deadline unless you verify the address.
The message looks like an automated notice, and the deadline is oddly specific. A single blue button appears to offer the fastest way to preserve access.
The Routine Update of User Database email scam has nothing to update. It directs recipients to a fake webmail login page where every submitted email address and password can be captured by criminals.
Overview
The warning says email account requires re-confirmation
The campaign tells recipients that their mail account is not updated for new Terms of Service for a user database update. It asks them to confirm an account update if they want to keep using the address.
A threat of suspension within a short deadline supplies the urgency. The wording suggests that the countdown has already started, even though the email does not explain which software is outdated or when any earlier warning was sent.
The “Update Account” button is framed as an account-maintenance control. In reality, it leaves the provider’s normal environment and sends the visitor toward a fraudulent login page.
The fake login imitates cPanel Webmail
The page used in the observed campaign copied the appearance of a cPanel Webmail sign-in screen. It asked for an email address and password, the same credentials many people use to enter a hosted business mailbox.
The phishing page was placed on cloud-hosting infrastructure rather than a legitimate mail portal. Criminals sometimes abuse reputable hosting services because a familiar cloud domain can look less suspicious than a newly registered standalone website.
Hosting location does not prove ownership. A page stored on a legitimate cloud platform can still be created by an unauthorized customer and used for fraud.
The attack can reach far beyond the mailbox
An email password is valuable because the inbox acts as a hub for identity, communication, and account recovery. Once attackers gain access, they can search old messages and reset passwords on other services.
Possible consequences include:
- Private messages and attachments being read or copied
- Password-reset links being intercepted
- Contacts receiving scams from the real compromised address
- Business invoices and payment conversations being manipulated
- Cloud accounts being entered through shared credentials or single sign-on
- Recovery settings being changed to lock out the legitimate owner
No legitimate email provider needs customers to visit an unrelated page to complete a vague “user database update.” Providers maintain their own infrastructure without collecting passwords through unsolicited messages.
Why the Routine Database Update Story Falls Apart
Email accounts do not expire because a server update was missed
A provider may retire an old application, require a password change after a breach, or introduce new terms. Those events are different from claiming that an individual mailbox is not updated for new Terms of Service for an unspecified user database update.
Server software is managed by the provider or hosting administrator. A user cannot update that server by typing a password into a page delivered through email.
The warning omits the information needed to verify it
The message does not identify the hosting company, domain administrator, mail plan, ticket, server, software version, or policy. It offers no route to a known dashboard and no support information that can be checked independently.
Generic wording allows the same email to target Gmail users, hosted-domain users, and people with workplace accounts. Each recipient is expected to imagine that the warning refers to their own provider.
The precise countdown is psychological, not technical
“Within a short deadline” sounds machine-generated and therefore authoritative. Yet the message provides no start time, time zone, scheduled maintenance window, or explanation for that number.
The countdown exists to shorten the decision. A person worried about losing work messages may click before contacting IT or opening the normal webmail portal.
How the Routine Update of User Database Email Scam Works
Step 1: The attackers collect or purchase active email addresses
Addresses can come from data breaches, public websites, business directories, scraped contact pages, newsletter lists, and earlier phishing attempts. Business-domain mailboxes are especially attractive because they may expose workplace conversations.
The campaign does not need advance knowledge of the recipient’s provider. A generic system message and adaptable login page can cover many services.
Step 2: The subject demands account re-confirmation
The words “Action Required” and “Re-Confirm” imply that an earlier update was missed. That can make a recipient feel late and responsible, even when no previous message existed.
The subject is designed for crowded inboxes. It communicates loss and urgency before the email is opened, encouraging a quick reaction on desktop or mobile.
Step 3: The body introduces the short suspension threat
Inside, the story changes slightly. The account supposedly needs an immediate database update to accept new Terms of Service and preserve uninterrupted access.
This moving status gives the victim a narrow rescue window. The “Update Account” button looks like the final administrative task required to avoid disruption.
Step 4: The button leads outside the real provider
The destination is not the login address the recipient normally uses. In the documented campaign, the phishing page was hosted using a cloud-storage service and imitated webmail.
A recognizable hosting brand in the URL can distract from the crucial question: who controls this particular page? Only the provider’s exact official domain or a known organization portal should receive credentials.
Step 5: A copied webmail form asks for the credentials
The page may display cPanel Webmail styling, a domain name, an email icon, or the recipient’s address. These elements can be copied, passed through the URL, or generated from public information.
The form does not check whether an update is needed. Its purpose is to collect the username and password in a familiar visual setting.
Step 6: The submission reaches the phishing operator
After the victim selects “Log in,” the data can be sent to a collection script, bot, or attacker-controlled mailbox. The page may redirect to the real provider afterward so that the failure appears temporary.
Some phishing kits ask twice, allowing the criminal to capture corrections or alternate passwords. Repeated errors on a questionable page are a reason to stop, not to keep trying.
Step 7: The attacker attempts an account takeover
Criminals use the credentials against the real mail server. They may act manually or rely on automated tools that test sign-ins and collect successful sessions.
If the password also protects other accounts, credential-stuffing attempts can spread. An unexpected multi-factor prompt may follow, and approving it can give the attacker the missing second factor.
Step 8: Mailbox access is converted into new opportunities
Attackers can study relationships, reset accounts, steal documents, and impersonate the owner. Hidden forwarding rules may copy future mail while filters move genuine security alerts away from the inbox.
For a company, the compromise can become business email fraud. For an individual, it can lead to shopping, social-media, cloud-storage, or financial account takeovers.
How Real Account Maintenance Normally Works
Alerts appear inside the authenticated account
Providers usually display storage, security, and billing notices after the customer signs in through the known app or website. The account dashboard offers context that an anonymous email cannot.
Administrators can identify the affected system
A workplace or hosting notice should name the domain, service, planned change, and support route. Employees can confirm it with IT, while hosting customers can use the provider’s normal control panel.
Updates do not require disclosing the current password
A password-change screen may ask the customer to authenticate on the official domain, but routine server maintenance does not need a password sent through a button in an unsolicited warning.
Account recovery begins from a known address
If access truly fails, type the provider’s address, use a saved bookmark, or contact the organization responsible for the mailbox. Do not search for support numbers in sponsored ads or use details from the suspicious email.
Why a Familiar Cloud Address Is Not Enough
Cloud platforms rent space to many unrelated customers
A legitimate cloud company provides storage, databases, and website hosting to millions of developers and organizations. The provider’s name in part of a URL identifies the infrastructure, not the person who created a particular page.
Attackers abuse these services for the same reason ordinary businesses use them: pages are easy to deploy, certificates are available, and the network is reliable.
HTTPS protects transport, not the truth of the claim
The padlock means the browser encrypted traffic to the displayed domain. It does not confirm that the page belongs to your email provider or that the request for a password is legitimate.
Read the domain from right to left and identify the registered service. If it is not the portal supplied by the host or employer, do not authenticate there.
Provider reports help remove abusive pages
Cloud services usually prohibit phishing and offer abuse-reporting channels. Reporting the message to your security team and the hosting provider can help disable the page, but victims should secure their accounts first rather than waiting for takedown.
Warning Signs in the Fake System Update Email
- The message claims a routine internal update requires the user to disclose a current password.
- A short deadline appears without a start time or maintenance schedule.
- No email provider, hosting company, domain, plan, or ticket is named.
- The only solution is a prominent verification button.
- The destination is a cloud-hosted or unrelated page, not the normal mail portal.
- A cPanel-style form appears even if the recipient does not normally use cPanel.
- The page requests the current password before showing any account information.
Do not judge the message solely by grammar or design. Some phishing emails look polished, while genuine automated messages can be plain. The sender, destination, account context, and independent verification matter more.
What to Do if You Have Fallen Victim to This Scam
- Stop using the linked page. Close it without entering anything else. Do not respond to the sender or call a number that arrives in a follow-up message.
- Change the email password through the real service. Use the official app, manually enter the known portal address, or ask your organization’s administrator for the correct route. Make the new password unique.
- End active sessions and revoke access. Sign out other devices, remove unknown connected applications, revoke app passwords, and check whether recovery addresses or telephone numbers were changed.
- Inspect the mailbox configuration. Look for unfamiliar forwarding, delegation, inbox rules, filters, automatic replies, blocked senders, and POP or IMAP access. Remove anything you did not authorize.
- Secure connected accounts. Change reused passwords and review recent activity on financial, cloud, shopping, social-media, and workplace services. Enable multi-factor authentication wherever possible.
- Inform IT or the hosting provider. A work mailbox compromise can affect colleagues and customers. Security staff may need the original headers, URL, timing, and login alerts to contain the incident.
- Check the device for additional threats. If the page downloaded a file, asked for an extension, or opened another installer, run a full Malwarebytes scan. Remove anything detected and update the operating system and browser.
- Add protection against repeat pages. AdGuard can block many known phishing domains, deceptive ads, and malicious requests. It reduces exposure but cannot determine that every brand-new login form is fraudulent.
- Monitor for secondary abuse. Check sent mail, deleted items, security events, and password-reset notifications. Warn contacts if unauthorized messages were sent, and reject paid recovery offers that demand money upfront.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is my mail account really not updated for new Terms of Service for a user database update?
No legitimate account condition is established by this message. Verify the account through the provider’s official portal or your organization’s administrator.
Will email access be suspended after a short deadline?
The countdown is part of the phishing pressure. The email supplies no authenticated account notice, provider identity, or technical reason supporting the suspension claim.
Is a page hosted on a well-known cloud service safe?
Not automatically. Reputable platforms host content for many customers, and criminals can abuse an account or storage feature to publish a phishing page.
What if the login screen looked exactly like cPanel Webmail?
A visual copy is easy to make. Check the complete address and use the webmail URL supplied by your actual host or administrator instead of the email button.
Does entering only my email address create a serious risk?
It confirms an active account and can support targeted follow-up attempts. The greatest immediate risk comes from submitting the password or approving a later sign-in prompt.
Can changing the password fully remove an attacker?
It is essential but may not be sufficient. Revoke sessions and applications, inspect forwarding and recovery settings, and review recent activity for persistent access.
The Bottom Line
The Routine Update of User Database email scam turns an imaginary short deadline into a credential request. Its cloud-hosted webmail page is a copy, not an account-maintenance tool.
Open the real provider independently whenever a message predicts suspension or expiration. If the password reached the fake form, act quickly and review the entire mailbox configuration, because the attacker may try to keep access even after a password change.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.