

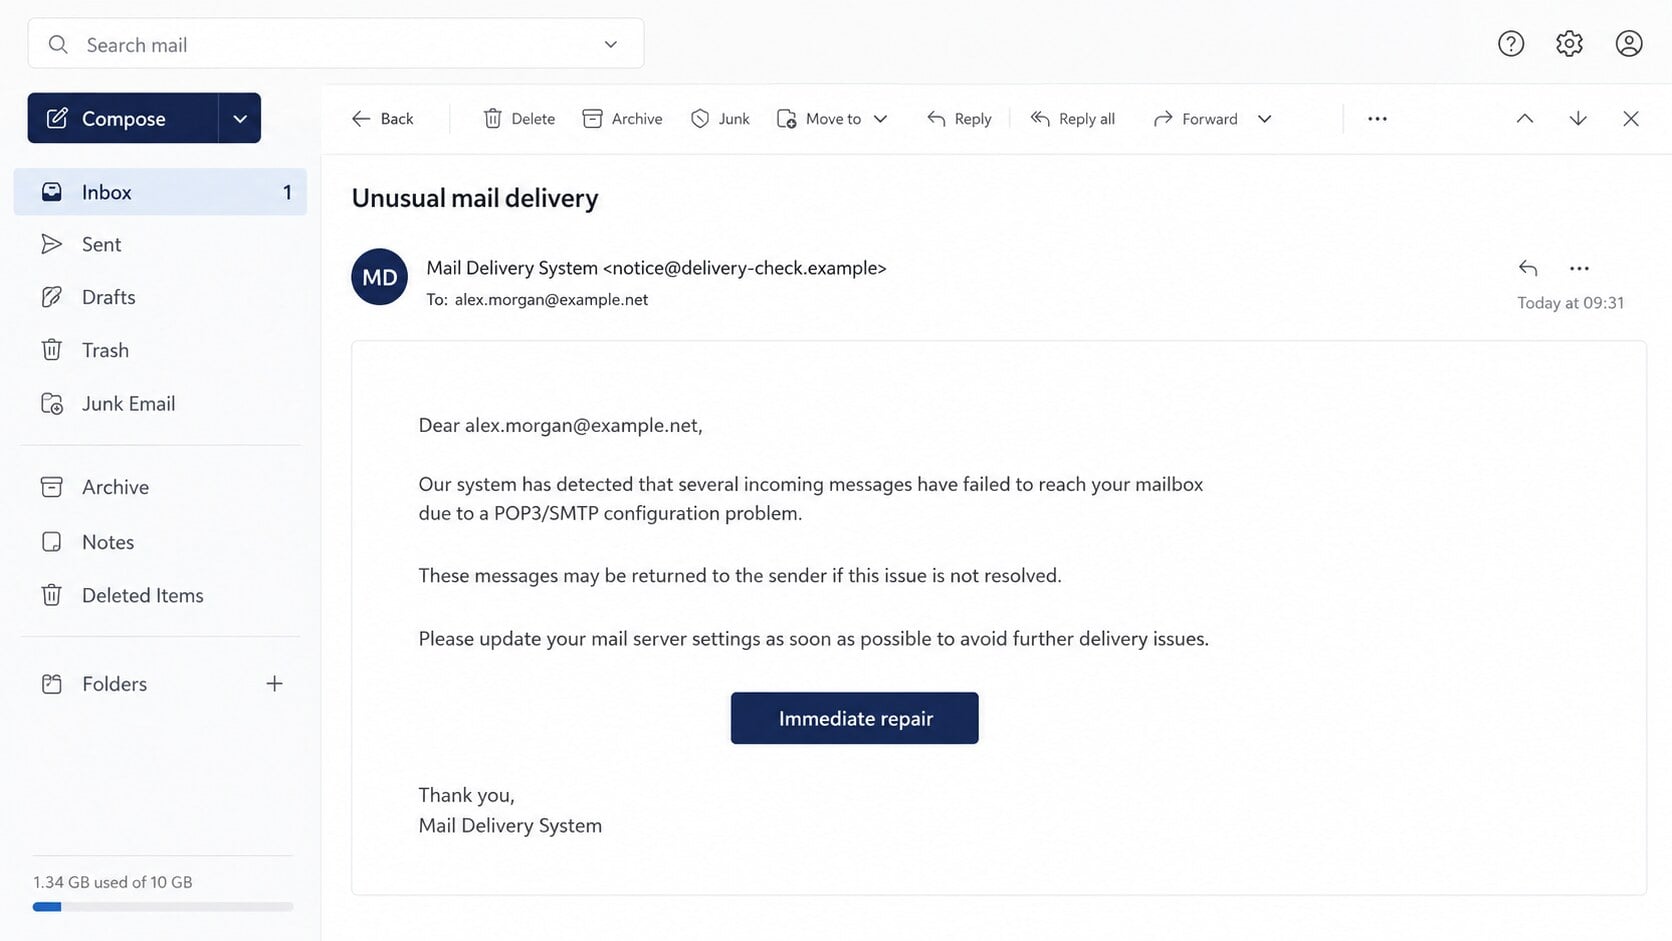
The message appears at an awkward moment: “Unusual mail delivery,” followed by a warning that several incoming emails never reached your inbox.
For anyone waiting on an invoice, appointment, or customer reply, the promised “Immediate repair” can feel difficult to ignore.
Overview
A technical-sounding problem that the recipient cannot see
The Unusual Mail Delivery email pretends to come from a POP3 or SMTP system responsible for moving messages into the recipient’s mailbox.
It claims a configuration problem stopped several emails and warns that the missing messages may be lost or returned unless the account is repaired quickly.
No affected sender, bounce code, server name, ticket number, or administrator is identified. The story sounds technical while remaining impossible to verify from the message.
The repair button leaves the real email service
The “Immediate repair” button opens a website that is unrelated to the organization supposedly managing the mailbox.
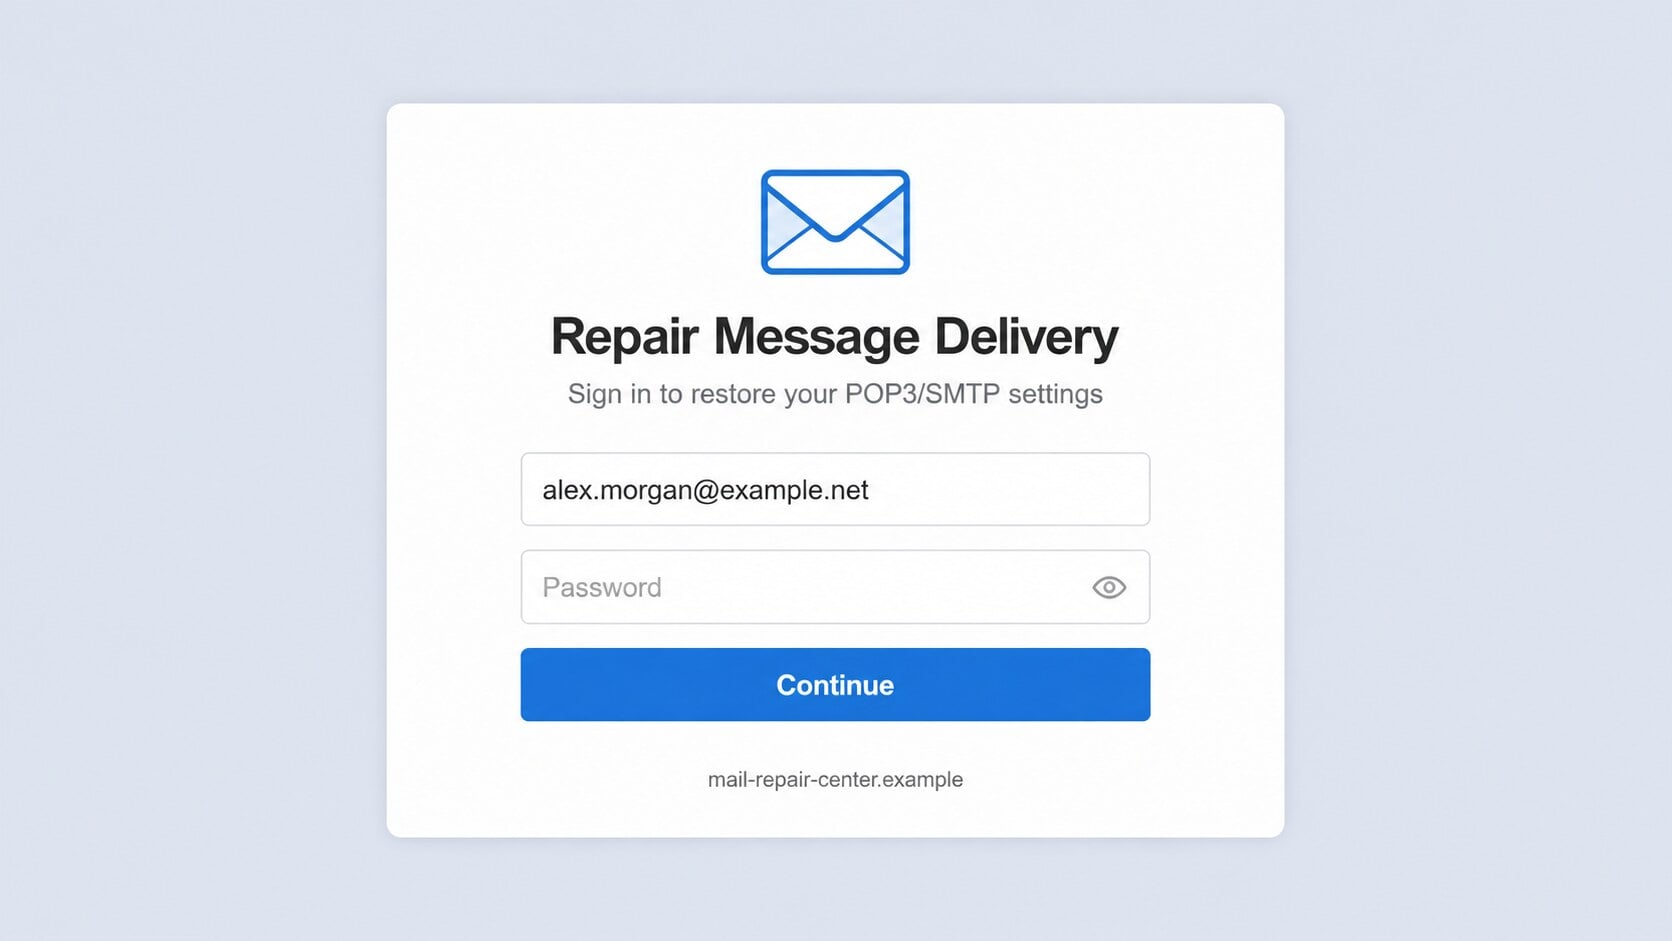
The destination displays a sign-in form and may imitate whichever provider matches the recipient’s address. Its appearance can change while the harvesting code remains the same.
Typing a password does not repair POP3 or SMTP. It supplies the credential to the operator controlling the counterfeit page.
The real target is the inbox and everything connected to it
Email access can expose private conversations, reset links, invoices, contacts, stored documents, and clues about financial accounts.
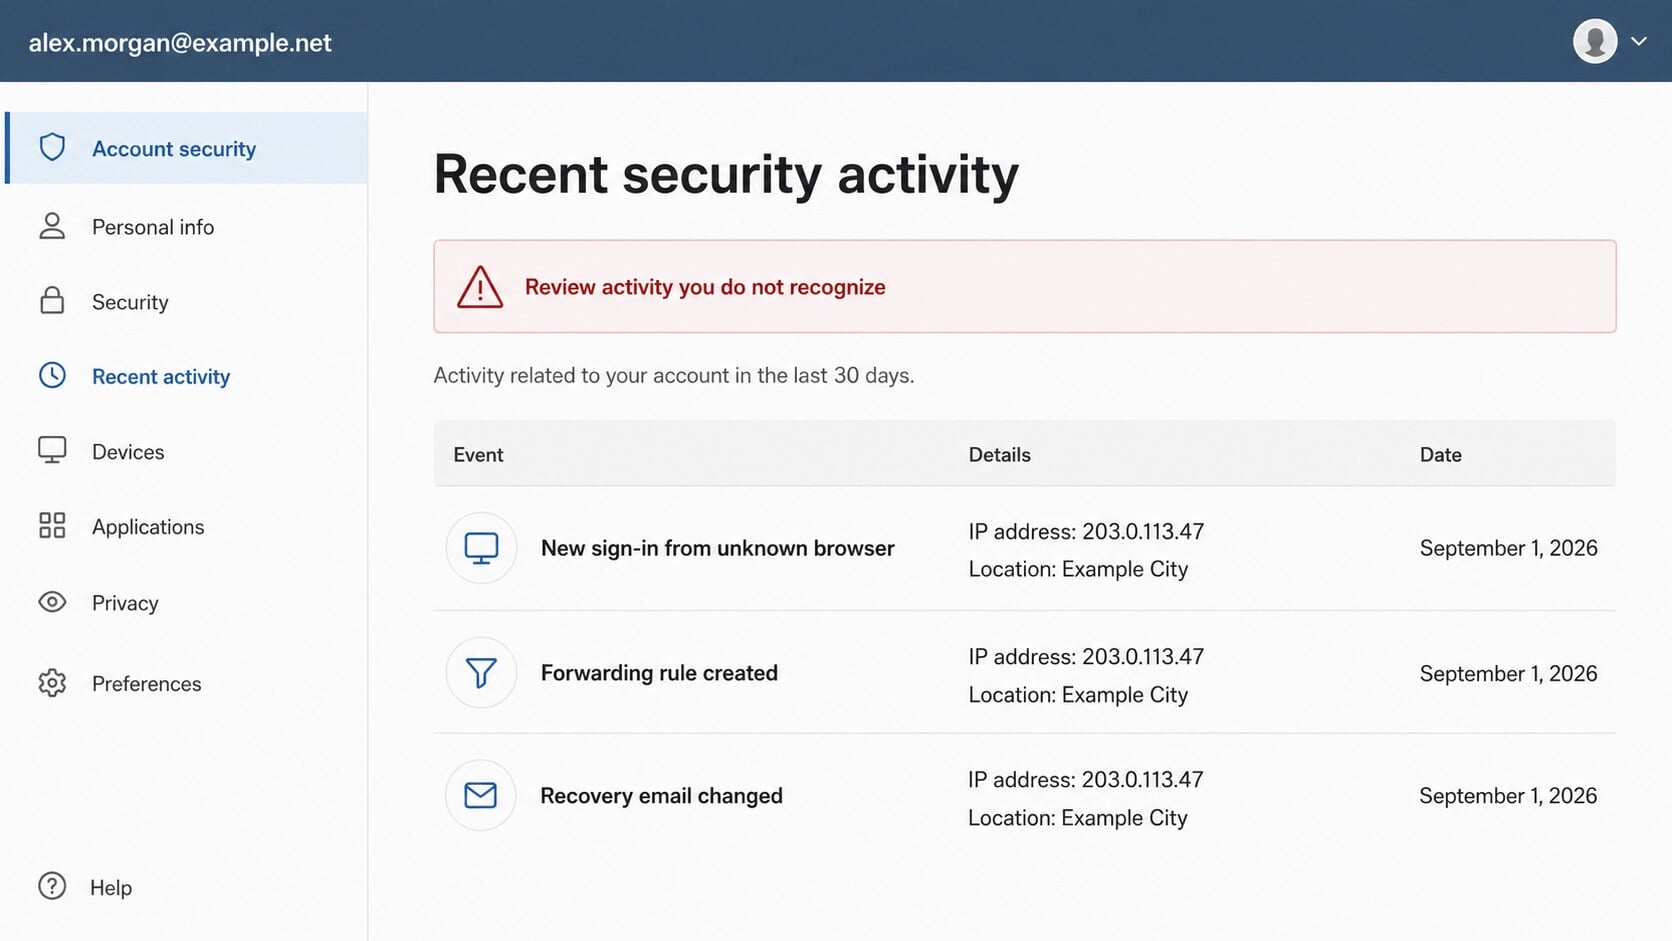
A criminal may quietly add forwarding rules instead of immediately locking out the owner. That lets new messages continue flowing to an outside address.
- The sender uses a generic mail-system identity rather than a known provider or administrator.
- The warning describes failed delivery without naming a single affected message.
- The button leads away from the mailbox’s genuine domain.
- The linked page requests a password for a problem that should be handled through server settings.
- Urgency replaces normal support details and verifiable technical evidence.
What Makes the Warning Look Believable
POP3 and SMTP are real terms used in the wrong way
POP3 can retrieve mail from a server, while SMTP handles sending and relaying messages. Their presence makes the notice resemble an administrator’s alert.
However, naming protocols does not prove a fault exists. A genuine notification normally identifies the affected host, account, error, and time of failure.
The scam supplies none of that context because the sender does not know how the recipient’s email is configured.
Missing mail creates uncertainty that cannot be checked instantly
A fake charge can be compared with a bank statement. An allegedly missing email is harder to disprove because the recipient does not know what never arrived.
That uncertainty encourages imagination. A worker may picture an urgent request, while a small business owner worries about a lost order.
The criminals do not need to know what the victim expects. They only need the warning to arrive during a believable moment.
The wording pushes one convenient solution
The message does not suggest opening normal settings, sending a test email, or contacting the known help desk.
Instead, every concern is compressed into one button. That design discourages independent checking and moves the recipient toward the attacker’s page.
Legitimate administrators can diagnose delivery problems through logs. They do not need users to enter passwords on an unfamiliar repair website.
How the Unusual Mail Delivery Scam Works
Step 1: A broad campaign reaches personal and workplace addresses
Attackers distribute the warning to addresses gathered from breaches, public contact pages, marketing databases, compromised accounts, and earlier phishing lists.
The email is usually not evidence that the sender knows anything about the mailbox. The same wording can be delivered to thousands of unrelated recipients.
Generic technical language helps the campaign cross industries. Almost everyone depends on email, but few users regularly inspect mail-server configuration.
Step 2: The alert invents a delivery failure
The body claims several messages could not be delivered because account settings are incorrect.
It adds a consequence, such as messages being returned or permanently lost. The threat makes waiting for an administrator feel risky.
Sometimes a date is attached to the repair button. That small detail turns a mass-produced message into something resembling a current incident.
Step 3: The link opens a page outside the trusted mailbox
The destination may use an obscure domain, a compromised website, free hosting, or abused cloud infrastructure.
A padlock icon does not make the page legitimate. Encryption only protects traffic to that site, even when the site belongs to a criminal.
Recipients should compare the full hostname with the provider they normally use. Visual branding inside the page is easy to copy.
Step 4: An adaptive login form asks for the mailbox password
The page may read the victim’s email address from the link and place it into the username field automatically.
Some phishing kits examine the domain after the @ symbol, then display colors or wording associated with that provider.
This personalization occurs inside the fraudulent site. It does not mean the page communicated with the real service or detected a configuration error.
When the password is submitted, the form sends it to attacker-controlled storage. A spinner or false error may conceal that transfer.
Step 5: Criminals attempt access before the victim becomes suspicious
Stolen credentials can be tested within minutes. Attackers check whether multifactor authentication is enabled and whether the same password works elsewhere.
If access succeeds, they search for financial conversations, identification documents, password resets, supplier details, and messages containing valuable personal information.
They may register an additional authentication method or create an app password to preserve access after the main password changes.
Step 6: Quiet mailbox rules hide the intrusion
Forwarding rules can copy every incoming message to an external account. Other filters can delete security warnings or move replies into rarely checked folders.
This approach lets the owner continue using email normally. The absence of an obvious lockout delays discovery.
Inside businesses, criminals can watch invoice discussions and intervene only when a payment is ready.
Step 7: The stolen identity supports additional fraud
Messages sent from a genuine compromised account are more persuasive than ordinary spam. Contacts recognize the address, signature, and existing conversation history.
Attackers may request gift cards, replace bank details, distribute malicious files, or ask colleagues to sign into another fake portal.
The original “repair” message therefore serves as an entry point. The most serious damage may happen days later through trusted conversations.
What a Genuine Delivery Problem Usually Looks Like
Real delivery failures leave evidence. A bounce message normally identifies the destination address, sending server, status code, and reason for rejection.
An administrator may also see queue information, storage limits, authentication failures, or DNS errors inside the legitimate hosting dashboard.
A generic email that asks for the current password cannot correct those conditions. Password submission is not a POP3 or SMTP diagnostic procedure.
If uncertain, send a test message from another account and contact the provider through a saved bookmark or independently located support address.
Sender, Domain, Server, and Mailbox Checks
The display name proves nothing
“Mail Delivery System” is ordinary text chosen by the sender. Expand the message details and inspect the full From and Reply-To addresses.
A free account, unrelated domain, or mismatched reply address is incompatible with a provider claiming authority over the mailbox.
The destination domain matters more than the page design
Hover over the repair button without clicking. The visible destination should belong to the email provider or organization that actually manages the account.
Random subdomains, unrelated country domains, URL shorteners, and cloud-storage links deserve immediate suspicion.
The server claim should produce specific evidence
Ask the administrator for the affected hostname, delivery status code, and message trace. A real incident can be supported with logs.
Scam messages avoid these details because there was no failed delivery event to record.
The mailbox should be checked through a clean route
Open webmail from a known bookmark or type the provider’s address yourself. Review notices, recent sessions, forwarding, filters, delegates, and recovery methods.
Do not use contact details inside the suspicious email. Locate support through the provider’s official site or an existing service agreement.
Warning Signs Worth Remembering
The strongest clue is the mismatch between the alleged technical fault and the requested action. Delivery troubleshooting does not require a password on a separate website.
- No failed sender, message subject, queue identifier, or error code is provided.
- The notice uses awkward grammar while claiming to be an automated professional system.
- The button is more prominent than any explanation or support path.
- The login page sits on a domain unrelated to the real mailbox.
- The form already knows the address because it was embedded in the phishing link.
- The page asks for credentials before showing any meaningful diagnostic result.
One clue may have an innocent explanation. Several appearing together strongly indicate that the message is designed to harvest credentials.
How Administrators Can Investigate the Reported Failure
Start with a controlled delivery test
Send messages from two unrelated external services to the affected address, then reply outward through the normal mail client.
Record timestamps and inspect whether each message arrives, bounces, or remains queued. A reproducible test is more useful than the email’s unsupported warning.
Do not reuse the suspicious link during testing. The goal is to examine the real mail path without giving the sender more information.
Read the headers and server logs together
Full headers reveal the servers that handled the warning, authentication results, source address, return path, and unexpected routing.
Delivery logs can show whether the named recipient experienced a rejection, storage problem, authentication failure, or transport delay.
If the system processed ordinary mail normally, there is no reason to accept the scam’s invented POP3 or SMTP diagnosis.
Look for evidence that the campaign reached others
Search the mail gateway for matching subjects, sender domains, button destinations, and message fingerprints.
Several copies sent to unrelated employees confirm broad targeting and help security staff identify anyone who clicked.
Block the malicious sender and destination, but retain a safe copy for investigation and user awareness.
Administrators should also check whether a compromised internal mailbox distributed the warning, since that requires account containment beyond ordinary spam blocking.
What to Do if You Have Fallen Victim to This Scam
Act promptly, but work methodically. The correct response depends on whether you only opened the email, clicked, entered credentials, or downloaded a file.
- Close the page and preserve evidence. Save the message, headers, destination address, and screenshots. Do not revisit the site to collect more details.
- Change the email password from a trusted device. Use a new, unique password that has never protected another service.
- End every active session. Use the provider’s security controls to sign out all browsers, devices, mail clients, and application sessions.
- Enable strong multifactor authentication. Prefer an authenticator application, passkey, or hardware security key over a reusable code sent by email.
- Inspect persistence settings. Remove unknown forwarding addresses, inbox rules, delegates, app passwords, recovery contacts, connected applications, and authentication methods.
- Protect connected accounts. Change reused passwords and review banking, shopping, cloud, payroll, and social accounts that depend on the compromised inbox.
- Tell the administrator and affected contacts. A workplace security team can search logs, revoke tokens, block the domain, and warn people who received follow-up messages.
- Scan if anything was downloaded. Run Malwarebytes to check for malicious files or browser changes. AdGuard can help block known deceptive pages and malicious advertising.
- Monitor for secondary fraud. Watch password-reset notices, invoices, sent mail, deleted items, bank activity, and unexpected authentication prompts.
- Report the campaign. Use the email provider’s phishing control and notify the relevant national cybercrime or consumer-protection authority when loss occurred.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
If you merely read the message and did not click, reply, download, or submit information, the email alone did not compromise the device.
Be cautious with anyone promising guaranteed recovery for an upfront payment. That follow-up may be another attempt to exploit the same incident.
Frequently Asked Questions
Is the Unusual Mail Delivery email real?
The version described here is fraudulent. Verify any genuine concern through your normal provider dashboard or a known administrator, never through the embedded repair button.
Can opening the email infect my computer?
Simply viewing ordinary message text is generally insufficient. Risk rises when you follow links, open attachments, enable scripts, or install downloaded software.
Why did the fake page already know my email address?
The phishing link can contain the address as a parameter. The page reads that value and pre-fills the form to create convincing personalization.
Does a padlock icon mean the repair page is safe?
No. HTTPS encrypts the connection to the current site. It does not confirm that the site belongs to your email provider.
What should I check after changing my password?
Review sessions, forwarding rules, filters, delegates, recovery methods, app passwords, connected applications, sent items, deleted mail, and recent security events.
Will changing the password remove malware?
No. Password changes secure the account. If you opened a file or installed anything, scan the device separately and remove unfamiliar software or extensions.
The Bottom Line
The Unusual Mail Delivery scam turns an invisible mail problem into a reason to visit a counterfeit login page.
Ignore the button, check the mailbox independently, and treat any submitted password as compromised. Fast session revocation and rule inspection can prevent broader damage.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.