

A new-device login warning can make you stop whatever you are doing. When it appears to concern your business mailbox, even a brief delay feels uncomfortable.
This cPanel-branded email gives you a button and a deadline. The details around that request deserve attention before you decide how to respond.
Overview
A security alert with a built-in response
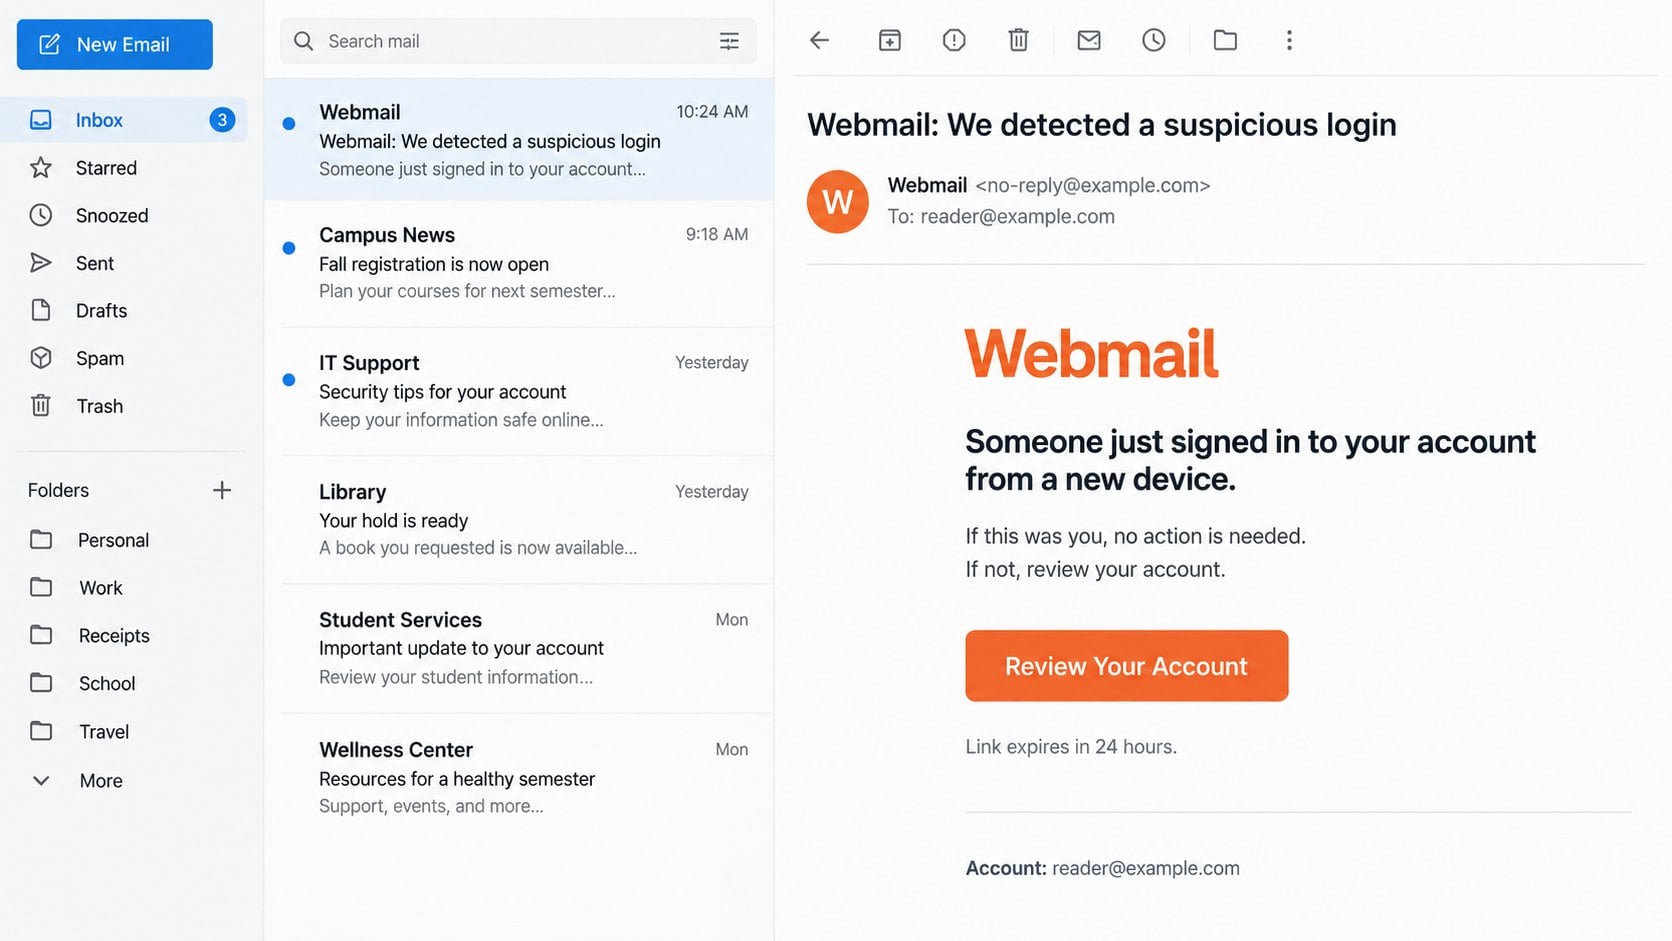
The cPanel new device login email scam impersonates a webmail security notification. It says a login was detected and asks the recipient to review the account.
The wording follows a familiar pattern: if the activity was yours, no action is needed. Otherwise, you should use the supplied review option.
That conditional instruction makes the message sound considerate rather than indiscriminately alarming. It resembles notices people receive from services they genuinely use.
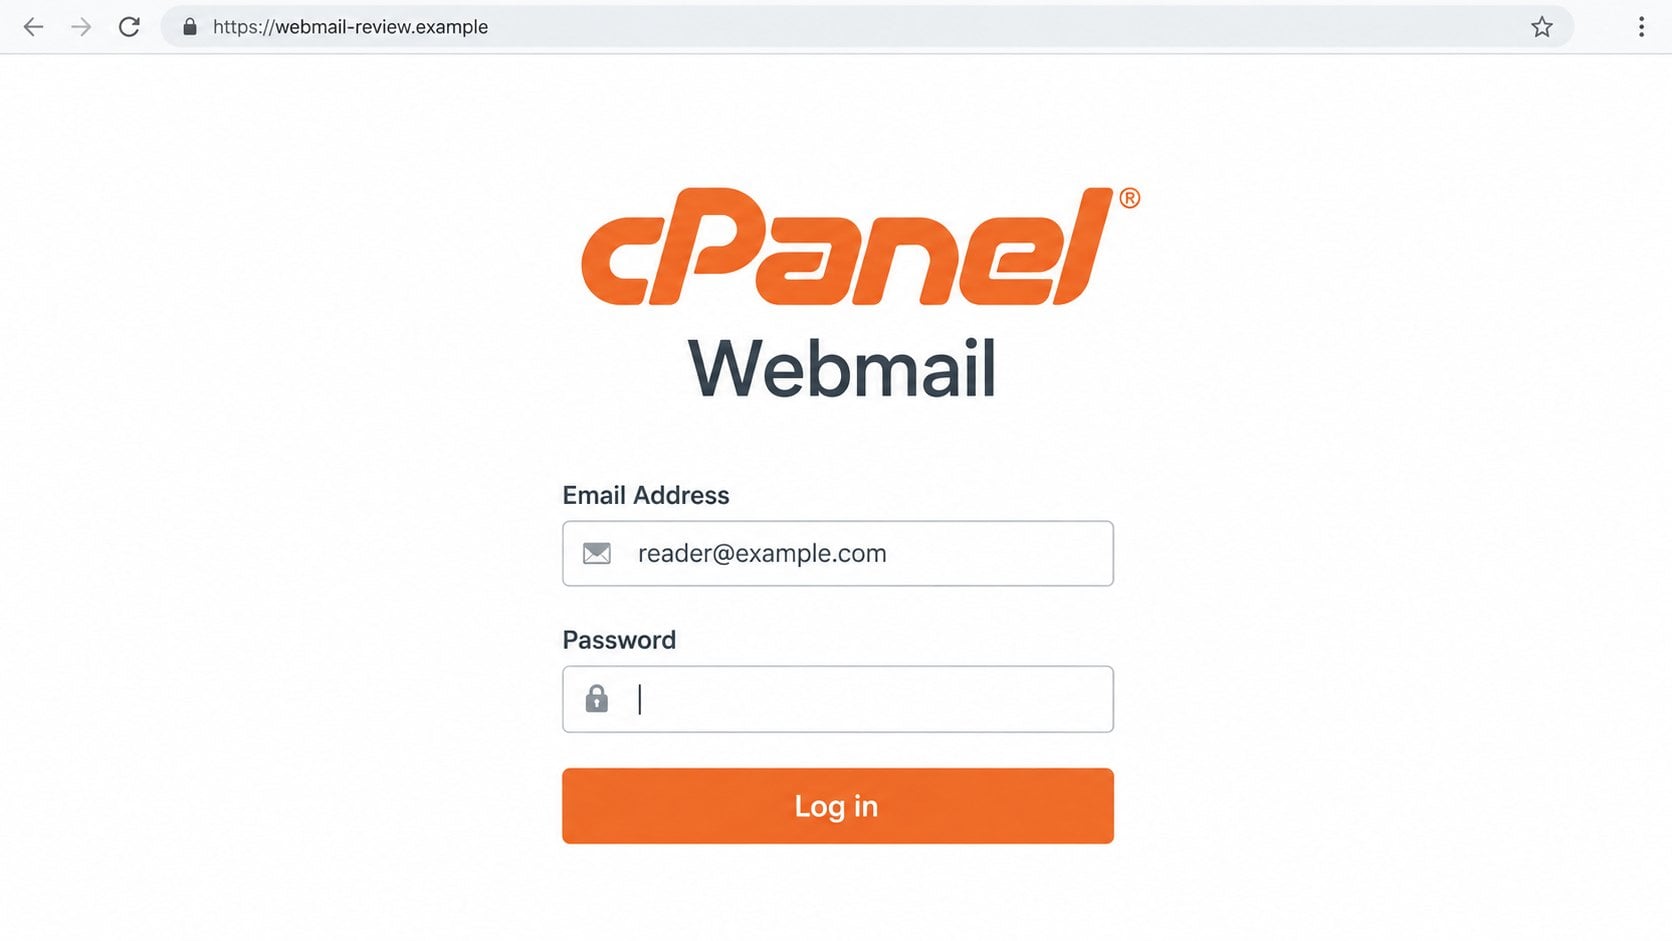
However, the reported button leads to webmail.reviewactivites[.]us, where a counterfeit cPanel-style page requests an email address and password.
The invitation to investigate a possible intrusion is therefore the route used to collect credentials. The warning itself does not prove that an intrusion already happened.
- Impersonated service: a cPanel-associated webmail account.
- Claimed event: a suspicious login from a new device.
- Pressure point: a request to review the account within 24 hours.
- Observed risk: credentials submitted to a fake webmail sign-in page.
Why the hosting context matters
cPanel is legitimate hosting software, not evidence that every email displaying its name came from your hosting company. Many unrelated providers use its interfaces.
Your webmail login might legitimately use your domain, a server hostname, or a provider-specific address. It does not have to be a page at cpanel.com.
That variety gives impersonators room to confuse people. A plausible-looking address containing “webmail” can feel acceptable when you are unsure what the genuine address should be.
The safe comparison is your established hosting setup. Check the login route in your own provider’s records instead of judging a new address by its vocabulary.
A fake alert is different from a confirmed account breach
The examined email and destination support a phishing finding. They do not establish an actual unauthorized session, a stolen website, or a compromised hosting server.
An attacker may attempt further access after obtaining valid credentials. What becomes accessible depends on the account, its permissions, password reuse, and any additional authentication controls.
A mailbox password is not automatically a hosting administrator password. Still, people sometimes reuse credentials, and email can contain sensitive hosting correspondence.
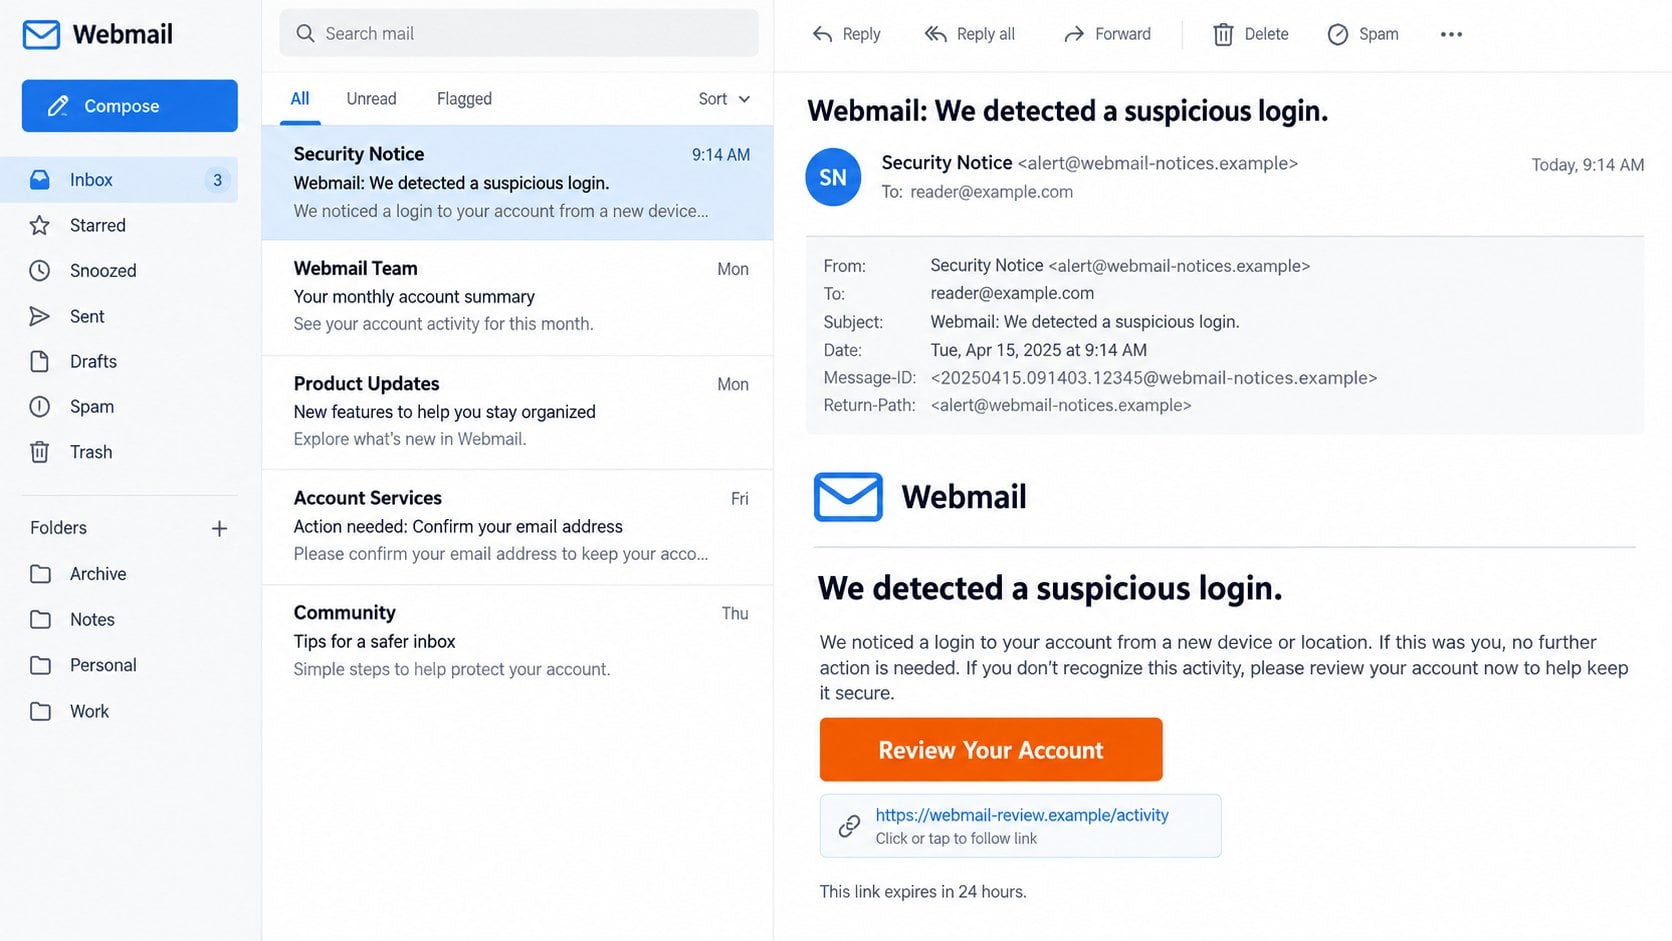
The images here are illustrative interface examples, not live captures of an affected reader’s account. Fictional addresses keep the visual explanation separate from active phishing infrastructure.
How the cPanel New Device Login Email Scam Works
Step 1: The message arrives as a security notification
The subject suggests that suspicious activity has already been detected. That places the recipient in response mode before they have checked the source.
Someone responsible for a company mailbox may worry about clients, invoices, or private documents. The alert borrows urgency from those genuine responsibilities.
The scam does not need to describe a sophisticated breach. A brief reference to an unfamiliar device can be enough to make an account review seem reasonable.
A legitimate service might also send such a notice. The problem is not the existence of security emails, but the unverified route this one supplies.
Step 2: The conditional wording builds credibility
The instruction to ignore the warning if the login was yours resembles normal account-security language. It gives the appearance of a measured, relevant notification.
For recipients who were not signing in, that same wording creates an obvious next move. They are the people supposedly expected to press the review button.
This is more subtle than demanding a password outright in the email. The request is presented as the first step in protecting an account.
Notice what remains unverified: whether the sender observed anything, whether it administers your mailbox, and whether its proposed review page belongs to your provider.
Step 3: The 24-hour deadline narrows the decision
A deadline encourages you to solve the issue immediately, perhaps while reading mail on a busy morning. Checking old hosting records can feel inconvenient by comparison.
That inconvenience is useful to the attacker. The supplied button appears faster than locating the familiar login page or asking a colleague who manages hosting.
A security incident deserves prompt attention, but prompt attention does not require using an untrusted link. You can investigate through your existing provider just as quickly.
Do not interpret the timer as an authoritative account policy. In this campaign, it is part of the message’s persuasion, not a verified provider instruction.
Step 4: The review button becomes an unfamiliar login
At the reported destination, the page imitates cPanel webmail and asks for credentials. Familiar colors and layout help conceal the change in who controls the session.
The address contains a webmail label and words suggesting account review. Those words describe what the operator wants you to believe, not who owns the page.
Even a secure connection symbol only concerns the connection to the displayed site. It cannot establish that the site is your hosting provider.
If you were already reading mail elsewhere, being asked to sign in again might seem routine. That expectation can prevent a closer look at the address.
Pause at that transition. The page is no longer merely telling you about a supposed event. It is asking you to disclose a secret.
Step 5: The counterfeit form receives the credentials
Information submitted to a page controlled by the attacker can be collected there. Entering the correct password does not turn that page into a legitimate login.
The attacker may then try the combination at the real mailbox. A successful attempt is not guaranteed, particularly where additional verification or provider protections intervene.
For the recipient, however, the password should be treated as exposed once submitted. Waiting for visible damage can leave a preventable access opportunity open.
A spinning indicator, blank page, or error afterward is not reassurance. The form may have received the information before showing anything else.
Step 6: A mailbox incident can affect connected work
If access succeeds, the mailbox may contain client discussions, account notices, or previous support conversations. Those details could make later impersonation attempts more convincing.
For example, an intruder reading an invoice discussion could attempt to insert a new payment instruction. That is a possible follow-on abuse, not an observed outcome here.
Unauthorized sending, forwarding, or recovery changes may also be possible, depending on the account. The provider should help establish what actually happened.
Do not jump from one disclosed mailbox password to assuming the entire server is lost. Investigate the affected account and any genuinely shared credentials first.
How to Verify the cPanel Warning and Your Hosting Provider
Start with your existing hosting relationship
Find the company that provides the mailbox through your normal billing account or established support contact. A cPanel logo alone does not answer that question.
If someone else set up the domain, ask them for the approved webmail route. For a workplace account, use the internal help desk rather than improvising.
Explain that you received a new-device alert and want its authenticity checked. Support does not need your password to understand which message you mean.
Avoid telephone numbers or chat links appearing only in the suspicious notice. They could return you to the same operator through a different channel.
Compare the full login address with a trusted record
Use an existing bookmark or the provider’s customer portal to reach webmail. Compare that address with the one supplied by the email.
Hosting logins can use different domains and server names legitimately. This is why a remembered brand color or a single familiar word is an unreliable test.
Your provider may also offer an external identity option. If so, confirm the arrangement through its documentation rather than assuming every unexpected login screen is fraudulent.
In the reported case, the unrelated review address and counterfeit collection page are the concern. Do not turn that specific finding into a universal domain rule.
Ask for actual account activity, not a copied warning
Look for recent sessions or security events through the account’s normal controls, if available. Not every webmail installation exposes the same activity information to users.
Where there is no suitable view, ask the host or administrator to investigate. They may have records that the mailbox interface does not show.
Describe your own recent logins accurately. A changed device, browser, network, or travel location can complicate interpretation, so avoid treating every unfamiliar detail as proof.
Equally, do not dismiss a confirmed unexplained session because the original email was fake. The email’s authenticity and your account’s condition are separate questions.
Establish which credentials and permissions were involved
A webmail account, hosting customer portal, and server administrator account can be different things. Identify exactly which username and password you entered.
If the same password was reused across them, explain that to the provider without disclosing the password itself. Reuse expands the accounts needing attention.
Ask whether forwarding, delegated access, or recovery settings changed. These checks are more useful than an unsupported assumption that every website file was altered.
For businesses, record the affected mailbox and relevant time window. That helps administrators assess exposure without making the incident sound broader than the evidence supports.
What to Do If You Fell Victim to the cPanel New Device Login Email Scam
- Leave the phishing page and identify what you disclosed.
Close the browser tab. Note whether you entered only an email address, a password, an authentication code, or other information.
Do not submit another form to undo the first one. An attacker-controlled page cannot reliably confirm that your account is safe.
- Reset the affected password through the established hosting route.
Open the provider’s genuine portal or normal webmail address. Replace an exposed password with a unique one, and avoid making only a small predictable change.
If the mailbox no longer accepts your credentials, contact the provider through existing customer records. Tell workplace IT immediately when an organizational account is involved.
- Ask about active sessions and additional access.
Use available controls to end unfamiliar sessions, or ask the administrator to invalidate access. Review recovery details and authentication settings for unauthorized changes.
Enable multifactor authentication wherever your provider supports it. If a login approval appears unexpectedly, deny it and report the attempt rather than approving it to proceed.
- Check mail handling and messages sent from the account.
Inspect forwarding, filters, delegated permissions, and the Sent folder. Ask the provider to help when these controls are hidden or centrally managed.
Keep a record of suspicious changes before correcting them. If recipients received fraudulent requests from your address, warn those recipients through a trusted alternative channel.
- Change genuinely reused credentials on other services.
Prioritize hosting administration, your customer portal, and any other account sharing the exposed password. Do not assume that changing one account changes the rest.
If all passwords were already different, report that too. It helps keep the response focused instead of treating every connected system as automatically compromised.
- Address downloads or installations separately.
The observed campaign centers on phishing. If your interaction also involved a downloaded file or unexpected software, run an updated Malwarebytes scan and inform IT.
AdGuard may reduce encounters with some malicious ads and tracking. It cannot revoke stolen credentials, inspect all hosting permissions, or authenticate every cPanel-looking page.
- Preserve the notice and request a documented follow-up.
Save the original email, the suspicious address, and approximate interaction time. Share these with the host through its established support system, without passwords or private codes.
Ask what activity was confirmed and what access was revoked. That answer is more useful than a vague reassurance based solely on changing the password.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
For Small Businesses Managing Shared Hosting
This warning can expose a practical gap: nobody knows the approved webmail address because everyone normally follows old links. Fix that confusion after handling any immediate exposure.
Keep the hosting provider, account owner, and support route in an accessible internal record. Employees should not need a suspicious email to discover who manages their mail.
A short reporting habit also helps. Staff can forward questionable account notices to a designated person instead of deciding alone whether a deadline is genuine.
Do not circulate passwords as part of that process. The goal is a clear route to verification, not a shared document containing credentials.
If one employee submitted information, investigate the relevant account calmly. Blame and exaggerated claims can discourage the next person from reporting a similar mistake promptly.
Frequently Asked Questions
Does this message mean someone already logged in?
No. The phishing email alleges a login, but that is not independent evidence. Check real activity through the hosting provider or your administrator.
Is cPanel responsible for the scam?
The campaign impersonates cPanel-associated webmail. Its branding does not establish involvement by the software vendor or by the company hosting your legitimate account.
Must a real webmail login use cpanel.com?
No. Providers commonly use their own domains or server addresses. Verify the route against your existing hosting records instead of relying on one universal hostname.
Can a mailbox password give an attacker server administration?
Not automatically. Account permissions and password reuse matter. Tell the provider which credentials were exposed so it can assess the appropriate scope.
What if I clicked but did not type anything?
Close the page and report the message. A click alone does not demonstrate credential theft, although downloads, approvals, or other interactions would change the response.
Should I ignore every new-device email now?
No. Genuine alerts can be useful. Investigate them through a trusted account route, especially when a notice supplies an unfamiliar login page or demands urgent action.
The Bottom Line
The cPanel new device login scam disguises password collection as an account review. A familiar interface and a 24-hour deadline do not authenticate its sender.
Reach webmail through your established provider. If credentials were submitted, secure the affected account and verify its activity without assuming more damage than the evidence shows.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.