

An email about phishing training seems like something worth reading. You want to follow the rules, especially when the subject mentions a potential threat.
But what should a security exercise actually ask you to do? Before responding to this notice, look at how its instructions fit together.
Overview
A training announcement with an account-access request
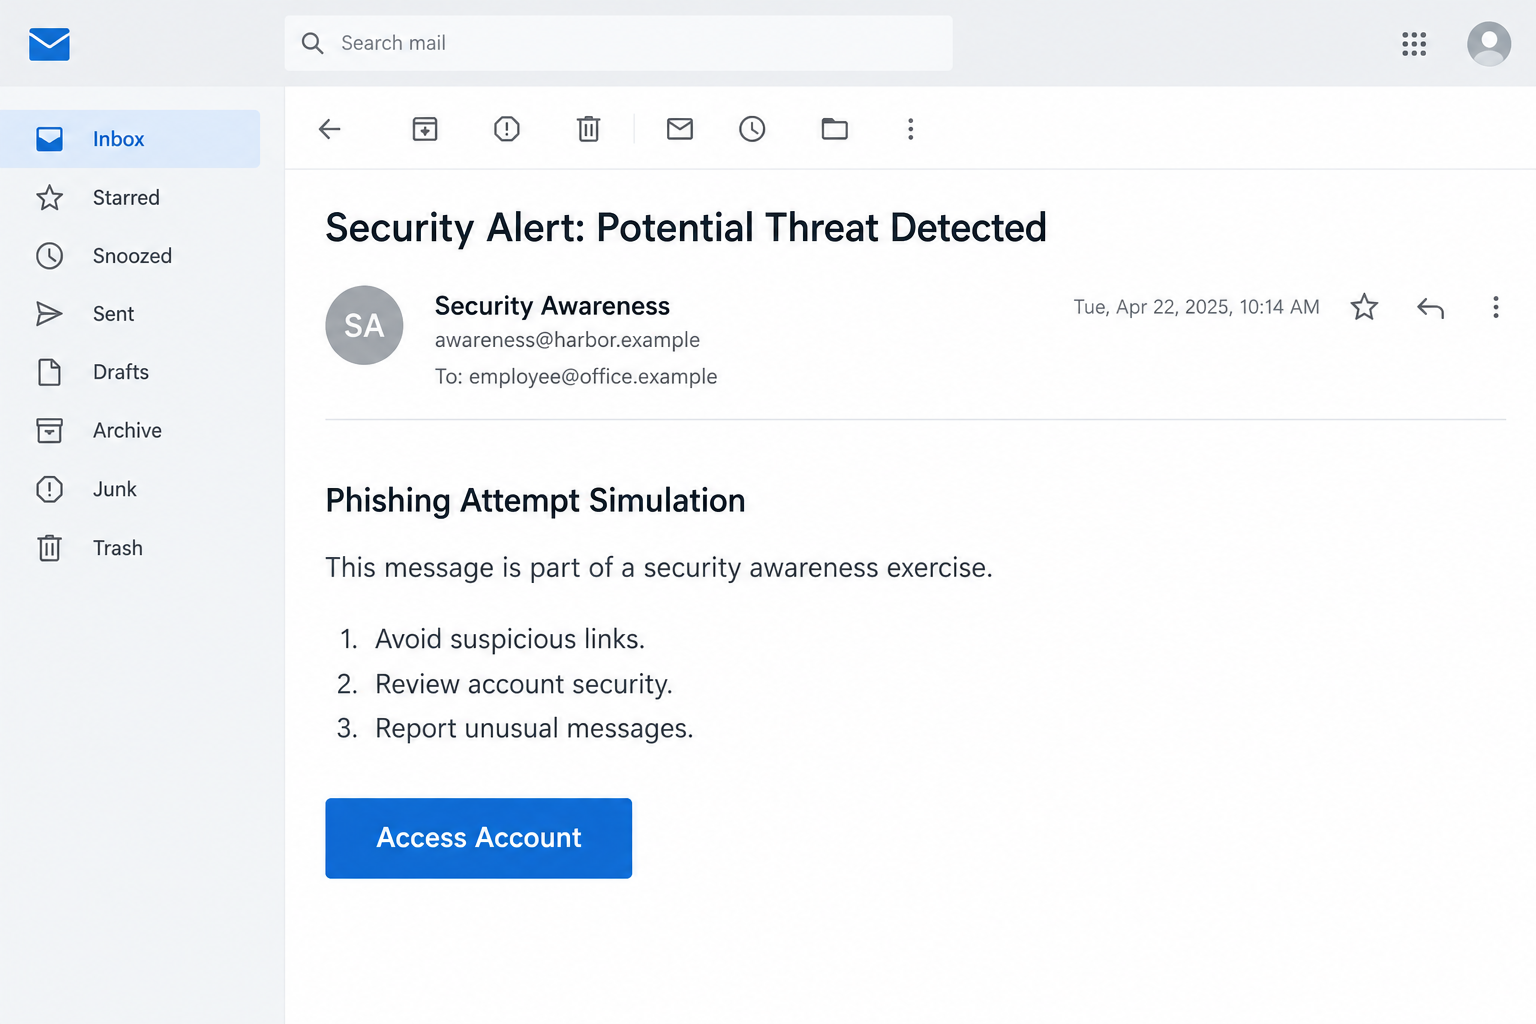
The phishing attempt simulation email scam presents itself as an authorized security exercise. The reported subject is “Security Alert: Potential Threat Detected.”
Its instructions mix sensible precautions with links for security measures, reporting, and an Access Account button. That combination makes the message sound protective rather than threatening.
The reported account link leads to skyverticals[.]com, where an imitation email-provider login seeks the recipient’s password. The original organization is not established by the notice.
Real simulations do not authenticate this particular email
Employers really do test phishing awareness. Microsoft’s Attack simulation training documentation describes controlled exercises that can include simulated messages and landing pages.
A third-party training domain or an unexpected test message is therefore not sufficient, by itself, to establish fraud. Authorization must come from your actual organization.
Here, the security story is used to draw readers toward a credential-collection page. Calling the request a simulation does not make that password request safe.
The useful question is who authorized the action
Before interacting, separate the claimed exercise from the account you are being asked to expose. These details deserve attention:
- A security alert announces training without independently establishing the organizer.
- Several helpful-sounding links encourage interaction with the same unverified message.
- An account-access button leads outside your established email sign-in route.
- Familiar provider graphics appear where the message has not established a trusted relationship.
- The requested secret protects your real mailbox, not a harmless practice account.
The image is an illustrative email with invented addresses and a sample date. It explains the training pretext, rather than documenting an actual employee’s inbox.
Why Security Advice Can Make This Email More Convincing
Most people expect phishing to arrive with a strange prize, unpaid invoice, or alarming account threat. Advice about avoiding suspicious links feels like the opposite.
You may recognize the safety advice and relax. The trouble is that accurate tips do not tell you who put the account-access link beside them.
The email also supplies a reassuring explanation for anything unusual. An unexpected sender or awkward link might seem intentional because the message says it concerns training.
This creates a trap for conscientious employees. They may believe participation demonstrates awareness, while refusing to click could look like ignoring a security requirement.
A useful workplace rule removes that pressure: reporting uncertainty is a valid response. Nobody needs to expose a real password to prove they recognize phishing.
Imagine receiving the notice shortly before a meeting. You may intend to clear a minor administrative task, not make a significant account-security decision.
The Access Account button turns that small intention into a different action. Instead of reading training material, you are asked to trust a new sign-in destination.
That is the point to pause. Helpful advice in the surrounding paragraphs cannot establish who receives information entered into the linked form.
How the Phishing Attempt Simulation Email Scam Works
Step 1: A potential-threat subject creates a reason to read
The subject suggests that something security-related needs attention. It is broad enough to fit almost any workplace without naming a particular incident.
Once opened, the simulation explanation reduces the initial alarm. The reader is encouraged to think the organization already understands and controls the situation.
That shift is useful to the attacker. The message first attracts attention, then offers a comforting reason to cooperate rather than question its origin.
No actual employer authorization follows from this wording. An outsider can describe an exercise without having any relationship with the company’s security staff.
Step 2: Familiar precautions lend credibility to the links
Instructions about suspicious messages and reporting sound like ordinary awareness training. Readers may recognize the advice from previous workplace reminders.
The fraudulent part does not need to occupy the whole email. A single unsafe instruction can sit among several statements that are broadly sensible.
Links described as security measures or reporting options also offer apparent choices. Yet the sender still chooses every destination available inside that message.
If you want to report the notice, use your mail client’s established reporting feature or the company’s known process. Do not rely on its own reporting link.
Step 3: Access Account moves the reader into a new context
The button sounds like a route to training records, account status, or further instructions. Its short label does not reveal who operates the destination.
In the reported case, that route used skyverticals[.]com. A branded page there cannot become your email provider merely by displaying the provider’s logo.
Legitimate training systems may use external services, so verification should involve your organization’s approved process rather than a simple rule against every unfamiliar domain.
Ask IT whether this specific notice and destination are part of an authorized exercise. Do so through contact details you already possess.
Step 4: A familiar login design requests a real secret
The reported landing page imitates an email sign-in experience, including provider-specific presentation. The aim is to make credential entry feel routine.
At this stage, the distinction between a practice exercise and a live account becomes critical. Your normal mailbox password is not a disposable training answer.
Appearance cannot establish where the form sends its contents. Copied branding, familiar field labels, and a copyright line can all be placed on an unrelated page.
Do not enter a password to discover whether the exercise is genuine. Close the form and verify the request before sharing anything.
Step 5: Credential exposure turns a supposed exercise into account risk
A captured password can be attempted against the real mailbox. Whether access succeeds depends on the account’s protections and any additional approvals the victim supplies.
The available evidence does not establish that every recipient lost access. It establishes a credential lure, not a demonstrated compromise of every targeted organization.
If access is obtained, correspondence may reveal useful contacts and ongoing business. Follow-up messages can then arrive with details that feel much more convincing.
The remedy is to protect the actual account and investigate its activity. Completing more instructions from the purported training email will not resolve that exposure.
How to Verify a Phishing Exercise Without Taking Its Bait
Use the reporting route you already know
A company may deliberately keep the timing of simulations confidential. That does not prevent staff from asking how suspicious messages should be handled.
Use a saved help-desk address, an internal directory, or the reporting button already installed by your organization. Describe the subject and the action requested.
Do not forward the message widely to ask coworkers whether they clicked. That can spread an active lure and generate conflicting guesses.
Security staff may decline to reveal whether a particular message is a test. Follow their established reporting procedure rather than trying to solve that uncertainty yourself.
Distinguish training access from mailbox access
An awareness platform can have its own account or use an approved identity service. Those arrangements should be explainable through your employer’s existing onboarding material.
A legitimate single sign-on process is not simply a page that asks for your usual password. The identity provider and the organization’s authorization both matter.
Open the known employee portal separately if you need training records. A required course can often be located without using the suspicious email’s button.
If access still seems unclear, ask which service should perform authentication. Do not send your password to the help desk as part of that question.
Do not let a possible test discourage reporting
Employees sometimes hesitate because they fear looking inexperienced. Others assume reporting a simulation will annoy the team that arranged it.
Both reactions help an impersonator. A prompt report gives the organization a chance to assess the message before more people respond.
If you already entered something, say so plainly. Reporting only that the email “looked suspicious” can hide the information needed to protect the account.
A useful report identifies the time, destination, account name, and actions taken. It should never contain the password or a fresh authentication code.
Check which organization is supposed to be running the exercise
Contractors and temporary staff may use more than one organization’s tools. A training email can seem plausible because either the employer or client might arrange it.
Do not resolve that uncertainty by trying both work passwords. Ask which organization owns the request and which approved identity should be used.
If the notice reaches a shared mailbox, establish who is responsible for training before anyone acts. A generic inbox is not automatically an individual employee’s learning account.
Keep the suspicious message available to the correct security team. Forwarding it between organizations without context can make another recipient mistake it for an approved instruction.
This check is particularly helpful when a message arrives during onboarding. Being new to the organization is a reason to ask, not a reason to improvise authentication.
What the Available Evidence Does and Does Not Show
The documented warning concerns a specific training-themed email and its counterfeit provider login. It is not an accusation against legitimate security-awareness programs.
A current attempt to capture the reported root address returned a forbidden page. That result did not reproduce the earlier login form or authenticate the original message.
Phishing pages can disappear, change, or require a particular path. A later error page is therefore not proof that an earlier credential submission was harmless.
No executable payload is established here. A person who only read the message has a different exposure from someone who installed a file offered during a follow-up.
Keep those distinctions when asking for help. They support a proportionate response without dismissing the real risk created by an exposed password.
What to Do If You Fell Victim
Stop interacting with the claimed exercise. Close its login page and ignore further requests to finish training, verify a result, or approve an unexpected sign-in.
If you only read the email, report it through your normal process. Reading its security advice does not, by itself, establish that your mailbox was compromised.
Tell the security team what you actually did. Identify the mailbox involved and whether you typed a password, shared a code, approved access, or installed anything.
Preserve the original message through the approved reporting system. Screenshots can help explain the experience, but the original email provides more useful routing information.
Replace the exposed password at the real service. Use your established sign-in route, not a recovery link supplied by the same sender.
For managed accounts, involve the administrator promptly. For a personal Google account, use Google’s compromised-account guidance if you cannot regain control normally.
Have existing access reviewed. Password replacement should be accompanied by checks of unfamiliar sessions, recovery changes, forwarding, and other mailbox access your provider supports.
Explain any authentication approvals you accepted. The administrator needs to assess actual access, not assume that changing one password automatically closes every route.
Deal with password reuse and affected conversations. Replace the same secret wherever else you used it. Give each important account a separate replacement.
If the mailbox sent messages without permission, let the responsible team warn affected contacts. Verify payment changes through established channels before anyone acts on them.
Check the device when there was device exposure. Use Malwarebytes if you installed unfamiliar software, opened a suspicious download, or notice unexplained browser changes.
AdGuard can help limit malicious advertising and known unsafe destinations. Neither product can undo a password disclosure or replace the organization’s account investigation.
Finish with a clear follow-up plan. Ask who owns the incident and which signs should be reported next. Continue using the genuine account only after recovery checks.
Avoid anyone demanding payment to certify that you passed the test or to recover the mailbox. Use the provider or your organization’s established support.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is every phishing simulation email a scam?
No. Authorized exercises are a real security practice. Verify this specific request through your organization’s established process instead of trusting the sender’s claim of authorization.
Does an external training domain automatically prove fraud?
No. Employers can use third-party platforms. The important questions are whether your organization authorized that destination and whether the requested authentication belongs there.
Why would a scam email include accurate security advice?
Accurate advice can make the surrounding message seem trustworthy. It does not establish who created the linked page or who receives credentials entered into it.
What if I clicked but supplied no information?
Report the notice and close the page. Without credential entry, approvals, downloads, or other interaction, a click alone does not demonstrate a successful mailbox takeover.
Should I revisit the page to see whether it was a test?
No. Let the responsible security team assess the original message. Reopening a reported credential lure adds exposure without providing dependable evidence of authorization.
Can a clean malware scan prove the account is safe?
No. A device scan concerns local software. Account security depends on credentials, approvals, active access, and settings that require separate review at the genuine service.
The Bottom Line
Do not enter your mailbox password through this phishing simulation notice. Its training explanation does not authorize the linked imitation login or establish a trusted security exercise.
Verify the message with your actual organization. If you responded, report the precise actions and secure the real account before treating the incident as closed.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.