

If your computer is locked, and you are seeing a “ATTENTION! Your computer has been locked and all data is encrypted!” notification from FBI CyberCrime Division (ICSPA) , then your computer is infected with a piece of malware known as Trojan Reveton.
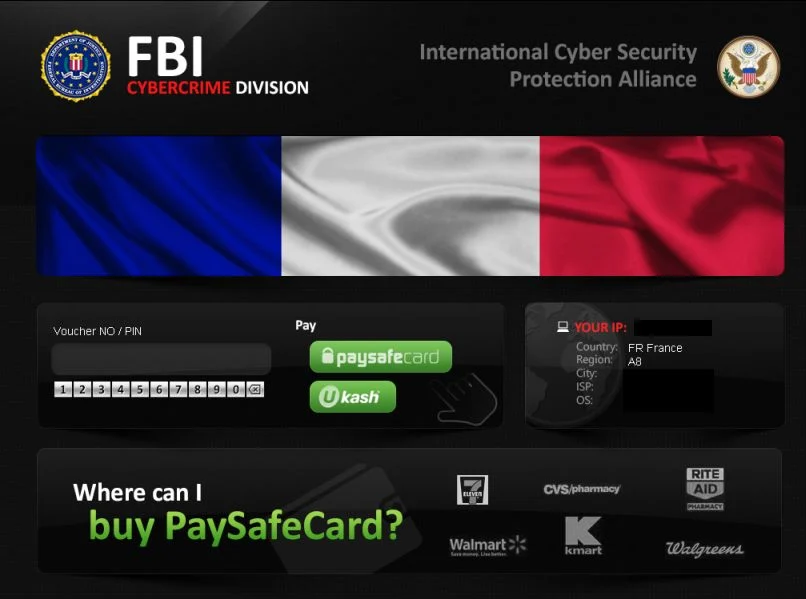
The FBI CyberCrime Division trojan is distributed through several means. Malicious websites, or legitimate websites that have been compromised, may drop this trojan onto a compromised computer. This drive-by-download often happens surreptitiously. Another method used to propagate this type of malware is spam email containing infected attachments or links to malicious websites. The threat may also be downloaded manually by tricking the user into thinking they are installing a useful piece of software.
The FBI CyberCrime Division (ICSPA) virus is also prevalent on peer-to-peer file sharing websites and is often packaged with pirated or illegally acquired software.
Once installed on your computer, the FBI CyberCrime Division virus will display a bogus notification that pretends to be from the International Cyber Security Protection Alliance, and states that your computer has been blocked due to it being involved with the distribution of pornographic material, SPAM and copyrighted content.
The FBI CyberCrime Division (ICSPA) virus will lock you out of your computer and applications, so whenever you’ll try to log on into your Windows operating system or Safe Mode with Networking, it will display instead a lock screen asking you to pay a non-existing fine in the form of a Ukash, MoneyPak or Paysafecard.
Furthermore, to make this alert seem more authentic, this virus also has the ability to access your installed webcam, so that the bogus FBI CyberCrime Division (ICSPA) notification shows what is happening in the room.
The FBI CyberCrime Division (ICSPA) virus locks the computer and, depending on the user’s current location, displays a localized webpage that covers the entire desktop of the infected computer and demands payment for the supposed possession of illicit material.
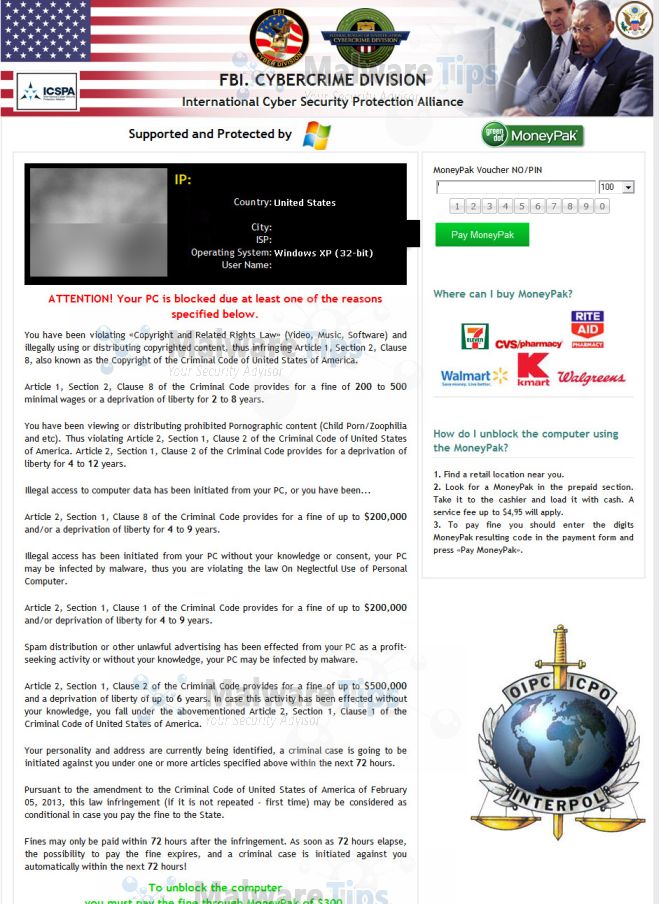
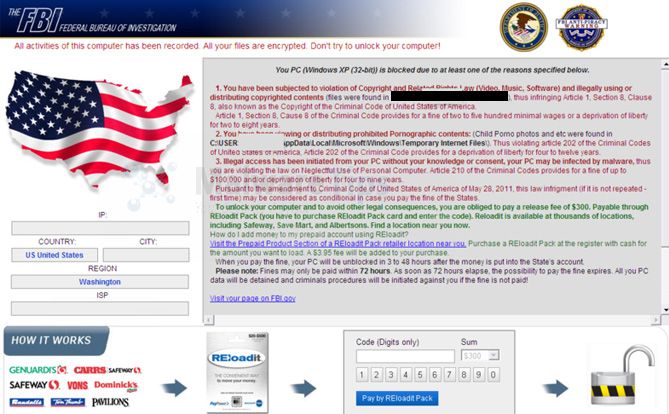
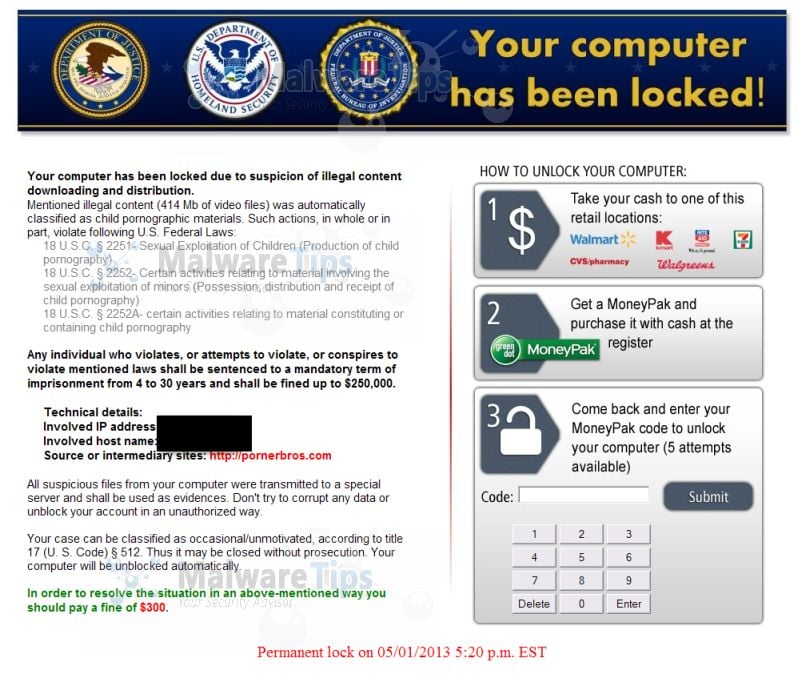
Cyber criminals often updated the design of this lock screen, however you should always keep in mind that the Federal Bureau of Investigation will never lock down your computer or monitor your online activities.
The message displayed by the threat can be localized depending on the user’s location, with text written in the appropriate language.
The FBI CyberCrime Division (ICSPA) lock screen is a scam, and you should ignore any alerts that this malicious software might generate.
Under no circumstance should you send any Ukash or MoneyPak code to these cyber criminals, and if you have, you can should request a refund, stating that you are the victim of a computer virus and scam.
FBI CyberCrime Division (ICSPA) lock screen – Virus Removal Guide
STEP 1: Remove FBI CyberCrime Division (ICSPA) lock screen from your computer
FBI CyberCrime Division (ICSPA) virus has modified your Windows registry and added its malicious files to run at start-up, so whenever you’re trying to boot your computer it will launch instead its bogus notification.To remove these malicious changes, we can use any of the below methods :
Method 1: Start your computer in Safe Mode with Networking and scan for malware
Some variants of FBI CyberCrime Division (ICSPA) virus will allow the users to start the infected computer in Safe Mode with Networking without displaying the bogus lock screen. In this first method, we will try to start the computer in Safe Mode with Networking and then scan for malware to remove the malicious files.
- Remove all floppy disks, CDs, and DVDs from your computer, and then restart your computer.
- Press and hold the F8 key as your computer restarts.Please keep in mind that you need to press the F8 key before the Windows start-up logo appears.
Note: With some computers, if you press and hold a key as the computer is booting you will get a stuck key message. If this occurs, instead of pressing and holding the “F8 key”, tap the “F8 key” continuously until you get the Advanced Boot Options screen. - On the Advanced Boot Options screen, use the arrow keys to highlight Safe Mode with Networking , and then press ENTER.
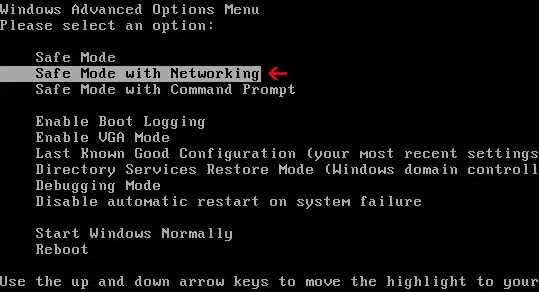
- If your computer has started in Safe Mode with Networking, you’ll need to perform a system scan (as seen on STEP 2) with Malwarebytes Anti-Malware and HitmanPro to remove the malicious files from your machine.
IF the FBI CyberCrime Division (ICSPA) virus didn’t allow you to start the computer in Safe Mode with Networking,you’ll need to follow Method 2 to get rid of its lock screen.
Method 2: Restore Windows to a previous state using System Restore
System Restore can return your computer system files and programs to a time when everything was working fine, so we will try to use this Windows feature to get rid of FBI CyberCrime Division (ICSPA) lock screen.
- Restart your computer, and then press and hold F8 during the initial startup to start your computer in safe mode with a Command prompt.
Note: With some computers, if you press and hold a key as the computer is booting you will get a stuck key message. If this occurs, instead of pressing and holding the “F8 key”, tap the “F8 key” continuously until you get the Advanced Boot Options screen. - Use the arrow keys to select the Safe mode with a Command prompt option.
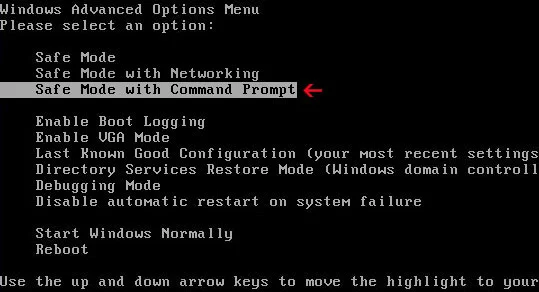
- At the command prompt, type cd restore, and then press ENTER.
Next,we will type rstrui.exe , and then press ENTER.Alternatively, if you are using Windows Vista, 7 and 8, you can just type : C:\windows\system32\rstrui.exe , and press ENTER.
If you are using Windows XP, you will need to type C:\windows\system32\restore\rstrui.exe, and then press ENTER.
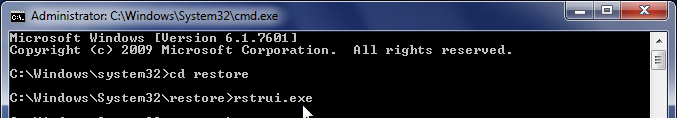
- The System Restore utility will start, and you’ll need to select a restore point previous to this infection.
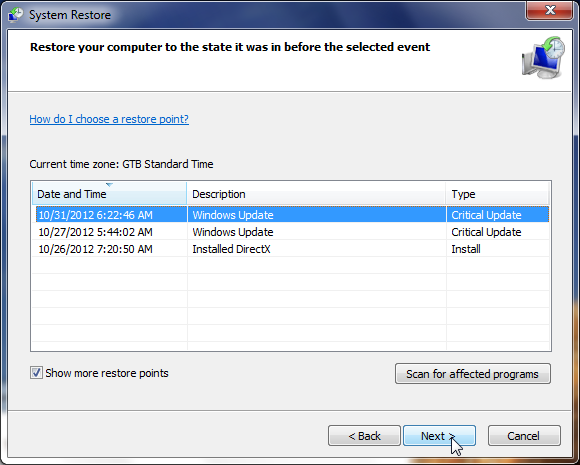
- After System Restore has completed its task, you should be able to boot in Windows normal mode, and perform a system scan (as seen on STEP 2) with Malwarebytes Anti-Malware and HitmanPro to remove the malicious files from your machine.
IF the FBI CyberCrime Division (ICSPA) virus didn’t allow you to restore your computer to a previous point, you’ll need to follow Method 3 to get rid of its screen lock.
Method 3: Remove FBI CyberCrime Division (ICSPA) lock screen with msconfig utility
When your computer was infected with the FBI CyberCrime Division (ICSPA) virus, this trojan has set a its malicious files to start whenever your computer is booting. IF you didn’t have a restore point, we can use msconfig to remove it’s malicious start-up entry.
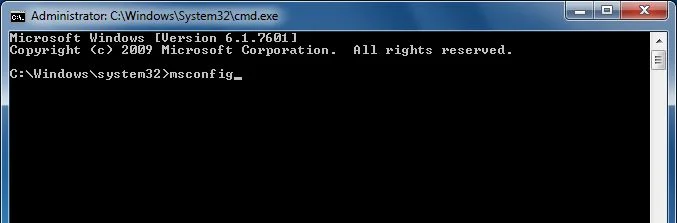
- While your computer is in Safe Mode with Command Prompt, type msconfig to start the Windows System Configuration utility.
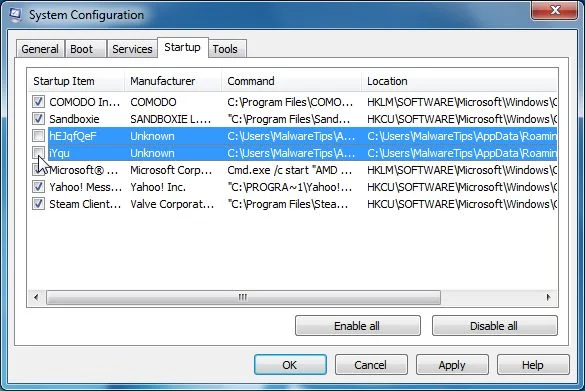
- Click on the Startup tab, then search for any suspicious or unknonw entries (random numbers or letters, ctfmon.exe, and other suspicious or unknown entries), and unckech them from startup, then click on OK.
This will stop the FBI CyberCrime Division (ICSPA) virus from starting with Windows, however it won’t remove the malicious files from your computer.
- Type shutdown /r in the command prompt to restart your computer, then perform a scan with Malwarebytes Anti-Malware and HitmanPro as seen on STEP 2.
IF the FBI CyberCrime Division (ICSPA) virus didn’t allow you to start the computer in Safe Mode with Command Prompt you’ll need to follow Method 4 to get rid of its screen lock.
Method 4: Remove FBI CyberCrime Division (ICSPA) virus with HitmanPro Kickstart
IF you couldn’t boot into Safe Mode with Command Prompt or didn’t have a System Restore point on your machine, we can use HitmanPro Kickstart to bypass this infection, and access your computer to scan it for malware.
- We will need to create a HitmanPro Kickstart USB flash drive,so while you are using a “clean” (non-infected) computer, download HitmanPro from the below link.
Download HitmanProOfficial Sophos download. Free scan, free 30-day trial to remove threats. - Insert your USB flash drive into your computer and follow the instructions from the below video:
- After you have create the HitmanPro Kickstart USB flash drive, you can insert this USB drive into the infected machine and start your computer.
- Once the computer starts, repeatedly tap the F11 key (on some machines its F10 or F2),which should bring up the Boot Menu, from there you can select to boot from your USB.
Next,you’ll need to perform a system scan with HitmanPro as see in the below video:
- After HitmanPro Kickstart has completed its task,you should be able to boot in Windows normal mode,from there you’ll need to perform a system scan (as seen on STEP 2) with Malwarebytes Anti-Malware and HitmanPro to remove the malicious files from your machine.
STEP 2: Remove FBI CyberCrime Division (ICSPA) malicious files from your computer
Run a computer scan with Malwarebytes Anti-Malware Free
- You can download Malwarebytes Anti-Malware Free from the below link,then double click on it to install this program.
Download MalwarebytesFree official installer. Your download starts right away. - When the installation begins, keep following the prompts in order to continue with the setup process.
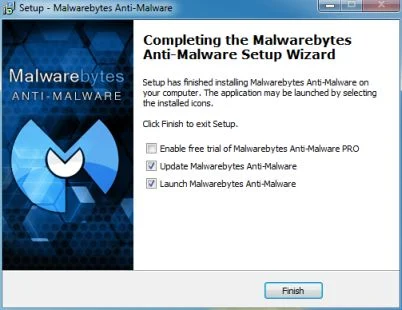
DO NOT make any changes to default settings and when the program has finished installing, make sure you leave both the Update Malwarebytes’ Anti-Malware and Launch Malwarebytes’ Anti-Malware checked,then click on the Finish button.
- On the Scanner tab,select Perform quick scan and then click on the Scan button to start scanning your computer.
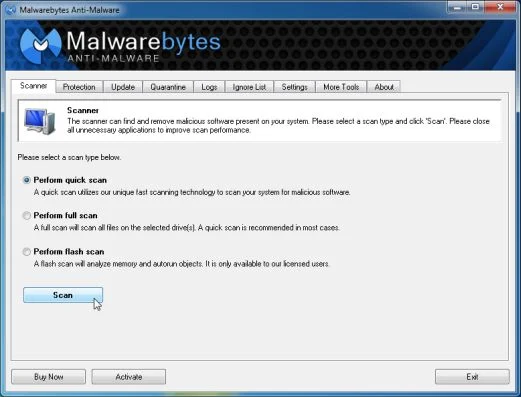
- Malwarebytes’ Anti-Malware will now start scanning your computer for FBI CyberCrime Division (ICSPA) virus as shown below.
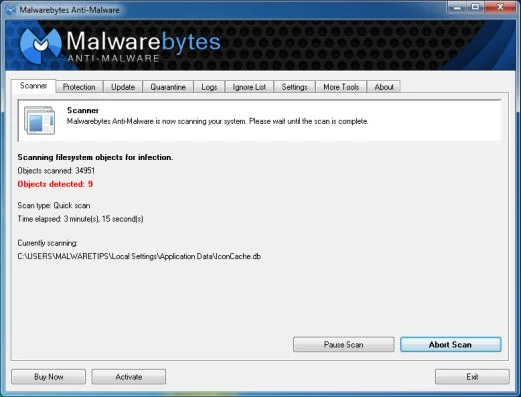
- When the Malwarebytes scan will be completed,click on Show Result.
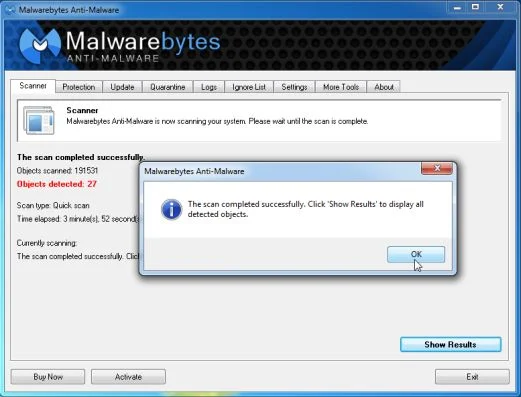
- You will now be presented with a screen showing you the malware infections that Malwarebytes’ Anti-Malware has detected.Please note that the infections found may be different than what is shown in the image.Make sure that everything is Checked (ticked) and click on the Remove Selected button.
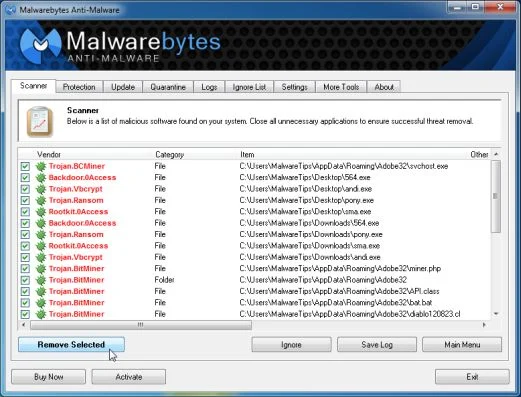
- After your computer will restart in Normal mode, open Malwarebytes Anti-Malware and perform a Full System scan to verify that there are no remaining threats
Run a computer scan with HitmanPro
- Download HitmanPro from the below link,then double click on it to start this program.
Download HitmanProOfficial Sophos download. Free scan, free 30-day trial to remove threats.
IF you are experiencing problems while trying to start HitmanPro, you can use the Force Breach mode.To start HitmanPro in Force Breach mode, hold down the left CTRL-key when you start HitmanPro and all non-essential processes are terminated, including the malware process. (How to start HitmanPro in Force Breach mode – Video) - HitmanPro will start and you’ll need to follow the prompts (by clicking on the Next button) to start a system scan with this program.
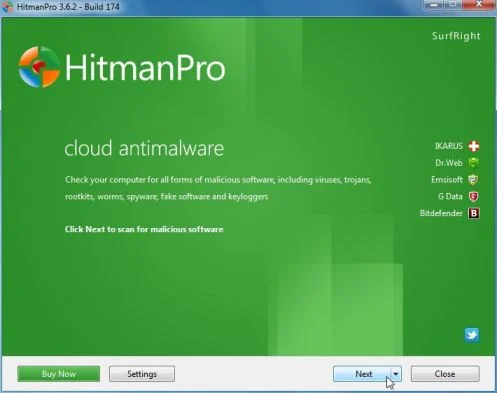
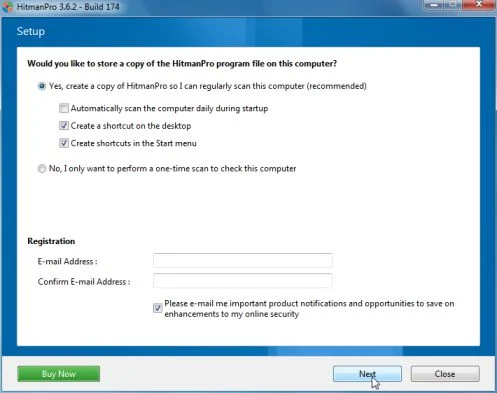
- HitmanPro will start scanning your computer for FBI CyberCrime Division (ICSPA) malicious files as seen in the image below.
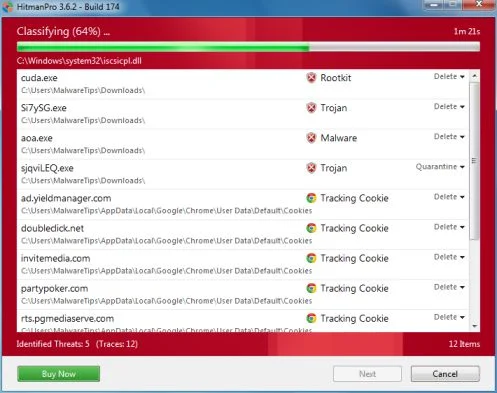
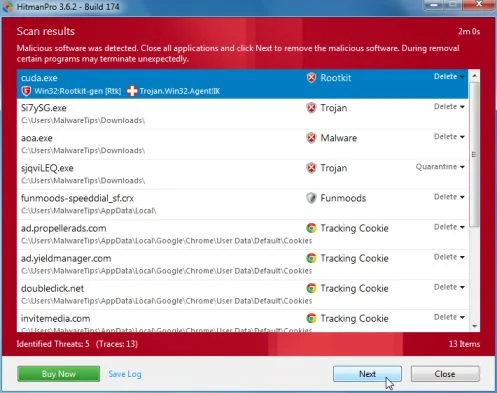
- Once the scan is complete,you’ll see a screen which will display all the infected files that this utility has detected, and you’ll need to click on Next to remove these malicious files.
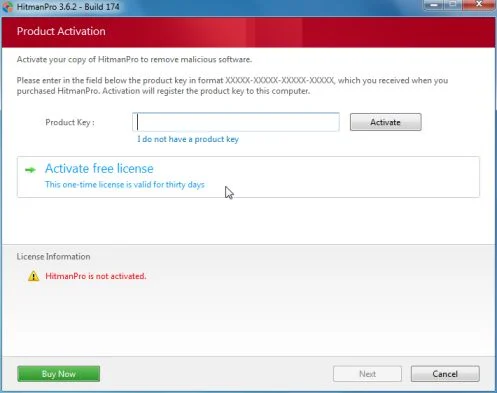
- Click Activate free license to start the free 30 days trial and remove all the malicious files from your computer.

Join the discussion
37 commentsShare your experience or ask a question about this article.
Your progress
Did these steps help?
Let us know how the guide worked for you.
Describe what you see and the step you reached. Keep passwords and other private information out.
Discussion
Thank You SO much, Stelian !!!
I successfully removed that fbi cybercrime virus thanks to your easy to follow instructions!!! I had to use method #2. My husband was certain we’d need to bring our laptop to a repair shop to remove the virus and God only knows what that would have cost. Thank you so much for saving us money!
Hi Stelian, infected with AFP icspa. Scanned with mwam but detected NO inflected file!!! Laptop still locked out of normal mode. Pls help!
In reply to Mike
Hello Mike,
Can you please run a scan with the following tools:
STEP 1: Run a scan with RogueKiller
RogueKiller Download Link (This link will automatically download RogueKiller on your computer)
STEP 2: Please perform a scan with HitmanPro as seen on the guide.
If you are having problems starting this program please use the ForceBreach mode as described in the guide.
STEP 3: Run a scan with ESET Online Scanner:
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
Waiting for your reply to tell me how everything is running!
Good luck…
Incredibly thorough and easy to understand instructions. Thank you. I’ve passed this on to my friends on Facebook and others.
I am so grateful for your website and help.i was scred for a little while.will pass this on.thanks so much.
Very good and concise write up! It’s a link I keep handy so I can forward to others who have gotten bitten.
Do we have to use those programs you suggested or is a Norton 360 scan enough?
In reply to Amy
Hello Amy,
Norton 360 has a good antivirus engine, however if it did not manage to protect your computer from being infected, it might mean that it does not have signatures for this particular infection.
Yes, you can can run a scan with Norton 360, however I do recommend that you also run a scan with Malwarebytes and HitmanPro. Both products are free, and it might result in additional malware being detected.
You rock dude,Thanks
Method 2: Restore Windows to a previous state using System Restore is that I used and I still had all my files and the virus (FBI Cyber Crime) was GONE………THANKS SO MUCH
I am by no means computer savvy & I was able to easily follow the directions to successfully remove the dreaded FBI virus. I can’t even imagine how much it would have cost for me to have “a geek” do it, let alone not have my computer for a few days to say the least.
Thank you for the free downloads and the very easy instructions for us non-techi’s.
In reply to Nolcrest
My wife has got this virus on her PC laptop and our other computer is a MAC. I have tried to start in safe mode with command prompt with no luck and I cannot run the hitman exe file from my mac to create a bootable USB . Can you offer me a solution?
In reply to Andrew
Hello,
These are the removal instructions for Mac OS X users: http://malwaretips.com/blogs/your-browser-has-been-locked-fbi-mac-os-x/