

File Recovery is a malicious program that will display fake alerts, claiming that several hard drive errors and computer issues were detected on your machine.
In reality, none of the reported issues are real, and are only used to scare you into purchasing File Recovery and stealing your personal financial information.
Apart from the bogus alerts and warning,this rogue software has changed your desktop background to a solid black color,has hidden your files and folders and it’s causing browser redirects.
As part of its self-defense mechanism,File Recovery has disabled the Windows system utilities, including Task Manager and Windows Registry and is block you from running certain programs that could lead to its removal.
If your computer is infected with File Recovery virus,then you are seeing this images:
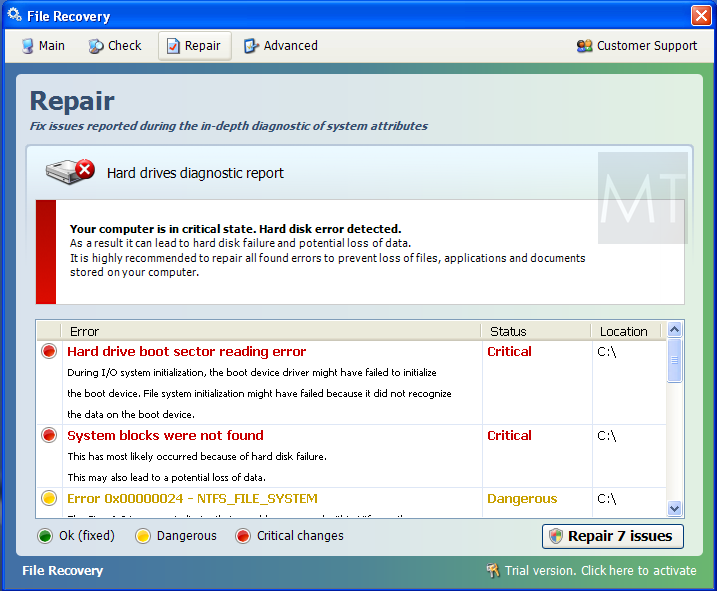
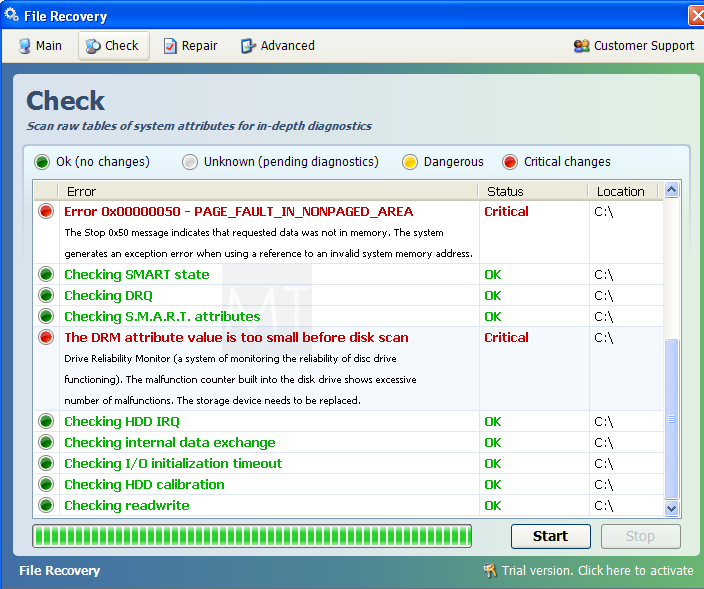
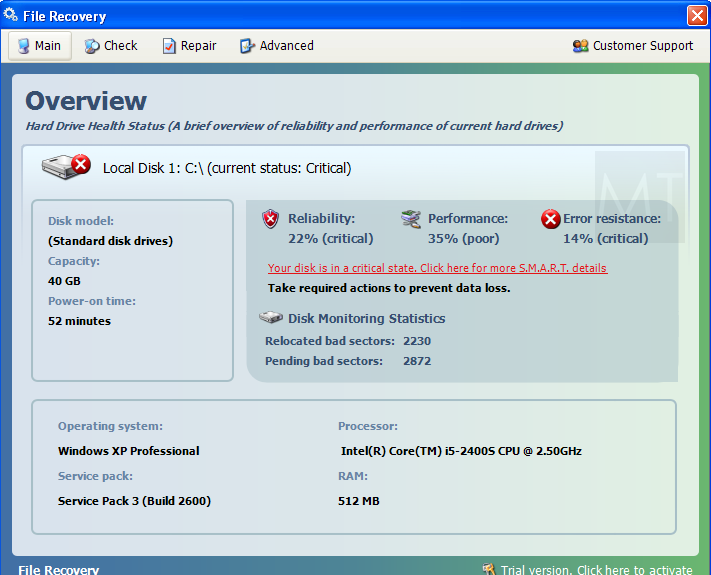
We strongly advise you to follow our File Recovery virus removal guide and ignore any alerts that this malicious software might generate.
Under no circumstance should you buy this rogue security software as this could lead to identity theft,and if you have, you should contact your credit card company and dispute the charge stating that the program is a scam and a computer virus.
Registration codes for File Recovery
As an optional step,you can use the following license key to register File Recovery virus and stop the fake alerts.
File Recovery activation code: 56723489134092874867245789235982
Please keep in mind that entering the above registration code will NOT remove File Recovery from your computer , instead it will just stop the fake alerts so that you’ll be able to complete our removal guide more easily.
File Recovery Removal Instructions
STEP 1 : Start your computer in Safe Mode with Networking
- Remove all floppy disks, CDs, and DVDs from your computer, and then restart your computer.
- Press and hold the F8 key as your computer restarts.Please keep in mind that you need to press the F8 key before the Windows start-up logo appears.
Note: With some computers, if you press and hold a key as the computer is booting you will get a stuck key message. If this occurs, instead of pressing and holding the “F8 key”, tap the “F8 key” continuously until you get the Advanced Boot Options screen. - On the Advanced Boot Options screen, use the arrow keys to highlight Safe Mode with Networking , and then press ENTER.
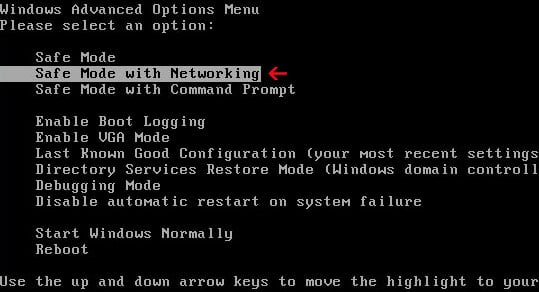
STEP 2: Remove File Recovery malicious proxy server
File Recovery may add a proxy server which prevents the user from accessing the internet,follow the below instructions to remove the proxy.
- Start the Internet Explorer browser and if you are using Internet Explorer 9 ,click on the gear icon
 (Tools for Internet Explorer 8 users) ,then select Internet Options.
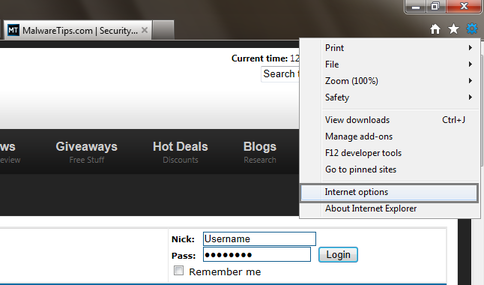
- Go to the tab Connections.At the bottom, click on LAN settings.
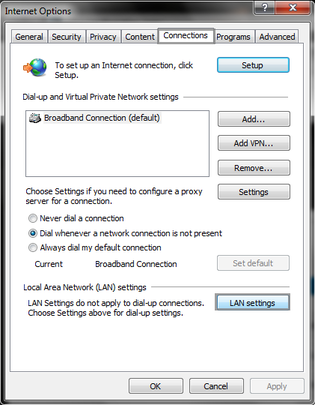
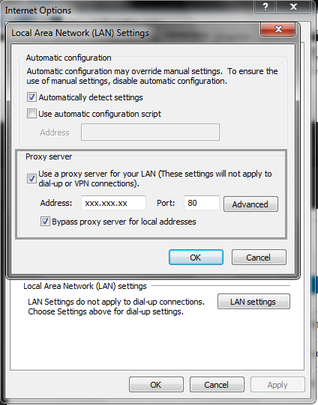
- Uncheck the option Use a proxy server for your LAN. This should remove the malicious proxy server and allow you to use the internet again.
 (Tools for Internet Explorer 8 users) ,then select Internet Options.
If you are a Firefox users, go to Firefox(upper left corner) → Options → Advanced tab → Network → Settings → Select No Proxy
STEP 3: Run RKill to terminate known malware processes associated with File Recovery.
RKill is a program that will attempt to terminate all malicious processes associated with File Recovery virus,so that we will be able to perform the next step without being interrupted by this malicious software.
Because this utility will only stop File Recovery running process, and does not delete any files, after running it you should not reboot your computer as any malware processes that are configured to start automatically will just be started again.
- While your computer is in Safe Mode with Networking ,please download the latest official version of RKill.Please note that we will use a renamed version of RKILL so that File Recovery won’t block this utility from running.
Download RKillYour download starts right away. - Double-click on the iExplore.exe icon in order to automatically attempt to stop any processes associated with File Recovery.

- RKill will now start working in the background, please be patient while the program looks for various malware programs and tries to terminate them.
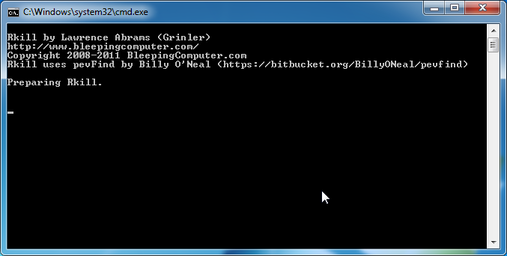
IF you are having problems starting or running RKill, you can download any other renamed versions of RKill from here. - When Rkill has completed its task, it will generate a log. You can then proceed with the rest of the guide.
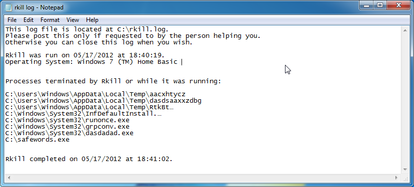

WARNING: Do not reboot your computer after running RKill as the malware process will start again , preventing you from properly performing the next step.
STEP 4: Remove File Recovery malicious files with Malwarebytes Anti-Malware FREE
- Download the latest official version of Malwarebytes Anti-Malware FREE.
Download MalwarebytesFree official installer. Your download starts right away. - Start the Malwarebytes’ Anti-Malware installation process by double clicking on mbam-setup file.

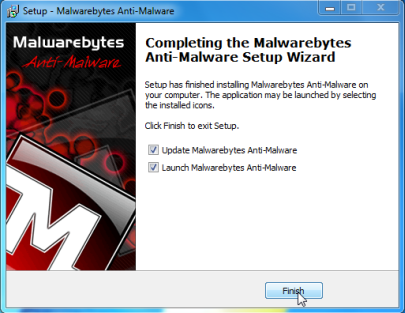
- When the installation begins, keep following the prompts in order to continue with the setup process. Do not make any changes to default settings and when the program has finished installing, make sure you leave both the Update Malwarebytes’ Anti-Malware and Launch Malwarebytes’ Anti-Malware checked. Then click on the Finish button. If Malwarebytes’ prompts you to reboot, please do not do so.
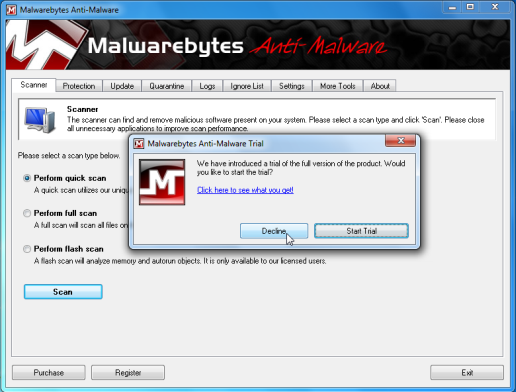
- Malwarebytes Anti-Malware will now start and you’ll be prompted to start a trial period , please select ‘Decline‘ as we just want to use the on-demand scanner.
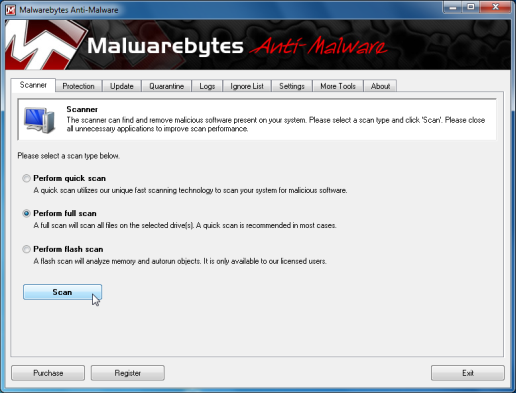
- On the Scanner tab,select Perform full scan and then click on the Scanbutton to start scanning your computer.
- Malwarebytes’ Anti-Malware will now start scanning your computer for File Recovery malicious files as shown below.
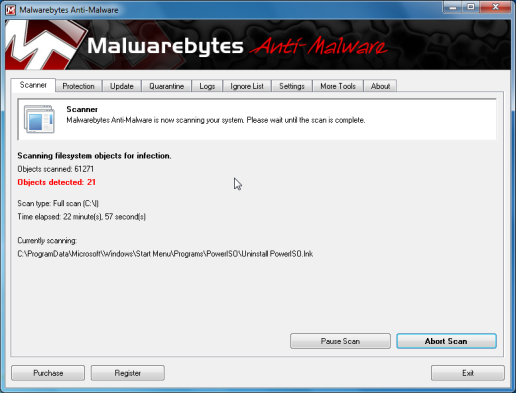
- When the scan is finished a message box will appear, click OK to continue.
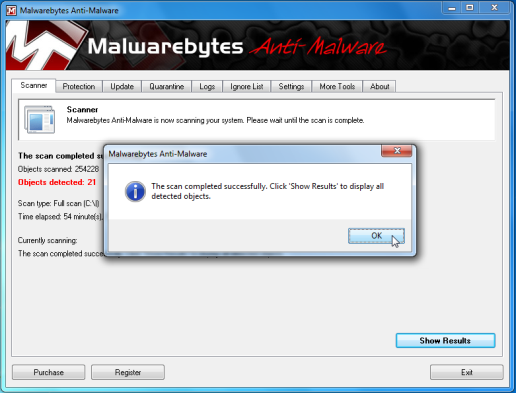
- You will now be presented with a screen showing you the malware infections that Malwarebytes’ Anti-Malware has detected.Please note that the infections found may be different than what is shown in the image.Make sure that everything is Checked (ticked) and click on the Remove Selected button.
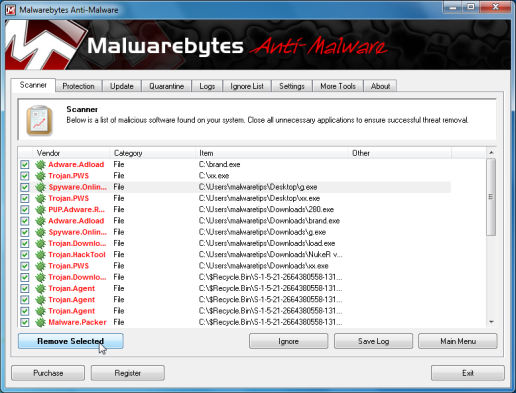
- Malwarebytes’ Anti-Malware will now start removing the malicious files.After completing this task it will display a message stating that it needs to reboot,please allow this request and then let your PC boot in Normal mode.

STEP 5: Double check your system for any left over infections with HitmanPro
- This step can be performed in Normal Mode ,so please download the latest official version of HitmanPro.
Download HitmanProOfficial Sophos download. Free scan, free 30-day trial to remove threats. - Double click on the previously downloaded fileto start the HitmanPro installation.

IF you are experiencing problems while trying to starting HitmanPro, you can use the “Force Breach” mode.To start this program in Force Breach mode, hold down the left CTRL-key when you start HitmanPro and all non-essential processes are terminated, including the malware process. (How to start HitmanPro in Force Breach mode – Video) - Click on Next to install HitmanPro on your system.
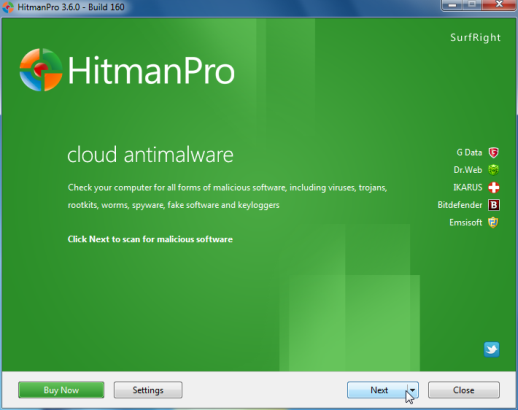
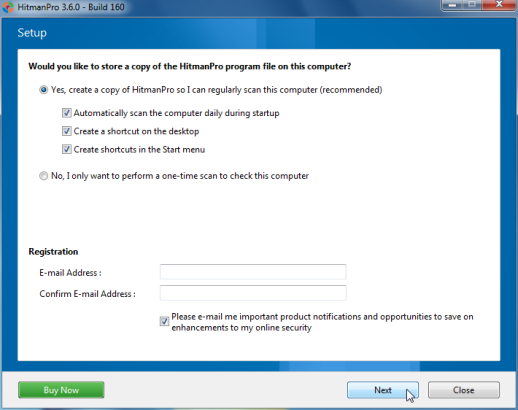
- The setup screen is displayed, from which you can decide whether you wish to install HitmanPro on your machine or just perform a one-time scan, select a option then click on Next to start a system scan.
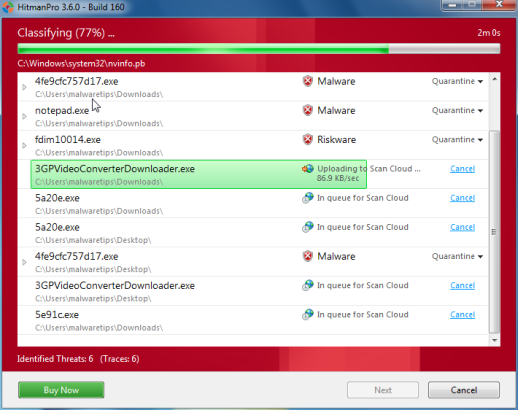
- HitmanPro will start scanning your system for malicious files as seen in the image below.
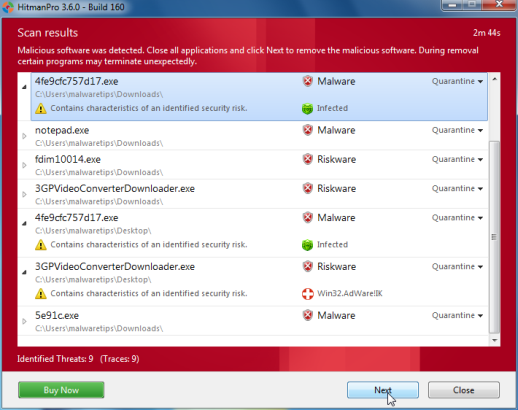
- Once the scan is complete,you’ll see a screen which will display all the malicious files that the program has found.Click on Next to remove this malicious files.
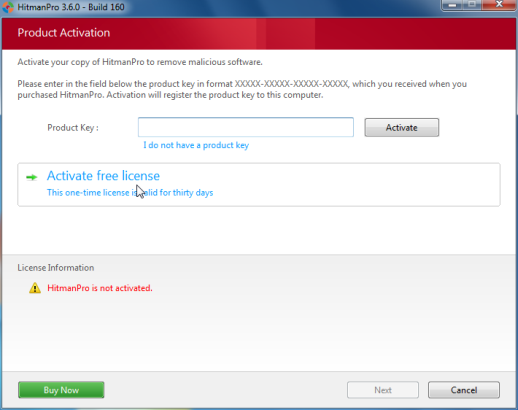
- Click Activate free license to start the free 30 days trial and remove the malicious files.
- HitmanPro will now start removing the infected objects.If this program will ask you to restart your computer,please allow this request.

STEP 6 : Restore your shortcuts and remove any left over malicious registry keys
File Recovery has moved your shortcuts files in the Temporary Internet folder and added some malicious registry keys to your Windows installation , to restore your files we will need to perform a scan with RogueKiller.
- Please download the latest official version of RogueKiller.
Download RogueKillerOpens the download page in a new tab. - Double click on RogueKiller.exe to start this utility and then wait for the Prescan to complete.This should take only a few seconds and then you can click the Start button to perform a system scan.
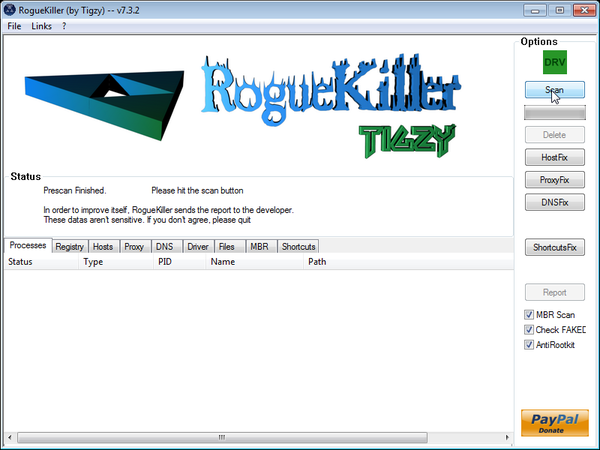
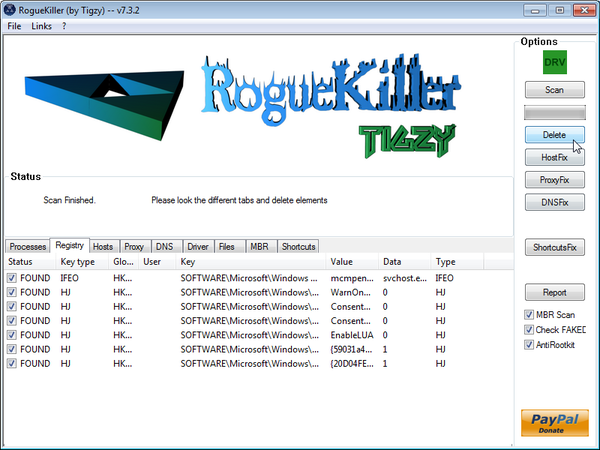
- After the scan has completed, press the Delete button to remove any malicious registry keys.
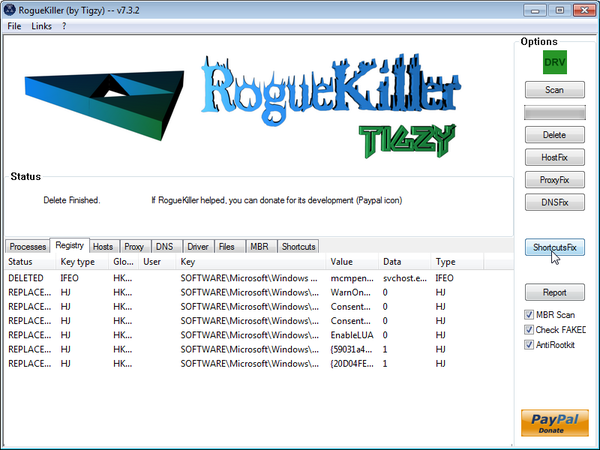
- Next we will need to restore your shortcuts, so click on the ShortcutsFix button and allow the program to run.
STEP 7: Unhide your files and folders
File Recovery modifies your file system in such a way that all files and folders become hidden, to restore the default settings , you’ll need to run the below program.
- Download the Unhide utility, to unhide your files and folders.
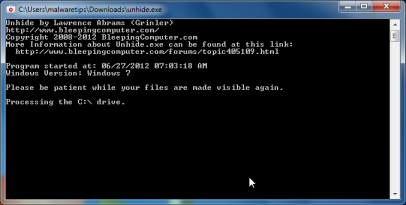
Download UnhideYour download starts right away. - Double-click on the Unhide.exe icon on your desktop and allow the program to run.The whole process should not take more than 10 minutes to complete,and at the end this utility will generate a report.
STEP 8: Get your desktop look back!
File Recovery changes your desktop background to a solid black color,to change it back to default one follow the below instruction.
- Windows XP : Click on the Start button and then select Control Panel. When the Control Panel opens, please click on the Display icon. From this screen you can now change your Theme and desktop background.
- Windows 7 and Vista : Click on the Start button and then select Control Panel. When the Control Panel opens, please click on the Appearance and Personalization category. Then select Change the Theme or Change Desktop Background to revert back to your original Theme and colors.

Join the discussion
468 commentsShare your experience or ask a question about this article.
Your progress
Did these steps help?
Let us know how the guide worked for you.
Describe what you see and the step you reached. Keep passwords and other private information out.
Discussion
All I can say is a BIG: THANK YOU!!
You saved my laptop!
Actually, it is the File Recovery Virus. They disabled my adaptor for my LAN. I now just undisabled it. Should I reinstall Malwarebytes?
In reply to Zvjezdan Veselinovic
I am running in normal mode now, where the kill worked and I reinstalled Malwarebytes. I updated it and it is scanning now. Is it safe for me to scan in normal mode now that I have internet? Or no???
In reply to Zvjezdan Veselinovic
Hello,
Yes,you also run this scan while in Normal mode.
Good lucK!:D
Worked like a charm! Thanks so much!
In reply to shots
Possibly a new twist, Vista Machine SP2 infected 9/9/2012 … in Safe Mode with Networking there was no proxy setting … however … there was something running in the background changing any attempts to connect to the internet specifically something was changing the TCPIP IP value … regardless of the addresses set, the moment the Network dialog is closed the IP address reverts to 192.168.210.152 … so … I went in to Regedit and searched for this IP address and removed all Gateway, and other related keys for this IP address … I then unistalled the Wireless Driver (device manager) then allowed the manager to reinstall the device drivers … this appears to have broken the hold on whatever was taking over the TCPIP IP settings … I am currently running Malwarebytes
Note: I had removed this drive and installed as a slave drive on another machine … it took over 5 hours to scan 190GB on an Esata port using Malwarebytes but this procedure didn’t touch this virus??? It only found 4 unrelated issues … now in safe mode after 30 minutes Malwarebytes has found another 26 issues and still running.
I suspect Malwarebytes may have issues with “MS” file Security when a drive is mounted as a slave … most of the vista files have permissions which won’t match the host machine.
Thanks for the help, I got everything back to usual. But then 3 hours later, the same thing comes back up even after I quarantined it. This time, the process name was different but it was under the same description in task manager “AAW.” Did I do something wrong, or is this forever reoccurring?
In reply to Mike
Hello Mike,
Can you please run a scan with Combofix, ESET online scanner and post the logs here so that I can get an idea on what’s going on:
STEP 1 : Run a scan with Combofix
Download ComboFix from one of the following locations:
COMBOFIX DOWNLOAD LINK #1 (This link will automatically download Combofix on your computer)
COMBOFIX DOWNLOAD LINK #2 (This link will automatically download Combofix on your computer)
VERY IMPORTANT !!! Save as Combo-Fix.exe during the download.ComboFix must be renamed before you download to your Desktop
Notes:
STEP 2: Run a scan with ESET Online Scanner:
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
NEXT,please run a scan with HitmanPro and RogueKiller as seen on the guide.
Waiting for your reply to tell me if your machine is ok and the logs from this utilities.
Thank-you very much for this guide. I’m a novice and your instructions were dummy proof.
Too little too late. I purchased this software and my computer crashed shortly thereafter. I will contact my credit card provider on this information. Much appreciated
In reply to Sherrie
Hello Sherrie,
You should contact your bank as soon as possible!Also you should do a scan with the above utilities because this virus is still on your computer even after you have purchased the rogue antivirus.
Why is it that when I ran RKill, it didn’t actually find anything to terminate. I clearly had the file recovery virus.
In reply to Mike
Hello Mike,
Please go ahead with the scan recommended in the guide,then reply back and tell me how everything is working.
I got this thing on my work laptop while working at home over the weekend. I can’t get the hitmanpro free 30 day license because it detected my computer as a commercial domain. Do you recommned an alternative?
In reply to Jason
Hello Jason,
We can manually remove this files however let’s see if we can get rid of some of them using the below software:
1.Run a scan with Kaspersky Virus Removal Tool
Click here to download the Kaspersky Virus Removal Tool.
2.Run a scan with Eset Online Scanner.
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
NEXT,please re-run a scan with HitmanPro and post the log or a screenshot here and I’ll give you instructions on how to remove the left over files.
Good luck!
I’m getting and error when I try to run Malwarebytes in both the safe mode and normal modes with XP. I have run as administrator, but get gui “setup” “Access is denied” click OK and then get “ERROR” gui “setup was not completed…..”Please correct the problem and run Setup again” . I’ve tried several times as different Admins, Safe mode, etc. can’t get by this Access denied… ?
In reply to Oly
Hello Oly,
STEP 1: Run a scan with Malwarebytes Anti-Malware in Chameleon Mode in Norman mode:
STEP 2: Run a scan with RogueKiller
RogueKiller Download Link (This link will automatically download RogueKiller on your computer)
STEP 3 Please perform a scan with HitmanPro as seen on the guide.
If you are having problems starting this program please use the ForceBreach mode as described in the guide.
STEP 4: Run a scan with ESET Online Scanner:
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
Waiting for your reply to tell me how everything is running!
Good luck…
I got all the way to the hitmanpro part but the program says that it is not activated. I can’t find the 30 day free trail and it only gives me the option of purchasing. Did they change that recently? Now they want $19.95 for 1 year. Is there another program that I can usej for free?
In reply to Aaron Z
Hello Aaron Z,
We can manually remove this files however let’s see if we can get rid of some of them using the below software:
1.Run a scan with Kaspersky Virus Removal Tool
Click here to download the Kaspersky Virus Removal Tool.
2.Run a scan with Eset Online Scanner.
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
NEXT,please re-run a scan with HitmanPro and post the log or a screenshot here and I’ll give you instructions on how to remove the left over files.
Good luck!
Thank you very much for your complete step by step instruction to restore my computer to the normal state. I will try to find a way to help others FREE just like you are doing. God Bless You!
In reply to Jae
OMG YOU ARE FANTASTIC n A GODSEND….TYVM for this!!!!! WOW U ARE GREAT!!!
Excellent article. Worked a treat. Easy to follow.
Great article, thanks!!!!!!!!
Thanks, this is a great thread. I think I got rid of the virus, but it seems to have disabled my internet. I have a TP Link wireless USB, and it no longer even acknowedges it is attached (when I plug/unplug the USB connection, the activity light on the unit does turn on). Can this virus “destroy” hardware? Or is there just some setting I need to reconfigure?
Thanks!
In reply to ScottR
Actually, got it. Virus had disabled it, just a matter of going into device manager. Phew! Thanks again, very well written tutorial!
I’ve removed the Windows Recovery virus from quite a few computers using the ‘old and true malware tools’. But, your procedure and very good description of how to do it is one of the best I’ve seen. I found your site by ‘googling’ the virus, and want to say that it’s ‘one hell of a good site’. everything is readable, usable and very clear. The virus is gone and thanks to you it was real easy,, thanks again ,
Bob Smith
Robert Smith Consulting
Fort Bragg, California
I followed the instructions and File reovery is still on my computer…
My catalyst control center keeps popping up with errors.
In reply to sanddunesaddict
Hello sanddunesaddict,
Can you please run a scan with Combofix and ESET online scanner and post the logs here so that I can get an idea on what’s going on :
STEP 1 : Run a scan with Combofix
Download ComboFix from one of the following locations:
COMBOFIX DOWNLOAD LINK #1 (This link will automatically download Combofix on your computer)
COMBOFIX DOWNLOAD LINK #2 (This link will automatically download Combofix on your computer)
VERY IMPORTANT !!! Save as Combo-Fix.exe during the download.ComboFix must be renamed before you download to your Desktop
Notes:
STEP 2: Run a scan with ESET Online Scanner:
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
Waiting for your reply to tell me if your machine is ok and the logs from this utilities.
In reply to Stelian Pilici
Hello,
Thanks for your tips.
I had the smae problem and here’s the log:
((((((((((((((((((((((((((((((((((((((( Other Deletions )))))))))))))))))))))))))))))))))))))))))))))))))
.
.
c:\programdata\iHbG8O6dS4kC1u
c:\programdata\iHbG8O6dS4kC1u.exe
c:\programdata\KRvLBPIruJNA.exe
c:\swtools\APPS\CSBED\CSBE\ACTIVATION_104\_desktop.ini
c:\swtools\APPS\CSBED\CSBE\ACTIVATION_104\BIN\_desktop.ini
c:\windows\SysWow64\jucheck.exe
c:\windows\SysWow64\jusched.exe
Q:\AUTORUN.INF
In reply to SMuse
Hello SMuse,
How is your machine running right now?
Can you please run a scan with Kaspersky Virus Removal Tool:
Click here to download the Kaspersky Virus Removal Tool.
This virus seems to have disabled all internet on the infected computer. I am unable to get any connection in explorer, either in safe mode w/ networking or in regular mode. Also checked to remove any proxy, but none was showing as being used in explorer. I’ve used the registration key to get it out of the way, but still have no internet for downloading the removal programs, any recommendations?
using Win 7, Professional
In reply to Nathan
Hello Nathan,
What antivirus/firewall do you have installed on this machine? Can you please try to disable the firewall and then connect to the Internet.
Not thing to say only a Big Thank You to You!!!!
In reply to Tida
After the malwarebytes scan.. it doesn’t prompt me to reboot. A notpad summary pops up If I restart the CPU on my own the virus is still present
In reply to Tida
Hey, it worked I believe. Is there a way to double check wether it was fully removed ?
I think it’s great you put this info on the web for people to use thank you.
In reply to Nathan
Hello Nathan,
HitmanPro and Malwarebytes should have removed this rogue antivirus,however for your peace of mind I would suggest that you perform a scan with the following utilities:
1.Run a scan with Kaspersky Virus Removal Tool
Click here to download the Kaspersky Virus Removal Tool.
2.Run a scan with Eset Online Scanner.
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
I am going through the steps detailed above. Question is, if I bought into the scam how can I minimize damage (in addition to completing the steps above). Is there anything I can do about the time in which this was active on my computer becuase I was not smart enough to avoid it?
In reply to PackerFan
Hello PackerFan,
This cyber criminals might have collected your personal data,when you have paid for this fake produc and they might try in the future to use your data.The best thing to do here is to inform your bank,that you are the victim of a cyber attack,they should know what’s the next step!
As an additional step I suggest that you do a scan with ESET ONLINE SCANNER
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
Stay safe!
Wow,, I was just about to rip all the hair outta my head, kick my boyfriend and have an anxiety attack, until I found you!!! You are friggin GENIUS.. Thank you and my boyfriend thanks YOU! Problem fixed…