

A contract shared through Dropbox can seem entirely ordinary, even when the sender’s name is unfamiliar or the filename offers little context.
The message involving “Explicit-Contract.pdf” uses that familiar workflow, but the journey behind its viewing button tells a different story.
Overview
The unexpected Explicit-Contract.pdf invitation
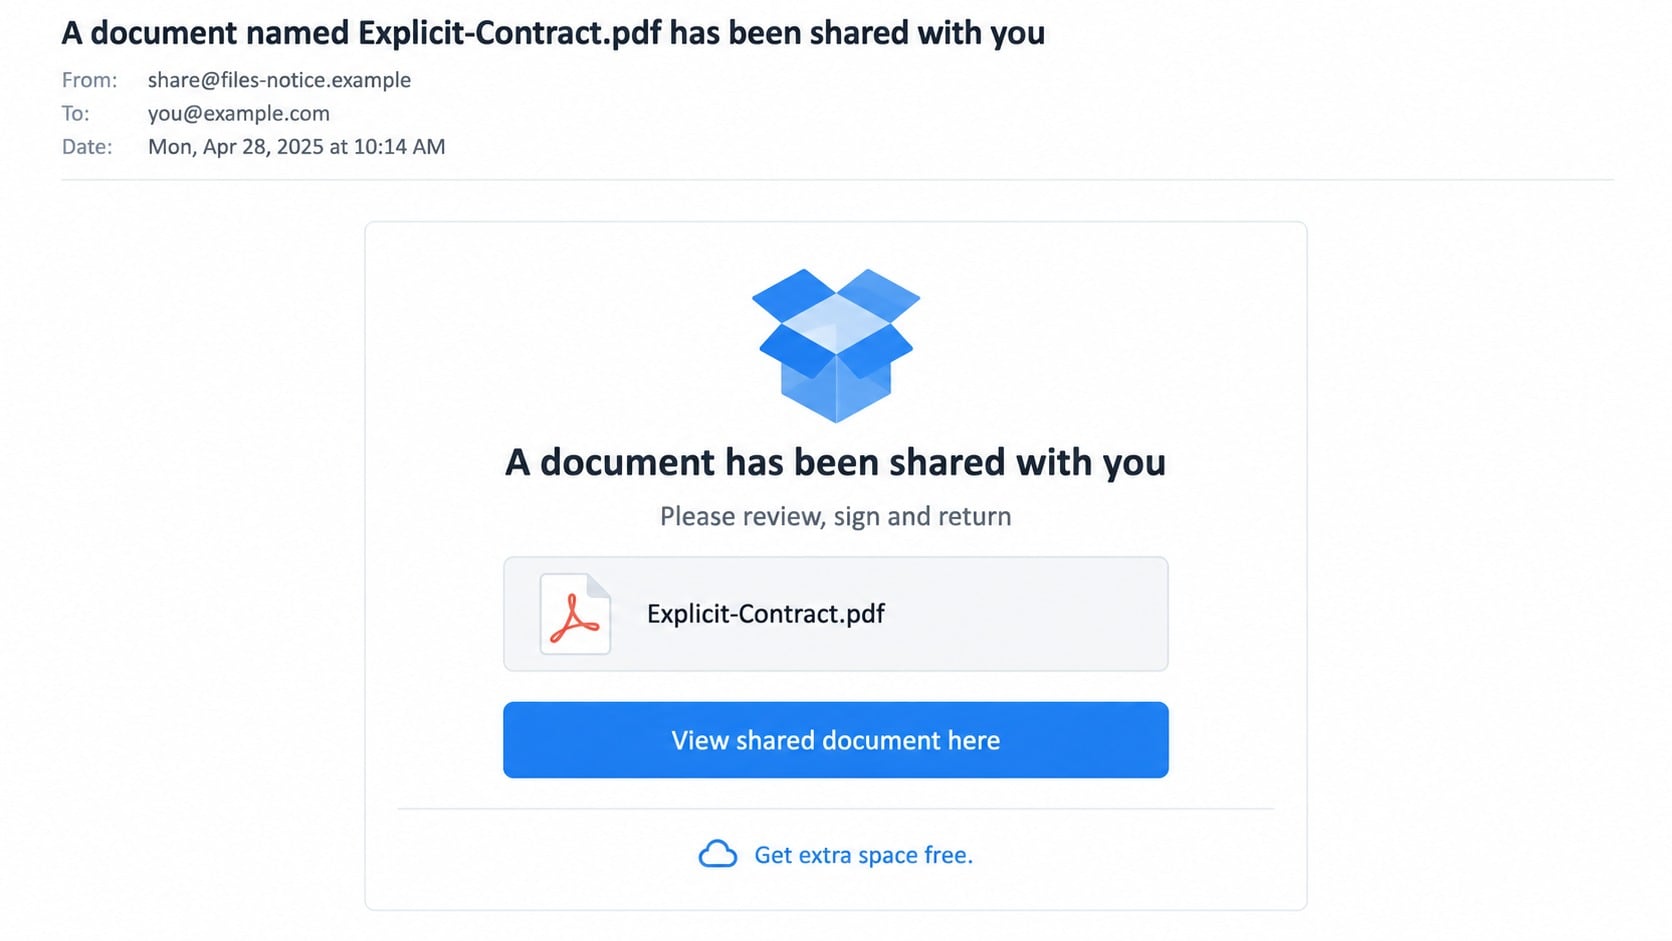
The email announces that a document named “Explicit-Contract.pdf” has been shared with the recipient.
Its subject may contain the awkward phrase “has been shared you,” an early sign that the template was assembled carelessly.
A short comment asks the recipient to review, sign, and return the file.
The central button reads “View shared document here,” while surrounding Dropbox-style language makes the invitation resemble a normal file notification.
No contract party, project, organization, deadline, or sender relationship explains why the recipient should expect this agreement.
The concealed credential request
The viewing button does not reveal a contract inside a recognizable Dropbox account.
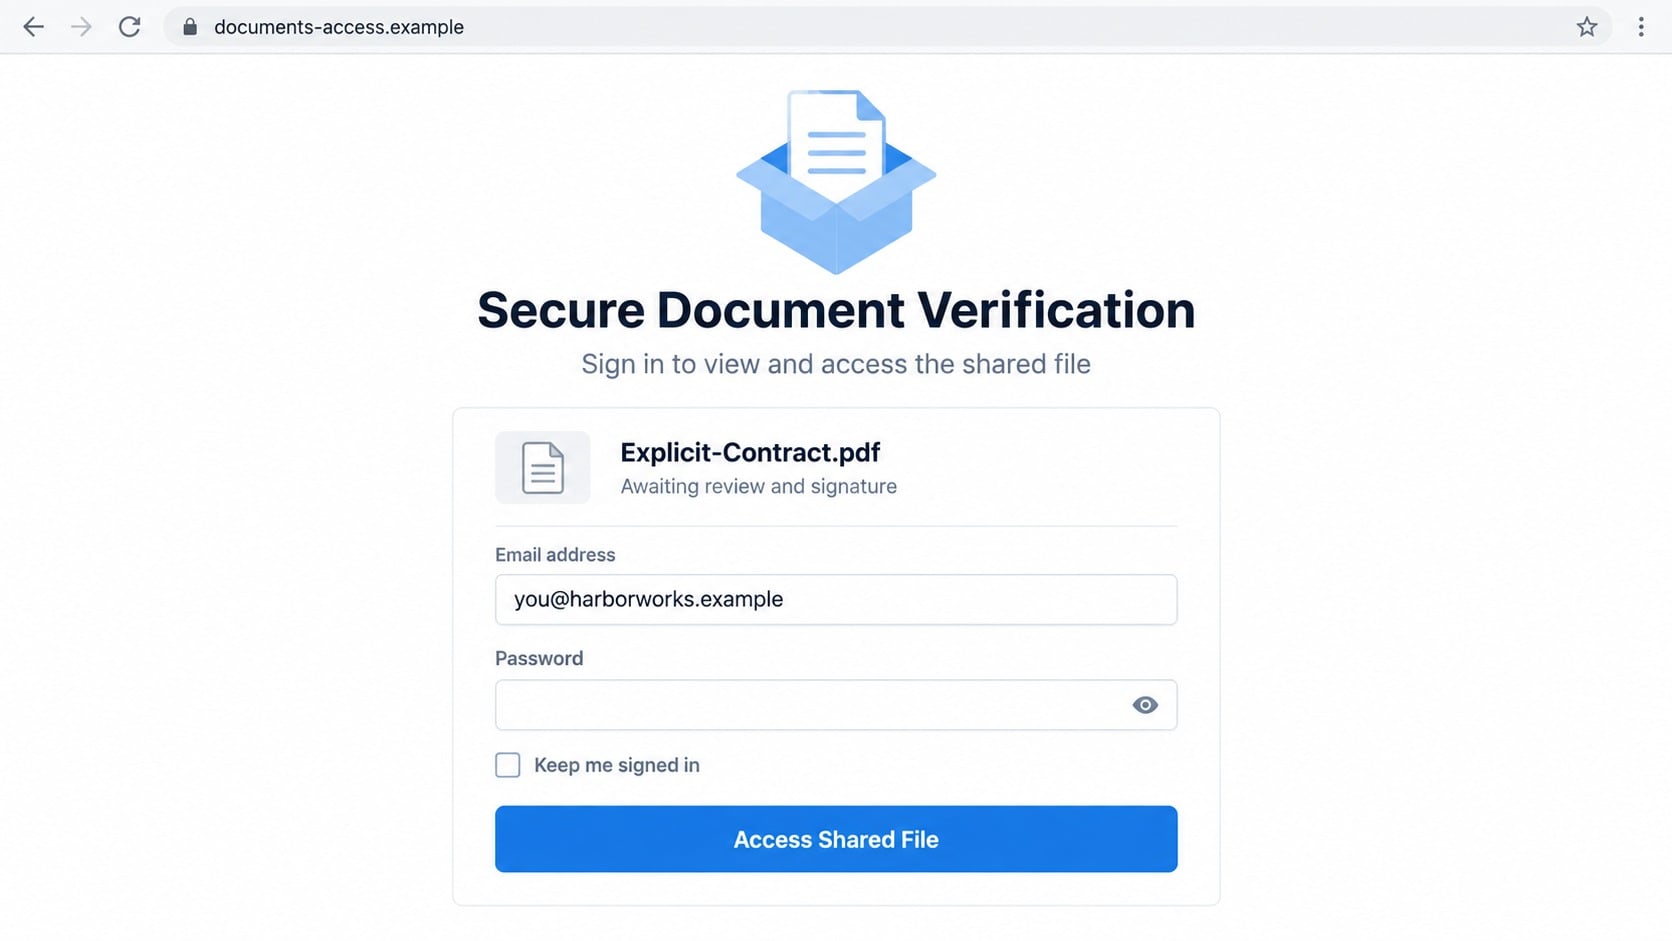
It opens an unrelated domain displaying a secured document verification form.
The page identifies the file, shows the visitor’s email address, and requests an email password to continue.
That request is not a harmless access check.
It places private mailbox credentials into a website that is neither Dropbox nor the recipient’s email provider.
How to recognize the complete pattern
Each individual element looks plausible: a PDF, a review request, a sharing button, and a protected-file screen.
The deception becomes clear when those elements are connected.
Warning signs include:
- A generic contract with no recognizable parties or purpose.
- An unrequested signature task sent outside an existing discussion.
- Unnatural wording in the subject or message.
- A viewing link that opens a non-Dropbox domain.
- A second brand theme introduced after the click.
- A form requesting the password for an unrelated email account.
Dropbox offers legitimate sharing features. This campaign merely imitates them to move recipients toward a credential collection page.
How the Explicit-Contract.pdf Dropbox Email Scam Works
Step 1: A vague legal document appears in the inbox
Contracts naturally create concern because ignoring a genuine one can delay work, payment, housing, employment, or a business relationship.
The filename is broad enough to suit almost any recipient.
“Explicit” sounds formal, while “Contract” supplies legal weight without revealing facts that could be checked.
The attacker avoids naming a customer, vendor, property, employee, or transaction.
That absence is useful to the sender because one template can be distributed across unrelated industries.
The recipient often supplies the missing story, wondering whether a colleague, client, or service provider sent it unexpectedly.
Step 2: The comment creates a simple assignment
“Please review, sign and return” compresses the supposed task into three familiar actions.
The language does not explain what is being accepted, who needs the signature, or when the agreement was discussed.
Instead, it encourages opening first and asking questions later.
A genuine contract request usually arrives after negotiation, onboarding, purchasing, renewal, or another recognizable conversation.
It should identify the responsible person and provide enough context to verify the request without opening an unknown link.
The fake invitation offers none of that because the file itself is only bait.
Step 3: Dropbox styling carries the recipient past uncertainty
File-sharing notifications use clean layouts and large action buttons, making them easy to imitate.
The email may include familiar phrases about shared documents, extra storage, or account access.
Those details create atmosphere rather than proof.
The visible button text says what the recipient wants to do, but it does not show who controls the destination.
Attackers depend on the brand impression remaining stronger than the actual web address.
Even a correctly spelled logo or polished template can be copied into an ordinary phishing message.
Step 4: The journey leaves Dropbox for a false verification page
The observed link led to an unrelated website rather than a Dropbox file preview.
Its page presented the contract as protected and asked the visitor to verify an account before viewing it.
This brand switch is important.
A legitimate Dropbox share may request a Dropbox sign-in, depending on permissions, but that happens on Dropbox-controlled infrastructure.
It does not require handing an email password directly to a generic document portal.
The unexpected destination separates the page’s appearance from the organization that supposedly authorized access.
Step 5: Personalization makes the password field feel legitimate
The fake page can read an email address from the link and place it inside the form automatically.
Seeing the correct address may convince the visitor that the service recognized them.
In reality, the attacker already had that address because it was needed to deliver the phishing message.
No secret account lookup is required.
The page may add lock icons, encrypted-file claims, or confidentiality labels around the form.
These visual assurances do not change where the password goes after submission.
Step 6: The operator tests the captured credentials
Once submitted, the email address and password can be tested against common mail and cloud services.
Automated attempts may begin quickly, or the data may be reviewed and used selectively.
If the password was reused, unrelated accounts can also become targets.
Successful mailbox access reveals contacts, documents, reset messages, billing records, and future sharing invitations.
The criminal can send another fake contract from a real account, giving the next lure a familiar sender and authentic signature.
That chain turns one vague invitation into a wider business email compromise incident.
Why a Shared Contract Creates Unusual Pressure
Legal language makes delay feel risky
People are often reluctant to ignore documents labeled agreement, contract, settlement, compliance, or signature required.
They may fear missing a deadline before understanding what the document concerns.
The attacker uses that hesitation as leverage.
A legitimate agreement should become easier to verify when questioned, not more mysterious.
Remote work normalized unexpected sharing notices
Employees now receive files from clients, temporary teams, external advisers, and collaboration platforms throughout the day.
An unfamiliar notification no longer looks automatically impossible.
That convenience creates a verification gap.
Recipients should connect the file to a known conversation before opening it, particularly when the document requests a signature.
The filename sounds specific without containing specifics
“Explicit-Contract.pdf” feels more deliberate than “document.pdf,” yet it identifies nothing useful.
There is no counterparty, project, date, revision, or agreement type.
Meaningful filenames help real collaborators distinguish documents.
Generic legal phrasing helps attackers invite curiosity while avoiding details that would expose the mismatch.
What a Stolen Cloud or Email Account Can Expose
Private files and active negotiations
A mailbox can contain shared-link notifications, draft agreements, identification records, invoices, and negotiation history.
Those materials reveal who is expecting documents and which subjects already feel credible.
An intruder can reuse a genuine filename in a later message or replace a clean link with a malicious one.
The resulting email may be much harder for colleagues to identify as fraudulent.
Password resets and connected services
Email often acts as the recovery channel for cloud storage, payroll, shopping, social, and workplace accounts.
Control of the inbox may allow an attacker to request resets and delete the resulting warnings.
Connected applications can extend access even after a password change.
That is why recovery must include sessions, app permissions, forwarding rules, and recovery methods.
Impersonation through genuine shared folders
If the victim uses Dropbox or another cloud platform, account access may expose existing shared folders and collaborators.
The attacker could add files, create public links, or invite new recipients using a trusted identity.
Contacts may assume the new invitation belongs to an ongoing project.
Quickly warning collaborators limits that secondary risk.
Sender, Filename, Dropbox, and Login Verification Checks
Identify the person who supposedly shared the file
Look for a real name, recognizable address, organization, and explanation tied to recent activity.
Do not accept a display name as proof because senders can choose any label.
Contact the person through a saved address, established chat, or known telephone number.
Ask them to state the filename and purpose without quoting details from the suspicious email.
An attacker reading your reply should not receive clues that help refine the story.
Test whether the filename matches a real conversation
Search prior mail and project records for the agreement, parties, or expected signature request.
A legitimate contract rarely appears without earlier discussion.
Check whether the naming pattern matches files normally exchanged by that sender.
A strangely generic filename, unexpected punctuation, or unexplained confidentiality label should increase caution.
Never sign a document until its origin and complete contents are independently established.
Use Dropbox through a known route
Open Dropbox using your normal bookmark or manually entered address.
Review notifications, shared items, and recent activity from inside the authenticated account.
If the invitation is genuine, you should find corresponding evidence there or obtain confirmation from the sender.
Official login pages keep the registered domain visible throughout authentication.
A generic “secure document” address is not transformed into Dropbox merely because the email mentioned Dropbox first.
Reject any unrelated mailbox password request
A file-viewing website should never ask you to surrender the password for a different service.
If access uses your organization’s identity provider, the browser should redirect to that provider’s known domain.
Stop when the domain, branding, or requested credential changes unexpectedly.
Send the link to organizational security for isolated analysis rather than experimenting on a work device.
The safest verification happens outside the path supplied by the suspicious message.
Safe Ways to Receive and Review a Contract
Ask the sender to confirm the invitation through the communication channel used during negotiations.
For business documents, request an envelope identifier, counterparty name, and expected signers.
Open the file platform independently and compare those details before downloading anything.
Read the full agreement, including attachments and signature blocks, before approving it.
Organizations can require contracts to pass through legal, purchasing, or document-management workflows rather than individual inbox decisions.
Security teams should block newly registered lookalike domains and monitor unusual mailbox rules following reported clicks.
These controls preserve useful sharing features without treating every unexpected button as trustworthy.
Teams can also establish one approved method for external signatures and document how recipients should confirm unfamiliar invitations.
A short verification checklist gives busy employees a practical alternative to guessing whether a polished notification deserves trust.
When the sender cannot explain the agreement through a separate channel, the review should stop until ownership is established.
What to Do If You Fell for the Explicit-Contract.pdf Dropbox Scam
- Change the submitted password immediately. Visit the genuine email provider directly from a trusted device and create a new unique password.
- Protect every reused account. If that password appeared anywhere else, change those accounts separately. Never reuse the replacement.
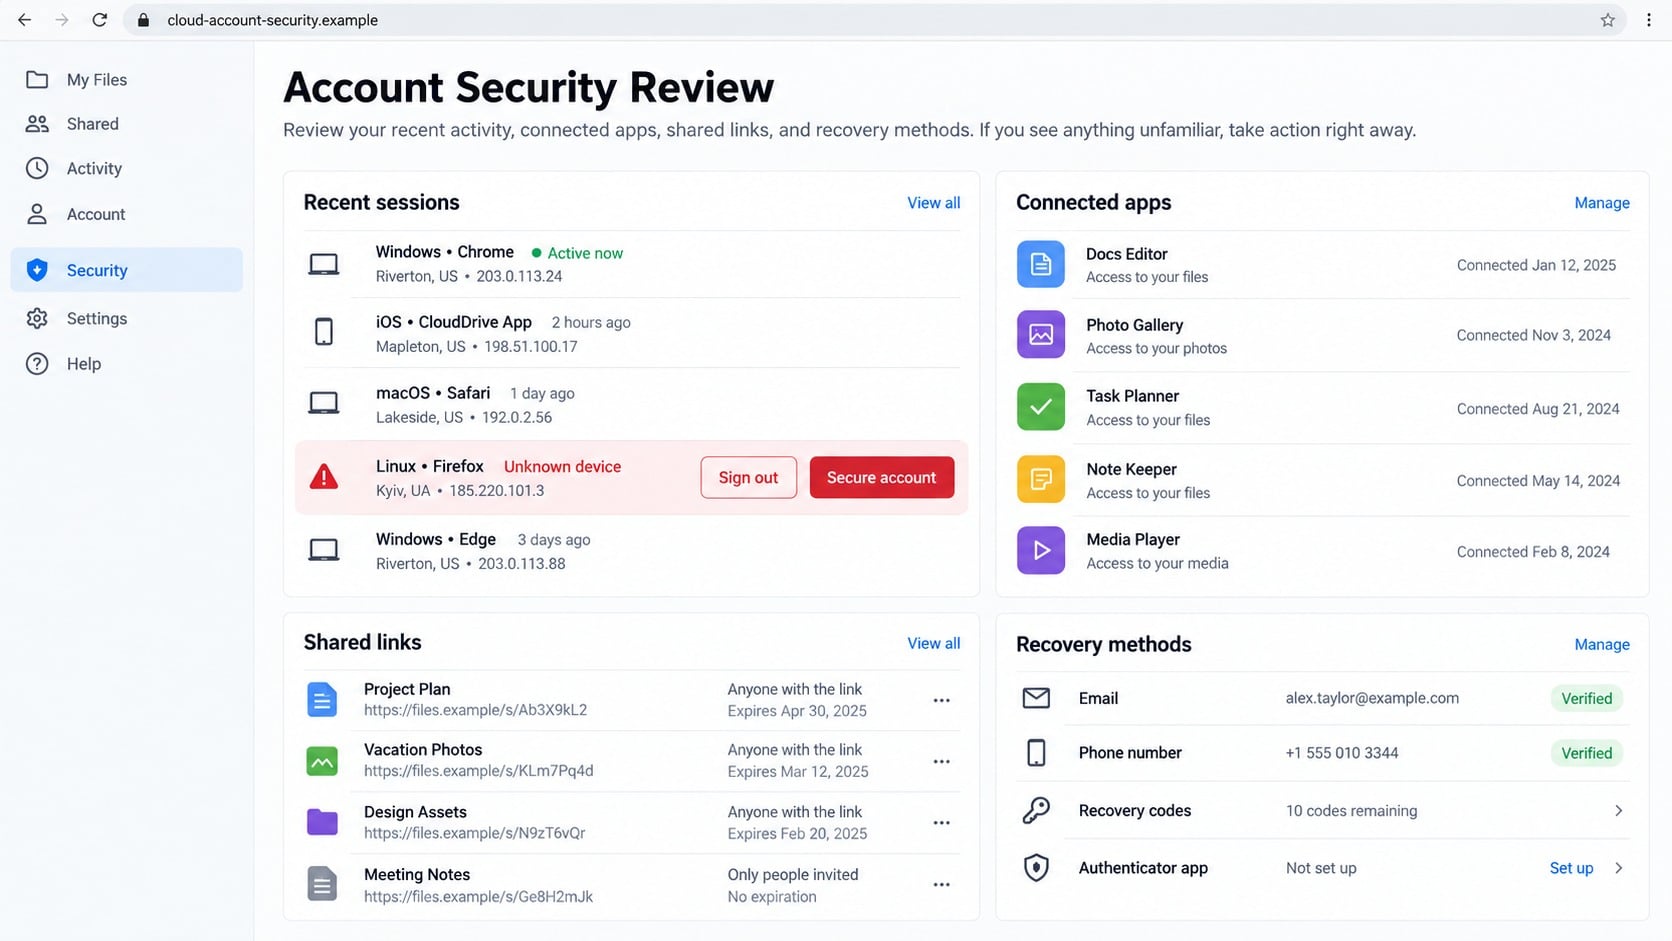
- Review login activity. End unfamiliar sessions and check locations, devices, access times, and security alerts for signs of successful entry.
- Remove hidden access. Inspect forwarding, filters, delegates, recovery contacts, connected applications, shared links, app passwords, and cloud integrations.
- Enable multifactor authentication. Use an authenticator application or security key when available. Replace recovery codes that may have been exposed.
- Notify affected collaborators. Warn coworkers and file-sharing contacts not to trust recent contract invitations or password-reset messages from the compromised account.
- Run a security scan. Use Malwarebytes to inspect the device. AdGuard can help block known phishing pages and malicious advertising during future browsing.
- Preserve evidence. Save the original message, headers, destination, submission time, and account alerts for security personnel and fraud reporting.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is every unexpected Dropbox share a scam?
No. Dropbox supports legitimate invitations and shared links, including files sent by people outside your contacts.
The danger here comes from the unrelated destination and credential request.
Verify unexpected shares independently instead of assuming either authenticity or fraud from the brand name alone.
Was Explicit-Contract.pdf a real contract?
The campaign used the filename as a lure.
The observed journey led to a credential form, not a verifiable agreement with identifiable parties.
Do not rely on a filename as evidence that a document exists or requires your signature.
Why would a shared document ask for my email password?
A phishing page requests it because mailbox access is valuable.
A legitimate external website cannot verify your private email account by collecting its password.
Authentication should occur on the known identity provider’s domain, with the destination clearly visible.
What if I clicked but did not enter anything?
Your immediate risk is lower, but close the page and avoid returning.
Update the browser, clear any unexpected downloads, and run Malwarebytes if a file opened or downloaded.
Report the message so administrators can block the destination for others.
Can multifactor authentication stop the attacker?
It often prevents a stolen password from being enough, but it is not a reason to keep that password.
Change it promptly and reject unexpected approval prompts.
Review sessions because stolen browser tokens or previously authorized applications can sometimes bypass a fresh login challenge.
How can a business reduce fake contract phishing?
Use a consistent contract platform, require recognizable sender details, and confirm unexpected envelopes through established channels.
Train employees to inspect registered domains and report brand switches.
Payment or legal changes should require a second-person review outside email.
The Bottom Line
The Explicit-Contract.pdf Dropbox email is a phishing invitation. It uses a vague legal file and familiar sharing design to reach an unrelated password form.
Connect documents to real conversations, open cloud accounts independently, and never give mailbox credentials to a generic file portal. Fast recovery can contain wider compromise.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.