


A signed real estate document can demand attention, especially when the message implies every participant already finished their part.
The SkySlope DigiSign notice examined here looks routine at first glance, but several details deserve a slower, more careful review.
Overview
What the completed-document message claims
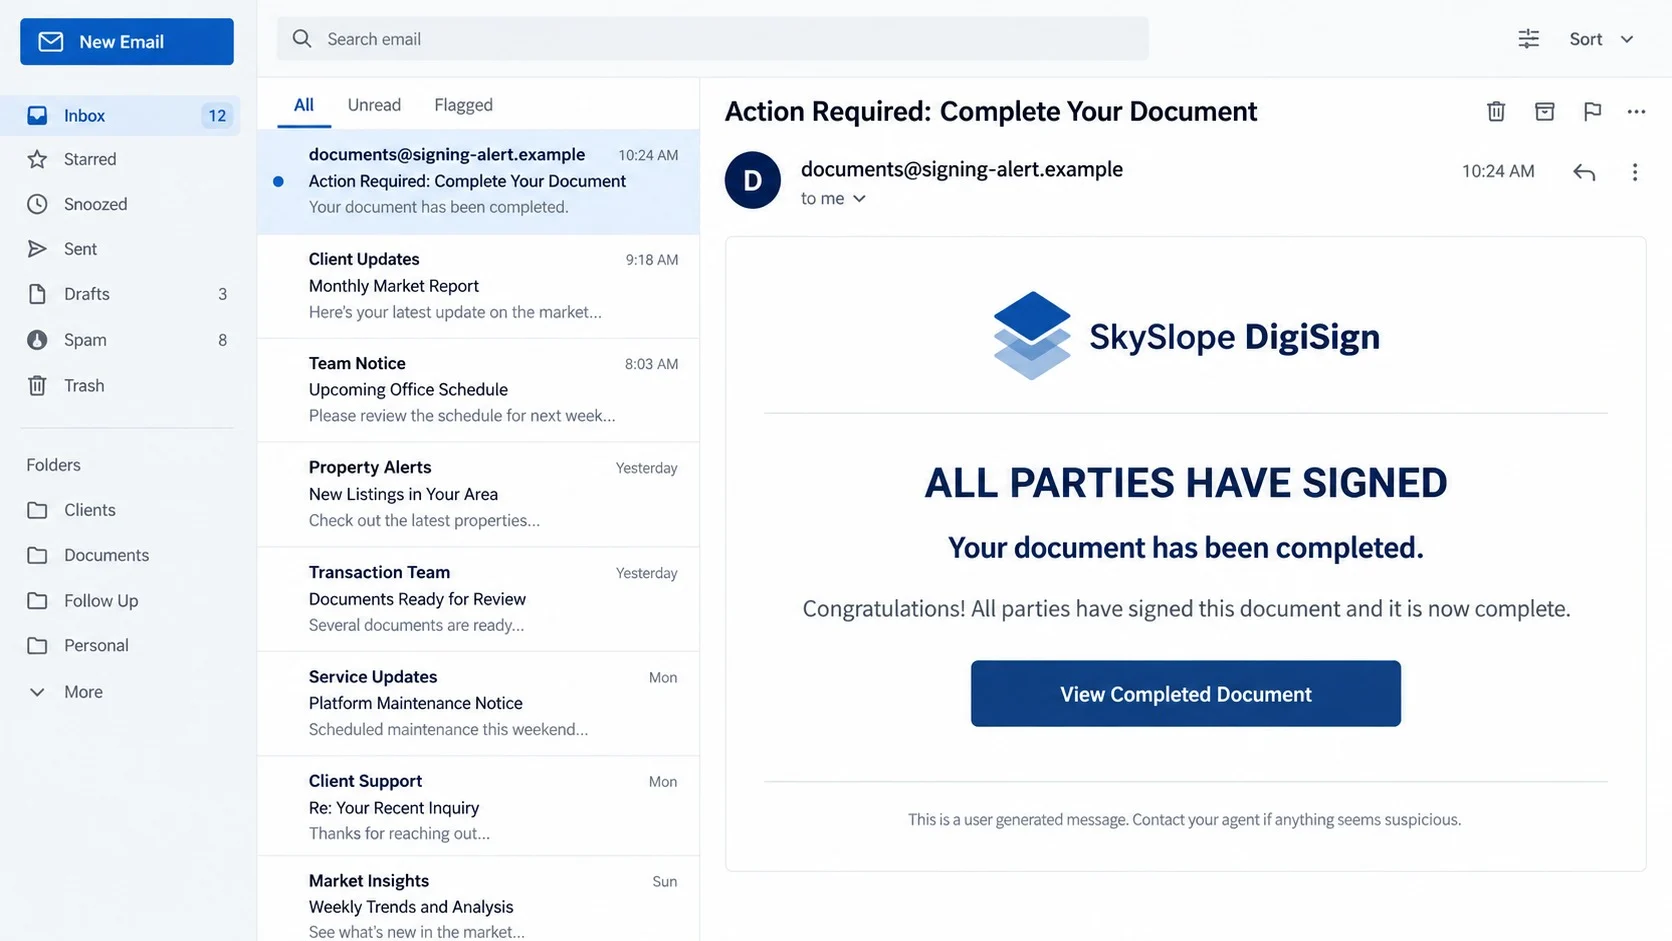
The email arrives with a subject resembling “Action Required: Complete Your Document.”
Inside, a SkySlope DigiSign heading appears above the awkward statement “ALL PARTY HAVE SIGNED.”
The message then says the document has been completed and presents a prominent “View Completed Document” button.
Congratulatory language suggests everyone signed successfully, creating the impression that the remaining task is simply downloading a final copy.
A small security warning may also appear, telling recipients not to share the email or its link.
That warning does not prove authenticity. Phishing messages routinely borrow security language because it makes an unfamiliar link feel protected.
Where the button actually leads
The observed button did not take the recipient to a recognizable SkySlope or document-signing account.
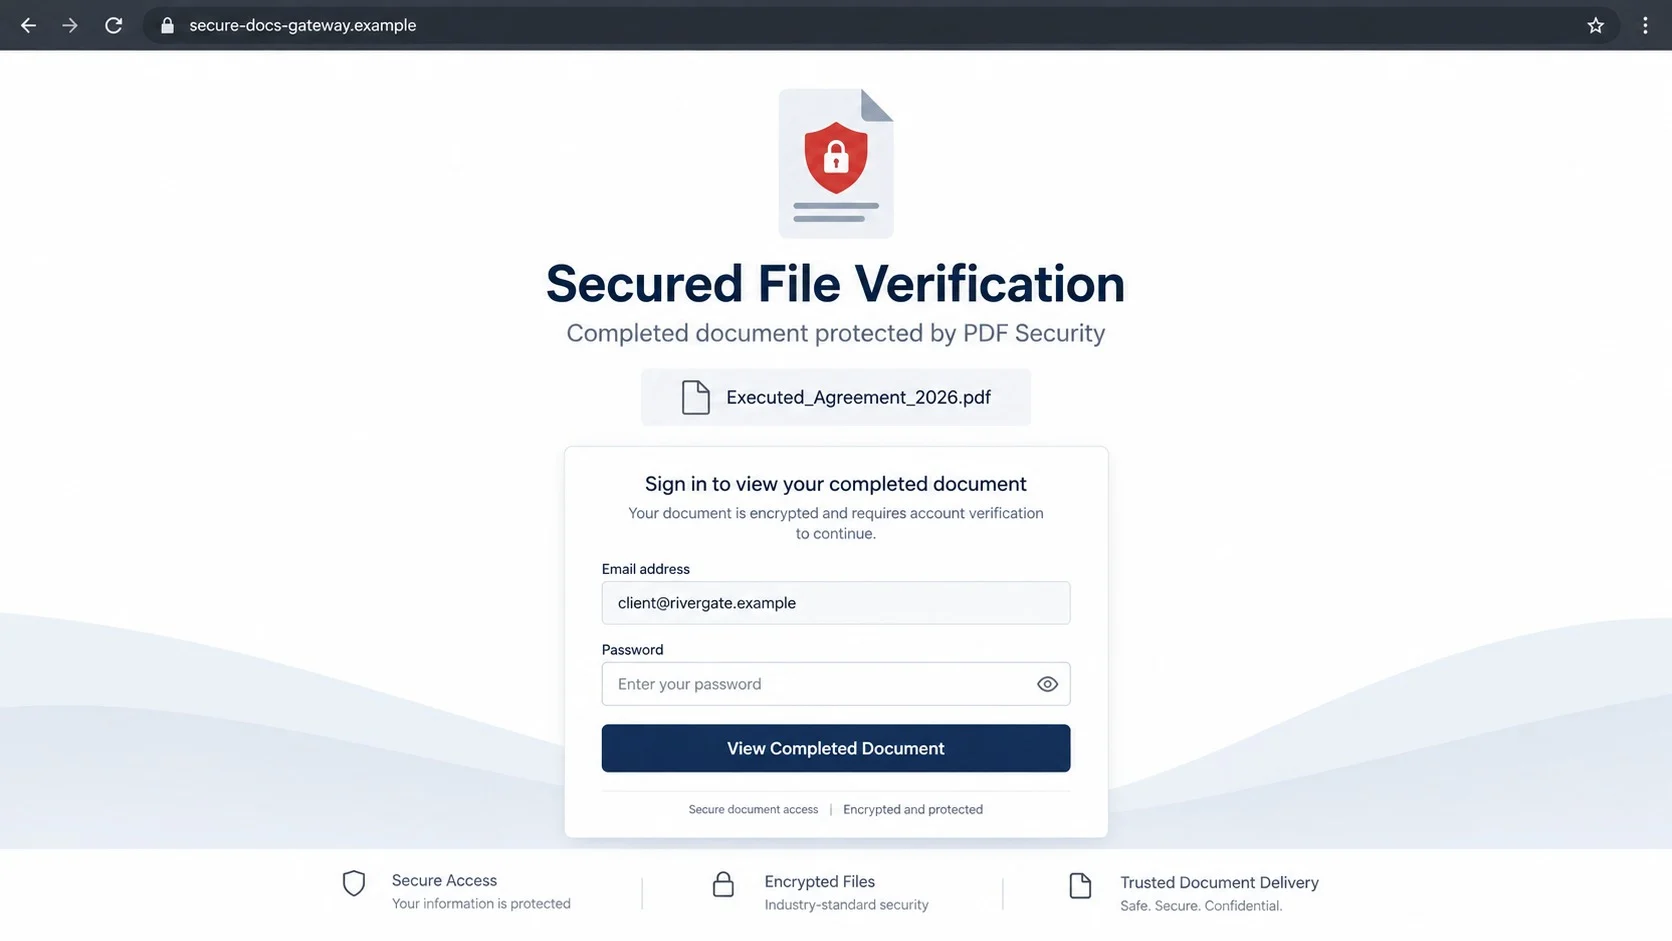
It opened an unrelated website that presented a “Secured Adobe File Verification” page.
The page displayed the recipient’s email address and requested the corresponding password before revealing the supposed file.
This transition is the decisive problem. A completed SkySlope document should not require mailbox credentials on an unrelated domain.
The page is designed to collect email passwords, not verify a legitimate transaction.
The warning signs in one view
The campaign combines familiar property paperwork with recognizable signing and PDF language.
Those references create borrowed trust, while the actual destination remains outside every organization named in the message.
Important warning signs include:
- An unexpected completed envelope that names no property, transaction, agent, or brokerage.
- Broken grammar such as “ALL PARTY HAVE SIGNED.”
- A button whose destination differs from the service named in the email.
- An Adobe-themed page that asks for an email account password.
- A prefilled address used to make the false login feel personalized.
- No trustworthy way to identify the document before signing in.
SkySlope, DigiSign, and Adobe are used as visual references in the lure. Their names do not establish involvement with the campaign.
How the SkySlope DigiSign Completed Document Email Scam Works
Step 1: The attacker sends an unexpected completion notice
The first message imitates the final stage of an electronic signature workflow.
Completion notices are effective lures because recipients expect signed documents to contain contracts, disclosures, leases, offers, or closing records.
The email avoids specific transaction details. That vagueness lets the same template reach agents, buyers, sellers, tenants, contractors, and office staff.
A recipient may assume a colleague started the envelope and click before asking who sent it.
The subject also mixes “action required” with “completed,” creating a small contradiction that encourages curiosity.
If everything is finished, the only apparent action is viewing the document. That makes the button seem both urgent and harmless.
Step 2: SkySlope and signature language provide borrowed credibility
Real estate teams regularly exchange documents through specialized transaction platforms.
Scammers exploit that routine by placing trusted names near generic signing language, even when their infrastructure has no connection to those services.
The phrase “all party have signed” communicates the intended story despite its grammar.
Recipients focused on a closing or deadline may notice the meaning before noticing the mistake.
The email may resemble an automated notification, which discourages replies and directs attention toward the central button.
Automation is easy to imitate. A logo, neutral layout, and standard footer can be copied without access to a legitimate platform.
Step 3: The button redirects outside the promised service
Clicking “View Completed Document” begins the campaign’s critical handoff.
The browser reaches a domain unrelated to the named transaction platform, signing service, brokerage, or known participant.
Attackers often choose neutral domain names containing words like document, secure, file, human resources, or verification.
Those words describe a function, but they do not identify who operates the website.
A padlock beside the address only means the connection is encrypted. It does not confirm that the page belongs to SkySlope.
Fresh phishing domains can obtain encryption certificates automatically, just like ordinary websites.
Redirects may also hide the final address until the victim has already followed one or more intermediate links.
Step 4: A fake PDF verification screen asks for the mailbox password
The landing page changes the story from transaction signing to PDF security.
It may claim that a protected document requires Adobe verification, then display the victim’s email in a completed field.
Prefilling the address creates familiarity and reduces the amount of information the victim must type.
The password field is the real collection point.
An unrelated document website cannot legitimately authenticate a private mailbox by receiving its password directly.
Secure integrations normally redirect users to the genuine identity provider, where the address bar shows the provider’s controlled domain.
The phishing form instead sends submitted values to the attacker or a collection service under their control.
Step 5: Failed-login theater can capture multiple passwords
Some fake portals reject the first entry and claim the password is incorrect.
This behavior is deliberate. People frequently retype carefully, submit an older password, or try another password used elsewhere.
Each attempt can be recorded.
The page may then show a loading animation, blank document, harmless error, or redirect to a real website.
That ending makes the incident look like a technical failure rather than successful credential theft.
The victim may postpone changing the password because no obvious confirmation appears.
Step 6: The stolen mailbox becomes a platform for deeper fraud
Email access is especially valuable in property transactions because conversations can contain names, signatures, phone numbers, invoices, and payment schedules.
An intruder can search for words such as closing, deposit, escrow, wire, commission, lease, or purchase agreement.
They may quietly create forwarding rules, delete security notices, and study conversation patterns before sending anything.
Once the timing looks favorable, the attacker can impersonate an agent, title representative, vendor, or client.
A fraudulent wire instruction sent inside an existing conversation can appear far more convincing than the original phishing email.
The account may also be used to distribute fresh completed-document lures to trusted contacts.
Why This Real Estate Document Lure Feels Convincing
Completed paperwork suggests a safe final step
People tend to treat signing requests cautiously because they expect to review terms before approving anything.
A completion notice feels different. It implies the important decisions already happened and the remaining file is simply a record.
That framing lowers resistance precisely when the link still deserves verification.
A genuine final copy should identify the envelope, parties, sender, and transaction context before demanding authentication.
Property transactions involve many unfamiliar participants
Buyers and sellers may interact with agents, coordinators, lenders, inspectors, attorneys, insurers, title companies, and contractors.
Because new names are normal, an unfamiliar sender may not feel immediately suspicious.
Scammers benefit from that crowded environment.
The safest question is not whether the sender’s role sounds possible. Ask whether a known participant independently confirms this exact document.
Deadlines make imperfect messages easier to overlook
Closings and leases create real time pressure.
A recipient worried about delaying other parties may overlook grammar, missing identifiers, or a strange destination.
Urgency should increase verification, not shorten it.
A brief call using a saved number can prevent days of account recovery or a devastating payment diversion.
What Criminals Can Do With a Compromised Real Estate Mailbox
Monitor conversations without announcing their presence
Attackers do not always act immediately after obtaining a password.
They may read weeks of mail, identify active transactions, and learn how each participant writes.
Hidden forwarding rules can copy incoming messages elsewhere while the owner continues using the account normally.
This surveillance helps criminals choose moments when a request for money or documents will appear believable.
Redirect deposits, invoices, or closing funds
A compromised conversation can be modified with new bank details shortly before payment.
The criminal may explain the change as an updated escrow account, accounting correction, or same-day closing requirement.
Because the message comes from a real mailbox and references real details, ordinary spam checks may not stop it.
Every payment instruction should be confirmed through a known telephone number, especially after any last-minute banking change.
Collect sensitive documents for identity fraud
Mailboxes may contain identification, tax records, loan applications, signatures, addresses, and financial statements.
Those materials can support identity theft, account recovery abuse, targeted impersonation, or fraudulent applications.
Recovery therefore involves more than changing one password.
The owner must review what information was accessible and notify affected organizations when exposure could create further harm.
Sender, Envelope, Destination, and Account Verification Checks
Confirm the sender through an existing conversation
Do not reply to the unexpected notice or call a number printed inside it.
Open a previous verified conversation with the agent, coordinator, attorney, or transaction contact.
Ask whether they sent a completed envelope and request its transaction reference.
A legitimate sender can identify the property, document type, participants, and expected delivery time.
If the answer is no, preserve the message and report it to the organization being impersonated.
Inspect the envelope details before opening any link
Real signing workflows provide meaningful context, not merely a button.
Look for the sender’s name, company, envelope identifier, property reference, signing date, and recognizable participants.
Compare those details with records you already possess.
Missing context matters because the attacker cannot safely guess information unique to your transaction.
Grammar alone is not proof, but mistakes reinforce concern when essential identifiers are also absent.
Examine the destination without trusting its design
On a desktop browser, hover over the button and read the actual destination.
On other devices, avoid opening it. Use the service’s saved bookmark or manually entered address instead.
The registered domain must belong to the expected provider, not merely contain reassuring words.
Subdomains and long paths can place a trusted name before an attacker-controlled domain.
Read the address from right to left around the registered domain, and stop if ownership remains unclear.
Open the known account independently
Sign in through the platform address you normally use, never through the email button.
Check the account’s envelopes, completed documents, notifications, and activity history.
If the document is real, it should appear there without requiring a mailbox password on another website.
Ask internal support to inspect the email headers and destination when a business account is involved.
Independent access breaks the attacker’s carefully staged route and gives you a trusted comparison point.
How to Handle a Suspicious Completed Document Safely
Keep the email intact while you verify it. Forwarding as an attachment can preserve routing information for security staff.
Do not test the password form with false credentials. Visiting further can expose browser details and confirm that your address is active.
If a colleague sent the message, ask them to share the envelope identifier through a separate channel.
Organizations should teach staff that completed documents never justify entering an email password into an unrelated PDF portal.
Payment teams should treat any later banking change from the same conversation as high risk.
Enable multifactor authentication before an incident, preferably using an authenticator application or security key rather than text messages alone.
What to Do If You Fell for the SkySlope DigiSign Scam
- Change the exposed password from a trusted device. Open the genuine email provider directly. Create a unique password that you have never used elsewhere.
- End active sessions. Review recent sign-ins and sign out every unfamiliar device. If available, revoke all sessions created before the password change.
- Enable strong multifactor authentication. Prefer an authenticator application or security key. Replace recovery codes if the mailbox stored or displayed them.
- Remove attacker persistence. Inspect forwarding rules, filters, delegates, connected applications, app passwords, recovery addresses, and automatic replies for unauthorized changes.
- Warn transaction participants quickly. Tell agents, clients, title staff, lenders, and accounting personnel that messages from the account may be untrustworthy.
- Pause pending payments. Confirm every wire or deposit instruction through previously verified contact details. Notify the financial institution immediately if money moved.
- Scan the device. Run Malwarebytes to check for malware, then use AdGuard to reduce malicious advertising and known phishing destinations during browsing.
- Document and report the incident. Save the email, destination, timestamps, and account alerts. Provide them to organizational security and relevant fraud channels.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is the SkySlope DigiSign completed document email real?
The specific campaign described here is phishing.
Its button leads away from the named services and ends at a page requesting mailbox credentials.
SkySlope can be used legitimately, so verify each notice inside your known account rather than judging only the displayed branding.
Why does the page already know my email address?
The address can be embedded in the link, taken from a mailing list, or collected during an earlier breach.
Prefilling it does not prove account access.
It mainly makes the fake form feel personalized and leaves the victim with only a password to enter.
Does the browser padlock mean the document page is safe?
No. The padlock indicates an encrypted connection between the browser and that website.
It does not verify the operator’s identity or claims.
A phishing website can use valid encryption while securely delivering stolen credentials to its owner.
Can I safely open a real completed document without the email button?
Yes. Navigate to the signing or transaction platform using your saved bookmark or manually entered address.
Review completed envelopes inside that account.
If nothing appears, contact the supposed sender through an established channel before taking further action.
What if I entered my password but multifactor authentication blocked access?
Change the password anyway.
The attacker still possesses it and may try another service, trigger repeated prompts, or wait for an opportunity.
Review sessions, recovery settings, and mailbox rules because a previous session may already exist.
Could this scam lead to real estate wire fraud?
Yes. A compromised mailbox can reveal transaction timing and trusted relationships.
Criminals may later insert altered payment instructions into genuine conversations.
Verify bank details by telephone using a number established before the requested transfer.
The Bottom Line
The SkySlope DigiSign completed document email is a credential-phishing lure. Its polished signing story ends on an unrelated page asking for an email password.
Verify envelopes inside the known platform, confirm senders separately, and act quickly after any submission. Those habits protect both the mailbox and the transaction.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Community experiences
Did this happen to you?
Your experience could help someone recognize the same scam. Submit a private report for our team to review.
I experienced this tooReports are reviewed before publication. Sharing publicly is always your choice.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.