NoxLock Ransomware Virus: Removal, Recovery, and File Decryption Guide
Written by: Lapain Epuran
Published on:
The first sign of NoxLock can look like a broken folder. Familiar filenames disappear, unfamiliar strings take their place, and ordinary documents stop opening.
That disorder carries useful evidence. Understanding what changed, and what should remain untouched, helps shape a safer response.
Overview
NoxLock Hides Both the Original Name and Extension
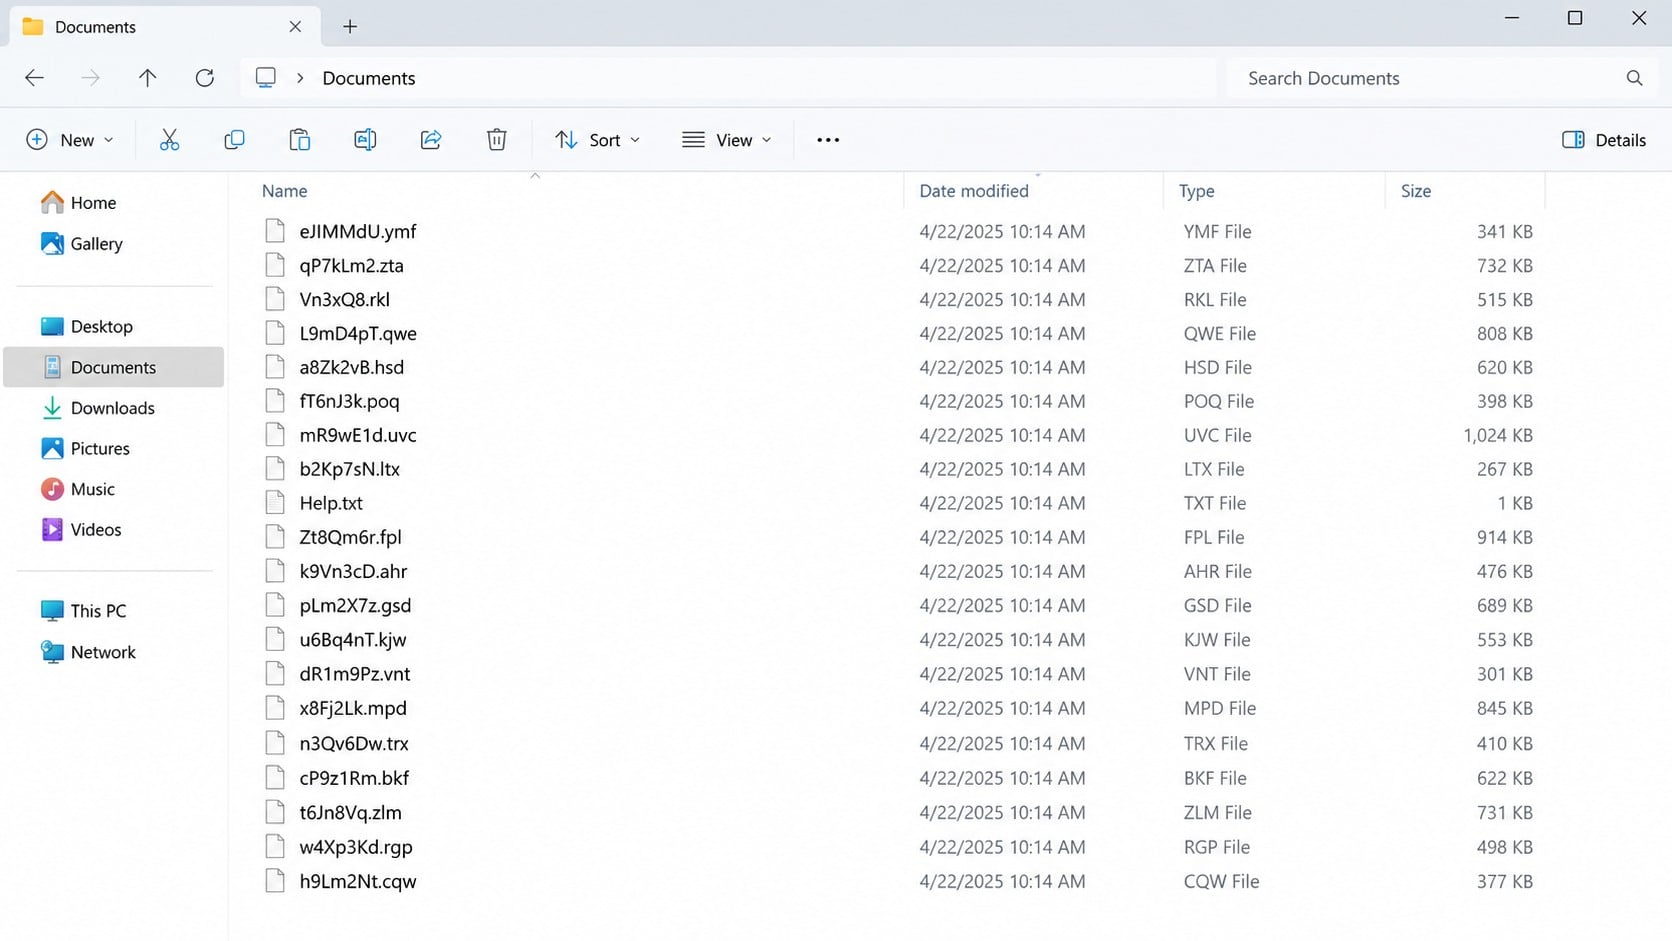
NoxLock ransomware does more than add a recognizable suffix. It replaces the original filename and extension with random-looking characters.
An observed example changed 1.jpg into eJlIMMdU.ymf. Other files can receive completely different names, making identification by sight difficult.
The random label does not describe the file type. A renamed spreadsheet, photograph, database, and archive may appear nearly identical inside one folder.
Opening the files produces errors because their contents were encrypted. Renaming them to guessed extensions cannot restore the original information.
This naming behavior complicates recovery because staff may no longer know which encrypted object belonged to a particular project.
Help.txt Combines Instructions With Extortion
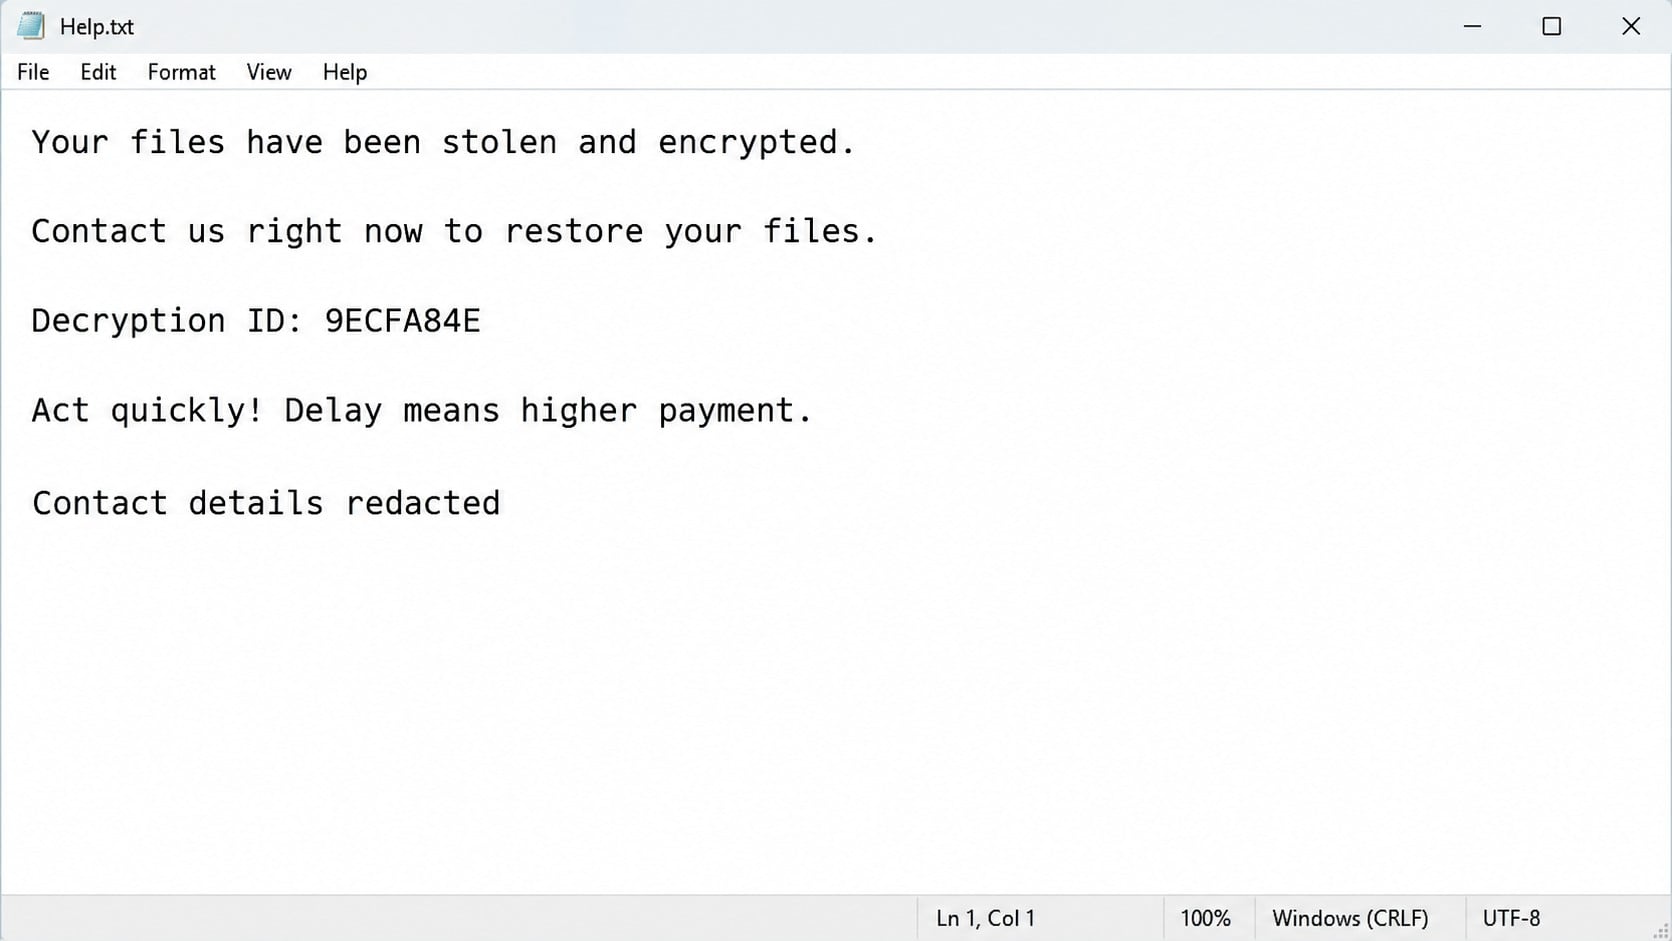
NoxLock places a text file named Help.txt on affected systems and may change the desktop wallpaper.
The note says important files were encrypted and claims confidential information was taken from the network.
It provides a unique decryption identifier and directs the victim toward private contact channels. Those details should remain with the incident team.
The message warns that waiting will increase the demand. This threat is intended to make technical verification feel unaffordable.
A deadline does not change the fundamentals. Criminals cannot offer an enforceable promise of working decryption or permanent data deletion.
Safe Recovery Starts With Scope and Identity
NoxLock’s random names can tempt administrators to delete everything as corrupt. Preserve representative files, the note, and system evidence instead.
Determine which machines, accounts, shared drives, and backup systems were reachable when encryption occurred.
Then identify how the operator entered and whether access remains active. Restoration before containment can repeat the damage.
Original filenames and extensions are replaced by random strings.
Encrypted files cannot be repaired through ordinary renaming.
Help.txt contains the demand and a victim identifier.
The wallpaper may be changed to reinforce the warning.
The note alleges encryption and confidential data theft.
Delay is threatened with a higher price.
Removal and file restoration require separate workstreams.
No publicly verified free decryptor was confirmed for the examined NoxLock incident when this article was prepared.
Preserving encrypted material still matters. Better technical intelligence or a future decryptor could create options later.
How NoxLock Ransomware Works
Step 1: Access Is Obtained Through a Vulnerable Path
A ransomware payload cannot encrypt a network from nowhere. It needs code execution, stolen access, or an exposed service.
Possible routes include compromised remote desktops, unpatched internet-facing software, malicious downloads, phishing attachments, and abused management tools.
The specific path must be proven from local evidence. An extension or ransom note cannot identify the original weakness alone.
Organizations should also inspect third-party access. A vendor account can reach sensitive systems without looking like an unknown user.
Step 2: Privileges and Reach Are Expanded
After entry, an operator may search for credentials, administrator sessions, shared folders, and systems that manage backups.
Higher privileges make it possible to deploy the payload widely, disable defenses, and access information unavailable to the first account.
Look for unexpected service creation, remote command activity, security exclusions, new scheduled tasks, and unusual administrative logins.
Endpoint alerts from several machines may reflect one central deployment. Investigate their timing instead of treating each host as an isolated infection.
Segmentation limits this movement. Flat networks and broadly shared administrator passwords give intruders a larger working area.
Step 3: Files May Be Staged Before Encryption
The Help.txt message claims data was stolen. Criminal groups use that allegation to threaten publication when backups reduce encryption leverage.
Files can be compressed into archives, copied to staging folders, or transferred through legitimate cloud utilities.
Search for unusual archive creation, rare processes, large outbound sessions, and access to repositories containing regulated information.
A claim may be exaggerated, but dismissing it without investigation can create legal and reputational risk.
Security and privacy teams should separate confirmed facts, reasonable indicators, and attacker statements throughout the response.
Step 4: Encryption Destroys the Familiar File Map
NoxLock encrypts accessible files, then substitutes randomized names and extensions.
This behavior breaks applications and removes human-readable context. A department cannot easily identify its contracts, images, or financial records.
Connected shares can expose data far beyond the first device. The running account’s permissions determine much of that reach.
Synchronization tools may upload damaged versions. Pausing sync protects remote version history while investigators establish boundaries.
Do not assume every randomly named file is identical. Preserve directory structure and metadata because location may help reconstruct identity.
Step 5: Help.txt and the Wallpaper Demand Contact
The ransom message introduces the NoxLock name and tells victims that ordinary recovery is impossible without the attackers.
It includes a unique identifier, which may connect the affected environment with an encryption key or campaign record.
The operators provide private communication options and warn that the amount will rise after delay.
That urgency serves the attacker. It does not establish how much data was encrypted, whether files were copied, or whether decryption will work.
Keep attacker contact details out of public screenshots. Imposters can reuse them, and employees may contact criminals without authorization.
Step 6: A Private Negotiation Becomes Another Risk
The operator may ask about company size, revenue, insurance, backups, and the importance of affected systems.
Each answer helps price the demand and reveals the victim’s remaining leverage.
Attackers sometimes decrypt samples, but selected files are not a reliable test of a large database or entire server collection.
A payment can produce a slow tool, corrupted output, an additional demand, or no response at all.
Any engagement should be coordinated through legal counsel and experienced responders. Personal improvisation can complicate evidence, insurance, and regulatory decisions.
Step 7: Dormant Access Can Survive the Visible Attack
The encryption event is dramatic, but quieter persistence may remain in accounts, services, or remote-management software.
A restored server can be compromised again if stolen credentials, vulnerable applications, or malicious tools survive.
Rebuild high-risk systems from trusted media when confidence in cleaning is insufficient.
Rotate secrets by priority, including identity administrators, backup operators, service accounts, cloud keys, and remote-access credentials.
Continue monitoring after operations resume. Late logins, beaconing, and attempted access can reveal that containment was incomplete.
How to Identify a NoxLock Infection
Examine the Pattern Without Guessing Filenames
Random-looking names across many file types are a strong clue when combined with failed opening attempts and Help.txt.
Record paths, timestamps, sizes, and several examples. Do not rename original evidence to familiar extensions.
Folder placement may provide the only practical hint about a file’s former purpose. Preserve the complete directory tree.
Compare affected shares and endpoints to locate the earliest cluster. That system may contain richer execution evidence.
Collect the Note, Wallpaper, and Decryption Identifier
Save Help.txt and capture the changed wallpaper. Preserve exact text internally while redacting contacts from public materials.
The victim identifier can help specialists correlate samples. It should not be treated as a password or posted casually.
Record creation times and every directory containing the note. Wide distribution can reveal how the payload traversed storage.
Take cryptographic hashes of collected artifacts so later analysis can confirm that evidence remained unchanged.
Investigate Systems That Appear Unaffected
A machine without renamed files can still contain stolen sessions, remote tools, or the account used for deployment.
Search endpoint telemetry for the same process lineage, network destinations, administrative tools, and persistence mechanisms.
Check backup infrastructure separately. Deleted snapshots, altered jobs, new administrators, or disabled protections demand immediate attention.
Cloud consoles, hypervisors, identity services, and email systems belong in the scope when shared credentials could reach them.
Use Variant-Specific Professional Confirmation
Another threat could copy the NoxLock label or create similar random filenames. Reliable identification combines multiple indicators.
A qualified laboratory can compare the note, payload behavior, encrypted file structure, and known technical signatures.
Check established public decryption resources for the exact variant, using a clean device and non-sensitive samples.
Avoid promoted “NoxLock decryptors” from unknown sellers. Such downloads may be useless, malicious, or copied from unrelated projects.
Recovering Files When Their Names Are Gone
File recovery has two challenges: reversing encryption and matching each object with its original identity.
A verified backup can solve both because it preserves readable content, filenames, directory structure, permissions, and application relationships.
Keep the backup isolated while containment continues. Restoring into a compromised environment can expose the clean copy immediately.
Cloud histories and snapshots may hold earlier versions. Access them through an uncompromised administrator account after revoking suspicious sessions.
Email attachments, collaboration platforms, exported reports, recipients, and offline archives can replace a smaller number of essential files.
Database recovery requires application-aware procedures. Copying random encrypted components into a live database can worsen corruption.
If a legitimate decryptor later appears, test duplicates from several file types and sizes. Successful photographs do not guarantee healthy business databases.
Compare restored totals, application checks, and user workflows. A folder that opens may still be incomplete.
Store unresolved encrypted copies with hashes and incident documentation. Do not mix them into active shares.
Document what was restored, reconstructed, lost, or awaiting future recovery. That record supports business and legal decisions.
What to Do If NoxLock Encrypted Your Files
A calm, ordered response preserves more options than hurried deletion or immediate negotiation.
Separate affected devices from every shared resource.
Unplug network connections, disable wireless access, pause VPN sessions, and disconnect external storage. Block compromised hosts at network controls where possible.
Coordinate shutdown decisions with specialists because volatile evidence can disappear when power is removed.
Stop synchronization and protect clean copies.
Pause clients that might upload encrypted versions. Restrict backup consoles and storage using credentials created on a known-clean machine.
Confirm retention and immutability settings before starting restoration work.
Preserve the random-name evidence.
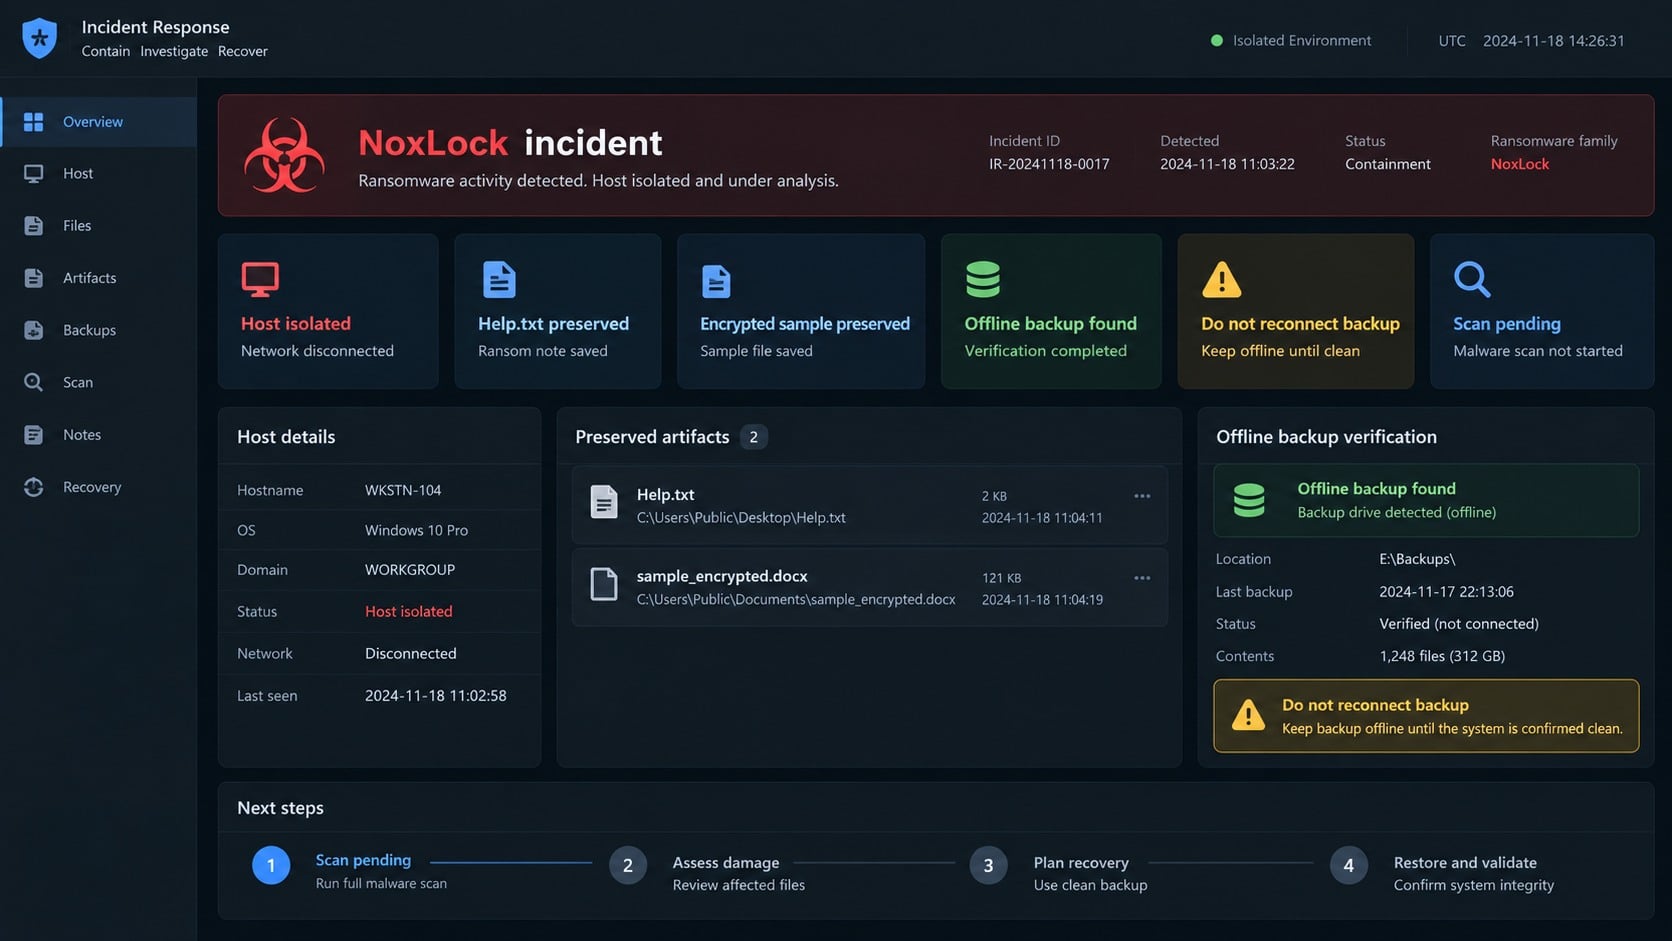
Copy Help.txt, the wallpaper, selected encrypted files, directory listings, timestamps, and security logs to controlled evidence storage.
Keep the unique identifier confidential. Record who handles each artifact.
Establish a coordinated incident team.
Bring together security, infrastructure, legal, privacy, leadership, communications, insurers, and outside responders as needed.
Contact law enforcement through official channels. Do not rely on a recovery offer received after the attack.
Revoke the attacker’s identity access.
Reset privileged accounts first, terminate sessions, rotate service credentials, and replace exposed keys or tokens.
Review multifactor methods, recovery contacts, federation settings, and newly registered devices for unauthorized changes.
Clean or rebuild before restoring business data.
Malwarebytes can assist with endpoint threat detection after forensic collection. Reimage systems when trustworthy removal cannot be established.
AdGuard can reduce future contact with malicious advertising and phishing sites, but it cannot reconstruct NoxLock filenames or decrypt data.
Recover from verified sources in stages.
Test backups for integrity, malware, and the correct restoration date. Bring priority services online in isolated segments.
Validate filenames, permissions, databases, and application behavior before allowing normal user access.
Assess the alleged data theft separately.
Review outbound traffic, sensitive repository access, archive creation, and cloud activity. Do not treat the ransom note as conclusive evidence.
Follow legal advice about customer, employee, partner, or regulator notification.
Reject unauthorized payment or contact.
Employees should not message the operators or send sample documents. Criminal communication can reveal leverage and expose more information.
Any decision must consider law, sanctions, insurance, safety, operational impact, and the absence of guarantees.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Anti-Malware Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
Adware — the cause of those annoying pop-ups
Browser hijackers — unwanted redirects and changed homepages
Trojans and spyware — hidden programs stealing your data
Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The whole process takes about 5 minutes.
Malwarebytes for WindowsMalwarebytes for MacMalwarebytes for Android
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
(The link opens in a new page where your download will start)
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.
Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.
Malwarebytes will now install on your device. This usually takes under a minute.
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.
On the final screen, click Open Malwarebytes to launch the program.
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.
In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.
Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take several minutes. Feel free to do something else — just check back occasionally to see the progress.
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.
Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, your PC is clean and you can continue with the next steps in this guide.
When the scan finishes, click Quarantine to remove everything Malwarebytes found. That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If your current antivirus allowed this malicious program on your computer, you may want to consider purchasing Malwarebytes Premium to protect against these types of threats in the future. If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.
When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.
Once the scan is done, remove every threat it detected. Your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If your current antivirus allowed a malicious program on your computer, you might want to consider purchasing the full-featured version of Malwarebytes Anti-Malware to protect against these types of threats in the future. If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.
When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options. This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue. Tap on “Got it” to proceed to the next step. Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue. Tap on “Allow” to permit Malwarebytes to access the files on your phone.
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.
Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
After the scan, tap Remove Selected to delete all detected threats. Your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If your current antivirus allowed a malicious app on your phone, you may want to consider purchasing the full-featured version of Malwarebytes to protect against these types of threats in the future. If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
Many ransomware families preserve the base filename and add one extension. NoxLock’s approach removes that convenient map.
This can slow priority recovery because teams cannot immediately select a named contract or presentation from an encrypted folder.
Directory metadata, application indexes, recent-file lists, backups, collaboration records, and user knowledge become valuable reconstruction sources.
A response team should preserve those supporting records before rebuilding devices.
Randomization also makes simplistic internet advice dangerous. Guessing extensions from file size or location can create confusion without addressing encryption.
Recovery plans should restore whole verified structures whenever possible, then reconcile exceptions through documented business owners.
Frequently Asked Questions
Can I recover a NoxLock file by restoring its old name?
No. The renamed file also contains encrypted data. Guessing the former name changes only the label, not its contents.
Preserve the current name and location so specialists can study the variant and correlate recovery records.
What is the Decryption ID inside Help.txt?
It is an identifier used by the operators to distinguish victims or encryption sessions. It is not a public recovery key.
Keep it with incident evidence and share it only with authorized responders or legitimate authorities.
Does the changed wallpaper mean encryption is still running?
Not necessarily. The wallpaper is a notification tactic, but malicious processes or remote access may still remain.
Maintain isolation until investigation confirms that execution and attacker access have ended.
Can antivirus software restore the original filenames?
Security software can remove malicious programs, but it usually cannot recreate names or decrypt previously transformed data.
Backups preserving folder structure offer the clearest restoration route. Future variant-specific tools may provide additional possibilities.
Is every file with a random extension infected?
NoxLock produces randomized labels, but other software and malware can also create unusual names.
Confirm identification through Help.txt, technical behavior, timestamps, and trusted analysis before choosing a recovery method.
Should an organization announce a data breach immediately?
Begin legal and forensic assessment immediately. Public or regulatory timing depends on jurisdiction, evidence, affected data, and applicable obligations.
A ransom claim deserves investigation, while precise statements should distinguish allegations from verified findings.
The Bottom Line
NoxLock encrypts information and erases familiar filenames, turning a security event into a difficult reconstruction problem. Preserve paths, notes, identifiers, logs, and clean backups.
Contain access before restoration, investigate the theft claim independently, and rebuild through verified stages. A criminal deadline should never replace a disciplined incident process.
10 Rules to Avoid Online Scams
Here are 10 practical safety rules to help you avoid malware, online shopping scams, crypto scams, and other online fraud. Each tip includes a quick “if you already got hit” action.
Stop and verify before you click, log in, download, or pay.
Most scams win by creating urgency. Verify using a trusted method: type the website address yourself, use the official app, or call a known number (not the one in the message).
If you already clicked: close the page, do not enter passwords, and run a malware scan.
Keep your operating system, browser, and apps updated.
Updates patch security holes used by malware and malicious ads. Turn on automatic updates where possible.
If you saw a scary “update now” pop-up: close it and update only through your device settings or the official app store.
Use layered protection: antivirus plus an ad blocker.
Antivirus helps block malware. An ad blocker reduces scam redirects, phishing pages, and malvertising.
If your browser is acting weird: remove unknown extensions, reset the browser, then run a full scan.
Install apps, software, and extensions only from official sources.
Avoid cracked software, “keygens,” and random downloads. During installs, choose Custom/Advanced and decline bundled offers you do not recognize.
If you already installed something suspicious: uninstall it, restart, and scan again.
Treat links and attachments as untrusted by default.
Phishing often impersonates delivery services, banks, and popular brands. If it is unexpected, do not open attachments or log in through the message.
If you entered credentials: change the password immediately and enable 2FA.
Shop safely: research the store, then pay with protection.
Be cautious with brand-new stores, “closing sale” stories, and prices that make no sense. Prefer credit cards or PayPal for dispute options. Avoid wire transfers, gift cards, and crypto payments.
If you already paid: contact your card issuer or PayPal quickly to dispute the transaction.
Crypto rule: never pay a “fee” to withdraw or recover money.
Common patterns include fake profits, then “tax,” “gas,” or “verification” fees. Another is a “recovery agent” who demands upfront crypto.
If you already sent crypto: stop paying, save evidence (wallet addresses, TXIDs, chats), and report the scam to the platform used.
Secure your accounts with unique passwords and 2FA (start with email).
Use a password manager and unique passwords for every account. Enable 2FA using an authenticator app when possible.
If you suspect an account takeover: change passwords, sign out of all devices, and review recent logins and recovery settings.
Back up important files and keep one backup offline.
Backups protect you from ransomware and device failure. Keep at least one backup on an external drive that is not always connected.
If you suspect infection: do not connect backup drives until the system is clean.
If you think you are a victim: stop losses, document evidence, and escalate fast.
Move quickly. Speed matters for disputes, account recovery, and limiting damage.
Stop payments and contact: do not send more money or respond to the scammer.
Call your bank or card issuer: block transactions, replace the card if needed, and start a dispute or chargeback.
Secure your email first: change the email password, enable 2FA, and remove unfamiliar recovery options.
Secure other accounts: change passwords, enable 2FA, and log out of all sessions.
Scan your device: remove suspicious apps or extensions, then run a full malware scan.
Save evidence: screenshots, emails, order pages, tracking pages, wallet addresses, TXIDs, and chat logs.
Report it: to the payment provider, marketplace, social platform, exchange, or wallet service involved.
These rules are intentionally simple. Most online losses happen when decisions are rushed. Slow down, verify independently, and use payment methods and account controls that give you recourse.
Hello! I'm Lapain Epuran, your go-to source for detailed and honest product reviews. From tech gadgets to miracle cures, I provide insights to help you make informed choices. Join me as we discover what's truly worth your time and money.