

A bank email warns that your account details need attention within 24 hours. With access supposedly at stake, the confirmation button can look like the sensible choice.
Before using it, compare the request with how you normally contact your bank. A few familiar-looking details may be doing more work than you realize.
Overview
A restriction warning pushes customers toward a login
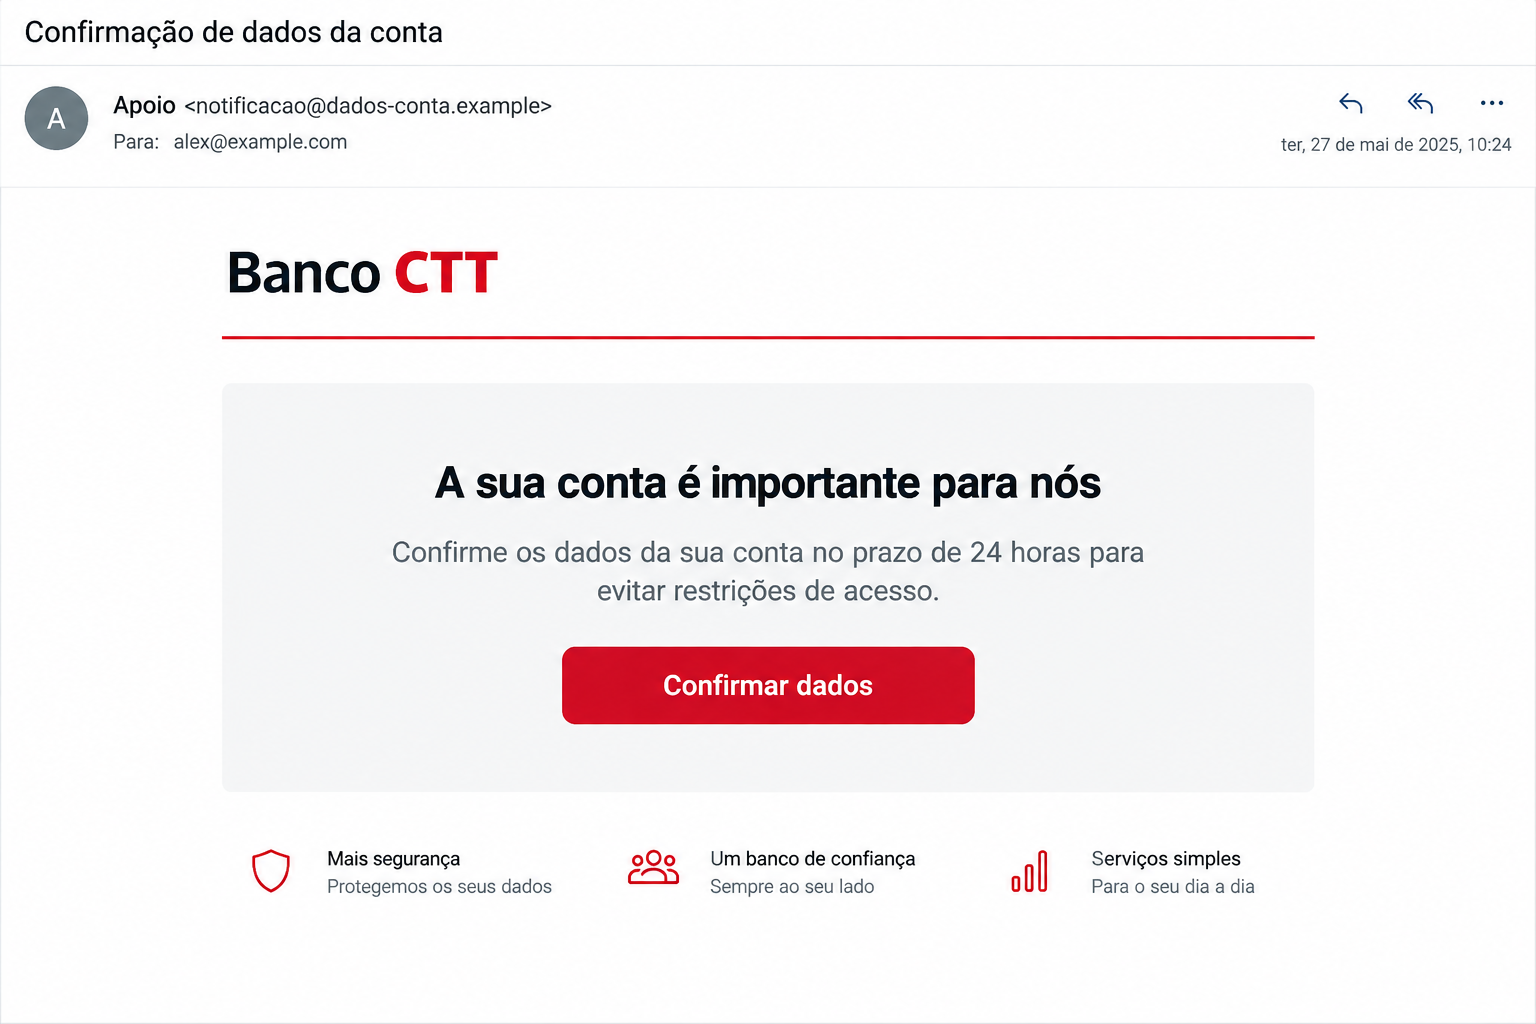
The Banco CTT email scam impersonates the Portuguese bank and says recipients must confirm account information within 24 hours to avoid restrictions.
The reported route leads toward a copied online-banking login. Its purpose is credential theft, not a genuine account-maintenance procedure.
Banco CTT is the organization being impersonated. This warning concerns the fraudulent notice, not an accusation that the real bank is running the scheme.
The bank’s published guidance contradicts the request
Banco CTT’s security guidance says it doesn’t send email or SMS asking customers to follow links into Homebanking or provide personal data.
It also warns customers against sharing credentials or operation codes with callers. A request framed as protecting the account doesn’t make disclosure appropriate.
The reported fraudulent destination is no longer active. Don’t assume its exact current screen or any additional requests match another person’s experience.
The safest next action depends on your exposure
- If you only received the email, leave its button alone and report it.
- If you shared banking credentials, contact the actual bank promptly.
- If you approved an operation, identify what the approval authorized.
- If you installed software, address the device as well as account access.
The illustration uses a fictional sender and representative layout. It shows the account-confirmation pitch, not a genuine bank email or a tested login page.
Why Account Restrictions Are Such a Useful Pretext
Most people don’t want to discover that banking access has stopped just when a payment is due. A restriction warning exploits that practical concern.
The proposed fix sounds smaller than the threatened inconvenience. Confirming details can feel like administration rather than a decision to trust a new financial website.
A 24-hour deadline adds pressure without giving the recipient a real reason to believe the sender. The deadline belongs to the message’s claim.
Don’t let it replace your normal way of verifying a banking issue. You can open the established app or contact the bank without using the email.
Even a correct name or recognizable account fragment wouldn’t settle the question. Personalization can make a false request more convincing without authorizing it.
Likewise, a familiar color scheme is only presentation. A copied page can look like a bank while being controlled by someone else.
Check the relationship between the request and your actual account. A real service notice should withstand independent confirmation.
If an issue really exists, the genuine bank can explain it through its established channels. Refusing an unverified login link doesn’t prevent you from resolving it.
That distinction is especially helpful when you’re busy. You don’t need to decide everything about the email; you need a trustworthy route to the bank.
How the Banco CTT Email Scam Works
Step 1: Introduce an urgent problem with account information
The notice gives the recipient something to fix. It presents a restriction as the likely consequence of failing to complete a simple verification.
This changes the reader’s focus from evaluating the sender to preventing an inconvenience. The requested action becomes the apparent way to keep everyday banking working.
Pause before accepting that framing. Ask whether the request appears inside your independently opened account or only in an unsolicited message.
A genuine need to update records is possible, but it doesn’t authenticate this particular route. Check through the bank rather than the claimant.
Step 2: Transfer trust from the bank name to an external page
The email’s button carries the apparent authority of the surrounding branding. Once clicked, that familiarity can make a copied login feel expected.
Look at the actual address and how you reached it. Don’t rely on the word Banco, a logo, or the appearance of a password field.
A secure connection protects communication with the destination, not the honesty of whoever operates it. A convincing banking page still needs a genuine origin.
Don’t search for alternative mirrors if the page fails. Open the real bank yourself instead of trying to repair the email’s route.
Step 3: Seek information that belongs only in a genuine banking session
A copied form can request login information under the same account-confirmation pretext. Submitting it gives an untrusted party information intended for the bank.
If the page keeps reporting a mistake, don’t keep entering more secrets to satisfy it. Repeated requests can increase what you’ve disclosed.
Banking authentication is specific to the service and action. A request that looks familiar isn’t safe merely because it resembles one part of the normal process.
Leave the form and contact verified support if you’ve entered anything. Tell the bank what type of information you shared without sending the secret itself.
Step 4: Make any further approval sound like verification
Banking fraud may involve a follow-up code, notification, or call. Don’t assume an additional request is harmless because it follows the first login screen.
Read what a genuine bank notification says you’re authorizing. An account-data check is not the same thing as a transfer or device enrollment.
These are possible escalation routes, not confirmed actions at the inactive page. If you received one, preserve its exact wording for the bank.
Never approve a transaction merely to cancel an alleged restriction. An unfamiliar person shouldn’t direct financial actions while you try to diagnose a warning.
Step 5: Leave the customer needing to recover real access
The email’s restriction may be imaginary, but information submitted to an impostor can create a real account-security problem.
Don’t wait for visible missing money before reporting exposed banking credentials. Early action gives the bank a better opportunity to assess and restrict misuse.
A successful login to your genuine account afterward doesn’t prove nobody else obtained access. Review the incident with the bank even if ordinary banking still works.
If money moved, preserve the real transaction details. A screenshot of the original email can’t replace the bank’s record of what was authorized or transferred.
Checks That Are Specific to Banco CTT
Use the genuine bank’s access route
Start from the app you already use or the bank’s established website. Avoid sponsored search results and contact links supplied inside the warning.
The bank’s official security page explains its access precautions and lists support contact information. Use it independently when unsure.
A sender address that appears correct is still not the only check. Consider the requested action and destination together instead of trusting the display name.
A partial-password request isn’t a universal authenticity test
Banco CTT currently states that genuine Homebanking asks for three password characters, with the same positions requested again after an unsuccessful attempt.
A demand for the complete password conflicts with that guidance. However, copying a partial-password format wouldn’t make an impostor’s page genuine either.
Use the bank’s actual site and current guidance. Don’t turn a remembered login detail into permission to enter secrets anywhere that imitates it.
Real customer-data updates have separate routes
The bank publishes genuine ways to update personal information. That makes it important to reject the fraudulent email without dismissing all record-maintenance requests.
Open the account yourself or ask a genuine branch or support representative how your situation should be handled. Don’t use the suspicious button as a shortcut.
You can resolve a real administrative issue while refusing the fake notice. Those decisions don’t contradict one another.
If You Really Need to Update Your Details
Don’t let the false notice prevent a genuine update. Use the bank’s own published process, starting from an app or website you opened independently.
A real change of address or identity document can require attention. The question is not whether banks maintain records, but who is directing this particular request.
Ask support which information is needed and where it should be provided. Don’t email confidential documents to an address taken from the suspicious notice.
Keep a record of any verified instruction and case reference. If another message follows, compare it with what the genuine bank told you.
If you’re helping someone else, let the account holder contact the bank through its proper process. Don’t collect their passwords to investigate on their behalf.
What to Do if You Have Fallen Victim to This Scam
For exposed banking access, contact the bank before spending time investigating the sender. Your priority is protecting the account and any pending operations.
Its published Portuguese support number is 212 697 144. Confirm current contact information through the genuine site or your own banking materials.
Explain what happened plainly: the email received, the page visited, information entered, and any notification or payment approved. Don’t guess when you’re uncertain.
Stop using the verification page. Close it and reject unrequested approvals. Don’t provide another code because the site says the previous one failed.
If someone calls about the incident, end the call and initiate contact through the bank’s known channel. A familiar incoming number can be misleading.
Ask Banco CTT to assess the exposure. State whether you provided a login identifier, password characters, full password, operation code, or device access.
Let the bank determine what access should be blocked, replaced, or reviewed. Follow its genuine recovery process rather than another link from the sender.
Identify any operation you approved. Keep the approval message and tell the bank exactly what it described.
A transfer, a new access method, and a profile change can require different responses. Ask about pending operations rather than only checking the visible balance.
Report money that actually moved. Provide the amount, destination, timing, and transaction reference from the real account record.
Explain accurately whether you approved it and what you were told. Request available recovery or dispute options without assuming a refund is guaranteed.
Secure other exposed access. If a password was reused, change it on the affected services through their genuine apps or websites.
Inspect the email account used for banking notifications if its access was disclosed too. Unauthorized recovery changes can affect more than one service.
Inspect the device if software was involved. Stop using an untrusted application or remote-access session and tell the bank about it.
Use Malwarebytes and the correct device section below when risky downloads or installation occurred. Coordinate with IT on a work-managed device.
AdGuard offers an additional layer against some malicious ads and sites. It cannot reverse a bank operation or certify that account access is safe.
Keep original evidence. Save the email with its headers, the destination address, any downloaded filename, and banking notifications.
Share this privately with the bank or appropriate authority. Remove customer numbers, codes, identity details, and financial information before posting a warning publicly.
Check the account after recovery. Review genuine transactions, registered devices, contact information, and security notifications as the bank recommends.
Report new discrepancies promptly. Don’t move funds to a supposedly protected account because an unsolicited caller says further fraud is underway.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
If the Follow-Up Caller Says They Are Protecting Your Money
A call arriving after a frightening bank email can feel reassuring. The caller appears to understand the problem before you’ve explained everything.
That knowledge is not enough. Someone involved in an earlier deception may already know the story, or may simply be using a common banking scenario.
Don’t read operation codes aloud to prove you’re the customer. The bank’s published precautions specifically warn against sharing them with callers.
Reject requests to install a protection application, share your screen, or make a transfer during the call. End it and contact the bank yourself.
If a real support case exists, give its reference through the verified channel. A genuine institution can look up its own records without your trusting an inbound claim.
Keep other authorized account holders informed. They may receive another message or approval request while you’re addressing the first incident.
For customers helping a family member, focus on stopping further instructions rather than blame. A calm conversation makes it easier to establish the actual sequence.
The goal is to return decisions to the legitimate bank and account holder, away from a stranger supplying both the emergency and its supposed solution.
Frequently Asked Questions
Is the Banco CTT 24-hour verification email genuine?
The described notice is a bank-impersonation phishing message. Don’t follow its login link; confirm any real account issue independently.
Is Banco CTT itself a scam?
No. It is the bank whose identity is being abused. Keep the warning attached to the fraudulent communication, not the legitimate institution.
Does a form asking for three characters prove it’s real?
No. Although the bank describes that genuine login format, an impostor can copy a form. The authentic access route remains essential.
What if I only clicked and entered nothing?
Close the page and check whether anything downloaded or any permission was granted. Clicking alone doesn’t establish credential theft or malware execution.
Should I send a code to cancel a restriction?
Don’t share operation codes with an unsolicited contact. Read the actual authorization details and ask the genuine bank about any unexpected request.
Can malware scanning recover a fraudulent bank transfer?
No. Scanning addresses the device. The bank must assess exposed access, pending operations, and any payment-recovery options separately.
The Bottom Line
Don’t use the Banco CTT email scam’s verification route. Open the established app or contact the real bank rather than obeying its deadline.
If you shared credentials, codes, or payment approval, report the details immediately. Handle any software exposure separately, without trusting a follow-up caller’s instructions.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.