

A refund approval is the kind of email you want to find after a frustrating card dispute. This Wells Fargo message promises just that.
Before you sign anything, take a closer look at what the notice is asking you to do.
Overview
An approved refund becomes a reason to sign in
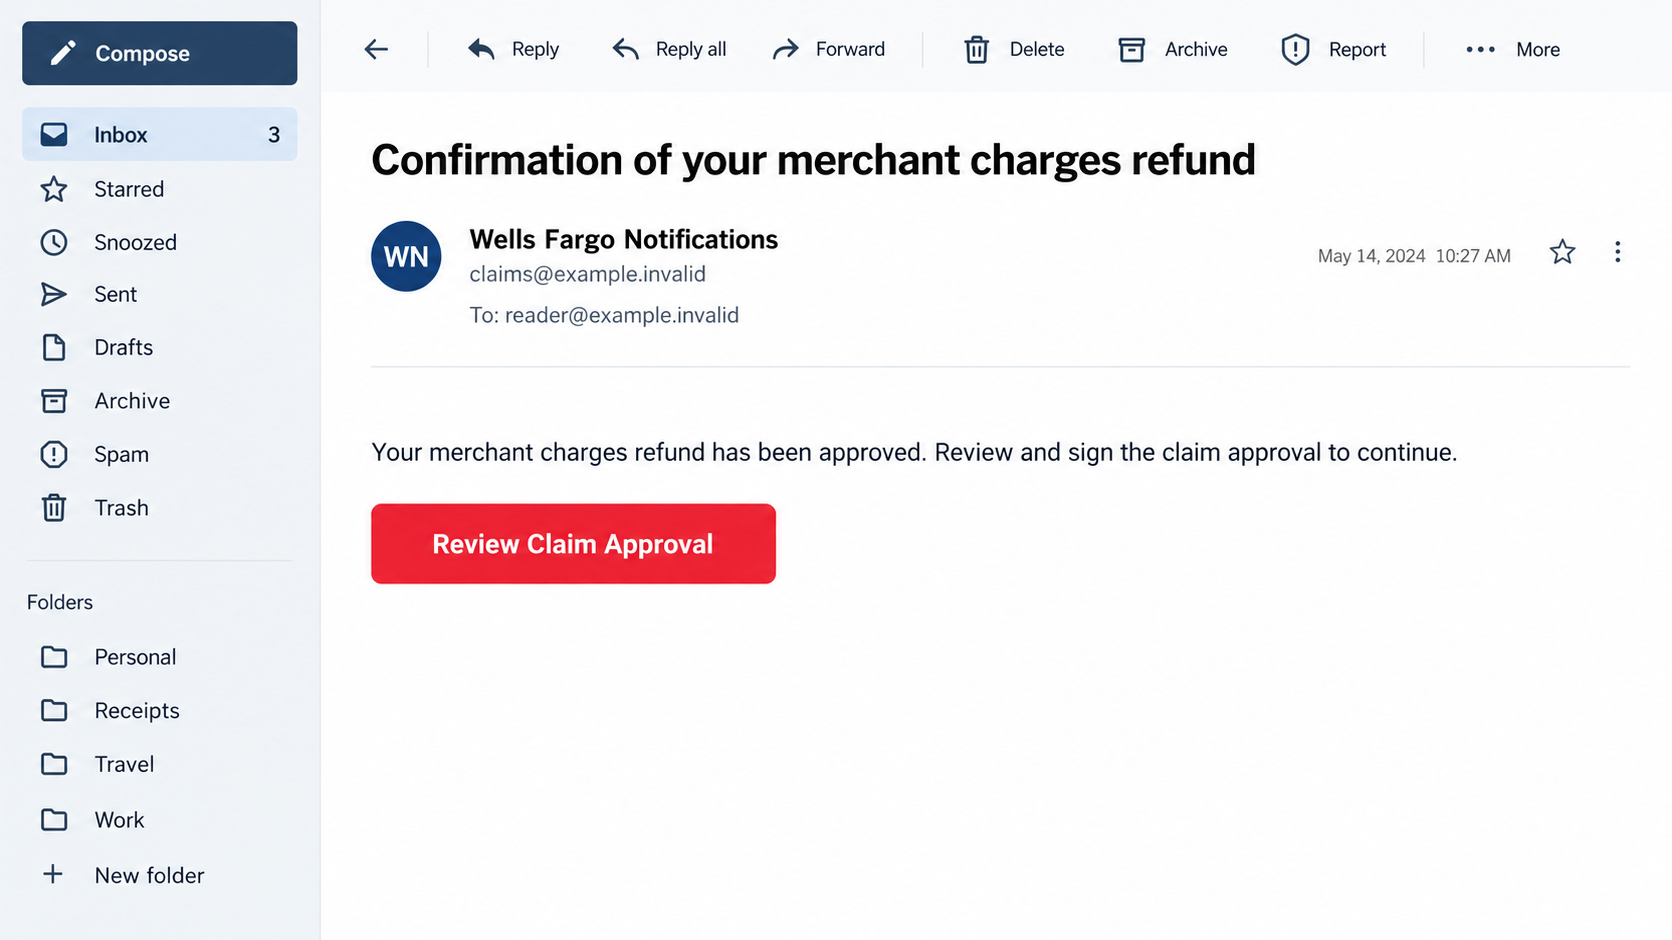
The Wells Fargo merchant charges refund email scam dresses a credential request as welcome news. Its reported message says an investigation has finished and reimbursement is approved.
A button labeled Review Claim Approval invites the recipient to review and sign. The documented destination imitates Wells Fargo’s online banking sign-on.
Wells Fargo is the impersonated bank, not the operator of this phishing message. The supposed approval does not establish that the bank investigated a real transaction.
The useful question is whether the notice matches a dispute you can confirm independently. A convincing presentation cannot answer that for you.
Why this notice deserves a different kind of check
Many bank scams threaten to close an account. This one offers resolution, appealing to someone who may already be waiting for money to come back.
That makes the requested signature feel like routine administration rather than a new financial decision. You may think the hard part is already over.
- The message claims merchant charges have been refunded after an investigation.
- It makes a linked approval the next action.
- The bank-branded destination seeks access credentials.
- The actual claim should be checked through your usual banking route.
A different refund-themed scam impersonates Bank of America. Its details should not be assumed to apply here simply because the central promise sounds similar.
What this warning does and does not establish
The reported email and sign-on lure establish the phishing pattern. They do not tell us whether a particular reader has an open dispute or a genuine refund pending.
No bank account was accessed to test the message. There is also no established malware payload attached to this particular refund notice.
The email illustration uses invented addresses and interface details. Its date is not a campaign date, and its appearance is not proof of a specific recipient’s message.
You can check your account without following the disputed link. That preserves your ability to deal with any real banking problem while avoiding the counterfeit route.
A Refund Notice Is Not the Refund Itself
Consider the difference between receiving an email and receiving a credit. An email describes an event. Your bank’s own records show whether that event occurred.
If you recently questioned a charge, a timely-looking message can feel personal. A mass-mailed scam can still arrive during a real dispute by coincidence.
Even a reference to your name or a familiar merchant does not settle the matter. Such information may come from earlier correspondence or unrelated exposure.
There is no evidence identifying how every recipient was selected in this campaign. You do not need that answer before refusing the link.
Open the banking app you already use. Look for the original transaction, any dispute record and messages attached to it, rather than searching only for the email’s wording.
A provisional credit, a merchant refund and a final dispute decision can mean different things. Ask the bank which applies before treating the matter as resolved.
The scam’s approval wording cannot change those distinctions. It also cannot require you to disclose credentials to a separate site to preserve your rights.
When the account record is unclear, use the contact information on your card or statement. Do not let the email supply both the problem and the verifier.
How the Wells Fargo Merchant Charges Refund Email Scam Works
Step 1: Lead With the Relief of an Approved Claim
The opening presents a completed investigation into unrecognized merchant charges. Instead of demanding an explanation, the sender appears to offer the outcome a customer would hope for.
This shifts your attention toward finishing the process. You may be less likely to question the sender when the apparent news is favorable.
The phrase merchant charges also sounds broad enough to fit many purchases. A reader may mentally supply the store, amount or dispute the email never actually verifies.
Pause at that gap. Match the claim against something you initiated, not something you can imagine having forgotten.
For a shared household account, check with the authorized person who normally handles disputes. For a business account, ask the employee responsible through established internal channels.
Neither conversation requires forwarding an active phishing button. Describe the subject and request a check in the genuine account instead.
Step 2: Make the Button Feel Like Harmless Paperwork
The invitation to review and sign suggests one remaining administrative step. It borrows the familiarity of legitimate electronic documents without establishing who controls the destination.
Review Claim Approval is a label, not a security guarantee. A sender can put those words on a link pointing anywhere.
A footer mentioning the bank’s website can be copied just as easily. Its presence does not authenticate the button above it.
On a desktop, examining a link preview can reveal a mismatch. On a phone, do not tap through merely because the full address is hard to inspect.
There is no need to become a domain specialist while worried about a refund. Leaving the email and opening the bank independently removes this uncertainty.
A closed or broken phishing link is not evidence that the refund became legitimate. Campaign pages can disappear while copies of the message keep circulating.
Step 3: Substitute a Counterfeit Banking Sign-On
The documented lure leads to a page made to resemble Wells Fargo authentication. The sensitive moment is entering information on that untrusted page.
In a credential-harvesting setup, the form can send submitted details to someone other than the bank. An error afterward does not undo that disclosure.
A page may ask you to try again, return you elsewhere or stop responding. None of those outcomes proves the first submission failed to reach its operator.
Do not test the form with your password, even if you intend to change it afterward. You would be giving the attacker an opportunity in the meantime.
Additional questions about a card, identity or verification code should be treated as further exposure if answered. Their appearance is not confirmed for every version here.
The response should follow what you actually supplied, not a guess that every phishing page collects the same fields.
Step 4: Turn Stolen Access Into Further Requests
Stolen banking credentials can support attempted account access. Whether that succeeds depends on the account’s protections, any additional verification and the bank’s fraud controls.
The attacker may also reuse a disclosed password elsewhere. A banking password shared with your email account creates a second problem, even before money moves.
A follow-up caller could exploit the same refund story to request a code or transfer. That is a possible escalation, not a recorded step in every recipient’s experience.
Do not move funds into a supposedly safe account to complete the refund. Do not install remote-control software so someone can help you sign an approval.
Tell the real bank what happened, including any codes or transfers. Precise information helps it distinguish an attempted login from an unauthorized payment already in progress.
Waiting for the counterfeit page to explain itself gives you no useful protection. The bank can review the actual account; the sender cannot be trusted to do so.
Check the Sender Without Handing It Another Opportunity
Display names are only the envelope’s front label
Expand the sender details if your email app permits it. The friendly name may say Wells Fargo while the underlying address belongs to someone else.
A mismatch is a warning. An address that looks familiar is not a final clearance, because spoofing and compromised mailboxes complicate appearances.
Save the original email rather than copying only its body. Your provider or security team may need headers that disappear when you paste text into another message.
A real claim needs a real banking record
Make a short note of the claim you actually filed, its date and the disputed transaction. Then compare those details through the genuine bank interface.
If the email names no amount or transaction, do not fill the silence with assumptions. Ask the bank to identify the relevant case before discussing any approval.
You can find Wells Fargo’s own advice on its phishing reporting page, including how to report a suspicious notice.
One protective action should not create a payment
A refund verification should not involve buying gift cards, sending cryptocurrency or transferring savings to a new destination supplied by a caller.
If someone adds those instructions after the email, end that interaction. Explain the new demand to the bank through an independently obtained contact route.
Keep any transfer confirmation, recipient account details and timestamps. Evidence of a completed payment matters more to recovery than the sender’s polished signature.
If a Real Refund Is Still Missing
A delayed reimbursement can make a second approval request seem plausible. Keep your existing case open with the bank rather than starting over through the email.
Ask whether the credit has been issued, which account should receive it and whether additional information is genuinely required. Obtain those answers through the verified case.
If the original purchase involved a merchant refund, retain the merchant’s confirmation too. The merchant’s promise and the bank’s account entry may refer to different stages.
Write down the amount, expected timing and reference number supplied by the legitimate organization. Those details help you follow up without depending on later unsolicited messages.
Do not send another payment to release an existing reimbursement. If someone says the bank accidentally refunded too much, stop and ask the real bank to review it.
A caller may show you a changed balance or an edited screen during remote access. A screen shown by an unverified helper is not an independent banking record.
For reimbursement to a business account, involve the person responsible for reconciliation. That prevents one employee from approving a new destination based on a plausible email alone.
Keep any legitimate dispute deadline in view. Reporting the phishing attempt and pursuing the real refund can proceed together, without using the suspect link.
What to Do if You Have Fallen Victim to This Scam
Stop the approval process. Close the linked page and stop replying. If you only read the email, report it as phishing without treating receipt as device infection.
Keep a copy first if you need to send it to your bank or workplace security team. Do not revisit the link for a better screenshot.
Contact Wells Fargo about disclosed information. Use your card’s printed number, your established app or the bank’s genuine fraud-reporting page.
Say whether you entered a username, password, card number, personal details or a one-time code. Mention any unexpected sign-in notification that followed.
Let the bank determine which account restrictions or credential changes are needed. Do not accept instructions from a caller whose identity rests only on this email.
Replace compromised credentials safely. Use a trusted device and the actual banking service. Secure other accounts where you reused the exposed password.
Protect your mailbox as well if its credentials were shared. Review recovery settings and active sessions rather than assuming one password change resolves every access route.
Identify real transactions promptly. Review activity with the bank and flag anything you did not authorize. Ask about available dispute or recall options.
Describe an attacker-directed transfer accurately, even if you initiated it while deceived. Recovery depends on circumstances, and no article can guarantee the bank’s decision.
Address device exposure if it occurred. If the page prompted software installation, an unexpected download ran or remote access was allowed, stop using that device for banking.
Arrange a Malwarebytes scan or help from your security team. AdGuard can reduce malicious advertising exposure, but it cannot retrieve a submitted password or reverse a payment.
The scan component below concerns device cleanup only. Banking restrictions, account recovery and payment reports must still be handled separately.
Document and report the impersonation. Wells Fargo lists reportphish@wellsfargo.com for suspicious messages. Its reporting guidance distinguishes merely receiving a notice from responding to one.
Record your bank case number and any financial loss. Refuse anyone promising guaranteed recovery in exchange for a release fee, another code or remote access.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is the merchant charges refund email really from Wells Fargo?
The notice described here impersonates Wells Fargo. Confirm an actual refund in the bank’s app or with the bank, not through its approval button.
What if I genuinely filed a dispute recently?
That makes verification more important, not the link safer. Ask the bank to match the notice to your existing claim using a trusted contact method.
Does the email prove money was refunded?
No. A message can claim any result. Check the transaction history and ask whether any credit is provisional, final or a separate merchant reimbursement.
Can my password be stolen if the page showed an error?
Yes, submitted information may already have reached the operator. Report the disclosure without waiting for evidence that someone successfully entered your account.
Should I scan after simply reading the notice?
Reading this phishing claim alone does not establish malware infection. Device cleanup becomes relevant if additional behavior, downloads, installation or remote access creates a software concern.
Can I get back money sent after the email?
Contact the bank immediately with the payment record. Options depend on the payment and circumstances. Ignore unsolicited recovery offers claiming they can guarantee reimbursement.
The Bottom Line
Do not sign in through this Wells Fargo merchant charges refund email. The approval story leads toward a counterfeit banking login, not a trustworthy claim check.
If you already shared details, contact the actual bank now. Verify genuine transactions, secure exposed access and handle any software installation as a separate cleanup issue.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.