

A signature notice says an industrial estate project is waiting on executive approval. Funding and compliance appear to depend on a quick response.
Its formal language can make an unfamiliar project feel like unfinished business. Before treating the deadline as yours, examine the request behind it.
Overview
The message invents a high-pressure executive authorization
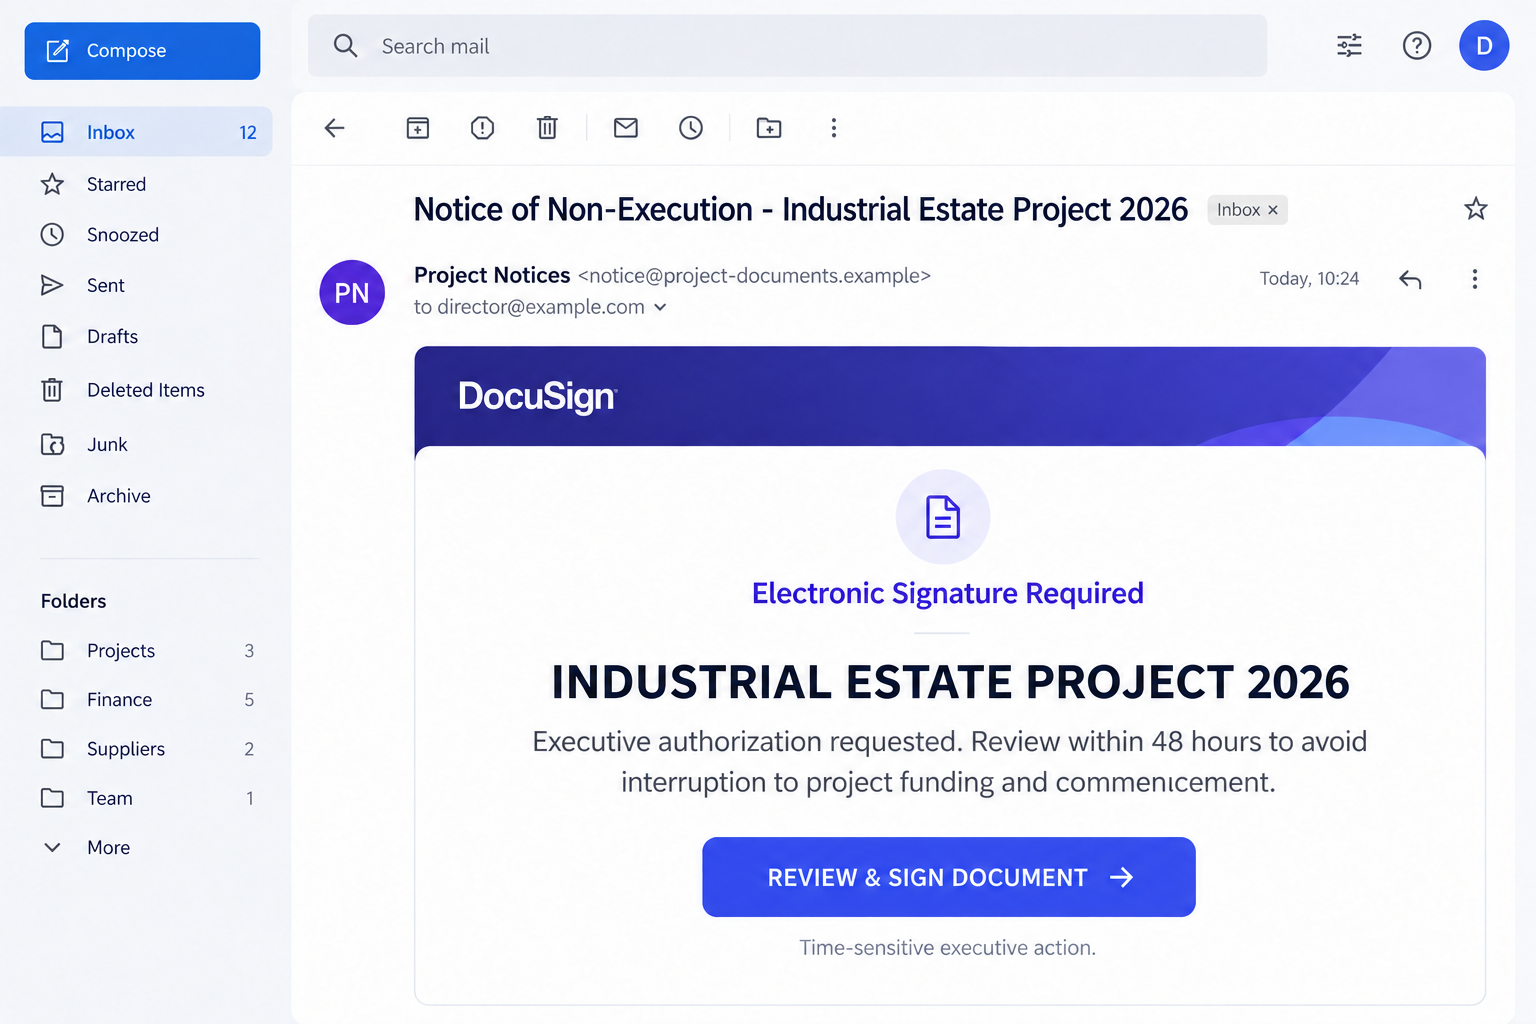
The Docusign Industrial Estate Project scam presents a supposed public-works authorization that must be signed within 48 hours.
The reported subject is “Notice of Non-Execution – Industrial Estate Project 2026.” The body invokes compliance, funding, and project commencement.
Those references make the request sound consequential without establishing any genuine project relationship. The email is a false signature notice, not verified correspondence from Docusign.
Its government and funding language should be read as the sender’s claims. They do not demonstrate approval by an agency or involvement by a real executive.
The image uses an illustrative email layout and fictional contacts. It is not a genuine envelope, legal instrument, or record of a recipient’s obligations.
The reported link delivers a program disguised as a document
The dangerous detail is not just the deadline. The reported linked page was unavailable, yet a malicious executable was still downloaded from the route.
An executable is a program, not merely a document waiting for a signature. A document-themed presentation can hide that important change.
The final purpose of the file was not established. Do not assume a named ransomware family, password stealer, or espionage operation from the email’s dramatic theme.
No file was downloaded or executed for this article. The safe response does not require running the program to see what it does.
Receiving, clicking, downloading, and executing are different exposure levels. Establish which happened before deciding how to contain the incident.
A legitimate signature workflow does not make this message authentic
Docusign is a genuine service that can be impersonated or abused. Its branding does not validate an unfamiliar project’s demands.
Its warning about deceptive document downloads says suspicious envelopes should not require extra viewing software and recommends independent sender verification.
- Confirm the project and requester through your organization’s established records.
- Do not install a program to meet the email’s signature deadline.
- Preserve the message and tell IT if a file was opened.
- Keep genuine contracting questions separate from device-security response.
If you have no connection to the named project, that is a reason to stop, not to sign first and ask questions afterward.
Why This Notice Can Create So Much Pressure
It borrows the language of internal responsibility
Words about executive authority, statutory reporting, and funding suggest a process already underway. The reader is positioned as the person delaying it.
That can be persuasive in an organization where important approvals genuinely arrive through electronic-signature systems.
A project manager may worry about missing something a colleague arranged. An executive assistant may wonder whether the request belongs in a queue they inherited.
The way to answer those questions is through existing project contacts and records. The message cannot establish its own place in your workflow.
A short deadline discourages asking the right people
The 48-hour window makes consultation feel risky. The notice suggests that delay itself could trigger consequences.
But the sender does not acquire authority by printing a deadline. A genuine obligation should be traceable to an identifiable relationship and appropriate documentation.
If there is a real contracting question, send it to your organization’s project owner or legal team through normal channels.
Do not treat this security article as an assessment of unrelated contracts. The warning is about the fabricated message and dangerous download route described here.
A failed page can hide a successful download
People often assume a page error means nothing happened. A download can start before the destination fails to display useful content.
That does not mean a downloaded program automatically ran. It means the page’s appearance is not enough to reconstruct the exposure.
Check your browser’s download history without opening the file. Tell IT what appears there and whether you launched it.
Do not repeatedly select the signing button to make the missing document load. Each retry can add another copy or another confusing event.
How the Docusign Industrial Estate Project Scam Works
Step 1: A non-execution notice suggests an overdue responsibility
The subject presents the issue as a failure to execute an authorization. That is different from a neutral invitation to review a new document.
It encourages the reader to believe an existing duty has been missed. Formal wording does some of the work that a real relationship would otherwise do.
Pause and identify the project owner. Do you recognize the organization, requester, and document purpose from independent records?
A title or personal greeting does not answer those questions. Both can appear in a message from someone outside the project.
Step 2: The body links your signature to funding and compliance
The message describes an industrial estate initiative and says executive authorization must precede commencement. It adds consequences for failing to sign quickly.
The combined pressure can make downloading a document feel like the least risky option. That is the decision the lure is trying to steer.
Do not accept a compliance story without checking who issued it. If the email is unexpected, contact a known project colleague separately.
A stranger’s document should not override your organization’s approval process, software policy, or verification requirements.
Keep any meaningful deadline in the internal report so the right team can assess it without using the suspicious route.
Step 3: The review-and-sign button moves you to an external route
The visible action is a request to review and sign. The destination, however, can behave differently from what that label suggests.
A copied Docusign-style card does not establish where the link leads. The message’s appearance and the destination’s ownership are separate questions.
Docusign’s Safety Center provides reporting and independent document-access guidance. Use an established route rather than trusting a button in an unexpected notice.
A document identifier can help a provider investigate, but it does not by itself prove the underlying project or request is legitimate.
For workplace mail, the safest inspection route may be the organization’s security-reporting feature, not a personal attempt to follow the link.
Step 4: A disguised executable substitutes for the expected document
The reported route downloaded a malicious executable even while its page was unavailable. The expected signature document had become a program.
An icon or familiar-looking name can distract from a file’s actual type. Do not decide what it is from appearance alone.
Check download details without launching it. A file described as an application deserves a different decision from reading a document in a trusted viewer.
Do not rename the extension or open it in another program to make it safe. Renaming does not change the content.
If a warning appears, do not bypass it because the email’s deadline is approaching. Report the warning and the file to the appropriate team.
Step 5: Execution changes the response from message handling to containment
If the program ran, the concern extends beyond the false authorization. Security responders need to assess what executed and what activity followed.
The unknown final payload is a reason for investigation, not a reason to invent the most alarming outcome.
A blank window or apparent failure does not prove the program did nothing. Record the launch time and stop testing it.
Containment and trusted malware assessment should come before resuming sensitive work. Account recovery may also be needed depending on the findings.
If it downloaded but never ran, say that clearly. Do not let the label “email virus” erase the distinction between receipt and execution.
Project, Document, and Download Checks
Check the project with someone you already know
Use your existing contact list or internal directory. Do not use a new number or address supplied by the suspicious notice.
Ask what document is expected, who requested it, and where the approved copy belongs. Avoid forwarding a live dangerous link to every project participant.
If a real person says they sent it, still clarify the unexpected program download. Their account could have been abused, or the link could differ.
Verification should resolve the mismatch, not merely produce another instruction to hurry.
Inspect the download record without opening the program
Record the filename, displayed type, source address, and time when available. These details help IT locate the event.
Do not upload a work-related sample to a public scanning site without authorization. A suspicious package may still include confidential information.
Preserve the original message and let responders specify evidence collection. Manually moving, deleting, or repeatedly copying files can obscure the sequence they need.
Check which device received the download. A link first opened on one computer may have been retried on another, creating more than one exposure to assess.
Tell responders whether the file was copied into a shared drive or sent to a colleague. That helps locate additional copies without assuming they executed.
If a browser warning blocked the download, preserve the warning text. Do not temporarily disable protection to retrieve the file for analysis.
If you do not know whether it ran, say so. Investigators can examine available records; guessing that a brief click did nothing can delay useful containment.
Separate technical cleanup from contract decisions
Removing malware does not validate a project request. Equally, confirming an unrelated real project does not make this particular download trustworthy.
Keep the business owner informed if the email disrupted an approval. They can arrange a verified document route without asking you to reopen the lure.
An incident note should state which steps occurred and which remain uncertain. Clear facts are more helpful than an assumed diagnosis.
If several employees received the same request, use one coordinated security report. Let IT search for related deliveries rather than encouraging colleagues to compare live links.
Keep the financial or project team informed through a separate conversation. They may need to pause a related approval while the document route is clarified.
A real project owner can arrange another verified way to review documents. That should not require restoring the suspicious file from quarantine.
If someone already signed unrelated genuine paperwork, keep those records separate. The false email does not by itself determine the status of another agreement.
What to Do if You Have Fallen Victim to This Scam
Stop the signature process. Do not run the downloaded file or retry the link. Preserve the email and any browser download record.
If you only received the notice, report it through your organization’s approved channel. Receiving a threat about project funding does not establish a real funding problem.
Tell IT exactly what happened. Distinguish reading, clicking, downloading, and executing. Include approximate times and the affected work device.
If the program ran, stop sensitive activity. Follow your incident procedure, including network isolation where appropriate, rather than trying several online repair utilities.
Use a trusted investigation and removal process. Updated Malwarebytes can help detect malicious software. Preserve scan findings and failed-removal messages.
A scanner cannot establish the legitimacy of a contract or guarantee that no later access occurred. Managed systems may require coordinated endpoint investigation.
Review wider device and account exposure. Responders may need process, network, and sign-in records around the launch time.
Microsoft’s endpoint-response guidance describes isolation and investigation options for managed environments. Use those tools through the responsible team.
Recover affected logins from a trusted device. If credentials were entered or exposure is suspected after execution, follow provider and IT instructions for replacement and session review.
Do not keep signing in on the questionable machine while waiting for cleanup. A fresh password should not be entered into an environment still under assessment.
Confirm the real business request separately. Ask the project owner or appropriate legal contact to establish whether any legitimate authorization is outstanding.
Use a newly verified document route. Do not let a reassuring reply from the suspicious sender reopen the same download chain.
Reduce future delivery risks. Keep software current, report suspicious signing notices, and consider AdGuard for malicious-ad exposure during browsing.
Advertising protection does not replace attachment controls or document verification. Follow-up “project recovery” offers should be checked through the same established business contacts.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is the Industrial Estate Project notice an official Docusign request?
The campaign described here is a false notice using Docusign branding. Verify any genuine envelope and its sender independently.
Does the 48-hour deadline prove a legal obligation?
No. A deadline printed in this fabricated email does not establish a valid obligation. Ask your organization about any separate, genuine contract concerns.
Why did a program download when I expected a document?
The reported route disguised an executable as the expected material. Do not launch it to review or sign the supposed authorization.
Can a broken webpage still download something?
Yes. A download may start even if the page fails to display properly. Review the browser’s download record without opening the file.
Is the payload definitely ransomware?
That was not established. The file is reported as malicious, but its final function should not be assigned a specific malware label without evidence.
What if I downloaded it but never ran it?
Do not execute it now. Report the download and let IT handle it safely; downloading and executing are not the same event.
The Bottom Line
Do not run a program to satisfy the Docusign Industrial Estate Project scam’s signature demand. Its compliance language does not authenticate the request.
Verify the project through known contacts. If the program executed, contain the device, report the sequence, and complete trusted removal and account checks.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.