


An app promises familiar features with a few extras. After installation, it asks for access that seems unrelated to what you wanted.
Arsink RAT shows why that moment deserves attention. The important clues are not always on the home screen or inside a dramatic warning.
Overview
Arsink is Android malware disguised as something useful
Arsink RAT is a remote-access trojan targeting Android. Reported campaigns distribute counterfeit APK packages through messages and file-sharing routes while borrowing familiar app branding.
An APK is an Android installation package. The extension describes a format, not whether the software is trustworthy.
The counterfeit may be offered as an enhanced or premium version. Its recognizable name is meant to encourage installation without the genuine publisher’s involvement.
This does not make the real applications being impersonated malicious. A copied icon and product name can belong to software distributed by someone else.
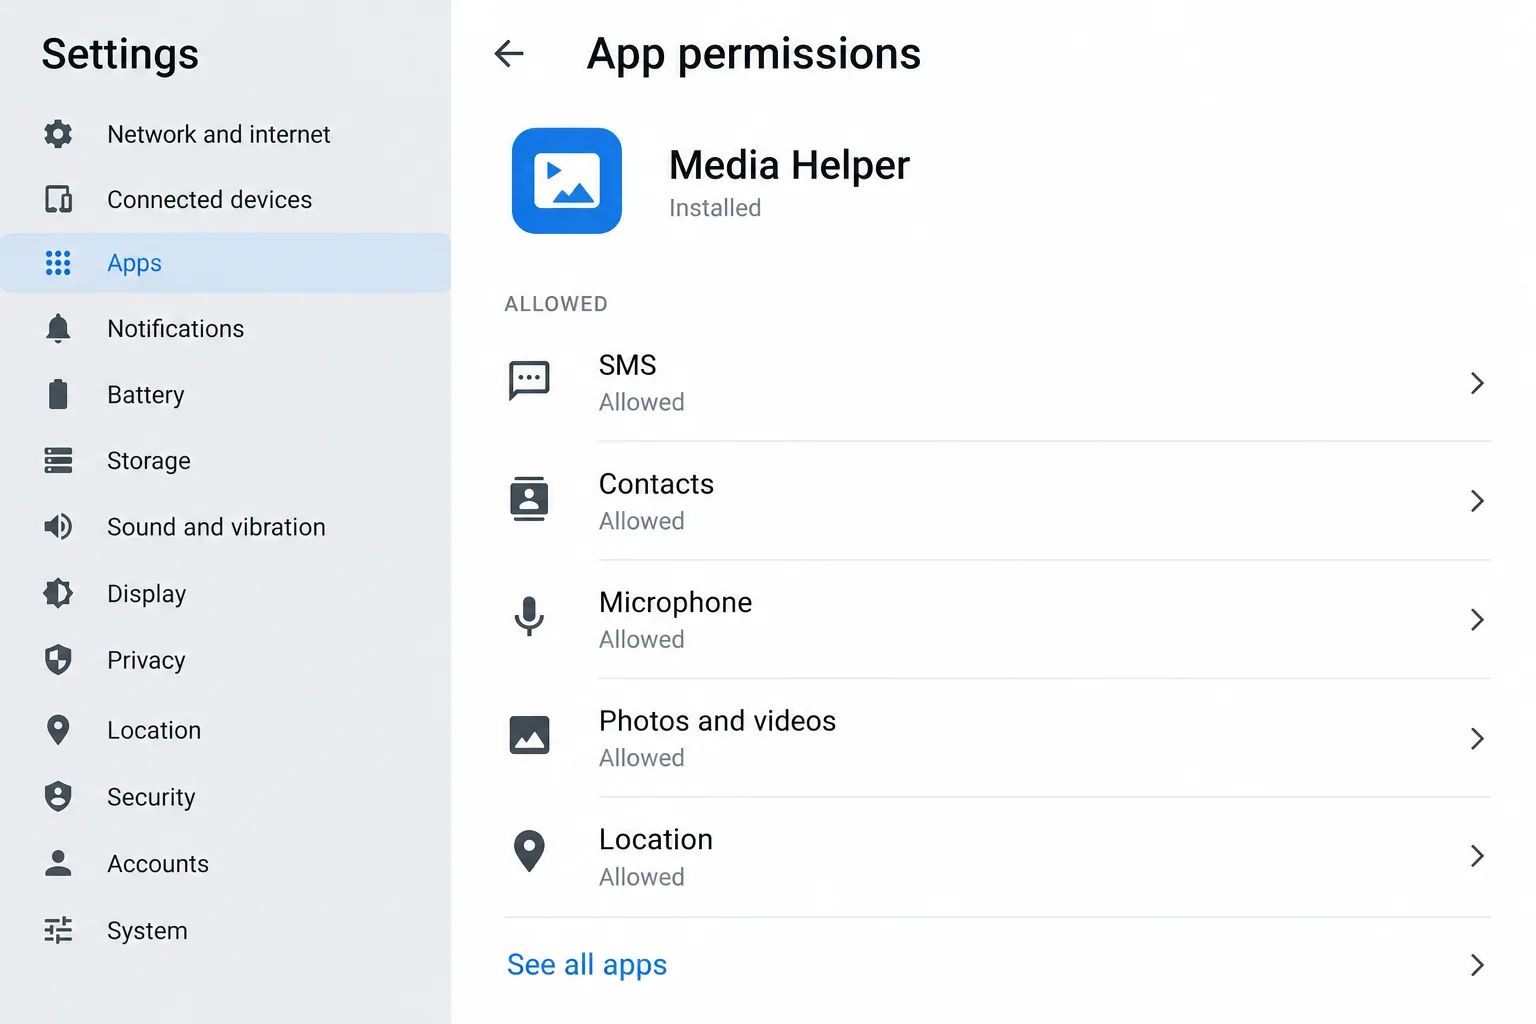
The image above shows a fictional app’s permissions. It is an illustration, not a screenshot of a real infection or a specific Arsink build.
Sensitive permissions can turn an app into a surveillance problem
Published analysis describes Arsink collecting information such as SMS, contacts, recordings, and files. Variants can also receive remote instructions and conceal their launcher icon.
The consequences depend on the installed build, Android version, granted access, and subsequent activity. An article cannot diagnose those details for an individual device.
Battery drain or slow performance alone is not an Arsink identification. Look at installation history and reliable security findings instead of guessing from common symptoms.
No malicious package was installed for this guide. It explains the documented threat and a practical response without claiming a reader’s data was stolen.
Removal must include account and data considerations
Deleting a suspicious app can stop an immediate problem, but it cannot recall information that already left the device.
If messages or account access may have been exposed, review those accounts separately from the Android cleanup.
- Stop using the suspect installation for sensitive activity.
- Identify the downloaded app through Android Settings, not its home-screen icon alone.
- Keep Play Protect and device security updates enabled.
- Use Android-specific removal instructions and trusted support.
If the device is managed by an employer, involve its IT team before wiping it or changing organizational access settings.
How a Familiar App Name Can Hide the Wrong Package
The download source matters more than the name on the icon
A message can offer a modified app with features the genuine version supposedly lacks. That explanation makes leaving normal installation routes seem intentional.
But the person supplying the package can choose its visible name. A familiar label does not connect it with the original developer.
Consider a link shared in a group where people exchange application tips. The fact that others discussed it does not establish what the package contains.
Use the publisher’s established route or an approved organizational catalog. Do not turn off warnings simply because a promoter says the app is misunderstood.
A permission request is an access decision
Some legitimate applications need sensitive permissions. The useful question is whether the access matches a feature you deliberately chose.
A request to read messages should have a clear purpose. A long list of unrelated permissions deserves scrutiny before you accept it.
Do not grant everything just to make an unfamiliar app start. If the promised function remains unavailable without unexplained access, stop rather than keep escalating permissions.
Permission names and menus vary by Android version and manufacturer. Follow the controls actually present on your device instead of copying a mismatched screenshot.
Removing an icon is not removing an application
A home-screen shortcut can disappear while an application remains installed. The installed-app list in Settings is the more useful place to check.
Do not assume a missing icon proves stealth malware either. Launchers and user settings can also affect what appears on the home screen.
Connect the observation with the package you installed and any security alert. Preserve enough information for support before making broad changes.
Never uninstall system components at random because their names sound unfamiliar. A technical responder can help distinguish the suspect package from normal Android services.
How the Arsink RAT Infection Chain Works
Step 1: A counterfeit app is offered outside the expected publisher route
The documented campaign uses impersonated applications and socially shared downloads. The visitor is persuaded to install a package rather than merely view a webpage.
This distinction is important. Seeing a link in a chat does not mean the app is installed, and downloading does not necessarily complete installation.
Record what happened: where the link arrived, which package downloaded, and whether Android’s installation process completed.
If you stopped at a warning, do not bypass it now to see the next screen. The installation attempt can be reported without completing it.
An unexpected request to allow installations from a browser or file manager is a reason to reconsider the source.
Step 2: The installed application asks for sensitive access
After installation, the permission decisions affect what the application can reach. Different data types may be controlled through different Android settings.
Read the actual request instead of the app’s explanation alone. “Required for protection” is not a complete account of why it needs your messages or microphone.
Some special access is separate from ordinary permissions. If a newly installed app asks you to enable additional services, understand the effect before proceeding.
This guide does not assume every Arsink sample uses every special permission. Check what is present on the actual device.
For a work installation, ask IT whether the software and requested access were approved. Do not interpret a promoter’s instructions as company policy.
Step 3: Background activity can expose information without a visible document
Arsink research describes background collection and abuse of legitimate cloud infrastructure. A trusted service name in network traffic does not authenticate the app sending data.
The ordinary user may not see a file leaving or a window opening. Lack of a dramatic symptom should not override a credible security finding.
Zimperium’s primary Arsink research explains the counterfeit-app campaign and its collection behavior. Its observations are not a current diagnosis of every Android device.
Do not disable essential cloud services indiscriminately. The problem is an abusive application and its access, not every legitimate use of the infrastructure.
On a managed device, responders may correlate app activity with account and network records. Give them the installation timeline rather than an assumed theft list.
Step 4: Cleaning the device does not settle every exposed account
Once an unwanted application is removed, account risks may remain. Information already disclosed cannot be made private again by uninstalling.
If authentication messages were potentially exposed, review relevant sign-ins and contact the account provider. Do not assume a one-time code remains usable indefinitely.
If private documents were involved, let the responsible person assess their sensitivity. A workplace may have reporting obligations and procedures beyond the owner’s personal cleanup.
Return to routine use only after device trust and important account access have been considered. Those are related tasks, not interchangeable ones.
Android Checks That Help Without Causing More Damage
Review installed apps and their permissions
Open Settings and the installed-app list. Compare recent additions with what you intended to install, using the package details where available.
Google’s privacy-dashboard guidance explains how supported Android versions show recent permission use and provide access controls.
A permission entry alone is not a malware verdict. Use it to understand the app’s reach and whether that access fits its purpose.
If an app cannot be removed, ask trusted support to assess why. Do not start altering device-administration or workplace-management controls without understanding them.
Use real security findings, not a browser alarm
A webpage telling you it found Arsink is not equivalent to a scan from an installed, trusted security product.
Record a genuine alert’s application name, detection label, and action taken. That context is more useful than matching every label exactly to this article.
Update security tools through their official distribution routes. Avoid a “special Arsink remover” offered by the same page that frightened you.
A completed scan should be considered alongside symptoms and installation history. No single result answers every question about data access or account misuse.
Plan a reset before starting one
If cleanup cannot be trusted, manufacturer-supported reset or recovery may be appropriate. Preserve essential personal data and necessary account-recovery information first.
Do not back up the suspicious APK as part of your restoration plan. Reinstall needed applications from approved sources instead of restoring everything blindly.
Make sure you can sign in afterward using a safe recovery route. Resetting before preparing can leave you locked out of legitimate accounts.
For company-managed equipment, let IT decide the collection and rebuild sequence. A personal reset can remove evidence or interfere with management.
What to Do for Arsink RAT Removal on Android
-
Limit sensitive use immediately. If a credible finding points to an installed malicious app, stop banking, handling confidential work, or changing important passwords on that device.
Use a separate trusted device to contact support. Disconnect the affected device where appropriate, while following workplace or manufacturer instructions for your situation.
-
Write down the exposure sequence. Record the app name, download source, approximate installation time, permissions granted, and any real detection alert.
Do not open the APK again to reproduce the installation. Keep potentially sensitive evidence private and let support specify a safe collection method.
-
Remove the untrusted application through Android controls. Use the installed-app settings or the security product’s recommended action. Ask the manufacturer or IT if removal is blocked.
Do not delete unrelated system files or disable broad security controls. Removing a home-screen shortcut alone does not establish that the application was uninstalled.
-
Run Android-appropriate security checks. Keep Play Protect enabled and install available security updates. Malwarebytes for Android can provide an additional malicious-app assessment.
Google’s unsafe-software guidance covers Play Protect, unwanted applications, account checks, and situations needing manufacturer help or a reset.
-
Secure important accounts from the clean device. Review recent sign-ins and recovery settings, and replace credentials where exposure or suspicious use warrants it.
If financial activity is unauthorized, contact the institution promptly. Preserve transaction details rather than assuming malware removal also disputes the payment.
-
Decide whether rebuilding is necessary. If the app returns, cannot be removed, or important trust questions remain, arrange a supported reset or professional assessment.
Restore reviewed data, update the system, and reinstall applications deliberately. Do not reintroduce the same modified package because it still promises a useful feature.
-
Prevent another unsafe installation. Review unnecessary install permissions for browsers and file managers. Consider AdGuard for malicious advertising, without treating it as an infection-removal tool.
Use the Android-specific illustrated procedure below. Windows and Mac installers do not apply to this Android threat.
Illustrated Android Steps for Removing Suspected Arsink
Use Android controls for the identified counterfeit package. On employer-managed equipment, or where surveillance creates personal-safety concerns, obtain trusted help before visible changes.
Step 1: Record the app and permissions before making changes
Note the package source, installation time, and real detection. Do not open the app again to reproduce a permission request or collect a better screenshot.
Step 2: Remove the identified untrusted app through Android Settings
Identify the actual unwanted application before removing it. Match the installation source, package details, timing, and detection; an unfamiliar name alone is not enough.
On a work-managed device, ask the administrator before changing management permissions. Do not disable a legitimate assistive service simply because it uses Accessibility.
Follow the controls shown, but select the application identified in your incident, not the sample app in the illustrations.
-
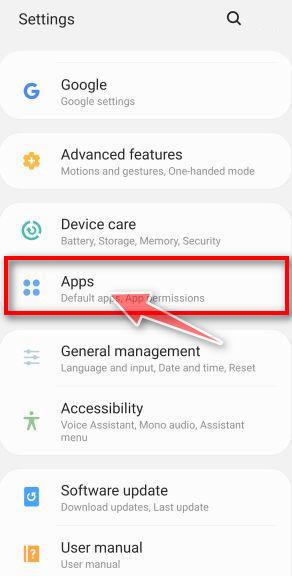
Open Android’s application settings.
Open Settings, then Apps or App management. Names differ by device maker; use the settings search if your version places the list elsewhere.
-
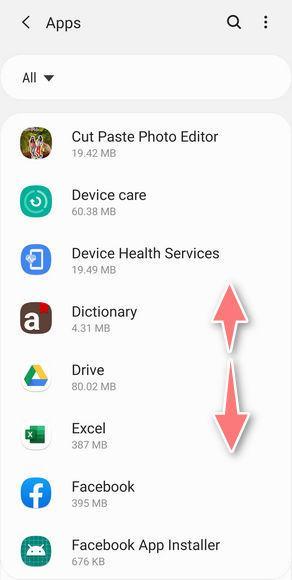
Locate the installation connected with the incident.
Review recently added applications and open the suspect app’s information page. Record its actual name and details before making changes.
-
Revoke inappropriate access if it obstructs removal.
For the identified malicious app, review Accessibility, device administrator access, notification access, and other permissions granted during setup. Restore the intended default messaging app if necessary.
If the app blocks settings or uninstalling, use your manufacturer’s Safe Mode instructions or trusted assistance. Do not remove an employer’s administrator profile without approval.
-
Uninstall the confirmed malicious app.
On its App info page, select Uninstall and confirm Android’s prompt. Opening App info is different from launching the suspect application.
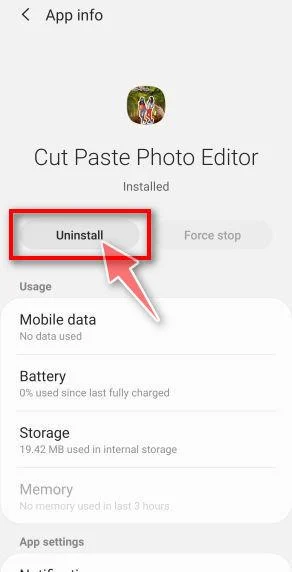
Confirm only the removal you intended. If the button is missing, disabled, or the app returns, stop and preserve the details for further help.
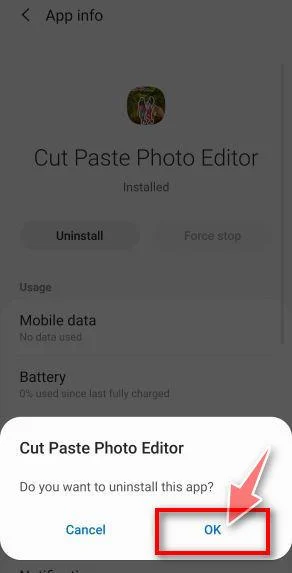
Uninstalling can remove local app data. Check what you need to preserve first, without restoring an untrusted APK or exposing private conversations to a public forum.
Step 3: Run an Android security scan and review the result
After addressing the suspect app and its permissions, run an Android malware scan. Use the genuine store listing, not another APK supplied by the original message.
-
Open the official Malwarebytes listing.
Malwarebytes for AndroidFree manual scanning, with optional paid protection.
Opens Google Play. Check the publisher before installing.
-
Install and open the app.
In Google Play, select Install, then Open when installation finishes. The store’s design and available options can vary by Android version and region.

Open Malwarebytes through the store or its own app icon. Do not return to the suspicious download page for activation instructions.

-
Review setup and choose only the features you need.
Select Get Started, or activate an existing subscription if you have one. Review optional plan and trial offers rather than assuming a purchase is required for manual scanning.
Grant the permissions needed for the scan through Android’s own prompts. Storage access lets the scanner examine accessible files as well as installed apps.
-
Run a manual device scan.
From the current dashboard, find Device and select Scan now. Let the scan finish, then open the results. Keep the application updated through Google Play.
-
Act on each detected item.
Open the menu next to a detected app and choose Uninstall app for a confirmed malicious installation. Confirm the removal in Android’s prompt.
Do not select Always allow merely to clear a warning. If a result is unclear, keep its name and details and request help before excluding it.
-
Check the outcome and unresolved access.
Confirm removal completed, restart if requested, and review the permissions again. A returning app or blocked uninstall needs further assistance.
A negative scan cannot establish what messages or credentials were accessed earlier. Complete account and session recovery separately from the device check.
Step 4: Recheck trust and arrange supported recovery if needed
Review permissions and available security updates. If the app returns or removal is blocked, ask the manufacturer or IT about supported recovery or a reset.
Confirm usable personal backups and account access before a reset. Restore reviewed data and official apps, not the counterfeit APK.
Consider Who Else May Be Affected
A compromised personal device may also hold work mail, shared files, and contacts. Inform the responsible team if those resources were accessible.
Do not warn every contact that all their messages were stolen unless the investigation supports it. Explain the known exposure and any specific requests to disregard.
If you suspect someone close to you is monitoring the device, consider whether visible cleanup could put you at risk.
Use a separate safe device to seek trusted assistance before making changes that might alert that person. The safest sequence can depend on your circumstances.
For ordinary malware response, keep a brief cleanup record: what was removed, which accounts were reviewed, and what remains unresolved.
That record prevents repeated guesswork if a security alert appears later. A second finding deserves comparison with the first incident, not automatic dismissal.
If the device supplies authentication for work, arrange a safe alternative with IT. Losing access to the affected installation should not force unsafe sign-in workarounds.
Check whether essential photos or documents have usable copies elsewhere before reset. Confirm that the backup opens without restoring the suspicious application.
Keep only the information needed for support. A report about suspected surveillance should not unnecessarily expose private conversations, contact lists, or photographs to additional people.
Where a financial account was misused, keep the fraud case reference with the device-cleanup record. The two investigations may proceed separately and need different evidence.
Frequently Asked Questions
What is Arsink RAT?
It is Android malware associated with counterfeit app packages and remote access. The reported campaign can expose private information through access granted to malicious software.
Are the real apps whose names were copied infected?
The impersonation does not establish that. Check the genuine publisher and installation source rather than blaming a legitimate app for an unrelated counterfeit package.
Can a slow device alone identify Arsink?
No. Slowdowns have many causes. Assess recent installations, permissions, and reliable security findings instead of assigning a malware family from performance alone.
Does a missing home-screen icon mean the app is gone?
No. Check Android’s installed-app list. An absent shortcut does not by itself prove either successful removal or malicious concealment.
Will uninstalling bring back information already exposed?
No. Removal addresses the installed threat. Account review, financial reporting, and assessment of disclosed data are separate follow-up tasks.
Should I follow the Windows removal instructions?
No. Arsink targets Android. Use the Android guidance here and controls appropriate to the device’s manufacturer, version, and management status.
The Bottom Line
Do not install a counterfeit app because its familiar name promises extra features. Arsink RAT removal starts with identifying and containing the untrusted Android installation.
Use trusted mobile security tools, recover important accounts through a clean route, and seek supported recovery if device trust remains uncertain.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.