

A quiet maintenance email says your configuration is waiting for verification. There is no dramatic threat, just a small task to keep mail running.
That ordinary tone can make the request easy to follow. Before reviewing anything through its button, check who is asking for access.
Overview
The request sounds like routine account maintenance
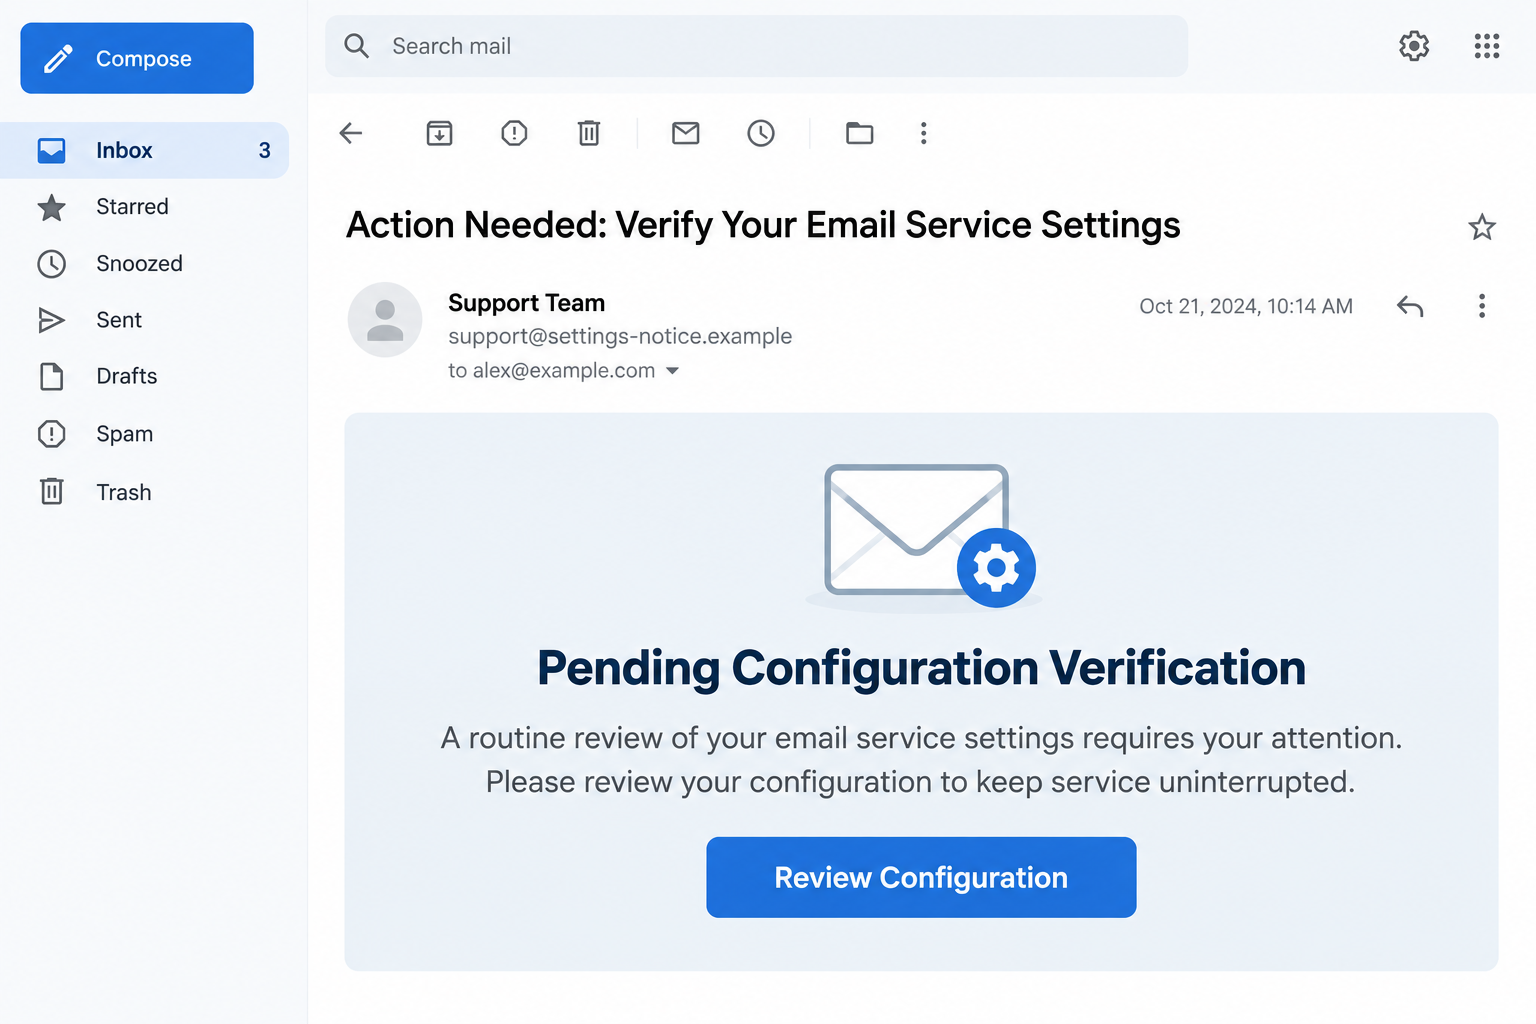
The reported message says a review of email settings has left the recipient’s account awaiting confirmation. It links the task to uninterrupted service and security.
A configuration-review button then moves the reader away from the inbox. The message does not explain a specific technical problem that the recipient can independently verify.
That is the appeal of a maintenance pretext. You do not have to believe something catastrophic happened, only that completing a small task will prevent inconvenience.
The reported destination imitated email sign-in pages
The identified landing host was ighmoseum.vercel[.]app. The reported page could tailor its appearance to the recipient’s email address, including familiar Gmail or Yahoo-style presentation.
The hosting provider is not the impersonated mail service. A page on a widely used hosting platform can still be operated by someone unrelated to your account.
Useful details to recognize include:
- A status suggesting that configuration confirmation is pending.
- A broadly worded maintenance explanation from a support team.
- A button inviting you to review settings.
- A login screen whose familiar appearance does not match an independently verified origin.
A tailored page can feel familiar without being authorized
Knowing your email address may help a page select a logo or layout. It does not show that the operator knows your password or manages your mailbox.
The reported mechanism is credential phishing, not a confirmed malware download. A harmful installation would be an additional exposure requiring its own evidence and response.
The image above is an illustrative email with sample details. The historical landing host is unavailable, so an active copy of its login flow is not presented here.
How the Configuration Verification Scam Works
Step 1: A modest maintenance task reaches your inbox
The email frames itself as a service-settings notice. That can slip into the same mental category as legitimate administrative messages you occasionally need to handle.
It asks for attention without making an extravagant demand. A reader may see reviewing configuration as the responsible thing to do, especially during a busy workday.
But responsibility starts with identifying the sender. A generic support signature does not establish who performed a review or who has authority over your account.
If the mailbox belongs to an employer, you probably have an established IT contact or portal. That known route is the place to confirm an unexpected maintenance task.
Step 2: Uninterrupted service becomes the reason to comply
The message associates confirmation with continued mail access. It does not need an explicit countdown to make a reader worry about missing important messages.
For a business account, that worry may involve customers or invoices. For a personal mailbox, it may involve password resets, appointments, or travel information.
The request borrows those real concerns without proving there is a real configuration issue. Your need for reliable email cannot authenticate someone claiming to protect it.
Open mail through your normal route and check for an account notice there. A service issue should be investigated with the provider, not diagnosed by an unfamiliar button.
If everything works, do not create an account exposure in the name of preventing a hypothetical interruption. Take the extra minute to verify the notice independently.
Step 3: The review button sends you to a separate login environment
The email’s link is the bridge between a harmless-looking task and a credential request. Clicking changes who controls the screen you are using.
The reported destination used a Vercel-hosted subdomain. Such hosting is available to many developers and should not be mistaken for an official Gmail or Yahoo login origin.
This does not make Vercel itself fraudulent. It means a hosting brand cannot vouch for every page a third party publishes through its infrastructure.
Read the browser address before interacting. A familiar logo in the page cannot replace checking the service that is actually receiving your information.
Do not repeatedly follow a broken link until a version appears. An unavailable phishing page is not something you need to troubleshoot for the sender.
Step 4: The page adapts its appearance to the intended account
The reported landing page could change its presentation based on the email address. That makes the experience look more specific than a generic password request.
Seeing your address already displayed may feel reassuring. In reality, it can be information included in a link or supplied during an earlier interaction.
A page does not have to know your account’s private contents to show the right provider name. Publicly visible address details can guide a convincing imitation.
Be careful when familiarity is doing all the persuasive work. Ask whether you reached this login screen through your normal account route or an unverified message.
A password manager can provide another useful check when it refuses to match the expected account. Do not override that mismatch simply because the logo looks right.
Step 5: A stolen login can outlast the original email
If credentials are submitted, the risk moves from the message to the account. An attacker may try to use them before the recipient notices anything wrong.
Mail access can expose conversations and reset messages. Depending on account permissions, it may also let an intruder impersonate the owner to people who already trust them.
Those are potential consequences, not proof that every recipient suffered them. Your response should check actual account activity, sessions, and settings.
A page showing an error after submission does not mean the password was rejected before being collected. Stop rather than trying another password on the same page.
Likewise, closing the original email does not revoke a login someone already obtained. Account security must be addressed through the genuine provider.
Sender, Hosting, and Login Checks That Matter
Find the organization responsible for the mailbox
For a work account, that may be your employer’s IT team rather than the company whose mail software you recognize. Use the organization’s established contact method.
For a personal account, enter through the provider’s normal app or known website. Do not let a maintenance email choose a new support route for you.
Ask a specific question: is there a configuration task for my account, and where should I see it after signing in normally?
A vague assurance from the same email sender is not an independent answer. Verification needs a route whose identity was established before this message arrived.
Distinguish a hosting address from an account authority
The host ighmoseum.vercel[.]app identifies where a reported page was published. It does not identify an authorized mail administrator or a genuine account-recovery service.
Attackers can move pages between hosts or change subdomains. Learning one exact address helps recognize this case, but it is not a complete future-proof filter.
The more durable check is whether the login origin belongs to the service or organization you intended to reach. Start from its established access route.
Do not treat an unavailable host as proof that no one was affected. Equally, its disappearance cannot establish when it stopped operating or who controlled it.
Check the request’s purpose before providing a secret
Some legitimate settings pages require reauthentication. The problem is not that a password is requested somewhere, it is that an unverified page is requesting yours.
If you are asked to approve an unexpected sign-in or share a verification code, pause. Confirm the action inside the account process you intentionally started.
Do not approve an authentication prompt just to make it stop appearing. Repeated prompts may be a reason to contact support, not a reason to consent.
Keep troubleshooting separate from the suspicious flow. Sending another code or trying a different password can give the operator more useful information.
What to Do If You Followed the Verification Request
End the interaction and note the exposure. Record whether you merely opened the message, visited the site, typed a password, or approved an authentication step.
Keep the original email for reporting. Its technical details may help your provider or IT team investigate more than a cropped screenshot would.
If no information was submitted and nothing was installed, report the message and move on to normal account checks without assuming an infection.
Replace any password entered into the counterfeit page. Use the genuine provider from a trusted device, not the verification email’s link.
Give the account a unique password and change it anywhere the exposed password was reused. Start with accounts that could affect recovery or financial access.
If access is already lost, use the official recovery procedure. Do not pay a stranger who claims they can bypass the provider’s ownership checks.
Review account sessions and security settings. Examine recent activity, signed-in devices, recovery contacts, and unfamiliar authentication methods where the provider offers those controls.
For Gmail users, Google’s compromised-account guide explains relevant security checks and recovery options.
For managed accounts, ask IT to review the incident. They may need to revoke sessions or inspect organization-level records you cannot see yourself.
Look for changes that could keep mail flowing to an intruder. Review forwarding, filters, delegation, and connected-app access through your provider’s supported settings.
Preserve details of anything unfamiliar before removing it. A rule hiding messages or forwarding them elsewhere may explain why an account appears normal afterward.
Do not delete legitimate business rules indiscriminately. Ask the administrator to help distinguish expected automation from changes introduced during the incident.
Check whether the account was used to mislead anyone else. Review sent messages and relevant activity for unauthorized requests or unusual conversations.
If a payment instruction or document-sharing request was sent without permission, alert the recipient through a separate known channel. Be specific about what should be disregarded.
For work mail, follow the organization’s incident process before making broad claims about exposed data. The actual access and message history determine what notifications are needed.
Investigate device exposure if the page added software or permissions. Remove unfamiliar notification permissions and ask for help with unexpected extensions or downloaded utilities.
Malwarebytes can help check for malicious software when a download or installation creates that concern. A clean scan does not cancel a stolen account login.
AdGuard can help limit some malicious ads and redirects. Continue account recovery separately, because browser filtering cannot undo information already submitted to a phishing page.
Report the lure without spreading its working link. Use the mailbox’s phishing-report feature and your organization’s established security channel where relevant.
Include the subject, original message, and landing address privately. Avoid posting a clickable copy in group chats where another reader may try it.
Keep watching recovery notifications and account activity after changing the password. If suspicious changes continue, return to official support with the new details.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Why a Calm Email Can Still Deserve a Firm No
Not every phishing message threatens immediate deletion or uses obvious mistakes. A restrained request can be more persuasive precisely because it resembles ordinary work.
That makes a consistent process more reliable than judging tone. Unexpected settings requests should be verified through the same trusted route whether they sound polite or alarming.
For teams, assign ownership of mailbox maintenance. Staff should know who can request a configuration change and where approved instructions normally appear.
A short internal reminder works better than a collection of frightening screenshots. Explain the actual rule: never enter a work password through an unverified maintenance invitation.
When someone reports a mistake quickly, treat that as useful information. Blame encourages delay, while early details may help stop an account takeover from spreading.
After recovery, write down the successful route you used to reach support. Having it ready makes the next unexpected notice easier to check without improvising.
Frequently Asked Questions
Is Pending Configuration Verification a genuine account status?
It is a claim used in this phishing message. Confirm any real maintenance requirement through your mail provider or established workplace administrator.
Why did the page appear to know my email provider?
The reported page could adapt its appearance using the recipient’s address. Matching a provider logo does not demonstrate authorized access to the account.
Does a vercel[.]app address mean Vercel sent the request?
No. It identifies hosting used by a third-party page. The hosting provider is not thereby the sender or the authority managing your mailbox.
What if the page said my password was incorrect?
Do not retry there. An error message cannot prove submitted information was not collected. Change an exposed password through the real account service.
Is changing the password enough after an account takeover?
Also review active access, recovery settings, and relevant mail rules. Ask the provider or administrator to help check whether another route into the account remains.
Do I need to reinstall my computer after reading the email?
No. Reading this notice alone does not justify reinstalling a device. Focus on account exposure, and investigate software separately if you installed or ran anything suspicious.
The Bottom Line
Do not use this configuration-verification email to sign in. Its maintenance story leads toward an impersonated login rather than a trusted account-settings process.
If you entered information, change the exposed password through the genuine service and review account access. Report the message so the same routine-looking request reaches fewer people.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.