

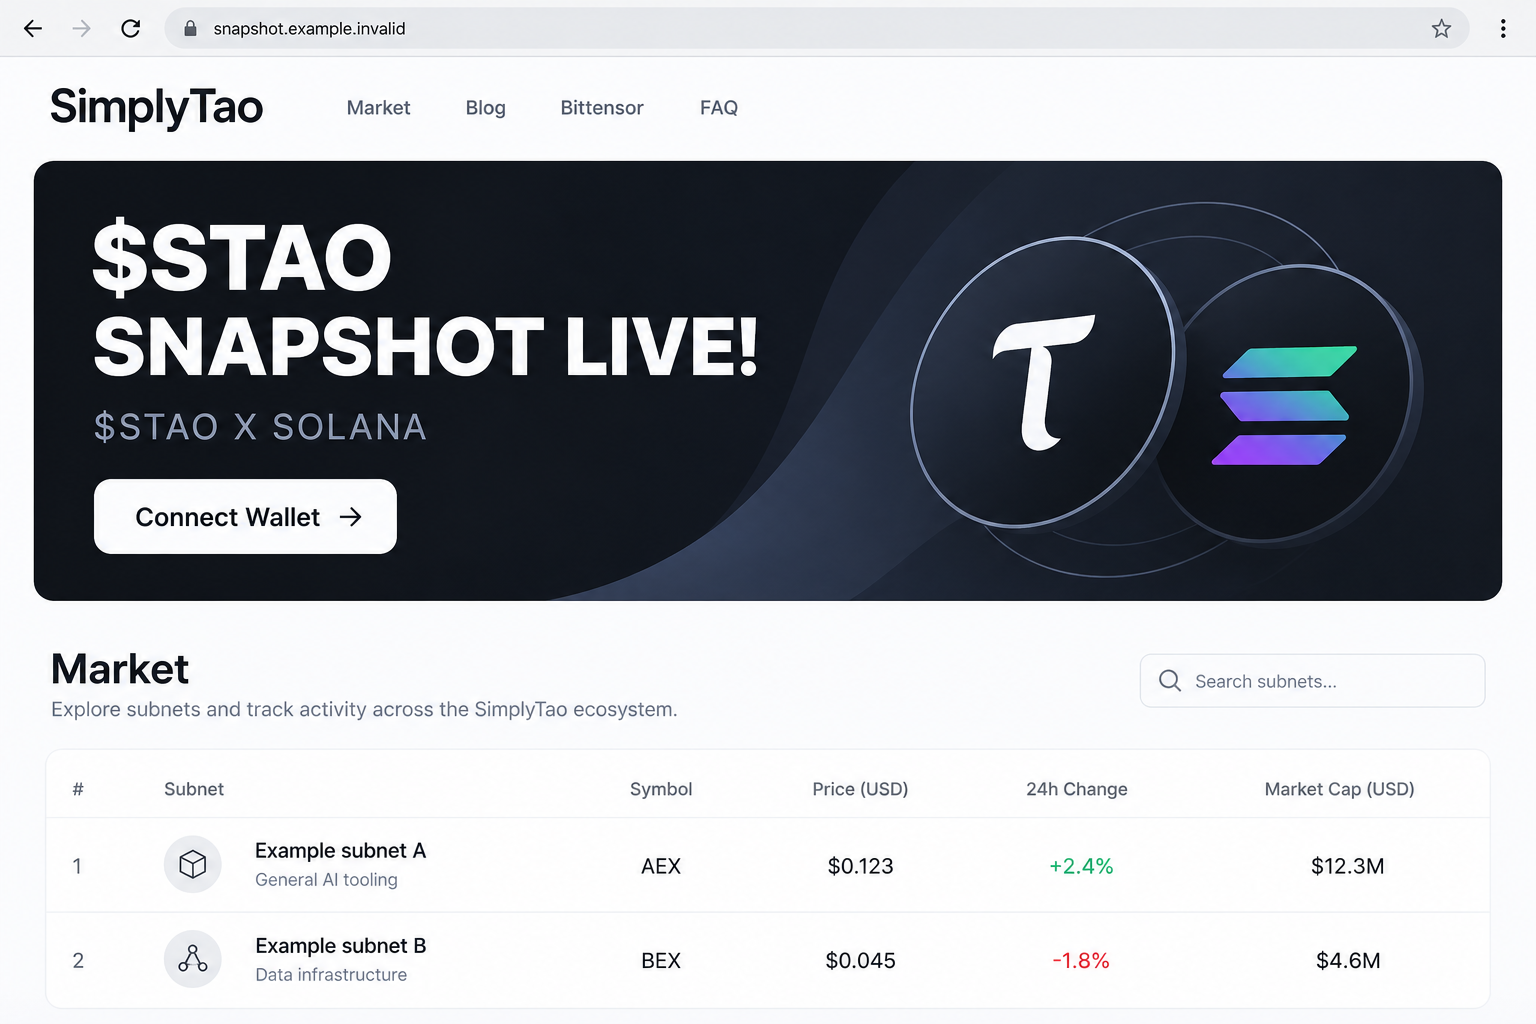
A SimplyTao-looking page announces a live $STAO snapshot and invites you to connect a wallet. The market dashboard around it makes the event look comfortably familiar.
Before joining, look beyond the promotion panel. The website address and the next wallet request matter more than the token symbols on the page.
Overview
The promotion appears on a copycat domain
The fake SimplyTao snapshot scam uses simplytaoai[.]xyz to impersonate the established simplytao.ai website. The added letters can be easy to miss beside familiar branding.
The reported copy borrows navigation and market-style information, then introduces a purported $STAO event. It asks visitors to connect a cryptocurrency wallet to participate.
The name being copied and the page requesting access are not the same thing. This warning concerns the impersonator, not a finding that SimplyTao operates the scheme.
The event is a route toward wallet authorization
The reported promotion combines a snapshot announcement with Solana-related wording. A wallet-selection dialog supplies familiar choices, making the next step resemble an ordinary crypto interaction.
Its reported purpose is draining assets. But connection, a signature, a token permission, and a transfer are distinct operations, not interchangeable descriptions of automatic theft.
The exact request matters. A harmless-sounding label on a web page does not limit what an approval inside the wallet can authorize.
Don’t authorize the snapshot offer to find out whether it is real
Verify announcements through established project channels before interacting. Do not use an unverified event as a reason to expose your main wallet.
A fresh capture of the impersonating page was unavailable, and no wallet request was tested. The illustration uses fictional market entries rather than live allocation data.
- Check simplytao.ai separately from the look-alike address.
- Confirm the exact event, not just the existence of the copied brand.
- Read the wallet operation before considering any signature.
- Match containment to the network and permissions actually involved.
What the Word Snapshot Doesn’t Tell You
In cryptocurrency discussions, a snapshot commonly means recording balances or eligibility at a particular point. The word sounds observational, as if nothing needs to leave your wallet.
That expectation can make an access request seem less significant. A reader may think they are only proving participation or letting a website check an address.
However, the promotional label doesn’t describe the contents of a signed operation. A transaction remains a transaction even when the website calls it a snapshot check.
A public blockchain address can often be inspected without giving anyone permission to move assets. A private key or recovery phrase is never needed for ordinary public inspection.
Don’t assume every legitimate eligibility tool works identically. Instead, ask why this specific operation is necessary and whether the event has been independently authenticated.
If the explanation relies on speed, secrecy, or ignoring a wallet warning, stop. A claimed distribution deadline does not make an unclear authorization safer.
The same caution applies when a page combines different ecosystems. Token names and network logos do not explain which chain, account, or assets the next request concerns.
Check whether an independently verified announcement identifies the relevant network and eligibility rules. A ticker alone can be copied and is not a unique asset identifier.
Don’t search only for the promotion’s headline and trust the first matching page. Multiple copies of the same claim are not independent confirmation.
A copied post can also include a genuine discussion of the project. Correct background information doesn’t authenticate the separate action appended to it.
How the Fake SimplyTao Snapshot Scam Works
Step 1: A recognizable market page supplies the setting
The reported impersonator looks like a cryptocurrency service rather than a stand-alone giveaway. Market rows and familiar navigation create a plausible setting for an announcement.
That surrounding detail can distract from the address bar. A visitor who recognizes the design may assume the website’s identity has already been settled.
It hasn’t. Public design elements can be reproduced, and a data table says nothing about who controls the page showing it.
Scam promotions may arrive through messages, social posts, advertisements, or search results. None of those channels establishes that a link belongs to the project it names.
Step 2: The event gives you a reason to act now
The snapshot panel turns an ordinary-looking visit into a participation opportunity. It suggests there is something to qualify for, with connecting presented as the next required action.
The promise need not include an exact payout to be effective. A visitor can worry about missing eligibility before learning what the supposed distribution involves.
That uncertainty benefits the promotion. Instead of checking whether the event exists, the reader starts asking how to complete it.
Reverse that order. Authenticate the announcement first. A page cannot prove its own event by supplying a button that begins the same event.
Step 3: Familiar wallet choices make the request look routine
A selection dialog can list well-known wallets and standard connection technology. The names may be genuine even when the website initiating the request is not.
Connection tools are infrastructure, not a certificate of honesty for every application using them. A recognizable wallet logo does not approve the surrounding promotion.
Ordinary connection generally lets a site interact with a public wallet address and request further actions. It should not be described as permission for every possible transfer.
That distinction helps identify exposure. Record whether you only connected or also accepted a later signature, permission, or transaction.
Step 4: A later approval can authorize something different from the headline
The dangerous request may seek asset movement or continuing authority. Its effect depends on the network, wallet, contract, and operation you actually approve.
Do not dismiss a transfer preview because the page says the action is a free claim. The wallet’s displayed operation deserves its own assessment.
A hardware wallet also cannot make an intentionally approved malicious operation benign. Protecting keys and deciding what to authorize are separate jobs.
There is no tested transaction payload here to identify a specific spender or chain. Avoid assuming one generic revocation procedure applies to every wallet listed.
If you cannot explain the requested operation in plain language, do not sign it. Missing an unverified promotion is preferable to granting unclear control.
Watch which account is selected in the wallet. Having several accounts or networks available does not mean the promotion should interact with all of them.
If a request groups several actions, examine the entire preview. A reassuring first item does not explain additional asset movements or authority in the same request.
When a wallet cannot show enough detail, reject the request rather than treating that lack of information as evidence of safety.
Step 5: Asset movement requires a different response from closing the site
If a transfer has been confirmed on-chain, closing a tab does not undo it. If authority remains active, future assets may also be exposed.
Disconnecting can end a site’s connection, but it may leave previously granted permissions untouched. Those permissions require a separate review.
A recovery phrase entered into any page creates a broader problem than an unwanted connection. Anyone holding that phrase may control the wallet independently.
Do not return to the promotion to request a reversal. Start containment from the genuine wallet’s support guidance and preserve transaction records for reporting.
Compare the Identity, Not Just the Logo
The established domain is simplytao.ai. The impersonating address adds characters and uses a different ending.
The legitimate home page currently presents market information and reading navigation. Its existence is not confirmation of the separate snapshot pitch.
Nor is identifying the established domain an investment recommendation. Whether to use a service or buy a token requires a separate assessment beyond this impersonation warning.
Look for an event announcement reached independently from known channels. Check the exact account, domain, token, network, and instructions rather than matching a single logo.
A social account can be compromised or copied too. If an announcement changes the normal destination or requests unusual permissions, seek confirmation through another established route.
Cached market figures and polished charts do not authenticate a promotion. Financial data can be old, copied, or displayed alongside an unrelated request.
Don’t send a small test payment to settle the question. A successful small interaction would not prove that a later approval or larger transaction is safe.
What to Do If You Interacted With the Snapshot Page
Stop additional signatures immediately. Close the promotion and reject pending requests. Don’t approve a supposed cancellation or refund transaction supplied by the same page.
Write down which wallet and network were involved. A useful response begins with the operation you actually accepted, not the website’s label for it.
Separate connection from authorization. Review connected applications and recent wallet activity through the real wallet interface.
If you only connected and rejected everything else, don’t assume assets were transferred. If you approved something, inspect that specific operation and any continuing permissions.
Review permissions with a tool appropriate to the chain. Obtain the route through your wallet’s official documentation rather than a stranger’s direct message.
Phantom’s approval guidance distinguishes Solana from EVM networks. A tool for one network should not be treated as universal protection.
Understand what revocation can accomplish. Removing a continuing allowance may reduce further exposure, but it does not reverse a completed transfer.
The Revoke.cash FAQ explains why disconnecting and revoking differ. Verify the relevant permission rather than signing an unfamiliar request on trust.
Use a new wallet if keys or recovery words were exposed. Create it through a trustworthy wallet process on a device you can rely on.
Follow the provider’s instructions for moving trusted remaining assets. Don’t import the same compromised phrase and assume the new installation created a new identity.
Check positions beyond the visible balance. Staking, deposited assets, and other positions may require separate attention when securing a wallet.
Phantom’s drained-wallet guidance covers these distinctions. Avoid interacting with unknown tokens merely because they appeared during the incident.
Investigate a software exposure if one occurred. A wallet transaction isn’t itself proof of a computer infection. An installed extension or downloaded program changes that assessment.
Malwarebytes can check for unwanted software, while AdGuard can reduce some deceptive-ad encounters. Neither tool changes a blockchain approval or returns transferred assets.
Preserve the evidence and notify relevant services. Keep public transaction hashes, destination addresses, the page URL, and the original promotional messages.
Contact an exchange promptly if it may be involved, and file an appropriate fraud report. Do not publish recovery words or pay an unsolicited recovery agent.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Two Recovery Mistakes That Can Make the Loss Worse
Sending more funds to an account that is still exposed
Someone may suggest adding funds to pay network costs. Before doing so, determine whether the wallet’s keys or continuing authority remain compromised.
If funds disappear repeatedly, don’t keep replenishing the address. Seek guidance through the genuine wallet provider and explain exactly what you observed.
A compromised-key problem cannot be solved simply by disconnecting one website. The person holding the key does not need that browser connection to act.
Also distinguish a genuine network transaction cost from a payment demanded by an alleged agent. Paying a stranger is not the same as submitting an appropriate revocation transaction.
Keep a record of which assets and networks remain at risk. A clean-looking balance on one chain doesn’t answer what happened to an account on another.
For a shared or business-controlled wallet, involve the responsible owner before moving assets. Explain the incident privately without exposing keys in a group chat.
Trusting a direct-message rescuer with the next signature
A public request for help can attract accounts claiming they can restore the wallet. They may offer a link, ask for a phrase, or request another signature.
Don’t hand them control because they mention the correct incident. Public transactions and information in your post may explain what they know.
Open provider support from its established site. Keep the conversation about containment and records rather than promises of guaranteed recovery.
Blockchain transfers generally lack a simple chargeback. That does not mean reporting is pointless, but anyone promising a certain reversal is offering more certainty than the evidence supports.
Frequently Asked Questions
Is SimplyTao itself the scam described here?
No. The case concerns a page impersonating its identity at simplytaoai[.]xyz. It is not an allegation that the established SimplyTao site runs that snapshot lure.
Does the $STAO snapshot title confirm a token distribution?
No. A promotion panel cannot establish eligibility, a real allocation, or project authorization. Confirm the exact event independently before considering any interaction.
Did connecting a wallet automatically transfer everything?
Connection alone should not be equated with every possible authorization. Review whether you also signed an operation or granted permission, and inspect actual transaction records.
Is a familiar wallet-selection dialog a safety check?
No. Standard wallet technology can be used by an untrustworthy site. The application’s identity and the requested operation still need scrutiny.
Can disconnecting recover assets already transferred?
No. Disconnecting doesn’t reverse an on-chain transfer and may leave permissions active. Review remaining authority and secure any assets still under your control.
What if I entered my recovery phrase?
Treat the wallet as compromised. Follow official guidance to establish a genuinely new wallet and move trusted remaining assets safely, rather than continuing to use the exposed phrase.
The Bottom Line
Do not connect or sign through the fake SimplyTao snapshot promotion. Copied market pages and familiar wallet names don’t authenticate an event.
If you already interacted, inspect the real operation, review continuing permissions, and treat exposed keys as a separate emergency. Use official wallet guidance, not a recovery link from the promotion.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.