

A PYRA giveaway page says early community members can claim tokens. If you’ve been following the project, the offer can look like the reward everyone else already knows about.
The page makes participation sound straightforward. Before checking eligibility, look at the connection it asks you to make between a community promise and your existing wallet.
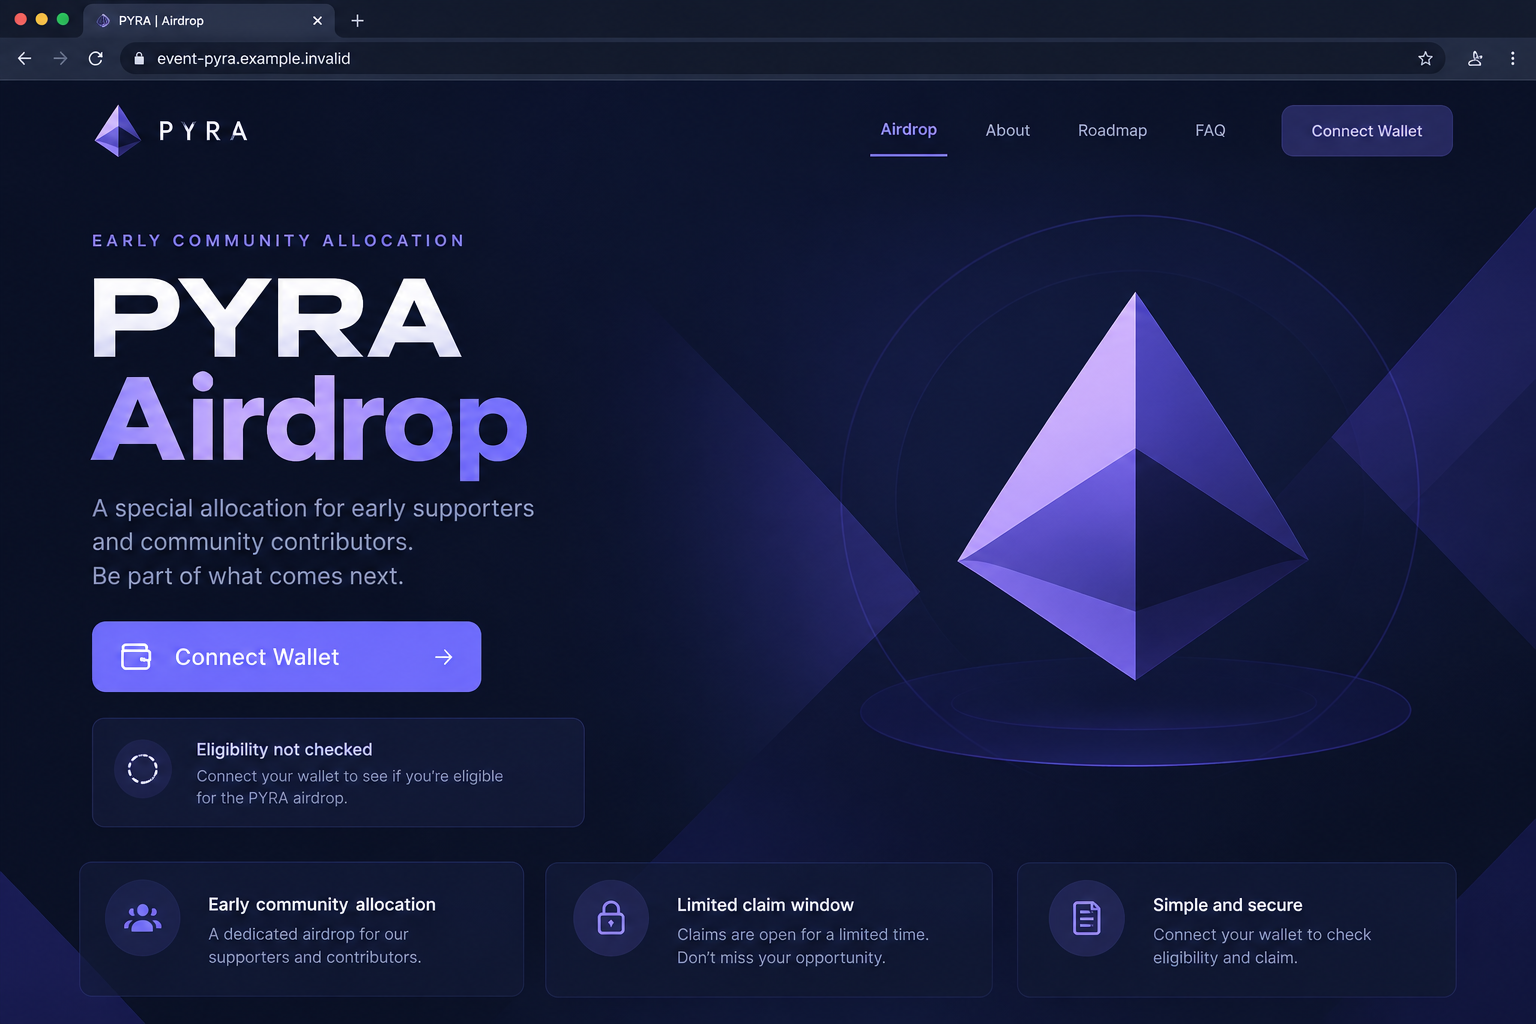
Overview
The reported giveaway uses a separate event domain
The PYRA airdrop scam promotes event-pyra[.]fun as a place to claim free tokens. It borrows the project name and appeals to early supporters.
The reported campaign is a counterfeit distribution leading to wallet-draining activity. Its community language doesn’t establish a genuine allocation or a relationship with the project’s operators.
The historical page couldn’t be reproduced during the current capture attempt. No signing payload, receiving address, or completed transfer was independently tested.
That limit matters: the exact network and authorization cannot be inferred merely from the token name or the fact that a connection button appears.
The underlying project description doesn’t authenticate an airdrop
Published PyraChain materials have described a network based on Solana’s code. That historical description doesn’t verify an airdrop, and the documentation host is currently unavailable.
A copied page can repeat technical terminology accurately while misrepresenting who operates the promotion. Correct background information doesn’t make its wallet requests trustworthy.
- Following a project doesn’t automatically establish that you qualify for a token distribution.
- A familiar ticker doesn’t identify the chain, asset address, or operator.
- Connecting an account is different from signing or granting spending authority.
- A claim status on a website doesn’t establish what happened to your holdings.
Protect the wallet you already have
Don’t pursue the claim through event-pyra[.]fun. The promised reward shouldn’t decide which accounts, assets, or permissions you expose to an unfamiliar destination.
If you interacted, work out what you actually did. A rejected prompt, a connection, an approval, a transfer, and disclosed recovery words need different responses.
The warning concerns the reported counterfeit offer. It isn’t an independent audit of PyraChain’s performance, token economics, or suitability as an investment.
Why the Early-Supporter Story Feels Personal
Community projects often recognize people who tried something early. A giveaway can borrow that expectation without knowing whether you ever used the software or held its token.
The label early supporter is flattering because it describes a role you may already identify with. It can make eligibility feel earned before anyone verifies it.
A limited claim window adds another pressure. You may worry about missing a benefit rather than asking whether the issuer announced one.
But the promotion doesn’t become official because people in a chat are excited about it. They might all be relying on the same unverified link.
Look for an announcement trail you can establish outside the page. A website’s own social icons and support account can’t independently confirm its authority.
You aren’t losing a verified entitlement by pausing an unsupported claim. The assets already in your wallet are real; the allocation promised by this page remains a claim.
How the PYRA Airdrop Scam Works
Step 1: A recognizable project name supplies the starting trust
The promotion uses PYRA wording to make the offer relevant to people interested in the project. A reader doesn’t have to learn an unfamiliar identity from scratch.
That familiarity can come from documentation, a community discussion, or a token listing. None of those establishes who controls a newly encountered claim domain.
A copied logo or technical description can make the page feel connected to earlier reading. Check the operator relationship instead of relying on visual continuity.
Don’t assume that a recommendation from a known profile settles the question. Accounts can be mistaken or compromised, and shared links can travel without verification.
Step 2: The event address makes a temporary promotion look plausible
A separate event domain can sound reasonable for a short distribution. It gives the page a purpose without explaining why the genuine project would use that address.
The reported event-pyra[.]fun address is a recognition indicator, not a destination to experiment with. Similar future wording could appear at another hostname.
Verify any campaign from the project’s independently established channels. Don’t let the claim page introduce both the announcement and the account supposedly confirming it.
A domain that spells PYRA correctly still needs that verification. Conversely, an alternate domain isn’t automatically malicious simply because it differs from a homepage.
The question is whether the specific operator and distribution can be authenticated. A polished event title cannot answer it.
Step 3: Eligibility becomes the reason to involve a wallet
The page presents wallet interaction as a way to participate. You may expect it merely to check whether your public address qualifies for tokens.
Before proceeding, notice which account is selected. A wallet application can manage several addresses, and the familiar nickname isn’t the same thing as the underlying account.
Connection can allow the site to see selected public account information and propose further actions. It isn’t, by itself, blanket permission to transfer all assets.
That distinction shouldn’t encourage experimentation with an unverified offer. Each later request is another decision, and the reward label doesn’t explain the authority being requested.
Don’t reveal a seed phrase to check eligibility. Receiving tokens at a public address doesn’t require giving a website the secret controlling that address.
Step 4: The claimed reward can conceal a different authorization
The reported purpose is draining cryptocurrency. In practice, the actual wallet request determines whether a particular interaction grants authority, moves an asset, or does something else.
Read the selected chain, account, recipient, affected asset, and permissions. If those details don’t make sense, reject the request rather than trusting the page’s explanation.
A transaction described as claiming PYRA could involve a different holding. The banner at the top of the website doesn’t define the contents of a wallet operation.
Some requests combine multiple instructions. A harmless-looking first instruction doesn’t explain everything else included in the proposed action.
The original request wasn’t available for inspection here. Don’t assume a particular allowance, contract standard, chain, or fee applies to every copy of the promotion.
Step 5: The page’s progress display competes with the actual record
A claim page can show success, pending review, or an error regardless of whether the wallet interaction was safe. Those labels come from the same unverified operator.
Your wallet history and relevant network records are the better place to examine completed activity. A website’s progress bar isn’t an account-security report.
Closing the page won’t undo an already completed transfer. Likewise, it may not remove permission granted earlier, even though it ends your immediate interaction.
Don’t sign again to finish a stuck eligibility check. First establish what the earlier request did and whether any continuing authority needs attention.
If a later message demands money to release the reward, treat it as another unverified demand. It doesn’t establish that the original allocation existed.
The Network Question Deserves More Than a Familiar Name
Related software doesn’t make networks interchangeable
The project’s description refers to Solana’s code. That doesn’t establish that a particular claim request is happening on Solana or that instructions for one chain fit another.
Check the network actually selected by the wallet. The operation needs to be understood in that environment, not guessed from a project’s technical background.
Don’t change networks or import keys because the promotion says your ordinary setup is incompatible. Resolve the offer’s authenticity before troubleshooting access to it.
A token symbol isn’t a unique identity
Names and tickers can be reused. When examining an asset, compare the relevant chain and asset identifier through trusted records rather than a display label alone.
A matching identifier can establish which asset a page discusses. It still doesn’t prove that the page is authorized to distribute it.
Similarly, an unsolicited token appearing in your account doesn’t authenticate a new website linked in its description. Don’t follow a claim instruction simply to remove an unwanted item.
Recovery tools must fit the authority that was granted
Phantom’s approval guidance distinguishes Solana-related handling from EVM-network approvals. That illustrates why generic revoke instructions can miss the actual problem.
For an affected wallet, use its genuine provider’s current support material and the correct network. Don’t choose a recovery tool from the claim page’s advertisement.
If the issue is leaked keys rather than an approval, revoking one permission won’t make the secret private again. Identify the exposure before choosing the remedy.
What to Do if You Have Fallen Victim to This Scam
- Stop the claim and cancel outstanding requests.
Leave the promotion and reject any pending signature or transaction. Don’t send a fee or contact the page’s supposed verifier to complete the reward.
Remove the site’s connection through the wallet’s own controls. Treat this as one containment action, not proof that every earlier authorization disappeared.
- Identify the account and activity involved.
Record the public address, network, approximate time, and transaction identifiers. Check the actual affected holdings rather than only the wallet’s total balance.
If the request was rejected, record that too. A canceled operation is different from a confirmed transfer or permission, and recovery should reflect that difference.
A pending transaction isn’t the same as a finalized one. Ask your wallet’s verified support how to interpret its status on that network.
- Review continuing permissions with the correct provider.
Inspect unwanted spending authority or other access using guidance for the affected wallet and chain. Confirm what each corrective action will change before approving it.
MetaMask’s permissions documentation notes that disconnection doesn’t revoke token approvals. Removing an approval limits its future use; it doesn’t reverse an earlier transfer.
- Replace compromised control if you disclosed secrets.
A shared recovery phrase or private key requires a genuinely fresh secret in a trusted environment. Another account derived from the same exposed phrase isn’t independent protection.
Get reputable wallet assistance with remaining assets if needed. Don’t copy new recovery words into a support chat, even when the helper seems knowledgeable.
- Preserve evidence and notify relevant services.
Keep the invitation, public transaction records, and non-sensitive screenshots. Contact any involved exchange through its verified channel and report financial losses to appropriate authorities.
Ethereum’s scam-help resources explain evidence and reporting options. Depending on the network, records may assist tracing, but that doesn’t guarantee recovery or transaction reversal.
- Investigate any claimed wallet update or utility.
If you installed software or an extension during the encounter, assess it separately and scan with Malwarebytes. Sensitive recovery work needs a trusted device environment.
AdGuard may reduce harmful advertising exposure. It cannot revoke blockchain authority, replace an exposed key, or validate the token entitlement displayed by a page.
- Keep recovery promises from expanding the loss.
Reject strangers offering a guaranteed return for an advance payment. A private message claiming access to the PYRA team doesn’t establish who is contacting you.
Don’t add funds repeatedly if they disappear immediately. Stop and seek verified wallet guidance rather than following a stranger’s instructions to keep funding the account.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
When a Community Chat Keeps Sharing the Same Claim Link
Repetition can feel like verification, especially when several familiar names discuss the reward. Ask what independent announcement each person is relying on.
If everybody points back to the same event page, you haven’t gained another source of confirmation. You’ve found several routes to one unsupported claim.
A screenshot of a successful claim doesn’t establish who created it or what permissions were granted. Don’t use somebody else’s result as a substitute for your own decision.
Warn others without reposting an active invitation as a clickable recommendation. Explain the impersonation concern and direct them toward independently established project information.
If moderators confirm the message is unauthorized, keep your recovery questions with verified wallet support. A community discussion shouldn’t become a place to share private keys.
Most importantly, don’t let concern about appearing inexperienced rush you. Understanding a wallet request is more important than keeping pace with a chat.
Frequently Asked Questions
Is event-pyra.fun an authenticated PYRA distribution?
The reported site is a counterfeit airdrop lure. Don’t connect or sign there; establish any genuine campaign independently through verified project information.
Does the real project documentation prove this giveaway exists?
No. Documentation about a blockchain and token doesn’t authenticate a separate event domain or demonstrate an allocation for your address.
Does connecting automatically move my tokens?
Not necessarily. Determine whether you also authorized a transaction, granted permission, or revealed a secret. The specific action defines the exposure.
Can I assume the claim uses Solana?
No. A project’s use of related open-source code doesn’t identify the network in a wallet request. Inspect the actual account and chain involved.
Will disconnecting remove every approval?
No. Connection controls and on-chain permissions can be separate. Review the authority using the correct wallet guidance rather than relying on the closed tab.
Are stolen blockchain funds always impossible to trace?
No. Records can sometimes support investigation, depending on the network and activity. Tracing doesn’t mean a private recovery contact can reverse the transfer.
The Bottom Line
Don’t claim tokens through event-pyra[.]fun. The early-supporter story doesn’t authenticate the operator or justify exposing existing assets to unexplained wallet authority.
If you participated, inspect the account, network, and action involved. Protect remaining access through genuine wallet support instead of trying to complete the promised reward.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.