

Your monthly business statement arrives with instructions for opening the attachment. It mentions familiar banking details and a document reader you may already have.
That can feel like ordinary account administration. Before following the instructions, make sure the document and the place requesting your information are what they appear to be.
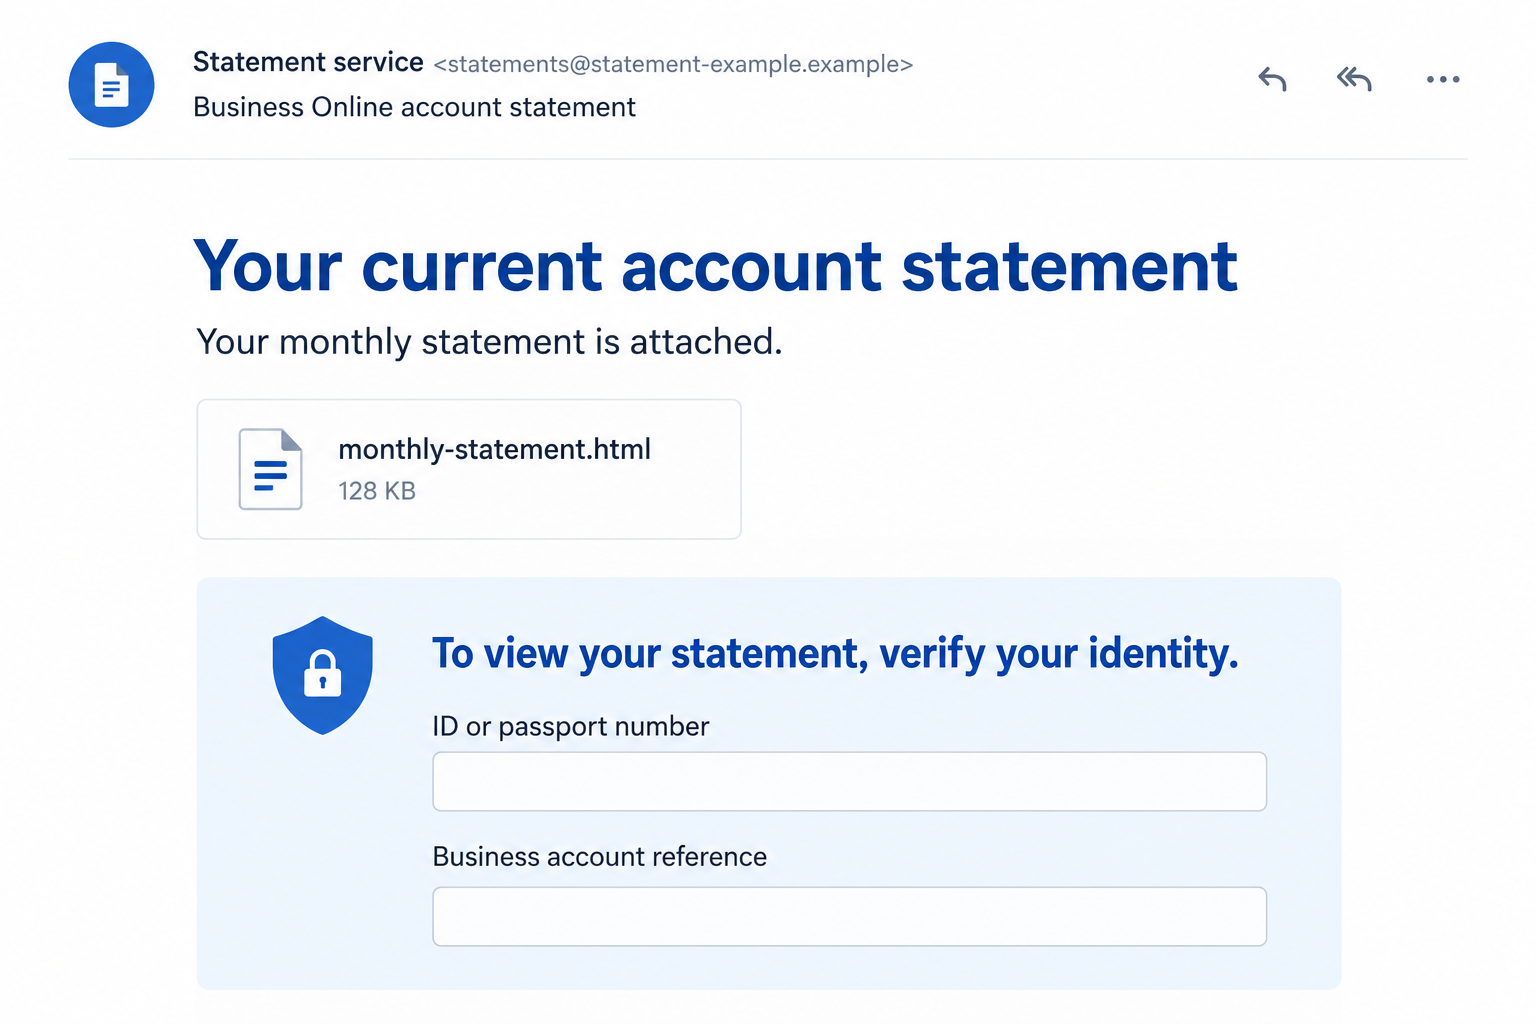
Overview
A statement notice provides the cover story
The Standard Bank account statement email scam impersonates a business-banking communication. It presents an attached monthly record as something the recipient should open for routine financial work.
The reported message borrows document-reader instructions and says personal or business identifiers can be used to open the statement.
A related counterfeit banking destination was reported at stabusionlineza[.]com. The danger is being moved from expected paperwork into a request controlled outside the bank.
A real statement password does not authenticate this attachment
Standard Bank does use protected electronic statements. Its own guidance distinguishes opening a statement with an ID number from entering email and banking credentials into a website.
That distinction matters. An ID-number instruction is not automatically fraudulent, but it cannot make an unverified attachment or redirected web form trustworthy.
Standard Bank and Adobe are real organizations. Neither a copied bank identity nor a reference to Adobe Reader proves who created the message.
Check the information request, not just the presentation
- Were you expecting a statement for the business account mentioned?
- Can you retrieve the same record through your normal banking route?
- Is a genuine local document asking to be unlocked, or has a browser form appeared?
- Does the request expand into an email password, banking secret, or approval code?
- Have you independently verified the destination rather than trusting a copied security footer?
The illustration uses fictional sender details and an example attachment label. It is not the original email, a real statement, or evidence of an actual account balance.
The Important Difference Between Opening a File and Sending Data
A genuine password-protected PDF can require a password before displaying its contents. Entering that password into trusted local software is not necessarily submitting it to a website.
A phishing form does something different. It asks you to provide information through a page controlled by another party, often under the excuse of opening a document.
Those experiences can look similar to a hurried reader. Both may show a bank name, a password field, and a statement-related explanation.
The question is where the information goes. A copied description of a legitimate statement process cannot establish that the current prompt belongs to that process.
Do not assume a file is a PDF because the email calls it one. Check the actual file type and any unexpected transition into the browser.
Equally, do not assume a document reader is malicious merely because its name appears in a scam. The recommendation may be copied from genuine banking correspondence.
You do not need to run the suspicious file to resolve the uncertainty. Retrieve the expected statement independently or ask the bank to confirm the communication.
How the Standard Bank Account Statement Email Scam Works
Step 1: A monthly banking task makes the message seem relevant
The email presents itself as a Business Online statement notice. For a finance employee or business owner, that resembles paperwork they may already process regularly.
A monthly record does not need a dramatic threat to attract attention. Reconciliation, bookkeeping, and cash-flow checks all provide ordinary reasons to open it.
The message can therefore exploit routine rather than urgency. The reader may focus on filing the statement instead of verifying its origin.
Check the claimed account relationship first. A business label and a date-like reference do not establish that the notice concerns an account you control.
If someone else normally handles statements, ask them through your existing internal channel. Do not forward the suspicious attachment as though it were already authenticated.
Step 2: Familiar document instructions lower resistance
The email explains how to use a reader and supplies a reason for entering identifying information. This makes the next prompt feel expected rather than intrusive.
That is particularly effective when the procedure resembles a real banking practice. A scam can borrow accurate background instructions while changing the destination receiving the data.
A useful security habit is to separate the instruction from the source. Something you have done safely before may not be safe through an unrelated message.
Do not install a reader, plug-in, or browser extension from the email just to continue. Obtain software through its genuine publisher if you actually need it.
No specific malicious Adobe installer was established in this case. The problem is trusting an unverified workflow, not the existence of a well-known PDF application.
The same caution applies to a security warning printed inside the message. Advice about checking domains can be copied by the very person directing you elsewhere.
Step 3: The attachment or link moves the reader toward a false form
The reported campaign involves deceptive statement material and a counterfeit banking destination. The exact experience should not be assumed identical across every copy.
Even a real browser or document reader can display an untrusted file. Recognizing the application does not verify the document inside it.
Notice whether the task changes. A request to unlock a statement should not silently become a request for your mailbox password or online-banking access.
A page displaying the bank’s name may still be controlled through the reported unrelated domain. Its logo does not connect it to the bank’s protected systems.
If you are uncertain, stop before entering anything. The bank can help you obtain a real statement without requiring experimentation with a suspicious attachment.
Step 4: Information supplied to the form can support further abuse
An identifier, account number, password, and authorization code are different disclosures. Their consequences depend on what was requested and what the recipient actually supplied.
Do not assume every item listed in the email was collected, or that entering a number into a legitimate offline PDF exposed it online.
But if information went to a false form, treat that disclosure seriously. It may help an impersonator tailor later calls or attempt access elsewhere.
If banking credentials or approval codes were involved, contact the bank promptly. Waiting for an unauthorized transfer may waste time that could help contain the incident.
Never read a fresh code to someone calling about the statement. A caller may be trying to complete an action while describing it as verification or cancellation.
Step 5: A failed opening attempt can lead to more requests
A blank document or failed form can look like a reader problem. That may encourage another download, another password attempt, or a call to the supplied support number.
Do not let a failed result expand the information you are willing to provide. A form can receive data even when it does not display the promised document.
Leave the suspicious workflow and use the established banking application or website. Ask verified support about the statement and any information already disclosed.
If an unsolicited caller follows up, end the call and contact the bank yourself. Knowing the timing of your attempt does not establish a genuine support role.
The safest resolution is an independently obtained account record, not a successful-looking screen supplied by the same unverified source.
How to Verify a Standard Bank Statement Safely
Retrieve it from your established account
Open Business Online through the route your business normally uses. Check the relevant account, statement period, and available documents there.
Do not search for a replacement download link from the suspicious notice. The task is retrieving your record, not repairing the sender’s attachment.
If the expected period is missing, ask the bank through a verified contact. Missing paperwork does not make an unsolicited substitute trustworthy.
Use the bank’s actual statement guidance
Standard Bank’s scam guidance specifically warns about false statements and requests for banking or email credentials.
It also explains that genuine eStatements can use an ID number. Do not turn that legitimate detail into a blanket accusation against every protected statement.
For a business-specific format or account, have the bank confirm the applicable procedure. Consumer guidance should not be stretched into a guarantee about every business document.
Verify the destination and the person asking
The reported stabusionlineza address should be retained as an incident detail, not used as a portal. A bank-like word does not establish a bank-controlled host.
Obtain contact information from your existing banking relationship, card, application, or independently opened official website. Do not validate the message by calling its own number.
The bank’s Business Online phishing advice emphasizes independent verification and protecting authentication details.
Work Out What Was Shared Before Choosing the Remedy
Write down where you entered information: a trusted local reader, a browser page, a separate application, or a phone conversation. That detail changes the assessment.
If all you did was receive the notice, do not assume someone controls your banking. Report the message and avoid its attachment.
If a file downloaded but did not run, preserve the filename and location for trusted support. Do not open it again to discover what it would ask.
If you entered identity or account information into an untrusted page, tell the bank exactly which fields were involved.
If you approved a notification or sent a payment, record that separately from the initial document attempt. Those actions may require immediate transaction review.
A clear account of the event is more helpful than saying you were hacked without knowing which account or action was affected.
Keep any sensitive screenshots private. Publicly posting identification numbers or a complete statement can create another disclosure while you are trying to obtain help.
When the Email Contains Details You Recognize
A matching business name or correct account reference can make a statement notice feel convincing. Those details still do not authenticate the attachment or linked form.
Information may be copied from earlier correspondence, public records, or another source. Its presence does not prove that the bank created the current message.
Use the known detail to locate the genuine record independently. Do not provide extra identity information simply because the sender already knows part of it.
If confidential details appear unexpectedly, tell the bank or your security team. They can consider the exposure without assuming the message proves a breach of banking systems.
Keep real statement records separate from the suspicious copy so an investigator can compare them safely. Do not overwrite the genuine document while trying to preserve evidence.
Recognition is a reason for a careful check, not permission to bypass one. The point remains who is receiving your information now.
What to Do if You Have Fallen Victim to This Scam
Stop the statement-opening attempt. Close the untrusted form and do not submit more passwords, identity details, or approval codes.
Save the original notice for investigation. If this is a workplace account, notify the person responsible for banking access and security.
Contact Standard Bank through verified channels. Explain the attachment, destination, and specific information you supplied.
Ask whether online access, payment instruments, or pending activity need protective measures. Follow the bank’s advice for the actual account involved.
Secure exposed authentication details. Replace any disclosed banking or email password through the genuine service and review unauthorized sessions or recovery changes.
A password change cannot retract an ID number already shared. Keep the account-access response separate from the identity-information response.
Review approvals, payees, and transactions. Report unfamiliar activity promptly, especially if a code or banking-app confirmation was supplied.
Do not approve another action because a caller says it reverses the first one. Read the real banking prompt and verify independently.
Document identity exposure accurately. Record which ID, passport, business, or account details went to an untrusted recipient.
Ask the bank and relevant local identity-support channels about appropriate safeguards. Avoid assuming that every listed identifier was stolen if you never provided it.
Check suspicious software or files with trusted support. If something ran or an unexpected reader was installed, investigate the device as well.
Malwarebytes can check for potential malware. AdGuard may reduce deceptive advertising, but neither replaces bank action or removes copies of disclosed identity information.
Report the message and keep a private record. Use the bank’s official phishing-reporting instructions and your email provider’s reporting tools.
Retain relevant transaction references and correspondence. Reject anyone demanding another fee or account approval to recover money or unlock the missing statement.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is this Standard Bank statement notice genuine?
The described campaign is an impersonation. Confirm the statement in your real banking account instead of relying on the attachment or reported counterfeit destination.
Are statements protected with an ID number always scams?
No. Standard Bank describes legitimate ID-protected eStatements. The crucial questions are authenticity, where information is entered, and whether the request expands into account credentials.
Is Adobe Reader responsible for the scam?
No. Mentioning a genuine reader does not authenticate the message. This case does not establish that an official Adobe download is malicious.
Does opening a password-protected PDF send my ID online?
Not necessarily. A trusted local document can use a password without submitting it online. An untrusted web form is a different interaction and needs separate assessment.
What if I gave a banking code after opening the notice?
Contact the bank immediately through a verified route. Explain the code and any approval shown, because they may relate to a real action rather than document viewing.
Can scanning recover identity details already disclosed?
No. A scan can address malicious device software. Shared identifiers, account access, and unauthorized transactions require their own protective steps.
The Bottom Line
Do not open or unlock a statement through this fraudulent notice. Familiar document instructions cannot authenticate an attachment or a website requesting your details.
Retrieve the record through your real banking account. If you already disclosed information, contact the bank and explain precisely where it was entered and what followed.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.