

An administrator warns that your domain ownership has expired. Email access will supposedly end within 72 hours, taking new messages and customer replies with it.
The revalidation button offers an immediate rescue. Before using it, separate a real domain renewal from a mailbox emergency created inside one email.
Overview
The warning combines two different services into one crisis
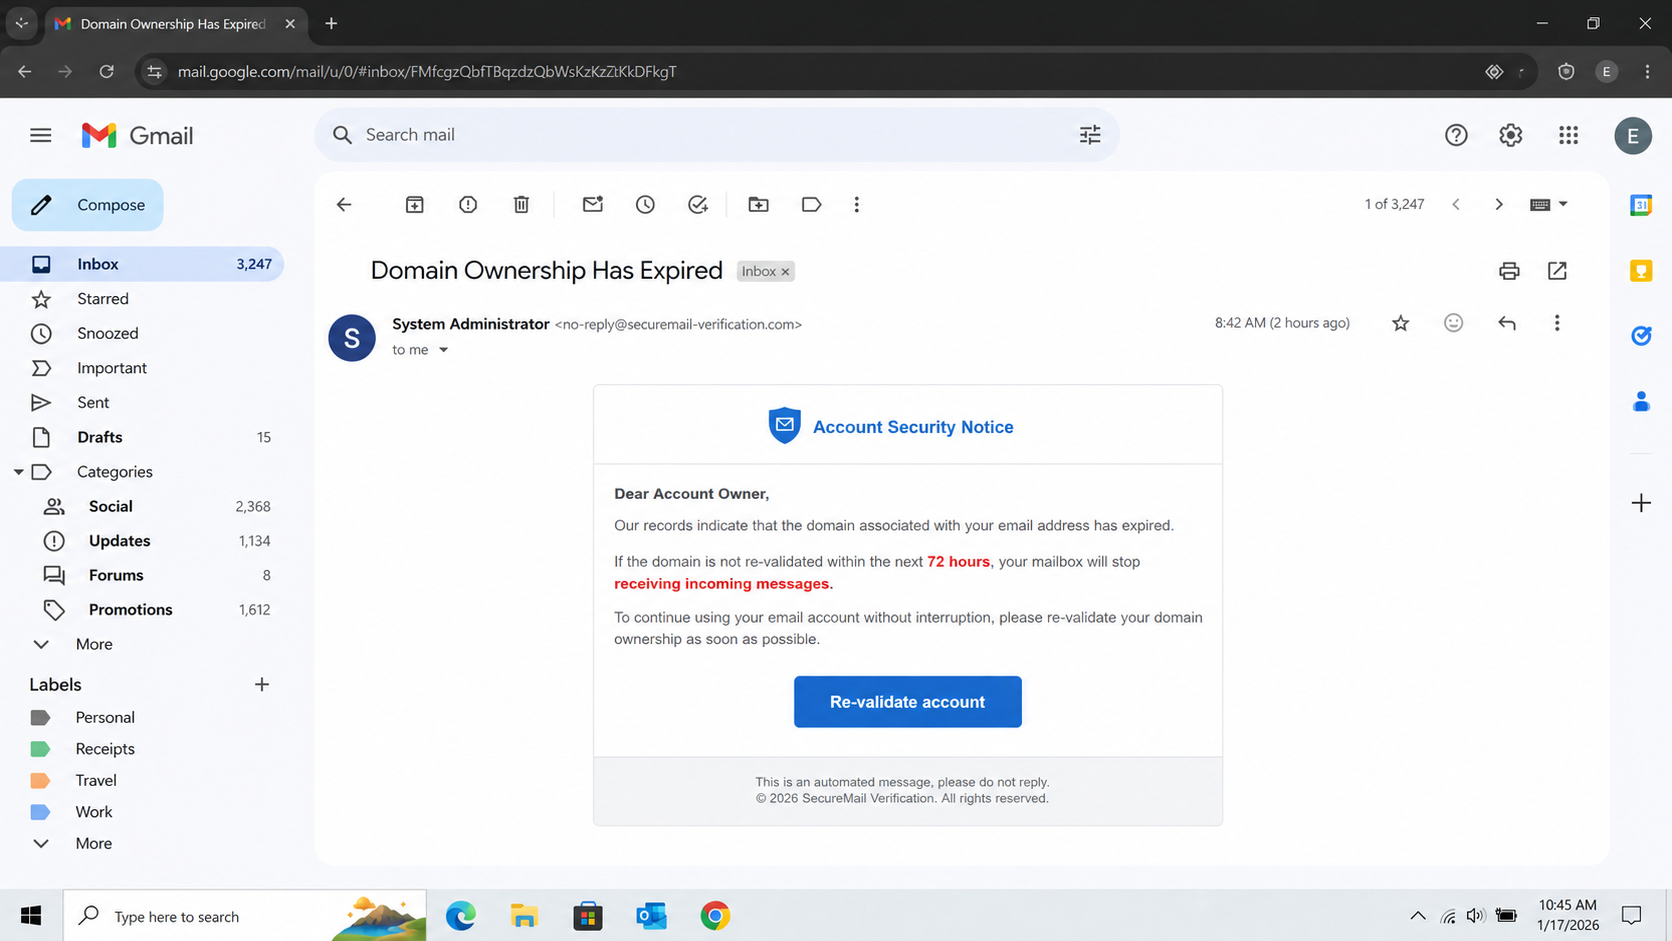
The Domain Ownership Has Expired email scam claims a recipient’s internet domain is no longer valid and that associated mailbox access will soon stop.
One version uses the subject “Re-validate your account” and announces a 72-hour deadline. Incoming and outgoing messages are supposedly being held.
The notice offers a revalidation portal as the solution. That button does not lead to the recipient’s registrar, hosting provider, or established webmail login.
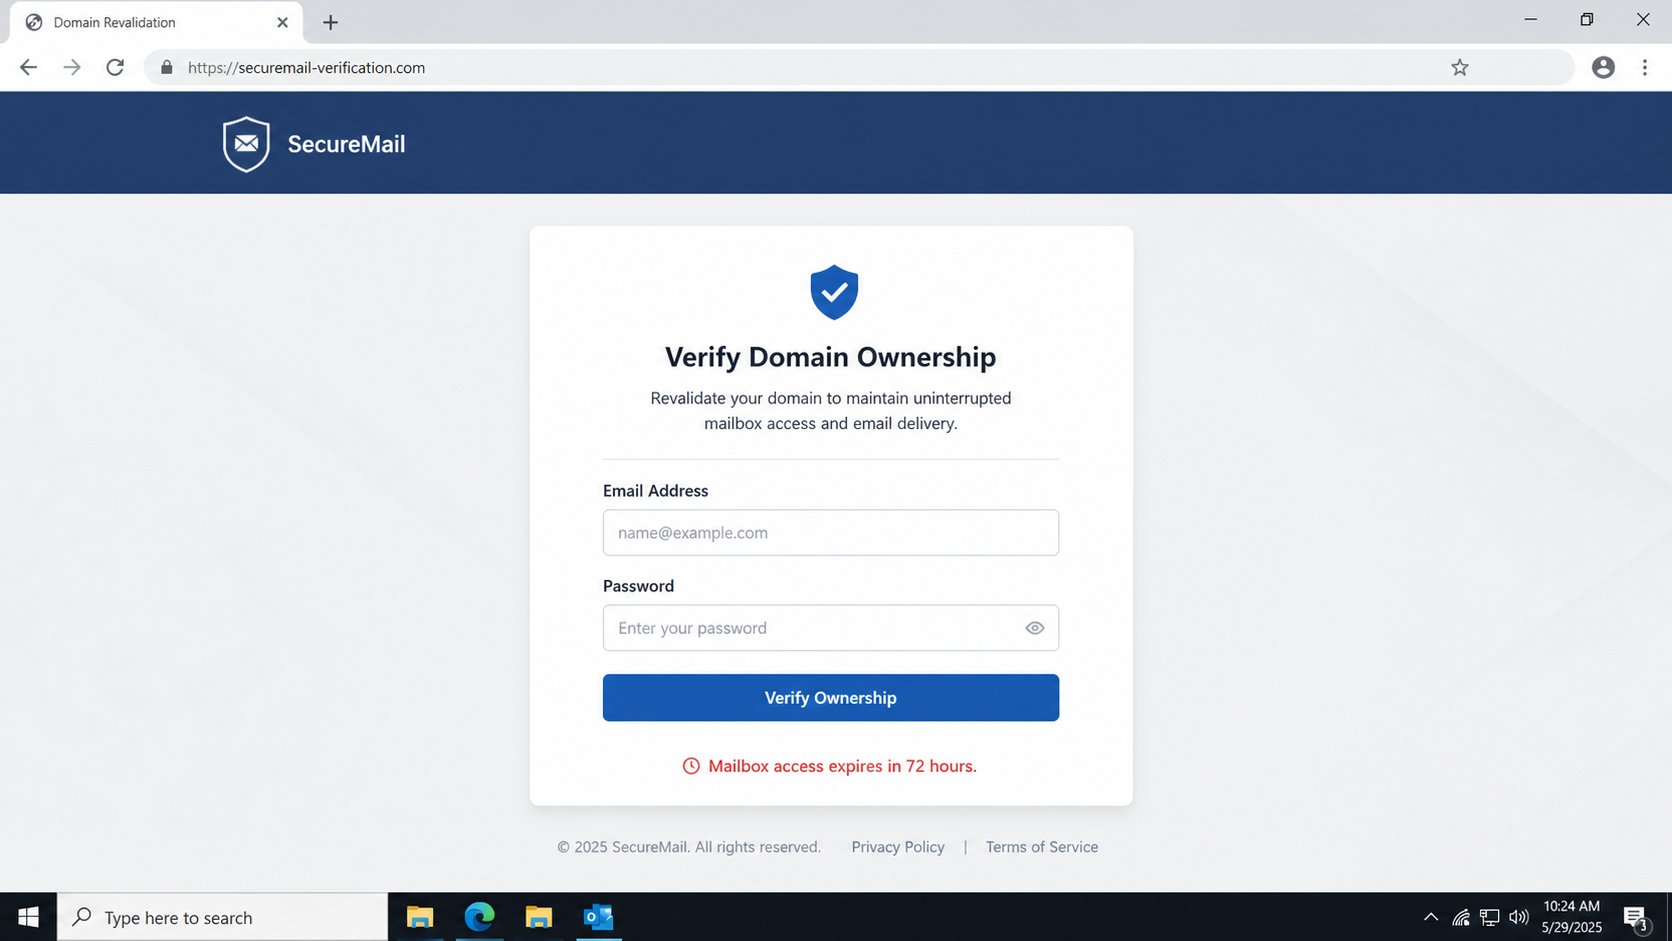
Instead, it opens a counterfeit authentication page intended to collect the email address and password entered by the visitor.
Domain registration, DNS hosting, website hosting, and mailbox service can be supplied by different companies with separate billing dates.
Scammers blur those distinctions. Confusion makes an off-domain password form appear like a reasonable administrative shortcut.
Small organizations are especially exposed to this story
Owners of small websites may not remember which company manages registration, nameservers, hosting, certificates, and email.
Renewals can arrive annually, sometimes through a developer or reseller. A vague warning may land when the responsible person is away.
Shared roles such as info, office, billing, and admin often receive the message. Staff monitoring those inboxes may feel responsible for preventing an outage.
The threat is operational rather than personal. Lost customer mail, failed invoices, and an offline website can push a recipient toward immediate action.
A real expiration status can be checked independently. The domain’s registrar dashboard and billing records should agree with any genuine renewal notice.
The counterfeit portal wants a working mailbox credential
The landing page may display a shield, generic “SecureMail” branding, or the recipient’s domain name. Those elements are inexpensive to generate dynamically.
It asks for the existing email password, claiming that authentication confirms ownership. In reality, possession of a mailbox password does not renew a domain registration.
Warning signs include:
- The sender never names the actual registrar.
- The expiration date and domain are missing or inaccurate.
- Mailbox suspension is tied to a vague 72-hour deadline.
- The button opens a domain unrelated to your providers.
- The page requests an existing email password.
- No invoice, account number, or renewal term appears.
- Support contacts exist only inside the warning.
Receiving the email does not alter the domain. The immediate danger is submitting credentials to the fake revalidation page.
Owners should type their registrar address manually and inspect domain status there. Employees should forward the notice to the known administrator without clicking.
If a password was submitted, act as though the mailbox is compromised. A stolen inbox can create far more damage than the fictional expiration.
How The Scam Works
Step 1: Public domain records help select targets
Websites expose domain names, company contacts, and role-based email addresses. Automated tools can collect them without entering any private system.
Registration privacy hides many owner details, but public pages still list sales, support, legal, and administrative mailboxes.
The attacker does not need to know the real renewal date. A broad annual warning will coincide with genuine administrative work for some recipients.
Business domains are valuable because one mailbox may reveal customer conversations, invoices, staff directories, and password-reset messages.
Target lists can also come from earlier breaches. Those records may associate a domain with a person’s name and job title.
Step 2: The subject presents an administrative fact
“Domain Ownership Has Expired” sounds like a completed status, not a marketing reminder. That phrasing discourages the recipient from treating it as optional.
The body may say ownership must be revalidated rather than renewed. Revalidation avoids explaining a price, term, invoice, or payment method.
Generic words such as system administrator and hosting service conceal who supposedly sent the notice.
A legitimate provider can name the exact domain, expiration date, account reference, renewal period, and account holder.
Missing records are not a harmless oversight when the message asks for credentials. They are evidence that the sender cannot describe the alleged account.
Step 3: Mail delivery is used as leverage
The warning claims incoming and outgoing mail will be suspended, rejected, or held after 72 hours.
Email is vital for sales, support, payroll, and account recovery. The possibility of silent message loss creates pressure beyond the website itself.
The claim may be technically muddled. Domain registration can affect services eventually, but an arbitrary email button does not restore ownership.
Some hosting arrangements continue temporarily during renewal grace periods. Exact behavior belongs in the registrar’s documented policies, not the attacker’s countdown.
Check real service dashboards before assuming an outage. If mail is functioning normally, that also contradicts claims that messages are already held.
Step 4: The revalidation link leaves trusted infrastructure
Button text may say “Re-validate account,” “Confirm ownership,” or “Keep mailbox active.” The underlying destination controls the actual action.
Attackers register domains containing secure, mail, server, ownership, or verification. Those reassuring words do not establish a provider relationship.
Subdomains can also display the victim’s brand before an attacker-owned main domain. Read the hostname from right to left near its public suffix.
A padlock only means the browser encrypted traffic to that host. It can securely deliver a password to a criminal server.
Use a saved bookmark or typed provider address. Never navigate to billing or security portals through an unsolicited expiration warning.
Step 5: A generic portal imitates hosted webmail
The fake site may avoid copying one famous provider. Generic webmail branding works for thousands of small domains and hosting resellers.
It can prefill the email address from a value encoded in the link. That personalization does not require access to the mailbox.
A form asks for the current password, sometimes twice. An error after the first submission may simply collect a second attempt.
No legitimate domain renewal requires revealing the mailbox password to an unrelated verification site.
After collection, the page can display success or redirect to the real webmail service, leaving the victim unaware of the theft.
Step 6: Attackers test the password against real services
The captured address identifies the likely mail domain. Automated tools can discover common webmail, Microsoft 365, Google Workspace, or hosting-panel endpoints.
If the credential works, the intruder can read messages and search for billing, invoices, customer records, and authentication links.
Password reuse creates additional exposure. The same value may open registrar, hosting, cloud storage, or accounting accounts.
Multifactor prompts may follow immediately. Approving one that was not initiated can turn a stolen password into full access.
Quiet attackers create forwarding rules or application passwords. Those mechanisms can continue collecting mail after the main password changes.
Step 7: A real business identity powers later fraud
A compromised company mailbox gives messages an authentic sender, signature, and conversation history.
Criminals can alter payment instructions, request gift cards, send malware, or ask coworkers for confidential documents.
Registrar access would create another danger. DNS changes can redirect websites, email, and authentication traffic toward attacker-controlled systems.
Administrators should therefore inspect mailbox and domain accounts separately. One password reset cannot resolve every possible route.
Early reporting helps warn customers and staff before they trust secondary messages sent from the genuine address.
Domain Registration and Email Hosting Are Not the Same Thing
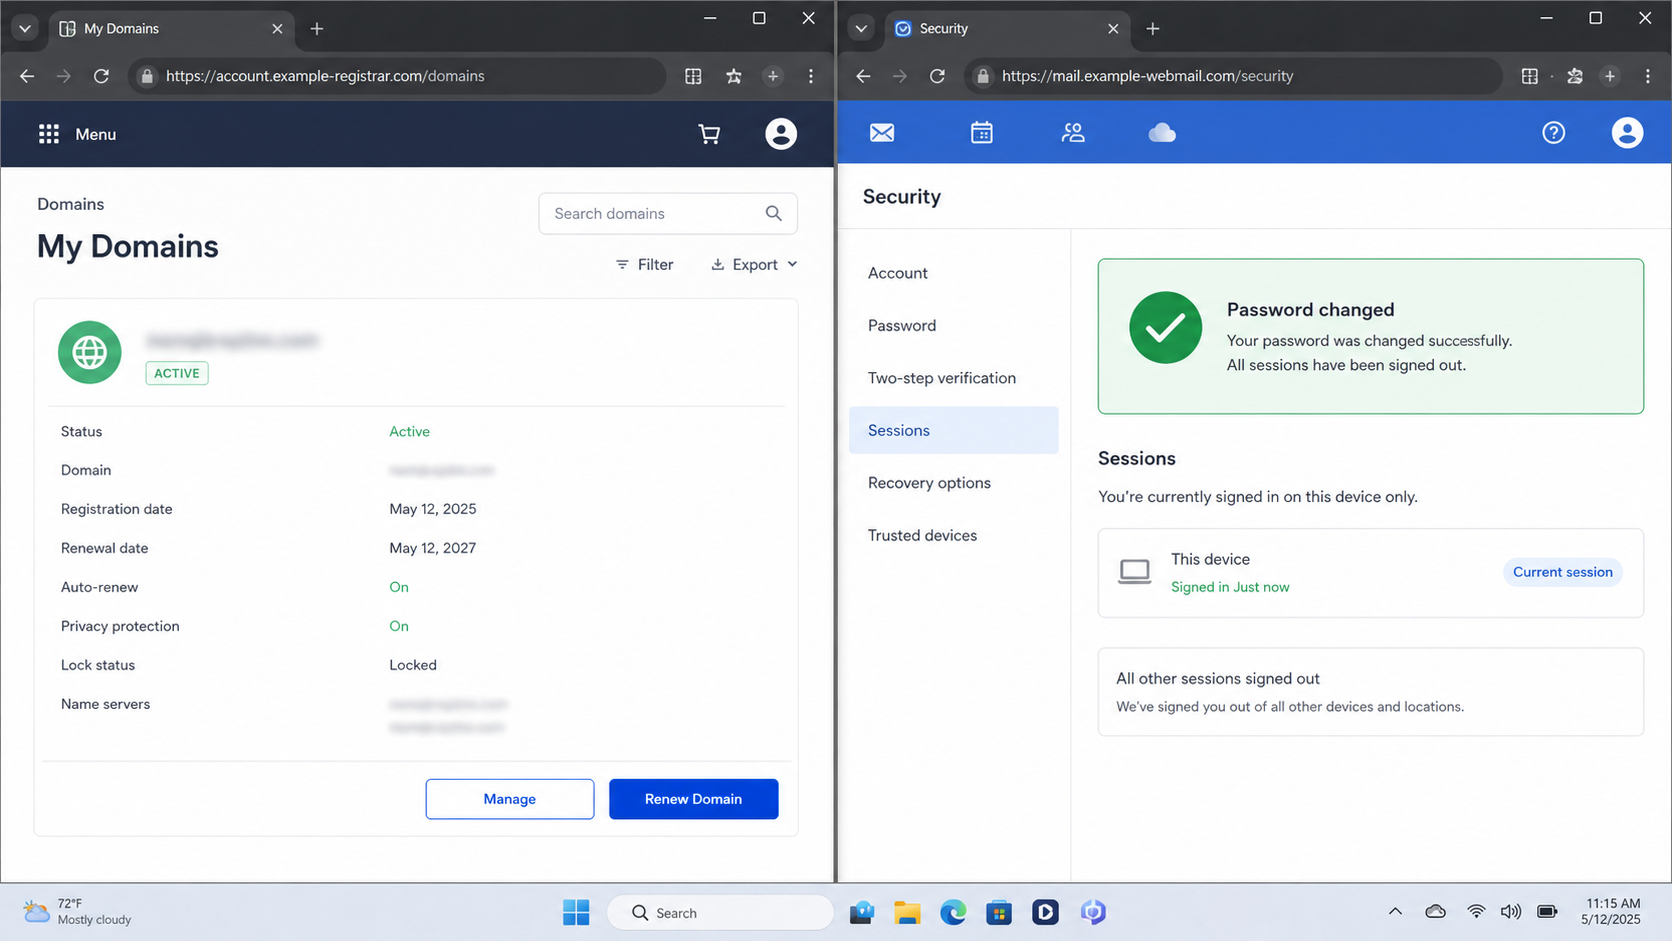
A registrar records the right to use a domain name for a defined term. The registrar account normally handles renewal, contacts, and transfer controls.
DNS nameservers direct internet services toward the correct website and mail systems. They may be operated by the registrar or another provider.
Web hosting stores the site, while email hosting stores mailboxes. Each service can have a separate account, password, invoice, and support team.
Some businesses buy everything through one vendor. Others use four companies, which is why vague “service administrator” notices can create confusion.
Renewing a domain usually occurs inside the registrar dashboard and involves a term and payment. Entering a mailbox password does not perform that transaction.
A genuine registrar notice names the domain and expiration date. It should correspond with the status already visible after independent login.
Webmail credentials authenticate one user to a mail service. They do not demonstrate legal ownership of the entire internet domain.
Understanding these roles makes the scam easier to reject. Its promised fix does not match the administrative problem it claims occurred.
Sender, Registrar, Mailbox, and Recovery Checks
Identify every real provider involved
Document the registrar, DNS host, web host, email provider, reseller, and responsible internal administrator.
Use past invoices, contracts, saved bookmarks, and verified account records. Do not let the warning define who supposedly manages the domain.
Businesses should keep this information available to more than one trusted person so urgent notices can be checked during absences.
Compare dates and status in the registrar dashboard
Log in through the registrar’s known address. Review expiration, auto-renewal, payment method, transfer lock, nameservers, and recent account activity.
If the domain is active through a future date, capture that evidence and report the false notice.
If renewal is genuinely due, complete it within the official dashboard. The phishing email remains unsafe even when its timing is coincidentally accurate.
Inspect mailbox security for hidden persistence
Review sessions, forwarding destinations, filters, delegates, recovery methods, application passwords, POP access, IMAP access, and connected applications.
Look for deleted security alerts, unusual sent messages, and password resets. An intruder may conceal activity by redirecting or marking mail.
Terminate all sessions after changing the password. Existing browser or mail-client tokens may otherwise remain active.
Protect the domain account separately
Use a unique registrar password and phishing-resistant multifactor authentication. Enable transfer lock and change alerts where available.
Confirm registrant contacts and nameservers have not changed. DNS tampering can affect the website and every mailbox simultaneously.
For valuable domains, consider registry lock, multiple authorized contacts, and documented recovery procedures with the provider.
What to Do if You Have Fallen Victim to This Scam
- Leave the fake revalidation page. Do not submit another password or contact the support information shown on that site.
- Replace the mailbox password. Open the real provider directly from a clean device and choose a unique, previously unused passphrase.
- Sign out every session. Revoke remembered browsers, application passwords, mail clients, tokens, and unfamiliar connected applications.
- Remove malicious mailbox changes. Inspect forwarding, filters, delegates, recovery contacts, and automatic replies for unauthorized entries.
- Secure the registrar account. Check expiration, nameservers, contacts, transfer status, payment records, and recent logins independently.
- Change reused credentials elsewhere. Prioritize hosting, DNS, cloud storage, accounting, banking, and workplace identities that shared the exposed password.
- Run Malwarebytes if files or extensions appeared. Credential submission alone differs from malware, but unexpected downloads require a full scan.
- Use AdGuard for supplementary filtering. It can reduce malicious page access, while verified bookmarks and domain checking remain the primary defense.
- Notify administrators and contacts. Warn staff about messages sent from the compromised inbox and ask finance teams to verify payment changes.
- Preserve and report evidence. Save headers, URLs, screenshots, account alerts, and timestamps for the provider and appropriate authorities.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Can a domain really expire?
Yes, registrations have renewal dates. However, that fact does not make an unsolicited revalidation email or unrelated password page legitimate.
Check the date and status inside the registrar’s official dashboard.
Would an expired domain stop email?
Domain and DNS problems can eventually disrupt mail routing, but exact timing depends on providers, grace periods, and configuration.
An arbitrary 72-hour threat should be verified through the registrar and mail host, not accepted at face value.
Why does the page already know my email address?
The campaign can place the address inside the link and prefill it on arrival. That does not mean the page connected with the real mailbox.
Public websites and breaches also expose role-based and individual addresses.
Does HTTPS prove the revalidation portal is safe?
No. HTTPS encrypts traffic to the domain shown in the address bar, including traffic sent to a phishing server.
Ownership and expected destination matter. A padlock cannot turn an unrelated domain into your registrar.
What if my domain is actually near expiration?
Open the registrar independently and renew there if necessary. A coincidental expiration does not validate the email’s link.
Review why the phishing sender knew the contact address, but do not disclose credentials to investigate.
Is changing the email password enough?
Not always. Revoke sessions, remove forwarding and connected applications, check reused passwords, and secure the registrar account separately.
Business administrators should review audit logs for messages or account changes made before recovery.
The Bottom Line
The Domain Ownership Has Expired email scam combines registration anxiety with a counterfeit mailbox login. Its proposed fix does not match the claimed problem.
Check domain status through the registrar you already use. Never supply an email password to an unrelated revalidation portal.
If credentials were entered, secure the mailbox and registrar separately, revoke sessions, inspect persistence, and alert contacts who could receive later impersonation.
Clear provider records and trusted bookmarks remove much of the scam’s leverage. Administrative confusion should lead to verification, not hurried authentication.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.