

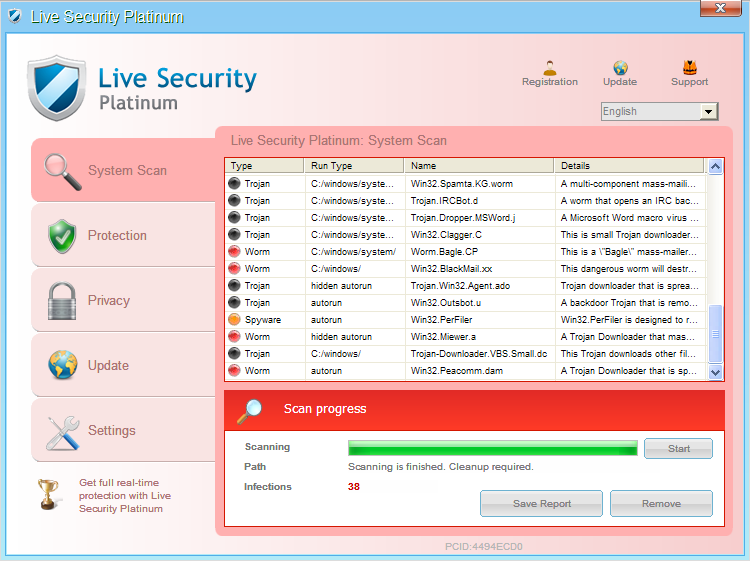
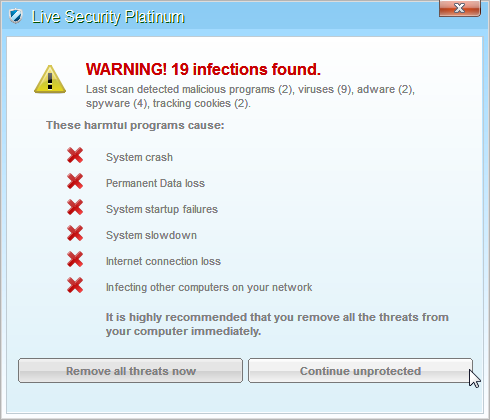
Live Security Platinum is a malicious program also known as rogue security software, which will display fake security alerts in an attempt to scare you into buying this fake security product.
In addition, Live Security Platinum has also hijacked your PC,blocking your from running files,so now when your trying to open and executable file (file ending with .exe), this program will instead display this fake alerts:
Warning!

Application cannot be executed. The file rdpclip.exe is infected. Please active your antivirus software.
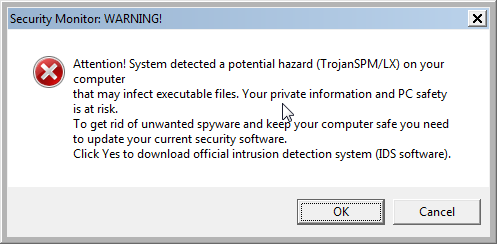
Security Monitor: WARNING!

Attention! System detected a potential hazard (TrojanSPM/LX) on your computer that may infect executable files. Your private information and PC safety is at risk.

To get rid of unwanted spyware and keep your computer safe you need to update your current security software.

Click Yes to download official intrusion detection system (IDS software).
Live Security Platinum Warning Spyware.IEMonster activity detected. This is spyware that attempts to steal passwords from Internet Explorer, Mozilla FireFox, Outlook and other programs. Click here to remove it immediately with Live Security Platinum
Live Security Platinum Firewall Alert Live Security Platinum Firewall has blocked a program from accessing the Internet. Internet Explorer Internet Browser is infected with SVCHOST.Stealth.Key-logger. This worm is trying to send your credit card details using Internet Explorer Internet Browser to connect to remove host
Live Security Platinum will also cause malicious browser redirects and system slowdowns so it needs to be removed from your computer as soon as possible.
This is are a few images of Live Security Platinum:
Registration codes for Live Security Platinum
As an optional step,you can use the following license key to register Live Security Platinum and stop the fake alerts.
AA39754E-715219CE
Please keep in mind that entering the above registration code will NOT remove Live Security Platinum from your computer , instead it will just stop the fake alerts so that you’ll be able to complete our removal guide more easily.
Live Security Platinum Removal Guide
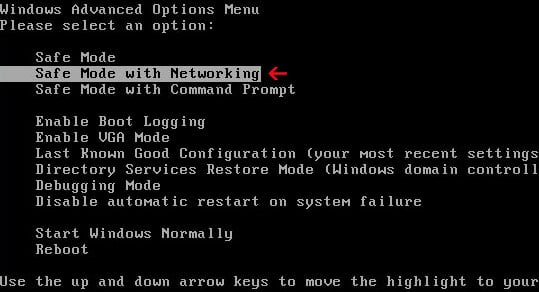
STEP 1 : Start your computer in Safe Mode with Networking
- Remove all floppy disks, CDs, and DVDs from your computer, and then restart your computer.
- Press and hold the F8 key as your computer restarts.Please keep in mind that you need to press the F8 key before the Windows start-up logo appears.
Note: With some computers, if you press and hold a key as the computer is booting you will get a stuck key message. If this occurs, instead of pressing and holding the “F8 key”, tap the “F8 key” continuously until you get the Advanced Boot Options screen. - On the Advanced Boot Options screen, use the arrow keys to highlight Safe Mode with Networking , and then press ENTER.
STEP 2: Remove Live Security Platinum malicious proxy server
Live Security Platinum may add a proxy server which prevents the user from accessing the internet,follow the below instructions to remove the proxy.
- Start the Internet Explorer browser and if you are using Internet Explorer 9 ,click on the gear icon
 (Tools for Internet Explorer 8 users) ,then select Internet Options.
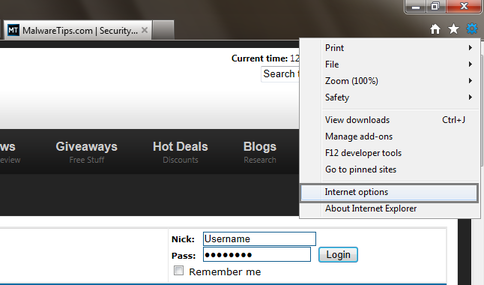
- Go to the tab Connections.At the bottom, click on LAN settings.
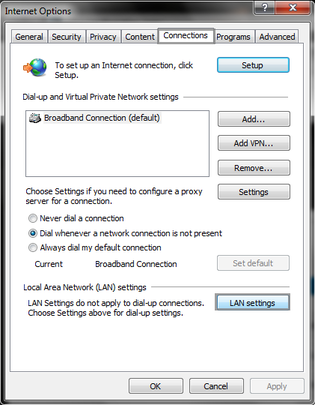
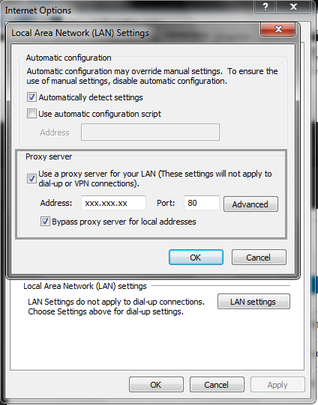
- Uncheck the option Use a proxy server for your LAN. This should remove the malicious proxy server and allow you to use the internet again.
 (Tools for Internet Explorer 8 users) ,then select Internet Options.
If you are a Firefox users, go to Firefox(upper left corner) → Options → Advanced tab → Network → Settings → Select No Proxy
STEP 3: Repair your Windows Registry from Live Security Platinum malicious changes.
Smart Fortress 2012 has changed your Windows registry settings so that when you try to run a executable file (ending with .exe ) , it will instead launch the infection rather than the desired program.
- Download the registryfix.reg file to fix the malicious registry changes from Live Security Platinum.
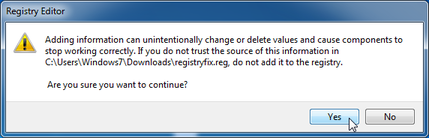
Download RegistryFix.regOpens the download page in a new tab. - Double-click on registryfix.reg file to run it. Click “Yes” for Registry Editor prompt window,then click OK.
STEP 4: Run RKill to terminate known malware processes associated with Live Security Platinum.
RKill is a program that will attempt to terminate all malicious processes associated with Live Security Platinum,so that we will be able to perform the next step without being interrupted by this malicious software.
Because this utility will only stop Live Security Platinum running process, and does not delete any files, after running it you should not reboot your computer as any malware processes that are configured to start automatically will just be started again.
- While your computer is in Safe Mode with Networking ,please download the latest official version of RKill.Please note that we will use a renamed version of RKILL so that Live Security Platinum won’t block this utility from running.
Download RKillYour download starts right away. - Double-click on the iExplore.exe icon in order to automatically attempt to stop any processes associated with Live Security Platinum.

- RKill will now start working in the background, please be patient while the program looks for various malware programs and tries to terminate them.
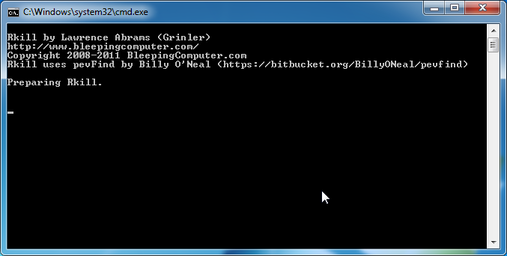
IF you are having problems starting or running RKill, you can download any other renamed versions of RKill from here. - When Rkill has completed its task, it will generate a log. You can then proceed with the rest of the guide.
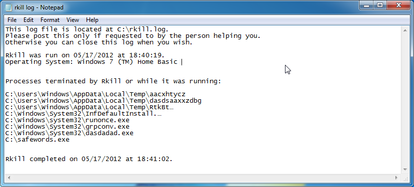

WARNING: Do not reboot your computer after running RKill as the malware process will start again , preventing you from properly performing the next step.
STEP 5: Remove Live Security Platinum malicious files with Malwarebytes Anti-Malware FREE
- Download the latest official version of Malwarebytes Anti-Malware FREE.
Download MalwarebytesFree official installer. Your download starts right away. - Start the Malwarebytes’ Anti-Malware installation process by double clicking on mbam-setup file.

- When the installation begins, keep following the prompts in order to continue with the setup process. Do not make any changes to default settings and when the program has finished installing, make sure you leave both the Update Malwarebytes’ Anti-Malware and Launch Malwarebytes’ Anti-Malware checked. Then click on the Finish button. If Malwarebytes’ prompts you to reboot, please do not do so.
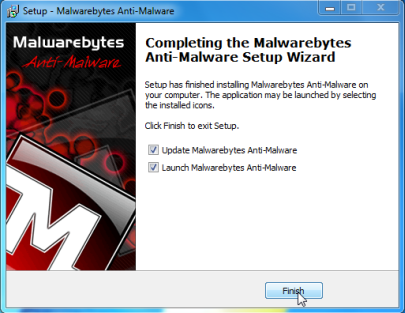
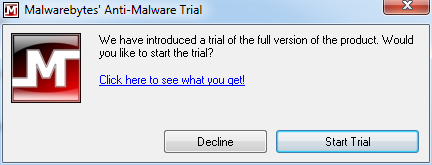
- Malwarebytes Anti-Malware will now start and you’ll be prompted to start a trial period , please select ‘Decline‘ as we just want to use the on-demand scanner.
- On the Scanner tab,select Perform full scan and then click on the Scanbutton to start scanning your computer.
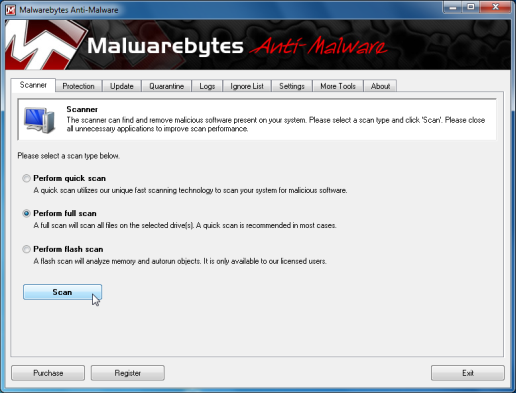
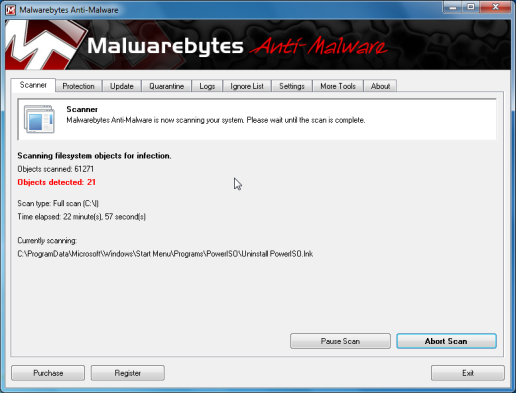
- Malwarebytes’ Anti-Malware will now start scanning your computer for Live Security Platinum malicious files as shown below.
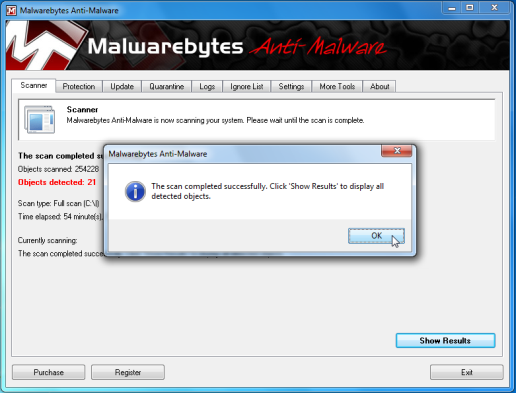
- When the scan is finished a message box will appear, click OK to continue.
- You will now be presented with a screen showing you the malware infections that Malwarebytes’ Anti-Malware has detected.Please note that the infections found may be different than what is shown in the image.Make sure that everything is Checked (ticked) and click on the Remove Selectedbutton.
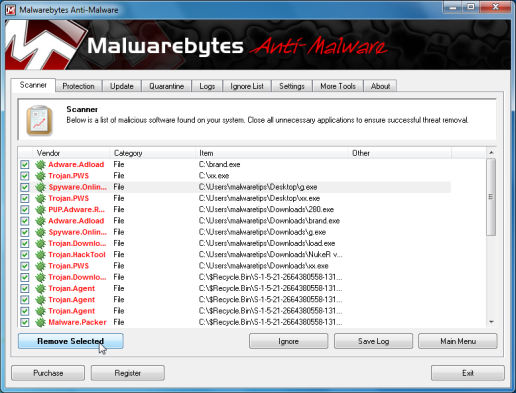
- Malwarebytes’ Anti-Malware will now start removing the malicious files.After completing this task it will display a message stating that it needs to reboot,please allow this request and then let your PC boot in Normal mode.

STEP 6: Double check your system for any left over infections with HitmanPro
- This step can be performed in Normal Mode ,so please download the latest official version of HitmanPro.
Download HitmanProOfficial Sophos download. Free scan, free 30-day trial to remove threats. - Double click on the previously downloaded fileto start the HitmanPro installation.

IF you are experiencing problems while trying to starting HitmanPro, you can use the “Force Breach” mode.To start this program in Force Breach mode, hold down the left CTRL-key when you start HitmanPro and all non-essential processes are terminated, including the malware process. (How to start HitmanPro in Force Breach mode – Video) - Click on Next to install HitmanPro on your system.
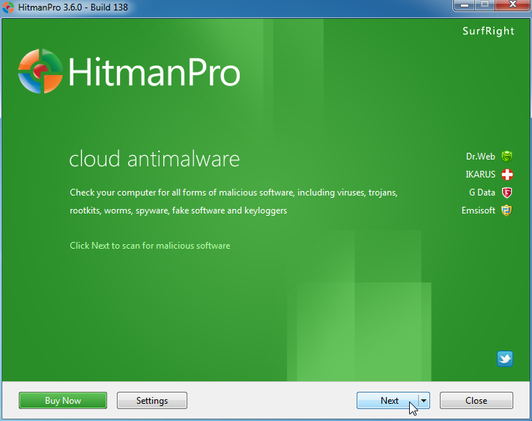
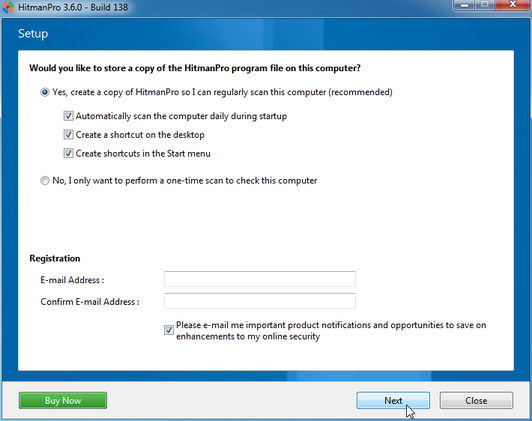
- The setup screen is displayed, from which you can decide whether you wish to install HitmanPro on your machine or just perform a one-time scan, select a option then click on Next to start a system scan.
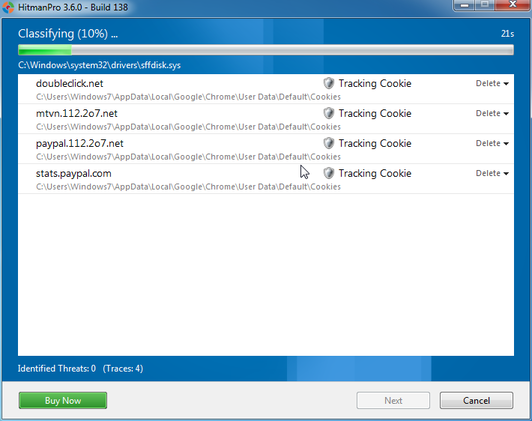
- HitmanPro will start scanning your system for malicious files. Depending on the size of your hard drive, and the performance of your computer, this step will take several minutes.
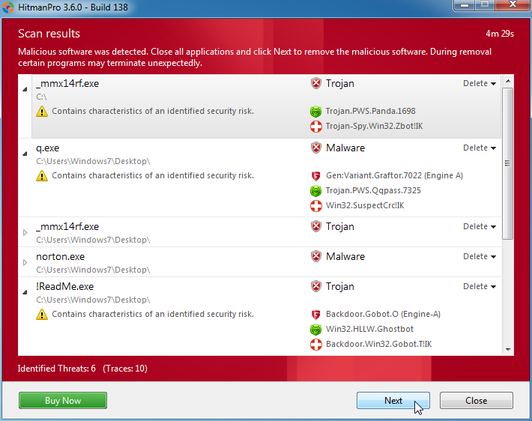
- Once the scan is complete,a screen displaying all the malicious files that the program found will be shown as seen in the image below.After reviewing each malicious object click Next.
- Click Activate free license to start the free 30 days trial and remove the malicious files.
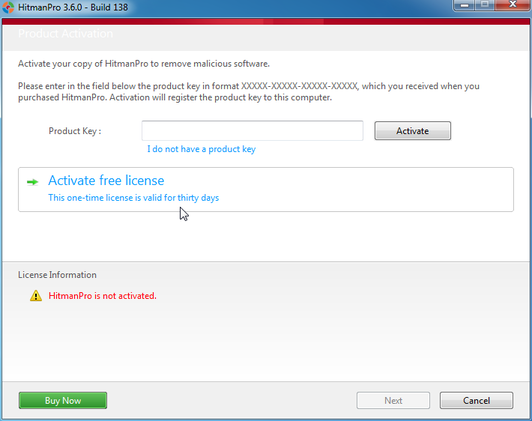
- HitmanPro will now start removing the infected objects, and in some instances, may suggest a reboot in order to completely remove the malware from your system. In this scenario, always confirm the reboot action to be on the safe side.

STEP 7: Remove any left over malicious registry keys and files
Live Security Platinum has sadded some malicious registry keys to your Windows installation , to remove this malicious changes we need to run a scan with RogueKiller
- Please download the latest official version of RogueKiller.
Download RogueKillerOpens the download page in a new tab. - Double click on RogueKiller.exe to start this utility and then wait for the Prescan to complete.This should take only a few seconds and then you can click the Start button to perform a system scan.
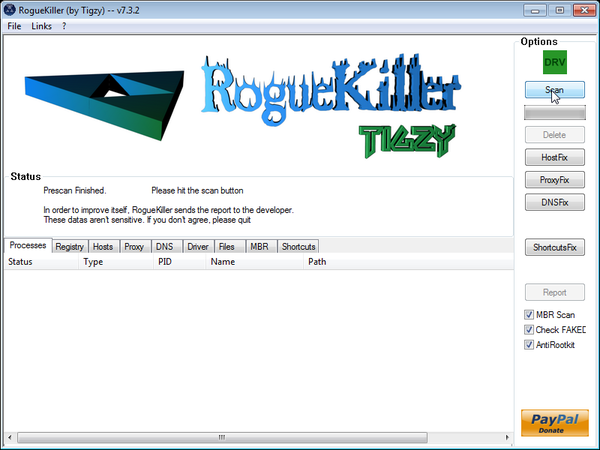
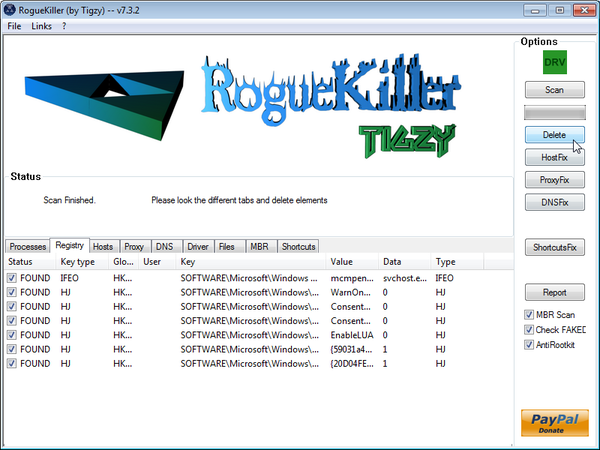
- After the scan has completed, press the Delete button to remove any malicious registry keys.
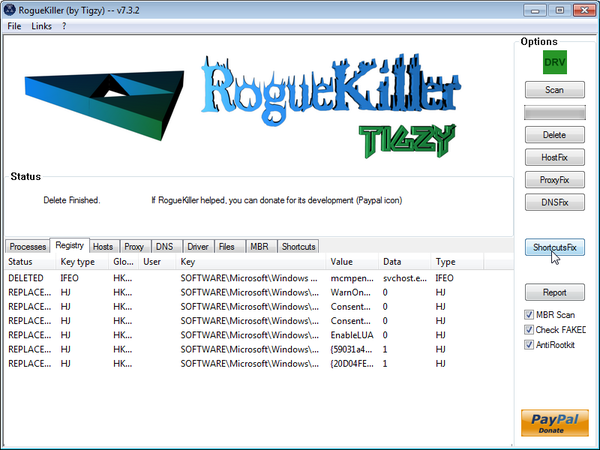
- Next we will need to restore your shortcuts, so click on the ShortcutsFix button and allow the program to run.

Join the discussion
538 commentsShare your experience or ask a question about this article.
Your progress
Did these steps help?
Let us know how the guide worked for you.
Describe what you see and the step you reached. Keep passwords and other private information out.
Discussion
It’s really a wonderful easy step by step removal of harmful marlware. I was shocked to see that my computer was affected. After reading your article, I got the confidence to do it myself and followed your 6 steps and everything went fine. Now my computer is without any malware. I really thank you for this wonderful article.
I love you Mr. Stelian Pilici!
Stelian
Thank you. Thank you. Thank you. Everything worked perfectly. My computer actually feels like it is running faster now!!
Sanjay
Hello Stelian:
I posted earlier thanking you – but now have a question. How do these people
continue on the web collecting unsuspecting users credit card information and using it without eventually getting caught? You would think that the credit card police would be able to track them down. Do you have any insight into this? – Thanks (more just wanting to vent my frustration – not only about going through the fix – which you made easy – but going through the initial panic when your computer/programs/data won’t run)
In reply to Debbie
Hello Debbie,
This cyber criminals are usually from China,Russia or another eastern European countries,and at some point they get caught however it takes along time for this to happen because different organizations across the globe from need to work together.As you imagine this process is not very quick and all the investigations take some time so from here comes the need for a International cyber crime police divison.
Another problem is that users aren’t even aware that they have been the victim of cyber criminals and they don’t report it.
Here is some very interesting video which you can watch:
http://www.youtube.com/watch?v=cf3zxHuSM2Y
http://www.youtube.com/watch?v=WQgeUHlTThc
Just today,there are reports that 3 cyber criminals where convicted to 8 years of prison for install keyloggers on some computers: http://nakedsecurity.sophos.com/2012/07/16/seattle-cybercrime-trio-sentenced-for-3m-hacking-spree-via-wifi-and-malware/
You ROCK!!!! All of the virus seems to be gone from my computer – I had this or a similar virus approximately 1 year ago and we wound up cleaning off the hard drive and starting over. Thank you, thank you, thank you.
Stelian, you are a saint! I initially thought this virus had totalled my computer (since nothing would open), but thanks to you and your six easy steps, everything seems to be back to normal. I am running the Kaspersky scan just to be extra-sure, but all seems to be going well. Thanks so much!
In reply to Lauren
Kaspersky did catch something the others did not. Here’s the report:
: Deleted (events: 1)
7/16/2012 9:20:17 PM Deleted Trojan program Trojan.Win32.Inject.eift C:\Documents and Settings\Lauren\AppData\LocalLow\Sun\Java\Deployment\cache\6.0\55\25877b37-15c52381 High
In reply to Lauren
Based on that report, I am now concerned about the Java icon that appeared on my toolbar at some point during the virus attack and keeps saying it needs to be updated. How do I get rid of this?
Thanks again, Stelian.
In reply to Lauren
Hello Lauren,
You can also run an ESET scan if you have the time:
Run a scan with ESET Online Scanner
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
Thanks so much! The instructions were amazing for someone who is not at all computer savvy. I was able to delete the malware myself and am very grateful.
Lavinia
I am trying to remove the virus for the 2nd time– thought I had it last night ( followed instructions) only to find it was in place when I started the computer this morning.
I don’t remember getting a “re-start” message after the latest scan with malwarebytes.. but apparrently 7 files were removed
Now the computer seems to be hung up at removing a trojan — while on the 2nd sweep, with Hitman
also for your info.. there was no Proxy checked on the LAN settings
any suggestions?
In reply to Heather
Hello,
Lets try do this another way.Please follow the below steps:
STEP 1. While in NORMAL MODE,download HitmanPro and then start this program in ForceBreach Mode
1.Here are the direct download links for HitmanPro,
– http://dl.surfright.nl/HitmanPro36.exe (For 32bit)
– http://dl.surfright.nl/HitmanPro36_x64.exe (For 64bit)
2.Hold down the left CTRL-key when you start HitmanPro and all non-essential processes are terminated, including this rogue malicious process
Here is a video that explains with graphic details how to do this : http://www.youtube.com/watch?v=m6eRWTv2STk
3. Let HitmanPro scan and remove the detected infections.
STEP 2: While in NORMAL MODE,download/Run Rkill and then run a scan with Malwarebytes
1.Download any re-named version of Rkill (direct download links bellow):
RKILL DOWNLOAD LINK #1
RKILL DOWNLOAD LINK #2
RKILL DOWNLOAD LINK #3
2.Next,please perform a scan with Malwarebytes as seen on the guide.
STEP 3. Run a scan with ESET Online Scanner
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
Waiting for your reply to tell me how everything is working.. :) Good luck!
Thanks a lot for this step by step guide. Really helpful!
Dear Stelian
Thanks this virus/trojan got into my computer too. Could still use the internet but antivirus and makware remover wouldnt work, and couldnt remove the pirate program either
The people doing these things are malicious arent they?
Managed without too much effort by following yr instructions…..
You laid it out very simply, you should also do something paid….. for sale, great style, that you have.
However my 75 yo Mum would be challenged, probably to follow this if she had to, probably why my brother set her up with linux LOL
Thanks again very very very much !
Hello,
I went through all the steps as instructed. Is there any way for me to check if all malware is gone? Also i had some files on my computer that i sent via e-mail after it was infected (didn’t want to lose them) is there any chance they are infected? As you can see i’m not very knowledgable about this stuff :). Any help is appreciated.
Steven
In reply to Steven
Hello Steven,
If you want to perform another check,then I recommend that you do a scan with the following tools:
1.Run a scan with Kaspersky Virus Removal Tool
Click here to download the Kaspersky Virus Removal Tool.
2.Run a scan with Eset Online Scanner.
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
Stay safe!
In reply to Stelian Pilici
Hello,
I ran both scans and they both found nothing :).
Thank you very much for your help!
Steven
Thank you very much, this has been highly helpful. God bless you :)
thank you for the sharing.
Great article…helped me save a lot of time.
Thanks,
Ram
Thank you very much for your easy guide in removing the Life Security Platinum virus…was able to do it just by following it step by step. God bless you.
I’m having a problem with my Windows Firewall. I followed the directions to get rid of the virus, and it looks like it’s gone. I double checked with a scan from ESET and again with HitmanPro to make sure and nothing came up. I’ve tried to reactivate the firewall manually but I keep getting the error code 0x80070424. I looked it up on the Microsoft site and it said I might have malware. Again, I scanned with HitmanPro and nothing came up. I tried a recommended solution telling me to update, but Windows Updater won’t work either. It says the service is not running. So I restarted like it said, and tried again, but the same message is appearing. Any suggestions?
In reply to Ashley
Hello,
Please follow this steps:
Download Windows Repair by Tweaking.com to your desktop. Use the direct download link for the Portable version of Windows Repair by Tweaking.com
Note: When asked if you would like to create a restore point. It is recommended just in-case something does not go as planned.
Note: Leave everything else unchecked
Hi I was able to remove this virus using.both programs. Now I have a new virus. It’s called security shield. It looks exactly like live security platinum. How do I remove this and why didn’t those previsoly installed programs prevent this. Lol. Same proccess? You should make a post about this
In reply to joe
The Security Shield rogue has been around for a long time….here is the removal guide: http://malwaretips.com/blogs/security-shield-2012-removal-instructions/
Stay safe!
In reply to Stelian Pilici
Thanks for all the help bro. Very helpful step by step guide. If I ever have another problem I’m just going to visit here instead of calling my useless security provider that il paying yearly for who suppose to prevent this stuff from happening in the first place. Lol
Thank you for sharing.
I just got hit with this darn thing today and figured I would Google it, not thinking I would find something that would be as descriptive and helpful.
Thank you
I followed all of your instructions and everything worked until after I ran HitmanPro. When I ran it, 17 threats were found but when I tried to remove them, I didn’t get the link to activate the free 30 day trial. I am unable to run the program without paying for it. Am I doing something wrong?
In reply to Don
Hello,
I’ll report this problem to the HitmanPro developers.please run a scan with ESET Online Scanner and then re-install HitmanPro and try again to do a scan scan.If there are stil malicious files found ,write the path down and we will remove them manually.
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
If you are still experiencing problems , start a thread in our Malware Removal Support forum : http://malwaretips.com/Forum-Malware-Removal-Assistance
Nods to Stelian, it looks daunting on the page, but it worked like a breeze
Thanks buddy;)
Thank you so much for these “easy to follow” instructions on how to remove this fake program! I was terrified when I booted my computer and was unable to remove it the normal way…you SAVED my computer!!