

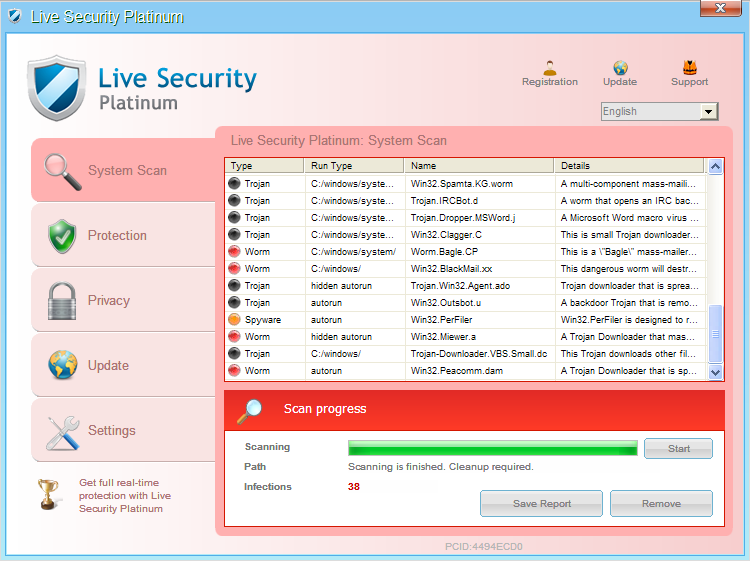
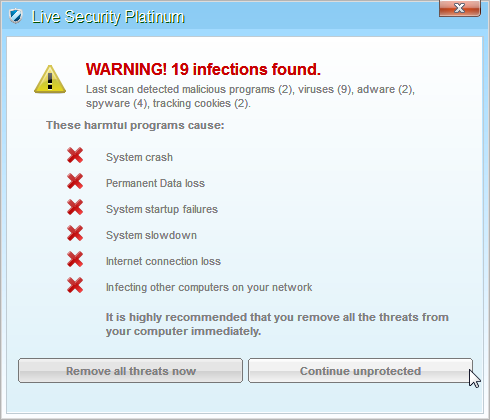
Live Security Platinum is a malicious program also known as rogue security software, which will display fake security alerts in an attempt to scare you into buying this fake security product.
In addition, Live Security Platinum has also hijacked your PC,blocking your from running files,so now when your trying to open and executable file (file ending with .exe), this program will instead display this fake alerts:
Warning!

Application cannot be executed. The file rdpclip.exe is infected. Please active your antivirus software.
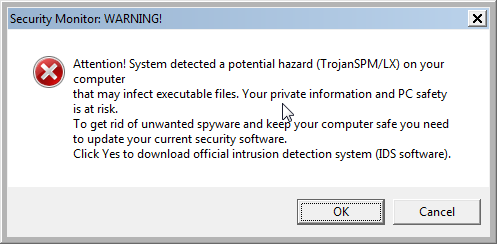
Security Monitor: WARNING!

Attention! System detected a potential hazard (TrojanSPM/LX) on your computer that may infect executable files. Your private information and PC safety is at risk.

To get rid of unwanted spyware and keep your computer safe you need to update your current security software.

Click Yes to download official intrusion detection system (IDS software).
Live Security Platinum Warning Spyware.IEMonster activity detected. This is spyware that attempts to steal passwords from Internet Explorer, Mozilla FireFox, Outlook and other programs. Click here to remove it immediately with Live Security Platinum
Live Security Platinum Firewall Alert Live Security Platinum Firewall has blocked a program from accessing the Internet. Internet Explorer Internet Browser is infected with SVCHOST.Stealth.Key-logger. This worm is trying to send your credit card details using Internet Explorer Internet Browser to connect to remove host
Live Security Platinum will also cause malicious browser redirects and system slowdowns so it needs to be removed from your computer as soon as possible.
This is are a few images of Live Security Platinum:
Registration codes for Live Security Platinum
As an optional step,you can use the following license key to register Live Security Platinum and stop the fake alerts.
AA39754E-715219CE
Please keep in mind that entering the above registration code will NOT remove Live Security Platinum from your computer , instead it will just stop the fake alerts so that you’ll be able to complete our removal guide more easily.
Live Security Platinum Removal Guide
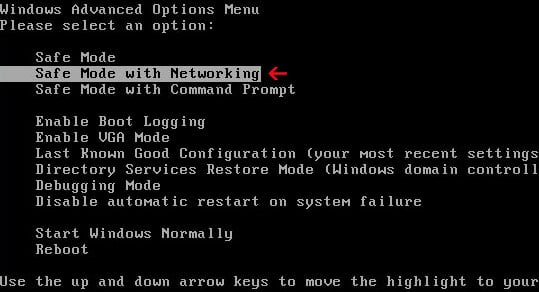
STEP 1 : Start your computer in Safe Mode with Networking
- Remove all floppy disks, CDs, and DVDs from your computer, and then restart your computer.
- Press and hold the F8 key as your computer restarts.Please keep in mind that you need to press the F8 key before the Windows start-up logo appears.
Note: With some computers, if you press and hold a key as the computer is booting you will get a stuck key message. If this occurs, instead of pressing and holding the “F8 key”, tap the “F8 key” continuously until you get the Advanced Boot Options screen. - On the Advanced Boot Options screen, use the arrow keys to highlight Safe Mode with Networking , and then press ENTER.
STEP 2: Remove Live Security Platinum malicious proxy server
Live Security Platinum may add a proxy server which prevents the user from accessing the internet,follow the below instructions to remove the proxy.
- Start the Internet Explorer browser and if you are using Internet Explorer 9 ,click on the gear icon
 (Tools for Internet Explorer 8 users) ,then select Internet Options.
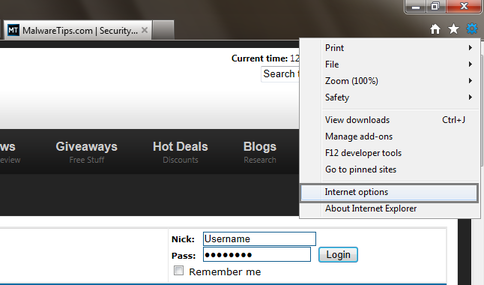
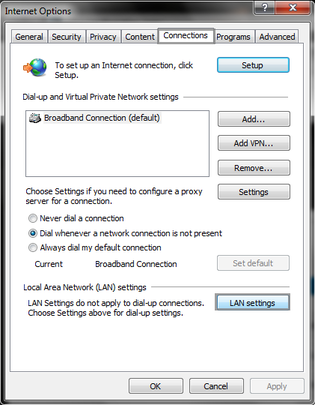
- Go to the tab Connections.At the bottom, click on LAN settings.
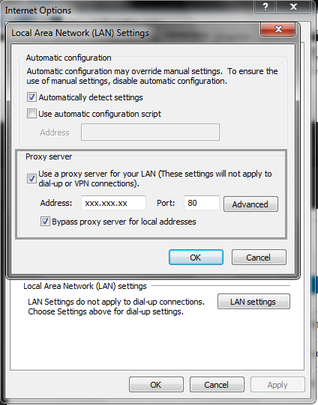
- Uncheck the option Use a proxy server for your LAN. This should remove the malicious proxy server and allow you to use the internet again.
 (Tools for Internet Explorer 8 users) ,then select Internet Options.
If you are a Firefox users, go to Firefox(upper left corner) → Options → Advanced tab → Network → Settings → Select No Proxy
STEP 3: Repair your Windows Registry from Live Security Platinum malicious changes.
Smart Fortress 2012 has changed your Windows registry settings so that when you try to run a executable file (ending with .exe ) , it will instead launch the infection rather than the desired program.
- Download the registryfix.reg file to fix the malicious registry changes from Live Security Platinum.
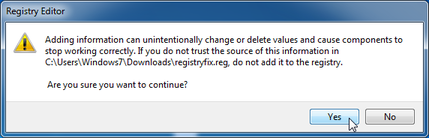
Download RegistryFix.regOpens the download page in a new tab. - Double-click on registryfix.reg file to run it. Click “Yes” for Registry Editor prompt window,then click OK.
STEP 4: Run RKill to terminate known malware processes associated with Live Security Platinum.
RKill is a program that will attempt to terminate all malicious processes associated with Live Security Platinum,so that we will be able to perform the next step without being interrupted by this malicious software.
Because this utility will only stop Live Security Platinum running process, and does not delete any files, after running it you should not reboot your computer as any malware processes that are configured to start automatically will just be started again.
- While your computer is in Safe Mode with Networking ,please download the latest official version of RKill.Please note that we will use a renamed version of RKILL so that Live Security Platinum won’t block this utility from running.
Download RKillYour download starts right away. - Double-click on the iExplore.exe icon in order to automatically attempt to stop any processes associated with Live Security Platinum.

- RKill will now start working in the background, please be patient while the program looks for various malware programs and tries to terminate them.
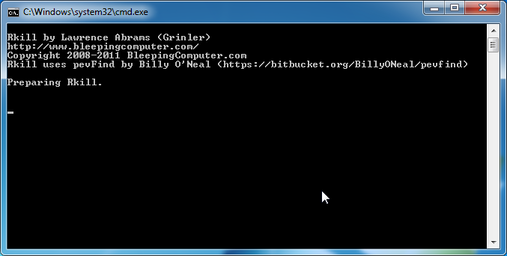
IF you are having problems starting or running RKill, you can download any other renamed versions of RKill from here. - When Rkill has completed its task, it will generate a log. You can then proceed with the rest of the guide.
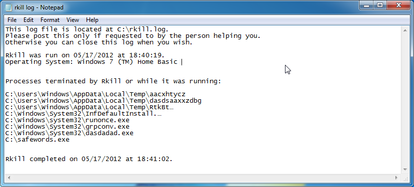

WARNING: Do not reboot your computer after running RKill as the malware process will start again , preventing you from properly performing the next step.
STEP 5: Remove Live Security Platinum malicious files with Malwarebytes Anti-Malware FREE
- Download the latest official version of Malwarebytes Anti-Malware FREE.
Download MalwarebytesFree official installer. Your download starts right away. - Start the Malwarebytes’ Anti-Malware installation process by double clicking on mbam-setup file.

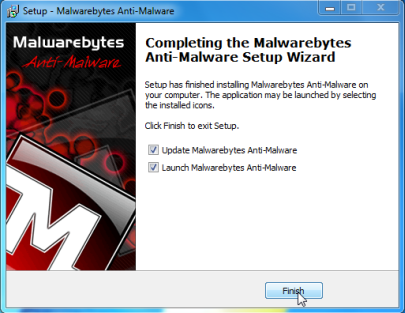
- When the installation begins, keep following the prompts in order to continue with the setup process. Do not make any changes to default settings and when the program has finished installing, make sure you leave both the Update Malwarebytes’ Anti-Malware and Launch Malwarebytes’ Anti-Malware checked. Then click on the Finish button. If Malwarebytes’ prompts you to reboot, please do not do so.
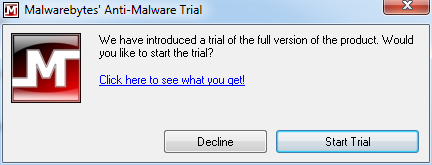
- Malwarebytes Anti-Malware will now start and you’ll be prompted to start a trial period , please select ‘Decline‘ as we just want to use the on-demand scanner.
- On the Scanner tab,select Perform full scan and then click on the Scanbutton to start scanning your computer.
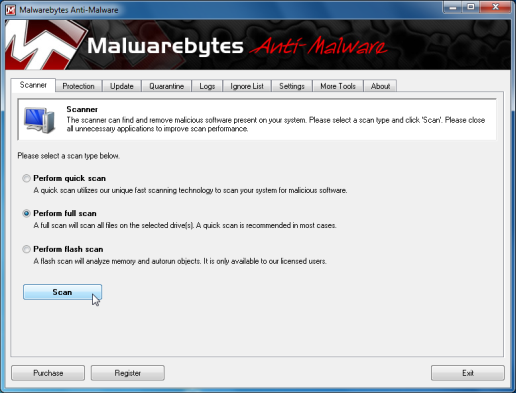
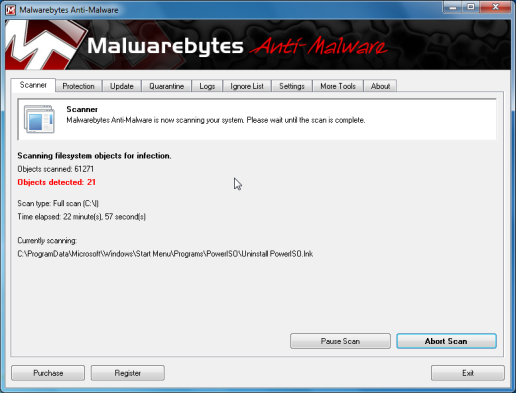
- Malwarebytes’ Anti-Malware will now start scanning your computer for Live Security Platinum malicious files as shown below.
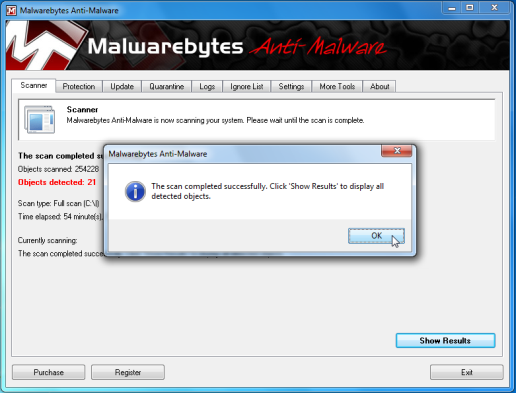
- When the scan is finished a message box will appear, click OK to continue.
- You will now be presented with a screen showing you the malware infections that Malwarebytes’ Anti-Malware has detected.Please note that the infections found may be different than what is shown in the image.Make sure that everything is Checked (ticked) and click on the Remove Selectedbutton.
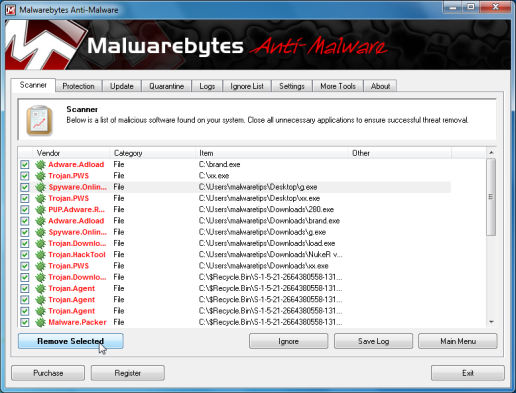
- Malwarebytes’ Anti-Malware will now start removing the malicious files.After completing this task it will display a message stating that it needs to reboot,please allow this request and then let your PC boot in Normal mode.

STEP 6: Double check your system for any left over infections with HitmanPro
- This step can be performed in Normal Mode ,so please download the latest official version of HitmanPro.
Download HitmanProOfficial Sophos download. Free scan, free 30-day trial to remove threats. - Double click on the previously downloaded fileto start the HitmanPro installation.

IF you are experiencing problems while trying to starting HitmanPro, you can use the “Force Breach” mode.To start this program in Force Breach mode, hold down the left CTRL-key when you start HitmanPro and all non-essential processes are terminated, including the malware process. (How to start HitmanPro in Force Breach mode – Video) - Click on Next to install HitmanPro on your system.
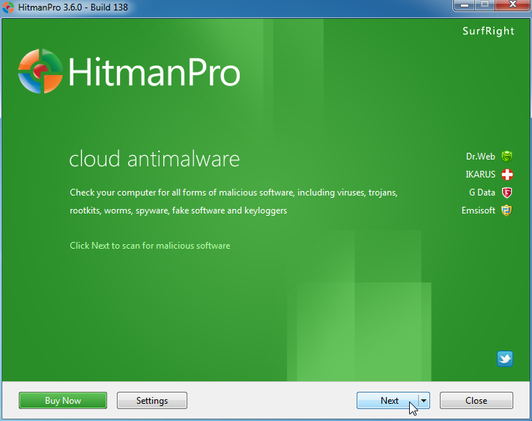
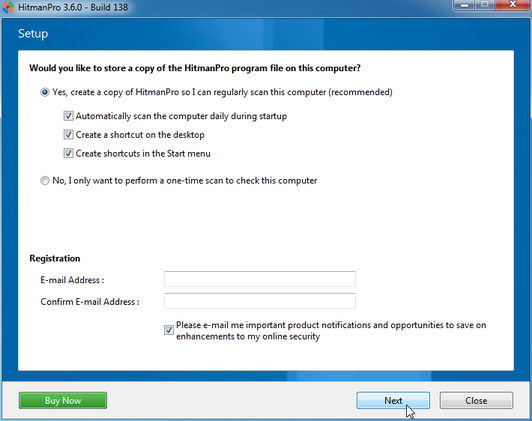
- The setup screen is displayed, from which you can decide whether you wish to install HitmanPro on your machine or just perform a one-time scan, select a option then click on Next to start a system scan.
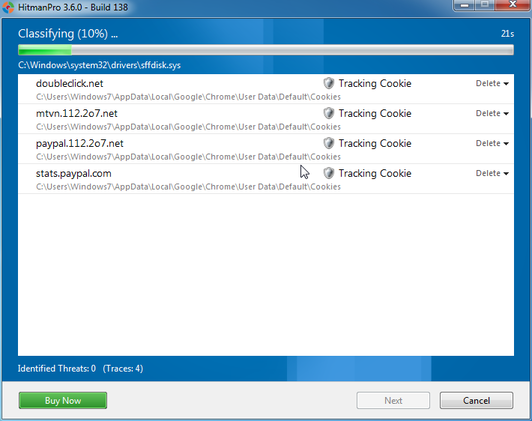
- HitmanPro will start scanning your system for malicious files. Depending on the size of your hard drive, and the performance of your computer, this step will take several minutes.
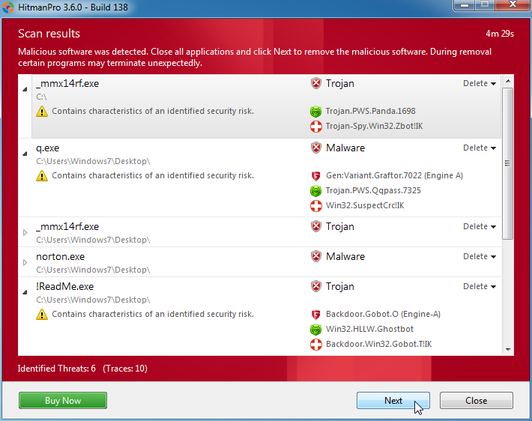
- Once the scan is complete,a screen displaying all the malicious files that the program found will be shown as seen in the image below.After reviewing each malicious object click Next.
- Click Activate free license to start the free 30 days trial and remove the malicious files.
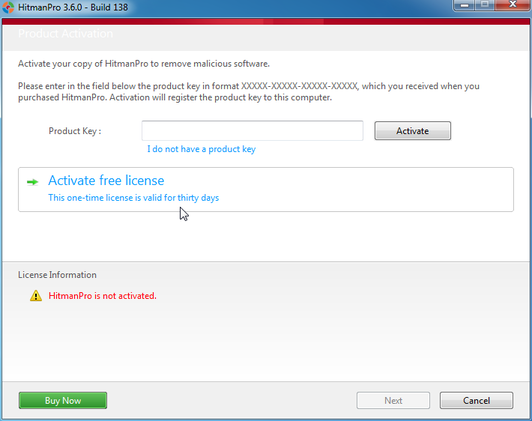
- HitmanPro will now start removing the infected objects, and in some instances, may suggest a reboot in order to completely remove the malware from your system. In this scenario, always confirm the reboot action to be on the safe side.

STEP 7: Remove any left over malicious registry keys and files
Live Security Platinum has sadded some malicious registry keys to your Windows installation , to remove this malicious changes we need to run a scan with RogueKiller
- Please download the latest official version of RogueKiller.
Download RogueKillerOpens the download page in a new tab. - Double click on RogueKiller.exe to start this utility and then wait for the Prescan to complete.This should take only a few seconds and then you can click the Start button to perform a system scan.
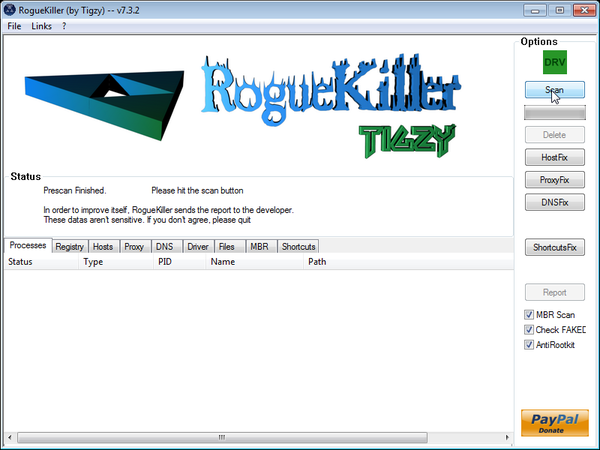
- After the scan has completed, press the Delete button to remove any malicious registry keys.
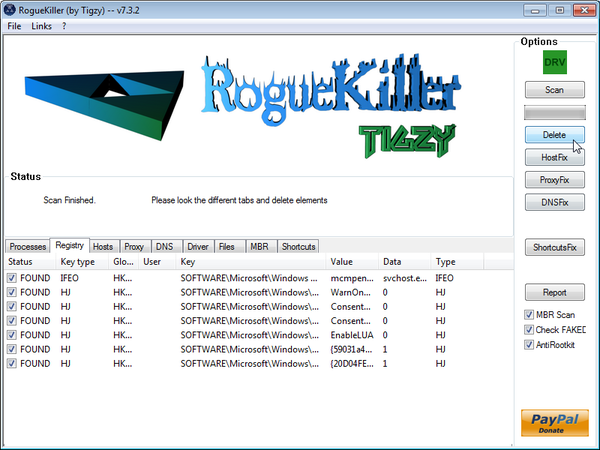
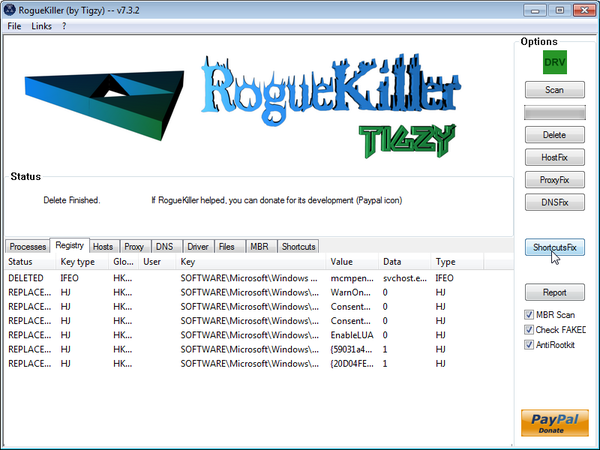
- Next we will need to restore your shortcuts, so click on the ShortcutsFix button and allow the program to run.

Join the discussion
538 commentsShare your experience or ask a question about this article.
Your progress
Did these steps help?
Let us know how the guide worked for you.
Describe what you see and the step you reached. Keep passwords and other private information out.
Discussion
I am not getting the “Safe Mode with Networking” when I press F8. When booting up, my computer only displays options for F2 and F10. I have an old Dell. Please help.
In reply to Peter
Hello Peter,
Lets work in Normal Mode:
Please run a scan with Malwarebytes Anti-Malware in Chameleon Mode in Norman mode:
2.Please perform a scan with HitmanPro as seen on the guide.
3.Run a scan with ESET Online Scanner:
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
In reply to Stelian Pilici
Hello, I have downloaded Malwarebytes Chameleon and tried to run it with the help file. The first one opened up a DOS screen and down loaded the file. When installing, I get Access Denied for a lot of files including rules.ref, config.conf, build.conf, custom.conf etc… I pressed rety and it does’t work. So I went ahead and installed it by pressing ignores for these files, I get “Failed to run MAM-Killer.exe”, “Failed to run Malwarebytes Anti-Malware” and ” Failed to disable protection driver”. Please help…
In reply to Peter
While in NORMAL MODE,download HitmanPro and then start this program in ForceBreach Mode
1.Here are the direct download links for HitmanPro,
– http://dl.surfright.nl/HitmanPro36.exe (For 32bit)
– http://dl.surfright.nl/HitmanPro36_x64.exe (For 64bit)
2.Hold down the left CTRL-key when you start HitmanPro and all non-essential processes are terminated, including this rogue malicious process
Here is a video that explains with graphic details how to do this : http://www.youtube.com/watch?v=m6eRWTv2STk
3. Let HitmanPro scan and remove the detected infections.
Next,run a scan with Malwarebytes and ESET Online scanner.
In reply to Stelian Pilici
Wow, it seems like I’m going deeper and deeper. Here’s the rundown:
When I tried to install the HitmanPro, it showed blue screen saying that it shut down to prevented the damage. Kernal-Stack-Inpage-error. Technical Info. STOP: 0X00000077 (0XC0000015, 0XC0000015, 0X00000000, oXoF63D000)
Wehn I restarted my computer, I got the second blue screen stating the following. A process or thread crucial to system operation has unexpectedly exited or terminated. Technical Info. STOP: 0X000000F4 (0X00000003, 0X826942C0, 0X82694434, 0X805D22AA)
When I restarted, the HitmanPro did start but didn’t find anything. Here’s the strange thing. I was able to start in safemode with network so I thought I give your full instruction a try. I was able to go online but when I tried to go on your site, it directed me to a different site (Randomly) every time.
When I tried to go to your step 5, I was getting this following errer message “Runtime Error ’13’: type mismatch. I also got “The trial is not available for your product version. We apologize for inconvenience” and also ‘Program_error_updating (0.0. Host not found).
I found out that I lost the connection to the internet (Home network). I tried resetting the ethernet card, reinstalled/rejoined the network, reset the modem, WiFi and everything but I’m not able to get my connection to the network back. I’m not able to perform step 6 as the HitmanPro wants to see the internet connection first.
By the way, I had to scan with MalwareBytes without updating as I didn’t have connection but found 89 items and deleted them. Please help me…
In reply to Peter
By the way, I cannot get to my windows fire wall settings or refresh my IP address due to “unknown error”… I’m on another computer to write this to you.
In reply to Peter
Hello,
You most likely have a ZeroAccess rootkit infection on your computer.
Can you please run a scan with Combofix:
STEP 1 : Run a scan with Combofix
Download ComboFix from one of the following locations:
COMBOFIX DOWNLOAD LINK #1 (This link will automatically download Combofix on your computer)
COMBOFIX DOWNLOAD LINK #2 (This link will automatically download Combofix on your computer)
VERY IMPORTANT !!! Save as Combo-Fix.exe during the download. ComboFix must be renamed before you download to your Desktop
———————————————————–
———————————————————–
———————————————————–
Notes:
STEP 2: Run a scan with ESET Online Scanner:
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)