

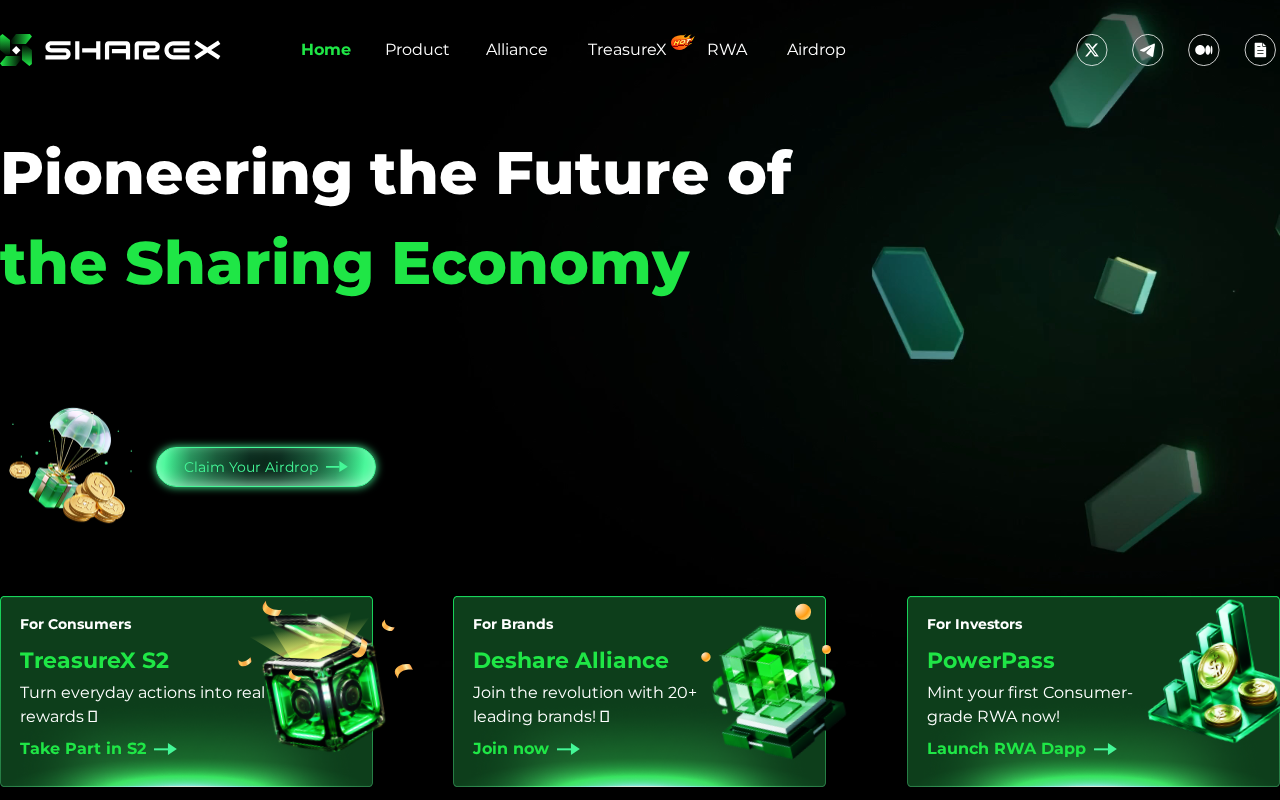
A polished ShareX page offers an airdrop, complete with familiar project names and a bright claim button. The reward looks ready to collect.
Before choosing a wallet, take a closer look at the address. The branding tells only part of this story.
Overview
A false claim page borrows a real project’s identity
The ShareX airdrop scam uses sharex-network[.]live to impersonate the ShareX project. Its design presents the supposed giveaway as part of a broader Web3 ecosystem.
The captured page displays a prominent airdrop invitation alongside TreasureX, Deshare Alliance, and PowerPass sections. These recognizable labels make the reward feel connected to an established project.
The real project uses sharex.network and documentation under docs.sharex.network. The hyphenated .live address is a different domain, not a section of that site.
The attraction is free tokens, but the concern is wallet authorization
The reported claim journey opens a wallet-selection interface and is associated with a cryptocurrency-draining lure. Do not use it to claim rewards or approve wallet requests.
No wallet was connected during this review. The exact contract, transaction, or signature that would be requested has not been independently executed or verified.
That limit matters: connecting a wallet is not automatically the same as authorizing a transfer. Dangerous approvals, signatures, transactions, or exposed recovery secrets create different risks.
What separates the impersonation from a genuine airdrop
- The claim page sits on a lookalike domain rather than the project’s established address.
- Project vocabulary and matching colors are used as borrowed credibility.
- The promise leads toward wallet interaction before independently established eligibility.
- A list of wallet brands does not establish a partnership or validate the reward.
- Genuine ShareX airdrop documentation does not authorize every page using the project’s name.
This article concerns the counterfeit claim route. It is not an allegation that ShareX’s real website or every legitimate token distribution is fraudulent.
Why This Lookalike Can Feel Convincing
A crude giveaway page is easy to dismiss. This one builds a larger setting around the reward, with navigation, product categories, and ecosystem language.
The airdrop appears to be one feature among several. That makes it look less like an isolated demand and more like an opportunity within a functioning platform.
Someone who has seen ShareX discussed elsewhere may recognize the name and stop checking. Someone unfamiliar with it may interpret the detailed layout as evidence of legitimacy.
Both reactions skip the same question: who controls the page asking for wallet access? Visual familiarity cannot answer it.
A copied homepage also provides cover for a malicious call to action. The surrounding marketing can look harmless while the claim button takes the reader somewhere risky.
You do not need to disprove every sentence on the page. The false claim route is enough reason to leave without testing a wallet connection.
How the ShareX Airdrop Scam Works
Step 1: The reward invitation brings you to a near-match address
A person may arrive through a shared link, promotion, or search result. The exact distribution route can vary, so do not assume only one social platform is involved.
At the destination, the page’s branding encourages you to recognize ShareX first and inspect the domain later. The address contains the project name and a network-related word.
That construction can seem sensible at a glance. But sharex-network.live and sharex.network are separate domains, not interchangeable spellings of the same location.
A genuine link to a third-party campaign would need independent confirmation from the project’s trusted channels. The third-party page cannot supply that confirmation by praising itself.
Do not rely on a search ad or a stranger’s reply to verify the route. They can send you back to the same impersonation.
Step 2: Ecosystem details make the giveaway feel expected
The page places its claim invitation within marketing for consumer rewards, an alliance, and a product called PowerPass. The message is that participation belongs to a larger ecosystem.
This matters because real crypto projects sometimes distribute tokens to community participants. The scam does not need to invent the entire concept of an airdrop.
Instead, it borrows the expectation that community activity can lead to rewards. A reader may supply their own reason for believing they qualify.
The genuine ShareX tokenomics documentation discusses airdrop eligibility and rules determined through the project’s own process. It does not validate this lookalike site.
Do not confuse general knowledge of a project’s token program with confirmation of a particular claim link. They are different checks, and the second one protects your wallet.
A page can copy accurate project terminology and still lie about the destination of the next button. That is why factual-looking background material is not sufficient reassurance.
Step 3: The claim button moves the reader into wallet selection
The reported claim interface offers a broad selection of wallet brands. Recognizable options can make the request resemble the connection process used by legitimate decentralized applications.
Those logos are not independent endorsements. A webpage can display a wallet’s name without any relationship with its developer or any guarantee about the page’s behavior.
At this stage, slow down rather than treating the familiar connection flow as routine. Check the site identity before allowing any request to reach a valuable account.
Do not install a new extension supplied by the reward page. If a service claims your wallet needs repairing, updating, or synchronizing, use the wallet provider’s established support.
A recovery phrase or private key is never an airdrop eligibility credential. Entering it into a claim form can give someone control far beyond that single website.
Step 4: A reward label can obscure a spending request
The page may describe the next action as verification or claiming. The wallet’s own request is what matters when determining what you would actually authorize.
A transfer sends assets. An approval can let another party move certain tokens later. Some signatures can confer useful authority without looking like an immediate payment.
The exact effect depends on the network, wallet, and request. There is no responsible shortcut that labels every signature harmless or every connection an instant drain.
The danger is being persuaded to approve something you do not understand because the webpage says it unlocks free tokens. A reward label does not change the permission.
If you cannot explain why an alleged incoming reward needs the requested access, reject it. Do not proceed just to see whether the promised balance appears.
A success screen is written by the page operator. Check actual wallet activity through trusted tools, not the same site that supplied the questionable request.
Connection, Approval, Signature, and Secret: Four Different Exposures
A connection is not a blanket spending authorization
Connecting commonly allows a site to learn your public address and request further interaction. That can affect privacy, but it is not universally permission to transfer assets.
If you connected without signing or approving anything, disconnect through the wallet’s own settings. Review activity before concluding either that everything is lost or everything is safe.
Do not return to the false page to search for its disconnect button. Use the wallet’s trusted interface instead.
Permissions can survive closing the page
On networks using token allowances, an approval can remain active after a browser tab closes. Disconnecting the website does not necessarily remove that on-chain authority.
MetaMask’s disconnection guidance makes that distinction. Use the appropriate tools for the actual network and account involved rather than assuming every wallet works identically.
A malicious approval may expose particular assets covered by that permission. Avoid the opposite exaggeration that every approval necessarily gives unlimited access to every chain and token.
Check which account signed, which network recorded the permission, and which asset it covers. A wallet application can hold several accounts with different exposure.
An empty balance after signing does not necessarily mean a permission is irrelevant. A standing allowance could matter when the affected token arrives later.
Conversely, unrelated assets should not be moved in a panic through unfamiliar tools. Start with the request you actually authorized and get qualified help where necessary.
Preserve the permission’s public transaction record before making changes. It helps a responder understand the scope without needing access to your wallet secrets.
An exposed recovery phrase changes the response completely
If you disclosed a phrase or private key, removing a website connection is not enough. The secret itself may allow another person to control the account.
Obtain official wallet guidance from a clean environment. A new password on the same wallet application does not make a disclosed recovery phrase private again.
Do not fund a compromised account experimentally or pay someone who appears in your direct messages. Moving assets under active compromise can require careful, network-specific help.
What to Do if You Have Fallen Victim to This Scam
Reject outstanding requests and leave the claim site. Do not sign an extra verification or pay a supposed fee to complete a claim that has stalled.
Record what happened while it is fresh: the domain, wallet account, network, approximate time, and whether you connected, approved, signed, transferred, or shared a secret.
Disconnect through the wallet, then examine its activity. Look for unexpected transactions and permissions using the wallet’s trusted tools and the correct blockchain explorer.
Keep public transaction identifiers for a report. Never include a recovery phrase, private key, or password in screenshots sent to a stranger offering assistance.
Review any approval you granted. For compatible accounts, follow official allowance-revocation guidance or equivalent instructions from your wallet provider.
Revocation is not a refund and may require a legitimate network fee. Do not use a revocation link supplied by the same suspicious claim page.
Treat disclosed recovery secrets as compromised. Seek trusted provider guidance on securing remaining assets with a newly generated wallet in a clean environment.
Be especially careful if funds disappear as soon as they arrive. Sending more money into a compromised account without a plan can increase the loss.
Report actual transfers promptly. Contact the exchange or service you used through its official support, and provide transaction hashes, destinations, timestamps, and the false domain.
Report financial losses to the appropriate authorities. A service may be able to investigate, but nobody should promise that a completed blockchain transfer can simply be reversed.
Check software exposure separately from wallet permissions. If you installed an extension, downloaded an app, or ran a tool, investigate that device with trusted help.
Malwarebytes can assist with malware checks. AdGuard can reduce some harmful web exposure. Neither tool cancels an on-chain authorization or retrieves transferred cryptocurrency.
Ignore unsolicited recovery offers. A supposed specialist who guarantees repayment, requests your phrase, or demands an advance fee can turn the first loss into another.
Keep the evidence, secure the account, and work through official channels. You do not need to share more secrets to prove that you deserve help.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
How to Check a Future ShareX Reward
Begin with the project address you independently know, not a forwarded claim link. Find the relevant announcement and follow the route it actually identifies.
Check whether the eligibility rules describe your situation. A page claiming everyone qualifies is not a replacement for the project’s own documented conditions.
Keep verification and participation separate. Even after confirming a genuine announcement, read the wallet request rather than assuming an official-looking page makes every permission appropriate.
If a support account contacts you first, verify it through the project’s established channels. An avatar, badge, or copied administrator name is not enough.
A separate low-value wallet can limit some exposure, but it does not make a dishonest site trustworthy. Never transfer important assets into it merely to satisfy an alleged eligibility requirement.
There is no need to rush because a third-party page claims the reward is nearly gone. Losing an unverified offer is safer than giving it authority over valuable assets.
Frequently Asked Questions
Is sharex-network.live the same as sharex.network?
No. They are distinct domains. The former is the lookalike addressed here; the genuine project’s established domain and documentation should be reached independently.
Does this mean ShareX has no real airdrop program?
No. Official documentation discusses airdrop rules. A real program’s existence does not authenticate a separate webpage using its name, design, or product labels.
Will connecting alone always empty a wallet?
No. Connection and spending authorization are different. Review whether you also approved permissions, signed a request, sent assets, or disclosed recovery secrets.
Why does the page show familiar wallet brands?
A selector makes the process look compatible and routine. A displayed logo does not prove endorsement, partnership, safety, or the legitimacy of the promised distribution.
Does disconnecting remove every token approval?
No. Where on-chain allowances apply, they may need separate revocation. Use the actual wallet provider’s guidance for your network rather than a link from the false page.
Can security software recover stolen tokens?
No. It can help address malicious software on a device. It does not reverse blockchain transfers, replace disclosed keys, or cancel permissions already recorded on-chain.
The Bottom Line
Do not claim through sharex-network.live or approve its wallet requests. The page borrows ShareX’s identity to make an untrusted reward route look established.
If you interacted, respond to the actual exposure: disconnect, inspect permissions and transactions, and protect compromised keys. Report losses through official services, not a recovery stranger.

Reviews & discussion
0 commentsShare a firsthand experience, or ask a question.
Community reviews
sharex-network.live
Moderated reader experiences, not an editorial verdict.
Start the conversation
Have a question or something useful to share? Add the first comment.