

SorbusAucuparia is a browser extension that injects advertisements into websites you visit and redirects your browser search queries. SorbusAucuparia uses the “Managed by your organization” policy to prevent users from easily removing it.
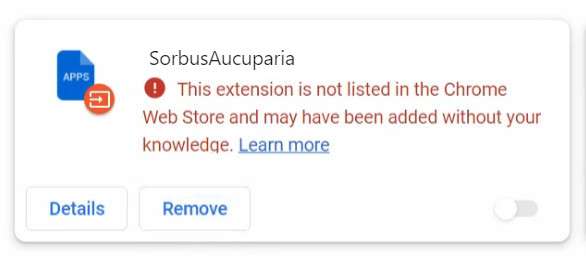
What is the SorbusAucuparia extension?
SorbusAucuparia is a malicious browser hijacker designed to inject advertisements and redirect searches without consent. Once installed, SorbusAucuparia can be difficult to uninstall due to its “Managed by your organization” policy that prevents easy removal.
When your browser is infected with the SorbusAucuparia hijacker, you may notice unwanted ads on websites, links redirecting to unfamiliar sites, and your search engine queries going through shady third-party engines rather than your preferred search engine.
The SorbusAucuparia browser hijacker works by infecting web browsers like Google Chrome, Mozilla Firefox, Microsoft Edge, and Apple Safari. After infection, SorbusAucuparia can:
- Inject advertisements into websites you visit, displaying ads that don’t originate from the actual site.
- Redirect your web searches through unwanted affiliate marketing search engines that generate revenue for the hijacker creators.
- Change website links to redirect your browser to unfamiliar and potentially dangerous sites.
- Makes it difficult to remove due to its “Managed by your organization” policy that requires advanced tech skills to remove.
How was the SorbusAucuparia extension installed on my computer?
The SorbusAucuparia extension is installed by the users, whether that is knowingly or not. Often, this type of program is offered through malicious advertisements, leaving the user puzzled about where this software came from.
The SorbusAucuparia extension is being promoted through ads similar to the one shown below.
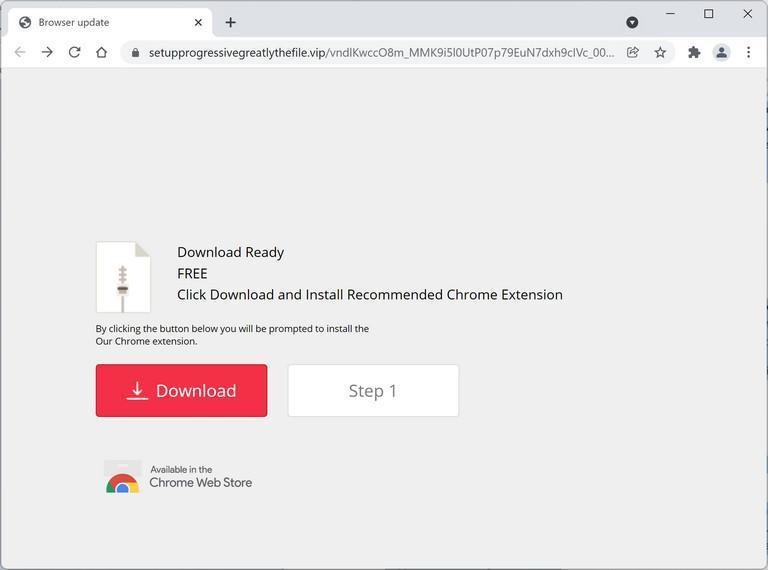
Less than reputable sites can redirect your browser to these SorbusAucuparia ads to generate advertising revenue. If this happens, you can close the page and install a legitimate ad blocker like AdGuard to remove ads from the sites you visit.
However, if you continuously see these SorbusAucuparia ads, then your computer might be infected with a malicious program, and we will need to scan your device for malware and remove it.
If you do not know how the SorbusAucuparia extension was installed or are concerned other extensions or unwanted programs may be installed on your device, you can use the removal guide below.
Removal Instructions for SorbusAucuparia Extension
Please perform all the steps in the correct order. If you have any questions or doubts at any point, stop and ask for our assistance.
 Remove SorbusAucuparia from Windows
 Remove SorbusAucuparia from Mac
Remove SorbusAucuparia from Windows
- STEP 1: Use Rkill to terminate malicious processes
- STEP 2: Uninstall malicious programs from your computer
- STEP 3: Remove malicious browser policies from Windows
- STEP 4: Remove malicious files and folders from Windows
- STEP 5: Reset your browser settings to their defaults
- STEP 6: Use Malwarebytes to remove trojans and browser hijackers
- STEP 7: Use HitmanPro to scan your computer for rootkits and other malware
- STEP 8: Use AdwCleaner to remove adware and malicious browser policies
STEP 1: Use Rkill to terminate malicious processes
In this first step, we will download and run Rkill to terminate malicious processes that may be running on your computer.
RKill is a program that was developed at BleepingComputer.com that attempts to terminate known malware processes so that your normal security software can then run and clean your computer of infections. When RKill runs it will kill malware processes and then removes incorrect executable associations and fixes policies that stop us from using certain tools.
-
Download Rkill.
You can download RKill to your computer from the below link. When at the download page, click on the Download Now button labeled iExplore.exe. We are downloading a renamed version of Rkill (iExplore.exe) because some malware will not allow processes to run unless they have a certain filename.
Download RKillOpens the BleepingComputer download page in a new tab. RKillStops malware processes so other tools can run
-
Run RKill.
After downloading, double-click the iExplore.exe icon to kill malicious processes. In most cases, downloaded files are saved to the Downloads folder.
The program may take some time to search for and end various malware programs.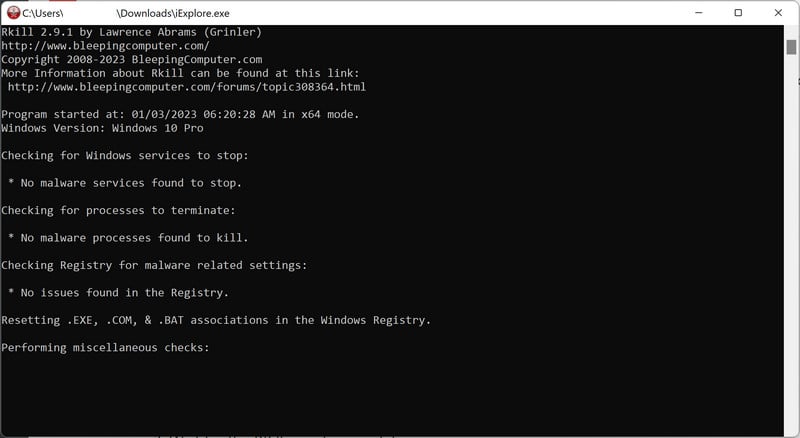
When it is finished, the black window will close automatically and a log file will open. Do not restart your computer. Proceed to the next step in this guide.
STEP 2: Uninstall malicious programs from your computer
In this second step, we will manually check if any unknown or malicious programs are installed on the computer. Sometimes adware and browser hijackers can have a usable Uninstall entry that can be used to remove them.
-
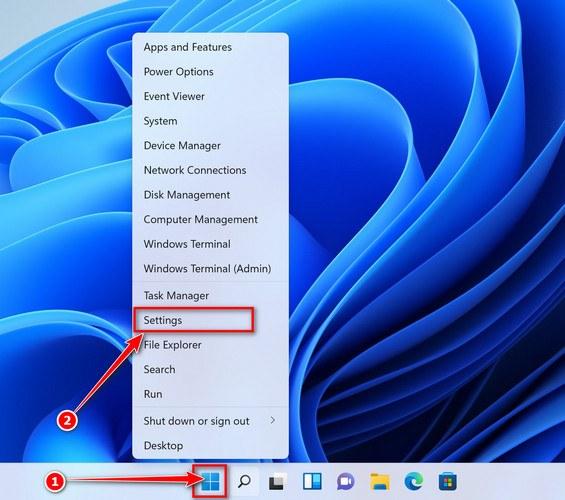
Open the Settings app
Press Windows + I on your keyboard to open Settings. Alternatively, right-click the Start button and select “Settings” from the menu.
-
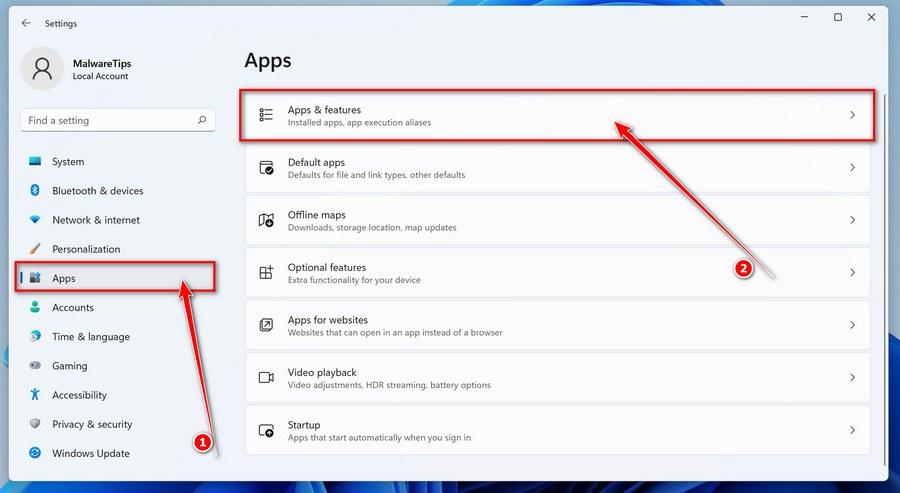
Go to “Apps & Features”
In the Settings window, click “Apps” in the sidebar, then select “Apps & Features“.
-
Find and uninstall the malicious program
Scroll through the list of installed apps and look for anything suspicious — a program you don’t remember installing, or one with a strange or generic name.
Quick tip: click “Sort by” and choose “Install date“. Malware is usually one of the most recently installed programs, so it will appear near the top.
When you find the malicious program, click the three dots next to it and select “Uninstall“.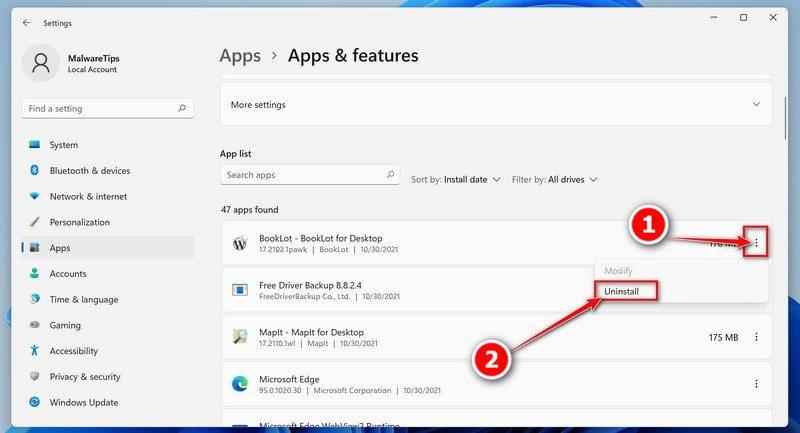 Didn’t find any suspicious programs? That’s fine — not all infections install visible apps. Just continue with the next step in this guide.
-
Complete the uninstall
Confirm by clicking Uninstall in the message box, then follow the remaining prompts.
Read each prompt carefully — some malicious programs use confusing wording or pre-ticked boxes hoping you’ll click through without looking.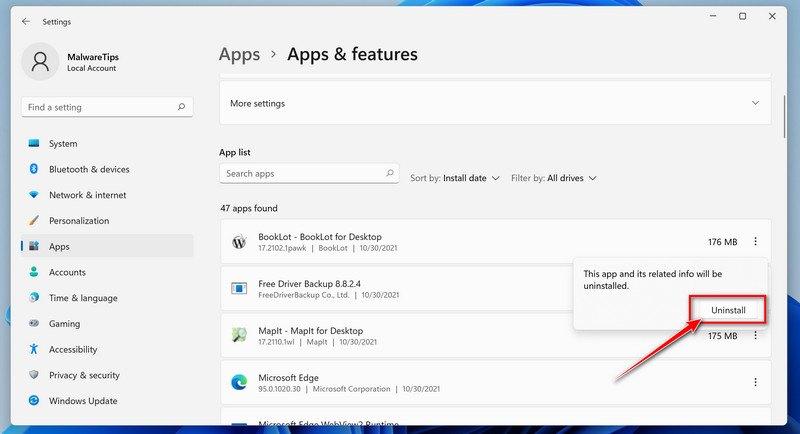
-
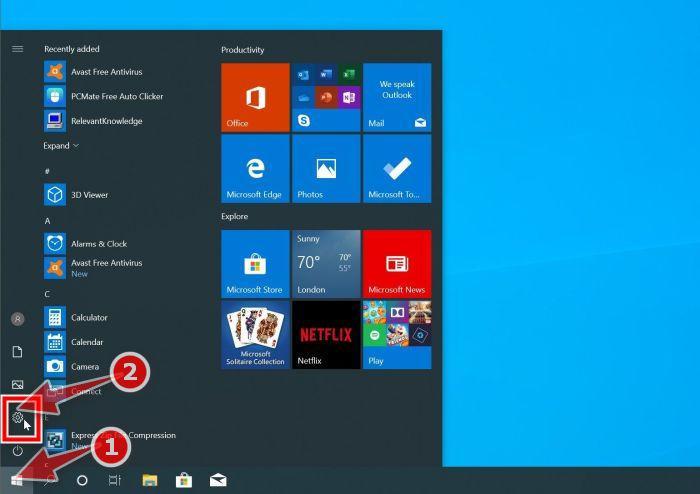
Open the Settings app
Press Windows + I on your keyboard to open Settings. Alternatively, click the Start button on the taskbar and select “Settings” (the gear icon).
-
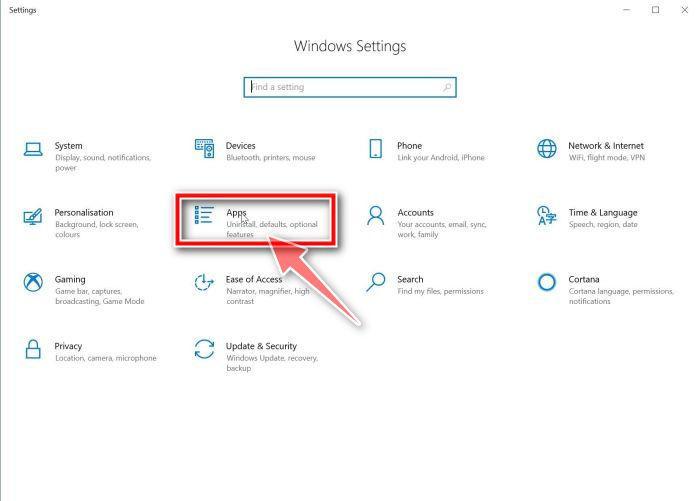
Click on “Apps”
In the “Windows Settings” window, click “Apps“. The “Apps & Features” section should open by default — if it doesn’t, select it from the list on the left.
-
Find and uninstall the malicious program
Scroll through the list of installed apps and look for anything suspicious — a program you don’t remember installing, or one with a strange or generic name.
Quick tip: click “Sort by” and choose “Install date“. Malware is usually one of the most recently installed programs, so it will appear near the top.
When you find the malicious program, click on it and select “Uninstall“.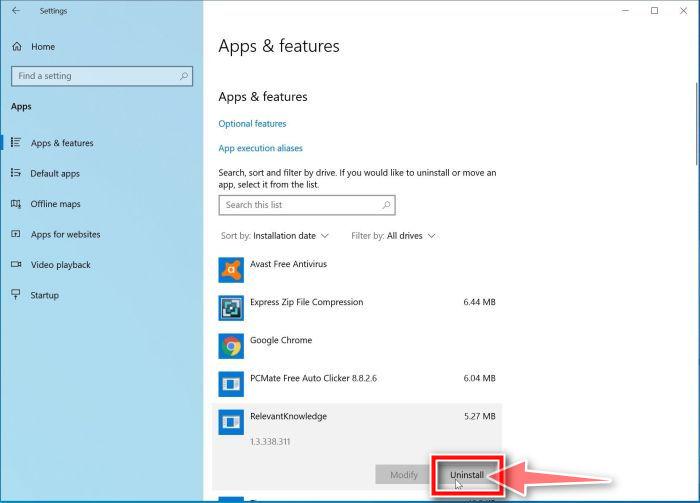 Didn’t find any suspicious programs? That’s fine — not all infections install visible apps. Just continue with the next step in this guide.
-
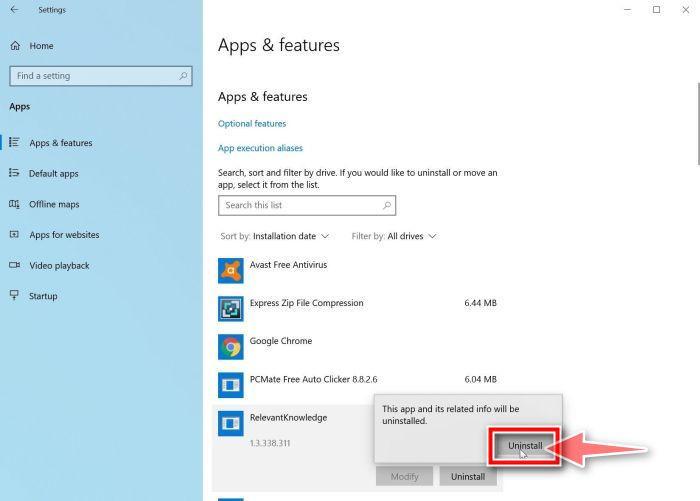
Complete the uninstall
Confirm by clicking Uninstall in the message box, then follow the remaining prompts.
Read each prompt carefully — some malicious programs use confusing wording or pre-ticked boxes hoping you’ll click through without looking.
-
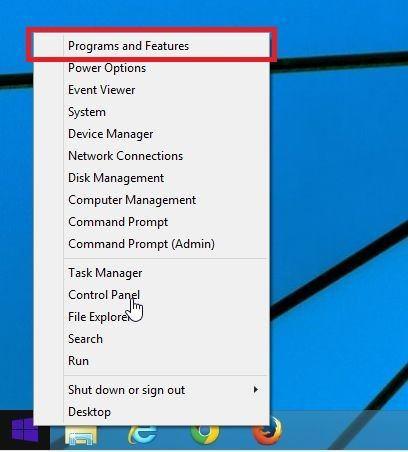
Open “Programs and Features”
Right-click the Start button in the taskbar, then select “Programs and Features“. This takes you straight to the list of installed programs.
-
Find and uninstall the malicious program
Scroll through the list of installed programs and look for anything suspicious — a program you don’t remember installing, or one with a strange or generic name. Click to highlight it, then click the “Uninstall” button.
Didn’t find any suspicious programs? That’s fine — not all infections install visible apps. Just continue with the next step in this guide.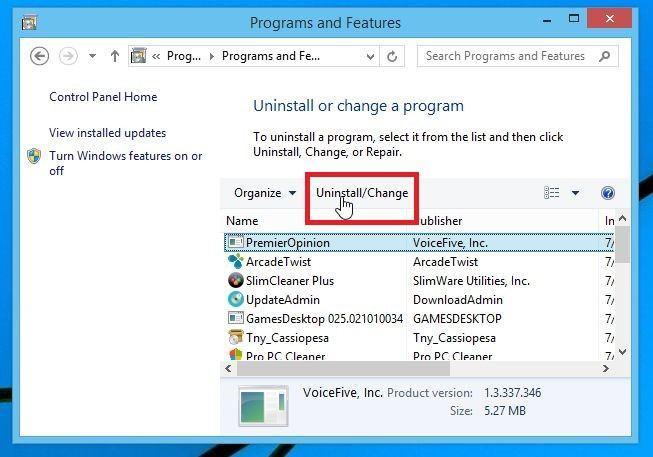
-
Complete the uninstall
Confirm by clicking Yes in the message box, then follow the remaining prompts. Read each prompt carefully — some malicious programs use confusing wording or pre-ticked boxes hoping you’ll click through without looking.
-
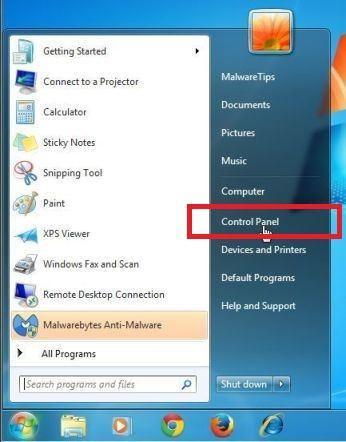
Open the Control Panel
Click the “Start” button, then click “Control Panel“.
-
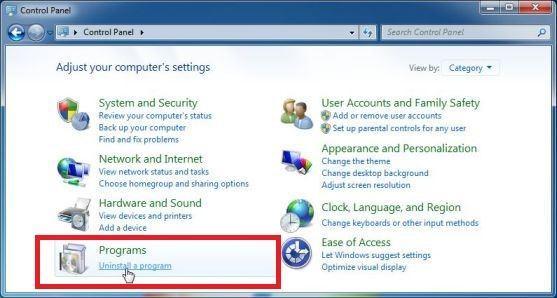
Click on “Uninstall a Program”
In the Control Panel, click “Uninstall a Program” under the Programs category.
-
Find and uninstall the malicious program
Scroll through the list of installed programs and look for anything suspicious — a program you don’t remember installing, or one with a strange or generic name. Click to highlight it, then click the “Uninstall” button.
Didn’t find any suspicious programs? That’s fine — not all infections install visible apps. Just continue with the next step in this guide.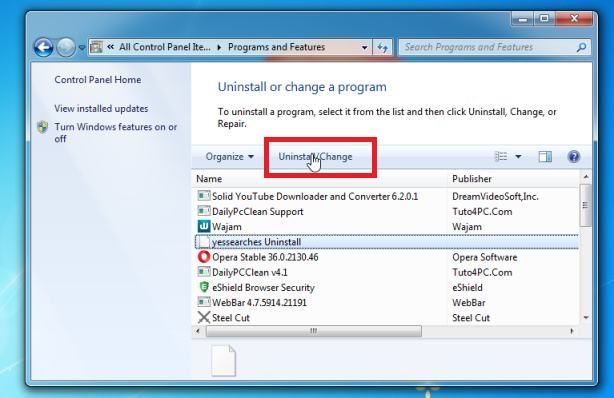
-
Complete the uninstall
Confirm by clicking Yes in the message box, then follow the remaining prompts. Read each prompt carefully — some malicious programs use confusing wording or pre-ticked boxes hoping you’ll click through without looking.
With the malicious programs removed, you’re ready for the next step in this guide.
STEP 3: Remove malicious browser policies from Windows
In this third step, we will download the Chrome Policy Remover file (credits to Stefan Van Damme) and remove the malicious browser policies. .
-
Download the Chrome Policy Remover
Click the button below to download the Chrome Policy Remover for Windows — a small batch script that automatically removes the malicious policies that malware uses to lock your Chrome settings.
Download Chrome Policy RemoverDownloads the delete_chrome_policies file from the developer’s site. Chrome Policy RemoverFree script that removes the policies malware adds to ChromeSeeing a security warning? That’s expected — browsers and Windows flag all batch (.bat) files as a precaution, regardless of what they do. The Chrome Policy Remover is a trusted, widely used tool; click “Keep” to proceed with the download.
-
Run the file as administrator
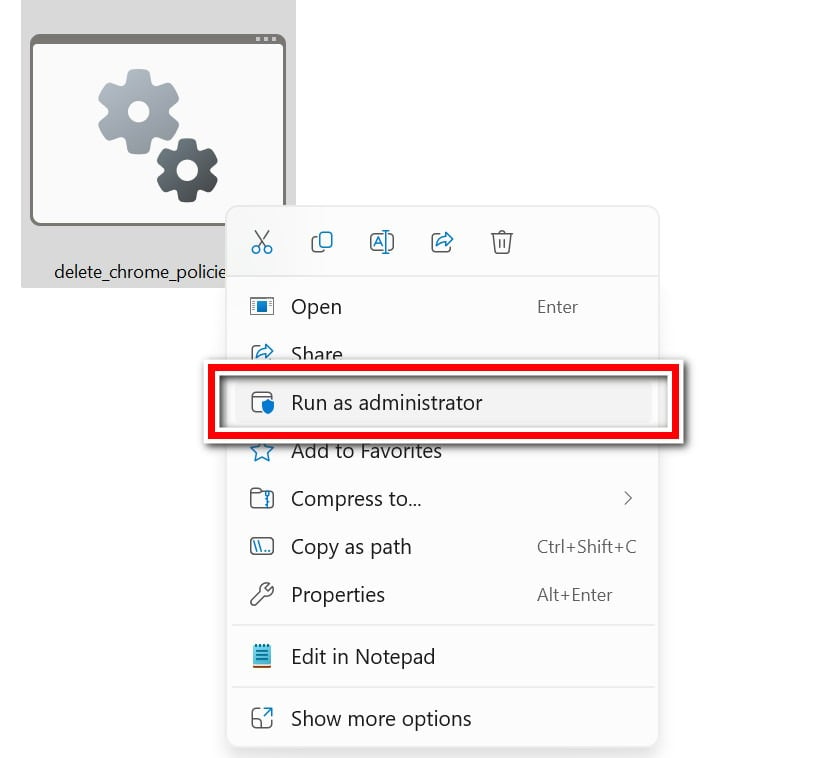
Right-click the “delete_chrome_policies.bat” file (usually in your Downloads folder) and select Run as administrator. Administrator rights are required because Chrome policies are stored in protected system settings — without them, the tool can’t remove the policies.
Confirm and let the script finish
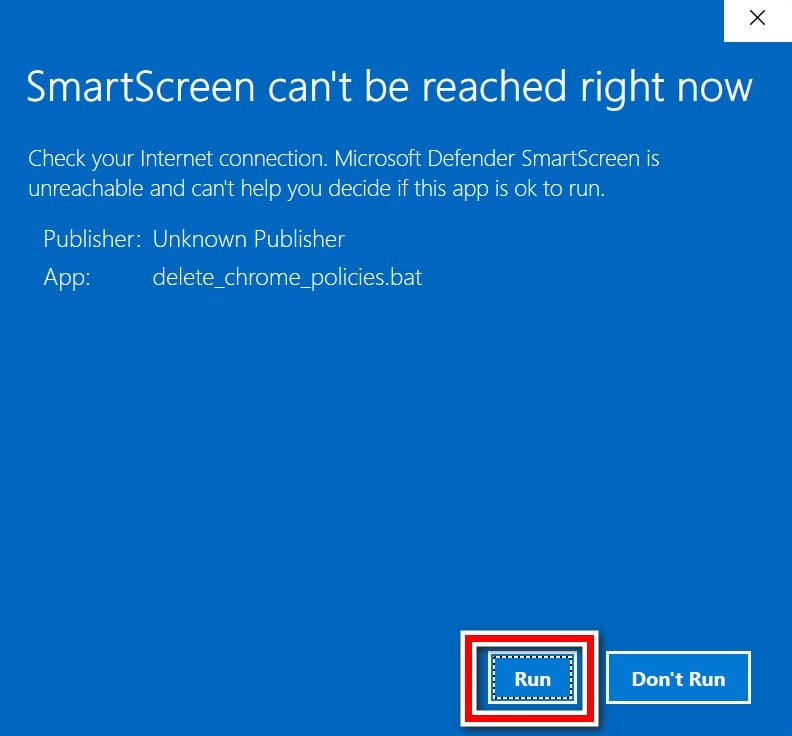
Windows will ask for confirmation before allowing the script to make changes — click “Yes” (or “Run“, depending on your Windows version). A Command Prompt window will open and the script will remove the policies automatically; this only takes a few seconds. When it’s done, close the window.
With the malicious policies removed, Chrome’s settings are unlocked again. In the next step, we’ll reset the browser to its defaults.
STEP 4: Remove malicious files and folders from Windows
In this fourth step, we will manually search and remove malicious scheduled tasks and folders on your computer.
1. Delete Malicious Scheduled Tasks
This infection often creates a scheduled task in the Windows Task Scheduler that reinstalls the malware every few minutes after you delete it. That’s why the redirects keep coming back even after a cleanup — until this task is removed, the infection will keep restoring itself.
- Type “Task Scheduler” in the Windows search bar and open the app, as shown below.
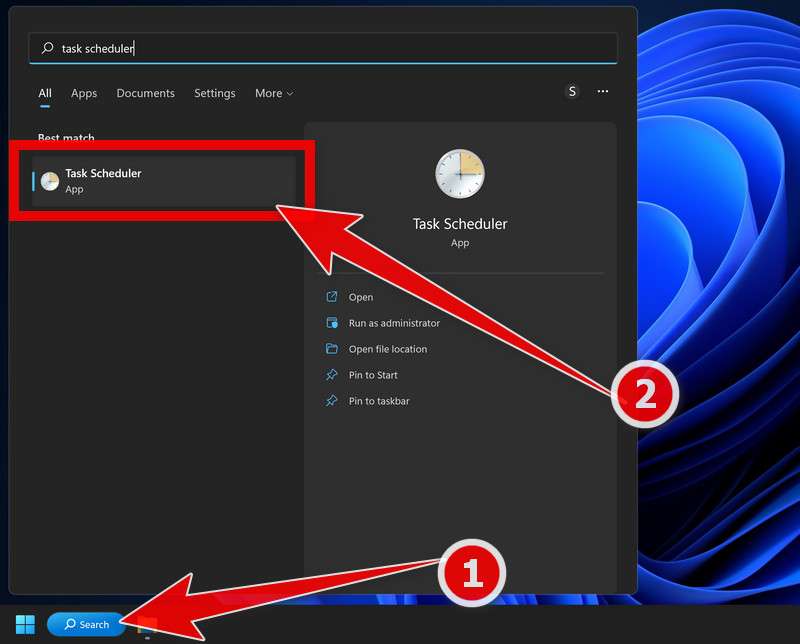 Alternatively, press Windows + R, type “taskschd.msc“, and press Enter.
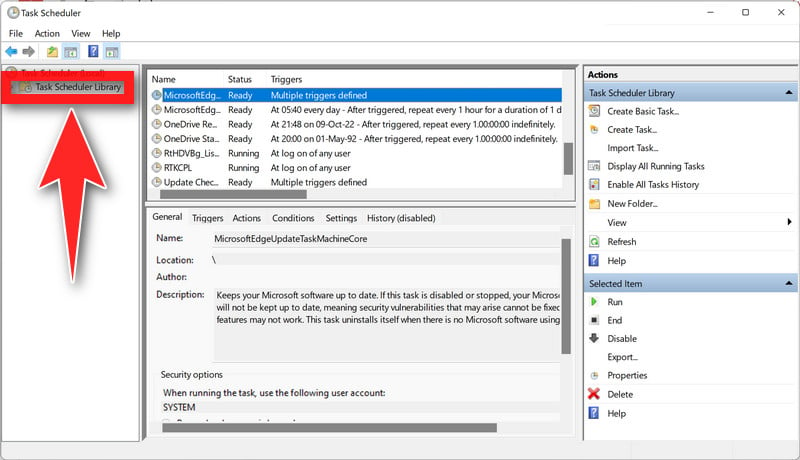
- In the Task Scheduler window, click Task Scheduler Library in the left pane.
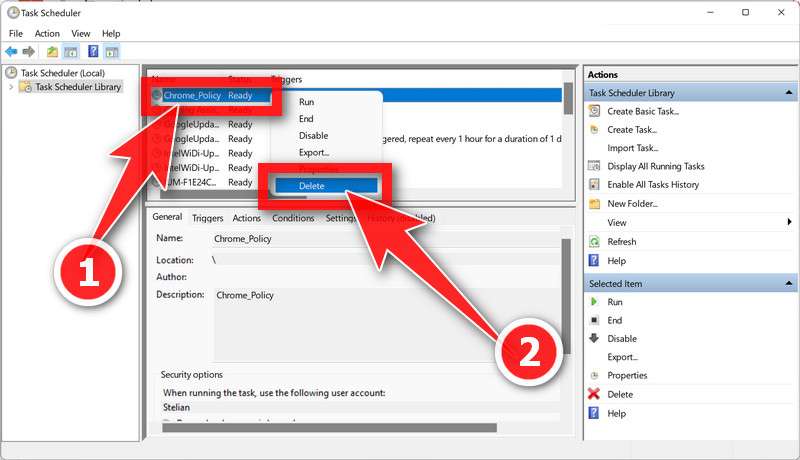
- Look through the list for the malicious scheduled task. It often imitates a legitimate name (e.g. Chrome_Policy, Chrome_Bookmarks, Chrome_Folder) or has a random string of characters as its name. A useful check: click a task and look at the Actions tab — if it runs a file from the AppData folder, it’s almost certainly malicious. Right-click the task and select “Delete“.
2. Delete Malicious Files from the AppData\Roaming Folder
Next, we’ll delete the malicious files the infection stores in the AppData\Roaming folder.
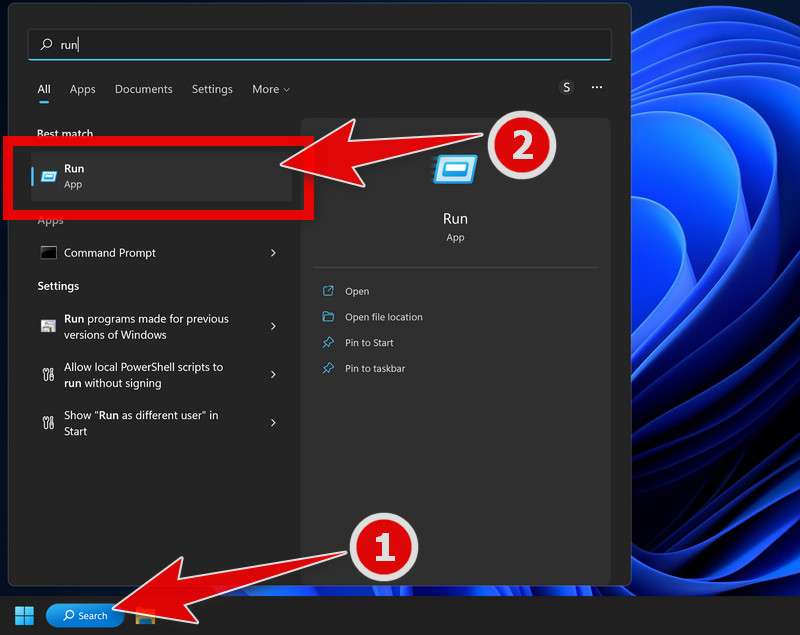
- Press Windows + R to open the Run app (or type “Run” in the Windows search bar).
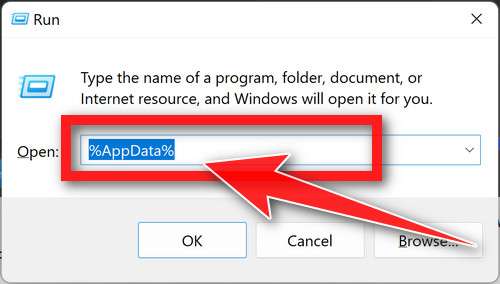
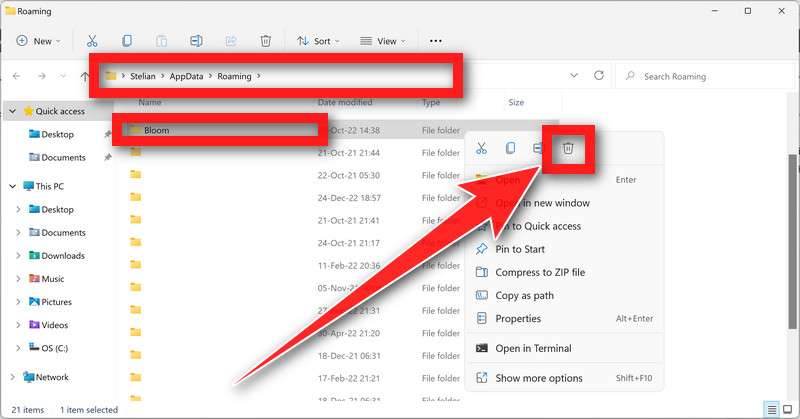
- In the Run box, type “%AppData%” and click OK. Windows will open the Roaming folder directly.
- Look for and delete any unknown folders with names like Default, Chrome32, Energy, Bloom, or Travel. The exact names on your computer may differ, but the pattern is the same: short, generic-sounding names that don’t match any program you’ve installed.
Be careful: only delete folders you’re confident don’t belong to a real program. Legitimate apps (Adobe, Spotify, Discord, etc.) also store their data here. If you’re unsure about a folder, search its name online first — or skip it; the automated scanners later in this guide will catch what you miss.
3. Delete Malicious Files from the AppData\Local Folder
Now we’ll do the same in the AppData\Local folder, and also remove the malicious Chrome extension the infection installed.
- Press Windows + R to open the Run app (or type “Run” in the Windows search bar).
- In the Run box, type “%localappdata%” and click OK. Windows will open the AppData\Local folder directly.
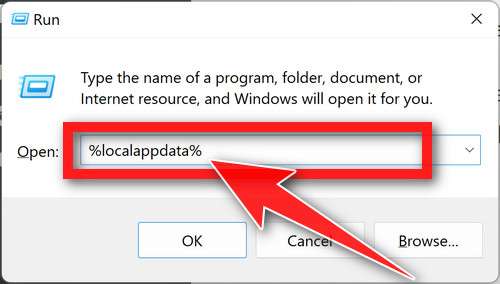
- Look for and delete the Default, WindowsApp, and ServiceApp folders, if present. (The same caution applies — when in doubt, look the name up before deleting.)
Next, open the Google folder and navigate to Google > Chrome > User Data > Default (or Profile) > Extensions. Inside the Extensions folder, find and delete the malicious extension’s folder — it will have a long, random-looking name. If you’re not sure which one it is, you can check each folder’s contents, or compare the names against the extensions visible at chrome://extensions in Chrome.
Important: inside User Data, the folder named “Default” is your legitimate Chrome profile — do not delete it. Only delete the individual extension folder inside Extensions.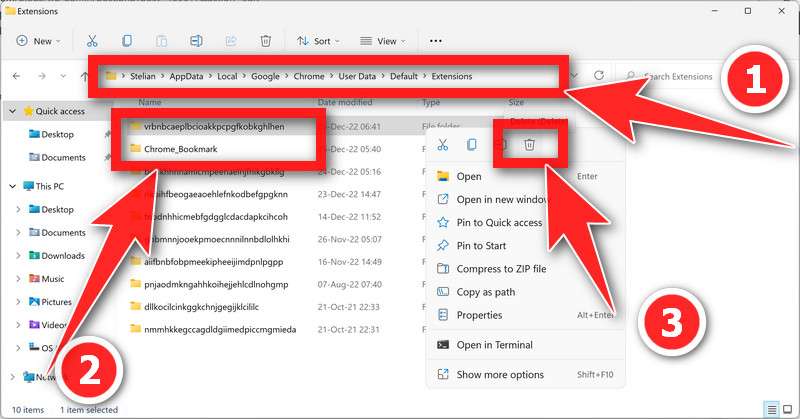
4. Fix the Hijacked Chrome Shortcut
This malware often modifies your Chrome shortcut so that every time you open the browser, the malicious extension loads with it. Here’s how to clean the shortcut:
- Right-click the Google Chrome shortcut on your desktop or Start Menu and select “Properties“.
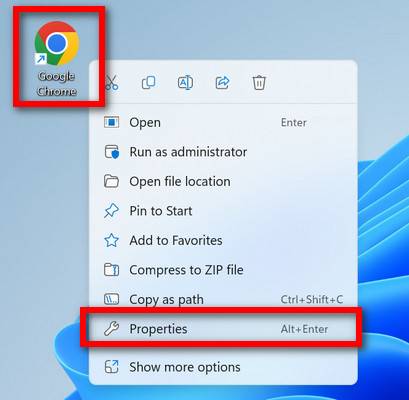
- On the Shortcut tab, check the “Target” field. It should end with chrome.exe” and nothing more. Delete any extra text appended after it — especially anything referencing the AppData folder, such as:
–load-extension=C:\Users\%USERNAME%\AppData\Local\Default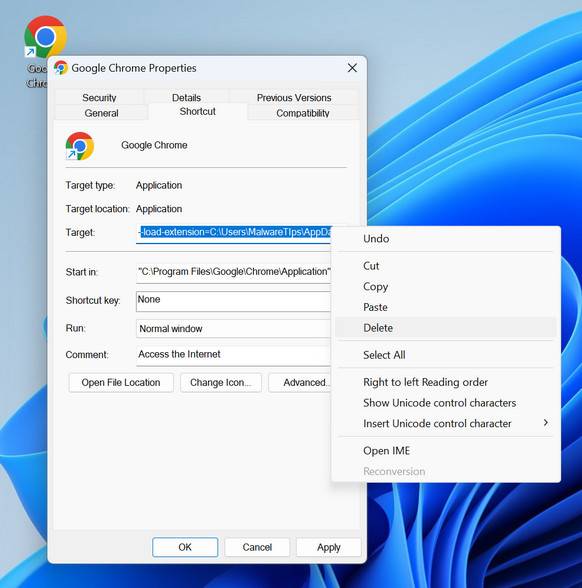
- Click OK to save the changes.
- Open Chrome from the shortcut as usual — the malicious extension should no longer load at startup.
Tip: if you’d rather not edit the Target field, there’s an easier fix — right-click the shortcut, select “Open File Location“, then drag chrome.exe to your taskbar to create a fresh, clean shortcut. Delete the old one.
With the malicious tasks, folders, and shortcut modifications removed, we can continue with the next step of this guide.
STEP 5: Reset your browser settings to their defaults
In this step, we will remove spam notifications, malicious extensions, and change to default any settings that might have been changed by malware.
Please note that this method will remove all extensions, toolbars, and other customizations but will leave your bookmarks and favorites intact. For each browser that you have installed on your computer, please click on the browsers tab below and follow the displayed steps to reset that browser.
Reset Chrome for Windows to default settings
We will now reset your Chrome browser settings to their original defaults. This will reset your startup page, new tab page, search engine, and pinned tabs. It will also disable all extensions and clear temporary data like cookies. Your favorites, history, and saved passwords will not be cleared.
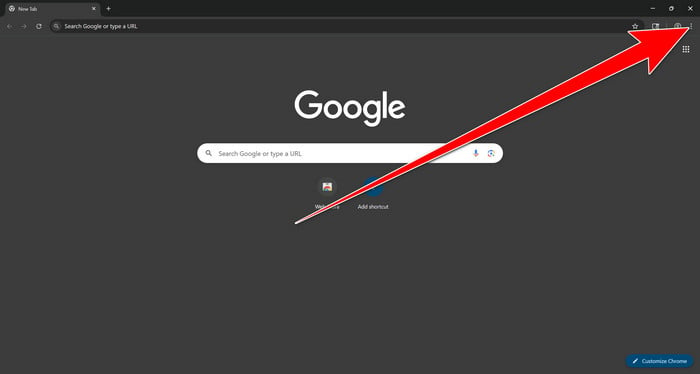
Open the Chrome menu
Open Google Chrome and click the three-dot (⋮) icon in the top-right corner.
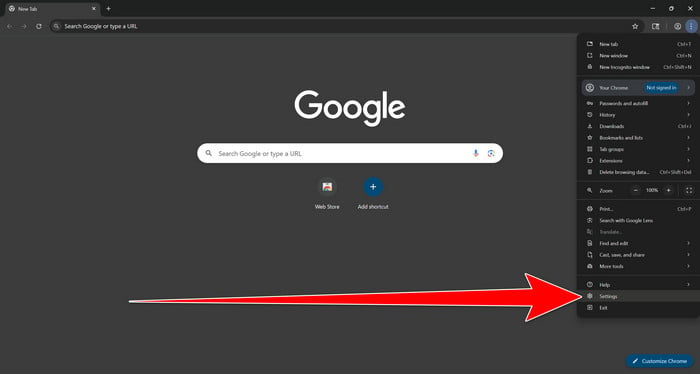
Open Chrome Settings
Select Settings from the Chrome menu.
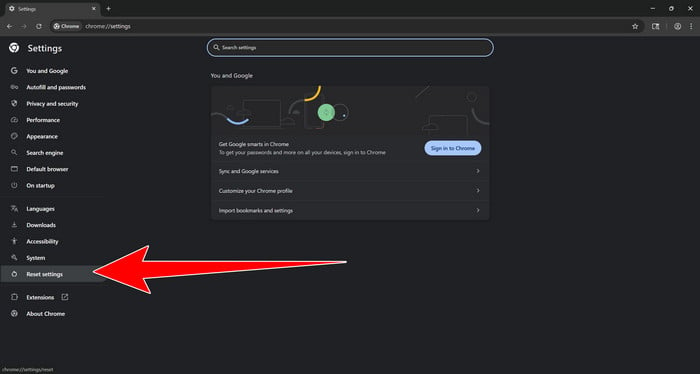
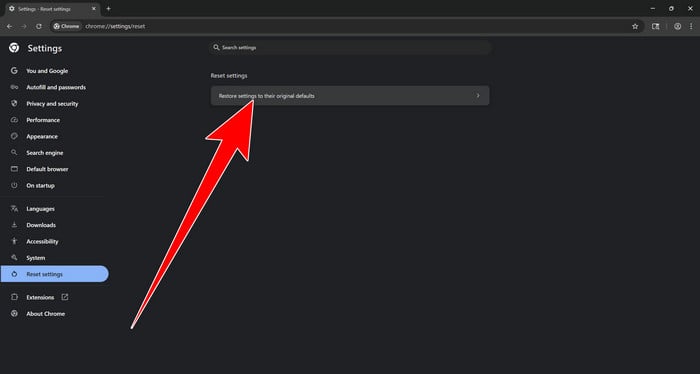
Select “Reset settings”
Look at the menu on the left side of the Settings page. Scroll down and click Reset settings.
Restore Chrome’s original settings
Click Restore settings to their original defaults.
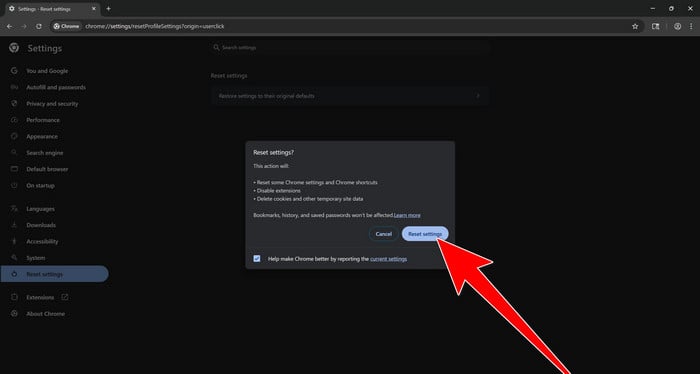
Confirm the Chrome reset
A confirmation window will appear. Click Reset settings.
This will:
- Restore the default search engine, homepage, and new tab page
- Reset startup pages and pinned tabs
- Disable installed extensions
- Clear temporary cookies and website data
Don’t worry: Chrome will not delete your bookmarks, browsing history, or saved passwords.
Restart Chrome and perform a test search. If your searches now open normally in Google, you can stop here.
If searches are still redirected through shady domains complete the additional step below.
Remove persistent search hijacker data
Only complete this step if the redirect continues after resetting Chrome.
Some browser hijackers hide inside Chrome’s local search-engine database. A standard Chrome reset may not remove this database, which is why searches can continue to pass through shady sites.
The following procedure creates a backup of the affected database and allows Chrome to build a new, clean version. This is safer and less disruptive than deleting the entire Chrome profile.
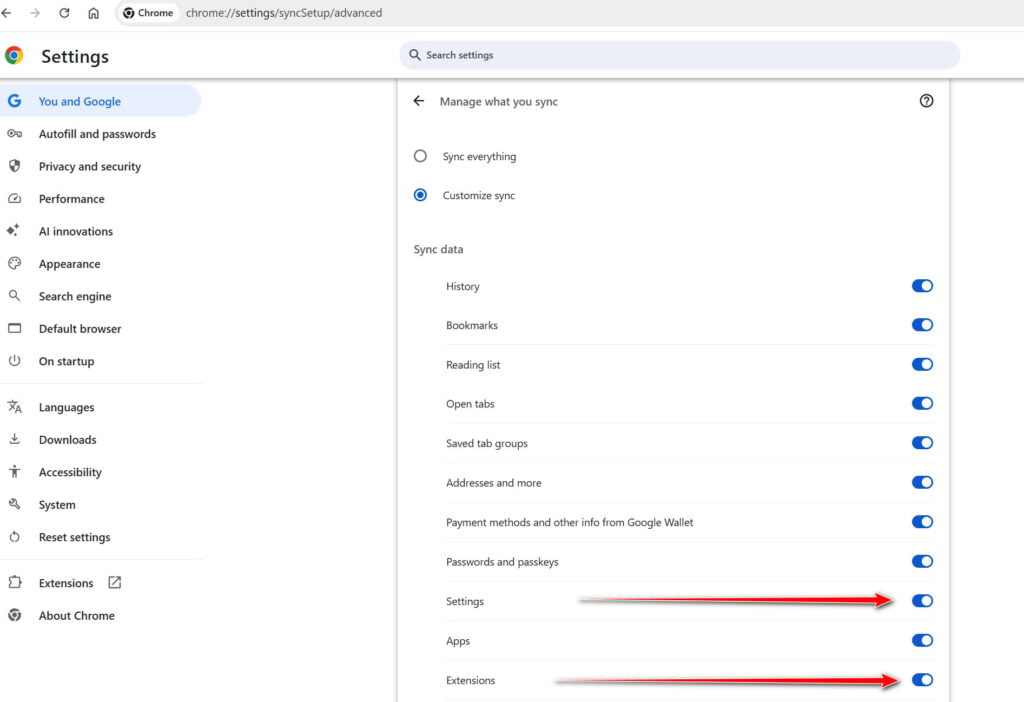
First, prevent Chrome Sync from restoring the hijacked settings:
- Open a new Chrome tab.
- Copy the following address, paste it into Chrome’s address bar, and press Enter:
chrome://settings/syncSetup/advanced - Under Manage what you sync, select Customize sync.
- Turn off Settings and Extensions.
- You can leave Bookmarks and Passwords enabled so your important data remains synchronized.
Note: Some newer Chrome versions may automatically redirect this address to the Google Account settings page. If that happens, locate the list of synchronized Chrome data and turn off Settings and Extensions there.
Now save anything you are working on and close every Chrome window.
Run the cleanup command:
- Press the Windows key on your keyboard.
- Type PowerShell.
- Open Windows PowerShell. Administrator access is not required.
- Copy the entire command shown below.
- Right-click inside the PowerShell window to paste the command, then press Enter.
- If Windows warns you about pasting multiple lines, select the option to continue.
$stamp = Get-Date -Format "yyyyMMdd-HHmmss"

Get-Process chrome -ErrorAction SilentlyContinue |
 Stop-Process -Force

$root = "$env:LOCALAPPDATA\Google\Chrome\User Data"

if (Test-Path $root) {
 $profiles = Get-ChildItem $root -Directory |
 Where-Object {
 $_.Name -eq "Default" -or
 $_.Name -match "^Profile \d+$"
 }

 foreach ($profile in $profiles) {
 foreach ($name in @(
 "Web Data",
 "Web Data-journal",
 "Web Data-wal",
 "Web Data-shm"
 )) {
 $file = Join-Path $profile.FullName $name

 if (Test-Path $file) {
 $backup = "$file.search-hijacker-backup-$stamp"
 Move-Item -LiteralPath $file -Destination $backup
 Write-Host "Backup created: $backup"
 }
 }
 }
}

Write-Host ""
Write-Host "Chrome search data has been cleaned."
Write-Host "You can now reopen Chrome."
Wait until PowerShell displays the following message:
Chrome search data has been cleaned.
You can now reopen Chrome.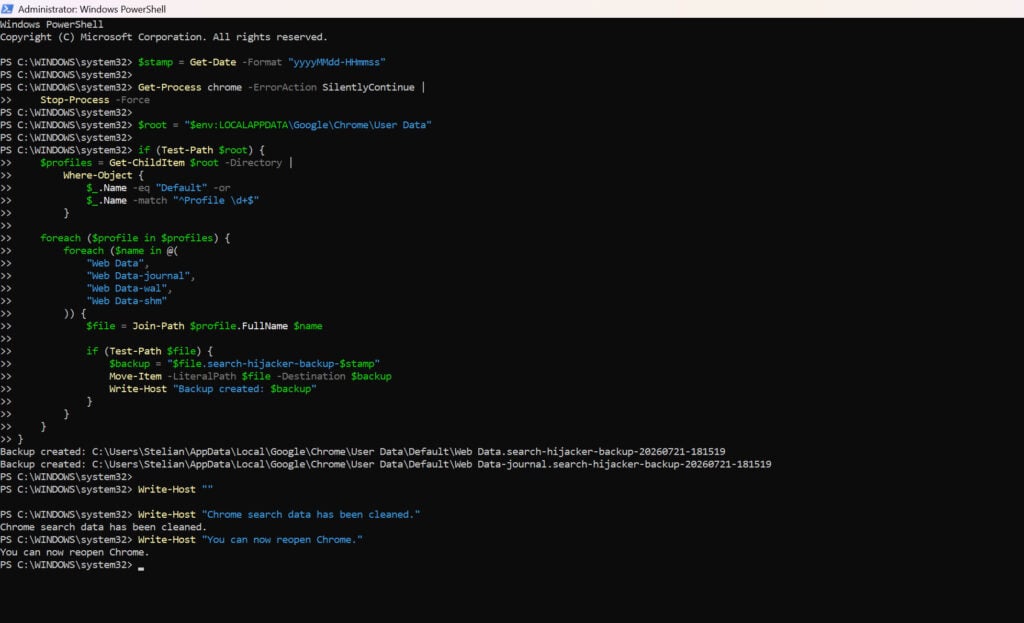
Close PowerShell and reopen Google Chrome. Chrome will automatically create a clean search database for every local profile.
Next, copy the following address, paste it into Chrome’s address bar, and press Enter:
chrome://settings/searchEnginesMake sure Google is selected as the default search engine. Test several searches from the address bar and confirm that they no longer pass through shady search engines.
Your important Chrome data is protected: the PowerShell cleanup does not remove bookmarks, saved passwords, browsing history, cookies, or installed extensions. However, it may reset locally stored Autofill addresses and form suggestions.
The original search database is not deleted. PowerShell renames it and adds
search-hijacker-backupto its filename so it can be recovered if necessary.Keep Settings and Extensions synchronization disabled while testing Chrome. Do not enable every extension at once. Enable only the extensions you recognize, one at a time, and test Chrome after each one.
If the redirect returns after enabling a particular extension, remove that extension immediately.
Reset Firefox for Windows to default settings
We will now reset your Firefox browser settings to their default. The reset feature fixes many issues by restoring Firefox to its factory default state while saving your essential information like bookmarks, passwords, web form auto-fill information, browsing history, and open tabs.
-
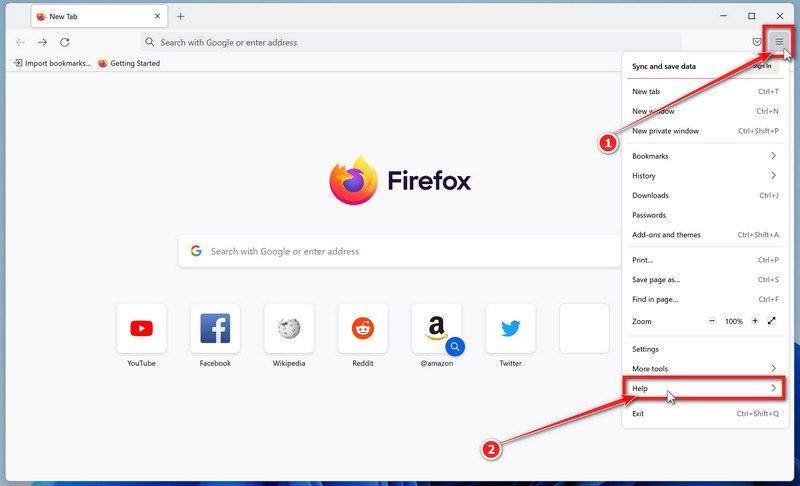
Open the Firefox menu and click “Help”
Click the three horizontal lines in the top-right corner of Firefox to open the main menu, then select “Help“.
-
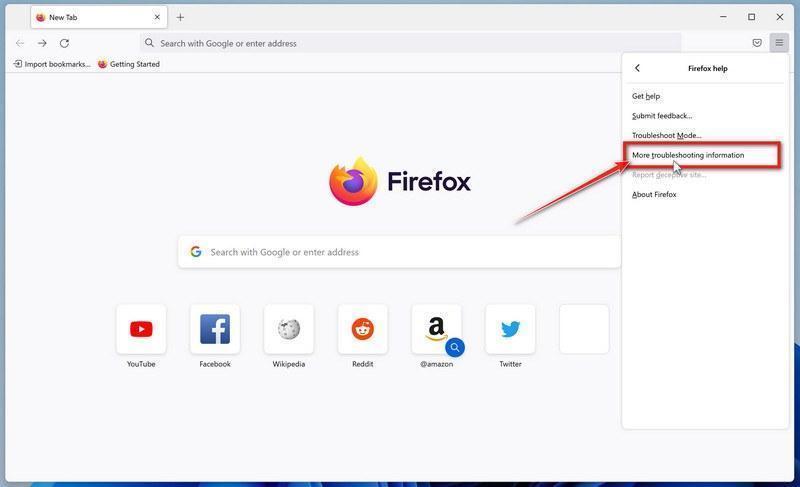
Click “More troubleshooting information”
In the Help menu, click “More troubleshooting information“.
-
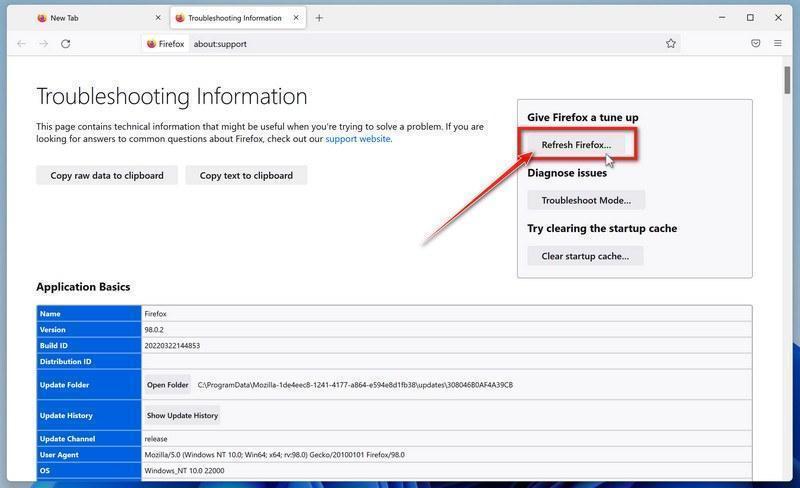
Click “Refresh Firefox”
On the “Troubleshooting Information” page, click the “Refresh Firefox” button in the top-right area of the page.
-
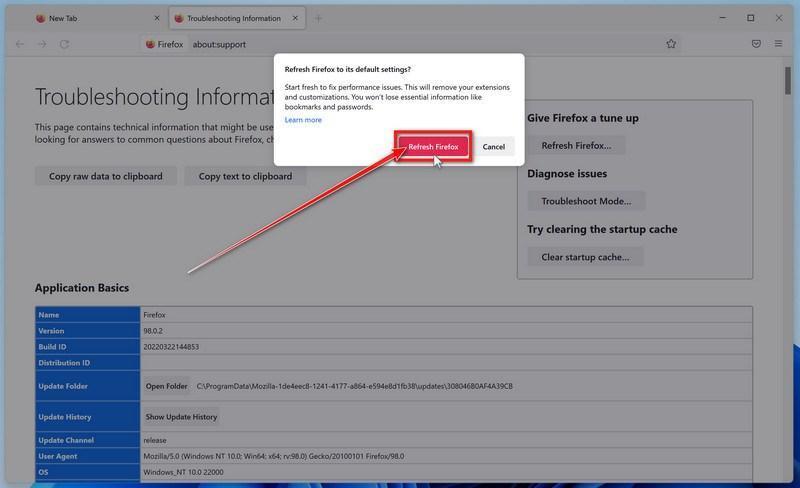
Confirm the refresh
In the confirmation window, click “Refresh Firefox” again. This removes extensions, themes, and customized settings — the usual hiding places for browser hijackers — while keeping your bookmarks, history, and saved passwords safe.
-
Click “Finish”
Firefox will close, reset itself to default settings, and reopen with a window listing the information that was restored. Click “Finish” — your Firefox is now clean.
About the “Old Firefox Data” folder: Firefox saves a copy of your old profile on your desktop. If something you need is missing after the reset, you can recover it from this folder. Otherwise, delete the folder — it contains sensitive data like passwords and cookies, and may also still hold the malicious files you just removed.
Reset Microsoft Edge to default settings
We will now reset your Microsoft Edge browser settings to their default. This will reset your startup page, new tab page, search engine, and pinned tabs. It will also disable all extensions and clear temporary data like cookies. Your favorites, history, and saved passwords will not be cleared.
Updated for Microsoft Edge on Windows 10 and Windows 11 — July 2026.
-
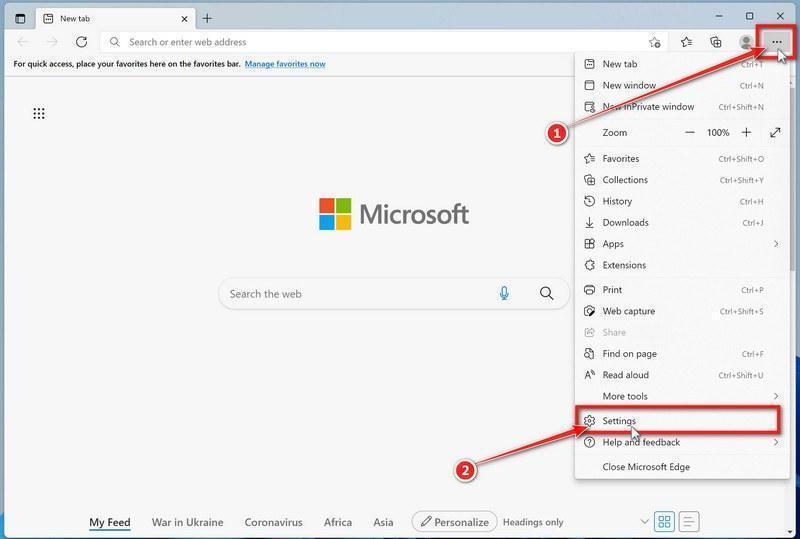
Open the Edge menu and click “Settings”
Open Microsoft Edge. In the top-right corner, click the three-dot (…) icon, then click Settings.
-
Prevent the unwanted settings from returning through Edge Sync
If you are signed in to Microsoft Edge, a bad setting or extension may be stored in your Microsoft account and return after the reset.
Copy the following address, paste it into the Edge address bar, and press Enter:
edge://settings/profiles/syncOn the Sync page, turn off these two options:
- Settings
- Extensions
You can leave Favorites and Passwords turned on.
If Edge says that sync is already off, simply continue to the next step.
Important: Edge Sync settings are separate for each profile. If you use more than one Edge profile, switch to each affected profile and repeat this step.
You do not need to sign out of your Microsoft account or delete the Edge profile.
-
Open “Reset settings”
In the left sidebar, click Reset settings.
You can also open the reset page directly. Copy the following address, paste it into the Edge address bar, and press Enter:
edge://settings/reset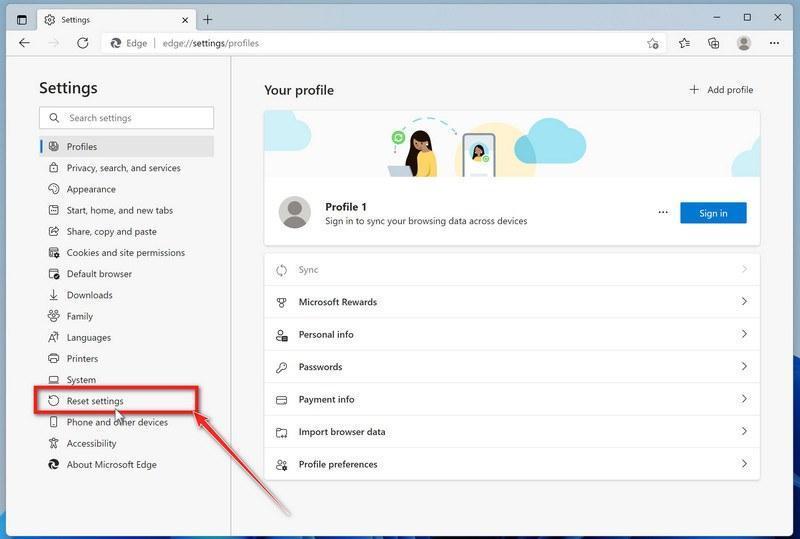
-
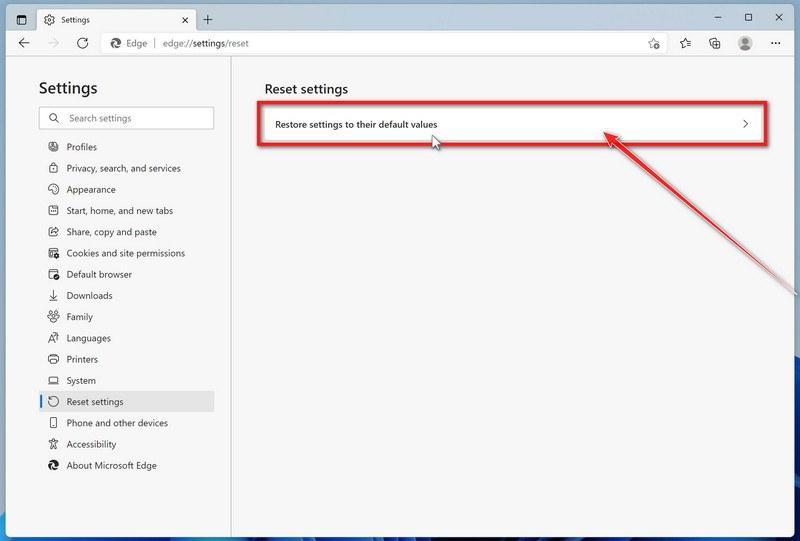
Click “Restore settings to their default values”
Click Restore settings to their default values.
-
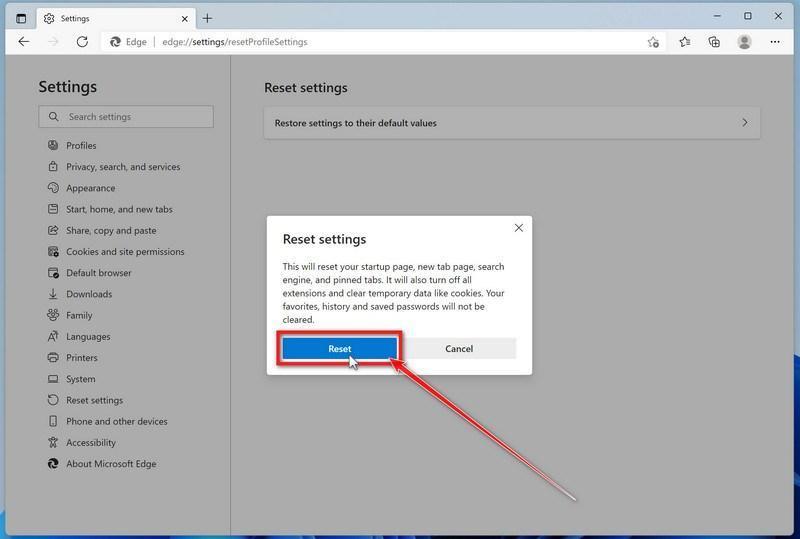
Confirm the reset
In the confirmation dialog, click Reset.
This resets the startup page, new tab page, search engine, and pinned tabs. It also disables all extensions and clears temporary site data, such as cookies.
Don’t worry: your favorites, browsing history, and saved passwords will not be deleted.
-
Check your extensions before turning them back on
Copy the following address, paste it into the Edge address bar, and press Enter:
edge://extensionsRemove any extension you do not recognize or no longer use. Pay particular attention to extensions related to search, coupons, shopping, PDF conversion, browser protection, new tabs, or video downloading.
Do not turn all extensions back on at the same time. Enable only the extensions you recognize and trust.
-
Select a trusted search engine
Copy the following address, paste it into the Edge address bar, and press Enter:
edge://settings/searchEnginesSelect Bing, Google, DuckDuckGo, or another search provider you trust and make it the default.
Remove any unknown search engines, especially providers with strange names or addresses that you did not add yourself.
Restart Edge and perform a search from the address bar. If searches are no longer redirected, you can stop here.
-
If the redirect remains, clean the corrupted search data without deleting the Edge profile
Use this additional step only if Edge continues to redirect searches after the normal reset.
This command cleans the search-engine database from every local Edge profile while keeping your favorites, saved passwords, browsing history, cookies, and profiles.
Before continuing: save anything you are working on because the command will close Microsoft Edge.
- Open the Windows Start menu.
- Type PowerShell.
- Open Windows PowerShell. Administrator access is not required.
- Copy the entire command below.
- Paste it into PowerShell and press Enter.
$stamp = Get-Date -Format "yyyyMMdd-HHmmss"
$root = Join-Path $env:LOCALAPPDATA "Microsoft\Edge\User Data"

Get-Process -Name msedge -ErrorAction SilentlyContinue |
    Stop-Process -Force -ErrorAction SilentlyContinue

Start-Sleep -Seconds 2

if (-not (Test-Path -LiteralPath $root)) {
    Write-Host "The Microsoft Edge profile folder was not found:"
    Write-Host $root
    return
}

$profiles = Get-ChildItem -LiteralPath $root -Directory |
    Where-Object {
        $_.Name -eq "Default" -or
        $_.Name -match "^Profile \d+$"
    }

$movedFiles = 0

foreach ($profile in $profiles) {
    foreach ($name in @(
        "Web Data",
        "Web Data-journal",
        "Web Data-wal",
        "Web Data-shm"
    )) {
        $file = Join-Path $profile.FullName $name

        if (Test-Path -LiteralPath $file) {
            $backup = "$file.search-reset-backup-$stamp"

            try {
                Move-Item -LiteralPath $file -Destination $backup -ErrorAction Stop
                Write-Host "Cleaned: $($profile.Name)\$name"
                $movedFiles++
            }
            catch {
                Write-Warning "Could not clean: $file"
            }
        }
    }
}

Write-Host ""

if ($movedFiles -gt 0) {
    Write-Host "Microsoft Edge search data has been cleaned." -ForegroundColor Green
    Write-Host "You can now reopen Microsoft Edge."
}
else {
    Write-Host "No Edge search database files were found." -ForegroundColor Yellow
}
The command does not permanently delete the original files. It renames them as backup files, and Edge creates a clean search database when it starts again.
Note: this additional cleanup may also reset saved form-fill suggestions, saved addresses, and manually added search engines. It does not delete favorites, passwords, or browsing history.
-
Reopen Edge and test the browser
Open Microsoft Edge again, visit edge://settings/searchEngines, and select your preferred search engine.
Perform several searches from the address bar to confirm that the redirect is gone.
Keep synchronization for Settings and Extensions turned off until you are certain that the computer and extensions are clean. If you enable them again, turn them on one at a time and test Edge after each change.
-
If Edge still redirects your searches
Open edge://policy. If this is your personal computer and Edge displays unknown policies such as ExtensionInstallForcelist or DefaultSearchProvider, the hijacker may be installed outside the browser profile.
In that situation, continue with the next malware-removal steps and run a complete antivirus scan. If the computer belongs to a company or school, contact its IT administrator before changing any policies.
Reset Internet Explorer to default settings
We will now reset your Internet Explorer browser settings to their default. You can reset Internet Explorer settings to return them to the state they were in when Internet Explorer was first installed on your computer.
-
Go to “Internet Options”.
Open Internet Explorer, click on the gear icon in the upper-right part of your browser, then select “Internet Options“.
-
Select the “Advanced” tab, then click “Reset”
In the “Internet Options” dialog box, select the “Advanced” tab, then click on the “Reset” button.
-
Click on “Reset”.
In the “Reset Internet Explorer settings” section, select the “Delete personal settings” checkbox, then click on the “Reset” button.
-
Click on “Close”.
When Internet Explorer has completed its task, click on the “Close” button in the confirmation dialogue box.
Close your browser and then you can open Internet Explorer again.
STEP 6: Use Malwarebytes to remove trojans and browser hijackers
In this step, we will install and run a scan with Malwarebytes Free to remove any infections, adware, or potentially unwanted programs that may be present on your computer.
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.
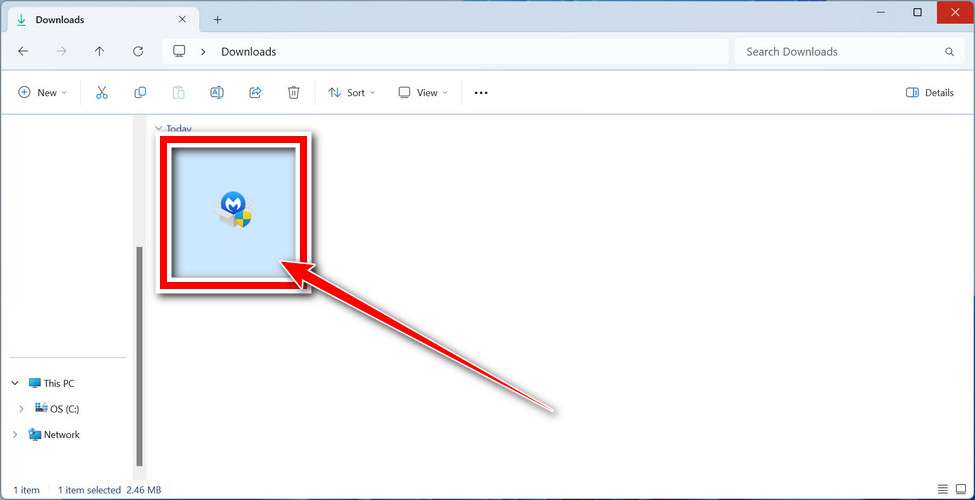
Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.
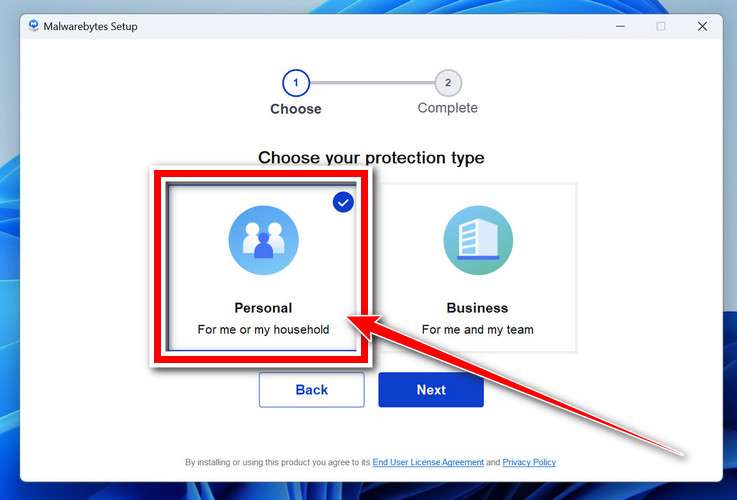
-
Malwarebytes will now install on your device. This usually takes under a minute.
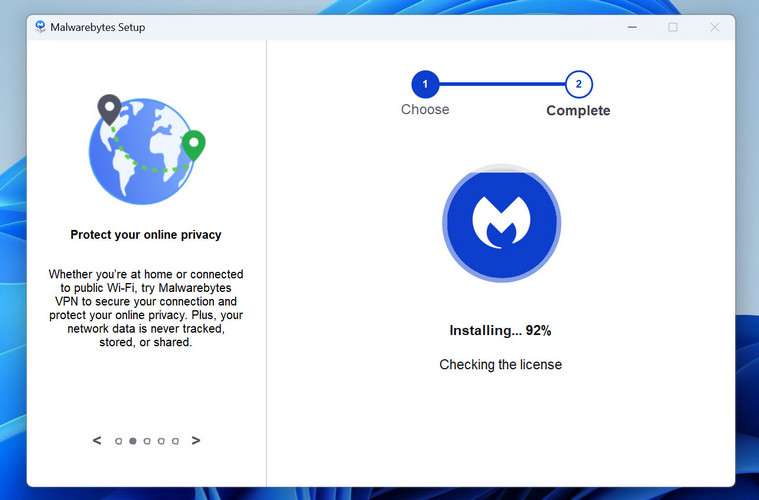
-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.
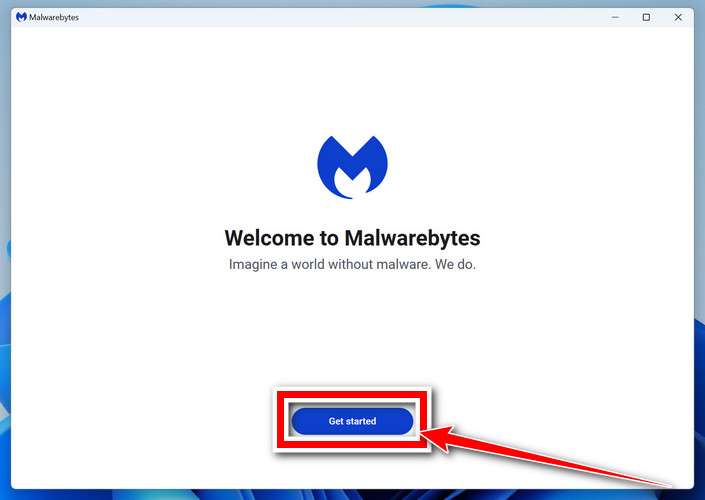
-
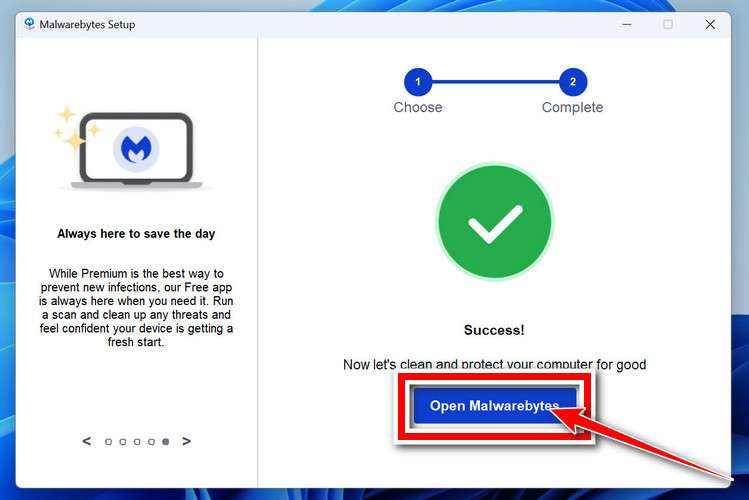
On the final screen, click Open Malwarebytes to launch the program.
-
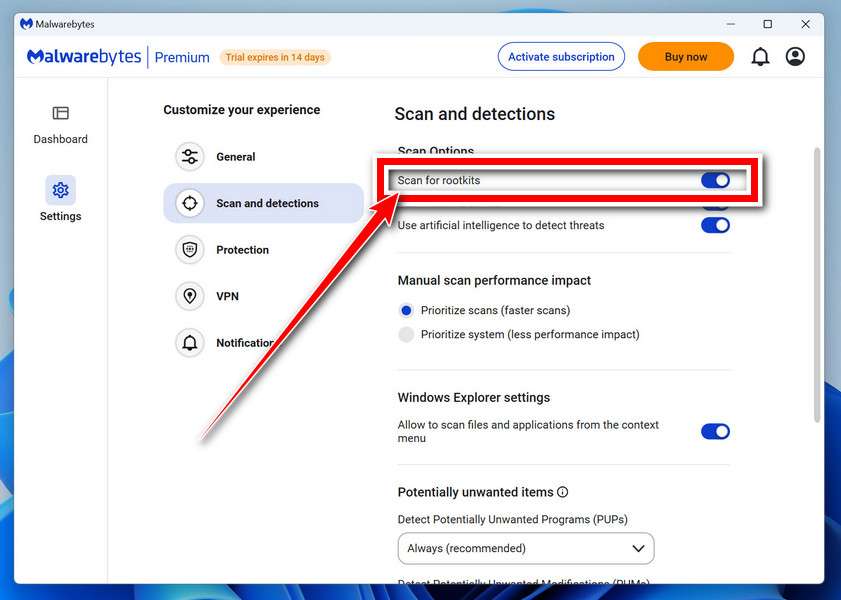
Enable “Scan for Rootkits”
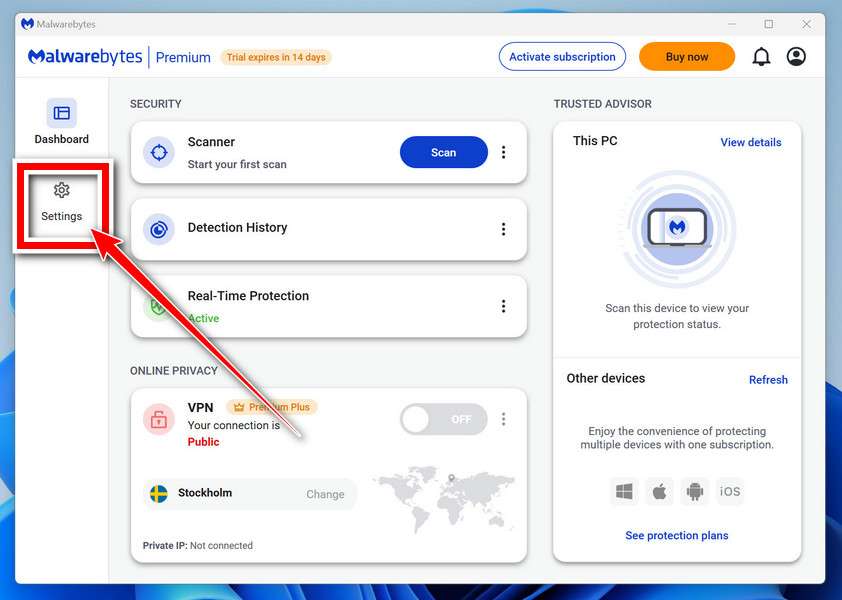
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.
In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.
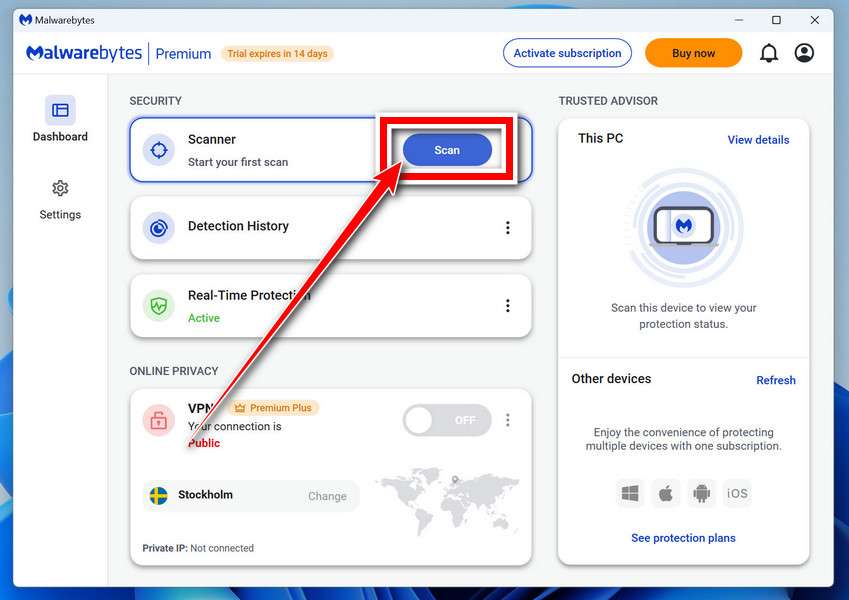
Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.
-
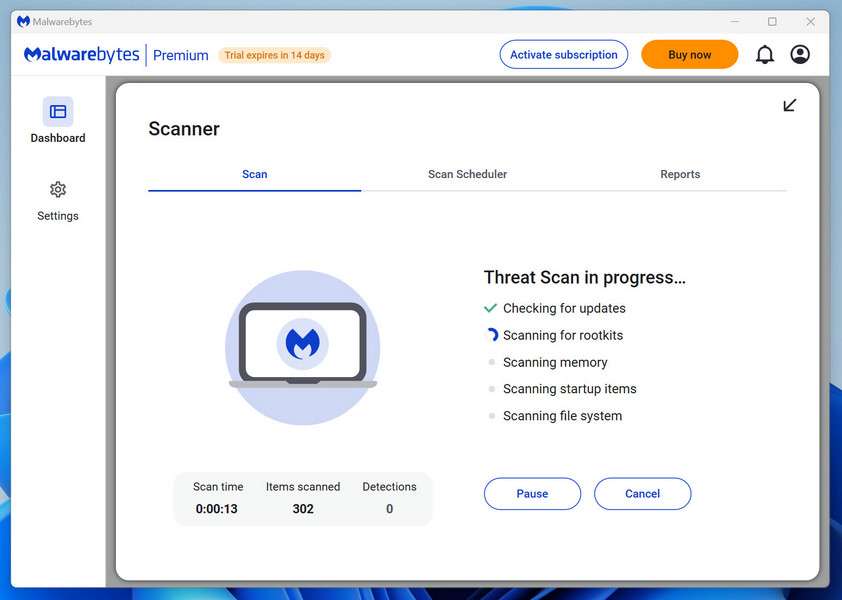
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.
-
Quarantine the Detected Threats
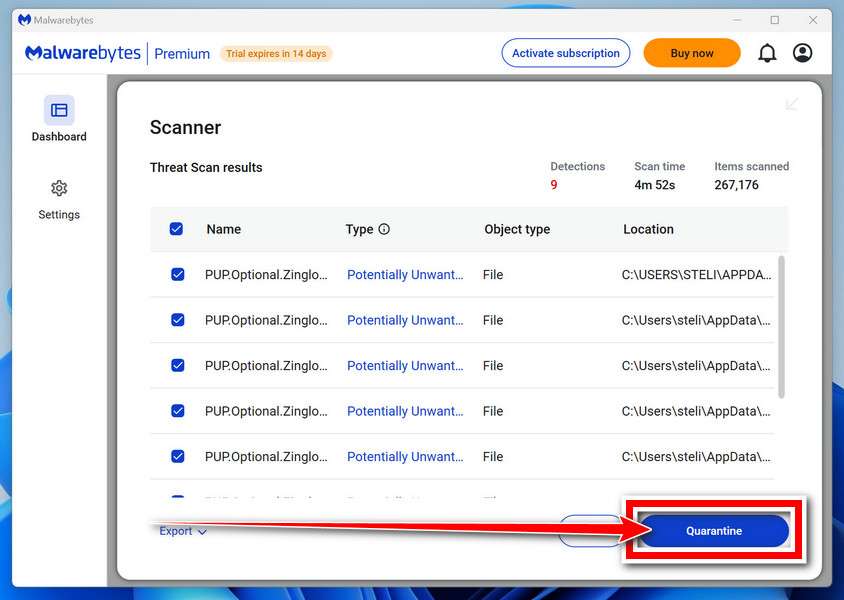
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.
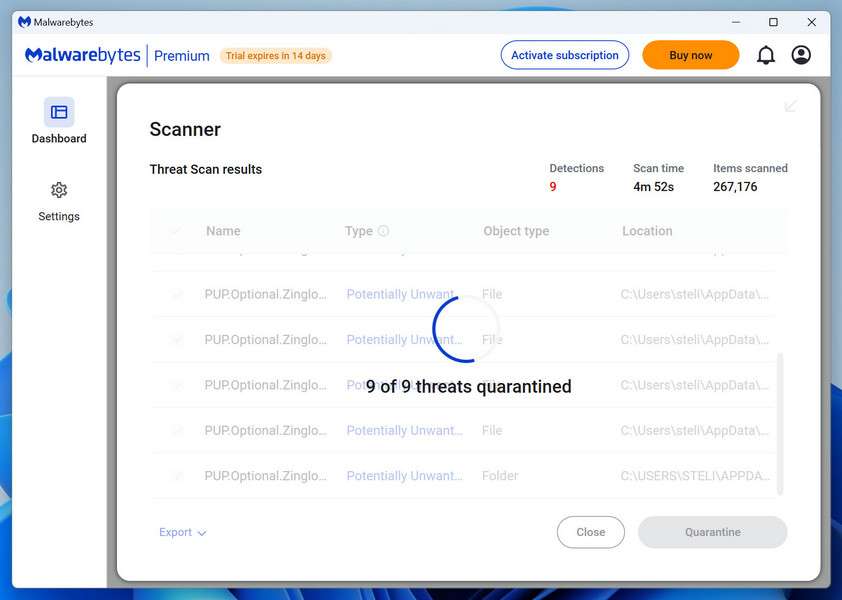
Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.
-
Restart Your Computer
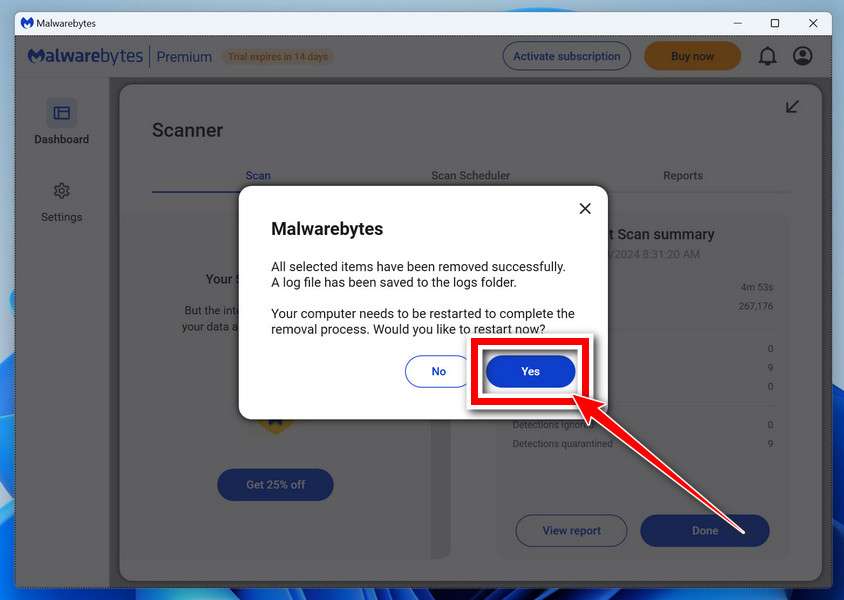
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.
STEP 7: Use HitmanPro to scan your computer for rootkits and other malware
In this next step, we will scan the computer with HitmanPro to ensure that no other malicious programs are installed on your device.
HitmanPro is a second-opinion scanner — it’s designed to catch what your main antivirus might have missed. Instead of relying on a single detection engine, it checks the behavior of files in the locations where malware usually hides. Anything suspicious gets sent to the cloud, where it’s analyzed by two of the best antivirus engines available: Bitdefender and Kaspersky.
Good news: scanning is completely free, with no limits. You only need a license when it’s time to remove what was found — and even then, you can activate a free one-time 30-day trial to clean your PC at no cost. (A full license is $24.95 per year for 1 PC.)
-
Download HitmanPro
Click the button below to download HitmanPro. Remember — the scan is free, so you have nothing to lose by checking your PC.
Download HitmanProFree scan. Removing threats needs the free 30-day trial. Opens the official HitmanPro page in a new tab. HitmanProSecond-opinion malware scanner from Sophos
-
Install HitmanPro
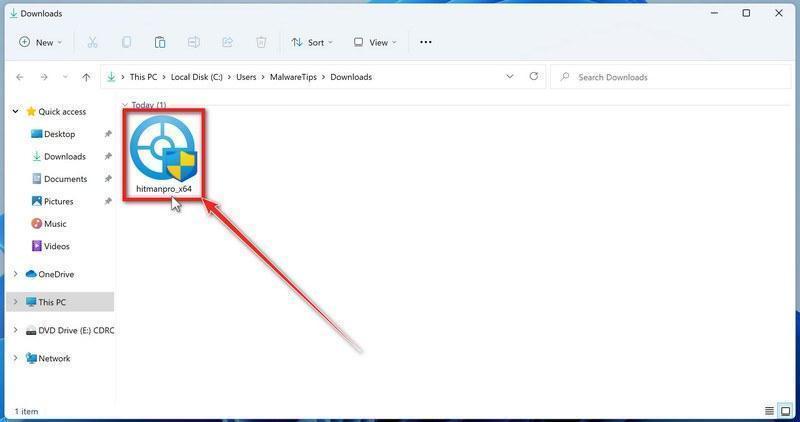
When the download finishes, open your Downloads folder and double-click the file: “hitmanpro.exe” on 32-bit Windows, or “hitmanpro_x64.exe” on 64-bit Windows.
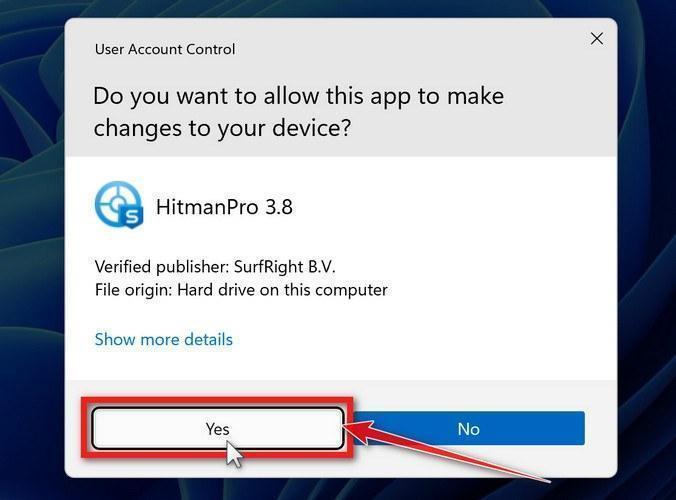
If a User Account Control pop-up asks whether HitmanPro can make changes to your device, click “Yes” to continue.
-
Follow the On-Screen Prompts
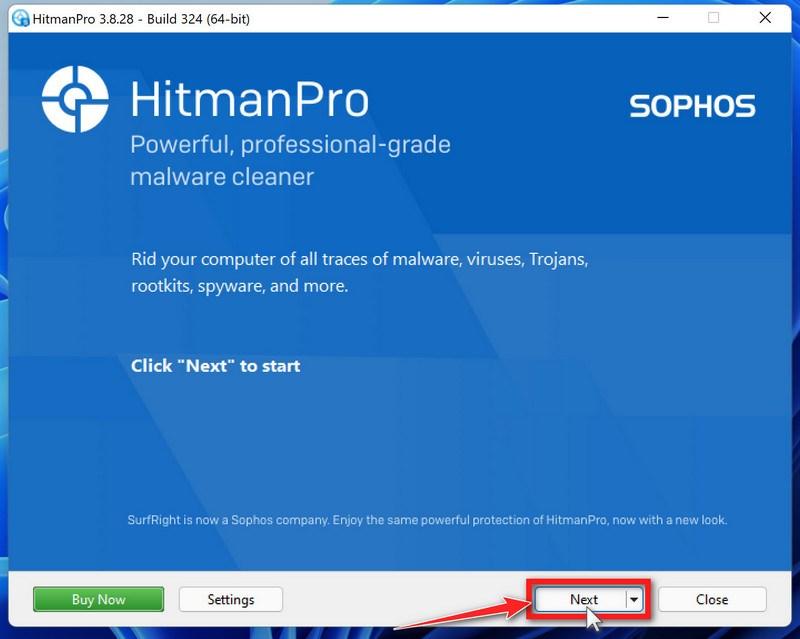
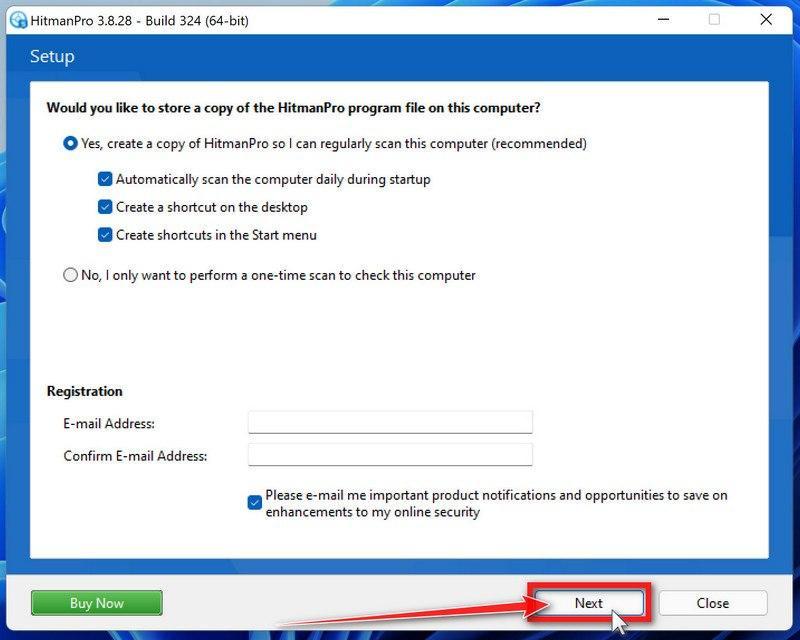
On the HitmanPro start screen, click “Next” to begin the system scan. No lengthy setup required — it goes straight to work.
-
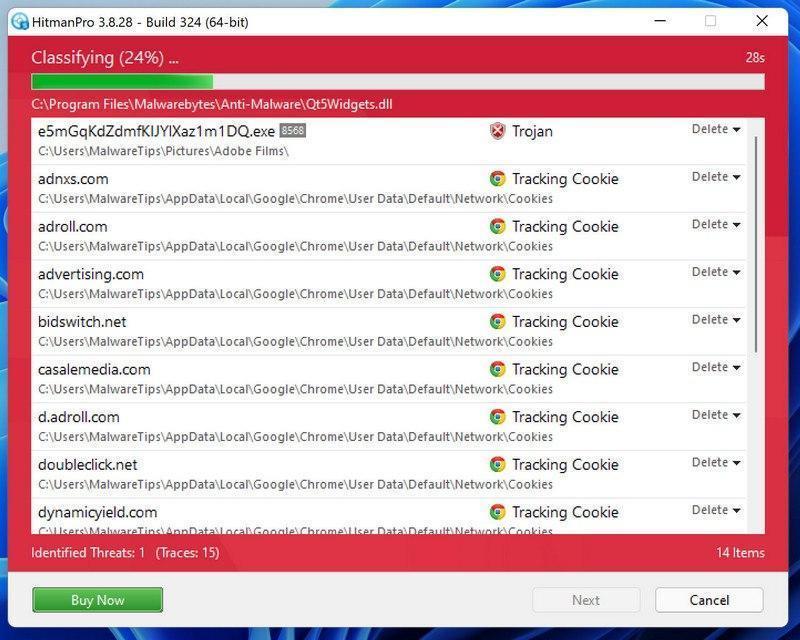
Wait for the Scan to Finish
HitmanPro will now check your computer for malicious programs. This usually takes just a few minutes thanks to its cloud-based scanning.
-
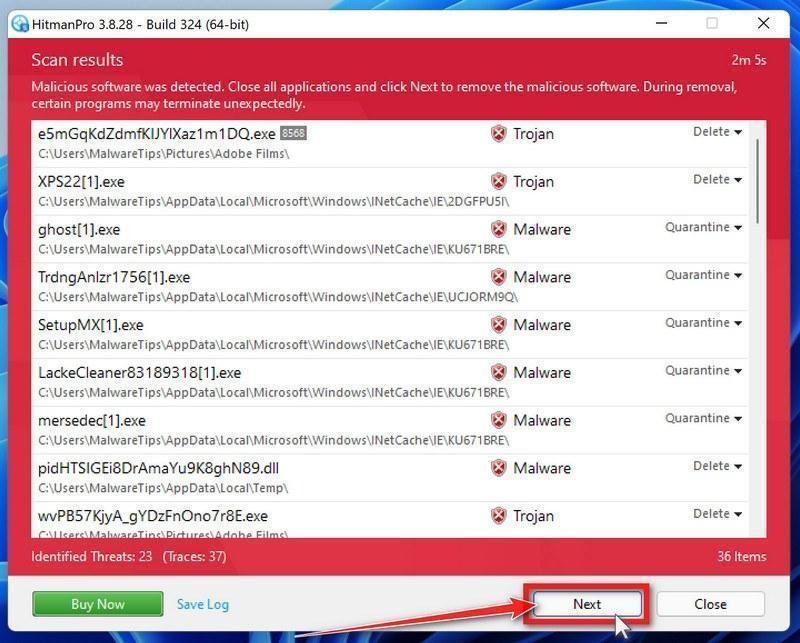
Review the Results and Click “Next”
When the scan is done, HitmanPro will show you everything it found. Click “Next” to remove the detected threats.
-
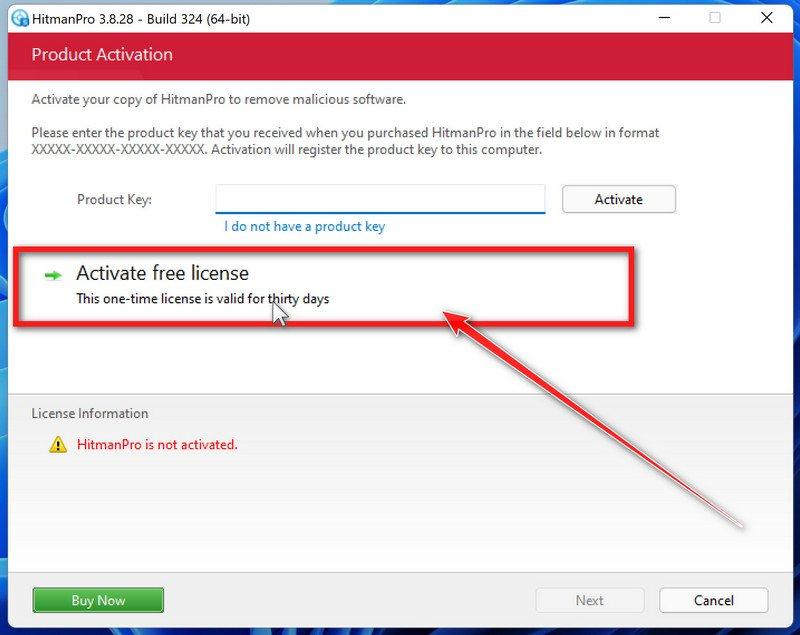
Click “Activate Free License”
To remove the malicious files, click the “Activate free license” button. This starts your free 30-day trial — no payment details needed — and unlocks the full cleanup.
When the removal is complete, HitmanPro will show a summary of everything it cleaned. Click Next, then click Reboot if prompted. If there’s no reboot prompt, just click Close — your PC is clean.
STEP 8: Use AdwCleaner to remove adware and malicious browser policies
In this final step, we will download and install AdwCleaner to remove the malicious browser policies that were set by browser hijackers on your computer and delete malicious browser extensions.
AdwCleaner is a free on-demand scanner that specializes in adware, browser hijackers, and unwanted toolbars — the exact threats that mainstream antivirus programs often miss. It also includes tools that repair the damage malware leaves behind, like hijacked browser settings and malicious policies. It’s a quick scan that’s well worth running.
-
Download AdwCleaner
Click the button below to download AdwCleaner — it’s free, portable, and requires no installation.
Download AdwCleanerOpens the official download page in a new tab. Malwarebytes AdwCleanerRemoves adware and unwanted programs at no cost
-
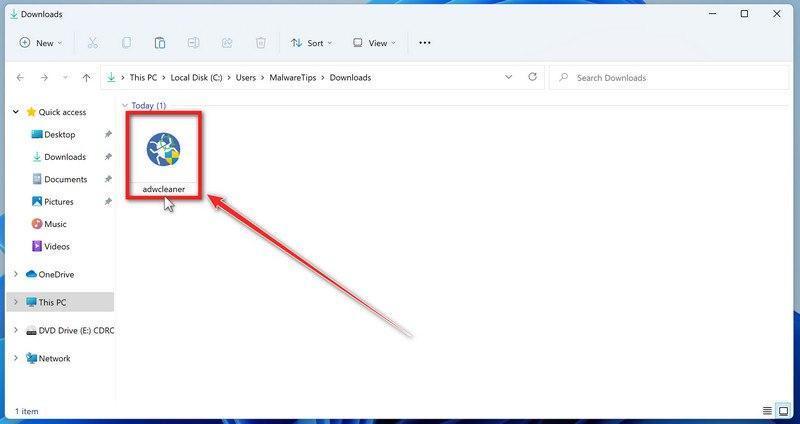
Run AdwCleaner
Open your Downloads folder and double-click the file named “adwcleaner.exe“. There’s no installation — the program starts right away.
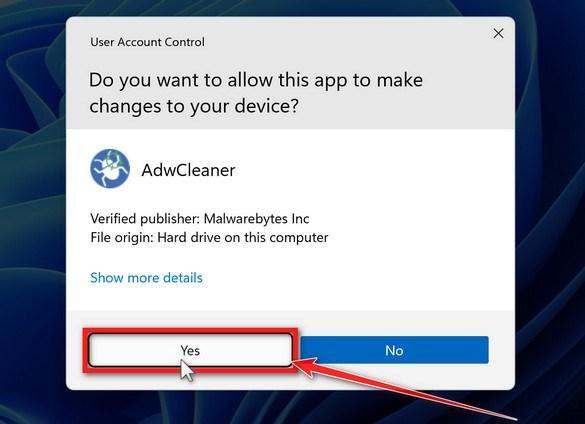
If Windows asks whether you want to allow AdwCleaner to run, click “Yes“. When the license agreement appears, click I agree to continue.
-
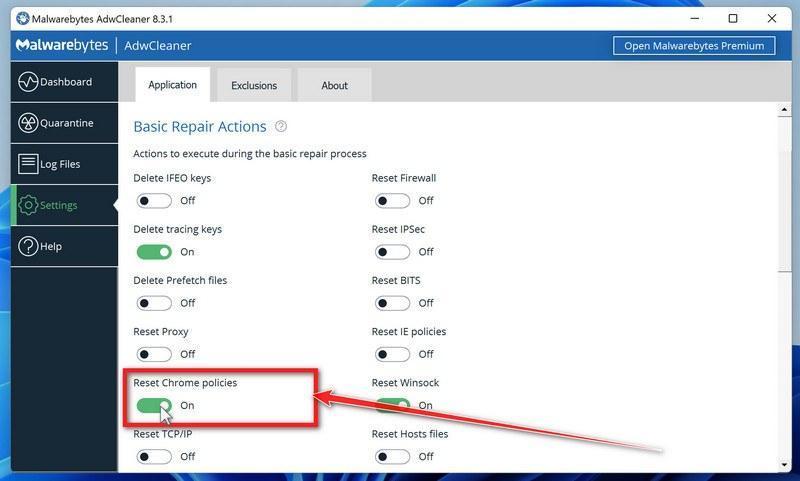
Enable “Reset Chrome policies”
This setting removes malicious browser policies — a trick malware uses to lock your browser settings so you can’t change them back. Click “Settings” on the left side of the window, then turn on “Reset Chrome policies“.
-
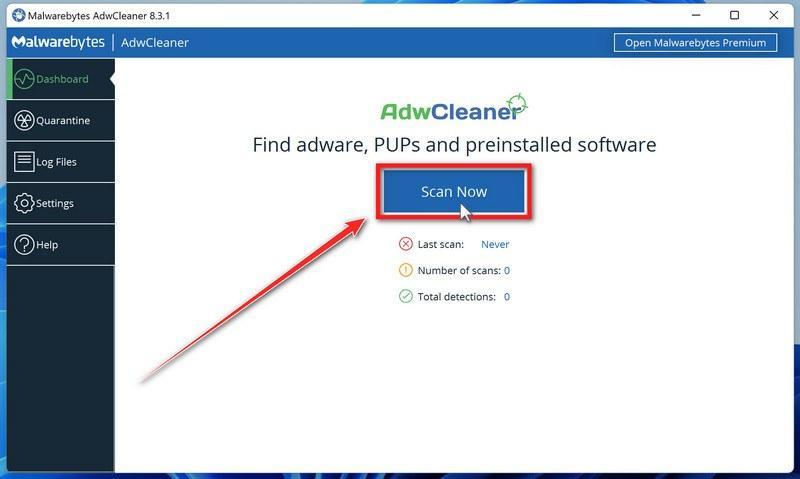
Start the Scan
Click “Dashboard” on the left side of the window, then click the “Scan” button.
-
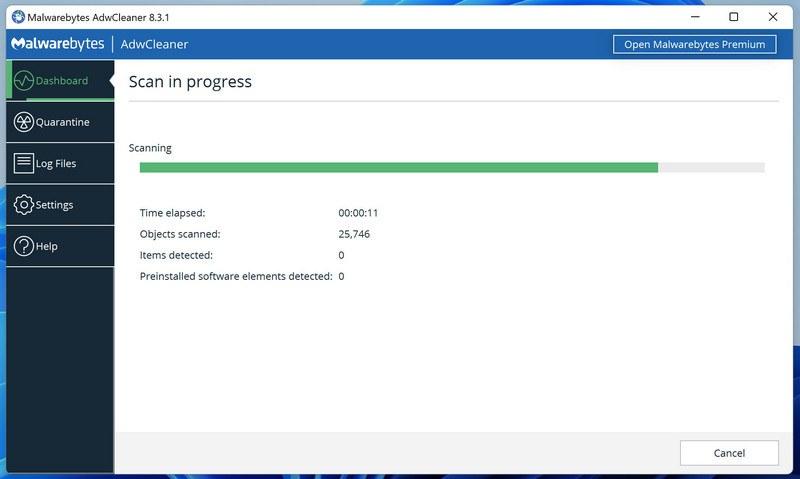
Wait for the Scan to Finish
AdwCleaner will now check your computer for adware and other malware. This usually takes only a few minutes — it’s one of the fastest scanners around.
-
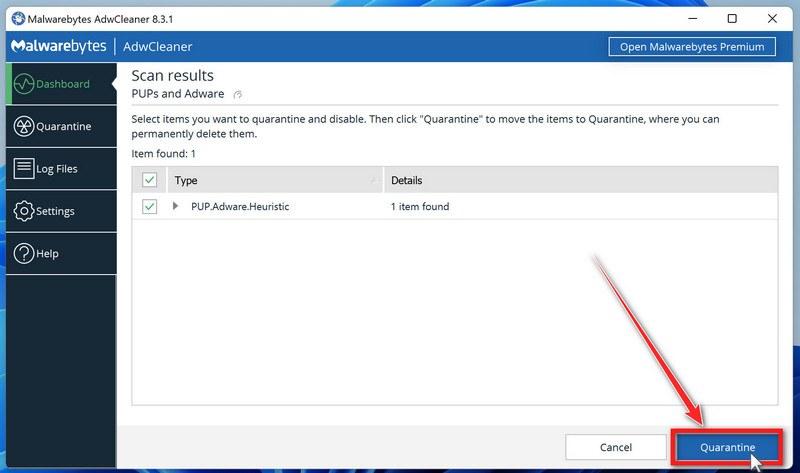
Quarantine the Detected Threats
When the scan finishes, AdwCleaner will list everything it found. Click the “Quarantine” button to remove all the malicious items at once.
-
Click “Continue” to Finish the Cleanup
Save any open work first — AdwCleaner needs to close your open programs before it can clean. When you’re ready, click the “Continue” button.
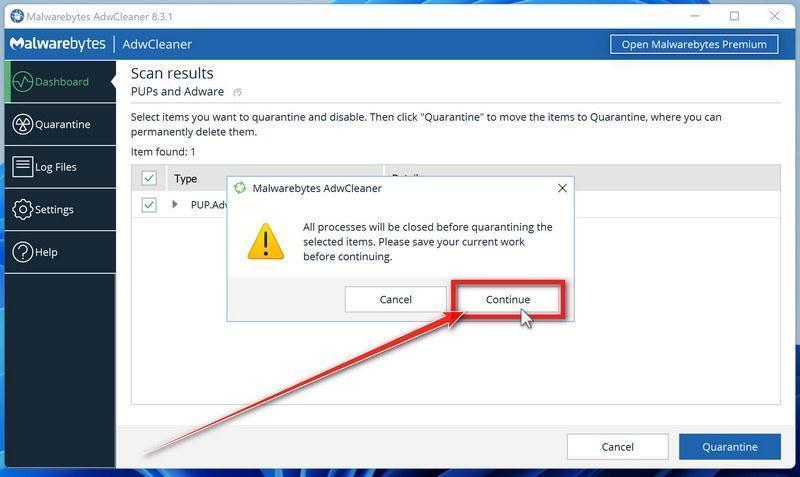
AdwCleaner will now delete all detected malware from your computer. If it asks you to restart your PC, allow it — your computer will be clean when you log back in.
Your computer should now be free of the SorbusAucuparia extension and other malware.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Remove SorbusAucuparia from Mac
- STEP 1: Reset browsers back to default settings
- STEP 2: Use Malwarebytes for Mac to remove malware and unwanted programs
STEP 1: Reset browsers back to default settings
First, we’ll restore your browser to its default settings — this removes the spam notification permissions, malicious extensions, and unwanted browser settings in one go.
Don’t worry: the reset removes extensions, toolbars, and customizations, but your bookmarks and favorites stay intact.
For each browser installed on your Mac, click its tab below and follow the steps to reset it.
Remove Malware and Spam Push Notifications from Safari
To stop the spam notifications in Safari, we’ll check for malicious extensions and restore the browser settings to their defaults.
-
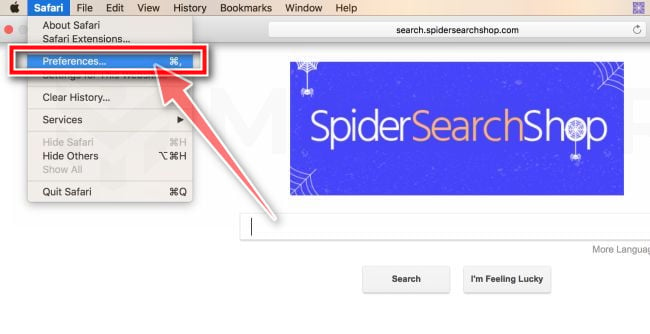
Go to Safari’s “Preferences”.
On the menu bar, click the “Safari” menu and select “Preferences”.
-
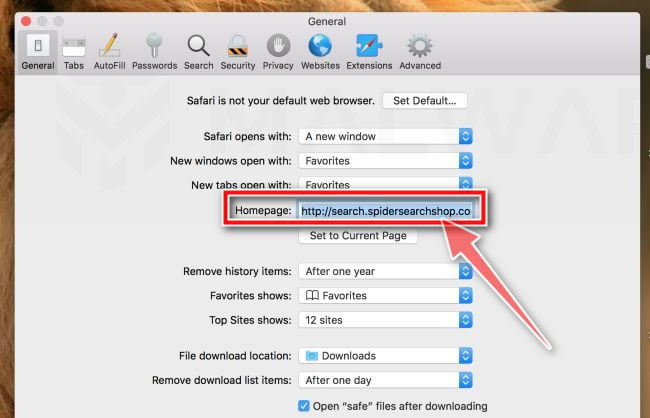
Check Homepage.
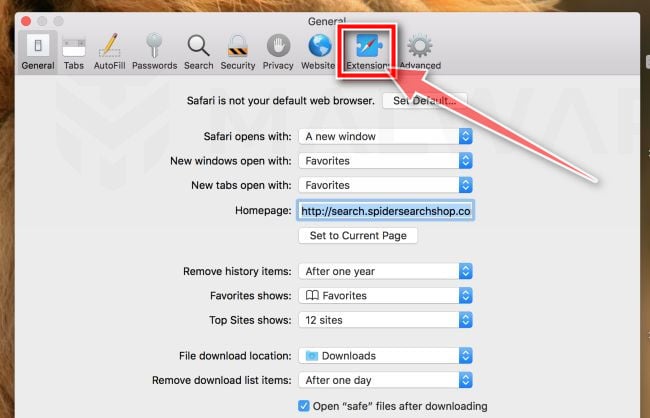
This will open a new window with your Safari preferences, opened to the “General” tab. Some browser hijackers may change your default homepage, so in the Homepage field make sure it’s a web page you want to use as your start-up page.
-
Click “Extensions”
Next, click on the “Extensions” tab.
-
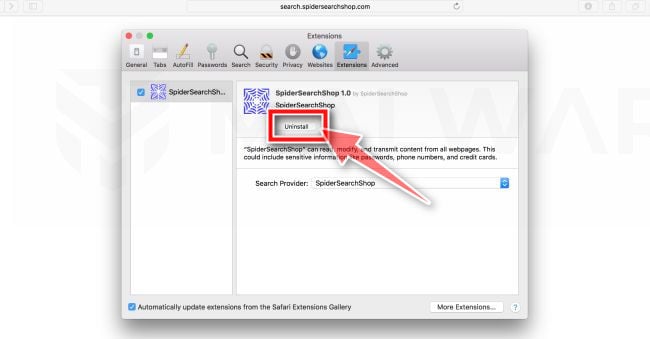
Find and uninstall malicious extensions.
The “Extensions” screen will be displayed with a list of all the extensions installed on Safari. Look out for any suspicious browser extension that could be behind all the drama – anything you don’t remember downloading or that doesn’t sound like a genuine extension. By default, there are no extensions installed on Safari so it’s safe to remove an extension
-
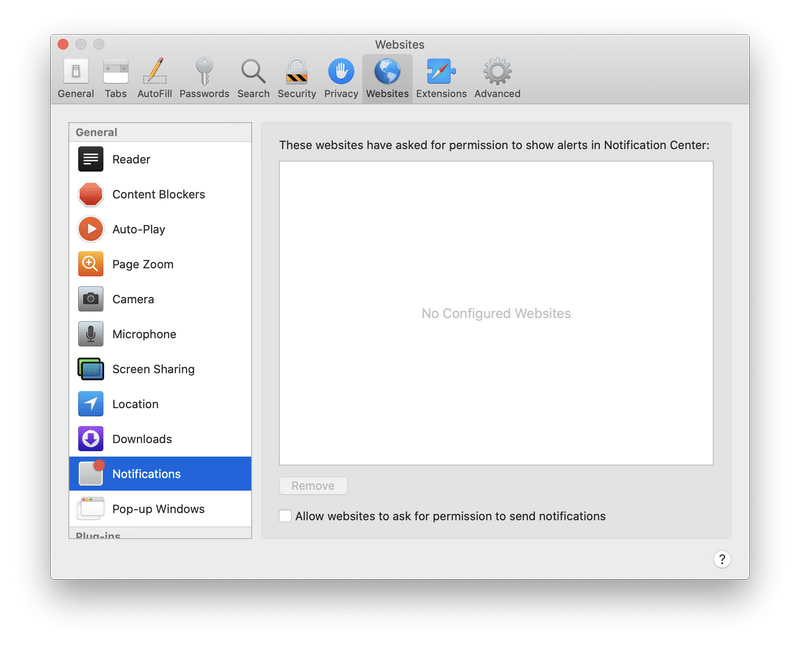
Remove spam notifications ads
Click Preferences, click Websites, then click Notifications. Deselect “Allow websites to ask for permission to send push notifications”.
-
Remove all data stored by websites on your computer.
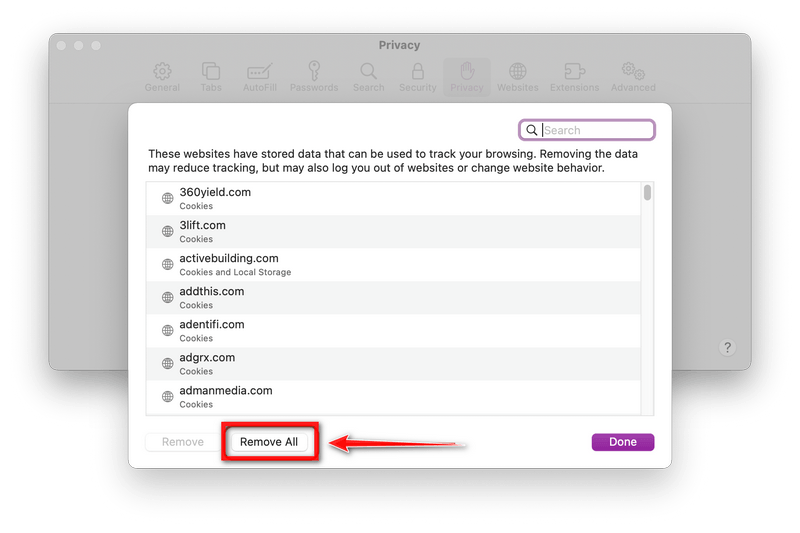
In the Safari menu, choose “Preferences…”, select “Privacy” at the top of the new window that appears, and then click the “Manage Website Data” button.
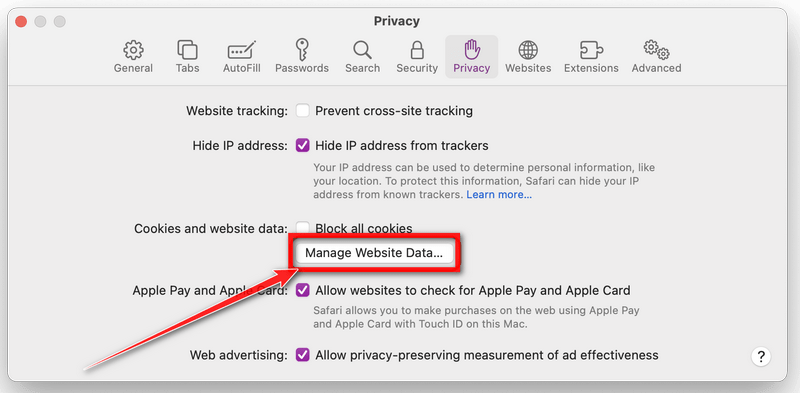
In the next dialog box, click “Remove All“. It will ask you if you are sure you want to remove all data stored by websites on your computer. Select “Remove Now” to clear data that could be used to track your browsing.
-
Empty Safari Caches.
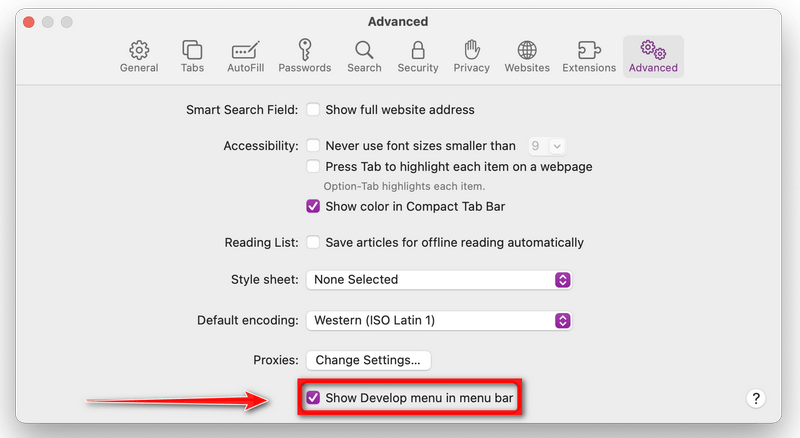
From your Safari menu bar, click Safari and select Preferences, then select the Advanced tab. Enable the checkbox to “Show Develop menu in menu bar“.
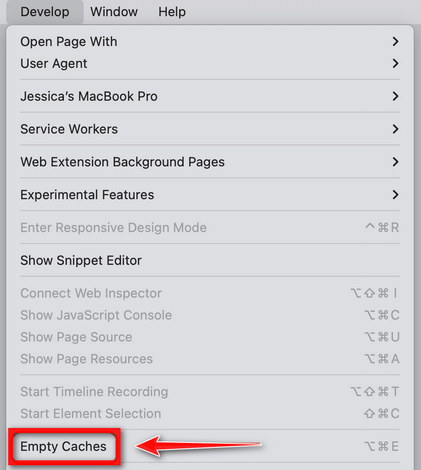
From the menu bar select Develop, then click on Empty Caches as seen in the image below.
Remove Malware and Spam Push Notifications from Chrome for Mac
To stop the spam notifications in Chrome, we’ll reset the browser to its default settings. This restores your homepage, tab settings, and saved form data, clears cookies and temporary data, and disables all extensions — undoing the changes the malware made. Your bookmarks will be preserved.
-
Click on the three dots at the top right and go to Settings.
Click on Chrome’s main menu button, represented by three dots at the top right corner. Now click on the menu option labeled Settings as shown by the arrow in the picture below, which will open the basic settings screen.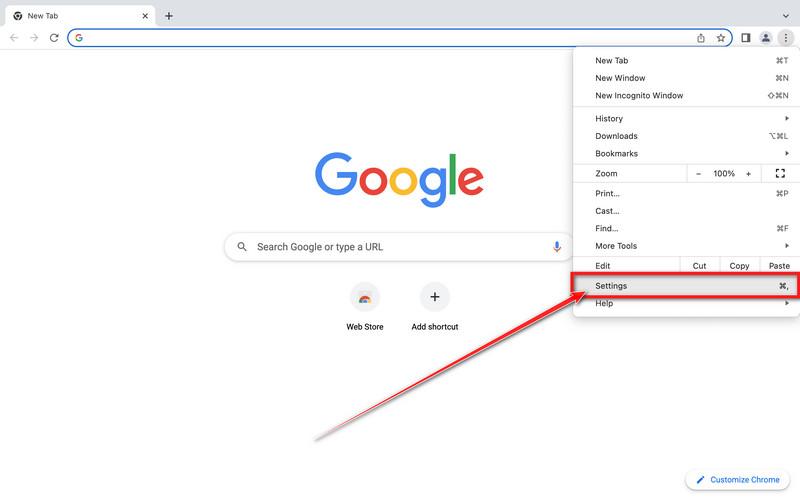
-
In the left sidebar, click on the “Reset and Cleanup” option.
In the left sidebar, click on “Reset and clean up“.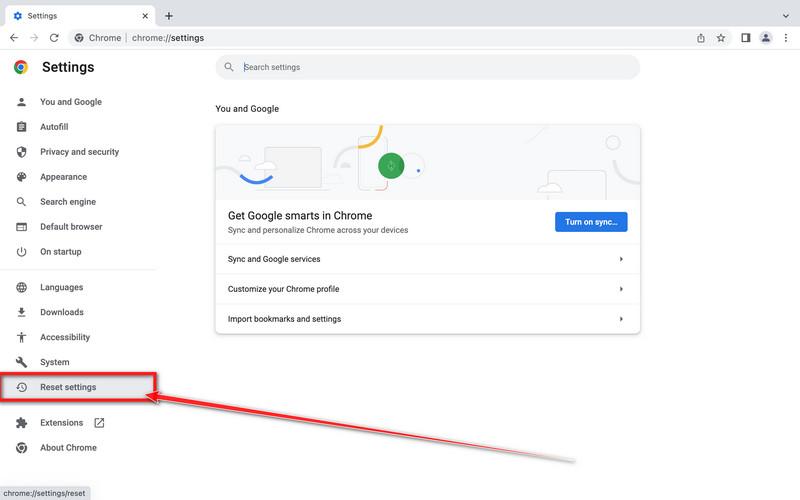
-
Click “Reset settings to their original defaults”.
Now click on the “Reset settings to their original defaults”. link as shown in the image below.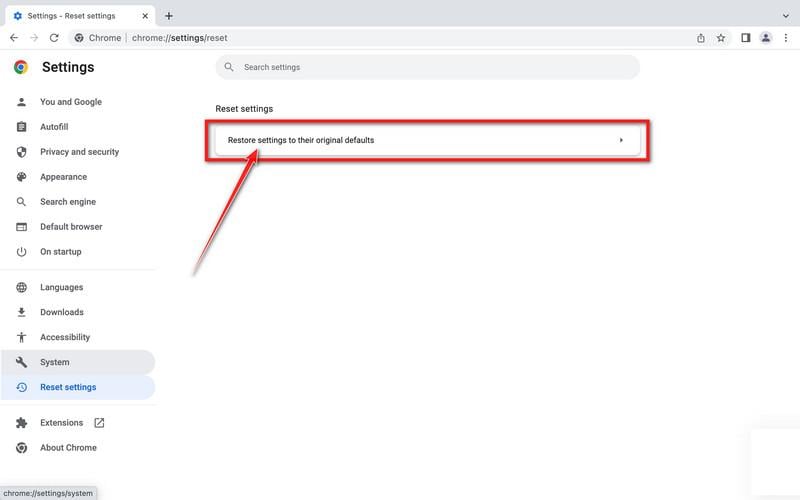
-
Click “Reset Settings” button.
A confirmation dialog should now be displayed, detailing the components that will be restored to their default state should you continue with the reset process. To complete the restoration process, click on the “Reset Settings” button.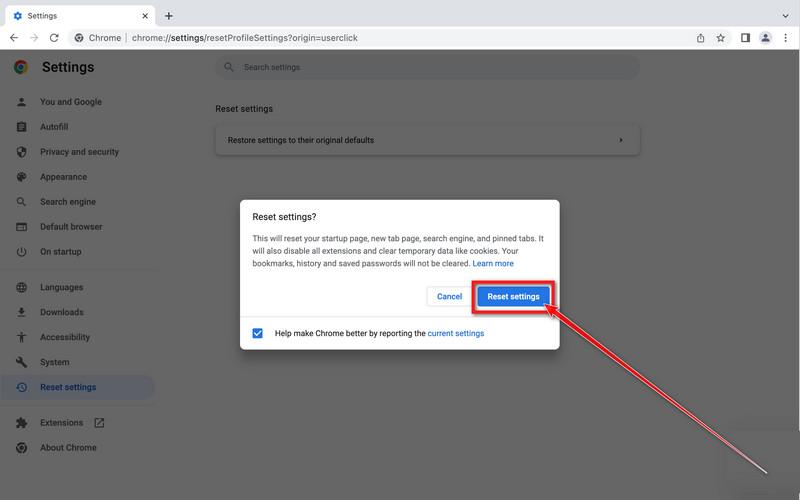
-
(Optional) Reset Chrome Data Sync.
In case a malicious extension reinstalls itself even after performing a browser reset, you have an additional option to reset the data sync for your browser. To do this, navigate to chrome.google.com/sync and click on the Clear Data button.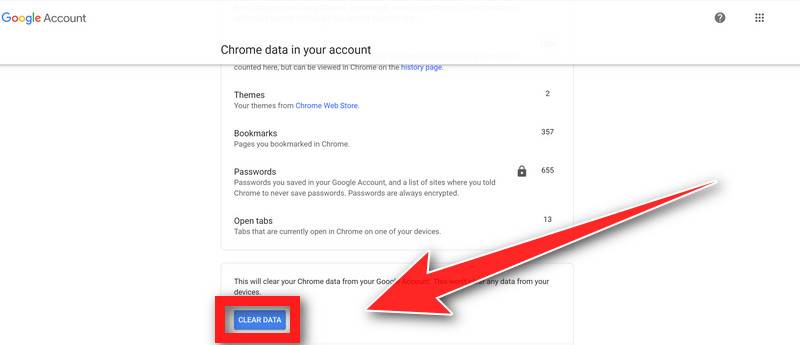
Remove Malware and Spam Push Notifications from Firefox for Mac
To stop the spam notifications in Firefox, we’ll use the built-in Refresh feature. It restores Firefox to its factory default state while keeping your essential data — bookmarks, passwords, web form auto-fill information, browsing history, and open tabs are all preserved.
-
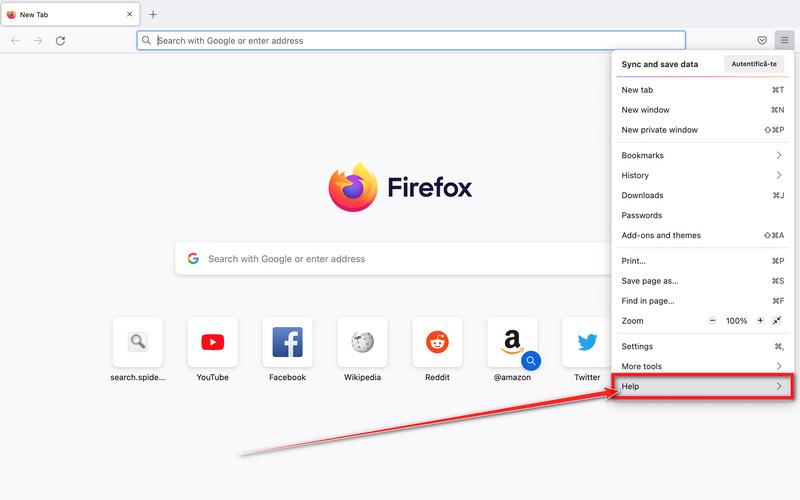
Go to the “Help” menu.
Click on Firefox’s main menu button, represented by three horizontal lines. When the drop-down menu appears, select the option labeled “Help“.
-
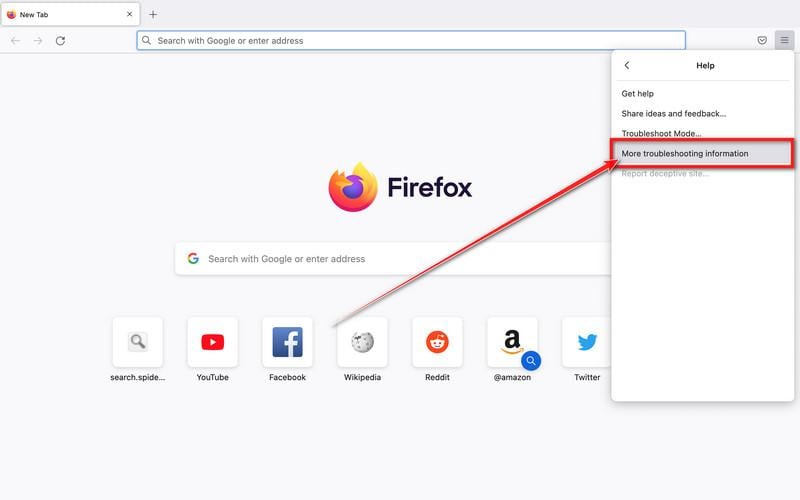
Click “Troubleshooting Information”.
Next click on the “Troubleshooting Information” option as indicated by the arrow in the image below. This will bring you to a Troubleshooting page.
-
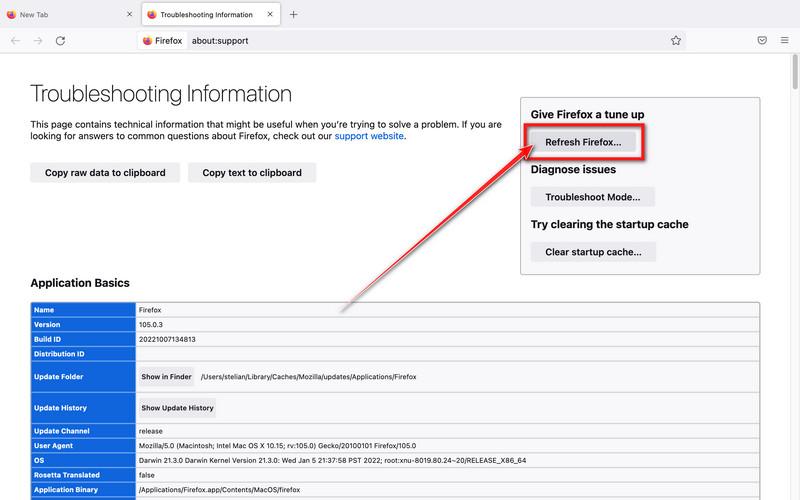
Click on “Refresh Firefox”
Click the “Refresh Firefox” button in the upper-right corner of the “Troubleshooting Information” page.
-
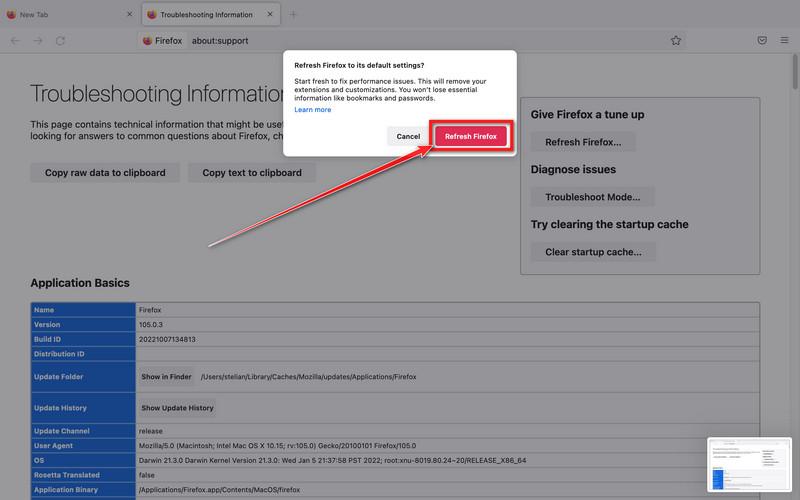
Confirm.
To continue, click on the “Refresh Firefox” button in the new confirmation window that opens.
-
Click on “Finish”.
Firefox will close itself and will revert to its default settings. When it’s done, a window will list the information that was imported. Click on the “Finish“.
STEP 2: Use Malwarebytes for Mac to remove malware and unwanted programs
Finally, we’ll download Malwarebytes for Mac and run a scan to find and remove browser hijackers, adware, malicious browser extensions, and any other malware on your Mac. If the scan comes back clean, your Mac is malware-free.
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
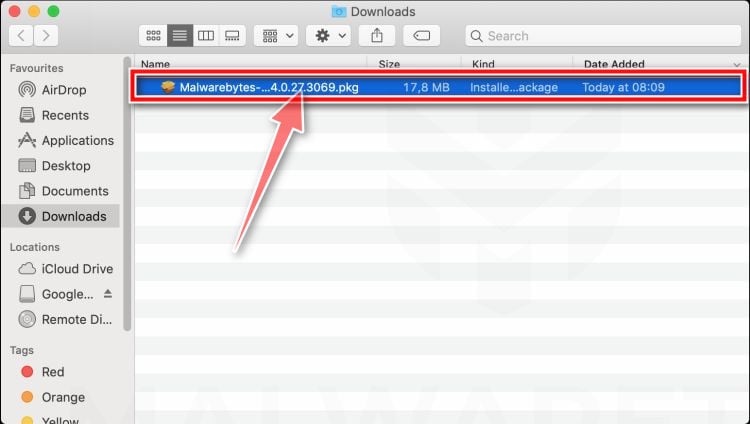
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.
-
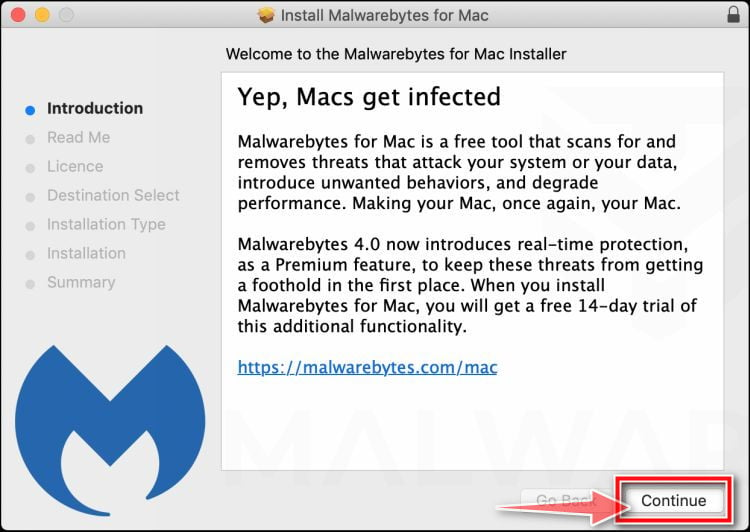
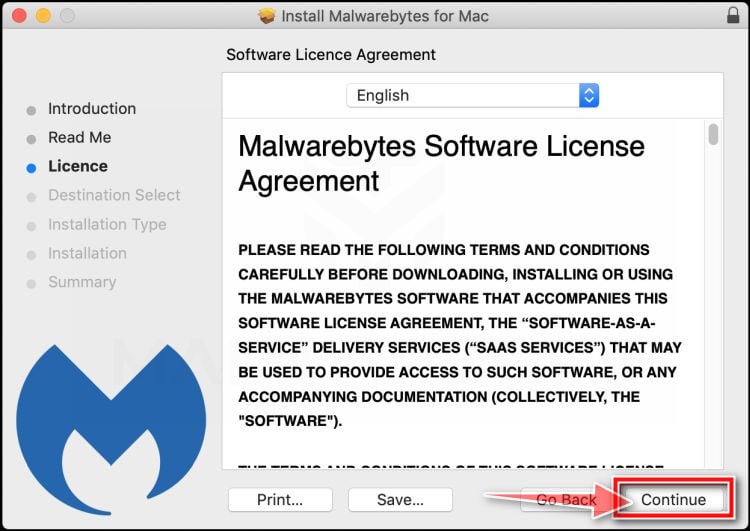
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.
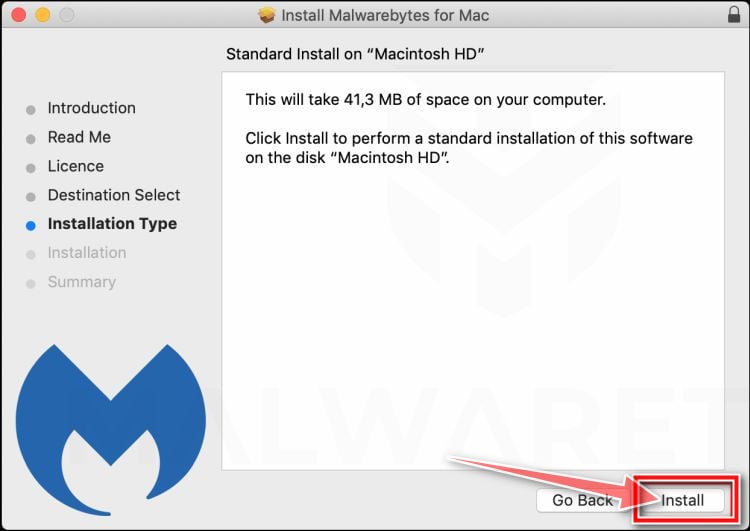
When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
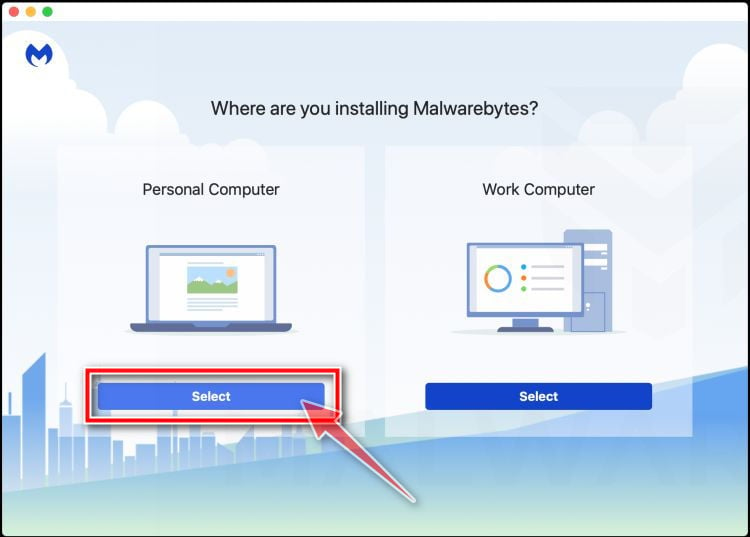
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.
-
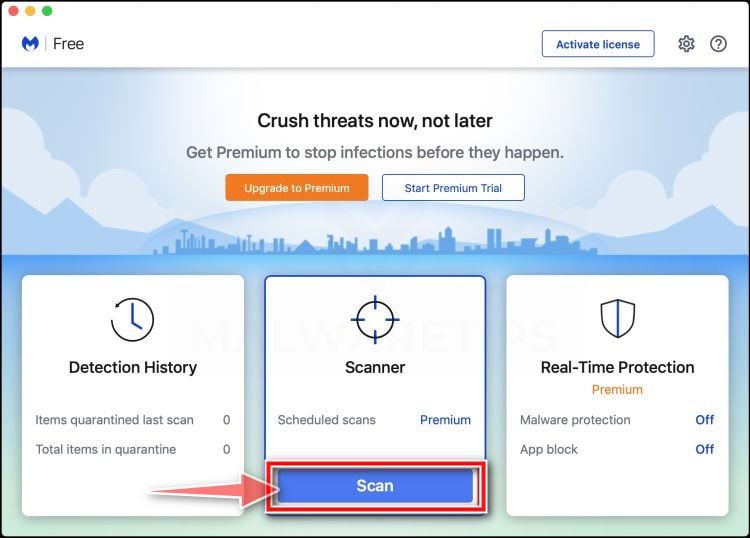
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.
-
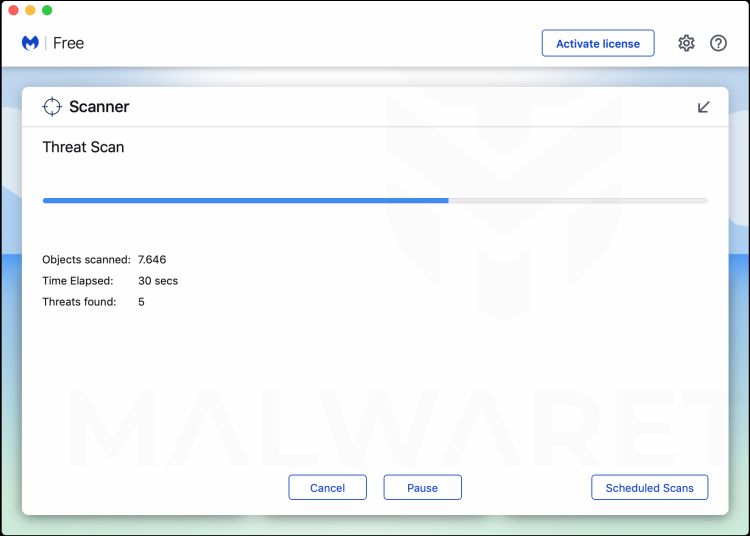
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.
-
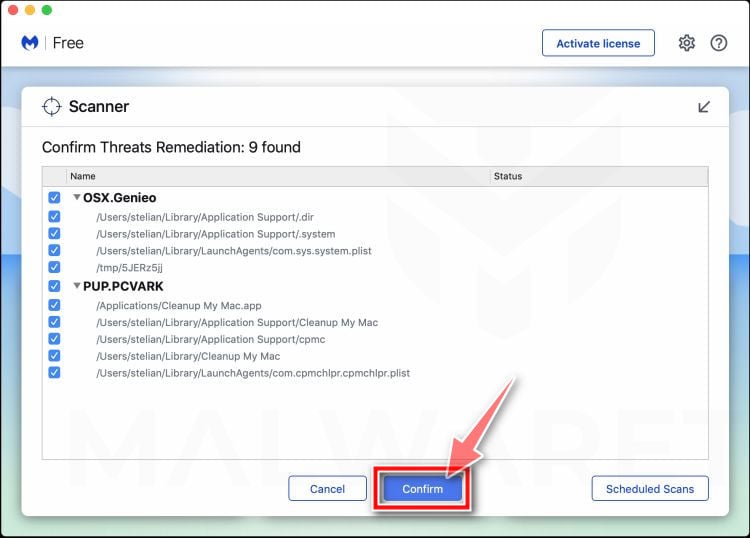
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.
-
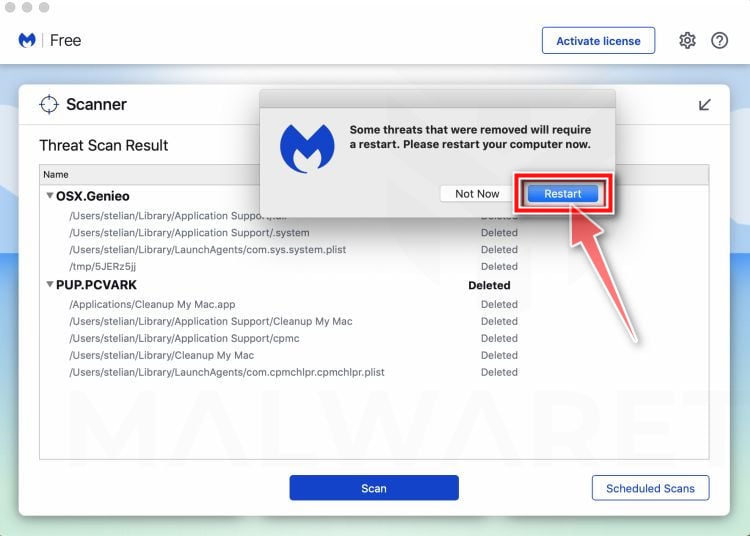
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.
Your Mac should now be free of the SorbusAucuparia extension and other malware.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
p>








