

If you received an email demanding Bitcoin payment to the address 1Loo6tksj4vV6k5PjxUArfaW8jVgvfazeA, do not panic.
This is not a private hacker watching you through your webcam. It is a fear-based crypto scam built to pressure people into sending money fast.
The email may claim your computer was hacked, your files were copied, your browsing history was stolen, and embarrassing videos will be sent to your contacts. The goal is simple: scare you so badly that you pay before thinking clearly.
The most important thing to know is this: this Bitcoin address has appeared in scam reports and sextortion-style blackmail campaigns. It is not proof that you were personally hacked. It is a red flag that you are looking at a recycled scam tactic.
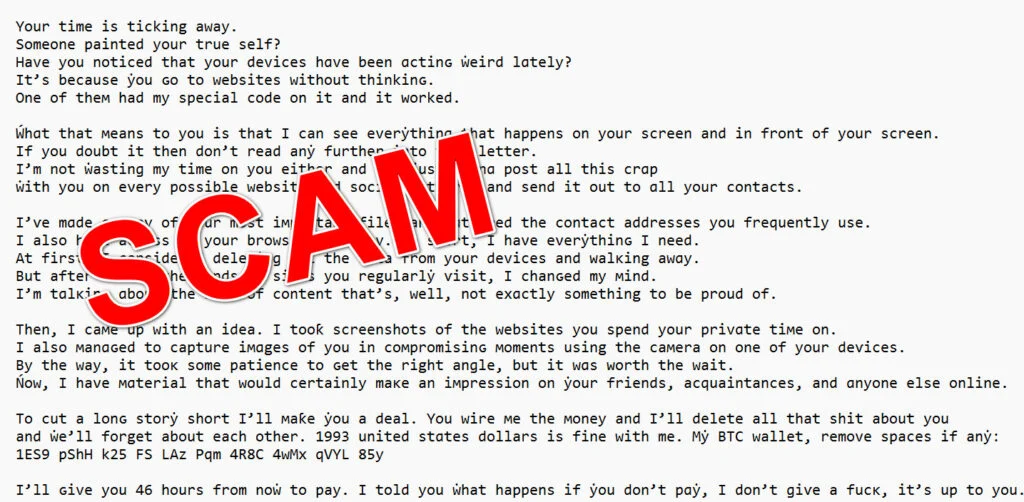
Scam Overview
What Is the 1Loo6tksj4vV6k5PjxUArfaW8jVgvfazeA Bitcoin Scam?
The 1Loo6tksj4vV6k5PjxUArfaW8jVgvfazeA Bitcoin scam is a crypto blackmail email.
The message usually says that a hacker has taken control of your device. It may claim they installed spyware, accessed your webcam, recorded your screen, copied your personal files, and collected your contacts.
Then comes the threat.
The scammer says they will release embarrassing material unless you send Bitcoin to the wallet address:
1Loo6tksj4vV6k5PjxUArfaW8jVgvfazeA
The demand may be $800, $1000, $2000, or another amount. The exact number changes from version to version. The pressure tactic stays the same.
You are told to pay quickly. You are told not to tell anyone. You are told the scammer has proof.
But in most cases, there is no proof.
There is only a threatening email.
This Address Is a Scam Red Flag
The Bitcoin address 1Loo6tksj4vV6k5PjxUArfaW8jVgvfazeA has been listed in public scam reports connected to sextortion and Bitcoin blackmail messages. Scam-report pages describe emails using this address to demand payment while threatening to leak private videos or personal material.
That matters.
A real targeted hacker would usually use a private payment address for a specific victim or campaign. But when the same crypto address appears across scam reports, it strongly suggests mass spam, recycled scripts, and copy-paste extortion.
In plain English: this address is not a sign that the sender knows you. It is a sign that the same wallet has been used in scam messages sent to other people too.
The Scam Is Built Around Fear
This email works because it hits people where they feel most vulnerable.
It talks about:
- Private browsing history
- Adult websites
- Webcam recordings
- Personal files
- Email contacts
- Social media exposure
- Reputation damage
- Family embarrassment
- Job loss
That is not random.
The scammer wants you to feel trapped. They want you to imagine the worst possible outcome. They want you to believe that paying is the fastest way to make the problem disappear.
But paying does not solve anything.
It only tells the scammer that you are scared enough to send money.
Why the Email Can Feel Convincing
Some versions of this scam include an old password. That can make the message feel personal.
But an old password does not mean your computer is hacked.
Passwords are often leaked in old data breaches. Scammers buy or collect lists of emails and passwords, then use them in blackmail templates. Seeing a password you recognize is scary, but it usually means the password came from an old breach, not from a live hack.
Other versions do not include a password at all. They simply make broad claims and hope fear does the rest.
Common claims include:
- “I installed malware on your device”
- “I recorded you through your webcam”
- “I copied your files”
- “I have your contacts”
- “I know what websites you visited”
- “I will send everything to your friends”
- “You have 24 to 48 hours to pay”
These claims are designed to sound specific while staying vague.
The scammer rarely names your device. They rarely provide real screenshots. They rarely show file names. They rarely list real contacts.
That lack of proof is the giveaway.
Why Scammers Demand Bitcoin
Bitcoin is popular in these scams because payments are difficult to reverse.
With a card or bank payment, a victim may be able to dispute the transaction. With Bitcoin, once the payment is sent and confirmed, recovery is much harder.
That is why the scammer wants crypto.
They do not want a payment method with customer support. They do not want a chargeback. They want fast money sent to a wallet address.
The FTC has warned about scam emails that demand Bitcoin and threaten blackmail. Its advice is simple: do not pay.
The Deadline Is Part of the Trap
Most versions of this scam give a short deadline.
It may say:
- You have 24 hours
- You have 48 hours
- You have 3 days
- Time is running out
- I will know when you read this
The countdown is not proof of anything. It is pressure.
The scammer does not want you to search the wallet address. They do not want you to ask a friend. They do not want you to contact your email provider. They do not want you to read scam reports.
They want you alone, embarrassed, and rushed.
That is why the best first move is to slow down.
How the Scam Works
1. Scammers Get Email Lists
The scam usually starts with a list of email addresses.
These lists can come from:
- Old data breaches
- Leaked account databases
- Spam lists
- Scraped websites
- Dark web marketplaces
- Previous phishing campaigns
The scammer does not need to know you personally.
They only need your email address. If they also have an old password, they may include it to make the message look more believable.
2. They Send a Mass Blackmail Email
Next, the scammer sends out thousands or millions of emails.
The message is written to sound personal, but it is usually a template.
It says the same general things to many people:
- Your device was hacked
- Your camera was accessed
- Your files were copied
- Your private activity was recorded
- Your contacts will receive the material
- You must pay in Bitcoin
This is a volume scam.
Most people ignore it. A few people panic. That is enough for the scammer.
Even if only a tiny percentage pays, the campaign can still make money.
3. They Use a Recycled Bitcoin Wallet
The address 1Loo6tksj4vV6k5PjxUArfaW8jVgvfazeA has appeared in public scam reports tied to Bitcoin blackmail and sextortion messages.
That is important because victims often believe the wallet address is unique to them.
It is not.
A reused wallet address is a strong sign of a broad scam campaign. The scammer is not carefully handling one private hacking case. They are pushing the same payment destination through threatening emails.
This is why searching the address can be helpful. If the same address appears on scam-report websites, the message is almost certainly part of a known scam pattern.
4. They Add Shame to Make You Stay Quiet
The scammer usually claims they recorded you visiting adult websites.
This is the emotional core of the scam.
The threat is not just “pay me money.” It is “pay me money or everyone will know something embarrassing about you.”
That shame is useful to the scammer.
It makes victims hesitate to talk to:
- Family
- Friends
- Coworkers
- IT support
- Law enforcement
- Their bank
- Their email provider
The scammer wants silence because silence keeps the fear alive.
Once you tell someone, the scam starts to fall apart.
5. They Use Fake Technical Language
These emails often include scary technical terms.
You may see words like:
- Spyware
- Malware
- Keylogger
- Trojan
- Remote access
- Screen recording
- Webcam capture
- Device control
- Backdoor
The terms sound serious, but the email usually provides no technical evidence.
A real infection would have details. A scam email usually has claims.
The scammer may say they installed “special software” or “malware,” but they do not name the file, the device, the exploit, the browser, or the time of infection.
That is because they probably do not know any of it.
They are bluffing.
6. They Push You Toward Bitcoin Fast
After building fear, the scammer gives instructions.
They may tell you to:
- Buy Bitcoin
- Install a crypto wallet
- Send funds to the provided address
- Remove spaces from the wallet address
- Pay before the deadline
- Avoid contacting anyone
This part is practical because the scammer wants action.
They do not want a conversation. They do not want questions. They want money.
Once the Bitcoin is sent, the victim has very limited options. That is why scammers prefer crypto payments for blackmail.
7. They Disappear or Ask for More
If a victim pays, the scammer may disappear.
But sometimes they come back.
They may say:
- The payment was too late
- The amount was wrong
- Another hacker wants money
- They need a second payment
- They will release the files unless more Bitcoin is sent
This is why paying is dangerous.
It does not guarantee peace. It can make you a better target.
The scammer now knows two things:
- Your email address is active.
- You are willing to pay under pressure.
That can invite more threats.
Red Flags in This Bitcoin Scam
Watch for these warning signs:
- The email demands payment in Bitcoin
- The message threatens to expose private videos
- The scammer gives a short deadline
- The email uses fear and shame
- It claims your webcam was hacked
- It says your contacts were copied
- It provides no real proof
- It includes a wallet address already found in scam reports
- It tells you not to contact anyone
- It uses vague technical language
- It may include an old password from a data breach
If you see these signs, treat the email as a scam.
What To Do If You Received This Email
1. Do Not Pay
Do not send Bitcoin to 1Loo6tksj4vV6k5PjxUArfaW8jVgvfazeA or any other wallet address in the email.
Paying does not protect you. It does not guarantee the scammer will stop. It may lead to more demands.
2. Do Not Reply
Do not argue with the scammer.
Do not ask for proof.
Do not threaten them.
Do not tell them you reported the email.
Any reply confirms that your inbox is active. That can make you a target for more scams.
3. Save Evidence
Before deleting the email, save useful evidence.
Keep:
- The full email
- The sender address
- The subject line
- The date and time
- The Bitcoin wallet address
- Any payment amount
- Any old password shown in the email
- Any attachments or links, without opening them
If you already paid, save the crypto transaction ID too.
4. Report the Scam
Report the email to your email provider as phishing or extortion.
You can also report cybercrime to the FBI’s Internet Crime Complaint Center through IC3. IC3 is the FBI’s main reporting intake for cyber-enabled fraud and scams.
If cryptocurrency was involved, IC3 also accepts cryptocurrency-related complaints.
5. Change Reused Passwords
If the scam email includes a password you recognize, change it immediately anywhere you used it.
Do not reuse passwords across accounts.
Use a strong, unique password for:
- Banking
- Social media
- Cloud storage
- Shopping accounts
- Crypto exchanges
- Work accounts
A password manager can make this much easier.
6. Turn On Two-Factor Authentication
Enable two-factor authentication on important accounts.
Start with your email account. If a criminal controls your email, they can reset passwords for other services.
Use an authenticator app when possible.
7. Scan Your Device
If you did not click anything in the email, your device is probably fine.
Still, it is reasonable to run a full scan with trusted security software for peace of mind.
If you clicked a link or opened an attachment, scanning is more important. Also check for unknown apps, browser extensions, or remote access tools.
8. Check Your Email Settings
Look for anything suspicious inside your email account.
Check:
- Forwarding rules
- Filters
- Recovery email
- Recovery phone
- Connected apps
- Recent login history
- Unknown devices
If anything looks wrong, remove it and change your password again.
9. Warn Others
If the email came to a work address, tell your IT team.
If it came to a personal address, warn family members or friends if needed. These scam campaigns often hit many people at once.
A quick warning can stop someone else from paying.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
What If You Already Paid?
If you already sent Bitcoin, stop communicating with the scammer immediately.
Do not send more money.
Then take these steps:
- Save the email and all messages.
- Save the Bitcoin wallet address.
- Save the transaction ID.
- Contact the crypto exchange or wallet service you used.
- File a report with IC3 or your local cybercrime authority.
- Change important passwords.
- Enable two-factor authentication.
- Watch your accounts closely for suspicious activity.
Be careful with “crypto recovery” services. Many are scams too. If someone online claims they can recover your Bitcoin for an upfront fee, treat that as another red flag.
FAQ
Is the 1Loo6tksj4vV6k5PjxUArfaW8jVgvfazeA email real?
The threat is usually fake. The wallet address has appeared in scam reports connected to Bitcoin blackmail emails, which strongly suggests a recycled scam campaign rather than a real personal hack.
Did the scammer really hack my webcam?
Probably not. These emails usually claim webcam access but provide no evidence. If there is no screenshot, no file name, no real contact list, and no proof, treat it as a bluff.
Why did they include my password?
If a password appears in the email, it most likely came from an old data breach. Change that password anywhere you used it.
Should I send Bitcoin?
No. The FTC advises people not to pay Bitcoin blackmail demands. Paying can make you a bigger target.
Can Bitcoin payments be reversed?
Usually no. Once a Bitcoin transaction is confirmed, it is very difficult to reverse. Contact the exchange or wallet service immediately if you already paid.
Should I delete the email?
Save evidence first. Then mark it as phishing or spam and block the sender.
The Bottom Line
The 1Loo6tksj4vV6k5PjxUArfaW8jVgvfazeA Bitcoin scam is a fear-based crypto blackmail scheme.
The email may sound personal, but the wallet address has appeared in scam reports and sextortion-style blackmail pages. That makes it look like part of a broader scam pattern, not a private hacker targeting only you.
Do not pay. Do not reply.
Save the evidence, report the email, change exposed passwords, enable two-factor authentication, and move on calmly.
The scammer’s biggest weapon is panic. Once you recognize the pattern, the threat loses most of its power.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.