

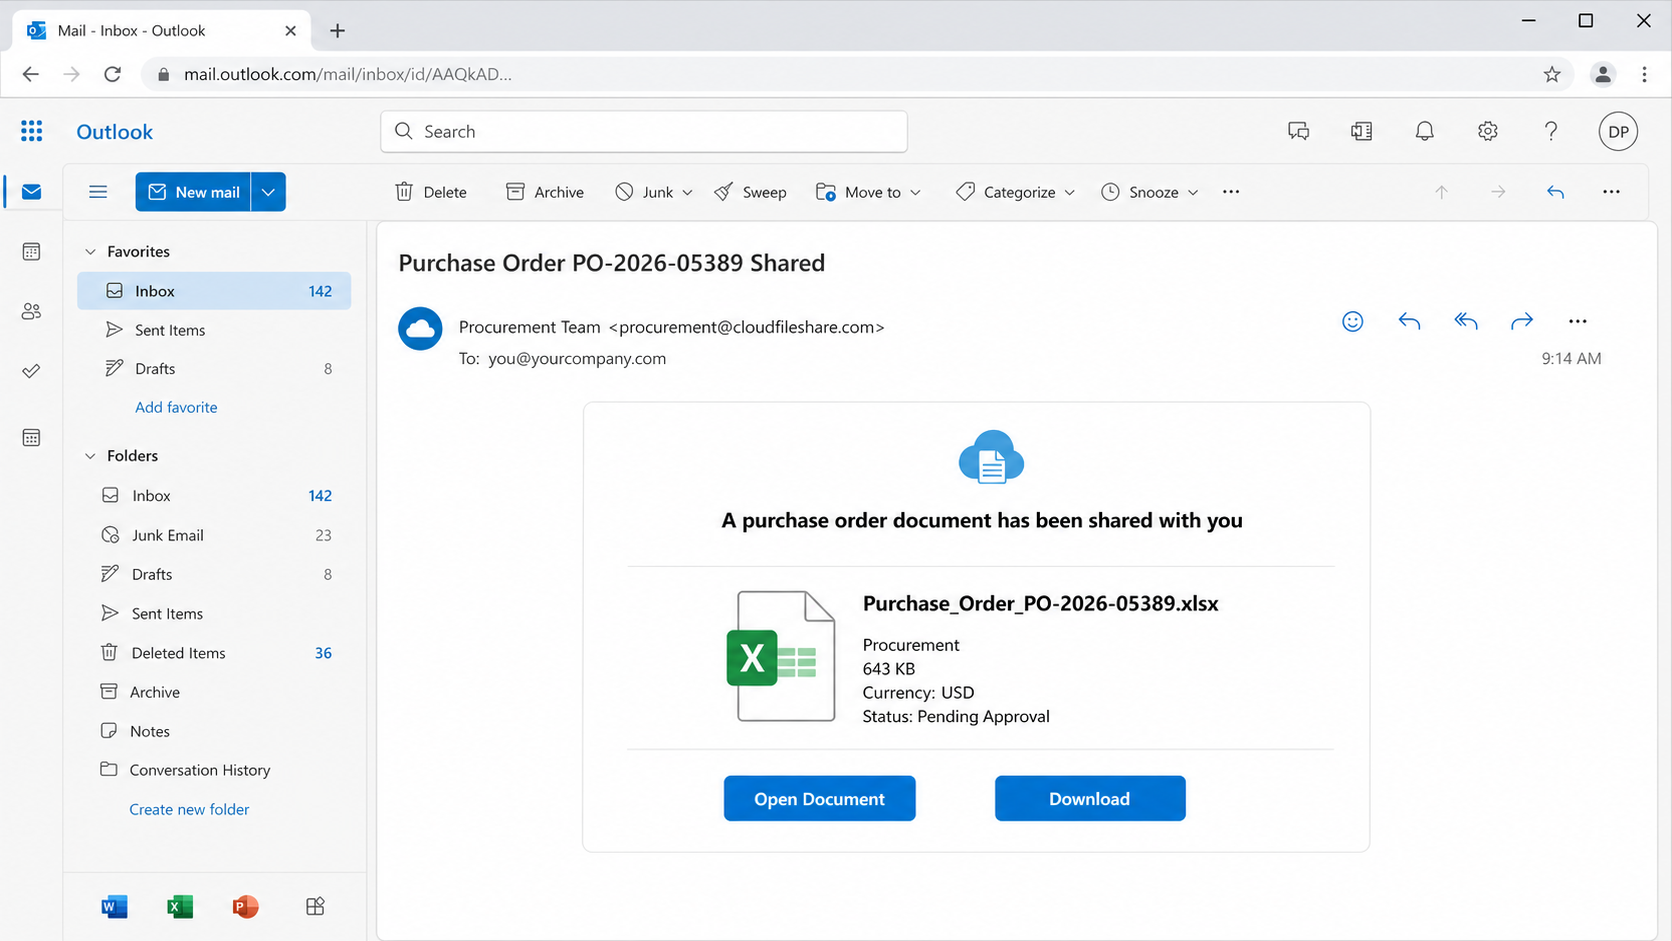
A new purchase order can look like good news. The email includes a PO number, spreadsheet filename, file size, currency, and a “Pending Approval” status, all the details a supplier expects to see.
The Dropbox Purchase Order email scam manufactures those details to lure recipients into a fake login. There is no confirmed order behind the notification, and the buttons are designed to expose credentials rather than deliver a spreadsheet.
Overview
This phishing message claims that a purchase order has been shared through Dropbox. An observed version referred to “PO-2026-05389,” named an XLSX file, showed a size of 643 KB, listed USD as the currency, and marked the document as pending approval.
Both “Open Document” and “Download” directed the recipient toward a phishing destination. The captured destination was no longer active when later reviewed, but the email’s design and workflow were intended to collect account credentials through a counterfeit login.
The PO number makes an invented order feel traceable
Real procurement systems assign references that combine years, departments, and sequential numbers. A plausible identifier can make the message feel as if it came from a process already underway.
A number printed in an email is not a record. It becomes meaningful only when it matches the recipient’s customer, quotation, ordering system, and verified contact.
The spreadsheet details imitate a supplier workflow
Purchase orders are often exchanged as PDFs or spreadsheets. Showing a file type, size, procurement label, vendor field, currency, date, and status creates the appearance of a complete document card.
Those fields are static email content. No file must exist for a scammer to display them, and clicking the card does not prove it came from Dropbox.
The target is the account used to conduct business
- Email or cloud-storage credentials entered on the fake page
- Supplier quotes, customer lists, and purchase histories
- Payment terms and bank details in existing conversations
- Contacts who trust messages from the compromised account
- Connected services accessible through password resets or single sign-on
Dropbox is not involved in the scam. The company’s name is used because suppliers recognize shared-file notices and may expect customers to use different document platforms.
Why Suppliers Are Attractive Targets
Unknown senders can be legitimate customers
Sales and order desks cannot reject every first-time contact. New buyers, distributors, and procurement teams often begin with an email and a document.
The scam exploits this necessary openness. An unfamiliar sender does not automatically end the conversation, so verification must focus on the company, domain, order history, and requested workflow.
A purchase order suggests revenue
The recipient may assume the selling work is complete and focus on fulfilling the order. That positive expectation can lower caution just as effectively as fear.
The campaign avoids promising an implausible prize. It offers a believable business opportunity whose value is hidden inside the document.
Every customer may use a different portal
Suppliers encounter many procurement systems, cloud drives, and vendor portals. A login page can therefore be unfamiliar without immediately looking fraudulent.
This variety makes independent confirmation essential. The buyer should be able to verify the platform and resend the invitation through an official corporate channel.
How the Dropbox Purchase Order Email Scam Works
Step 1: The campaign targets sales and supplier accounts
Addresses such as sales, orders, quotes, info, and accounts are often published publicly. Attackers may also use trade directories, professional networks, breached mailing lists, and vendor databases.
The message can be sent to thousands of organizations. Any recipient accustomed to purchase orders may find the theme relevant.
Step 2: A cloud-sharing notification is copied
The email presents itself as an automated Dropbox alert, using a clean document card and action buttons. The sender label may say procurement or file sharing while the actual address belongs elsewhere.
Official Dropbox mail comes from verified domains documented by Dropbox. The visible design cannot override a mismatched address.
Step 3: Specific order metadata creates credibility
A PO number, filename, file size, currency, date, and approval status are included. The recipient’s address may appear as the vendor, creating the impression that the system personalized the order.
Email addresses are easy to merge into bulk messages. Personalization shows that the attacker knows where the email was sent, not that a buyer created a record.
Step 4: Two action buttons increase the chance of a click
“Open Document” appeals to someone who wants a preview, while “Download” appeals to someone who plans to save the order. Both can resolve to the same phishing flow.
Providing a choice makes the card feel interactive. It does not create two genuine functions.
Step 5: The destination imitates a login portal
The page may copy Dropbox, Microsoft 365, Google Workspace, or the recipient’s webmail provider. Some phishing kits select a template after inspecting the supplied email address.
The original destination may later disappear. Criminals rotate domains, compromised sites, and cloud storage to keep the campaign running after reports and takedowns.
Step 6: The victim submits credentials to view the order
The fake page claims that authentication is required because access is restricted to authorized users. The recipient enters an email address and password expecting the spreadsheet to load.
The credentials are captured by the attacker. A blank screen, error, or redirect can be shown afterward to disguise the collection.
Step 7: The attacker enters the real account
The stolen password is tested against email, cloud storage, vendor portals, and other services. Password reuse can widen the compromise.
With mailbox access, the criminal can study genuine orders and learn which customers, products, quantities, and payment methods are normal.
Step 8: Real commercial relationships are abused
The attacker can send more fake orders from the compromised address, request sensitive documents, or change bank information in an active payment thread.
A supplier’s account may also be used to target customers. The trusted history between the businesses makes the next fraudulent message more persuasive.
Warning Signs in the Purchase Order Notification
- No earlier quotation, customer conversation, or account setup matches the PO.
- The buyer is not named clearly and no corporate domain is verified.
- The PO number exists only inside the email.
- The Vendor field merely repeats the recipient’s email address.
- The date is duplicated, malformed, or inconsistent with the order reference.
- The Open Document and Download buttons lead to the same unrelated host.
- The page asks for mailbox credentials instead of using a verified Dropbox login.
- The “security note” discourages sharing but offers no real administrator or support path.
Well-formed metadata is not evidence of a buyer. The most important question is whether the order exists in a verified relationship outside the email.
How to Verify a Purchase Order Safely
Match it to the sales history
Look for a quotation, customer account, product discussion, delivery address, or named buyer connected to the reference. A purchase order that follows no commercial conversation deserves careful review.
Ask the sales owner and accounts team whether they recognize the customer. Do not let a detailed filename substitute for a business record.
Find the buyer independently
Locate the company’s official website and call its published main number. Ask to be connected to procurement and verify the buyer, PO number, and shared-file platform.
Do not rely on a telephone number, reply address, or signature supplied only in the suspicious email.
Open Dropbox through its official domain
Type dropbox.com yourself or use the official application. Check shared items and notifications after signing in through the normal route.
Dropbox says it requests private login information only on its official login domain. Do not enter a Dropbox password, email password, or single sign-on credential elsewhere.
Validate the order before production or shipment
Confirm billing and shipping details, payment terms, product quantities, tax information, and authorized contacts. Fraudulent orders can also be used to obtain goods, even when no credential page is involved.
New or high-value customers may require credit checks, deposits, or documented approval under the supplier’s normal policy.
When the Phishing Site Is Already Offline
An inactive destination is good news for anyone who clicks later, but it does not make the original email harmless. The page may have collected credentials while it was active.
The same message can be relaunched with a new domain. Attackers often reuse email templates because changing a button link is cheap and fast.
Security teams should block the sender, URLs, attachment hashes, and recognizable subject patterns where appropriate. They should also search historical mail to identify people who interacted before takedown.
If a victim entered credentials while the site worked, the response remains the same after it goes offline: change the password, revoke sessions, inspect the account, and investigate related activity.
How Businesses Can Protect Procurement Workflows
Publish a clear process for receiving first-time orders. Sales staff should know which documents can be accepted, where they should be stored, and how new buyers are verified.
Use phishing-resistant multifactor authentication and disable legacy login methods. Protect shared mailboxes and general sales accounts with the same care as executive accounts.
Separate commercial approval from email access. A person who receives a PO should not be able to change payment or shipping controls without an independent check.
Train staff using realistic procurement lures. A generic lesson about fake prizes will not prepare a sales team for a clean spreadsheet card and a credible PO number.
Purchase Order Checks That Should Happen Before Any Login
Confirm the commercial sequence
A normal PO usually follows a quotation, product discussion, negotiated price, or customer-account setup. Search the CRM and shared sales inbox for that history before treating the document as an order.
An unsolicited PO is not always fraudulent, but the lack of prior context should trigger verification with the buyer rather than immediate portal access.
Compare the buyer’s domain and legal details
Check whether the sender’s domain belongs to the company named in the order. Look for the legal business name, billing address, delivery address, tax details, and a buyer who can be reached through the official switchboard.
Lookalike domains may change one letter, add a hyphen, or place a company name before an unrelated ending. Read the complete domain carefully.
Separate document access from order acceptance
Even a genuine shared document should not automatically authorize production, credit, or shipment. Apply the company’s normal approval and fraud controls after the file is verified.
This separation limits the damage if a real customer account has been compromised. A valid Dropbox share can still contain fraudulent instructions when the sender’s account is under attacker control.
What to Do if You Have Fallen Victim to This Scam
- Leave the fake portal. Do not submit a second password or approve an unexpected verification request.
- Change the exposed password. Reach the official account website from a trusted device and choose a new password that is not reused.
- Revoke active access. Sign out sessions and remove unknown devices, app passwords, connected apps, delegates, and recovery methods.
- Check mailbox and cloud settings. Review forwarding, rules, shared links, recent downloads, file permissions, and deleted activity.
- Tell IT, sales, and finance. Provide the PO reference, sender, time clicked, data entered, and any files downloaded.
- Contact the represented buyer independently. Confirm whether any real order exists and warn the company that its name may be misused.
- Pause related fulfillment. Do not ship goods, extend credit, or process a payment until the customer and order are verified.
- Review recent business messages. Look for new bank instructions, unusual quote requests, shared documents, or messages sent from the account.
- Replace reused credentials. Prioritize email, Dropbox, Microsoft 365, Google Workspace, CRM, accounting, and vendor portals.
- Warn business contacts if necessary. Use a separate trusted channel and explain how genuine requests will be verified.
- Run a trusted scan. Malwarebytes can check for information stealers or remote-access software if the page downloaded or launched anything.
- Report and block the campaign. Forward suspicious Dropbox-themed mail to the platform and your security team. Use AdGuard to reduce exposure when later campaign links reach domains on established blocklists.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is PO-2026-05389 a real purchase order?
The number in the email does not prove a real order exists. Confirm it with the buyer through independently sourced company contact details.
Why did the email include my address as the vendor?
Bulk phishing systems can insert each recipient’s address into the message. This simple personalization is not proof of a customer record.
Does Dropbox send purchase order notifications?
Dropbox can notify users about shared files, but the file owner and notification must be verified. Open Dropbox independently and check the service’s official domains.
What if the link is now offline?
Do not assume earlier visits were safe. If you entered credentials while it was active, secure the account and report the incident.
Am I safe if I downloaded nothing?
If you entered a password, the account is still at risk even without a download. Credential phishing does not require malware installation.
Should I fulfill the order if the customer later contacts me?
Only after the company, buyer, order, payment terms, and shipping details are verified through normal business controls. Treat new contact from the same email cautiously.
The Bottom Line
The Dropbox Purchase Order email scam turns realistic procurement metadata into a path toward a counterfeit login. A PO number, spreadsheet icon, and pending status are easy to fabricate and cannot establish a buyer.
Verify new orders through independent company channels and open shared files from the official platform. If you entered credentials, secure the account and pause related orders before the compromise spreads into payment or shipment fraud.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.