


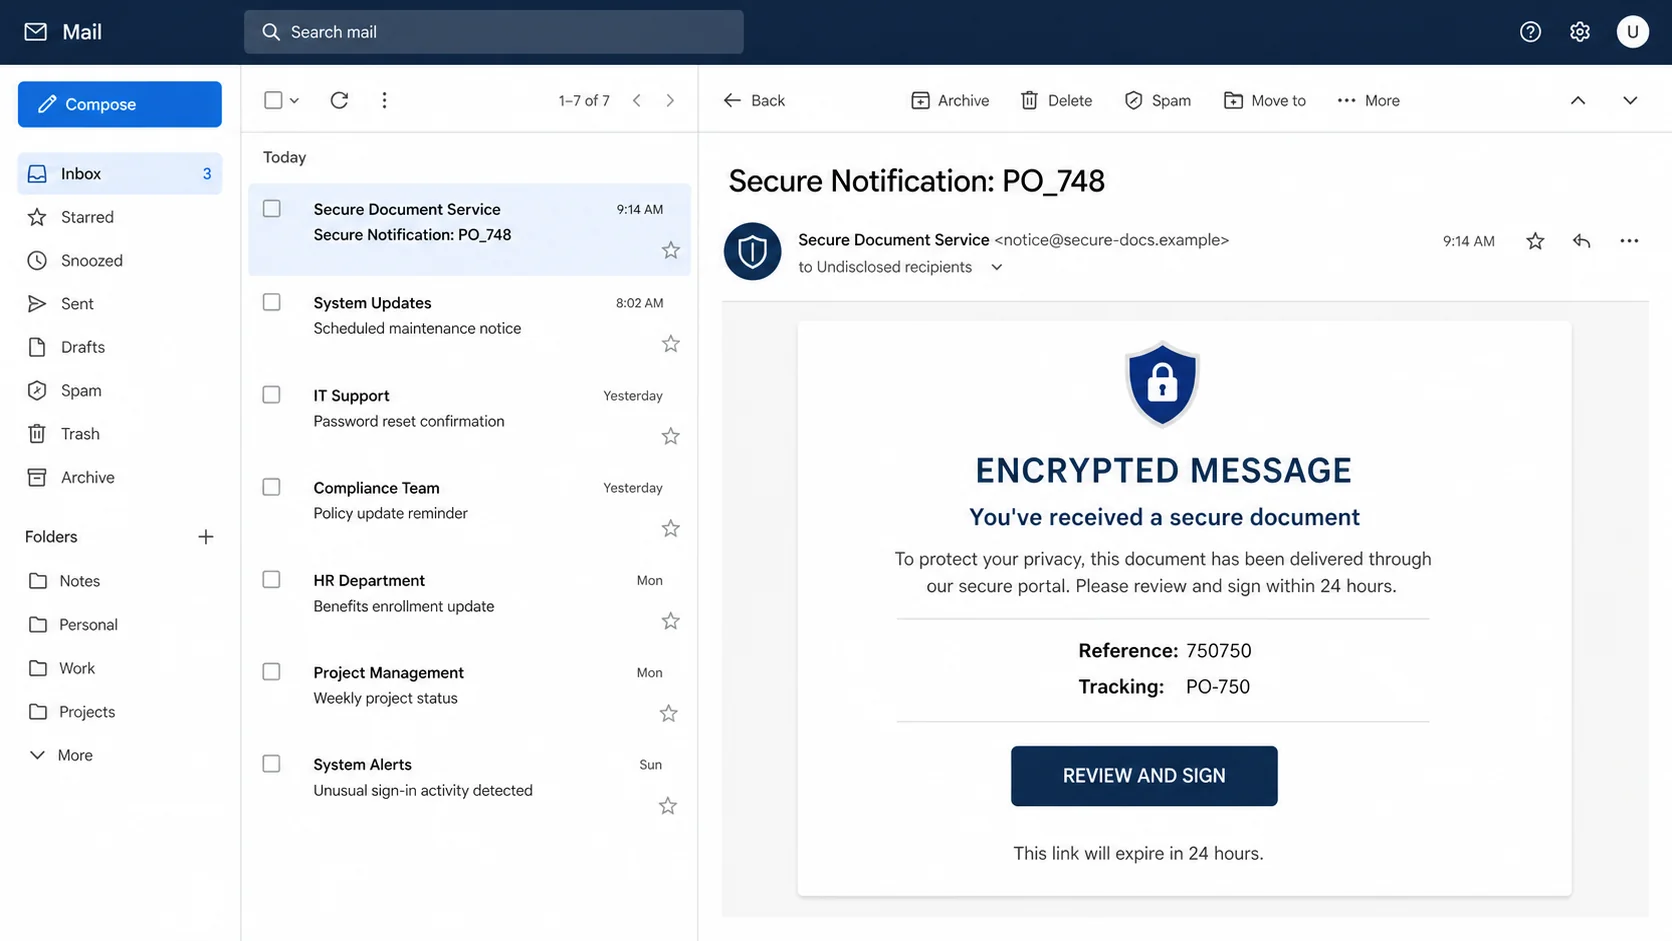
A polished notification says you have received a secure document that must be reviewed and signed. It includes a reference number, tracking code, and a 24-hour expiration warning.
The message looks like a routine electronic-signature request, especially to someone who handles contracts, approvals, or purchase orders.
The You’ve Received a Secure Document email scam is not delivering a protected file. Its “Review and Sign” button is designed to lead to a fake portal that steals login credentials.
Overview
The notification imitates a normal signing workflow
The email announces an encrypted message and says a document was delivered through a secure portal. It asks the recipient to review and sign, then displays a sender field, reference number, and tracking code.
Electronic signatures are part of everyday business, housing, insurance, healthcare, and financial transactions. People are accustomed to opening a portal, authenticating, and approving a file, so the request does not seem unusual by itself.
The scam copies that workflow while withholding meaningful context. The purported sender may be generic or unfamiliar, and the message does not identify the document title, organization, transaction, or reason for the signature.
A 24-hour expiration discourages independent confirmation
The link allegedly expires within one day. This creates a plausible deadline because real sharing services do sometimes limit access, but it also pressures the recipient to act before contacting the sender.
The countdown is often just text. It does not prove a file exists, and the phishing page may continue working after the stated deadline.
A legitimate urgent document can still be verified. The sender should be able to confirm the request through an existing conversation, phone number, or known business system.
The destination collects an account login, not a signature
The button can open a page resembling webmail, cloud storage, or an e-signature service. Instead of displaying a document, it asks the victim to enter an email address and password.
The collected information may expose:
- Email conversations and attachments
- Cloud files and shared business records
- Password resets for connected accounts
- Contact lists and trusted correspondence
- Invoices, contracts, and payment instructions
- A credible identity for sending new document lures
Generic terms such as “Secure Document Service” do not name a real platform. Familiar shield and padlock graphics can be created by anyone.
How This Campaign Differs From a Malicious Attachment
The observed lure directs recipients to a website
This version centers on a “Review and Sign” link. The expected danger is credential phishing through a remote portal, not a PDF or Office file attached directly to the email.
That distinction matters for recovery. Entering a password requires account containment, while opening a malicious file may also require device isolation and malware investigation.
The absence of an attachment does not make it safe
People often associate email danger with executable files and macros. A simple link can be just as damaging when it captures the credentials controlling an inbox or cloud account.
The page may also offer a download after the login stage, so recipients should not assume the campaign has only one risk.
The generic portal is not a known signing provider
A genuine notification normally identifies the service and sender clearly. The recipient can visit that service independently or check an existing account for pending documents.
This lure relies on generic security language. It wants the reader to supply the name of whatever signing platform they already recognize.
How the You’ve Received a Secure Document Email Scam Works
Step 1: The email lands among ordinary business notifications
Attackers send the campaign broadly or target addresses belonging to employees likely to approve documents. Roles in finance, legal, human resources, sales, procurement, and management receive many legitimate external requests.
A personal recipient may interpret the file as a lease, insurance form, employment agreement, tax notice, or medical authorization.
Step 2: The subject promises a protected document
Words such as secure, encrypted, private, and notification make the email sound procedural rather than promotional. A PO-style subject or reference number adds the appearance of an established transaction.
The subject does not have to reveal much. Its job is to make the recipient open the message and inspect the details.
Step 3: Reference codes simulate an audit trail
The email lists a sender, reference, and tracking code. These fields resemble the metadata used by real document systems, but the values may be generated randomly.
A useful reference should match an existing contract, purchase order, case, or conversation. A number with no recognizable source is decoration, not verification.
Step 4: The expiration warning creates a decision deadline
The recipient is told that access ends in 24 hours. Waiting to contact a colleague now feels risky because the supposed approval window may close.
Urgency also encourages mobile clicks, where the full destination domain is harder to inspect and the recipient may be away from normal business records.
Step 5: The button opens a copied secure portal
The destination can imitate a webmail login, shared-file page, or signature service. It may display the targeted address and a logo selected from the email domain.
The page is controlled by criminals even if it has HTTPS. The certificate encrypts the connection to the phishing site but does not validate the business claim.
Step 6: Authentication data is captured in real time
The fake form collects the address and password. Some kits immediately relay those credentials to the genuine provider and ask for the one-time code generated by MFA.
This real-time relay can defeat weaker forms of MFA if the victim supplies the code. Phishing-resistant passkeys and hardware security keys offer stronger protection because they are bound to the legitimate domain.
Step 7: The victim sees an error, blank page, or harmless redirect
Once the credentials are recorded, the site may claim the document expired, display a loading failure, or redirect to the provider’s real homepage.
The recipient may ask the supposed sender for a new link instead of realizing that the login itself was the objective.
Step 8: Stolen access powers a more convincing second attack
Criminals can read real document threads and send new requests from the compromised mailbox. They may replace payment instructions, request confidential files, or target executives and suppliers.
Because the follow-up arrives within an authentic conversation, it can be far more persuasive than the original generic email.
How to Verify a Review-and-Sign Request
Consider whether you expected the document and recognize the sender. Search existing conversations for the transaction, but do not reply through the unexpected notification if the sender identity is uncertain.
Contact the person through a known email thread, saved phone number, or internal messaging system. Ask for the document title, platform, and reference before opening anything.
If the email names a real signing provider, type that provider’s official address manually and check the account for pending items. Do not search for the service through sponsored results when handling a sensitive request.
Inspect the link destination without opening it when possible. The domain must belong to the stated service or an established organizational login system. A familiar logo on an unrelated host is not enough.
Warning Signs in the Secure Document Message
- The sender is generic, missing, or unrelated to any expected transaction.
- No document title, organization, or meaningful reason for signature is given.
- Reference and tracking numbers do not match known records.
- A 24-hour deadline is used to hurry the recipient.
- The button leads away from the claimed service or company.
- The portal requests a mailbox password before showing any useful context.
- The page accepts any address or changes branding automatically.
- The document fails to appear after credentials are submitted.
Why Business Accounts Are Especially Valuable
A work mailbox contains relationships, not just data. It reveals who approves payments, which vendors are active, how executives write, and when projects are expected to close.
Attackers can use that knowledge for business email compromise. A fake invoice or banking change sent at the right point in a real conversation may avoid the obvious warning signs of mass phishing.
Organizations should require independent verification for payment changes, use phishing-resistant MFA for high-risk roles, and monitor mailbox forwarding rules. A fast internal reporting channel also helps security teams block a campaign before more employees respond.
Electronic Signature Requests Need Context
A legitimate signing notice is usually the final step in a conversation, not the first time a recipient hears about a document. There should be a known sender, transaction, property, policy, employment process, or agreement behind it.
Unexpected requests are not automatically fraudulent, but they deserve verification. A short call to the sender can establish the document title, platform, deadline, and reason for signature without exposing account credentials.
Recipients should be especially cautious when the email uses a generic service name and hides the document until after a mailbox login. A signing provider does not normally need the user’s unrelated email password to display basic invitation details.
What Organizations Can Do to Reduce the Risk
Companies can publish which signing platforms they use and show employees examples of normal notification domains. Unexpected platforms can then be escalated instead of treated as routine.
Payment and contract approvals should require a second verification channel. Security teams can monitor impossible travel, new inbox forwarding, mass downloads, and unusual OAuth grants after a suspected credential theft.
Phishing-resistant authentication offers additional protection. Passkeys and security keys verify the legitimate domain, making them harder to relay through a counterfeit portal than typed one-time codes.
Training should focus on the complete decision, not just grammar. Modern phishing can be polished. The sender relationship, expected transaction, exact domain, and independent confirmation remain stronger signals.
Teams should practice reporting suspicious signing requests without punishing cautious employees. A quick question that delays one legitimate signature is far less costly than an unnoticed account takeover.
What to Do if You Have Fallen Victim to This Scam
- Stop using the link. Close the portal and reach the actual mail, cloud, or signing service through a trusted bookmark, known app, or manually typed address.
- Change the exposed password immediately. Use a unique replacement. Update reused credentials on every other service, especially financial, cloud, and recovery accounts.
- Revoke sessions and connected access. Remove unknown devices, OAuth applications, delegates, and app passwords. Confirm that recovery phone numbers and addresses remain yours.
- Review mailbox activity. Inspect forwarding rules, filters, sent messages, deleted items, and login history. Look for security alerts that an attacker may have hidden.
- Secure MFA. Deny unexpected prompts, replace backup codes, and use a passkey or security key where available. Never relay a one-time code to a page reached from an unsolicited email.
- Notify the organization quickly. Security teams can revoke tokens, block domains, preserve logs, identify other recipients, and examine whether files or conversations were accessed.
- Verify pending payments and document requests. Contact vendors, clients, or colleagues through known channels. Pause changes to banking details until they are independently confirmed.
- Scan downloaded content. If the portal supplied a file, extension, or program, Malwarebytes can check the device for malicious software. Do not reopen the file to identify it.
- Use an additional web-filtering layer. AdGuard can block many known phishing sites and malicious redirects, but new domains still require careful inspection.
- Preserve evidence and report harm. Save the original email, headers, URL, screenshots, login alerts, and transaction records. Report the incident to the provider, FTC, and IC3 as appropriate.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is this the same as a malicious PDF attachment?
No. This campaign uses a link to a fake portal and primarily targets credentials. A different secure-document scam may attach malware, so evaluate the exact message and actions taken.
Can a real signing request expire after 24 hours?
Yes, legitimate services can set expiration periods. The deadline does not authenticate the email. Confirm the sender and access the service independently.
Why was my email address already filled into the portal?
The phishing URL can carry the address as a parameter. Prefilling makes the page look personalized but does not show that it belongs to the real provider.
What if I clicked but never selected Review and Sign?
Opening the message alone is usually lower risk. If you visited the site, check for downloads, notification permissions, and auto-filled data. Replace the credential if the browser could have sent it.
Can MFA completely stop this scam?
MFA greatly reduces risk, but criminals may request codes or approvals in real time. Passkeys and hardware security keys provide stronger phishing resistance than relayed codes.
Should I contact the person named as the sender?
Yes, through a channel you already trust. Do not use phone numbers, reply addresses, or contact links supplied only by the suspicious notification.
The Bottom Line
The You’ve Received a Secure Document email scam recreates a familiar review-and-sign workflow, adds reference codes, and imposes a 24-hour deadline. The document is bait for a fake login portal.
Confirm unexpected files with the sender and open document services independently. If credentials were submitted, contain the account quickly before criminals use real conversations to launch a more damaging second attack.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.