

A file marked for review can resemble the countless agreements and approvals that move through a business inbox every week.
The notification feels ordinary, yet its generic document and carefully personalized login deserve a slower look.
Overview
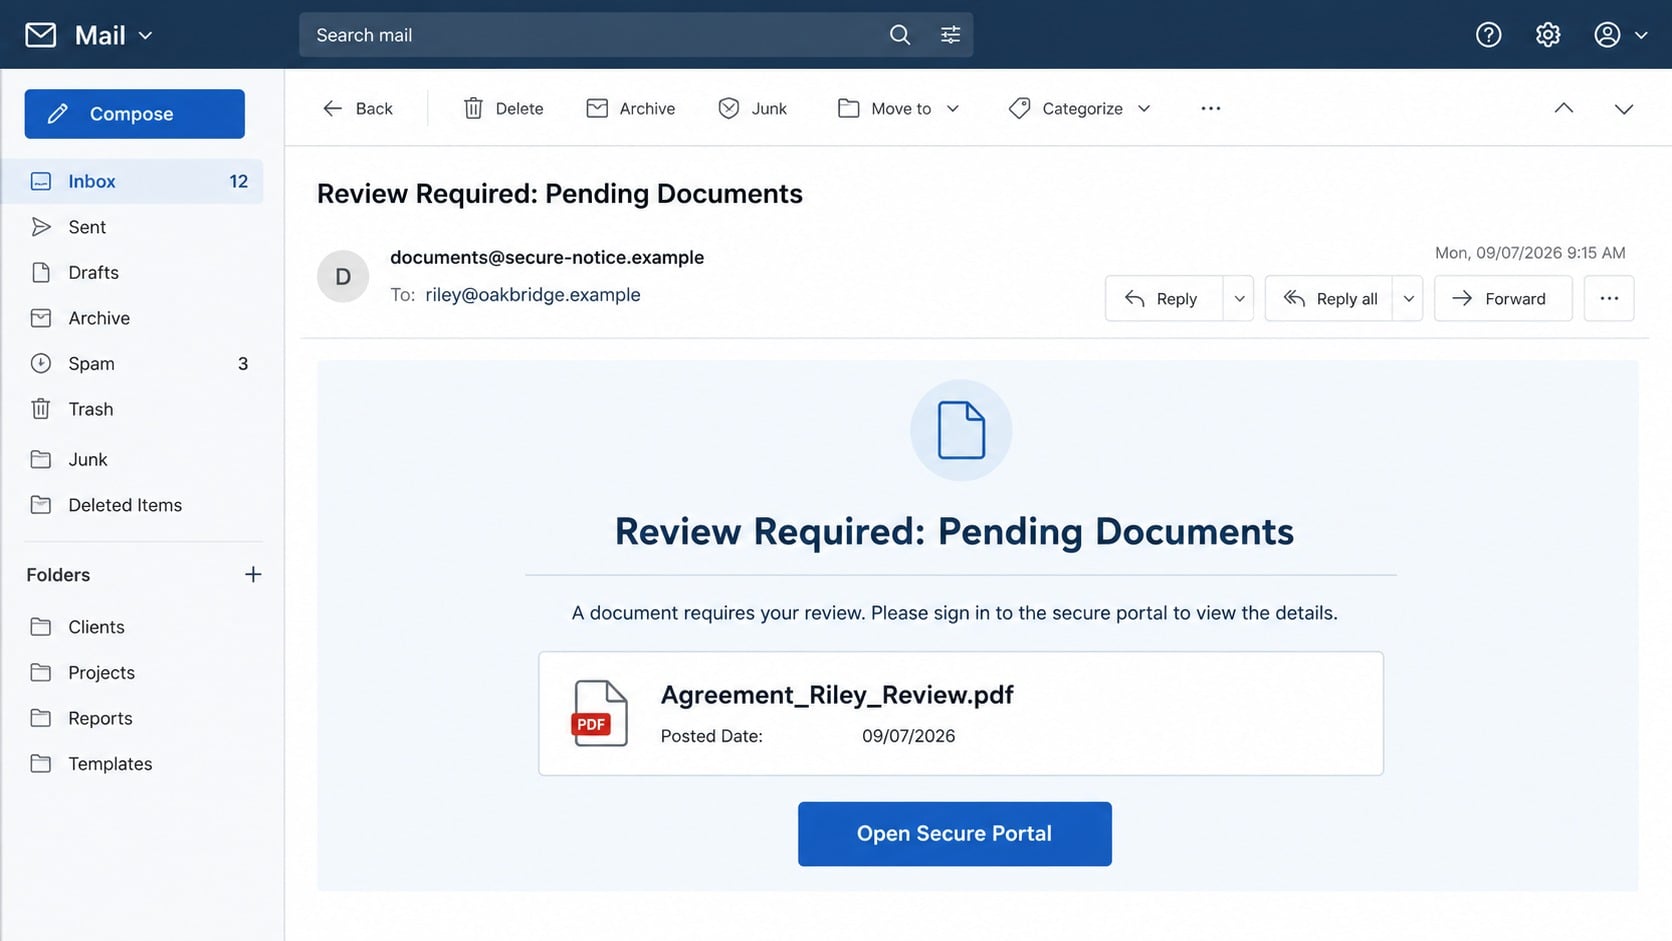
The message announces a document waiting for review
The email uses a subject similar to “New document for your review” followed by a date and identifying text.
Inside, a heading says “Review Required: Pending Documents” and names a PDF resembling Agreement_[name]_Review.pdf.
An “Open Secure Portal” button invites the recipient to view or approve the file.
- The sender supplies a generic agreement title but little information about the parties, project, or reason for review.
- The filename may include the recipient’s name, making a mass-produced message appear personally assigned.
- The linked page can adapt its appearance to the victim’s email provider.
- Credentials entered on that page are delivered to the phishing operator, not the real provider.
The login page uses information already inside the link
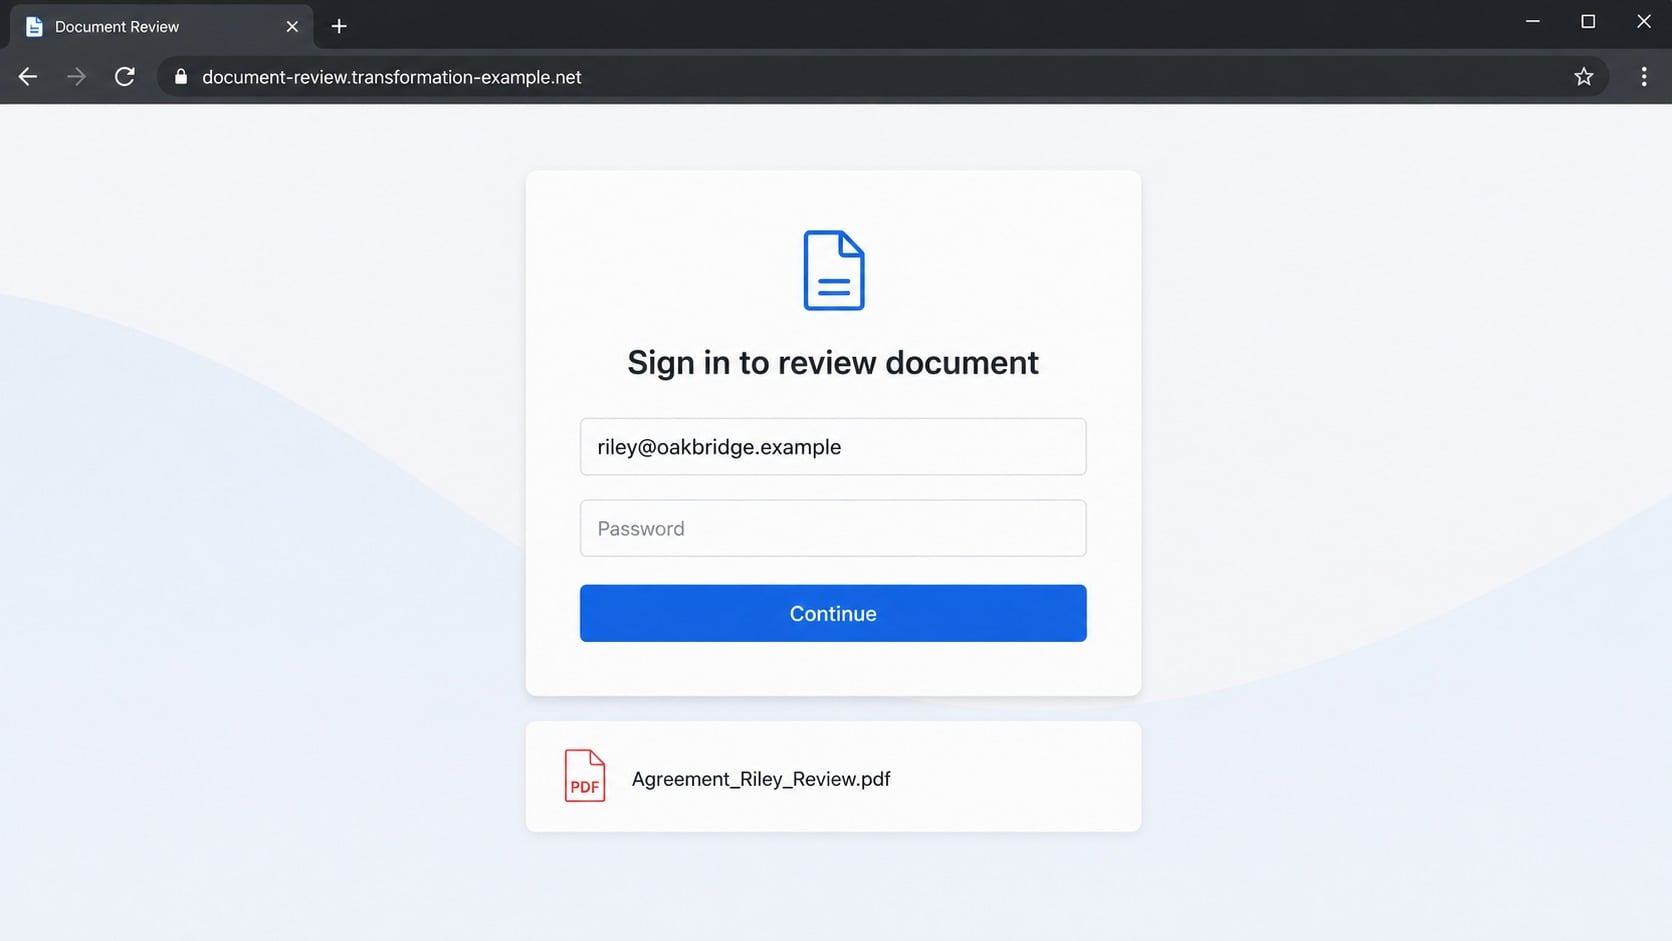
One observed campaign led to a domain unrelated to the recipient’s mail service and passed the email address as a parameter.
The counterfeit portal could then show a matching address or provider style before the victim typed anything.
That visual match is scripted personalization, not proof that a secure document was shared.
New variants can keep the same credential trap
Campaigns may replace the title with “Pending Document,” “ACTION REQUIRED,” or “Review Document” while preserving the same basic path.
Filenames, dates, hosting domains, logos, and button text can change quickly.
The durable warning is an unexpected document that requires sign-in through a destination outside the known workplace system.
How Adaptive Document Phishing Builds Trust
Traditional phishing often copies one brand for every recipient.
Adaptive pages take a more flexible approach by changing their appearance based on data carried in the link.
An email address reveals both a username and a domain.
A phishing script can read that domain and select a logo, color scheme, or login wording associated with the expected provider.
The page may also display the victim’s address as if an account lookup already occurred.
No private access is required to do this.
The attacker placed the information in the URL or collected it from a mailing list before sending the message.
This explains why a fake portal can feel unusually specific even when the document itself is vague.
The agreement filename plays a similar role.
Adding a name to a template requires little effort but makes the notification seem generated by a real document workflow.
Dates provide freshness and can reduce the chance that a recipient searches older mail for context.
A secure-sounding button is another psychological cue.
Words such as “portal,” “protected,” “encrypted,” and “authorized” describe an experience but do not verify who operates the destination.
Security must be established through the domain, established sharing platform, sender relationship, and independently confirmed document request.
If the organization uses Microsoft 365, Google Workspace, DocuSign, Dropbox, or another service, employees should know its expected notification pattern.
An unknown imitation should not receive credentials simply because it resembles one of them.
How the Pending Documents Email Scam Works
Step 1: A generic agreement is assigned to the recipient
The message claims a new document, agreement, contract, proposal, or approval is waiting.
It may include the recipient’s name and current date while omitting the sender’s genuine business context.
That balance is intentional.
Personal details attract trust, while vague transaction details avoid easy contradiction.
Step 2: Urgency is framed as workflow responsibility
The email says review is required, action is pending, or a signature remains incomplete.
Instead of threatening punishment directly, it suggests the recipient is delaying a shared process.
Employees accustomed to quick approvals may click to identify the file before asking who sent it.
The campaign exploits helpfulness and professional responsibility.
Step 3: The secure portal button opens an unrelated domain
The visible button hides a destination that does not belong to the claimed organization or recognized document service.
An observed version used online.transformation[.]vu, a domain unrelated to the victim’s email provider.
The link can contain the recipient’s email address in readable or encoded form.
Redirects may be inserted to complicate automated scanning and later investigation.
Step 4: The page selects a familiar-looking sign-in
The phishing site uses the email domain to choose matching imagery or generic webmail branding.
It may present the address above a password field and claim reauthentication is needed to decrypt the document.
The user interprets correct personalization as evidence of connection.
In reality, the page is reflecting information that arrived in the link.
Step 5: The form records credentials
The victim enters a password and presses a button labeled View, Continue, Verify, or Open Document.
The page forwards those details to an attacker-controlled collection point.
Some versions show a false password error to capture a second credential.
Others redirect to a genuine provider page or an empty PDF to make the failure appear temporary.
Step 6: The mailbox is used to study and impersonate
The criminal tests the credentials against email and related cloud services.
If access succeeds, they can inspect conversations, collect attachments, map contacts, and identify valuable payment or document exchanges.
Mailbox rules may hide login alerts or forward incoming messages.
A real account can then send the same lure to colleagues and customers.
Step 7: Additional fraud grows from trusted threads
The intruder may request payments, change banking instructions, steal confidential files, or launch password resets for other services.
An intercepted agreement can reveal names, dates, pricing, and signatures useful for targeted impersonation.
The original document lure becomes only the entrance to a larger compromise.
Rapid containment reduces the time available for that expansion.
Sender, Portal, Document, and Account Checks
Demand context before opening an agreement
A real reviewer should recognize the project, counterparty, sender, or conversation connected to the file.
If those details are missing, ask the supposed sender through a known address or telephone number.
Do not reply to the questionable notification because its reply path may belong to the attacker.
A legitimate colleague will understand a security-minded confirmation.
Identify the actual registered domain
Read the address bar from right to left and find the domain that controls the page.
Brand names placed in subdomains, folders, or query text do not transfer ownership.
A padlock means the browser encrypted the connection to that domain.
It does not mean the domain is authorized to collect your workplace password.
Open the document service independently
Use a saved bookmark, company portal, or trusted application to check pending files.
If the document exists, its sender and activity should appear inside the authenticated service.
If nothing is waiting, report the email rather than returning to its link.
Never search the suspicious filename online and sign in through an advertisement or unknown result.
Search the account for persistence
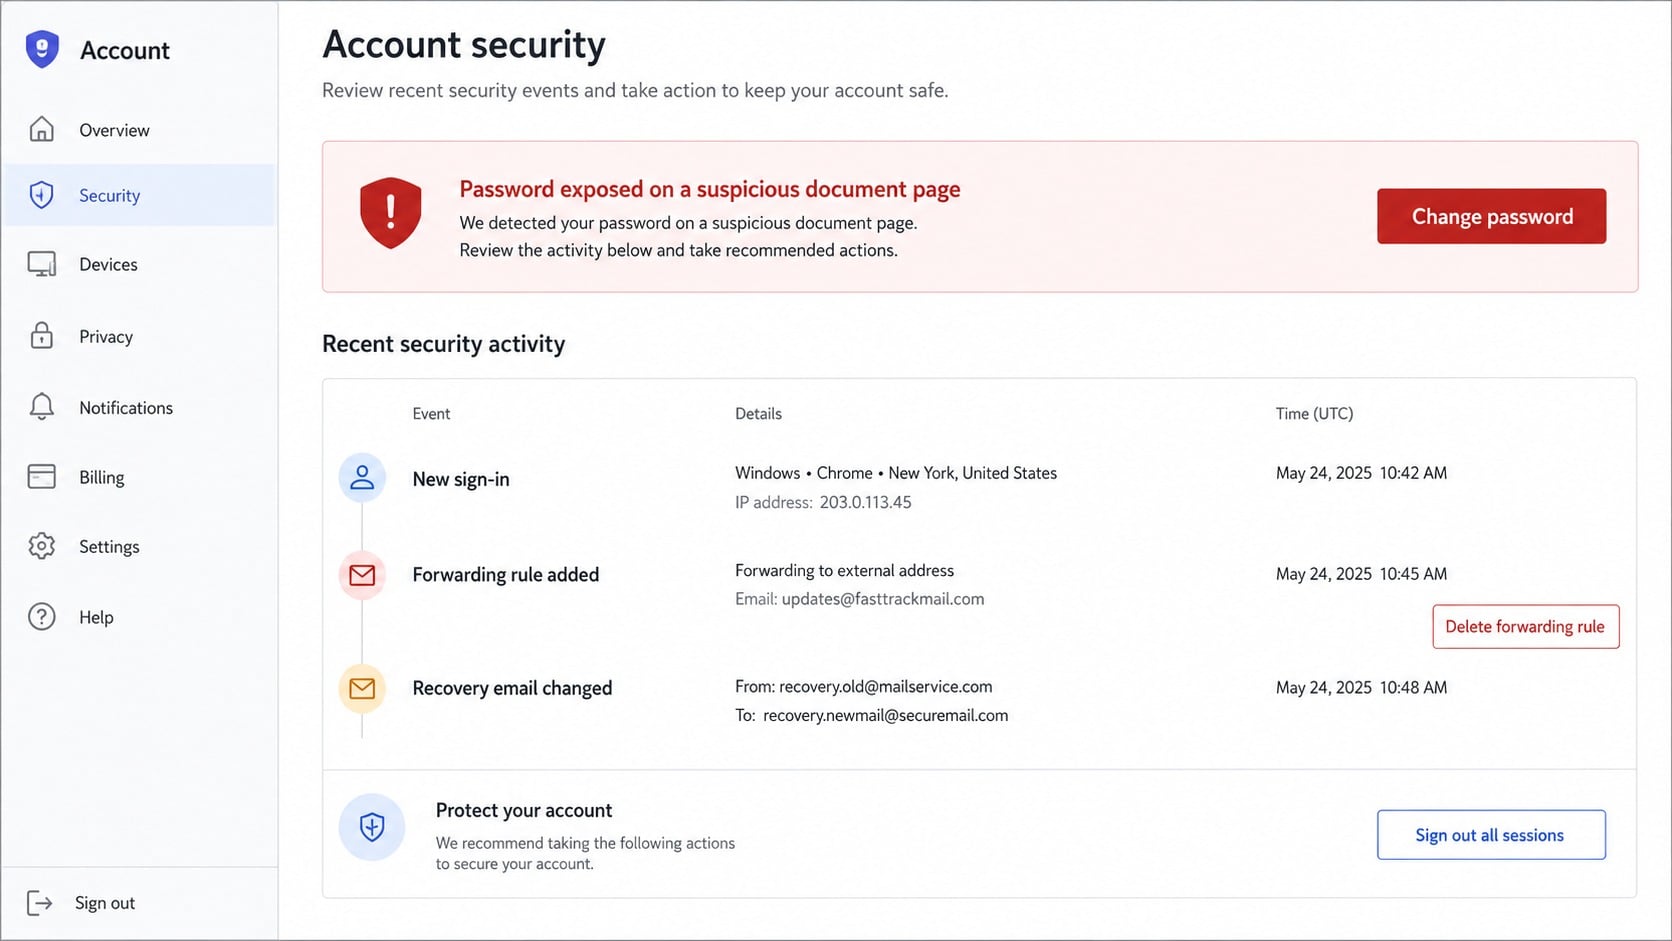
After credentials are exposed, inspect sessions, devices, application consent, forwarding, delegates, inbox rules, and recovery information.
Look for deleted security alerts and messages sent to contacts without the owner’s knowledge.
Administrators should review access logs and revoke active tokens.
Password replacement alone may leave an already authenticated attacker connected.
Why Document Lures Spread Inside Organizations
A compromised business account brings the attacker inside an existing trust network.
Recipients recognize the sender’s address and may see the message embedded in a genuine conversation.
The criminal can select a filename appropriate to the department.
Legal staff may receive an agreement, finance may receive remittance advice, and human resources may receive a policy acknowledgment.
That tailoring requires no sophisticated artificial intelligence once the mailbox exposes prior examples.
Copying a real subject line and signature can be enough.
Document phishing also crosses organizational boundaries.
Consultants, suppliers, customers, and partners regularly exchange files without sharing the same internal security controls.
An outside notification is therefore plausible, but it still needs independent confirmation.
Security gateways face another challenge because campaign links can be inactive during scanning and activated after delivery.
Redirects and provider-specific pages also make one message behave differently for different visitors.
Human verification remains important even when automated filtering is strong.
Organizations can reduce uncertainty by standardizing approved document platforms and teaching their exact login routes.
External-sharing banners should name the sender, service, and destination clearly.
Phishing-resistant authentication limits the usefulness of captured passwords.
Restricted application consent and external forwarding controls reduce persistence after a mistake.
Payment and data-release procedures should require confirmation outside email when sensitive instructions change.
These controls assume that believable messages will occasionally reach a real person.
A Safer Routine for Reviewing Unexpected Files
Begin with the relationship, not the button.
Ask whether the named sender normally assigns this type of document and whether a related conversation exists.
Next, open the approved collaboration service independently and inspect its notification center.
A genuine pending file should appear there with a recognizable owner, activity history, and permission record.
If the service requires a fresh login, start from its saved bookmark or managed application.
Do not copy the address displayed by the suspicious page because lookalike spelling can survive that transition.
Preview filenames cautiously.
A personalized name proves only that the sender knew an email address or obtained a contact list.
Confirm the document’s purpose before downloading macros, archives, disk images, or executable files.
Agreements are normally delivered as ordinary documents, not software installers or browser extensions.
When a colleague confirms the share, ask them to identify the platform and filename without repeating information from the suspicious email.
Independent details are stronger than a simple yes answer to a leading question.
Finally, report false invitations even when nobody clicked.
One copy can help administrators find other recipients and block a campaign before a coworker supplies credentials.
Mobile review needs extra care because narrow screens often hide the complete domain and collapse sender details behind a display name.
Open the message properties before acting, or wait until a larger screen exposes the address clearly.
Security teams can also examine the link safely without asking the recipient to revisit it.
That separation protects the employee while preserving evidence needed to block related messages.
Evidence can reveal the wider campaign.
What to Do if You Have Fallen Victim to This Scam
- Leave the counterfeit portal. Close every related tab and do not submit another password if the first attempt appeared unsuccessful.
- Notify the organization. Contact the security team or administrator immediately and explain precisely what you clicked, entered, downloaded, or approved.
- Change the exposed password. Use the genuine account page from a trusted device and choose a completely unique replacement.
- End existing sessions. Revoke tokens, unknown devices, app passwords, external applications, and suspicious authentication methods.
- Review the mailbox. Remove unauthorized rules, forwarding, delegates, and recovery changes, then examine sent and deleted folders.
- Secure reused accounts. Replace matching or similar passwords everywhere, beginning with email, cloud storage, finance, and identity services.
- Check shared documents. Review recent access, downloads, external shares, permission changes, and files containing confidential or financial information.
- Warn likely recipients. Tell contacts if the compromised account sent document invitations, but describe the lure without forwarding its active link.
- Review financial instructions. Verify bank-detail changes, payment approvals, and contracts discussed during the possible access period.
- Run a security scan. Use Malwarebytes if anything was downloaded, and enable AdGuard to help prevent connections to known phishing domains.
- Preserve evidence. Save the original message, headers, URLs, screenshots, login alerts, and timestamps before administrators remove the campaign.
- Monitor follow-up activity. Watch for reset notices, unexpected multifactor prompts, impersonation messages, and calls pretending to investigate the incident.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is Agreement_[name]_Review.pdf a dangerous file?
In this campaign, the name is part of the lure and does not establish a real agreement.
The main observed risk is the portal reached through the message.
Treat any accompanying file cautiously as well.
How did the fake page know my email provider?
The link can carry your email address as a parameter.
A script reads the part after @ and selects matching branding.
No account access is required for that trick.
Does HTTPS make the secure portal genuine?
No.
HTTPS encrypts traffic between your browser and the site you reached.
Criminal sites can obtain certificates, so ownership and context still need verification.
What if I entered only my email address?
The attacker may already know it, but submission confirms an active recipient and can support more targeted phishing.
Do not provide a password, and report the page.
Should I ask the sender by replying?
Use a separate, previously trusted channel.
The reply address may be fraudulent, and a genuine sender’s mailbox may already be compromised.
A known telephone number is often useful.
Why was I redirected to my real email service afterward?
A phishing page can redirect anywhere after recording information.
Landing on the genuine provider does not erase the earlier submission.
Reset the password and review the account immediately.
The Bottom Line
The Pending Documents email disguises a credential trap as an ordinary agreement review and uses link-based personalization to strengthen the illusion.
Open shared files through known platforms, verify unexpected assignments separately, and complete a full session and mailbox review after any submitted password.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.