

A notice about incentive pay naturally attracts attention, especially when it appears to come from human resources during a busy payroll period.
The promise of a private document makes the email feel personal, but that privacy theme deserves closer inspection.
Overview
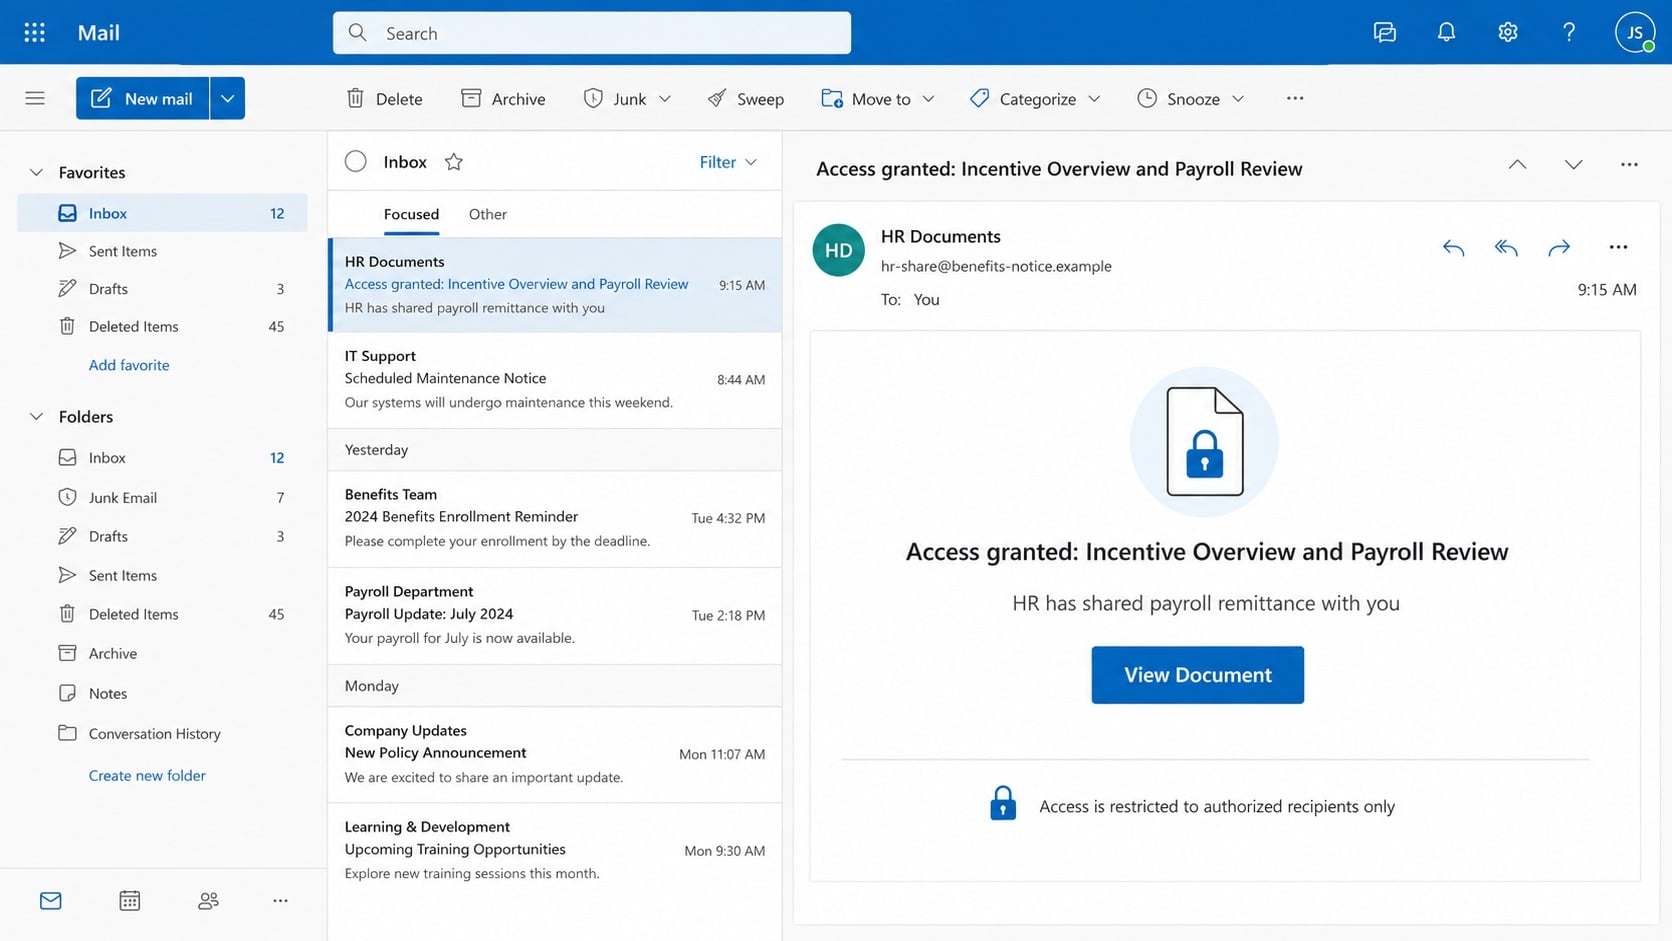
The email claims HR shared a restricted payroll file
The message announces access to an “Incentive Overview and Payroll Review” and says human resources shared payroll remittance with the recipient.
It includes a “View Document” button and warns that access is restricted to authorized recipients.
That confidentiality language is meant to make an unfamiliar sign-in request feel appropriate.
- The subject says access was granted, although the employee may not have requested any payroll document.
- The email uses compensation language that can trigger curiosity before the recipient checks ordinary HR channels.
- The document button directs the employee outside the expected payroll or collaboration portal.
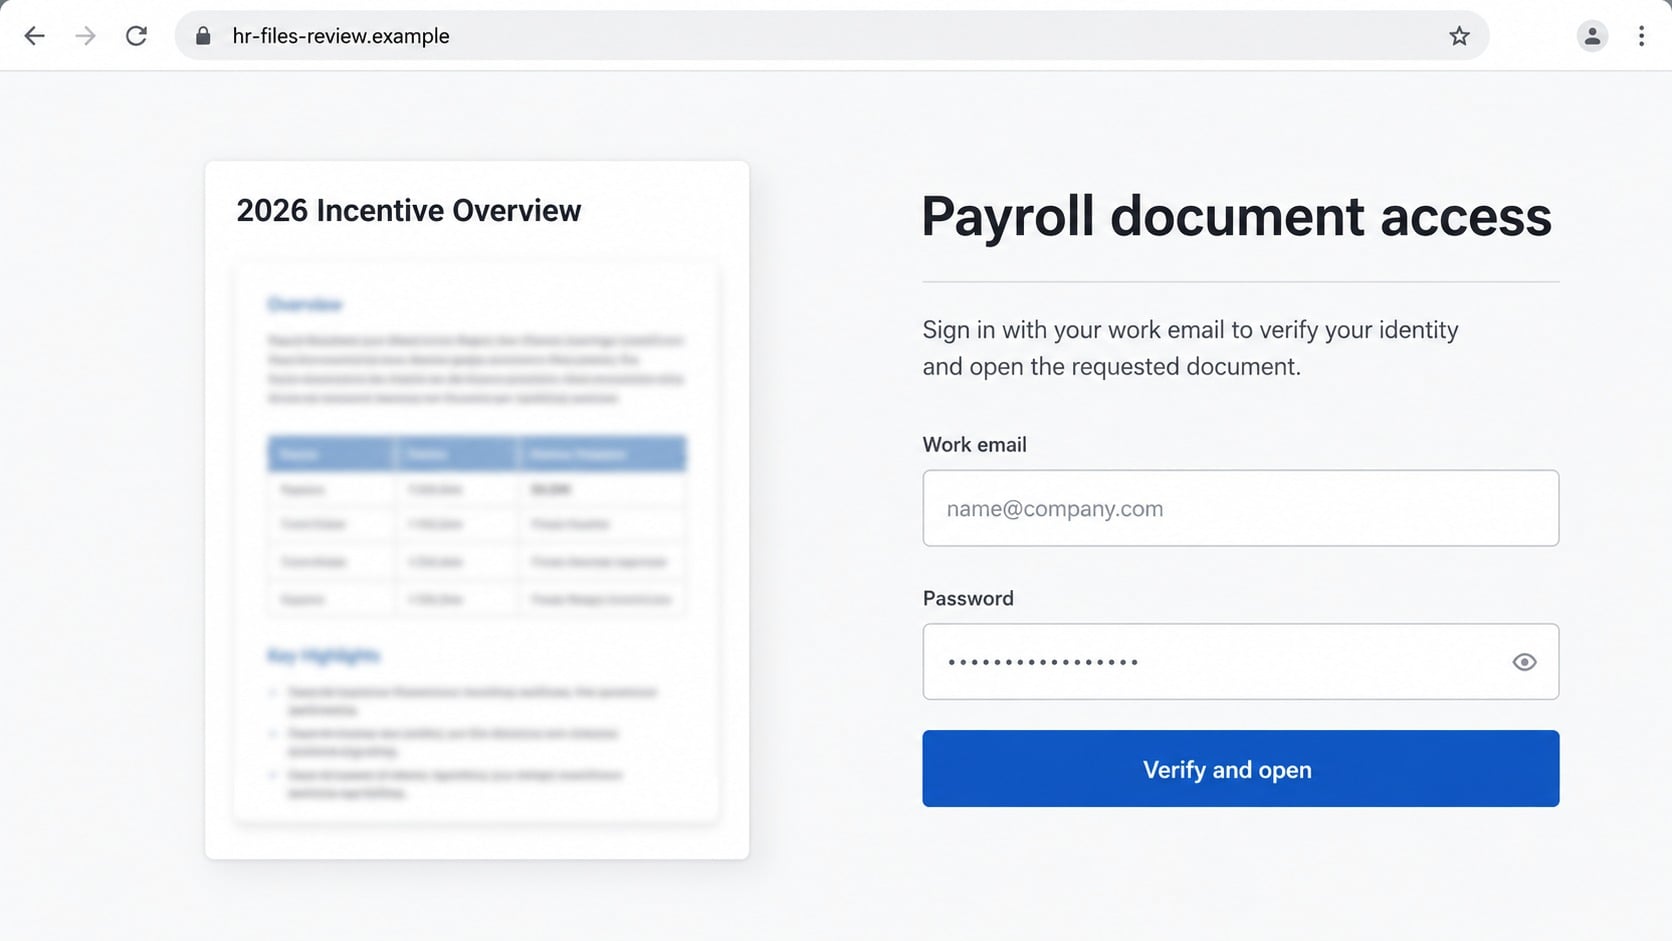
- The linked site may seek work credentials, but the examined destination was inactive when reviewed.
The inactive link does not make the email harmless
Phishing pages often disappear after abuse reports, hosting suspension, or a campaign’s scheduled end.
A dead destination prevents direct confirmation of its final form, so its precise fields should not be described as observed fact.
The message remains unsafe because it fabricates HR document access and routes the recipient through an unverified link.
Work credentials can expose far more than payroll
A stolen organizational password may unlock email, shared documents, cloud storage, internal directories, benefits systems, or remote-access services.
Even when multifactor authentication blocks the first login, attackers may bombard the employee with approval prompts or imitate the help desk.
Prompt reporting lets administrators revoke sessions and examine the account before the intrusion reaches colleagues.
Why Payroll and Incentive Themes Feel Convincing
Compensation is private, time-sensitive, and emotionally important.
Employees may open an incentive notice quickly because it could explain a bonus, commission, deduction, adjustment, or annual review.
Confidentiality also discourages casual verification.
A recipient may hesitate to ask coworkers about a document that appears to contain individual pay information.
Criminals turn that hesitation into isolation, leaving the employee to rely on the message’s button.
The wording does not need to describe the supposed payment in detail.
Ambiguity allows each reader to imagine a plausible reason for the file.
Sales staff may expect commission information, while other employees may think of a bonus or payroll correction.
A label such as “Access granted” resembles an automatic notification from a shared-document platform.
However, a real platform normally identifies the sender, organization, file location, and service through consistent domains and established workplace procedures.
A generic statement that “HR has shared payroll remittance with you” supplies authority without a verifiable person.
The absence of a named HR contact is particularly suspicious when the organization usually personalizes compensation communications.
Real payroll portals should already be bookmarked, managed through single sign-on, or linked from a known intranet.
Employees do not need an unsolicited email route to discover whether a new document exists.
How the Incentive and Payroll Review Email Scam Works
Step 1: The attacker sends a confidential-looking notification
The subject announces access to an incentive overview, payroll review, remittance advice, salary update, or benefits document.
The email may arrive near payday, quarter-end, tax season, or performance reviews to increase relevance.
Mass campaigns can succeed without knowing an employer’s actual schedule.
More targeted campaigns may use public job information or previously stolen company data.
Step 2: Restricted-access wording creates legitimacy
The body states that only authorized recipients may view the document.
This explanation prepares the victim to accept a login challenge on the next page.
It also suggests the content is too sensitive to discuss openly.
The privacy warning becomes part of the manipulation instead of a genuine protection.
Step 3: A document button opens an outside site
The employee selects “View Document,” expecting a familiar collaboration or payroll system.
The link can pass through a redirect before reaching disposable phishing infrastructure.
Attackers sometimes use compromised websites or legitimate hosting services to make blocking more difficult.
The final domain still does not belong to the employer, payroll vendor, or authorized document provider.
Step 4: The page imitates workplace authentication
Typical versions display a Microsoft-style, webmail-style, or generic employee login form.
A prefilled work email address can make the page look connected to the organization.
For this observed campaign, the link was inactive during review, so the exact interface and requested fields could not be verified.
Employees should treat any reactivated destination as hostile and avoid testing it.
Step 5: Credentials or session access may be captured
A simple phishing page records the password when the employee submits the form.
More advanced adversary-in-the-middle pages relay a real login and attempt to capture the authenticated session.
The attacker may also request an approval code or send repeated multifactor prompts.
No employee should approve a sign-in they did not initiate through the normal workplace portal.
Step 6: The intruder searches for valuable workplace access
After a successful takeover, the attacker reviews email, cloud files, address books, shared drives, and recent conversations.
Payroll data can contain names, addresses, tax details, bank information, and identity documents.
Even without direct payroll access, the mailbox can support convincing impersonation of HR or management.
The compromised account may send the same document lure to coworkers who already trust the sender.
Step 7: A second-stage fraud targets colleagues or payments
The criminal may request direct-deposit changes, purchase gift cards, alter supplier payments, or distribute additional credential traps.
Messages sent inside an existing organization can bypass the skepticism applied to unknown outsiders.
Attackers may delete replies and create inbox rules to delay discovery.
A payroll-themed phish can therefore become an organization-wide incident rather than one employee’s mistake.
Sender, Portal, HR, and Account Checks
Confirm the notification through normal HR channels
Open the payroll platform from a bookmark, company intranet, or managed application.
Check whether the promised document exists there before contacting anyone.
If clarification is needed, message HR through the directory or call a known internal number.
Do not use an address, number, or reply route supplied only by the questionable email.
Inspect the complete delivery path
Review the sender address, reply address, link preview, and any security banner added by the organization.
An HR display name can hide an outside mailbox.
Lookalike domains may replace one letter, add a department word, or attach the company name to an unrelated ending.
Forwarded notifications should still match the document service your organization actually uses.
Question unexpected authentication
A login prompt is not automatically safe because the document was described as confidential.
Check the address bar before entering anything, and leave if the domain differs from the approved single sign-on provider.
Password managers often expose a mismatch by refusing to fill credentials on the counterfeit site.
Never provide a one-time code to someone who contacts you after the attempted login.
Audit the work account as an administrator would
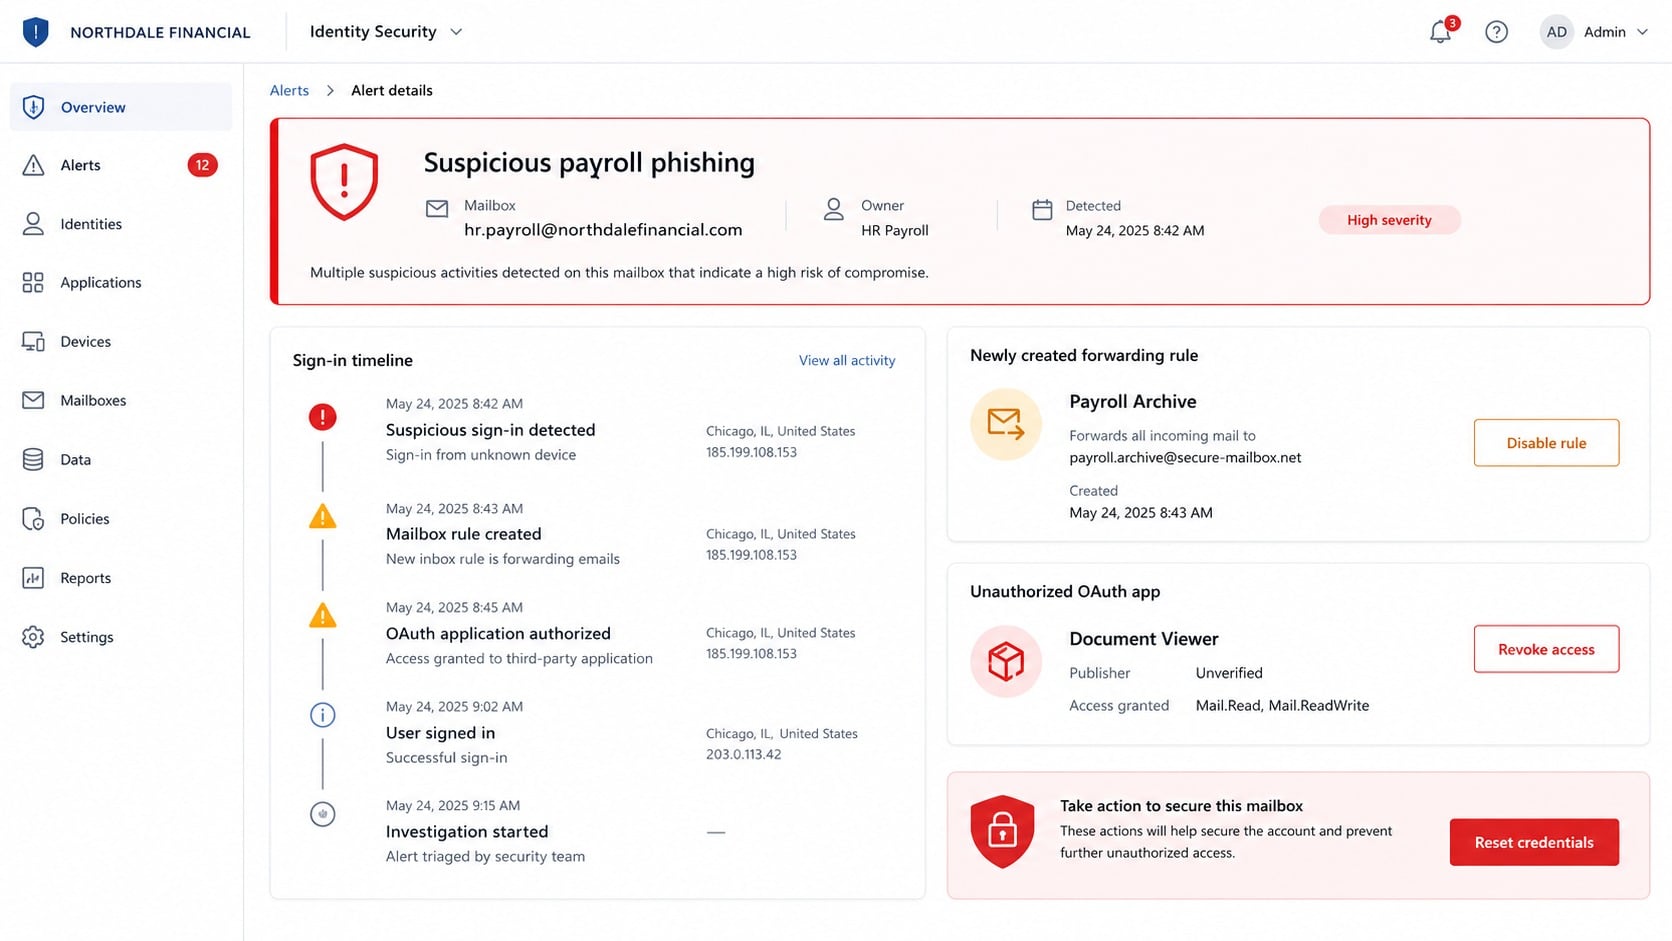
After exposure, review sign-in logs, registered devices, session tokens, multifactor methods, inbox rules, application grants, and forwarding settings.
Look for activity beginning before the employee noticed the incident because credentials may have been tested quickly.
Search for sent messages, deleted alerts, and HR or payment conversations accessed by the intruder.
Document findings and preserve the original phishing email for containment and notification decisions.
What an Employer Should Do After One Employee Clicks
A click without data entry is different from a submitted password, approved prompt, downloaded file, or successful session takeover.
The response should begin by establishing exactly what happened and when.
Security staff can isolate the destination, block related domains, and search mail logs for other recipients.
Removing matching messages limits additional exposure, but copies may have been forwarded or delivered to personal devices.
The affected account should have its sessions revoked, not merely its password changed.
Existing authenticated sessions can survive a password reset on some services.
Administrators should also reset compromised authentication methods and revoke suspicious application consent.
If the account accessed payroll information, privacy and legal teams may need to assess whether personal data was viewed or exported.
The organization should inspect direct-deposit changes, employee profile edits, and messages requesting financial action.
Colleagues may need a warning that names the lure without repeating its clickable link.
Use a screenshot or plain description so employees can recognize the message safely.
A calm internal notice encourages reporting from people who already interacted.
Blaming the first reporter drives later incidents underground and gives attackers more time.
After containment, improve the workflow that made the lure believable.
Employees should know exactly where incentive, payroll, tax, and benefit documents normally appear.
A predictable official route removes much of the uncertainty that phishing campaigns exploit.
Organizations can also restrict external forwarding and adopt phishing-resistant sign-in methods for accounts holding sensitive HR data.
These controls reduce the consequence of a believable message without relying on perfect human judgment.
Payroll Information Creates Long-Term Identity Risk
Payroll systems can hold more durable information than a typical shopping account.
Names, home addresses, government identifiers, salary records, tax forms, dependents, and banking details may remain useful for years.
An intruder who reaches only email can still locate attached payslips or enrollment documents through search.
Shared drives may contain exports intended for managers, accountants, or benefits administrators.
The response team should determine what the account could access, not merely what the employee remembers opening.
Audit logs can reveal downloads, mass searches, external shares, and unusual access to sensitive folders.
Direct-deposit fraud has a narrower time window.
A submitted change may redirect the next paycheck unless payroll staff freeze alterations and verify the employee through known details.
Tax-related identity fraud can surface much later, particularly when government identifiers or annual forms were exposed.
Affected employees may need credit monitoring, fraud alerts, or guidance from the appropriate tax authority.
The employer should explain confirmed exposure plainly and avoid claiming safety before the access review is complete.
Clear updates help employees protect themselves without creating unnecessary panic or speculation.
Managers should preserve normal payroll deadlines while adding manual confirmation for profile or banking changes linked to the incident.
That temporary safeguard protects wages without forcing every employee to rebuild unrelated accounts.
What to Do if You Have Fallen Victim to This Scam
- Disconnect from the page. Close the tab and stop responding to any person who contacts you about the supposed payroll file.
- Call your security or IT team. Report the time, device, email subject, link, information entered, and any multifactor prompt you approved.
- Change the work password safely. Use the official company portal from a clean browser and create a unique replacement.
- Revoke active sessions. Ask an administrator to invalidate tokens, unknown devices, app passwords, and unauthorized connected applications.
- Review authentication methods. Remove unfamiliar telephone numbers, backup addresses, passkeys, security keys, or authenticator registrations.
- Check email settings. Delete malicious forwarding rules, hidden filters, delegates, and automatic replies created without your approval.
- Protect related accounts. Replace reused passwords on personal email, payroll, banking, benefits, and cloud services.
- Inspect payroll changes. Verify direct-deposit details, contact information, tax elections, and recent documents through the real HR system.
- Alert coworkers carefully. Tell them your account may have sent unsafe messages, but do not forward the active phishing link.
- Scan the affected device. Use Malwarebytes to look for unwanted downloads, and use AdGuard to help block known malicious destinations.
- Preserve evidence. Keep the original email, full headers, screenshots, security alerts, and a timeline for the incident team.
- Monitor for identity misuse. Watch financial accounts and credit records if tax, payroll, or personal information may have been exposed.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Does “Access granted” mean the document was shared securely?
No.
Those words are message content and can be written by anyone.
Confirm the file inside the organization’s approved HR or collaboration platform.
What if the View Document button no longer works?
A dead page may have been removed, expired, or moved after the campaign ended.
It does not validate the email.
Report the message and avoid testing replacement links.
Can the attacker know my employer and job title?
Yes.
Professional profiles, company websites, data brokers, and earlier breaches can reveal enough information to personalize an HR lure.
Accurate public details do not prove the sender is internal.
I clicked but entered nothing. Am I safe?
Your risk is lower, but you should still report the click.
The page could have collected technical information or attempted a download.
Security staff can decide whether device inspection is needed.
Why would payroll require my email password?
A legitimate portal may use organizational single sign-on, but it should appear on the approved identity domain.
An unfamiliar page asking for the password is not made safe by displaying a company logo.
Should I tell HR if no money was lost?
Yes.
The campaign impersonates HR and may target other employees.
Early reporting supports message removal, account review, and protection of payroll information.
The Bottom Line
The Incentive Overview and Payroll Review email uses confidential compensation language to steer employees toward an unverified document route.
Check payroll notices inside trusted workplace systems, report questionable links promptly, and treat submitted work credentials as an organization-wide security event.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.