


An accounting invitation can arrive in the middle of an ordinary workday, tucked between client questions and payroll reminders. It looks like another small task.
Before accepting an unexpected QuickBooks invitation, take a closer look at who arranged it. A few details can change how you should handle the message.
Overview
What the QuickBooks Invitation Claims
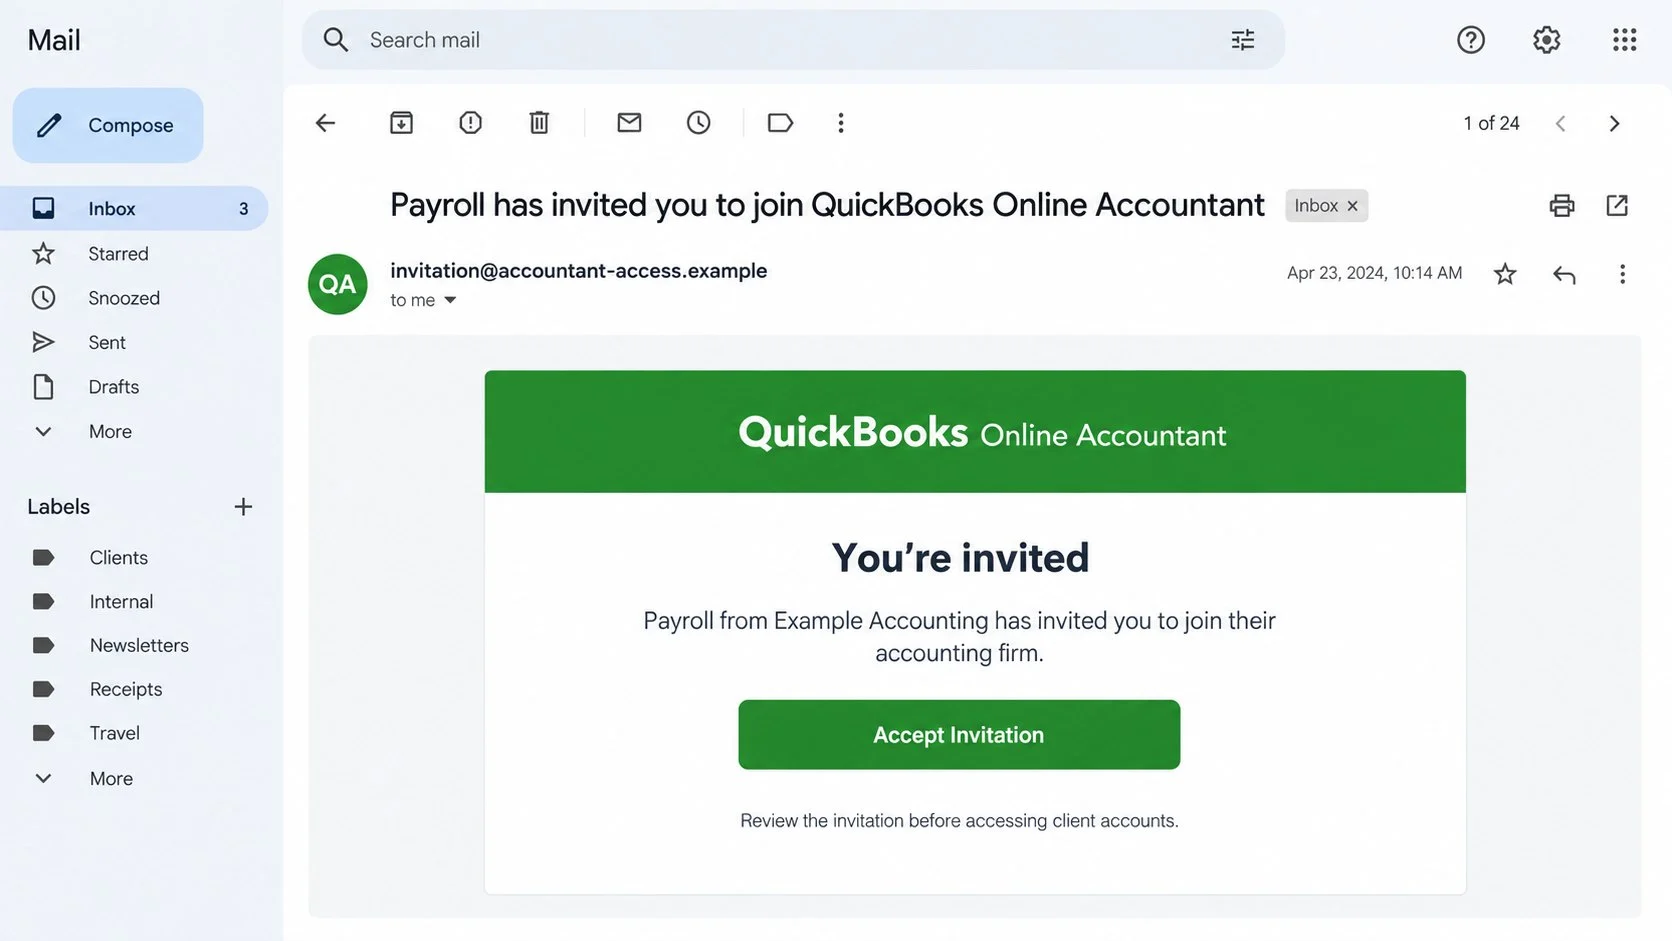
The QuickBooks Online Accountant invitation email scam borrows the language of a genuine workplace process. Someone called Payroll supposedly wants you to join an accounting firm.
The reported message presents this as an invitation for a new user. It suggests that accepting will provide access to the firm’s client work.
That premise fits an accountant’s routine. Firms add staff, onboard contractors, and arrange client access through online systems, often using email notifications.
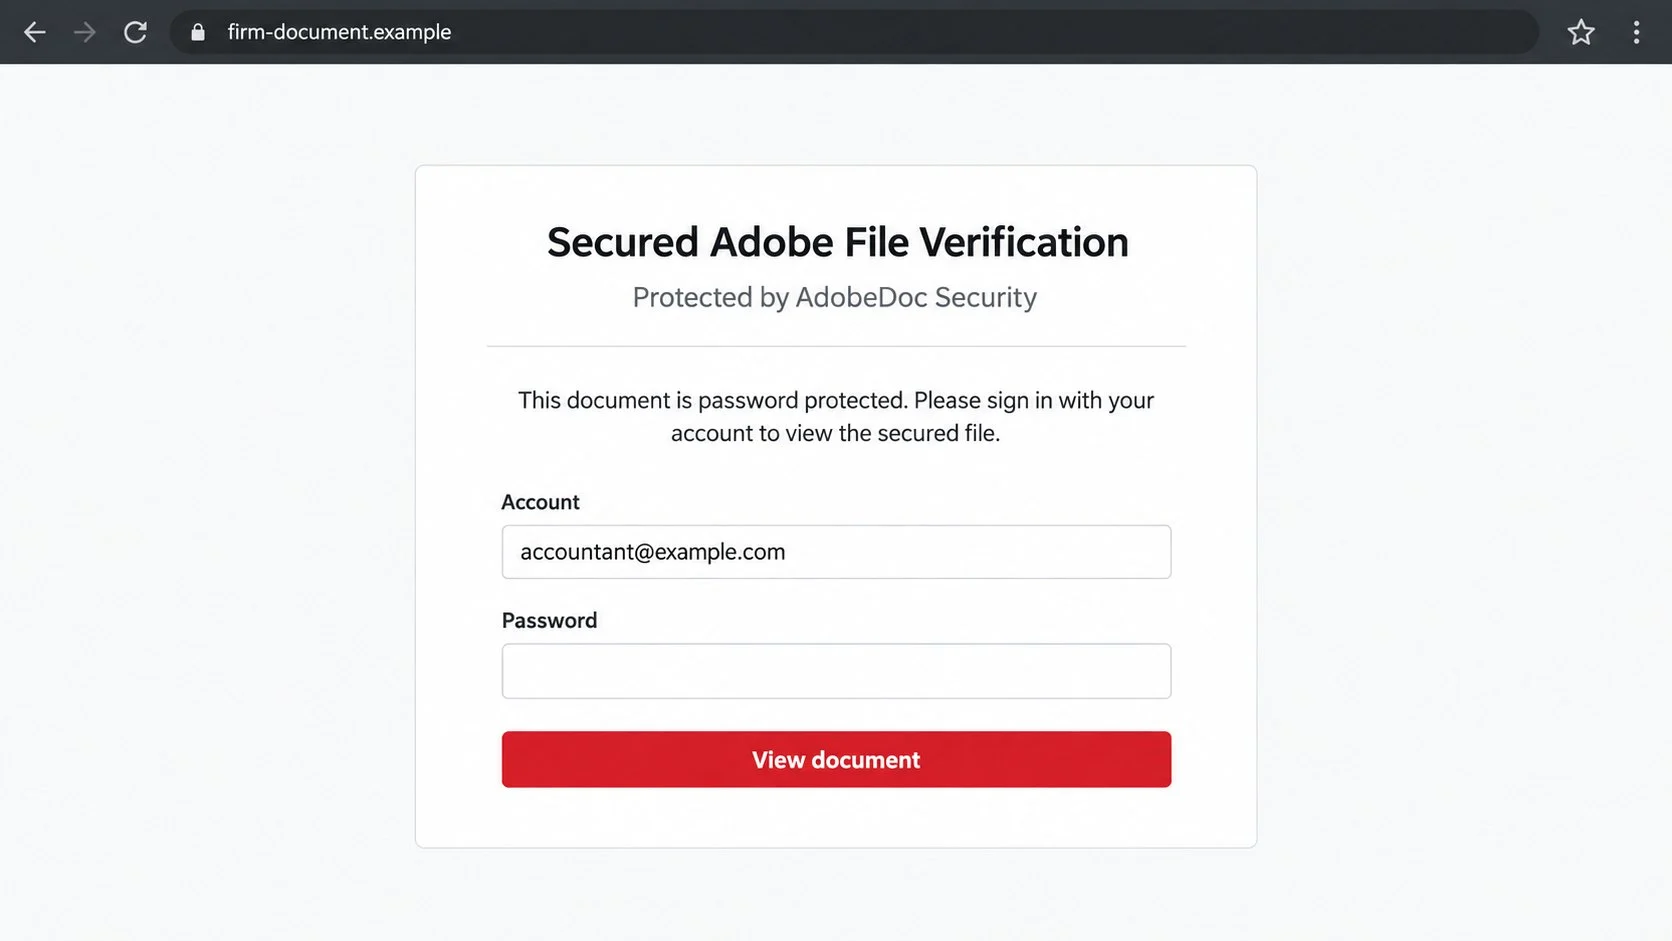
However, this particular invitation leads away from an accounting workflow. Its reported destination is a counterfeit Adobe-themed page requesting an email password.
QuickBooks is a real service operated by Intuit. The scam is the impersonated invitation and credential-collection page, not the existence of online accounting invitations.
The Details That Identify This Version
The documented sample combines an accounting invitation with an unrelated document-verification screen. That change of purpose matters more than the familiar green branding.
- The invitation names Payroll as the inviting party.
- It describes joining QuickBooks Online Accountant as a new user.
- An Accept Invitation button provides the main action.
- The reported sender does not use an Intuit domain.
- The destination switches to Adobe-styled verification and asks for an email password.
The reported destination is humanandairesources[.]com. Treat that as a historical indicator, not a complete blocklist, because operators can replace a landing address.
The same reported address appears in another protected-invoice lure. Shared infrastructure suggests reuse, but does not independently identify the people running either campaign.
The images here illustrate the invitation and credential request using fictional addresses. They are not original captures of a recipient’s private correspondence.
Why an Accounting Theme Raises the Stakes
An accountant’s mailbox may contain payroll discussions, tax documents, invoices, and instructions for sending money. Access can expose much more than a contact list.
A compromised mailbox can also make later messages convincing. Criminals may reply inside existing conversations, where clients already recognize the address and earlier discussion.
Those are possible consequences of account compromise, not proof that every recipient has lost client records. Receiving this invitation alone does not grant anyone access.
The practical question is what happened next: did you only read it, follow its button, enter a password, or approve an additional sign-in request?
How the QuickBooks Online Accountant Invitation Scam Works
Step 1: The Message Arrives as a Familiar Administrative Task
The opening move is modest. Rather than offering a prize, the email asks you to complete something that could plausibly belong on your work list.
Payroll is a useful label for this deception. It sounds like an internal function, even when no individual, employer, or recognized firm is clearly identified.
A recipient expecting new responsibilities might mentally supply the missing context. Perhaps an administrator created the invitation, or a colleague forgot to mention it.
That assumption replaces an important check. An invitation should connect to an actual person and a real reason for granting access, not merely a plausible department name.
Step 2: The Invitation Offers a Convenient Shortcut
The Accept Invitation button appears to finish the task in one click. The surrounding wording promises a connection with the firm’s accounting environment.
Legitimate invitations can also contain buttons. The button’s existence is not the problem; the unverified sender, unknown invitation, and destination create the concern together.
Workplace momentum helps the lure. When someone is processing a crowded inbox, accepting an invitation may feel less consequential than approving a payment.
Yet an invitation link can lead anywhere. The words printed on the button do not establish which organization controls the page that opens.
Step 3: The Journey Changes from Accounting Access to Document Verification
In the reported sample, the link leads to a page styled as Adobe verification. It no longer resembles the accounting task described in the invitation.
This is the point where the story stops fitting together. Joining a firm’s accounting system and unlocking an Adobe document are different actions.
A real firm might use both services separately. That possibility does not explain an unsolicited invitation silently changing into a request for your mailbox password.
Pause at the change itself. Do not invent a technical explanation on the sender’s behalf, such as assuming that every document system shares your email login.
Step 4: A Prefilled Address Makes the Form Feel Personalized
The described phishing form already contains the recipient’s email address. Its remaining request is the password, presented as a necessary verification step.
A prefilled address can be passed through a link or inserted into a page. It does not demonstrate that the page has authenticated your identity.
Nor does it prove a relationship with your employer. Anyone who sent the invitation already had an address to place in that field.
The important boundary is the password. A third-party page should not receive your mailbox secret simply because its design includes an Adobe logo or security wording.
Step 5: Submitting the Form Exposes Credentials
The reported purpose of the destination is credential theft. Information entered into the imitation form can go to its operator instead of a legitimate sign-in service.
The harm depends partly on which password you supplied. An email password threatens the mailbox; an Intuit password threatens that account if the credentials work.
If you reused the same password for both, the exposure is broader. Reuse can turn one misleading form into several account-recovery tasks.
Multi-factor authentication may prevent some unauthorized logins. Still, a submitted password needs changing, and an unexpected approval request should never be accepted to complete this invitation.
Step 6: Stolen Access May Support More Targeted Fraud
Someone who gains mailbox access may search for payment conversations or impersonate staff. Accounting correspondence gives those messages useful context and a believable voice.
They could attempt an invoice redirection, request confidential records, or send another invitation from the compromised account. These are follow-on risks, not guaranteed outcomes.
Actual accounting permissions are separate. Stealing an email password does not automatically grant every client role or override every control inside QuickBooks.
Nevertheless, mailbox access can assist password resets and social engineering. That is why a firm should investigate promptly rather than treating the incident as harmless spam.
How to Verify an Accounting Invitation Safely
Ask the Firm Who Sent It
Contact the administrator or colleague who normally manages access. Use an existing directory entry or established conversation, not a number included in the questionable email.
Ask which account was invited, when the invitation was issued, and what role you should receive. Specific answers are more useful than a vague confirmation.
If Payroll is the only identity shown, ask who that label represents. Do not assume it belongs to your own payroll department or accounting provider.
Separate Staff Invitations from Client Connections
Accounting platforms support different relationships. Joining a firm as staff is not the same thing as a client inviting an accountant to its books.
Check which relationship the email claims to establish. A message that describes one arrangement while requesting an unrelated login deserves an independent verification.
For a genuine request, have the responsible administrator confirm the intended permissions. Nobody should receive broader client access simply because an invitation was convenient to accept.
Inspect the Sender and Destination Together
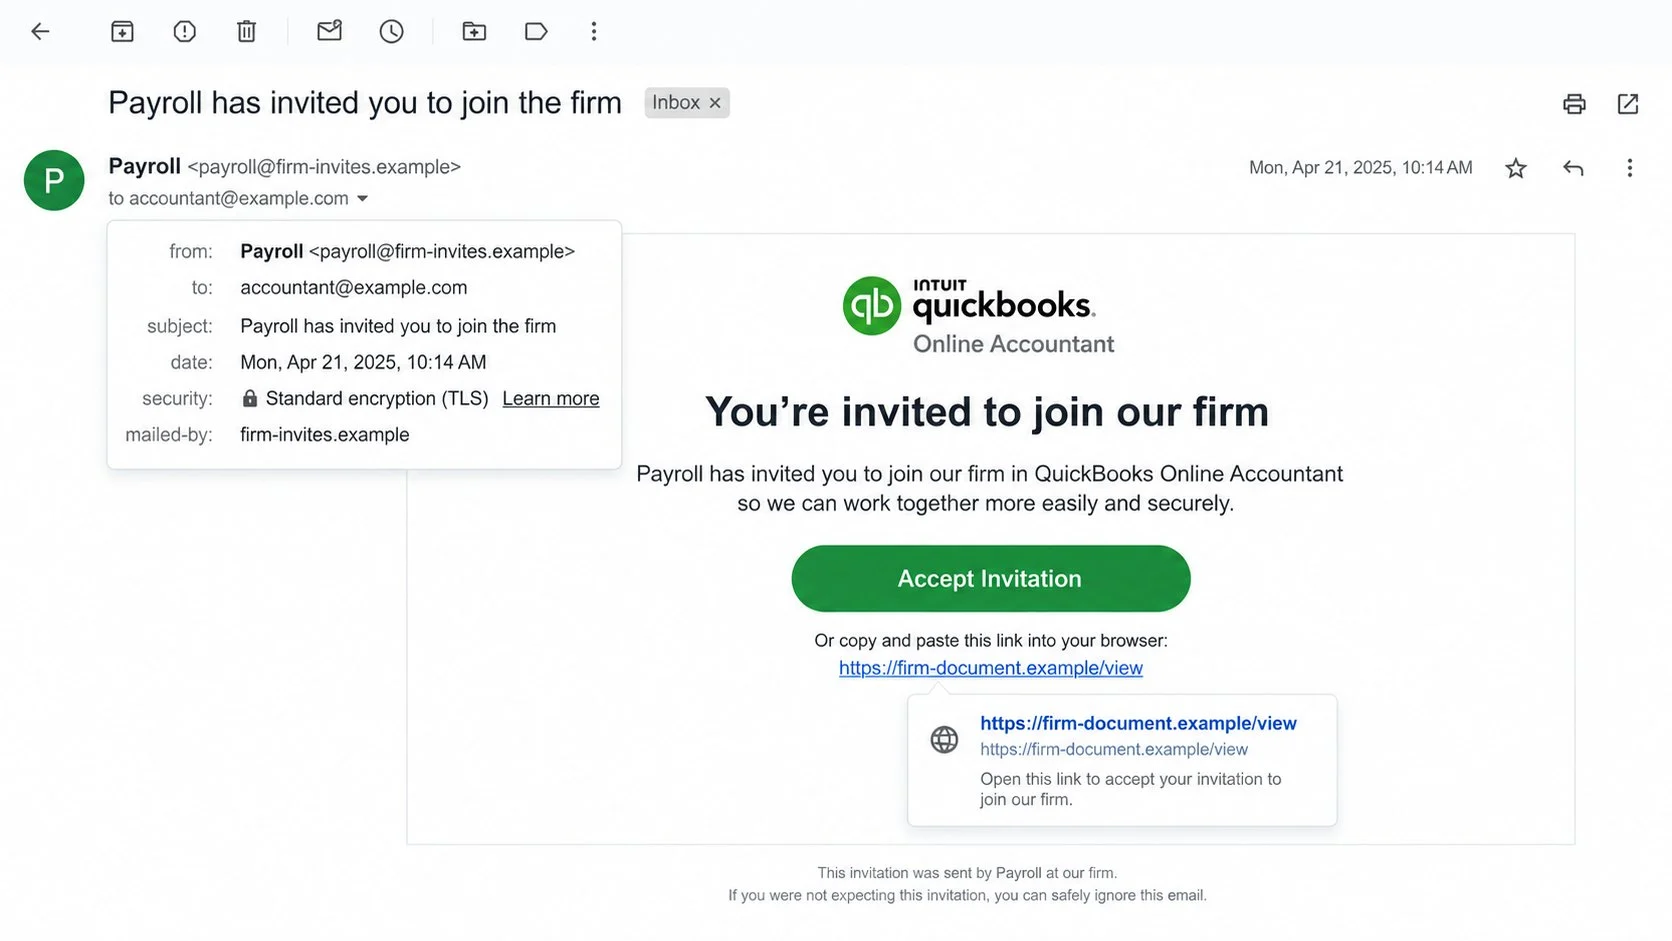
Expand the sender information rather than relying on the Payroll display name. Then inspect the actual link without opening it, where your mail application permits.
A mismatch between an accounting invitation and an unrelated document host is a strong warning. HTTPS only encrypts the connection; it does not endorse the business.
Some legitimate services use multiple sending systems. When you cannot confidently verify a domain, ask the firm or Intuit through a separately located support route.
Enter Through Your Established Account Route
Open your saved Intuit or QuickBooks sign-in location directly. Confirm that you are using the account the firm intended, especially if you manage several addresses.
If an invitation cannot be located or completed there, ask the administrator to explain the official process or resend it after verifying your address.
A missing invitation in one view is not conclusive by itself. The stronger test is agreement between the responsible person, the expected account, and the legitimate service.
What to Do If You Fell Victim to the QuickBooks Invitation Email Scam
You can contain the problem without assuming the worst. Begin with the information you actually entered, then check the accounts and business processes connected to it.
- Stop the invitation process and record your actions.
Close the suspicious page. Note whether you entered an email password, an Intuit password, a verification code, or nothing at all.
Keep the original message and the approximate interaction time. Your administrator can use those details to compare sign-in activity and locate other recipients.
- Change the exposed password through the real service.
Use a trusted device and a known sign-in address. Create a unique replacement rather than a slight variation of the password you submitted.
If the same secret protected other services, replace it there too. Start with the mailbox and any financial or work accounts sharing it.
- Review sessions and authentication settings.
Inspect recent sign-ins and active sessions. Use the provider’s controls to remove unfamiliar access and sign out sessions where appropriate.
Check recovery contact details and multi-factor methods. Remove additions you did not make, and tell your administrator about unexpected authentication prompts.
- Notify your firm’s security or access administrator.
Report the incident even if the password change appears to work. Managed environments may require session revocation and checks that ordinary users cannot perform.
State which credentials were exposed without sending the password itself. Ask whether other staff received matching invitations or whether suspicious logins occurred.
- Inspect the mailbox for quiet changes.
Review forwarding settings, inbox rules, delegated access, sent messages, and deleted items. An intruder may hide replies or redirect future correspondence.
Ask a qualified administrator to review connected applications if necessary. Do not delete legitimate firm integrations simply because their technical names look unfamiliar.
- Verify accounting access and sensitive transactions.
If an Intuit account may be affected, inspect its user access and recent activity with the firm administrator. Investigate unfamiliar changes before removing anything.
Reconfirm changed payment instructions through established contacts. If money was sent because of a related message, contact the bank promptly and preserve transaction details.
- Check the device if you downloaded or ran anything.
A password phishing incident is not automatically a malware infection. A download, installed extension, or executed file creates a separate reason for a device check.
Malwarebytes can help scan for malicious software. AdGuard may reduce exposure to some malicious destinations, but neither product replaces password recovery or guarantees every phishing link is blocked.
- Report the impersonation and warn affected contacts.
Use your mail provider’s phishing report option and Intuit’s independently verified reporting channel. Share the original email with internal security using the firm’s approved method.
If your account sent fraudulent messages, notify relevant recipients through a trustworthy route. Explain which requests should be ignored without exposing confidential client information.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Why This Is Not Simply an Unwanted QuickBooks Invitation
A genuine invitation sent to the wrong address can be an administrative mistake. An unfamiliar invitation alone does not establish that its sender is a criminal.
This reported campaign has additional evidence: an unrelated sender, an unexpected Adobe-themed destination, and a request for the recipient’s email password.
Those elements support the phishing classification. They are more meaningful than a broad claim that every unsolicited accounting notification is fake.
The distinction also helps legitimate work continue. You can decline the suspicious route while still asking a real colleague to arrange access through the proper process.
For firms, a simple expectation helps: access changes should have an identifiable owner. Staff should know whom to contact when an invitation arrives without context.
That habit is especially useful during onboarding. New employees and contractors often expect unfamiliar systems, making a brief independent confirmation worth the extra minute.
Frequently Asked Questions
Is QuickBooks Online Accountant a Scam?
No. QuickBooks Online Accountant is a legitimate Intuit service. This warning concerns an invitation impersonation that diverts recipients to a counterfeit verification page.
A real product name can appear in a fraudulent email without the product provider having sent or approved that message.
Does Payroll Mean the Email Came from My Employer?
No. Payroll is only a displayed label unless you verify the sender and the underlying request. It does not identify a particular employee or company.
Ask your established payroll or accounting contact whether they issued an invitation for your exact account.
Why Would a QuickBooks Invitation Ask for an Adobe Login?
In this campaign, the brand switch is part of the deception. The reported Adobe-themed form collects credentials instead of completing the advertised accounting invitation.
Do not treat the switch as normal just because both brands are familiar. Confirm any separate document-sharing request with its real sender.
Is the Prefilled Email Address Proof the Page Is Genuine?
No. A page can display an address supplied in its link or page data. Showing that address does not prove control of an official account system.
The destination’s legitimacy and the purpose of the request still need verification before you enter a password.
What If I Clicked Accept but Entered Nothing?
Close the page and report the invitation. A click alone does not establish that your password or accounting records were stolen.
Check whether anything downloaded or whether you granted permissions. If neither happened, avoid escalating the situation beyond the evidence, but remain alert for follow-up messages.
Can a Password Change Alone Resolve the Incident?
It is an important first step, but existing sessions, mailbox rules, recovery settings, and connected applications may also need review.
For business accounts, involve the administrator. They can examine access history and determine whether client correspondence or accounting permissions require a wider investigation.
The Bottom Line
This QuickBooks invitation scam turns a routine accounting task into an email-password request. The unexplained Adobe detour is a warning, not a step to complete.
Confirm invitations with the firm, enter through trusted account routes, and respond quickly to exposed credentials. Keep the legitimate service separate from the people impersonating it.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Community experiences
Did this happen to you?
Your experience could help someone recognize the same scam. Submit a private report for our team to review.
I experienced this tooReports are reviewed before publication. Sharing publicly is always your choice.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.