


An invoice schedule shared by the Finance Department does not look unusual in a busy workplace. The filename is specific, the notification resembles a cloud-sharing service, and the blue “View File” button promises a quick answer.
The Finance Department Invoice email scam uses that routine workflow to steal email credentials. The invoice is only a story designed to move the recipient from an unexpected message to a counterfeit webmail login.
Overview
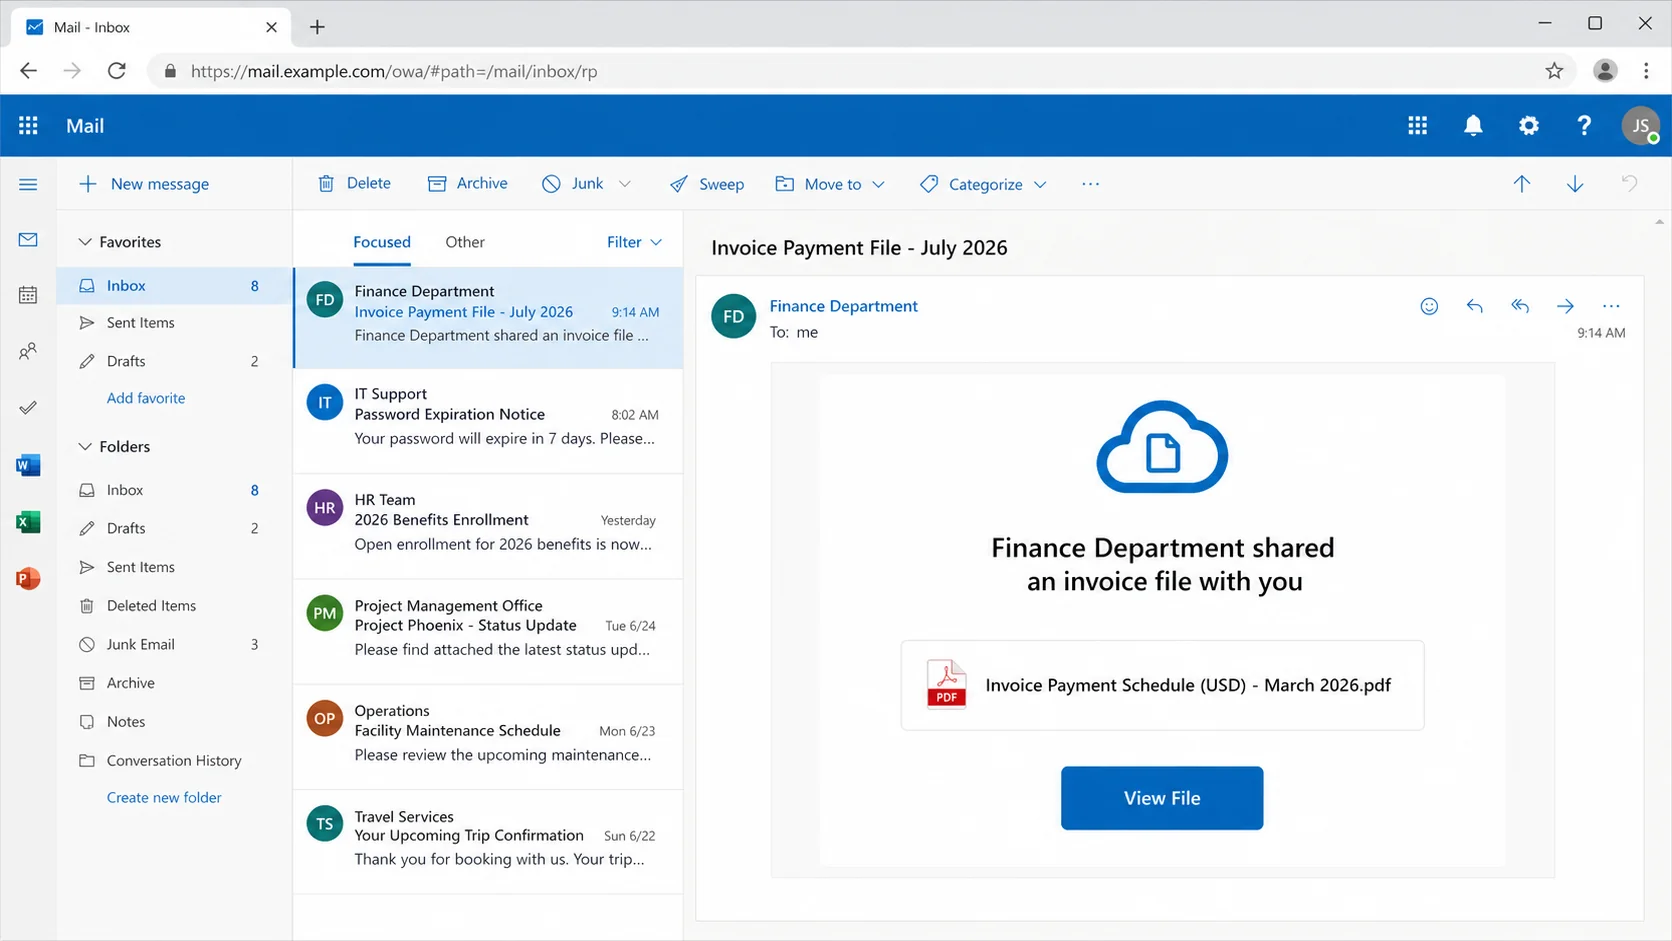
This phishing campaign impersonates a cloud file-sharing notification. An observed message used the subject “Invoice Payment File – July 2026” and claimed that a generic Finance Department had shared “Invoice Payment Schedule (USD) – March 2026.pdf.”
The button led to a fake webmail form on a website hosted with a legitimate site-building provider. The page asked for an email address and password and included a “Log in via cPanelID” option to resemble a flexible corporate mail portal.
The invoice theme fits ordinary business traffic
Accounting, purchasing, sales, and management teams exchange invoices every day. A shared payment schedule can sound important without making an outrageous promise, especially near a monthly closing date.
The sender is simply “Finance Department,” which lets the message fit many organizations. It does not need to know the actual name of the recipient’s accounting team to create a moment of doubt.
The cloud-sharing design supplies borrowed trust
File-sharing notifications often contain a document name, modification time, and one prominent action button. Criminals reproduce that familiar layout so the recipient responds to the workflow before inspecting the sender and link.
Dropbox states that official communications and login requests use its verified domains. A page on a site builder, webmail clone, or unrelated host is not made safe by a cloud icon or the phrase “Happy Dropboxing.”
The stolen inbox can support payment fraud
- Attackers can search real invoice and supplier conversations.
- They can create forwarding rules to monitor future payments.
- They can impersonate the employee from the genuine mailbox.
- They can reset passwords for connected business services.
- They can send altered bank instructions inside an existing thread.
Dropbox and any real finance department whose identity is copied are not involved. The scam abuses recognizable business processes to obtain the account access needed for a more convincing second stage.
Why Fake Invoice Notifications Are So Effective
They arrive where urgency is already normal
Invoices have due dates, approval windows, and month-end consequences. An employee may believe that opening the file quickly is part of doing the job well, not a risky exception.
Scammers do not need to threaten account deletion when a payment schedule creates its own pressure. The possibility of delaying a vendor can be enough.
Document details create a false sense of provenance
A polished filename, date, file type, and modification time look like records produced by a real platform. None of those fields proves that the file exists or that the named department uploaded it.
Every detail can be placed directly in the email’s HTML. The recipient sees a description of a file, not cryptographic proof of its origin.
The real fraud may happen after the password theft
The first page is interested in login details, not an immediate payment. That can make the message seem less financially dangerous than an email containing new bank instructions.
However, an inbox takeover gives criminals the history and authority needed for business email compromise. The FBI warns that attackers use compromised accounts and real invoice threads to redirect payments.
How the Finance Department Invoice Email Scam Works
Step 1: Attackers select employees who handle documents
Finance, accounts payable, purchasing, sales, and general office addresses are attractive targets. Their addresses may appear on company websites, professional profiles, leaked lists, or previous email chains.
The campaign can also be sent broadly. A generic Finance Department label works anywhere an employee might plausibly receive an invoice.
Step 2: The message imitates a shared-file alert
The email uses a cloud-service layout rather than attaching a real PDF. A recognizable icon, concise notification language, and prominent button make it feel automated.
The represented service name is borrowed. The From address, reply path, and button destination may have no relationship to the official provider.
Step 3: A specific invoice filename invites the click
The document name includes a currency and month, suggesting a payment schedule rather than a random file. A recipient may click simply to learn which invoices are involved.
Odd date combinations are a warning. In the observed lure, the subject, shared date, and month in the filename did not form a clear timeline.
Step 4: “View File” opens an external phishing page
The link can lead through redirects or directly to content hosted on an unrelated service. Criminals abuse legitimate hosting platforms because their domains may appear less suspicious to filters.
A legitimate platform being used as a host does not make the page legitimate. The owner of the hosting service is not the sender of the invoice.
Step 5: A generic webmail login replaces the document
Instead of seeing a PDF preview, the recipient is asked to authenticate with office email credentials. The page may show cPanel, Microsoft, Google, or neutral webmail styling.
A real Dropbox login belongs on Dropbox’s documented domain. A shared PDF also has no reason to collect the password for an unrelated corporate mailbox.
Step 6: Submitted credentials reach the attacker
The fake form records the address and password. It may display an error, reload, or send the user to a harmless page so the missing invoice looks like a technical failure.
The absence of a visible invoice does not mean nothing happened. Credential collection can finish before the redirect appears.
Step 7: The real mailbox is searched and monitored
After signing in, an intruder may search for vendors, bank details, wire instructions, contracts, tax documents, and people authorized to approve payments.
Rules can move security alerts out of view or forward selected messages externally. The attacker may wait for a high-value conversation instead of acting immediately.
Step 8: Trust is reused in a second fraud
The compromised account can request a payment, send another phishing link, or tell a supplier that banking details changed. Because the message comes from a real mailbox, ordinary sender checks may no longer help.
Criminals can also reply inside a genuine thread. The invoice lure that captured one password can therefore produce financial loss for the victim’s organization or its partners.
Red Flags in the Finance Department Invoice Email
- The sender uses a generic department name with no identifiable employee.
- The recipient was not expecting an invoice schedule or shared file.
- The From address is outside the organization and outside verified Dropbox domains.
- The subject date, file month, and modification date do not match naturally.
- The button opens a site builder, unrelated domain, or generic webmail page.
- The page asks for office email credentials before showing the PDF.
- The login offers cPanel even though the message claims to be from another service.
- The email supplies no invoice number, supplier, amount, owner, or internal case reference.
One imperfection may have an innocent explanation. The combination of an unexpected finance file, unrelated destination, and mailbox-password request is decisive.
How to Verify the Invoice Without Using the Email
Check the real sharing account
Open Dropbox or the organization’s document platform from a bookmark or manually typed address. Look for the file in recent activity, shared items, and notifications.
If the file is genuine, it should be associated with an identifiable owner inside the real service. Do not log in through the suspicious message just to test it.
Ask finance using known contact details
Contact the internal finance team through the company directory, chat system, or a known phone extension. Send a new message rather than replying to the suspicious sender.
Ask for the document name, owner, purpose, and expected platform. A legitimate colleague can confirm the request without asking you to bypass security procedure.
Confirm the supplier and invoice context
Search the accounting system for a matching supplier, amount, and invoice number. A generic payment schedule with no connection to recorded business should not move forward.
Any request that changes payment information requires out-of-band verification using a previously known number. Never rely on contact details supplied in the same request.
Report the message to the impersonated service
Dropbox advises recipients who receive suspicious shared-file notices to avoid the links and forward the complete message to its abuse address. Internal security teams should receive the original message as well.
From Credential Phishing to Business Email Compromise
Business email compromise does not always begin with a direct request for money. Stealing an employee’s mailbox can be the reconnaissance phase.
The inbox reveals who pays whom, how invoices are formatted, which words employees use, and when key staff are unavailable. An attacker can reproduce those details more convincingly than a cold impersonator.
Once a payment thread is found, the criminal may register a lookalike domain or send from the compromised account itself. A subtle change to the beneficiary account can redirect a legitimate payment.
Organizations should treat the exposure of finance-related email credentials as a potential financial incident. Waiting for evidence of a fraudulent transfer gives the attacker time to study and manipulate active transactions.
Controls That Help Businesses Stop This Attack
Use multifactor authentication that resists phishing, restrict legacy authentication, and alert on unusual sign-ins. Requiring more than a reusable password limits the value of a fake login form.
Create a clear process for shared finance documents. Employees should know which platform is used, how senders are named, and where authentic notifications appear after they sign in independently.
Require a second person and a separate communication channel for new beneficiaries or changed bank details. Email alone should never authorize a material payment change.
Monitor mailbox rules, external forwarding, suspicious OAuth grants, and large downloads. Fast detection can stop an inbox intrusion before it becomes supplier fraud.
A Simple Rule for Shared Finance Files
Treat the notification and the document as two separate things. The email only tells you that a file allegedly exists. The authenticated finance or storage system must confirm the file, its owner, and your permission to view it.
If a colleague genuinely shared a payment schedule, opening the established platform directly should lead to the same item. When the task exists only behind one email button, the sender is asking you to trust the message before the business record.
Teams can make this rule practical by keeping one approved document route and naming an owner for exceptions. Employees then have a fast safe alternative when an unusual notification arrives.
What to Do if You Have Fallen Victim to This Scam
- Close the counterfeit login. Do not submit another password or approve any authentication notification.
- Change the email password through the official provider. From a trusted device, replace it with a strong password used nowhere else.
- Revoke sessions and connected access. Remove unknown devices, apps, tokens, app passwords, delegates, and recovery methods.
- Inspect forwarding and inbox rules. Look for hidden rules that copy, delete, archive, or redirect finance-related messages.
- Notify IT and finance immediately. Provide the original email, destination, time of entry, and any multifactor prompt you approved.
- Review current payments. Verify invoices, beneficiary changes, wire instructions, and recent approvals through known contacts.
- Alert suppliers and customers when needed. Tell them to verify unusual instructions through a separate channel.
- Replace reused passwords. Prioritize accounting, storage, customer-management, payroll, and banking services.
- Check sign-in and file activity. Record unfamiliar locations, downloads, searches, sent messages, and deleted items for the investigation.
- Contact the bank if money moved. Request an urgent recall or fraud hold and preserve transaction details for law enforcement.
- Run a security scan. Malwarebytes can look for information stealers, remote-access software, or malicious extensions if the page caused any download.
- Report the lure. Send it to company security and the impersonated platform. For future browsing, AdGuard may stop access when a destination is already identified as deceptive.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Did the Finance Department really share a file?
The email alone does not establish that. Contact finance through the company directory and check the real document platform without using the link.
Does Dropbox ask for my office email password?
No unrelated page should collect it. Dropbox says private login information is requested only on its official login domain, not on a site builder or generic webmail form.
Why was the phishing page hosted on a legitimate service?
Attackers abuse site builders and cloud storage to gain reliable hosting and a familiar domain. The platform is not endorsing the content and may remove it after a report.
Am I safe if I saw the fake login but entered nothing?
The credential risk is much lower. Report the click, close the page, and check for unexpected downloads or prompts. Follow company incident procedures.
What if I entered the password twice?
Treat every entered password as compromised. A fake “wrong password” message can be used to collect multiple passwords.
Can this lead to a fraudulent invoice payment?
Yes. Access to a business inbox can expose real invoice threads and allow criminals to impersonate an employee or alter payment instructions.
The Bottom Line
The Finance Department Invoice email scam hides a credential trap behind an ordinary shared-file notification. A detailed filename and polished cloud design do not explain why an unrelated page needs the password to your entire mailbox.
Verify invoices inside the real platform and speak to finance through known channels. If credentials were submitted, secure the account and review active payments immediately, because the stolen inbox may be used for a second, more expensive fraud.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.