

Malicious software like viruses, spyware, ransomware, and other malware poses severe risks to Windows computers by infecting systems, damaging files, slowing performance, and stealing sensitive user data. Comprehensively removing viruses and malware requires specialized knowledge and proven techniques to isolate, identify, and fully erase infections before they cause further harm.
Windows 10 in October 2026: regular support ended on October 14, 2025. If you still use Windows 10, open Settings → Update & Security → Windows Update and check your Extended Security Updates enrollment. Eligible consumer devices can receive security updates through October 12, 2027. Removing malware does not replace those updates.
This in-depth guide will provide readers with expert methodology for detecting, troubleshooting, and completely ridding Windows PCs of viruses, adware, spyware, ransomware, bots, trojans, rogue security software, browser hijackers, and other malware using the step-by-step removal processes below. Follow these best practices to restore infected Windows computers to normal function.
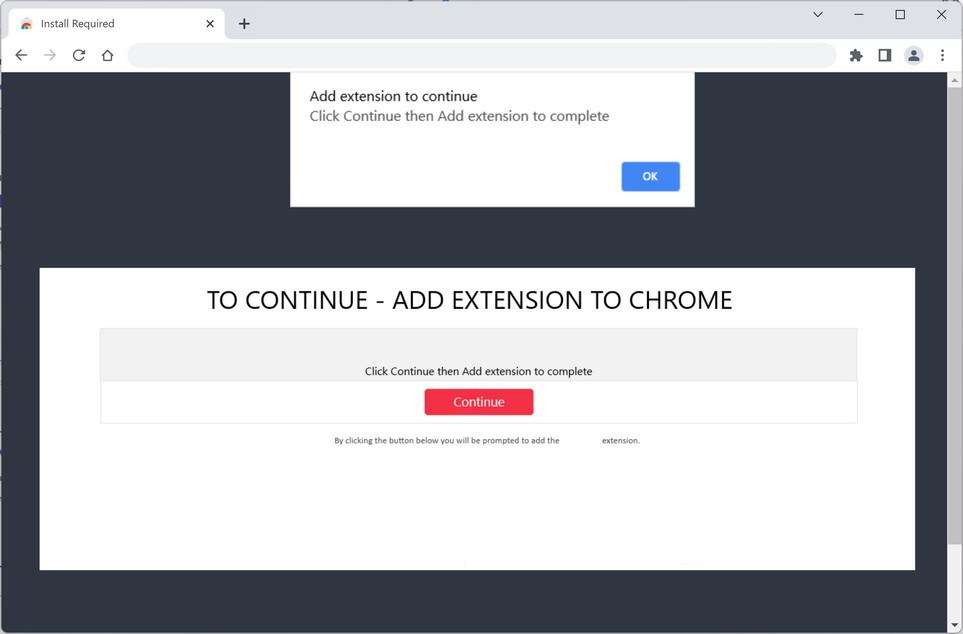
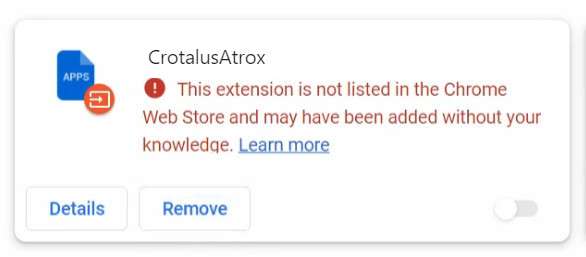
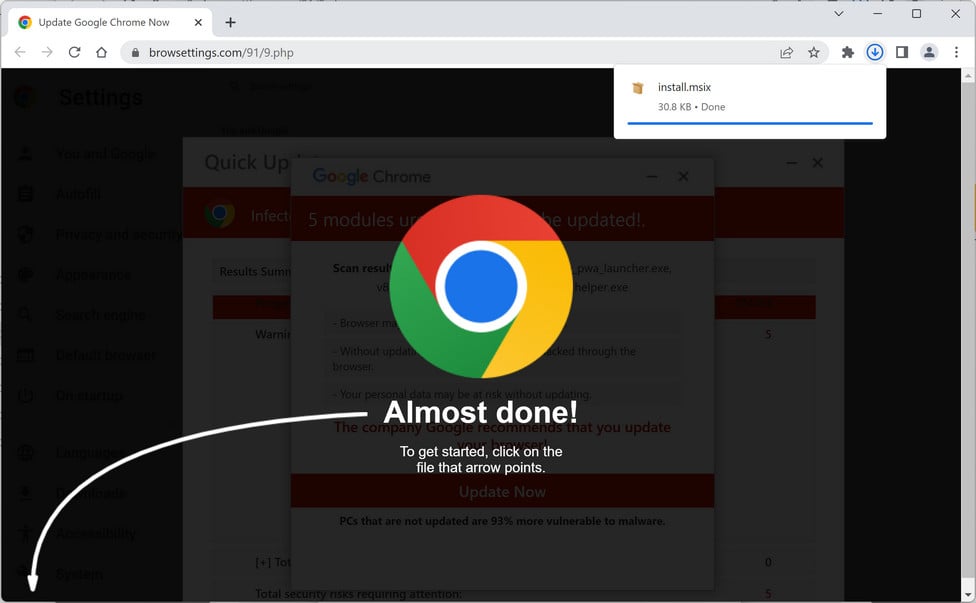
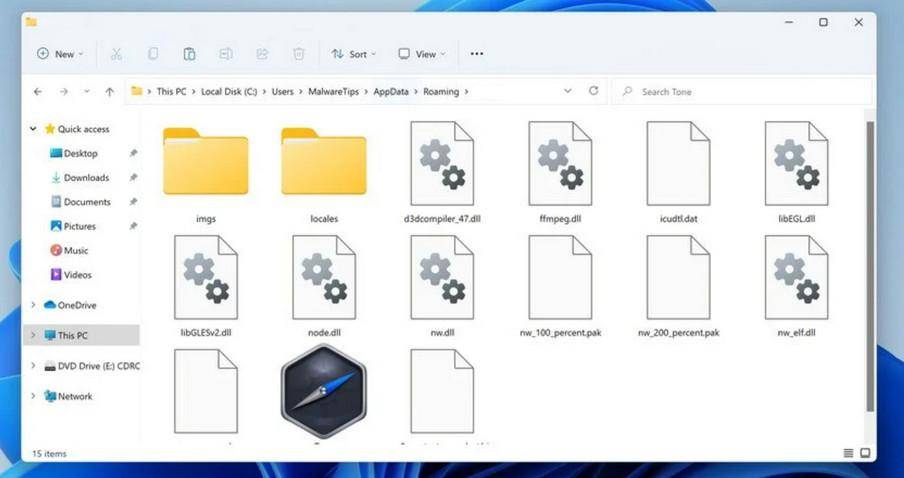
What Are Viruses and Malware?
Malware refers to various forms of malicious software that are intentionally designed to secretly access, damage or infect computers and mobile devices without the user’s consent. Malware comes in many forms, each with unique dangers and challenges when it comes to removal. Gaining a deeper understanding of the most common malware varieties that threaten Windows computers will help inform effective removal strategies.
Computer Viruses
One of the most common and familiar forms of malware are computer viruses. These are programs that spread by inserting copies of themselves into other software applications, critical system files or even the computer’s boot sector. The defining aspect of viruses is this self-replication functionality that enables them to propagate quickly from one system to another via networks, email attachments, infected storage devices and more.
Once a virus has infected a Windows computer, it can exhibit a variety of malicious behaviors such as corrupting, overwriting or even completely deleting important system files and user documents. Some viruses are designed to intentionally damage or disrupt the system in minor ways as a nuisance, while others can render entire operating systems unusable or inaccessible.
Examples of well-known Windows viruses include the Melissa virus from 1999 that spread rapidly via infected Microsoft Word documents sent over email, as well as the infamous ILOVEYOU virus that caused billions in damages by overwriting image, music and data files with copies of itself propogated through email and internet relay chat.
More sophisticated modern virus threats like Conficker and WannaCry have leveraged advanced propagation methods and even weaponized leaked NSA hacking tools to carry out wide-scale infections across the globe.
Spyware
Spyware is a form of malware whose primary function is to collect data and personal information about the user and relay it back to external intruders without the user’s consent or knowledge. Spyware modules are often bundled with free software downloads and then installed silently along with them.
Once active on a Windows computer, spyware can capture a wide range of sensitive user data including browsing history, login credentials stored in the browser, financial account numbers and personal identifying information that is transmitted back to data harvesting botnets or sold to cybercriminals. Some spyware programs even have keylogging functionality to record real-time keystrokes, capturing login passwords and other confidential info.
Because spyware operates covertly in the background gathering data, infections often go unnoticed for long periods while enormous amounts of private information gets exfiltrated. Well-known examples of Windows spyware threats include CoolWebSearch, Zbot, and keyloggers like Hawkeye that targeted banking credentials.
Ransomware
Ransomware is a more modern evolution of malware that, as the name suggests, takes user files ransom by encrypting documents, images, databases and other critical data with strong encryption algorithms. After encryption, ransomware displays demands for payment in cryptocurrency to receive the decryption keys and regain access to the files.
Some of the most damaging and widespread examples of ransomware that have affected Windows users include CryptoLocker, WannaCry, and Sodinokibi. Strong encryption may make recovery impossible without a valid key, but paying does not guarantee one. Check clean backups and verified decryptors before taking any recovery action. Ransomware can be catastrophic for businesses in particular by crippling essential data and documents.
Adware
Adware refers to malware that aggressively displays unwanted advertising content including popups, auto-playing video ads, and obtrusive banner notifications. Much of the adware targeting Windows injects these intrusive ads into web browsers in particular. However, some particularly annoying adware varietals also generate desktop pop-up notifications.
Because adware is focused on generating profits through forced ad views, oftentimes the data of infected users is tracked and sold as well to enable more targeted, personalized advertisements based on browsing habits and usage patterns. Adware strains system resources and can significantly slow down computer performance.
Examples of unwanted advertising behavior include injected ads, changed search results, and bundled browser components. Genieo was associated with unwanted Mac browser changes; it is not an example of Windows tax-preparation malware. Check the exact detection and installed component rather than treating a familiar name as a diagnosis.
Browser Hijackers
Browser hijackers are an insidious form of malware that as the name implies, hijacks web browser settings like the pre-set homepage, new tab URL, default search engine and bookmarks. Hijackers override these settings to redirect web traffic towards unwanted sites, often pages with further malware downloads or phishing scams.
Since all web activity on an infected machine is essentially redirected, browser hijackers enable cybercriminals to generate fraudulent ad revenue through forced page views or harvest entered data like credit cards and passwords via fake websites.
Some older examples of browser hijackers that plagued Windows browsers like IE and Firefox include e.xploit.in, Bahama Bot and CoolWebSearch. Modern variants continue to evolve related tactics.
Bots
Bots are programs that are covertly installed on victim computers to enlist the machine as part of a broader remote-controlled malware network called a botnet. Botnets can include thousands to millions of compromised computers under the command of a central “bot herder”.
These massive networks are leveraged to conduct all kinds of illicit activity including credential theft, distributed denial of service attacks (DDoS), spreading spam emails, mining cryptocurrency and enabling further malware uploads.
Well-known Windows botnet malware families includeZeroAccess, Kelihos, and Zeus which at its peak in 2010 controlled over 10 million infected machines. Modern bots feature advanced evasion tactics making them particularly challenging malware threats for Windows users.
Rogue Security Software
Also referred to as “scareware”, rogue security software is a highly devious form of social engineering malware that pretends to be legitimate anti-virus or anti-malware security tools. They falsely claim to detect nonexistent infections or performance issues on the victim’s machine in order to pressure the user into purchasing a “full version” of the scam software for removal of the fake issues.
Examples targeting Windows users include Rogue:Win32/FakeRean and Win32:Malware-gen which leveraged convincing interfaces and warnings to trick users into downloading malware under the guise of security software. This remains a persistent scam malware tactic.
Trojans
Trojans, or Trojan horses, are named after the deceptive wooden horse used to infiltrate Troy in ancient times. They similarly appear benign externally but contain hidden malicious functions. Trojans disguise themselves as legitimate software downloads and oftentimes even claim to have useful utilities to entice installation.
However, installed Trojans provide backdoor access to intruders, enabling remote execution of code, control and spying over the infected computer. Well-known Windows trojans include DarkComet RAT used for credential harvesting and other remote-access Trojans. Blackhole, by contrast, was an exploit kit used to deliver malware, not a Trojan family.
Modern trojans leveraging social engineering via so-called “cracked” versions of legitimate software remain ubiquitous on peer-to-peer sharing networks and torrent sites.
This overview of the most common types of viruses, spyware, adware, ransomware, bots, trojans and other malware provides Windows users key insights into how these attacks function and the dangers they pose. These insights will prove valuable when selecting removal strategies.
Malware Infection Vectors
To effectively prevent future malware infections, users must understand how malicious software initially accesses Windows computers:
Phishing Emails
Malicious email attachments or links that install malware if opened. Social engineering tricks users into enabling the infection.
Infected Websites
Websites hacked to embed malware or exploits in the code, infecting visitors through vulnerabilities in browsers and plugins.
Pirated Software
Peer-to-peer piracy networks and unauthorized download sites frequently contain malware bundled with cracked versions of software.
Contaminated Removable Drives
Malware residing on USB flash drives, external hard drives, and other removable media infects PCs upon connection and autorun.
Software Vulnerabilities
Unresolved flaws and weaknesses in operating systems and applications can enable some forms of malware to slip through and infect the system.
Network Intrusions
Malware worms propogating through networks, weak passwords enabling attacks, and other security holes that facilitate infection.
Social Engineering Manipulation
Tricking users via phone, email, or chat to voluntarily install fake “antivirus” software or remote access tools containing malware.
Staying vigilant against these vectors helps prevent malware from successfully infiltrating Windows computers in the first place. But it’s also crucial to be prepared to remove malware infections.
Signs of Malware Infection on Windows
While advanced malware works unseen in the background, most varieties eventually cause visible issues that indicate infection:
- Degradation in system performance
- Slow boot times
- Programs freezing or crashing frequently
- Unknown processes running in Task Manager
- Mysterious network activity
- Disabled security software and antivirus tools
- Modified, missing, or corrupted files
- Changes to the Windows registry
- New administrator accounts
- Shortcut files appearing on the desktop
- Popups for fake software upgrades or scans
Catching malware early before extensive damage is done requires proactively monitoring for any suspicious changes in system operation and performance. Now let’s dive into the methodology for removing detected malware.
How to Remove Malware on Windows
When viruses, spyware, ransomware, or other malware strikes a Windows PC, swift action is required to eliminate all traces of infection. Here’s how to remove all malware from Windows:
- STEP 1: Use Rkill to terminate malicious processes
- STEP 2: Uninstall malicious programs from Windows
- STEP 3: Reset browsers back to default settings
- STEP 4: Use Malwarebytes to remove Trojans and Unwanted Programs
- STEP 5: Use HitmanPro to remove Rootkits and other Malware
- STEP 6: Use AdwCleaner to remove Malicious Browser Policies and Adware
- STEP 7: Perform a final check with ESET Online Scanner
- STEP 8: Run the System File Checker (SFC) tool
- STEP 9: Run the Disk Check tool
STEP 1: Use Rkill to terminate malicious processes
In this first step, we will download and run Rkill to terminate malicious processes that may be running on your computer.
RKill is a program that was developed at BleepingComputer.com that attempts to terminate known malware processes so that your normal security software can then run and clean your computer of infections. When RKill runs it will kill malware processes and then removes incorrect executable associations and fixes policies that stop us from using certain tools.
-
Download Rkill.
You can download RKill to your computer from the below link. When at the download page, click on the Download Now button labeled iExplore.exe. We are downloading a renamed version of Rkill (iExplore.exe) because some malware will not allow processes to run unless they have a certain filename.
Download RKillOpens the BleepingComputer download page in a new tab. RKillStops malware processes so other tools can run
-
Run RKill.
After downloading, double-click the iExplore.exe icon to kill malicious processes. In most cases, downloaded files are saved to the Downloads folder.
The program may take some time to search for and end various malware programs.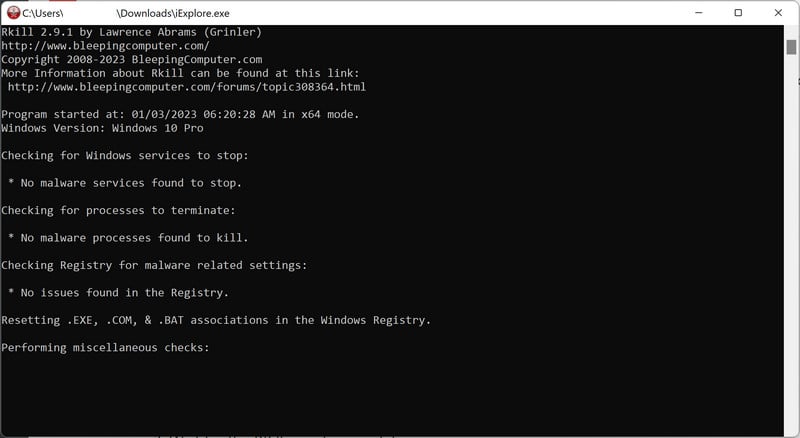
When it is finished, the black window will close automatically and a log file will open. Do not restart your computer. Proceed to the next step in this guide.
STEP 2: Uninstall malicious programs from Windows
In this second step, we will manually check if any unknown or malicious programs are installed on the computer. Sometimes adware and browser hijackers can have a usable Uninstall entry that can be used to remove them.
Use the tab for your Windows version. Windows 7 and 8 are legacy systems; some current scanners no longer support them. On Windows 10, check your Extended Security Updates enrollment after cleanup.
-
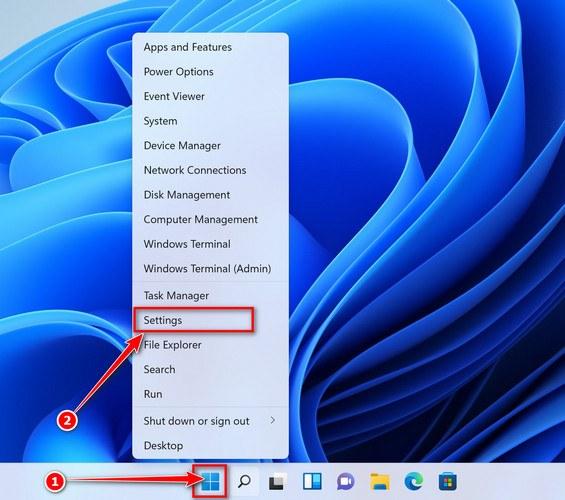
Open the Settings app
Press Windows + I on your keyboard to open Settings. Alternatively, right-click the Start button and select “Settings” from the menu.
-
Go to “Installed apps”
In the Settings window, click “Apps” in the sidebar, then select “Installed apps“.
-
Find and uninstall the malicious program
Scroll through the list of installed apps and look for anything suspicious — a program you don’t remember installing, or one with a strange or generic name.
Quick tip: click “Sort by” and choose “Install date“. Malware is usually one of the most recently installed programs, so it will appear near the top.
When you find the malicious program, click the three dots next to it and select “Uninstall“.Didn’t find any suspicious programs? That’s fine — not all infections install visible apps. Just continue with the next step in this guide. -
Complete the uninstall
Confirm by clicking Uninstall in the message box, then follow the remaining prompts.
Read each prompt carefully — some malicious programs use confusing wording or pre-ticked boxes hoping you’ll click through without looking.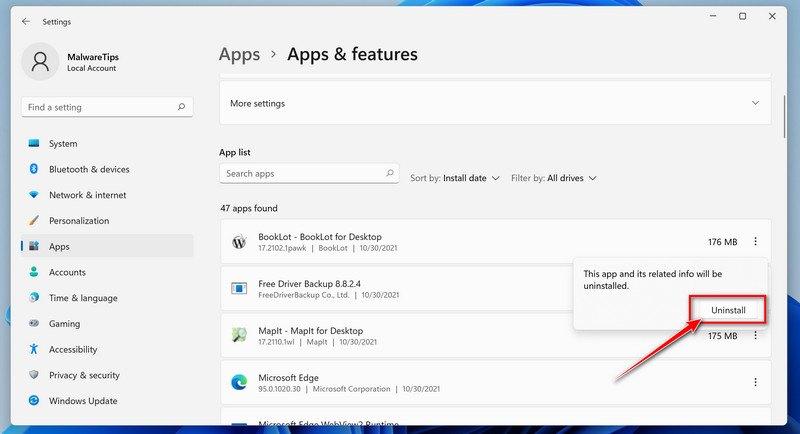
-
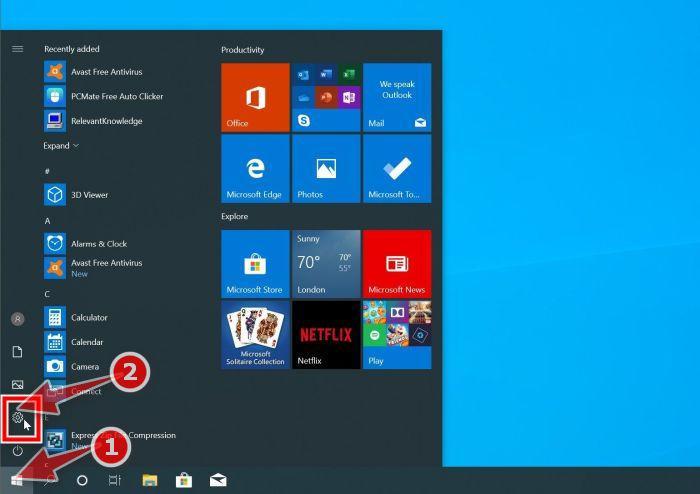
Open the Settings app
Press Windows + I on your keyboard to open Settings. Alternatively, click the Start button on the taskbar and select “Settings” (the gear icon).
-
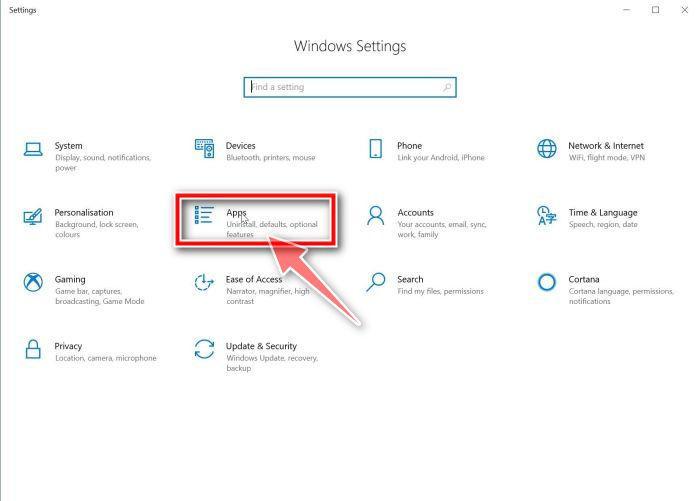
Click on “Apps”
In the “Windows Settings” window, click “Apps“. The “Apps & Features” section should open by default — if it doesn’t, select it from the list on the left.
-
Find and uninstall the malicious program
Scroll through the list of installed apps and look for anything suspicious — a program you don’t remember installing, or one with a strange or generic name.
Quick tip: click “Sort by” and choose “Install date“. Malware is usually one of the most recently installed programs, so it will appear near the top.
When you find the malicious program, click on it and select “Uninstall“.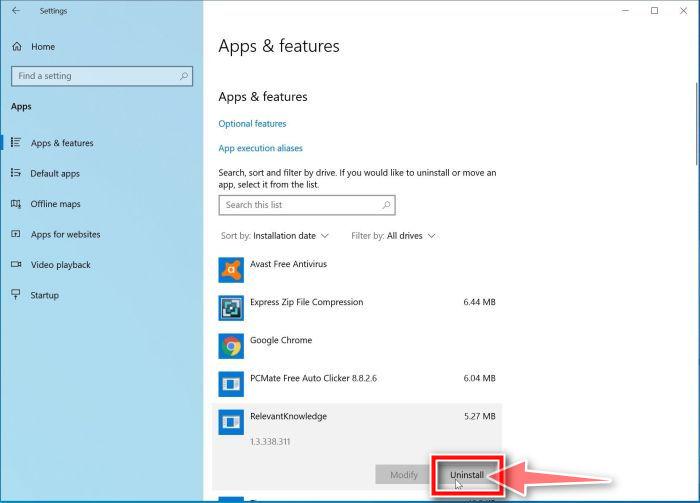 Didn’t find any suspicious programs? That’s fine — not all infections install visible apps. Just continue with the next step in this guide.
-
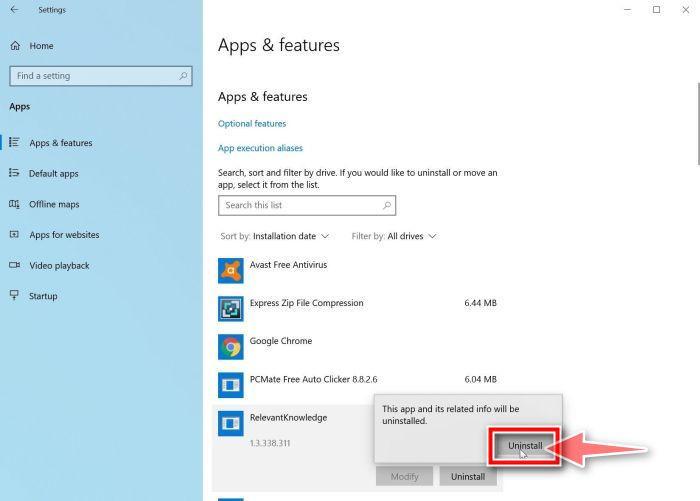
Complete the uninstall
Confirm by clicking Uninstall in the message box, then follow the remaining prompts.
Read each prompt carefully — some malicious programs use confusing wording or pre-ticked boxes hoping you’ll click through without looking.
-
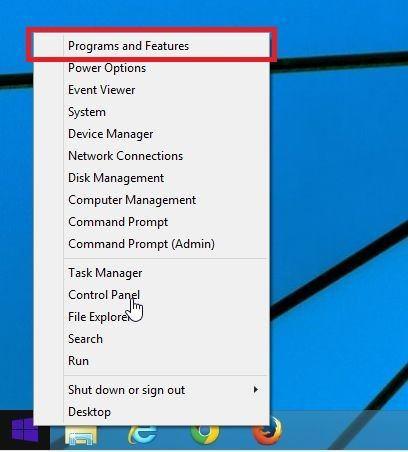
Open “Programs and Features”
Right-click the Start button in the taskbar, then select “Programs and Features“. This takes you straight to the list of installed programs.
-
Find and uninstall the malicious program
Scroll through the list of installed programs and look for anything suspicious — a program you don’t remember installing, or one with a strange or generic name. Click to highlight it, then click the “Uninstall” button.
Didn’t find any suspicious programs? That’s fine — not all infections install visible apps. Just continue with the next step in this guide.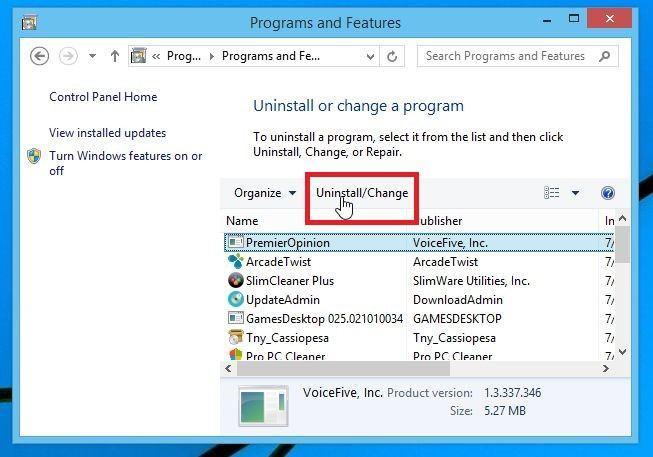
-
Complete the uninstall
Confirm by clicking Yes in the message box, then follow the remaining prompts. Read each prompt carefully — some malicious programs use confusing wording or pre-ticked boxes hoping you’ll click through without looking.
-
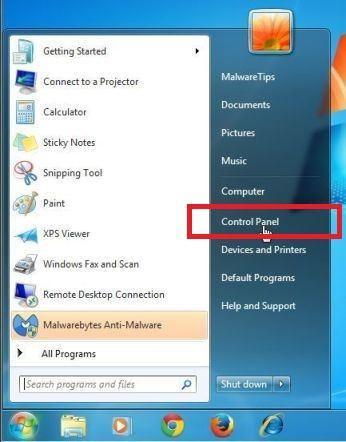
Open the Control Panel
Click the “Start” button, then click “Control Panel“.
-
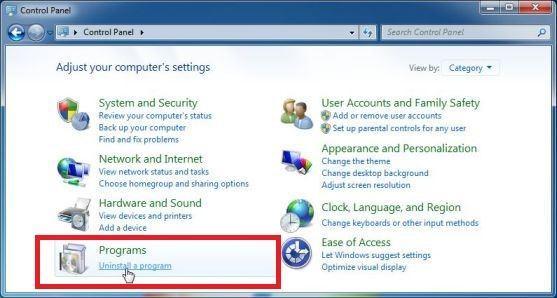
Click on “Uninstall a Program”
In the Control Panel, click “Uninstall a Program” under the Programs category.
-
Find and uninstall the malicious program
Scroll through the list of installed programs and look for anything suspicious — a program you don’t remember installing, or one with a strange or generic name. Click to highlight it, then click the “Uninstall” button.
Didn’t find any suspicious programs? That’s fine — not all infections install visible apps. Just continue with the next step in this guide.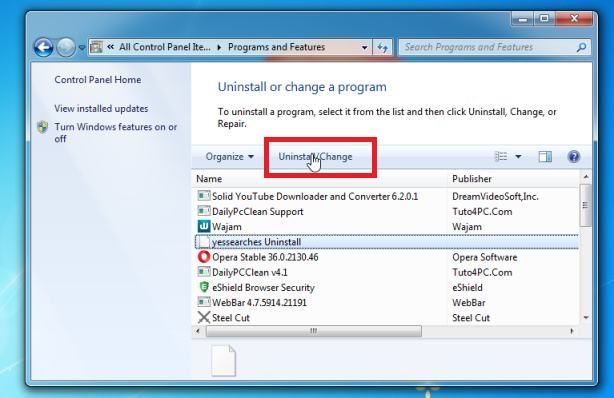
-
Complete the uninstall
Confirm by clicking Yes in the message box, then follow the remaining prompts. Read each prompt carefully — some malicious programs use confusing wording or pre-ticked boxes hoping you’ll click through without looking.
With the malicious programs removed, you’re ready for the next step in this guide.
STEP 3: Reset browsers back to default settings
In this step, we will remove spam notifications, malicious extensions, and change to default any settings that might have been changed by malware.
Please note that this method will remove all extensions, toolbars, and other customizations but will leave your bookmarks and favorites intact. For each browser that you have installed on your computer, please click on the browsers tab below and follow the displayed steps to reset that browser.
Reset Chrome for Windows to default settings
We will now reset your Chrome browser settings to their original defaults. This will reset your startup page, new tab page, search engine, and pinned tabs. It will also disable all extensions and clear temporary data like cookies. Your favorites, history, and saved passwords will not be cleared.
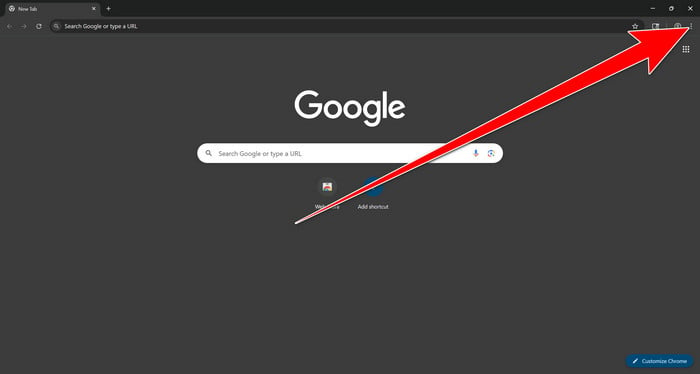
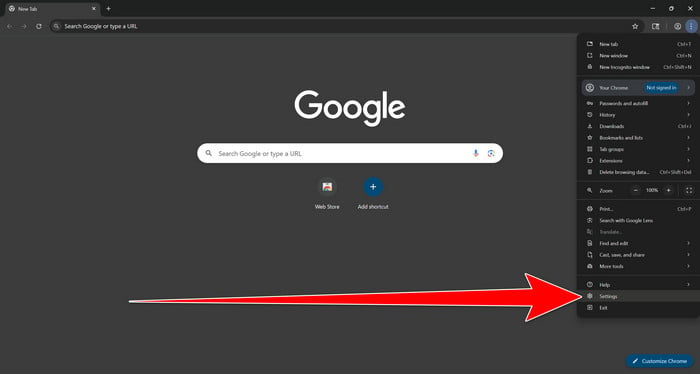
Open the Chrome menu
Open Google Chrome and click the three-dot (⋮) icon in the top-right corner.
Open Chrome Settings
Select Settings from the Chrome menu.
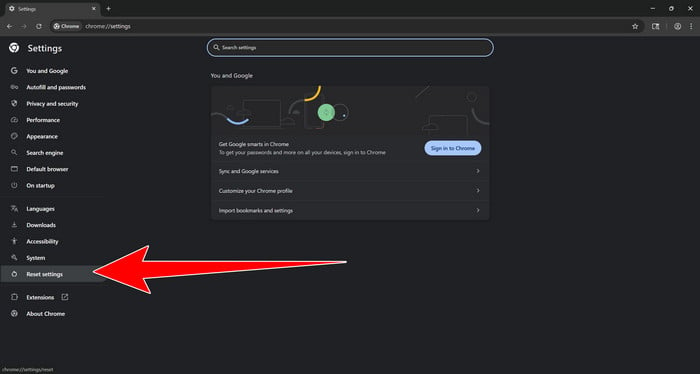
Select “Reset settings”
Look at the menu on the left side of the Settings page. Scroll down and click Reset settings.
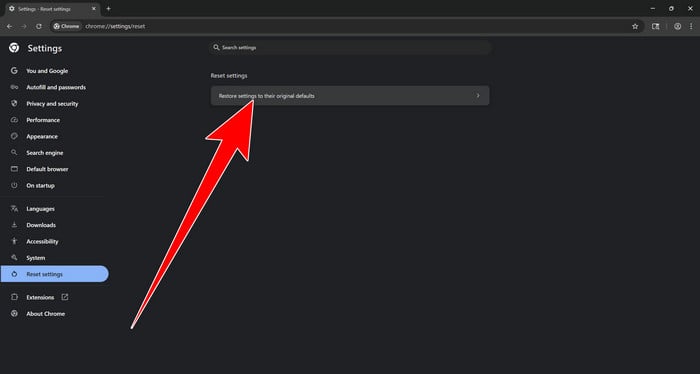
Restore Chrome’s original settings
Click Restore settings to their original defaults.
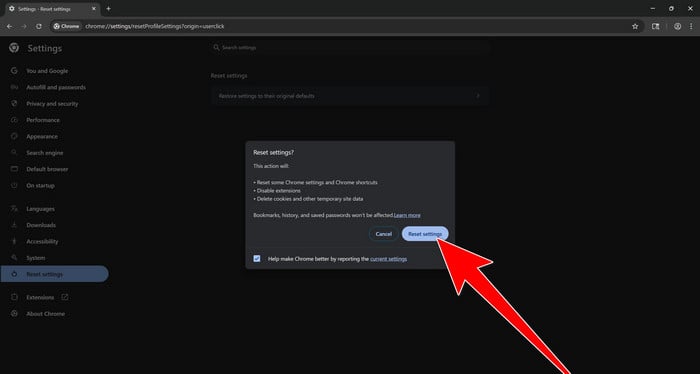
Confirm the Chrome reset
A confirmation window will appear. Click Reset settings.
This will:
- Restore the default search engine, homepage, and new tab page
- Reset startup pages and pinned tabs
- Disable installed extensions
- Clear temporary cookies and website data
Don’t worry: Chrome will not delete your bookmarks, browsing history, or saved passwords.
Restart Chrome and perform a test search. If your searches now open normally in Google, you can stop here.
If searches are still redirected through shady domains complete the additional step below.
Remove persistent search hijacker data
Only complete this step if the redirect continues after resetting Chrome.
Some browser hijackers hide inside Chrome’s local search-engine database. A standard Chrome reset may not remove this database, which is why searches can continue to pass through shady sites.
The following procedure creates a backup of the affected database and allows Chrome to build a new, clean version. This is safer and less disruptive than deleting the entire Chrome profile.
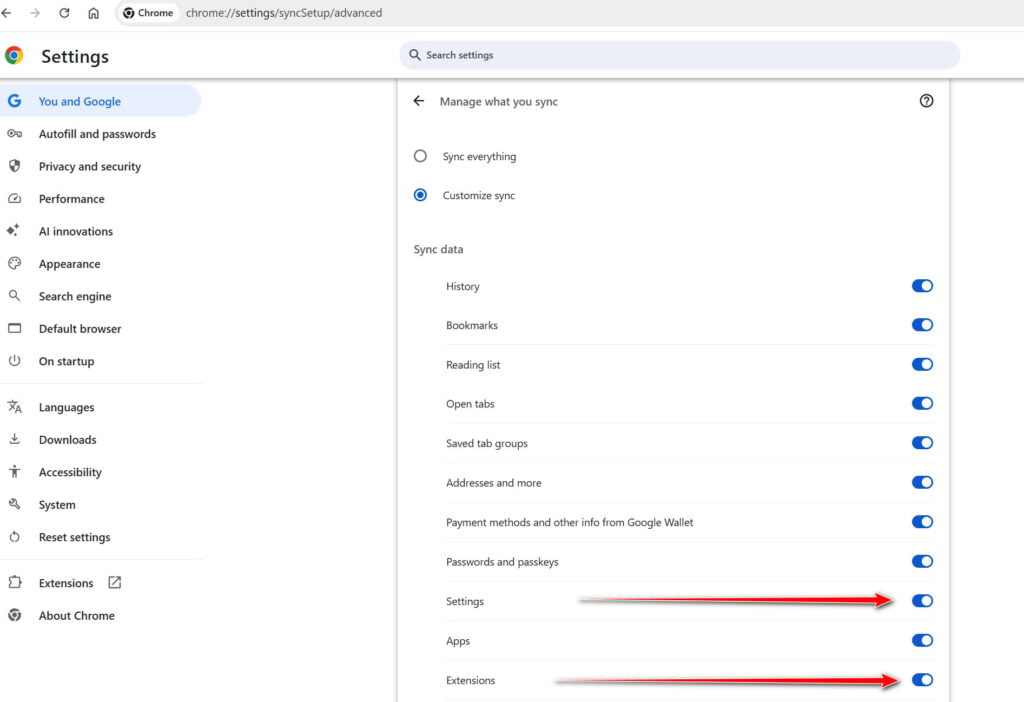
First, prevent Chrome Sync from restoring the hijacked settings:
- Open a new Chrome tab.
- Copy the following address, paste it into Chrome’s address bar, and press Enter:
chrome://settings/syncSetup/advanced - Under Manage what you sync, select Customize sync.
- Turn off Settings and Extensions.
- You can leave Bookmarks and Passwords enabled so your important data remains synchronized.
Note: Some newer Chrome versions may automatically redirect this address to the Google Account settings page. If that happens, locate the list of synchronized Chrome data and turn off Settings and Extensions there.
Now save anything you are working on and close every Chrome window.
Run the cleanup command:
- Press the Windows key on your keyboard.
- Type PowerShell.
- Open Windows PowerShell. Administrator access is not required.
- Copy the entire command shown below.
- Right-click inside the PowerShell window to paste the command, then press Enter.
- If Windows warns you about pasting multiple lines, select the option to continue.
$stamp = Get-Date -Format "yyyyMMdd-HHmmss"

Get-Process chrome -ErrorAction SilentlyContinue |
 Stop-Process -Force

$root = "$env:LOCALAPPDATA\Google\Chrome\User Data"

if (Test-Path $root) {
 $profiles = Get-ChildItem $root -Directory |
 Where-Object {
 $_.Name -eq "Default" -or
 $_.Name -match "^Profile \d+$"
 }

 foreach ($profile in $profiles) {
 foreach ($name in @(
 "Web Data",
 "Web Data-journal",
 "Web Data-wal",
 "Web Data-shm"
 )) {
 $file = Join-Path $profile.FullName $name

 if (Test-Path $file) {
 $backup = "$file.search-hijacker-backup-$stamp"
 Move-Item -LiteralPath $file -Destination $backup
 Write-Host "Backup created: $backup"
 }
 }
 }
}

Write-Host ""
Write-Host "Chrome search data has been cleaned."
Write-Host "You can now reopen Chrome."
Wait until PowerShell displays the following message:
Chrome search data has been cleaned.
You can now reopen Chrome.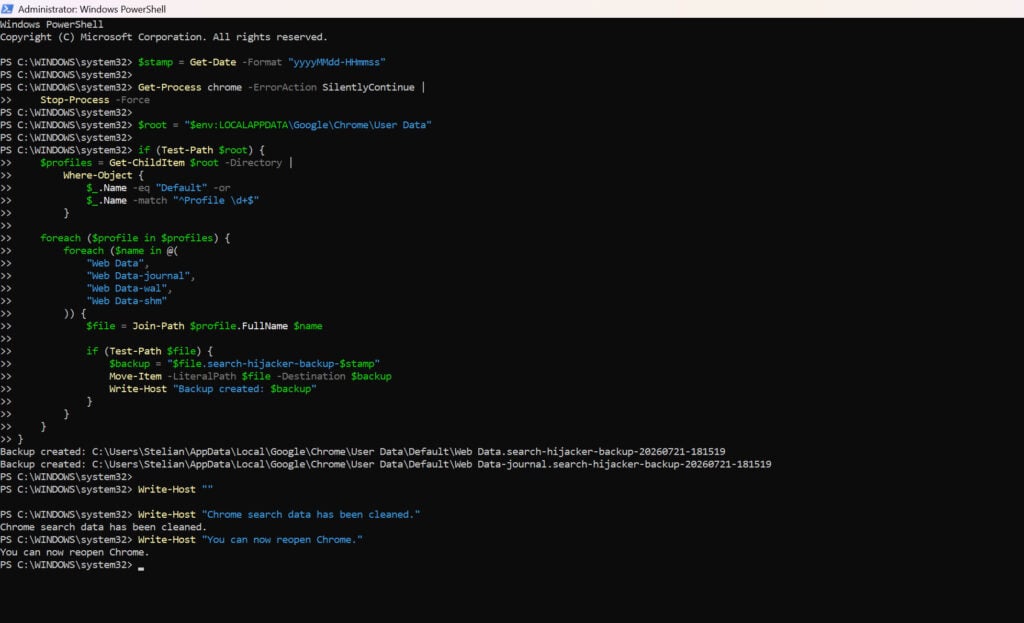
Close PowerShell and reopen Google Chrome. Chrome will automatically create a clean search database for every local profile.
Next, copy the following address, paste it into Chrome’s address bar, and press Enter:
chrome://settings/searchEnginesMake sure Google is selected as the default search engine. Test several searches from the address bar and confirm that they no longer pass through shady search engines.
Your important Chrome data is protected: the PowerShell cleanup does not remove bookmarks, saved passwords, browsing history, cookies, or installed extensions. However, it may reset locally stored Autofill addresses and form suggestions.
The original search database is not deleted. PowerShell renames it and adds
search-hijacker-backupto its filename so it can be recovered if necessary.Keep Settings and Extensions synchronization disabled while testing Chrome. Do not enable every extension at once. Enable only the extensions you recognize, one at a time, and test Chrome after each one.
If the redirect returns after enabling a particular extension, remove that extension immediately.
Reset Firefox for Windows to default settings
We will now reset your Firefox browser settings to their default. The reset feature fixes many issues by restoring Firefox to its factory default state while saving your essential information like bookmarks, passwords, web form auto-fill information, browsing history, and open tabs.
-
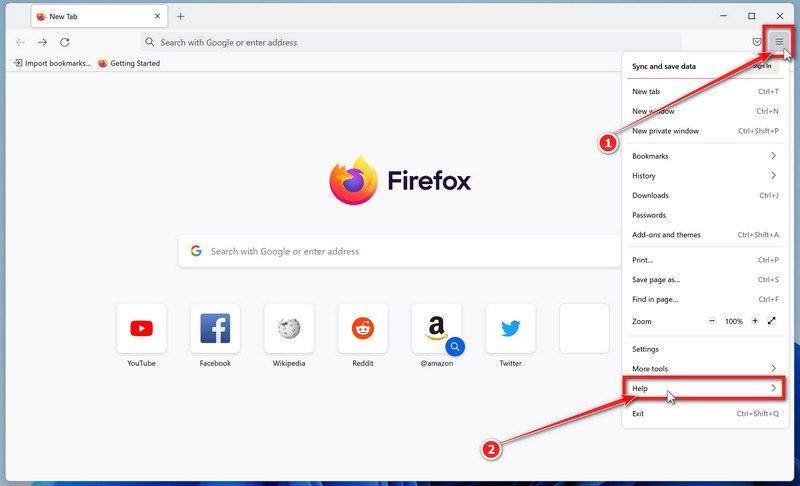
Open the Firefox menu and click “Help”
Click the three horizontal lines in the top-right corner of Firefox to open the main menu, then select “Help“.
-
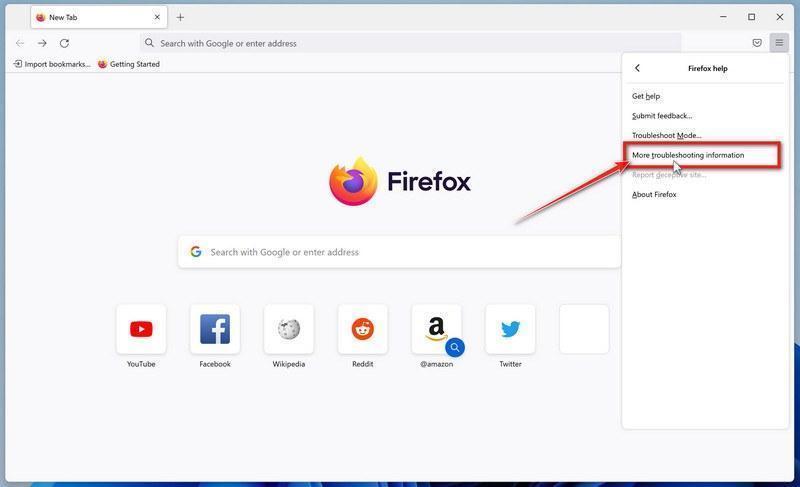
Click “More troubleshooting information”
In the Help menu, click “More troubleshooting information“.
-
Click “Refresh Firefox”
On the “Troubleshooting Information” page, click the “Refresh Firefox” button in the top-right area of the page.
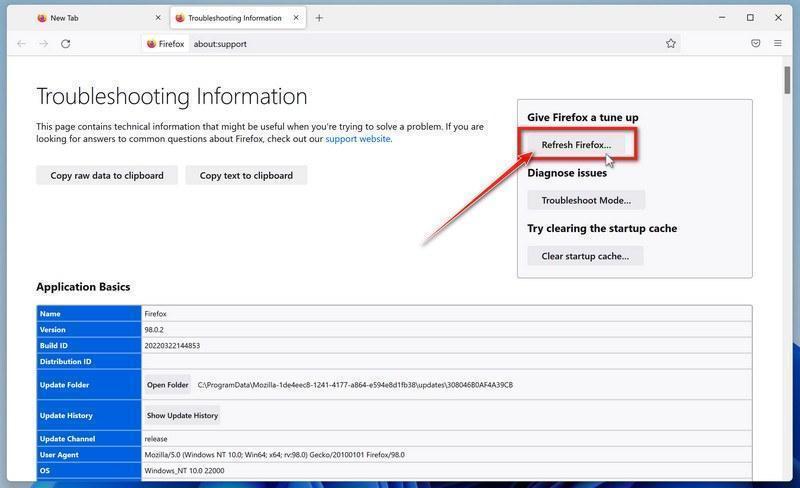
You can also type about:support in the address bar. If Refresh Firefox is missing with the newer profile manager, update Firefox; Mozilla restored that option for those profiles in version 150.
-
Confirm the refresh
In the confirmation window, click “Refresh Firefox” again. This removes extensions, themes, and customized settings — the usual hiding places for browser hijackers — while keeping your bookmarks, history, and saved passwords safe.
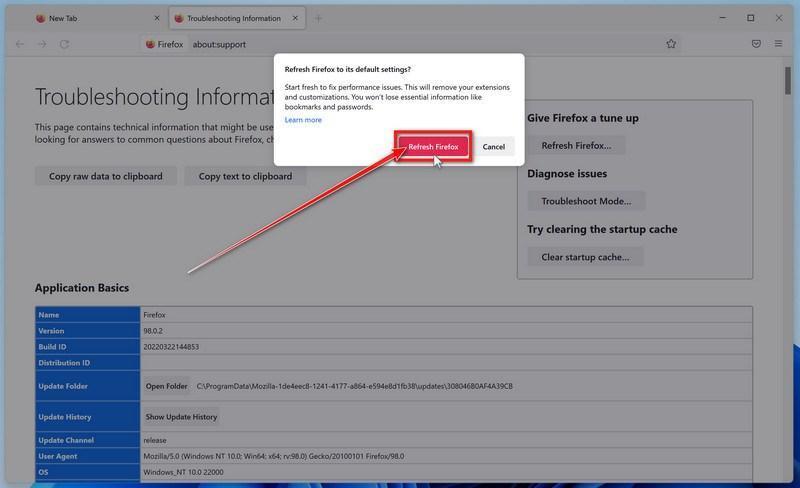
-
Click “Finish”
Firefox will close, reset itself to default settings, and reopen with a window listing the information that was restored. Click “Finish” to finish restoring your Firefox profile. Test the browser before reinstalling extensions.
About the “Old Firefox Data” folder: Firefox saves a copy of your old profile on your desktop. If something you need is missing after the reset, you can recover it from this folder. Otherwise, delete the folder — it contains sensitive data like passwords and cookies, and may also still hold the malicious files you just removed.
Reset Microsoft Edge to default settings
We will now reset your Microsoft Edge browser settings to their default. This will reset your startup page, new tab page, search engine, and pinned tabs. It will also disable all extensions and clear temporary data like cookies. Your favorites, history, and saved passwords will not be cleared.
Updated for Microsoft Edge on Windows 10 and Windows 11 — July 2026.
-
Open the Edge menu and click “Settings”
Open Microsoft Edge. In the top-right corner, click the three-dot (…) icon, then click Settings.
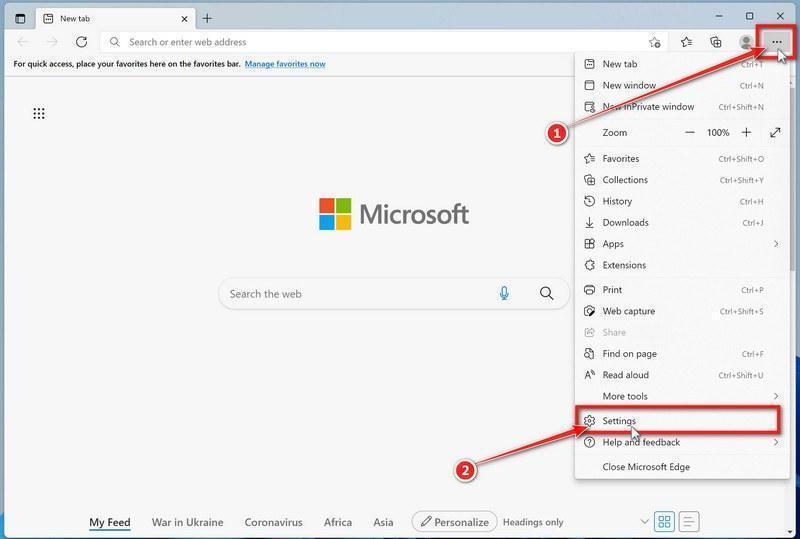
-
Prevent the unwanted settings from returning through Edge Sync
If you are signed in to Microsoft Edge, a bad setting or extension may be stored in your Microsoft account and return after the reset.
Copy the following address, paste it into the Edge address bar, and press Enter:
edge://settings/profiles/syncOn the Sync page, turn off these two options:
- Settings
- Extensions
You can leave Favorites and Passwords turned on.
If Edge says that sync is already off, simply continue to the next step.
Important: Edge Sync settings are separate for each profile. If you use more than one Edge profile, switch to each affected profile and repeat this step.
You do not need to sign out of your Microsoft account or delete the Edge profile.
-
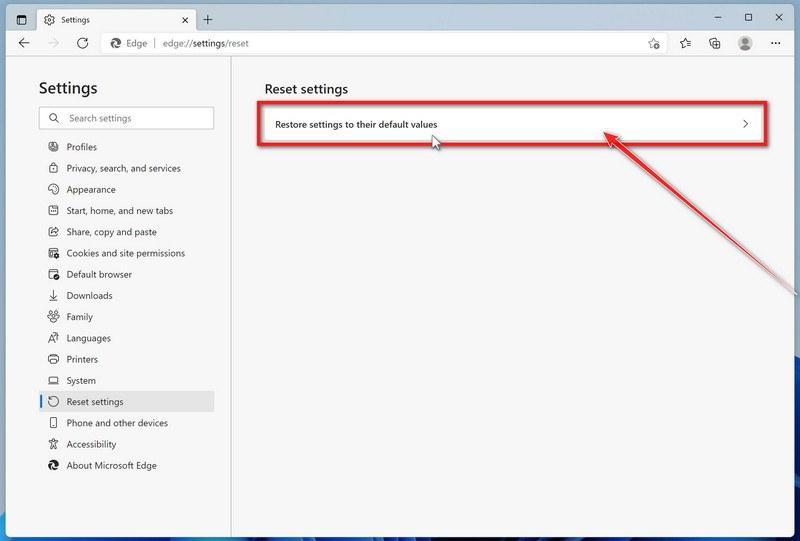
Open “Reset settings”
In the left sidebar, click Reset settings.
You can also open the reset page directly. Copy the following address, paste it into the Edge address bar, and press Enter:
edge://settings/reset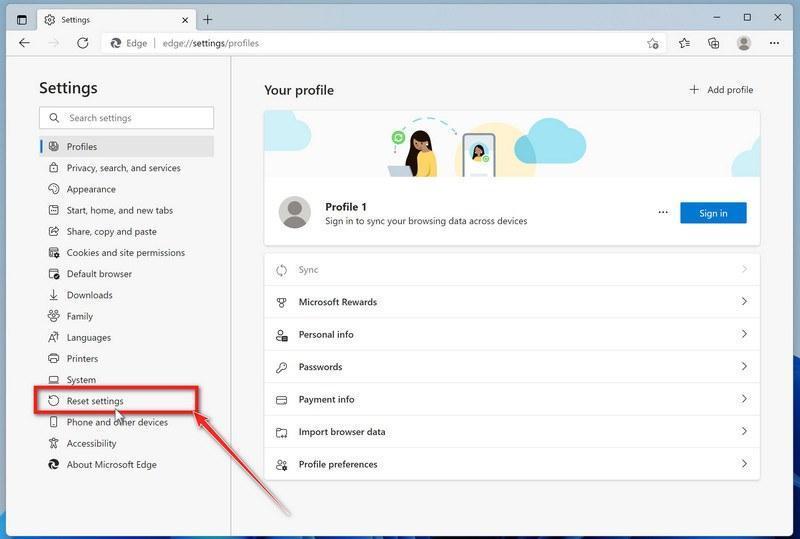
-
Click “Restore settings to their default values”
Click Restore settings to their default values.
-
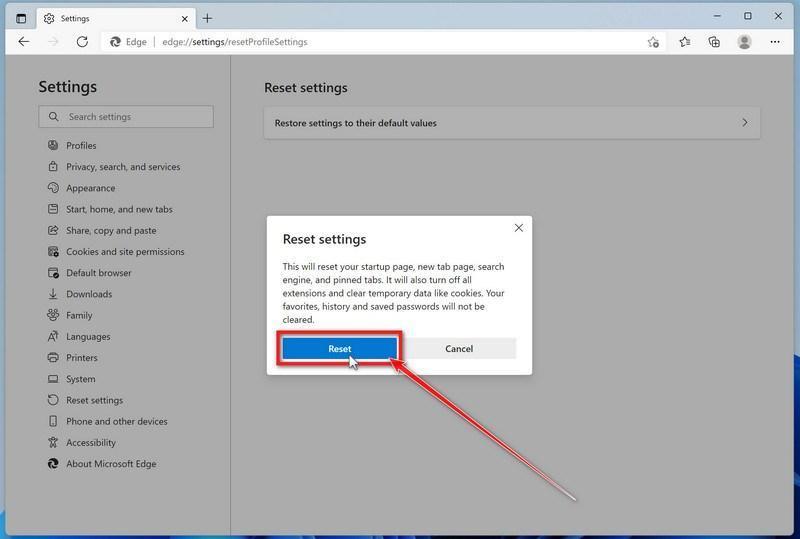
Confirm the reset
In the confirmation dialog, click Reset.
This resets the startup page, new tab page, search engine, and pinned tabs. It also disables all extensions and clears temporary site data, such as cookies.
Don’t worry: your favorites, browsing history, and saved passwords will not be deleted.
-
Check your extensions before turning them back on
Copy the following address, paste it into the Edge address bar, and press Enter:
edge://extensionsRemove any extension you do not recognize or no longer use. Pay particular attention to extensions related to search, coupons, shopping, PDF conversion, browser protection, new tabs, or video downloading.
Do not turn all extensions back on at the same time. Enable only the extensions you recognize and trust.
-
Select a trusted search engine
Copy the following address, paste it into the Edge address bar, and press Enter:
edge://settings/searchEnginesSelect Bing, Google, DuckDuckGo, or another search provider you trust and make it the default.
Remove any unknown search engines, especially providers with strange names or addresses that you did not add yourself.
Restart Edge and perform a search from the address bar. If searches are no longer redirected, you can stop here.
-
If the redirect remains, clean the corrupted search data without deleting the Edge profile
Use this additional step only if Edge continues to redirect searches after the normal reset.
This optional repair renames the Web Data database in one affected Edge profile. It may reset form-fill information, saved addresses, and custom search engines. Back up the profile first. Favorites, passwords, and browsing history are stored separately, but do not use a database repair as your first troubleshooting step.
Before continuing: save anything you are working on because the command will close Microsoft Edge.
Before closing Edge, open edge://version in the affected profile and copy its Profile path. The command asks for that path and checks it is inside Edge’s profile folder. Do not select another person’s profile or paste a folder suggested by an unverified caller.
- Open the Windows Start menu.
- Type PowerShell.
- Open Windows PowerShell. Administrator access is not required.
- Copy the entire command below.
- Paste it into PowerShell and press Enter.
$stamp = Get-Date -Format "yyyyMMdd-HHmmss"
$root = Join-Path $env:LOCALAPPDATA "Microsoft\Edge\User Data"

Get-Process -Name msedge -ErrorAction SilentlyContinue |
    Stop-Process -Force -ErrorAction SilentlyContinue

Start-Sleep -Seconds 2

if (-not (Test-Path -LiteralPath $root)) {
    Write-Host "The Microsoft Edge profile folder was not found:"
    Write-Host $root
    return
}

$profilePath = Read-Host "Paste the affected Profile path from edge://version"
$profilePath = [System.IO.Path]::GetFullPath($profilePath.Trim().Trim('"'))
$profileParent = [System.IO.Path]::GetDirectoryName($profilePath.TrimEnd('\'))
if ($profileParent -ne [System.IO.Path]::GetFullPath($root)) {
    Write-Warning "The selected folder is not a direct Edge profile folder. No files were moved."
    return
}
$profiles = @(Get-Item -LiteralPath $profilePath -ErrorAction Stop)
$movedFiles = 0

foreach ($profile in $profiles) {
    foreach ($name in @(
        "Web Data",
        "Web Data-journal",
        "Web Data-wal",
        "Web Data-shm"
    )) {
        $file = Join-Path $profile.FullName $name

        if (Test-Path -LiteralPath $file) {
            $backup = "$file.search-reset-backup-$stamp"

            try {
                Move-Item -LiteralPath $file -Destination $backup -ErrorAction Stop
                Write-Host "Cleaned: $($profile.Name)\$name"
                $movedFiles++
            }
            catch {
                Write-Warning "Could not clean: $file"
            }
        }
    }
}

Write-Host ""

if ($movedFiles -gt 0) {
    Write-Host "Microsoft Edge search data has been cleaned." -ForegroundColor Green
    Write-Host "You can now reopen Microsoft Edge."
}
else {
    Write-Host "No Edge search database files were found." -ForegroundColor Yellow
}
The command does not permanently delete the original files. It renames them as backup files, and Edge creates a clean search database when it starts again.
Note: this additional cleanup may also reset saved form-fill suggestions, saved addresses, and manually added search engines. It does not delete favorites, passwords, or browsing history.
-
Reopen Edge and test the browser
Open Microsoft Edge again, visit edge://settings/searchEngines, and select your preferred search engine.
Perform several searches from the address bar to confirm that the redirect is gone.
Keep synchronization for Settings and Extensions turned off until you are certain that the computer and extensions are clean. If you enable them again, turn them on one at a time and test Edge after each change.
-
If Edge still redirects your searches
Open edge://policy. If this is your personal computer and Edge displays unknown policies such as ExtensionInstallForcelist or DefaultSearchProvider, the hijacker may be installed outside the browser profile.
In that situation, continue with the next malware-removal steps and run a complete antivirus scan. If the computer belongs to a company or school, contact its IT administrator before changing any policies.
Reset Internet Explorer to default settings
We will now reset your Internet Explorer browser settings to their default. You can reset Internet Explorer settings to return them to the state they were in when Internet Explorer was first installed on your computer.
Legacy Internet Explorer only: the retired desktop app is unavailable on many Windows 10 PCs and is not included with Windows 11. Skip this tab if you use Edge. Resetting Edge and configuring IE mode are separate procedures.
-
Go to “Internet Options”.
Open Internet Explorer, click on the gear icon in the upper-right part of your browser, then select “Internet Options“.
If Internet Explorer will not open, press Windows + R, type inetcpl.cpl, and press Enter. Continue only if the Advanced tab actually has a Reset button. Do not reinstall an obsolete browser to obtain it.
-
Select the “Advanced” tab, then click “Reset”
In the “Internet Options” dialog box, select the “Advanced” tab, then click on the “Reset” button.
-
Click on “Reset”.
In the “Reset Internet Explorer settings” section, select the “Delete personal settings” checkbox, then click on the “Reset” button.
-
Click on “Close”.
When Internet Explorer has completed its task, click on the “Close” button in the confirmation dialogue box.
Close your browser and then you can open Internet Explorer again.
STEP 4: Use Malwarebytes to remove Trojans and Unwanted Programs
In this next step, we will install Malwarebytes to scan and remove any infections, adware, or potentially unwanted programs that may be present on your computer.
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
Current installers may offer Browser Guard, a trial, or a paid plan. Read each screen; use Skip for optional offers you do not want. Manual Windows scans and quarantine remain available in the free version.
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Choose the scan type and optional rootkit check
Start with the normal Threat Scan. For an additional rootkit check, click the three dots on the Scanner tile, choose Advanced Scan, then Custom Scan.
In the Custom Scan options, enable Scan for rootkits and select the entire C:\ system drive. Click Start Custom Scan when you have reviewed the remaining options. This option is unavailable on Windows ARM devices; do not change Windows security settings to make it appear.
Run the Custom Scan if you selected it. Otherwise, return to the Dashboard and follow the Threat Scan steps below. You do not need rootkit scanning enabled to run a normal scan.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
A Threat Scan checks memory, startup items, the registry, and common malware locations; it does not inspect every file on every drive. Allow it to finish. Use a Custom Scan if you also need to check a particular drive or folder.

-
Quarantine the Detected Threats
When the scan finishes, review the detected items and leave the threats you want removed selected. Click Quarantine. If you are unsure about a detection, save the report and ask for help before excluding it.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

STEP 5: Use HitmanPro to remove Rootkits and other Malware
In this fifth step, while the computer is in normal mode, we will download and run a scan with HitmanPro to remove Trojans, rootkits, and other malicious programs.
HitmanPro is a second-opinion scanner designed to check for threats your usual antivirus may have missed. It examines suspicious files and uses cloud analysis from several security labs, including SophosLabs. An internet connection is needed for that cloud check.
Scanning is free. Removing detected threats requires an eligible one-time 30-day trial or a paid license. If this computer already used its trial, do not expect another free activation; the purchase screen shows the current price.
-
Download HitmanPro
Click the button below to download HitmanPro. Remember — the scan is free, so you have nothing to lose by checking your PC.
Download HitmanProFree scan. Removal requires an eligible 30-day trial or a paid license. Opens the official HitmanPro page in a new tab. HitmanProSecond-opinion malware scanner from Sophos
-
Install HitmanPro
When the download finishes, open your Downloads folder and double-click the file: “hitmanpro.exe” on 32-bit Windows, or “hitmanpro_x64.exe” on 64-bit Windows.
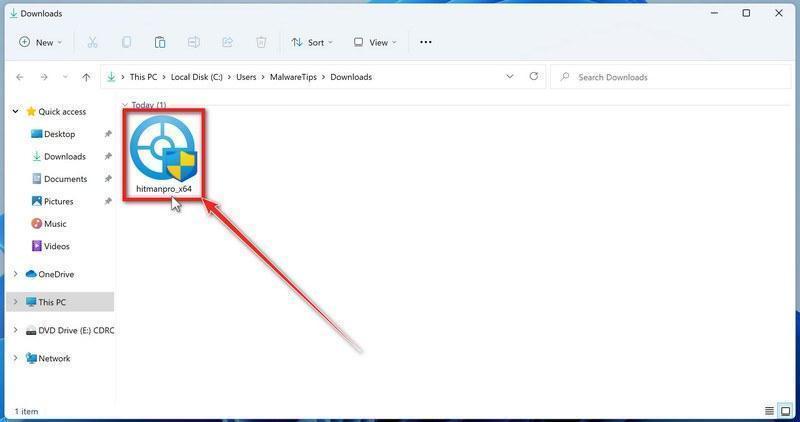
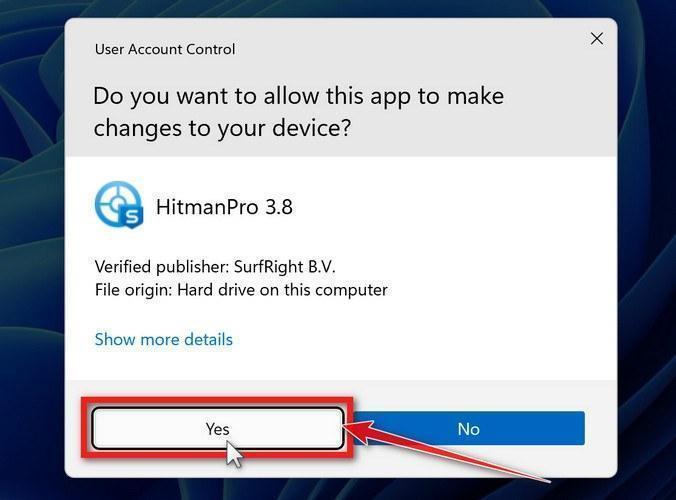
If a User Account Control pop-up asks whether HitmanPro can make changes to your device, click “Yes” to continue.
-
Follow the On-Screen Prompts
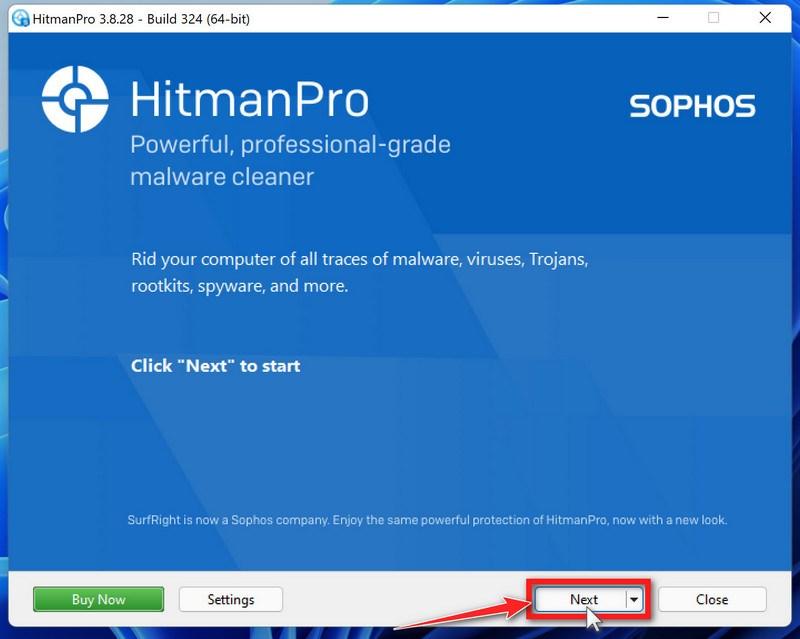
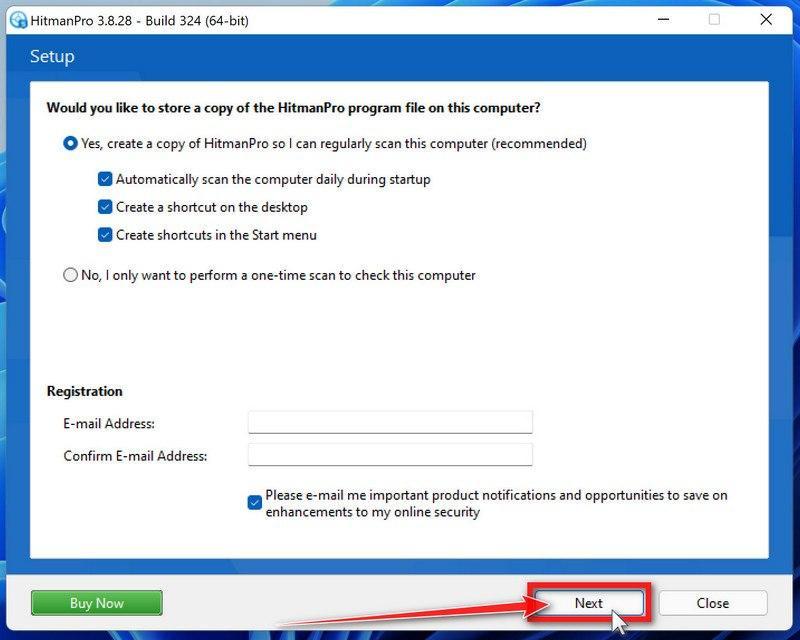
On the HitmanPro start screen, click “Next” to begin the system scan. No lengthy setup required — it goes straight to work.
-
Wait for the Scan to Finish
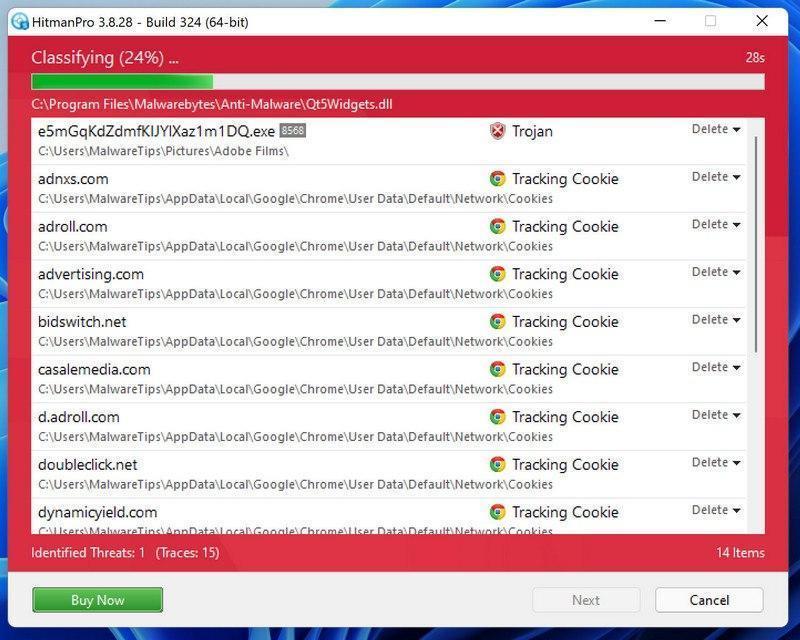
HitmanPro will now check your computer for malicious programs. This usually takes just a few minutes thanks to its cloud-based scanning.
-
Review the Results and Click “Next”
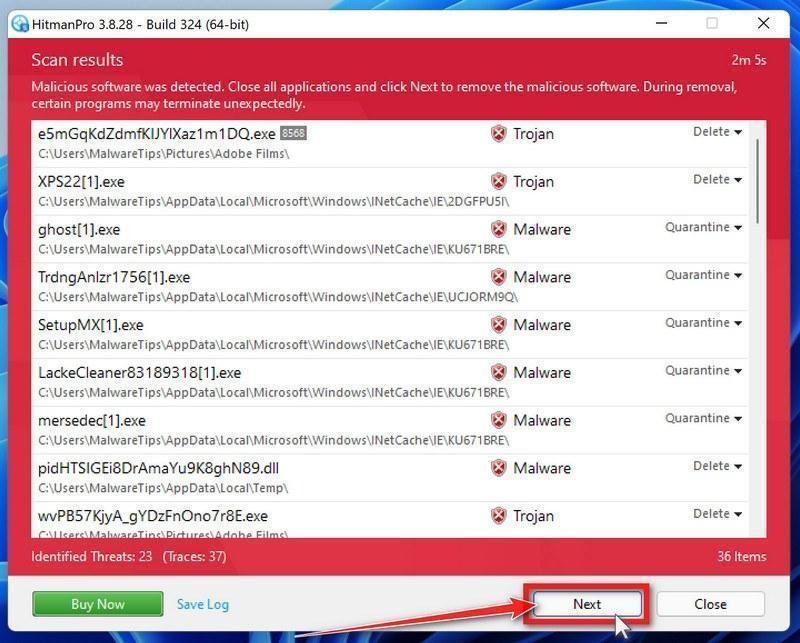
When the scan is done, HitmanPro will show you everything it found. Click “Next” to remove the detected threats.
-
Click “Activate Free License”
If the trial is available on this computer, click Activate free license and follow the activation prompts. If it is unavailable, use an existing paid license or keep the report for assistance; do not buy through an unexpected pop-up.
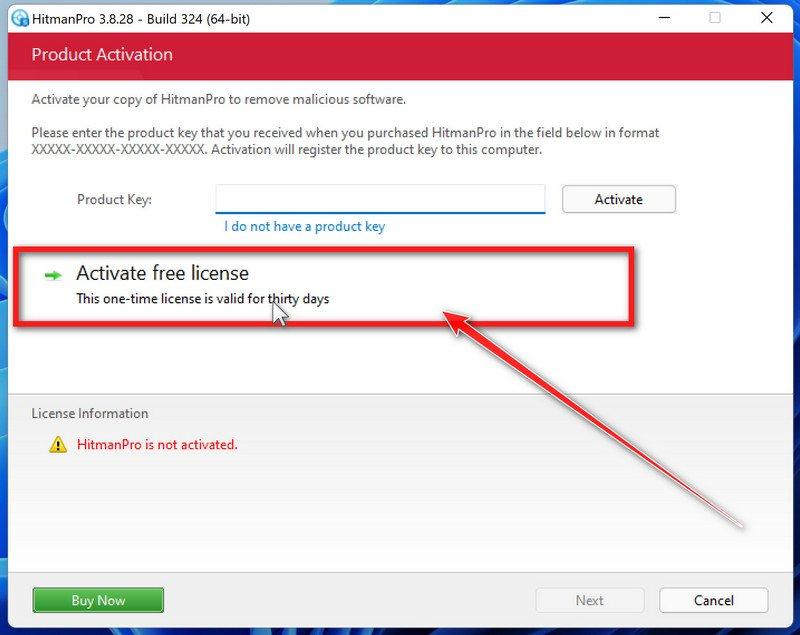
When the removal is complete, HitmanPro will show a summary of everything it cleaned. Click Next, then click Reboot if prompted. If there’s no reboot prompt, just click Close and check whether the original symptoms have stopped. A clean scan cannot rule out every threat.
STEP 6: Use AdwCleaner to remove Malicious Browser Policies and Adware
In this next step, we will use AdwCleaner to remove malicious browser policies and unwanted browser extensions from your computer.
AdwCleaner is a free on-demand scanner that specializes in adware, browser hijackers, and unwanted toolbars — the exact threats that mainstream antivirus programs often miss. It also includes tools that repair the damage malware leaves behind, like hijacked browser settings and malicious policies. It’s a quick scan that’s well worth running.
-
Download AdwCleaner
Click the button below to download AdwCleaner — it’s free, portable, and requires no installation.
Download AdwCleanerOpens the official download page in a new tab. Malwarebytes AdwCleanerRemoves adware and unwanted programs at no cost
-
Run AdwCleaner
Open your Downloads folder and double-click the file named “adwcleaner.exe“. There’s no installation — the program starts right away.
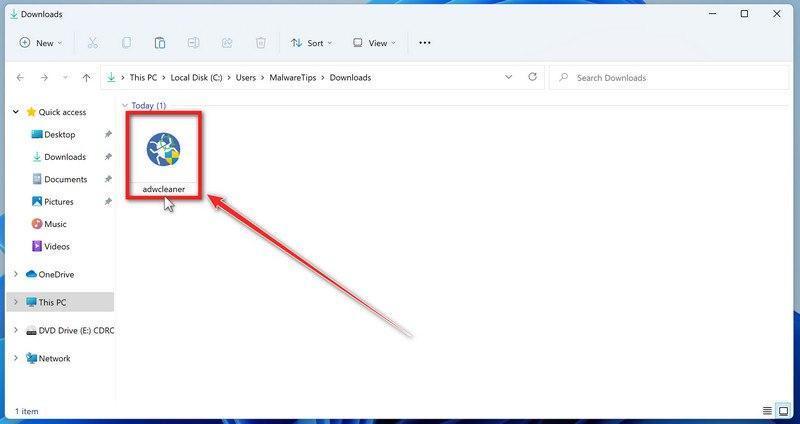
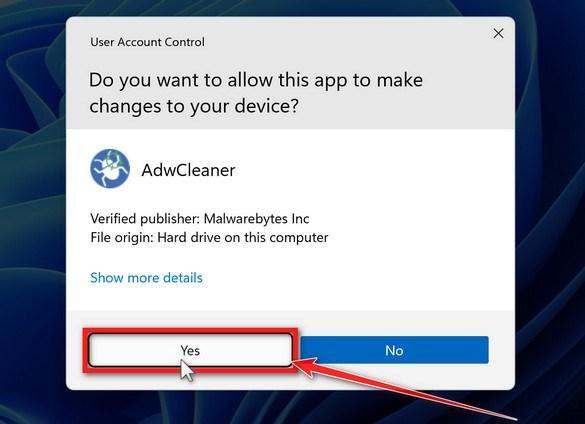
If Windows asks whether you want to allow AdwCleaner to run, click “Yes“. When the license agreement appears, click I agree to continue.
-
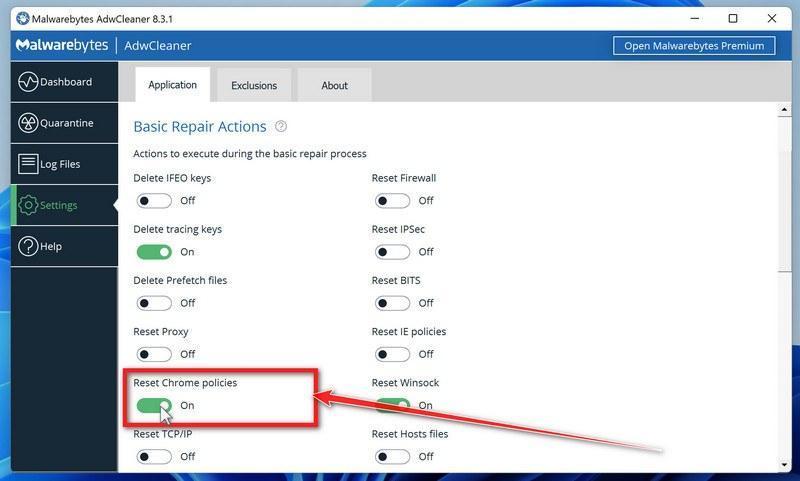
Check whether a Chrome policy reset is needed
Leave policy resets off for an ordinary scan. On a personal PC with confirmed unwanted Chrome policies, open Settings and enable Reset Chrome policies only if needed. On a work or school device, ask its administrator first.
-
Start the Scan
Return to Dashboard and click Scan Now.
-
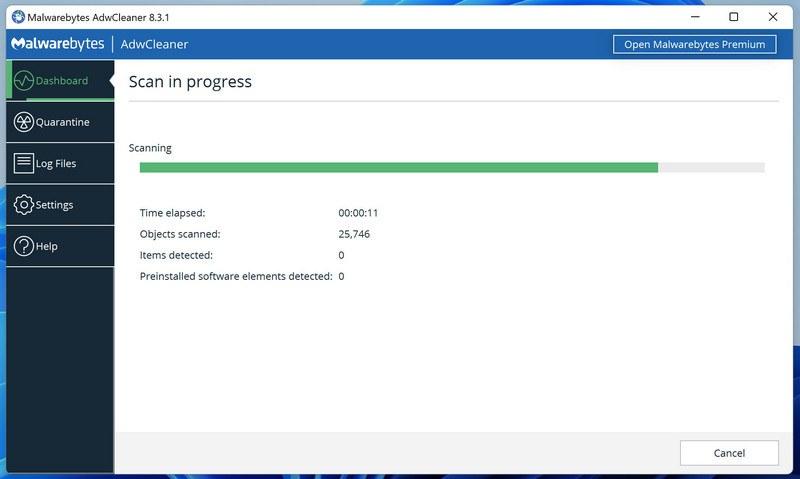
Wait for the Scan to Finish
AdwCleaner will now check your computer for adware and other malware. This usually takes only a few minutes — it’s one of the fastest scanners around.
-
Quarantine the Detected Threats
Review the detected adware and potentially unwanted programs, select the items to remove, and click Next. If a separate preinstalled-software list appears, review it too, then click Quarantine. Leave programs you intentionally use unselected.
-
Click “Continue” to Finish the Cleanup
Save any open work first — AdwCleaner needs to close your open programs before it can clean. When you’re ready, click the “Continue” button.
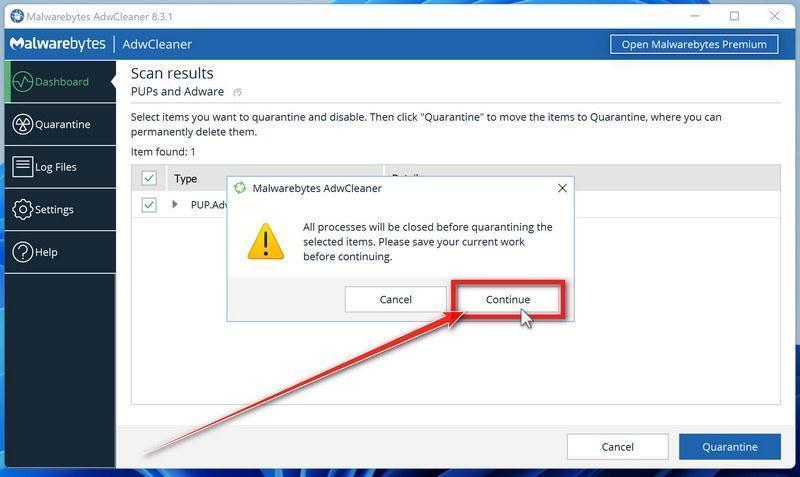
AdwCleaner quarantines the selected items. Restart when prompted, then review the cleanup log. Click Skip Basic Repair to finish; use Run Basic Repair only when a support agent has instructed you to do so.
STEP 7: Perform a final check with ESET Online Scanner
This step involves installing and running a scan with ESET Online Scanner to check for any additional malicious programs that may be installed on the computer.
ESET Online Scanner is a free second-opinion scanner for Windows. It offers a thorough check for threats other scans may have missed. Let it update before scanning, and use the final report to see what it found and whether cleanup succeeded. A clean result is useful evidence, not a guarantee that no malware remains.
-
Download ESET Online Scanner
Click the button below to download ESET Online Scanner.
Download ESET Online ScannerOpens the official download page in a new tab. ESET Online ScannerFree one-time malware scan from ESET
-
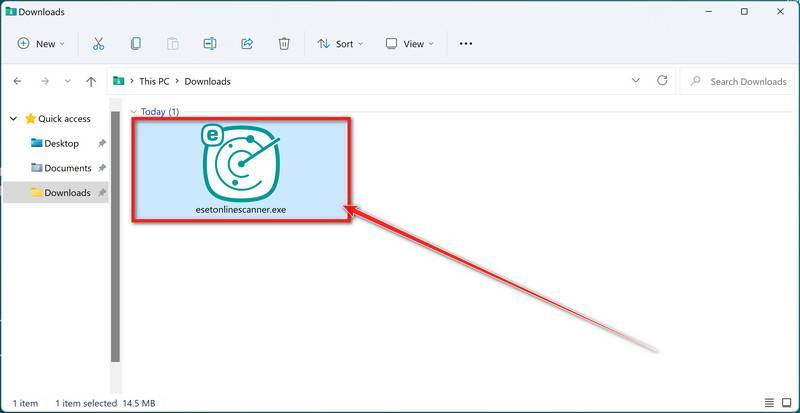
Run the Installer
When the download finishes, open your Downloads folder and double-click “esetonlinescanner.exe“.
-
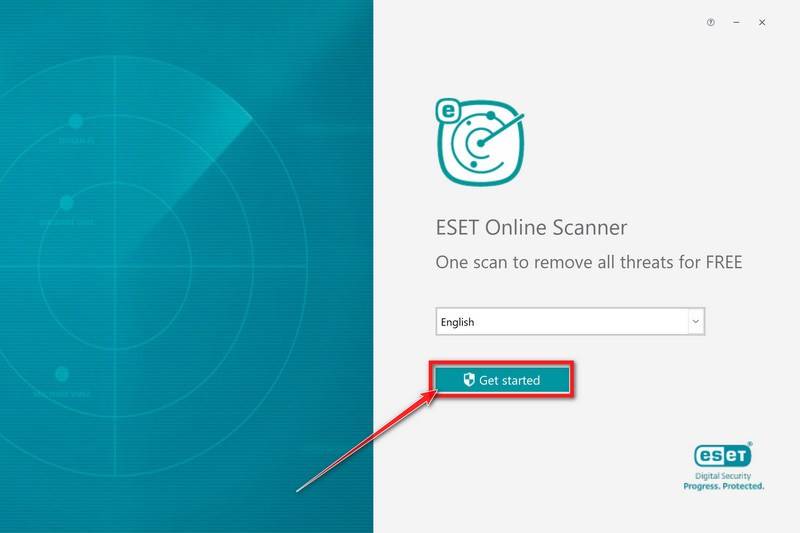
Install ESET Online Scanner
On the start screen, select your language from the drop-down menu and click Get started.
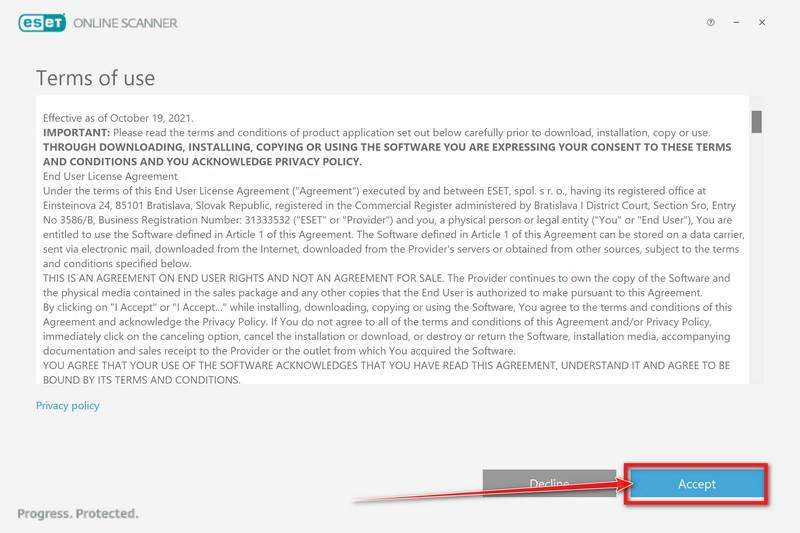
On the Terms of use screen, click Accept.
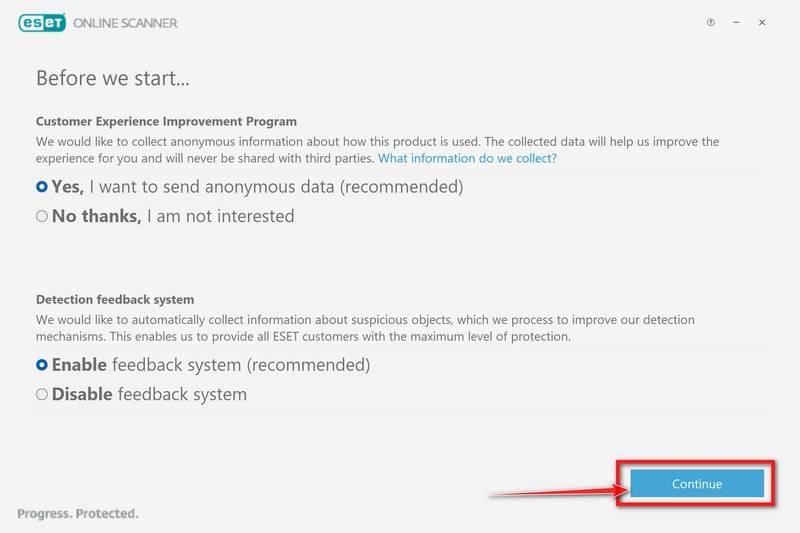
Choose your preferences for the Customer Experience Improvement Program and the Detection feedback system (either choice is fine), then click Continue.
-
Start a Full Scan
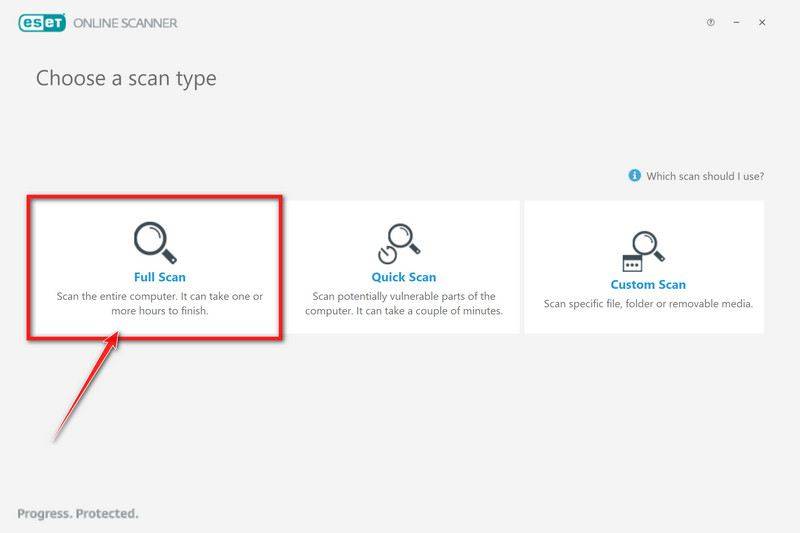
Click Full Scan — this checks your entire computer, not just the common hiding spots.
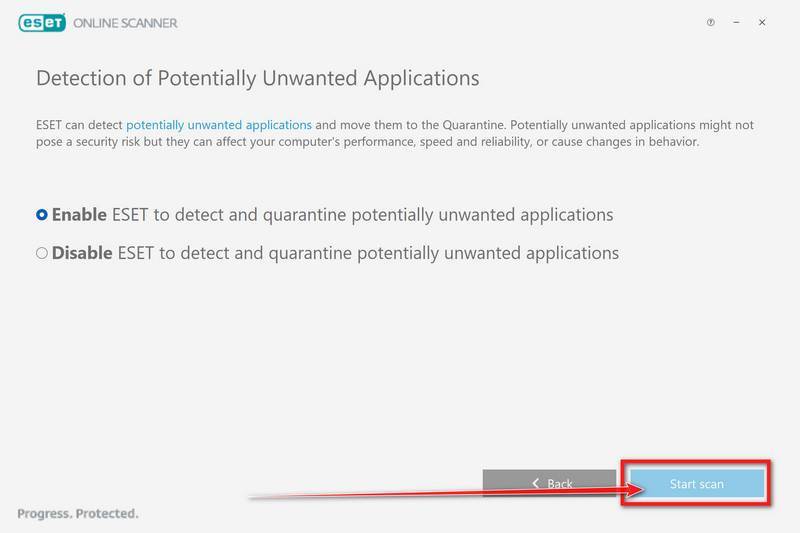
Select Enable for Detection of Potentially Unwanted Applications — this lets ESET catch adware and bundled junk programs, not just viruses. Then click Start scan.
-
Wait for the Scan to Finish
ESET will now check every file on your computer. Because it’s a full scan, this can take a while — often an hour or more, depending on how much data you have. Leave it running in the background and check on it from time to time.
-
Review the Results
When the scan finishes, open View detailed results and check the action recorded for each detection. ESET attempts to clean detected threats, but unresolved items still need attention. Save the report if anything could not be cleaned.
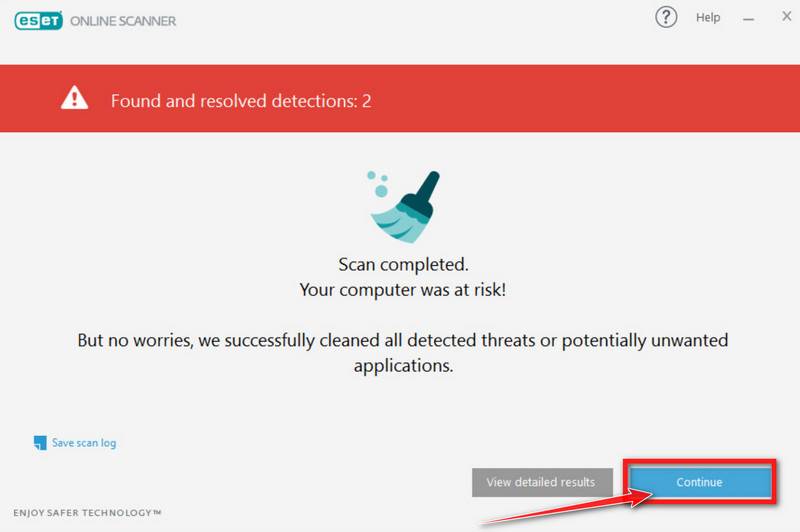
If ESET found nothing, restart and check whether the original problem is gone. If warnings, redirects, or other symptoms continue, keep the scan reports and ask for help in the MalwareTips removal forum.
STEP 8: Run the System File Checker (SFC) tool
In this step, we will use System File Checker (SFC) tool to detect and repair files that may have been corrupted by malware.
System File Checker checks protected Windows system files and replaces damaged copies using Windows’ component store. It repairs Windows files; it does not remove malware or repair personal documents. On Windows 10 and 11, run DISM first, then SFC as shown below.
-
Open Command Prompt as Administrator.
To open the Command Prompt as an administrator in Windows, type “cmd” in the search bar and then right-click on the Command Prompt result and select “Run as administrator” as shown in the image below.
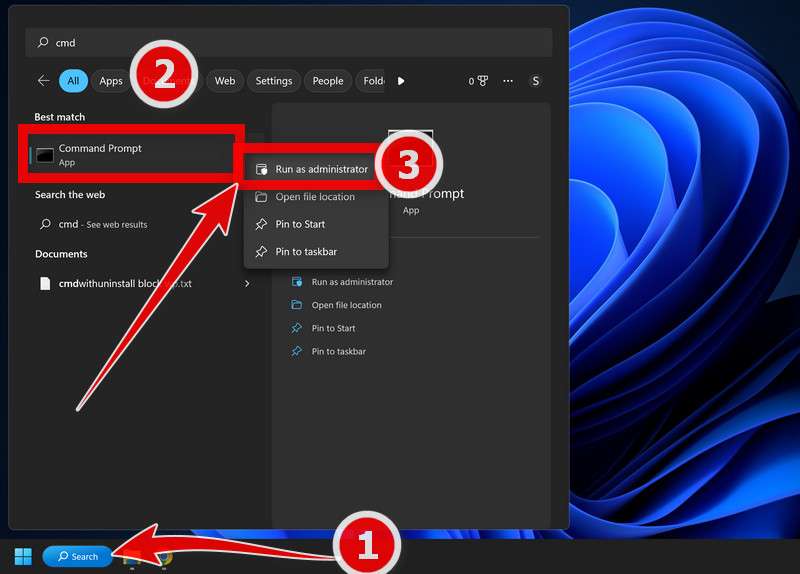
A User Account Control (UAC) prompt will appear asking for permission to allow the program to run. Click “Yes”.In the administrator window, enter DISM.exe /Online /Cleanup-Image /RestoreHealth and wait for it to finish. Then run sfc /scannow. If DISM fails, note its error before continuing; Windows Update or a matching repair source may be needed.
-
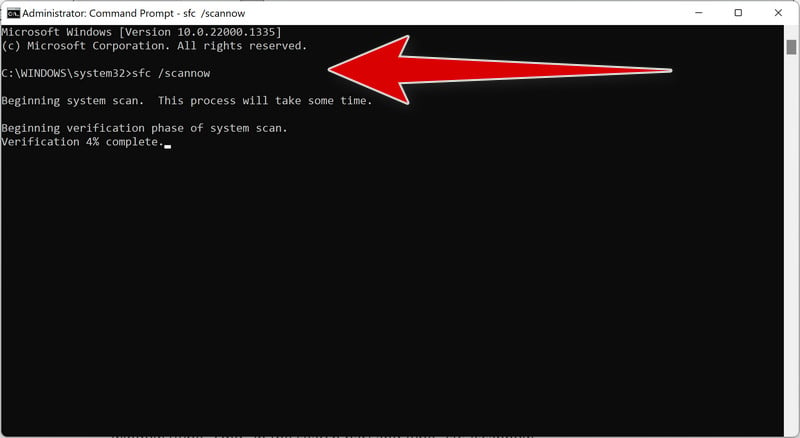
Type “sfc /scannow”.
You will now be presented with a black screen called the ‘Administrator: Command Prompt’. On this screen, type “sfc /scannow” to scan for and repair any corrupt system files.
-
Restart your computer.
Restart your computer if sfc /scannow repaired files. System File Checker may or may not prompt you to restart but even if it doesn’t, you should restart anyway.
-
Run again sfc /scannow.
Run again sfc /scannow to check if the files were repaired.
STEP 9: Run the Disk Check tool
Use the Disk Check step if file-system errors remain after malware removal. It is a Windows repair tool, not another malware scan; you can skip this repair when the drive and Windows are working normally.
Use this repair only if Windows reports disk or file-system errors. Back up important files first. A drive making unusual noises or repeatedly disconnecting needs a recovery assessment before a repair scan; CHKDSK is not a malware scanner.
This tool checks your hard disk for errors and can fix any issues it finds. To use the Disk Check tool, you will need to open the command prompt and enter the “chkdsk” command followed by the drive letter (e.g., “chkdsk C:”). You can also add the “/f” flag to the command to instruct the tool to fix any errors it finds. By running the Disk Check tool, you can help ensure that your hard disk is functioning properly and fix any issues that may be causing high disk usage.”-
Open Command Prompt as Administrator.
To open the Command Prompt as an administrator in Windows, type “cmd” in the search bar and then right-click on the Command Prompt result and select “Run as administrator” as shown in the image below.
A User Account Control (UAC) prompt will appear asking for permission to allow the program to run. Click “Yes”. -
Choose the disk check you need
On Windows 10 or 11 with an NTFS system drive, start with chkdsk C: /scan. If Windows reports errors requiring repair, use chkdsk C: /f. The /r option in the older screenshot also checks sectors and can take much longer; use it only when there is a reason to check for bad sectors.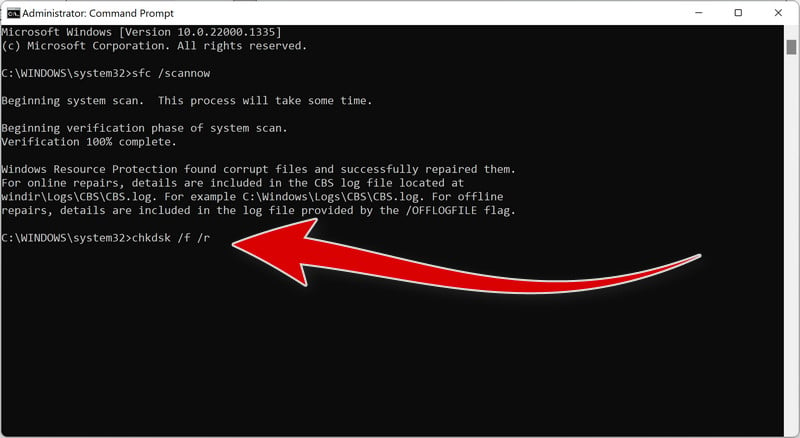
-
Restart your computer
The Disk Check tool may require you to restart your computer in order to complete the scan and repair process. Type “Y” and click on Enter, then restart the computer. A CHKDSK command can take a long time, especially when performed on larger drives. Once it’s done, however, it will present a summary of results including total disk space, byte allocation, and, most importantly, any errors that were found and corrected.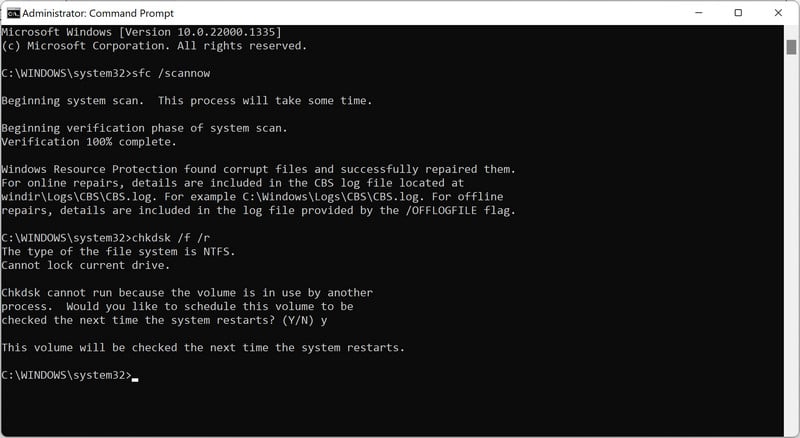
Frequently Asked Questions about Removing Malware from Windows
Here are some of the most frequently asked questions regarding removing viruses, spyware, ransomware, and other malware from Windows PCs and laptops:
What are the signs my Windows computer has malware?
Common infection signs include slowed performance, crashing programs, unknown processes in Task Manager, changed settings, disabled security tools, popups, etc.
How does malware get onto my Windows PC?
Infection vectors include phishing emails, compromised sites, pirated software, vulnerabilities, infected USB drives, and social engineering tricks.
What is the best anti-malware software for Windows?
Products such as Malwarebytes Premium and currently supported Bitdefender or ESET security plans provide paid protection features. Check the current product name, supported Windows version, and included features before buying; a paid plan is not required for the manual Malwarebytes removal steps in this guide.
Does Windows Defender remove all malware?
No security product detects every threat. An additional Malwarebytes or HitmanPro scan can provide a second opinion, but neither a paid subscription nor a clean scan proves that an advanced infection is gone. Follow up on recurring symptoms and unresolved detections.
Should I use multiple anti-malware programs together?
Using more than one real-time anti-malware tool is not recommended, but alternate scanners can help remove missed infections.
What risks are there with malware removal tools?
Some free removal tools actually contain malware themselves. Only use trusted options with positive reviews. Avoid unknown software claiming to detect issues.
How can I avoid malware reinfecting my PC after removal?
Practice safe computing habits, avoid suspicious links/attachments, update your operating system and programs, use a firewall and VPN when on public WiFi.
Is completely removing malware possible?
Using the proper technical removal process enables eliminating all traces of malware – but infections can return if you aren’t cautious about prevention.
What should I do if malware keeps coming back?
Persisting malware often indicates a dormant infection or reinfection source. Stick to the proven removal methodology and determine how it is reaccessing your system.
Why is malware removal an essential computer security skill?
Allowing malware infections to persist and accumulate can lead to loss of sensitive data, identity theft, system instability, and even permanent damage. Removing malware keeps Windows PCs performing smoothly and protects your privacy and security.
What precautions should Windows users take to avoid malware?
- Use strong passwords and 2FA authentication
- Maintain comprehensive local and cloud backups
- Don’t open attachments or links from unknown senders
- Only download software from official sources
- Use a modern antivirus program and keep it updated
- Be wary of fake “security alerts” asking you to download software or call tech support numbers
- Regularly update your operating system, browser and other software
Staying informed about malware and following security best practices keeps your Windows PC free of viruses and cyberthreats.
Preventing Malware Reinfection
Removing existing malware is only part of the battle. Users must remain vigilant and take proactive measures to prevent future reinfection:
- Maintain updated antivirus software with real-time scanning enabled
- Avoid clicking links or attachments from suspicious emails
- Only download software from trusted, authorized sources
- Beware phishing attempts and social engineering manipulation
- Enable firewalls and employ a VPN when accessing public WiFi
- Regularly update the Windows operating system and programs
- Exercise caution with removable drives from untrusted sources
- Backup important data routinely
- Disable administrative privileges on user accounts
Combining robust preventive practices with proven malware removal techniques keeps Windows computers clean, secure, and running smoothly. Stay informed on the latest malware threats and removal innovations for maximum Windows PC protection.

THANK YOU!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!