


Scammers are becoming more sophisticated, using real company names and official-looking designs to deceive unsuspecting users. One of the latest phishing schemes making the rounds targets users of Crypto.com, a popular cryptocurrency exchange platform. The scam involves a fake email claiming that there’s a “restriction on your account,” urging recipients to verify their email address immediately.
If you’ve received such a message, you’re not alone. Thousands of people have reported receiving similar fake alerts. In this comprehensive guide, we’ll break down exactly how this scam works, what to do if you fall victim, and how to protect your crypto assets from future attacks.
Understanding the “Crypto.com Restriction On Your Account” Emai
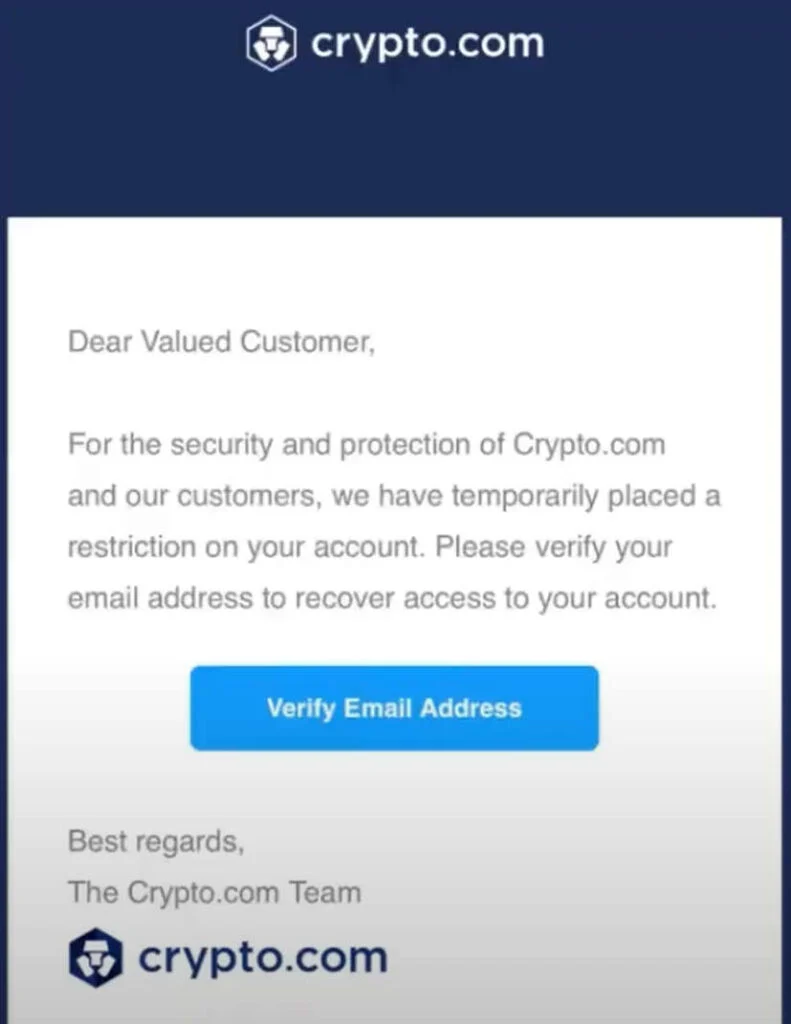
The Crypto.com restriction email scam is a well-crafted phishing campaign that imitates the legitimate branding of Crypto.com. The message is designed to trigger panic and urgency, making users believe their account access is temporarily restricted. The email typically claims it’s a security measure and prompts users to click a link to verify their email or recover access.
1. The First Impression: A Professional-Looking Message
At first glance, the email appears authentic. It often includes:
- The Crypto.com logo and color scheme
- A professional greeting, such as “Dear Valued Customer”
- A seemingly legitimate sender name like hello@crypto.com or security@crypto.com
- A clickable button labeled “Verify Email Address”
To the untrained eye, nothing looks suspicious. The design closely mimics genuine Crypto.com correspondence, right down to the footer and company logo.
2. The Emotional Trigger: Fear and Urgency
Cybercriminals know how to exploit human psychology. The email uses phrases like “for your protection”, “temporary restriction”, and “recover access to your account”. These words create a sense of urgency, making users act quickly without thinking critically.
Scammers rely on the fact that cryptocurrency users are particularly sensitive to security issues. The idea of losing access to funds can push people to click the verification link immediately.
3. The Dangerous Link
The link or button provided in the email redirects users to a fake Crypto.com website. This cloned page looks identical to the real login portal. Once the victim enters their credentials, the scammers capture them instantly.
In more advanced variants, the fake website may also prompt users to enter:
- Two-factor authentication (2FA) codes
- Personal identification details
- Recovery phrases for crypto wallets
With this information, scammers can drain a user’s account in minutes.
4. The Global Spread of the Scam
Reports of this phishing scam have surfaced across multiple countries. Security researchers have identified fake domains resembling Crypto.com, such as:
crypto-com-verification.comcryptocom-loginsecure.netcryptocomverifymail.com
These malicious domains are often hosted on short-lived servers, making it difficult for cybersecurity teams to shut them down quickly.
Scammers continuously register new look-alike domains to replace those that are taken offline. This tactic ensures the longevity of their operation and keeps new victims coming.
5. Why This Scam Is Particularly Dangerous
Unlike generic phishing attempts, this one is targeted and contextually relevant. Many people actually have accounts with Crypto.com, which makes the message more believable.
Additionally, cryptocurrency transactions are irreversible. Once funds are stolen, there is virtually no way to retrieve them. The anonymity of blockchain makes tracing stolen assets extremely difficult.
6. The Role of Social Engineering
At its core, the Crypto.com restriction email scam relies on social engineering—the manipulation of human trust and behavior. Scammers don’t need to hack into systems when they can trick people into handing over their credentials voluntarily.
They design every aspect of the email to appear legitimate, from the typography to the sender address. In some cases, they even spoof Crypto.com’s actual email domain, making the message appear to come directly from the company’s official servers.
7. How Victims Are Targeted
Phishing scammers use a combination of methods to build email lists:
- Data breaches: Compromised databases containing crypto user emails.
- Social media scraping: Collecting contact information from public profiles.
- Crypto forums: Extracting emails of registered users from online communities.
- Purchased lists: Buying leaked data from underground markets.
Once they have a list, they distribute the phishing email in bulk using automated tools.
8. The Aftermath for Victims
Victims who fall for the scam often notice unusual activity in their Crypto.com account within minutes or hours. Common consequences include:
- Unauthorized withdrawals
- Changed account settings
- Locked access due to altered credentials
- Stolen funds or tokens
In some cases, the attackers also use stolen information to target victims again through follow-up scams, pretending to offer recovery assistance for a fee.
How the Crypto.com Restriction Email Scam Works
Now that we’ve covered the overview, let’s go step-by-step through how the scam unfolds. Understanding this sequence can help you recognize similar tactics in the future.
Step 1: The Phishing Email Is Sent
The scam starts when the victim receives an email that appears to be from Crypto.com’s security team. The subject line typically contains alarming wording, such as:
- “Important: Restriction on Your Crypto.com Account”
- “Action Required: Verify Your Crypto.com Account”
- “Security Alert: Account Temporarily Locked”
The goal is to capture attention and create a sense of urgency.
Step 2: The User Reads the Message
Upon opening the email, the user sees a professionally formatted message with Crypto.com branding. The content usually reads something like:
“For the security and protection of Crypto.com and our customers, we have temporarily placed a restriction on your account. Please verify your email address to recover access.”
It looks harmless, but the message is a classic phishing lure designed to make the recipient act quickly.
Step 3: The Victim Clicks the Verification Link
The blue “Verify Email Address” button or the embedded hyperlink is where the real danger lies. Clicking this takes the victim to a fraudulent website that looks exactly like Crypto.com’s official login page.
In most cases, the domain name is subtly altered—for example, using hyphens or alternate extensions:
crypto-com-support.cominstead ofcrypto.comcryptocom.ioinstead of the legitimate.comdomain
The differences are easy to miss, especially when viewed on a mobile device.
Step 4: The Fake Website Captures Login Details
Once the victim enters their credentials on the fake page, the scammers immediately receive the information. They can then log into the real Crypto.com account and take over.
If the user has two-factor authentication (2FA) enabled, the fake site may prompt for the verification code as well. This allows scammers to bypass even enhanced security measures.
Step 5: The Attackers Access the Real Account
With full access, scammers can:
- Transfer cryptocurrency assets to external wallets
- Change account recovery settings
- Disable notifications or 2FA
- Lock out the original owner
Since blockchain transactions cannot be reversed, victims often lose their entire balance permanently.
Step 6: Optional Secondary Attack
Some scammers go a step further by installing malware through a downloadable attachment or redirecting victims to a fake support chat. These tactics can compromise additional accounts, including emails and banking information.
Step 7: The Victim Realizes Too Late
By the time victims notice suspicious activity, it’s often too late. Crypto.com’s customer support may attempt to freeze the account, but recovering lost assets is typically impossible.
The best-case scenario is preventing the scammers from accessing future funds. However, any tokens or coins already withdrawn are unrecoverable.
What to Do If You Have Fallen Victim to the Crypto.com Restriction Scam
If you’ve clicked the link or entered your details into a fake Crypto.com site, time is critical. Here’s a step-by-step guide on what to do immediately.
1. Change Your Password Immediately
Log in to your official Crypto.com account using the verified website: https://crypto.com.
Change your password right away. If you can’t log in, try to reset it using the account recovery option before the scammers lock you out.
2. Enable Two-Factor Authentication (2FA)
If you haven’t already, activate 2FA immediately. Use an authentication app like Google Authenticator or Authy, rather than SMS-based codes, since phone numbers can be spoofed or hijacked.
3. Contact Crypto.com Support
Go to the official support page and report the incident. Provide the phishing email’s details, including:
- Sender address
- Subject line
- Date received
- Any links you clicked
Crypto.com’s security team can help secure your account and may track the phishing operation.
4. Report the Email to Anti-Phishing Authorities
Forward the fraudulent email to:
- phishing-report@crypto.com (if available)
- reportphishing@apwg.org (Anti-Phishing Working Group)
- Your local cybercrime authority
Reporting these scams helps platforms take down fake domains faster.
5. Scan Your Device for Malware
Use reputable antivirus or anti-malware software to scan your computer or mobile device. Some phishing links install hidden software that can steal more information.
Recommended tools include:
- Malwarebytes
- Bitdefender
- Kaspersky Security Cloud
6. Secure Your Email Account
If you used the same password on your email as your Crypto.com login, change it immediately. Hackers often use compromised email accounts to reset other passwords.
7. Monitor Your Financial Accounts
Check your crypto and bank accounts for any unauthorized activity. Scammers sometimes test small transactions before larger withdrawals.
Set up alerts for any transactions to catch suspicious behavior quickly.
8. Report to Law Enforcement
File a report with your local police or cybercrime division. While cryptocurrency theft is difficult to trace, filing an official report helps authorities track organized scams and may assist future investigations.
9. Notify Your Contacts
If the scammers gain access to your email or social media accounts, they might send messages to your contacts pretending to be you. Alert friends and family not to click suspicious links sent from your accounts.
10. Stay Updated on Crypto.com Security Alerts
Regularly check Crypto.com’s official blog or Twitter account for new security advisories. The company often posts warnings about active scams and phishing campaigns.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions About the Crypto.com Restriction On Your Account Email Scam
What is the “Crypto.com Restriction On Your Account” email scam?
The “Crypto.com restriction on your account” email scam is a phishing attempt that impersonates Crypto.com. It sends users a fake message claiming that their account has been temporarily restricted for security reasons. The email urges recipients to click a button labeled “Verify Email Address” or “Recover Account Access.” Once clicked, it redirects users to a fraudulent website designed to steal login credentials, recovery phrases, and other sensitive information.
The goal of the scam is to trick victims into providing access to their genuine Crypto.com accounts, allowing scammers to withdraw funds, steal tokens, or sell personal data.
How can I tell if a Crypto.com email is fake or real?
Spotting a fake Crypto.com email can be difficult because scammers often replicate the company’s logo, layout, and tone. However, there are key warning signs that can help you identify a phishing attempt:
- Check the sender’s email address. Legitimate Crypto.com emails come from domains ending in @crypto.com only. Anything else is suspicious.
- Hover over links before clicking. A real Crypto.com link should lead directly to https://crypto.com/, not to a domain with extra words, hyphens, or unusual endings.
- Watch for urgent language. Phrases like “verify immediately” or “account restricted” are red flags.
- Look for grammatical errors or awkward phrasing. Official Crypto.com communications are written professionally and clearly.
- Contact support directly. If you’re unsure, log into your account using your own bookmark or the Crypto.com app and check for notifications there.
Why are scammers targeting Crypto.com users?
Scammers target Crypto.com users because cryptocurrency accounts hold real financial value and transactions are irreversible. Once a scammer gains access to your account, they can transfer digital assets to external wallets without any possibility of recovery.
Additionally, Crypto.com is a well-known and trusted brand, which makes impersonating it an effective strategy for cybercriminals. Many users are quick to react to any message mentioning “security restrictions,” assuming it’s a genuine alert.
What happens if I click the link in the scam email?
If you click the link in a fake Crypto.com email, you’ll likely be redirected to a spoofed website that looks identical to the real Crypto.com login page. If you enter your email, password, or two-factor authentication (2FA) code there, the information will go directly to scammers.
In some cases, clicking the link may also trigger the download of malicious software designed to steal saved passwords, crypto wallet data, or browser cookies.
If you clicked the link but did not enter any information, you may still be safe. However, it’s important to run a malware scan and report the phishing email to Crypto.com.
What should I do if I entered my Crypto.com credentials on a fake website?
If you accidentally entered your details into a fake Crypto.com website, act immediately to minimize damage:
- Go to the real Crypto.com site at https://crypto.com.
- Change your account password right away.
- Enable or update two-factor authentication (2FA) using a secure authentication app.
- Contact Crypto.com support to report the incident and request assistance.
- Check your account for unauthorized transactions.
- Scan your device for malware using reputable antivirus software.
The faster you act, the greater your chances of preventing total account compromise.
Is the Crypto.com restriction scam only sent through email?
No, this scam can appear in multiple forms. While email phishing is the most common method, scammers also use:
- Text messages (SMS phishing or smishing): Messages claiming account restrictions with short links.
- Social media messages: Fake support accounts on X (formerly Twitter), Telegram, or Discord.
- Pop-up ads: Malicious advertisements mimicking Crypto.com login pages.
- Fake mobile apps: Counterfeit versions of Crypto.com on unofficial app stores.
Always verify communications through official channels and never click unsolicited links, regardless of where they come from.
Can Crypto.com recover my stolen funds if I fall for the scam?
Unfortunately, once cryptocurrency has been transferred out of your account, it cannot be recovered. Blockchain transactions are permanent and anonymous, meaning Crypto.com cannot reverse them.
However, Crypto.com’s security team may freeze your account to prevent further theft if you report the incident quickly. They can also investigate the fraudulent activity and may assist law enforcement with relevant data to track the scammers.
How can I protect myself from Crypto.com phishing scams?
You can protect yourself by following a few essential cybersecurity practices:
- Bookmark the official Crypto.com website and use it for all logins.
- Never click links in unsolicited messages.
- Enable multi-factor authentication using an authenticator app, not SMS.
- Regularly review your login activity on your Crypto.com account.
- Keep your device software and browser updated.
- Educate yourself on common phishing red flags.
- Use a password manager to generate and store strong, unique passwords.
Consistent caution and awareness are your best defense against phishing scams.
Are there other scams similar to this one?
Yes, several other scams imitate popular crypto platforms. Similar phishing campaigns have targeted users of Binance, Coinbase, Kraken, and MetaMask, often using identical wording about “account restrictions” or “security verification.”
Some scammers also impersonate hardware wallet companies like Ledger and Trezor, asking users to “verify their recovery phrase.” This is another trick designed to steal wallet access. Always treat any unsolicited message about account verification as suspicious until proven authentic.
How can I report the Crypto.com restriction scam?
You can report the scam through several channels:
- Forward the phishing email to Crypto.com’s official security team or phishing-report@crypto.com if available.
- Submit the email to the Anti-Phishing Working Group (APWG) at reportphishing@apwg.org.
- Report fake domains to Google Safe Browsing or PhishTank.com.
- Contact your local cybercrime authority to file an official report.
Reporting helps stop scammers from targeting more people and enables authorities to investigate the operation.
Is it safe to open the Crypto.com email if I don’t click any links?
Generally, yes, opening the email itself is not immediately harmful as long as you don’t click links, download attachments, or enter personal data. However, it’s always safest to delete suspicious emails after reporting them, as some may contain tracking pixels that confirm your email address is active, which can lead to more phishing attempts in the future.
The Bottom Line
The Crypto.com restriction on your account email scam is one of many phishing attempts designed to steal personal and financial information from unsuspecting users. What makes this particular scam dangerous is its realism. It convincingly imitates Crypto.com’s design and tone, exploiting users’ trust and fear of losing access to their crypto assets.
The key to protection is vigilance. Always verify the sender’s email address, never click unsolicited links, and bookmark the official Crypto.com login page to access your account safely.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.