

Scammers are at it again with a new phishing scam impersonating delivery service Evri. Fraudulent text messages are being sent claiming your shipping information is missing an address, so your package cannot be delivered. The messages provide a link to upload correct shipping info, but it’s a trap to steal personal and financial data.
This article will dive into how the Evri scam works, how to protect yourself, and best practices for avoiding phishing attacks.
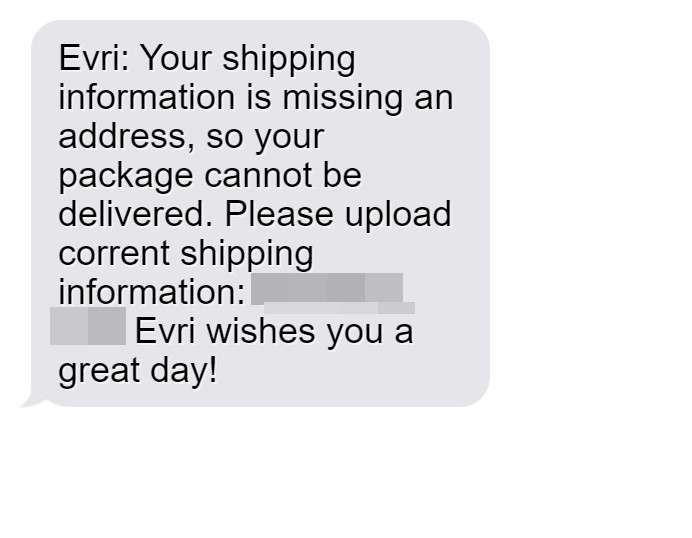
Overview of the Evri “Shipping Information is Missing” Scam
The Evri “Shipping Information is Missing” scam starts with potential victims receiving a text message claiming to be from Evri.
The fraudulent message states that your shipping details are missing an address needed to deliver your package. It provides a link urging you to upload correct shipping information to get your package delivered.
However, the link redirects to a fake Evri website that is engineered to steal personal and financial data from victims. If users input any information into the phishing site, scammers can steal it to commit identity theft and credit card fraud.
For example, a fraudulent Evri smishing text may say:
“Evri: Your shipping information is missing an address, so your package cannot be delivered. Please upload correct shipping information: evri23.deliveryportal.com. Evri wishes you a great day!“
This cunning smishing scam closely mimics real Evri delivery notifications. The texts use Evri branding and messaging to appear legitimate. But the real Evri service would never text customers links to account login portals.
This scam is a form of phishing conducted over SMS text messaging, also known as smishing. The texts link to convincing fake websites pretending to be Evri, designed to deceive users into inputting valuable personal data that is captured for malicious use.
Victims who engage with the phishing link and site can end up providing scammers information like their full name, address, phone number, credit card number, security codes, and other login credentials. This data enables criminals to commit identity theft, credit card fraud, and steal money from accounts.
Being aware this Evri smishing scam is circulating can help identify and avoid the fraudulent text messages. Do not click links in suspicious texts, even if branding appears official. Protecting your personal information from phishing scams prevents extensive financial damages from fraud.
Next, we will detail exactly how this scam works from start to finish and provide tips to help avoid falling victim.
How the Evri “Shipping Information is Missing” Scam Works
From harvesting phone numbers to deploying fake texts and websites, here’s an in-depth look at how scammers execute this scam:
1. Scammers Obtain a Database of Phone Numbers
Scammers first acquire a large database of consumer phone numbers through various illicit means. Lists are bought and sold on the dark web by cybercriminals. Hackers may compromise e-commerce sites to steal customer contact info. Botnets and malware infect devices to harvest data entered.
Phone numbers are a key target, as numbers can’t expire or be changed easily like compromised passwords. Stolen mobile contacts fuel various smishing campaigns.
2. Phony Evri Texts are Blasted Out
Once scammers compile phone numbers, they send fake Evri texts en masse. The texts are made to look like real shipping notifications from Evri using its branding and messaging.
The texts claim a shipping address is missing, preventing delivery of a package. A link is provided to supposedly upload correct shipping details.
3. The Link Leads to a Fake Evri Site to Steal Info
Users who click the link are taken to an elaborate phishing site impersonating Evri’s real shipping portal. The site asks users to enter details like their name, address, phone number, and sometimes additional info like credit card details.
Various techniques like fake domains, padlock icons, and corporate branding make the site appear legit. But in reality, it’s only collecting data for malicious purposes.
4. Victims Enter Personal and Financial Information
Tricked into entering details on what they believe is Evri’s site, victims end up providing scammers valuable personal and financial information.
This includes full name, shipping/billing addresses, contact info, credit card numbers, security codes, and other account login credentials entered on the phony portal.
5. Scammers Steal and Use the Data for Financial Fraud
Once submitted, scammers steal all the sensitive information entered on the fake Evri site. Stolen data enables a wide range of fraudulent activity:
- Identity theft – Names, addresses, and other PII is used to open fraudulent accounts.
- Credit card fraud – Stolen card numbers are used to make purchases online or create cloned cards.
- Account takeover – Login credentials are leveraged to infiltrate financial, social media, email, and other online accounts.
- Sell data on the dark web – Info like social security numbers, account logins, and credit card numbers can be sold for profit.
- Launch additional smishing campaigns – Phone numbers are targeted again for other scams.
Being aware of the immense financial damage resulting from phishing scams is key to avoiding engagement.
How to Identify Fake Evri Text Messages Related to the “Shipping Information is Missing” Scam
It’s important to be able to recognize fraudulent Evri text messages used in the “shipping information is missing” smishing scam. There are several indicators to help discern fake texts from real Evri communications:
Analyze the Sender’s Phone Number
Carefully inspect the phone number or short code the text is sent from. Legitimate Evri messages will come from an official short code:
- 7726 (Evri Tracking Updates)
Scam Evri texts often spoof local area codes or use arbitrary short codes:
❌ 555-123-4567
❌ 82456
Unknown numbers should signal a smishing attempt. Search online to confirm if a code is truly affiliated with Evri.
Watch for Odd Links and Website Addresses
Real Evri texts would never contain links to outside websites. Smishing texts provide links to shady sites engineered to steal your data when entered.
Hover over any links to inspect the web address. Fake domains with “evri” misspellings like “evrr1” should reveal a scam.
Verify Any Threats or Warnings
Smishing texts make dubious claims of unpaid delivery fees, package cancellations, or redirects to fake sites. But Evri would not threaten these actions over text.
Inspect texts carefully and confirm any warnings through official Evri customer service before taking action.
Check for Requests for Personal Information
Much like phishing emails, smishing texts try to trick users into inputting sensitive information like account numbers, IDs, or login credentials.
Evri would never ask customers for personal or financial details over text. Requests for address updates, package tracking numbers, or payment info signal a scam.
Watch for Poor Spelling and Grammar
Typos, spelling and grammar errors are common in smishing texts from unknown or foreign numbers. Real Evri messages are professionally written with no language issues.
Stay vigilant against Evri smishing scams by analyzing texts closely for these red flags. Report scam messages to 7726 and avoid clicking links or providing personal information requested.
What to Do If You Are Targeted by This Evri Smishing Scam
If you receive an unsolicited text from Evri saying your shipping details are missing, take the following steps:
1. Do Not Click Links or Provide Any Information
First and foremost, do not click on any links in the message or enter any personal or financial information on linked sites. This directs you to the phishing trap set by scammers.
2. Report the Scam Text
Forward the scam Evri text message to 7726, the carrier’s anti-fraud reporting number. You can also report it to Evri online for phishing investigation.
3. Contact Your Bank if Compromised
If you did provide any financial information through the scam site, call your bank immediately. Alert them of the fraudulent charges so they can block your card and dispute the charges.
4. Change Any Exposed Passwords
Also reset passwords for any online accounts which you entered credentials for on the fake portal. Use strong, unique passwords for each financial, email, social media and shopping account.
5. Review Accounts and Credit for Suspicious Activity
Carefully monitor all your financial accounts and credit reports for any unusual transactions. Place an initial 90 day credit fraud alert to help protect your credit if info was stolen.
6. Avoid Communications Claiming to Recover Losses
Be wary of any calls or emails claiming they can recover stolen money or data. These are likely scammers looking to extort victims who already fell for the phishing scam.
How to Avoid Falling Victim to Similar Smishing Scams
While text scams are on the rise, there are ways to avoid falling victim to smishing schemes:
- Do not click links in texts from unknown numbers – Real companies will never text unsolicited links. Visit sites through the official app or saved bookmarks.
- Verify the sender – Call the company directly using the official number to inquire if a text is legitimate. Search sites like WhoCalledUs to identify spam numbers.
- Never provide information via text – Legit businesses will not request personal or account info over SMS. Calls are more secure.
- Use multi-factor authentication – Add layers like biometrics and one-time passcodes to your online accounts for enhanced security beyond passwords.
- Install anti-phishing apps – Apps like Malwarebytes can detect and block phishing texts and sites.
- Report scam texts – Forward smishing messages to SPAM (7726) to aid carriers in terminating fraudulent numbers.
- Monitor accounts closely – Keep a close eye on all financial statements and credit reports for any unusual activity signaling fraud.
- Educate friends and family – Share information about the latest smishing scams to help prevent them from being victimized.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions About the Evri “Shipping Information is Missing” Scam
This FAQ provides key facts and information about the fraudulent Evri text message scam targeting consumers. Learn how to identify this smishing scam and avoid falling victim.
What is the Evri “shipping information is missing” scam?
This scam involves fake text messages pretending to be from delivery service Evri. The messages claim your shipping details are missing an address needed to deliver a package. A link is provided to upload correct info, but it leads to a phishing site stealing personal and financial data.
What do the fake Evri texts say?
Examples of fraudulent messages used in this scam include:
- “Evri: Your shipping information is missing an address needed to deliver your package. Please update here: evdeliveryportal.com”
- “Attention Evri customer: We cannot process your package for delivery due to incomplete shipping info. Please enter your address here: evri Updated page.”
- “Evri Shipping Error – Your delivery cannot be completed due to missing address information. Please complete your shipping profile here: evrideliveryonline.com”
What happens if you click the link in the text?
The phishing link in the Evri smishing texts directs victims to a fake website impersonating Evri. The site requests users enter personal details like your name, address, phone number, credit card info and more under the guise of completing shipping. Data entered is stolen.
How can you identify fake Evri texts?
Fake indicators include:
- Unknown sender phone number
- Links to odd domain names
- Spelling/grammar errors
- Requests for personal information
- Threats of fees or delivery cancellations
What should you do if you get a suspicious Evri text?
If the text appears fake:
- Do not click any links or provide info
- Report it by forwarding to 7726
- Contact Evri to confirm text is not real
- Monitor accounts if compromised
How can you avoid smishing scams?
Tips to avoid smishing:
- Never click links in texts from unknown numbers
- Use multi-factor authentication on accounts
- Monitor bank statements routinely
- Verify texts claiming urgent action
- Report scam texts to 7726
What should you do if you provided your information?
If you entered any data into the phishing site:
- Contact banks to cancel compromised cards
- Reset passwords on affected accounts
- Place fraud alert on credit reports
- Closely monitor accounts for any fraudulent activity
How can I report the scam text?
To report the scam Evri text:
- Forward it to 7726
- File a complaint with the FTC
- Report it to Evri via their contact email
- Notify your cell phone carrier
Stay alert for smishing scams misusing brands like Evri to steal consumer data. Use caution with unsolicited texts and verify legitimacy before providing information.
The Bottom Line
The fake Evri delivery notice scam shows fraudsters continue to leverage the names of legitimate companies to phish for data via text. But understanding common smishing techniques makes it possible to recognize and report scam texts. Remember to never click embedded links, provide personal information, or engage with suspicious texts from unknown numbers. Using caution against phishing attempts can prevent damaging identity theft and financial fraud.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.