

A harmless-looking Android app can become a window into everything happening on the phone. Flying Eagle gives criminals the tools to record screens, capture passwords and remotely operate a device after one deceptive installation.
The threat is not tied to a single app name or icon. Attackers can repackage Flying Eagle with a new disguise for each campaign, making the installation source, permissions and behavior far more important than its appearance.
Overview
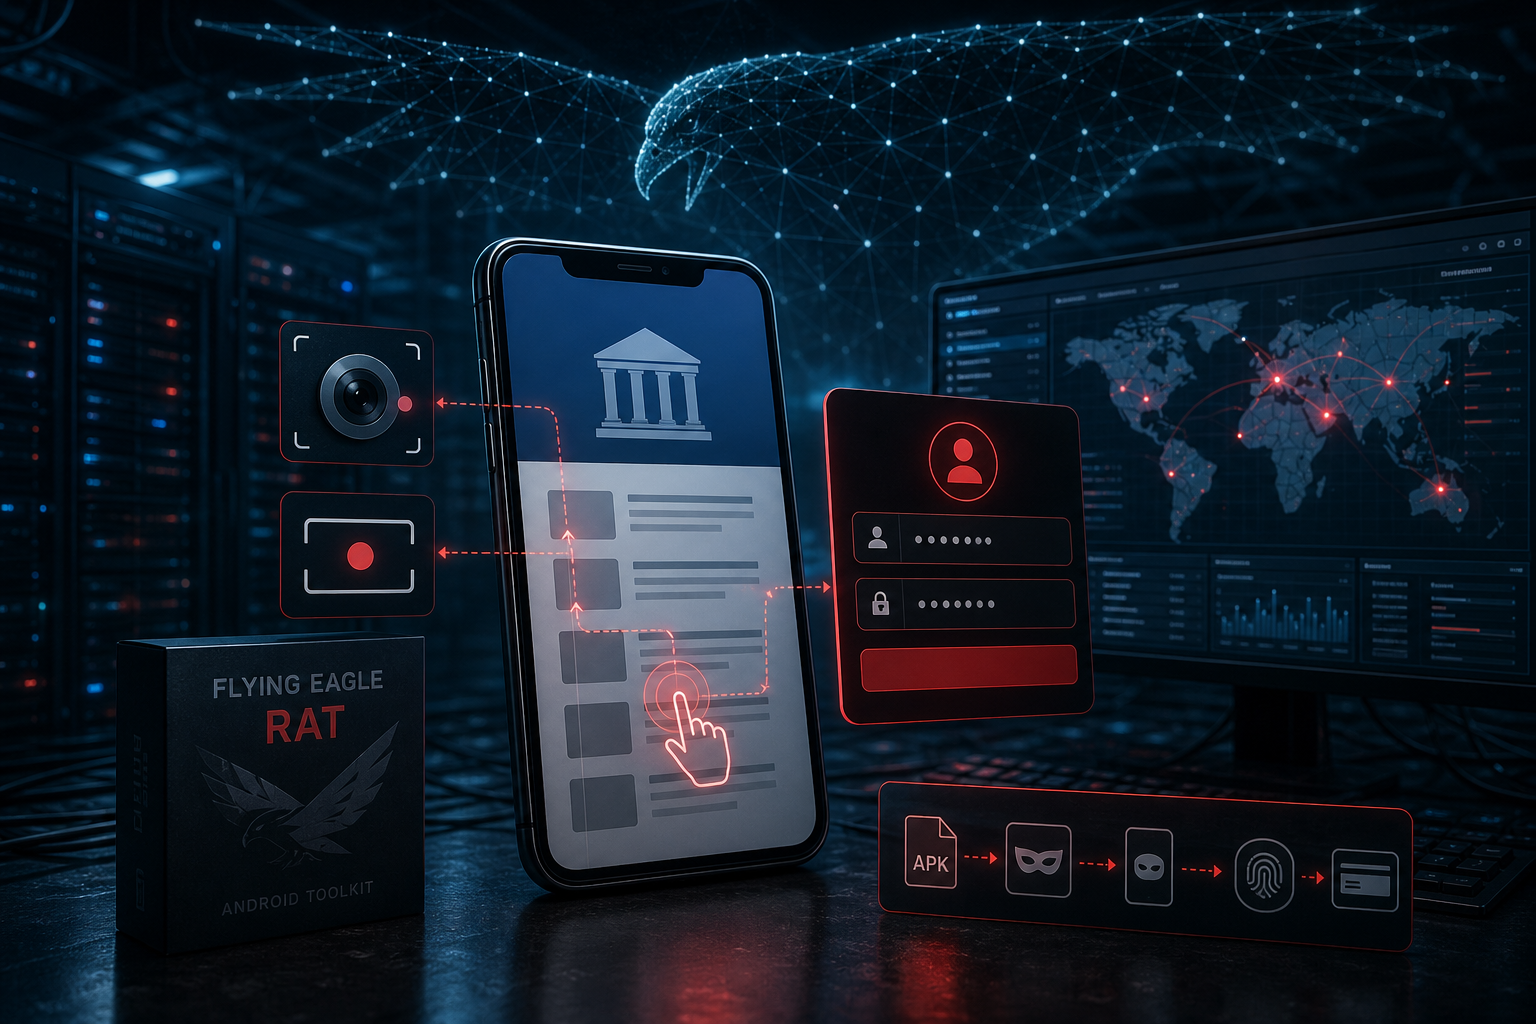
Flying Eagle is a commercial Android remote access trojan distributed as a complete criminal toolkit. Its buyers do not need to build an operation from scratch: the package includes source code, server components, a web control panel, app-building tools and templates that can be adapted to different lures.
An operator can choose the malicious app’s visible name, icon and story before generating a signed APK. The result may look like a government service, security tool, financial app or ordinary utility. Behind that changing exterior, the app attempts to obtain Android Accessibility access and other sensitive permissions that allow it to observe and control the device.
Accessibility abuse is central to the attack. Flying Eagle can use the service to monitor interface content, simulate gestures and interact with apps. It also supports screen recording, keylogging and counterfeit overlays that appear above legitimate login pages. A victim can type a banking password into what looks like the correct app while the information is actually sent to a criminal.
The toolkit is designed to help individual builds evade simple detection. It can randomize package and class names, encrypt the address of its command server and add bulky, low-information data to change the app’s size and appearance. Those changes do not make the program legitimate; they make repeated samples harder to match using basic signatures.
Flying Eagle has been disguised as official-looking Android software and distributed through deceptive websites, private messaging channels and other unofficial sources. The malicious app does not need to break into a phone remotely. It relies on the victim enabling installation from an unknown source and approving the permissions presented after launch.
- Threat type: Android remote access trojan and credential stealer
- Delivery: customized APK files distributed outside official app stores
- Core techniques: Accessibility abuse, screen recording, keylogging and fake overlays
- Operator tools: web panel, app builder and configurable command server
- Primary danger: account takeover, payment fraud and loss of private data
How the Flying Eagle Android RAT Works
Step 1: A criminal creates a customized fake app
Flying Eagle includes tools that let an operator select the app name, icon, package details and server address. This allows the same malware to be reused under many convincing identities.
A campaign can imitate an institution or build a generic utility that fits the message being sent. The polished appearance is part of the lure and does not show who actually developed the underlying code.
Step 2: The APK is promoted outside an official store
Victims are directed to a third-party webpage, Telegram channel, text-message link or another unofficial download source. The instructions may tell them to permit installations from the current browser or messaging app.
One observed disguise imitated a Chinese public-security application, but that is only one example. A different operator can replace the branding without changing the malicious behavior.
Step 3: The app asks for Accessibility and other permissions
After installation, the fake app requests access that greatly exceeds what its claimed purpose needs. Accessibility Services can give it visibility into screen content and the ability to simulate taps and swipes.
Additional permissions may expose files, notifications, camera or microphone functions. The prompts can be wrapped in an activation, identity-verification or update story to make approval seem necessary.
Step 4: The device connects to the attacker’s panel
The app decrypts its configured command-server address and contacts the operator’s infrastructure. Device details and connection status are then made available through a web panel.
Encrypted configuration and randomized code help each malicious build look different, but the purpose remains the same: establish a channel through which the operator can monitor and control the phone.
Step 5: Screens, keystrokes and credentials are collected
Flying Eagle can record the display and log information entered by the victim. Fake overlays can reproduce login screens for banking, payment or government apps and send the submitted credentials to the attacker.
Screen access can reveal balances, private conversations, one-time codes and recovery information even when a particular app is not directly targeted.
Step 6: The attacker expands the compromise
Stolen email and financial credentials can be used on other devices, while remote-control functions let the operator alter settings or gather more information from the phone. Contacts may also receive new malicious links from an account that now appears familiar.
A successful infection can therefore continue after the APK is removed unless compromised passwords, sessions and recovery methods are also replaced.
Why Flying Eagle Is More Than a Single Malicious App
Flying Eagle should be understood as a toolkit. Different criminals can deploy it with different icons, domains and stories, so a list of known filenames will never be complete.
- The builder changes visible app branding for each lure
- Randomized package and class names complicate simple matching
- Encrypted server configuration hides the destination from casual inspection
- A ready-made control panel lowers the skill needed to operate the malware
- Phishing templates and server components support full campaigns
- Source-code access allows criminals to modify future versions
Warning Signs on an Android Phone
- An app was installed from a link rather than an official store
- A simple utility requests Accessibility or device-administrator access
- Banking or government apps display unusual login panels
- The screen activates, changes or records without a clear reason
- The camera or microphone indicator appears unexpectedly
- A newly installed app vanishes or has a blank icon
- Battery, processor or mobile-data use increases sharply
- Security settings change or permission prompts return repeatedly
What to Do If You Installed a Flying Eagle App
Take the phone offline
Enable airplane mode, then make sure Wi-Fi and Bluetooth are off. This interrupts the live connection and limits the attacker’s opportunity to issue more commands while you clean the device.
Do not open banking, email or password-manager apps on the suspected phone. Use another trusted device for urgent account protection.
Check and revoke special access
In Android Settings, review Accessibility, Device admin apps, notification access, VPN settings and permission to install unknown apps. Disable the suspicious app wherever it appears.
If the app prevents changes, restart into Safe Mode. Third-party applications normally remain inactive there, which can make it possible to revoke administrator rights and uninstall the package.
Remove the app and its installer
Open the full Apps list in Settings and sort by recently installed where possible. Do not rely on the launcher, because malicious packages can hide their icons. Uninstall the suspicious entry and delete its APK from Downloads.
Turn off unknown-app installation for the browser, messenger or file manager involved. That prevents the same route from silently being reused.
Run a mobile malware scan
Scan the phone for remaining components and other malicious packages that may have arrived through the same source.
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for Android Malwarebytes for AndroidScans your phone and removes malware at no cost
-
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
Recover affected accounts
From a clean device, replace passwords for email, banking, payment, cryptocurrency and social accounts used on the phone. Revoke active sessions, review connected applications and generate new recovery codes.
Contact banks or payment providers if credentials, card details or transactions were visible. Ask the mobile carrier to protect the number with an account PIN if SMS messages or verification codes may have been exposed.
Reset the phone if symptoms remain
A factory reset is appropriate when the app cannot be removed, surveillance symptoms continue or the level of access is uncertain. Back up personal photos and documents carefully, then reinstall trusted apps from official sources instead of restoring the suspicious package.
How to Protect Android Devices From RATs
- Use official app stores and verify the developer before installing
- Never grant Accessibility access merely to activate a downloaded app
- Treat APK links in private messages and QR codes as high risk
- Keep Android and Google Play system components updated
- Review special app access and device administrators regularly
- Use unique passwords and strong multi-factor authentication
- Remove unknown-app installation permission after legitimate use
Frequently Asked Questions
Is Flying Eagle a real Android security tool?
No. Flying Eagle is a remote access trojan toolkit built to create disguised malicious apps, operate infected phones and steal sensitive information.
Can I identify it by one app name?
No. Operators can customize the app’s name, icon and package information. An unofficial installation combined with excessive permissions is more meaningful than any single filename.
Will uninstalling the app secure my accounts?
Uninstallation stops the installed package, but credentials already captured remain exposed. Passwords, sessions, recovery codes and financial activity must be reviewed separately.
Does receiving a link infect the phone?
No. The typical chain requires the victim to download and install the APK and approve permissions. Delete the message if you did not install anything, and do not forward the link.
The Bottom Line
Flying Eagle is a confirmed Android RAT toolkit whose changing names and icons are designed to make malicious APK files look trustworthy. Its real functions include screen recording, keylogging, fake login overlays and remote device control.
If you installed an unofficial app and granted Accessibility access, disconnect the phone immediately. Remove the package, scan the device and secure every important account that was used while the app was present.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.