

If you are reading this article than you’re most likely trying to find out, what Live Security Platinum is and how you can get rid of this virus.
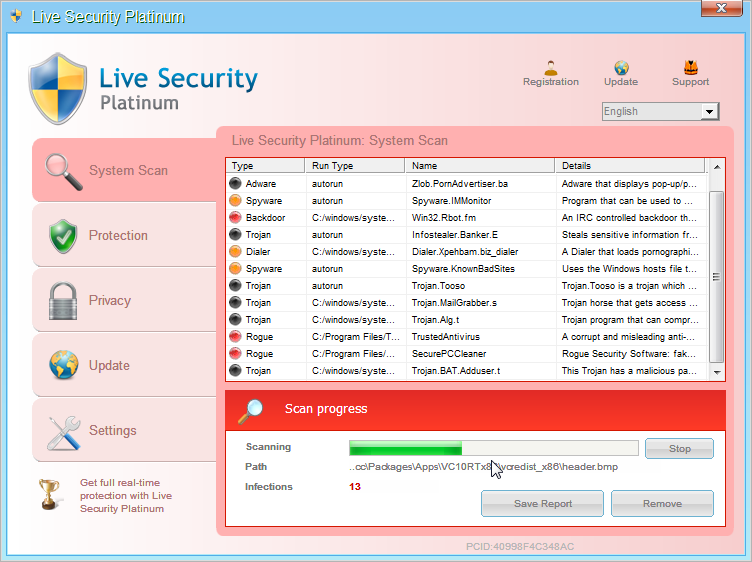
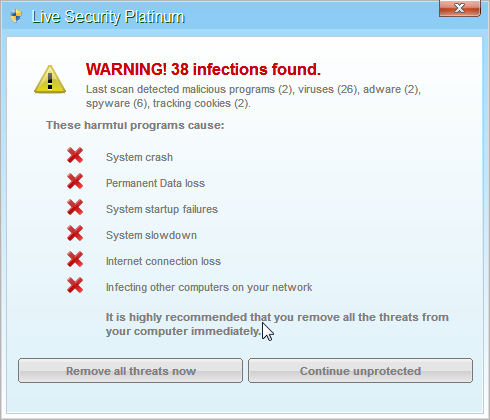
As you’ve probably realized by now,Live Security Platinum is a malicious software (rogue security software) that is displaying bogus antivirus alerts in an attempt to scare you into buying this fake security product.
Live Security Platinum is also blocking you from running programs and is causing browser redirects and slowing down your PC.
Live Security Platinum Images
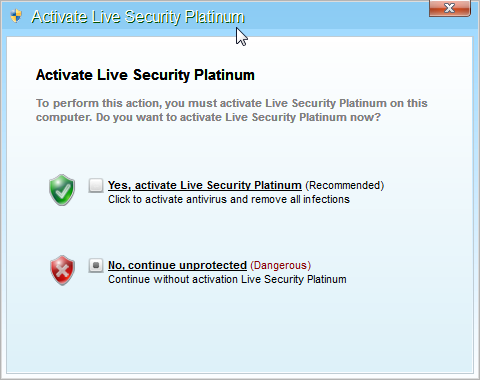
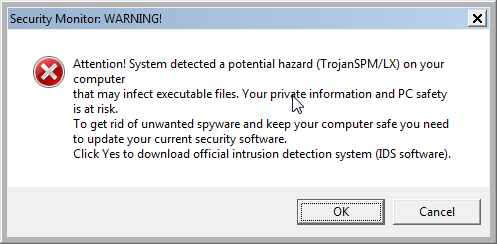
Below you can see some images of Live Security Platinum.
Registration codes for Live Security Platinum
As an optional step,you can use the following license key to register Live Security Platinum and stop the fake alerts.
AA39754E-715219CE
Please keep in mind that entering the above registration code will NOT remove Live Security Platinum from your computer , instead it will just stop the fake alerts so that you’ll be able to complete our removal guide more easily.
Live Security Platinum Removal Instructions
STEP 1 : Start your computer in Safe Mode with Networking
- Remove all floppy disks, CDs, and DVDs from your computer, and then restart your computer.
- Press and hold the F8 key as your computer restarts.Please keep in mind that you need to press the F8 key before the Windows start-up logo appears.
Note: With some computers, if you press and hold a key as the computer is booting you will get a stuck key message. If this occurs, instead of pressing and holding the “F8 key”, tap the “F8 key” continuously until you get the Advanced Boot Options screen. - On the Advanced Boot Options screen, use the arrow keys to highlight Safe Mode with Networking , and then press ENTER.


STEP 2: Remove Live Security Platinum malicious proxy server
Live Security Platinum may add a proxy server which prevents the user from accessing the internet,follow the below instructions to remove the proxy.
- Start the Internet Explorer browser and if you are using Internet Explorer 9 ,click on the gear icon
 (Tools for Internet Explorer 8 users) ,then select Internet Options.

- Go to the tab Connections.At the bottom, click on LAN settings.
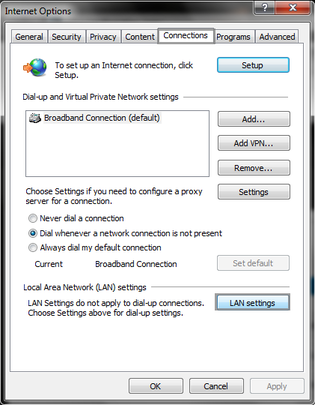
- Uncheck the option Use a proxy server for your LAN. This should remove the malicious proxy server and allow you to use the internet again.

 (Tools for Internet Explorer 8 users) ,then select Internet Options.


If you are a Firefox users, go to Firefox(upper left corner) → Options → Advanced tab → Network → Settings → Select No Proxy
STEP 3: Repair your Windows Registry from Live Security Platinum malicious changes.
Smart Fortress 2012 has changed your Windows registry settings so that when you try to run a executable file (ending with .exe ) , it will instead launch the infection rather than the desired program.
- Download the registryfix.reg file to fix the malicious registry changes from Live Security Platinum.
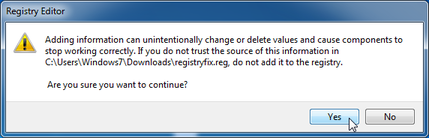
Download RegistryFix.regOpens the download page in a new tab. - Double-click on registryfix.reg file to run it. Click “Yes” for Registry Editor prompt window,then click OK.
STEP 4: Run RKill to terminate known malicious processes associated with Live Security Platinum.
RKill is a program that will attempt to terminate all malicious processes associated with Live Security Platinum,so that we will be able to perform the next step without being interrupted by this malicious software.
Because this utility will only stop Live Security Platinum running process, and does not delete any files, after running it you should not reboot your computer as any malware processes that are configured to start automatically will just be started again.
- While your computer is in Safe Mode with Networking ,please download the latest official version of RKill.Please note that we will use a renamed version of RKILL so that Live Security Platinum won’t block this utility from running.
Download RKillYour download starts right away. - Double-click on the iExplore.exe icon in order to automatically attempt to stop any processes associated with Live Security Platinum.

- RKill will now start working in the background, please be patient while the program looks for various malware programs and tries to terminate them.

IF you are having problems starting or running RKill, you can download any other renamed versions of RKill from here. - When Rkill has completed its task, it will generate a log. You can then proceed with the rest of the guide.
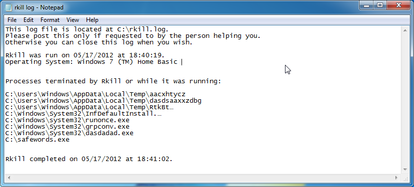


WARNING: Do not reboot your computer after running RKill as the malware process will start again , preventing you from properly performing the next step.
STEP 5: Remove Live Security Platinum malicious files with Malwarebytes Anti-Malware FREE
- Download the latest official version of Malwarebytes Anti-Malware FREE.
Download MalwarebytesFree official installer. Your download starts right away. - Start the Malwarebytes’ Anti-Malware installation process by double clicking on mbam-setup file.

- When the installation begins, keep following the prompts in order to continue with the setup process. Do not make any changes to default settings and when the program has finished installing, make sure you leave both the Update Malwarebytes’ Anti-Malware and Launch Malwarebytes’ Anti-Malware checked. Then click on the Finish button. If Malwarebytes’ prompts you to reboot, please do not do so.

- Malwarebytes Anti-Malware will now start and you’ll be prompted to start a trial period , please select ‘Decline‘ as we just want to use the on-demand scanner.

- On the Scanner tab,select Perform full scan and then click on the Scanbutton to start scanning your computer.

- Malwarebytes’ Anti-Malware will now start scanning your computer for Live Security Platinum malicious files as shown below.
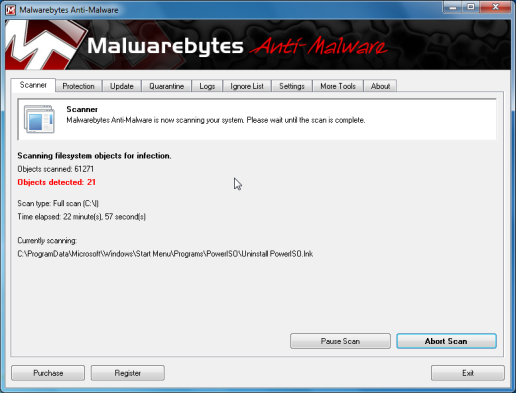
- When the scan is finished a message box will appear, click OK to continue.
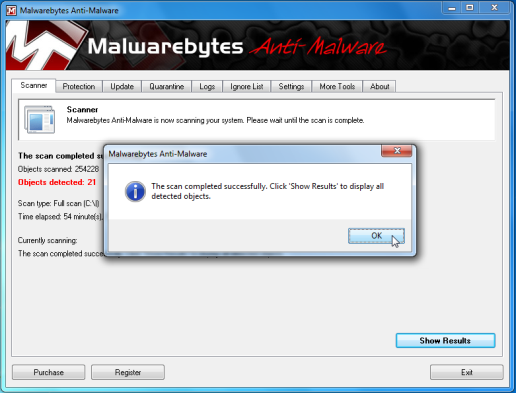
- You will now be presented with a screen showing you the malware infections that Malwarebytes’ Anti-Malware has detected.Please note that the infections found may be different than what is shown in the image.Make sure that everything is Checked (ticked) and click on the Remove Selectedbutton.
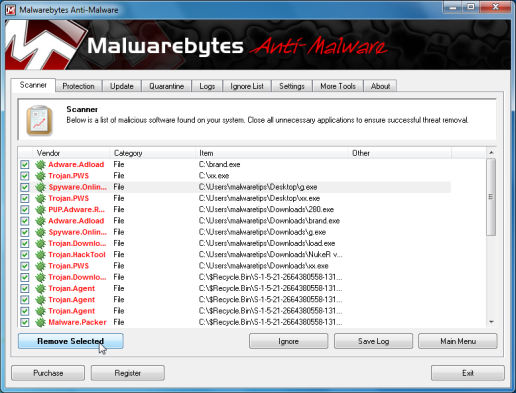
- Malwarebytes’ Anti-Malware will now start removing the malicious files.After completing this task it will display a message stating that it needs to reboot,please allow this request and then let your PC boot in Normal mode.


STEP 6: Double check your system for any left over infections with HitmanPro
- This step can be performed in Normal Mode ,so please download the latest official version of HitmanPro.
Download HitmanProOfficial Sophos download. Free scan, free 30-day trial to remove threats. - Double click on the previously downloaded fileto start the HitmanPro installation.

IF you are experiencing problems while trying to starting HitmanPro, you can use the “Force Breach” mode.To start this program in Force Breach mode, hold down the left CTRL-key when you start HitmanPro and all non-essential processes are terminated, including the malware process. (How to start HitmanPro in Force Breach mode – Video) - Click on Next to install HitmanPro on your system.

- The setup screen is displayed, from which you can decide whether you wish to install HitmanPro on your machine or just perform a one-time scan, select a option then click on Next to start a system scan.

- HitmanPro will start scanning your system for malicious files. Depending on the size of your hard drive, and the performance of your computer, this step will take several minutes.

- Once the scan is complete,a screen displaying all the malicious files that the program found will be shown as seen in the image below.After reviewing each malicious object click Next.

- Click Activate free license to start the free 30 days trial and remove the malicious files.
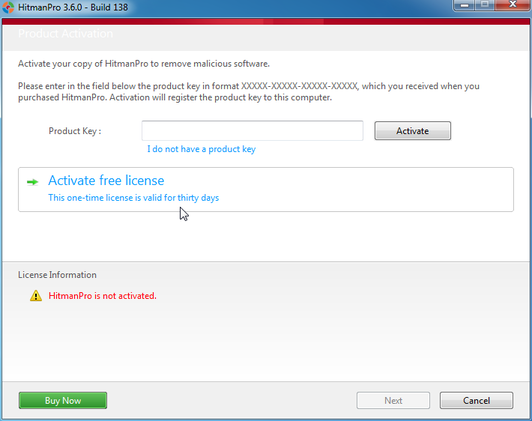
- HitmanPro will now start removing the infected objects, and in some instances, may suggest a reboot in order to completely remove the malware from your system. In this scenario, always confirm the reboot action to be on the safe side.


Join the discussion
311 commentsShare your experience or ask a question about this article.
Community experiences
Did this happen to you?
Your experience could help someone recognize the same scam. Submit a private report for our team to review.
I experienced this tooReports are reviewed before publication. Sharing publicly is always your choice.
Discussion
WOW, that was a tough one. It’s the second time in two weeks that a hostage malware came in through a Java update.
In reply to Stephen Mann
Annnnnd… it’s back.
Help?
In reply to Stephen Mann
OK,lets make sure this time it’s really gone:
STEP 1 : Run a scan with Combofix
Download ComboFix from one of the following locations:
COMBOFIX DOWNLOAD LINK #1 (This link will automatically download Combofix on your computer)
COMBOFIX DOWNLOAD LINK #2 (This link will automatically download Combofix on your computer)
VERY IMPORTANT !!! Save as Combo-Fix.exe during the download. ComboFix must be renamed before you download to your Desktop
———————————————————–
———————————————————–
———————————————————–
Notes:
STEP 2: Run a scan with ESET Online Scanner:
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
Next,perform a scan with Malwarebytes and HitmanPro.
Waiting for your reply to tell me if your machine is ok ..
Your guide worked wonderfully! Thank you!!
Thanks a lot, just saved my final dissertation.
Dear Stelian,
You really save me from very deep troubles. Excellent support.
Thanks a lot !!!
Stelian, You have earned your wings as an angel to many people! Thank you SO much. My computer guy said he would charge me my discounted rate of $130 to find and remove the virus and I did it myself with your instruction in just 3 and a half hours (lots of files to scan on my desktop) while using my laptop for work. I found that Malwarebytes said it could not run in safe mode but I clicked off the message and it ran. :) Also, HitmanPro said my firewall was blocking it but I clicked it again twice and it did it’s thing! Just FYI for those who may feel they are stuck like I did. Keep clicking! :) Thanks again. I’m going over to brag about you on Facebook now.
thanks for this matey!!!!!!
Hey thanks for this post. Helped me a lot in dealing with that evil malware.
When i run rkill, right before it’s done, a dialog box comes up and says:
Windows has found a critical error and needs to log off. Please save all your work.
HELP!
In reply to William
Hello William,
Lets try another way around this :
STEP 1. While in NORMAL MODE,download HitmanPro and then start this program in ForceBreach Mode
1.Here are the direct download links for HitmanPro,
– http://dl.surfright.nl/HitmanPro36.exe (For 32bit)
– http://dl.surfright.nl/HitmanPro36_x64.exe (For 64bit)
2.Hold down the left CTRL-key when you start HitmanPro and all non-essential processes are terminated, including this rogue malicious process
Here is a video that explains with graphic details how to do this : http://www.youtube.com/watch?v=m6eRWTv2STk
3. Let HitmanPro scan and remove the detected infections.
STEP 2: While in NORMAL MODE,download/Run Rkill and then run a scan with Malwarebytes
1.Download any re-named version of Rkill (direct download links bellow):
RKILL DOWNLOAD LINK #1
RKILL DOWNLOAD LINK #2
RKILL DOWNLOAD LINK #3
2.Next,please perform a scan with Malwarebytes and then do a RogueKiller and Unhide.exe scan as seen on the guide
STEP 3. Run a scan with ESET Online Scanner
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
Waiting for your reply to tell me how everything is working.. :) Good luck!
In reply to Stelian Pilici
I had the same problem as William… and nothing could be opened and no cursor when running in normal mode.
Fortunately I have access to another computer so I downloaded the portable version of “SuperAntiSpyware”, put it onto a usb drive and opened it up in safe mode on the infected laptop. The program did just enough to allow me to get working again in normal mode and run Malwarebites ( which found a further 8 infected files ).
I don’t know what other havoc it had wreaked, but the machine was still misbehaving, and I couldn’t get MS Security Essentials to switch on, so I rolled back two days and reinstalled/upgraded MS SE. Interesting couple of hours that I could have done without.
Thanks for this article which got me started on the right path to get rid of this gruesome little bug.
In reply to Stelian Pilici
I had the same problem as william and i tried following your tutorial afterwards and it wouldnt even let me download hitman pro? it says open and save (wont let me press open) so i press save and then it asks me to open it with another programme? :S HELP!
Hey Most of the steps mentioned don’t work for me because I just can’t get ANY Programs to run :( I used registryfix.reg in Safe mode but I still can’t run Rkill in regular mode because the virus just blocks the application…
Also I didn’t even have any problems with Proxy Servers the only problem is ,that I can’t open anything including: Browser, registry, taskmanager, RKill NOTHING. Iam really desperate I don’t want to reboot I have many important files on my PC
PLEASE HELP ME :'(
In reply to Jakob
Hello Jakob,
Lets try another way around this :
STEP 1. While in NORMAL MODE,download HitmanPro and then start this program in ForceBreach Mode
1.Here are the direct download links for HitmanPro,
– http://dl.surfright.nl/HitmanPro36.exe (For 32bit)
– http://dl.surfright.nl/HitmanPro36_x64.exe (For 64bit)
2.Hold down the left CTRL-key when you start HitmanPro and all non-essential processes are terminated, including this rogue malicious process
Here is a video that explains with graphic details how to do this : http://www.youtube.com/watch?v=m6eRWTv2STk
3. Let HitmanPro scan and remove the detected infections.
STEP 2: While in NORMAL MODE,download/Run Rkill and then run a scan with Malwarebytes
1.Download any re-named version of Rkill (direct download links bellow):
RKILL DOWNLOAD LINK #1
RKILL DOWNLOAD LINK #2
RKILL DOWNLOAD LINK #3
2.Next,please perform a scan with Malwarebytes and then do a RogueKiller and Unhide.exe scan as seen on the guide
STEP 3. Run a scan with ESET Online Scanner
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
Waiting for your reply to tell me how everything is working.. :) Good luck!
In reply to Stelian Pilici
Hi, I got same prob as William that Rkill keeps booting, so trying this way. I downloaded Hit Pro, but when I got to run it onc downloaded it wont let me as it says the same as its an exe file.. Any advise
In reply to Martin
Hello Martin,
Did you run the registryfix.reg file?
Lets work in NORMAL MODE to see if we can get around this :
Please run a scan with Malwarebytes Anti-Malware in Chameleon Mode in Norman mode:
2.Please perform a scan with HitmanPro as seen on the guide.
3.Run a scan with ESET Online Scanner:
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
Hello Stelian OMG HOW CAN I THANK YOU I am a person who writes story and after spending a hour trying to fix it I sat and cried I didn’t want to lose anything than I found this I pasted every step and it is finally working THANK YOU SO MUCH I COULD JUST HUG U *Virtal Hug* ;) I will recommend This to all of my friends (:
Thank you so, so much for this wonderful, easy-to-follow guide.
Though some people have mentioned the virus returning, my laptop seems
fine for now, after about 2 hours of battling with this malicious virus.
I was crying in front of my laptop before I decided to borrow my mom’s
to find a way to solve this issue, as my own wouldn’t let me open any site
because “the site may cause harm to [my] computer”, according to the virus.
All my important documents and projects from school are in my laptop,
and, since I use it to write down notes from classes instead of an actual
notebook, so are the notes I took down over the whole year of IB.
And – though not as important – the thousands of videos and pictures I have
been collecting, too…. I don’t know how I could have overcome this problem
without your useful post; I couldn’t find one that was as easy or as assuring
as this one! Really, thank you very much, I think it is wonderful work you’re
doing, saving crucial data – and tears – of so many people. Your guide was
very easy to follow, and your comments – though none of them apply to
myself, for now – are so kind and informative as well.
Thank you, and God bless you ♥
Hi Stelian.
Thanks for the guide. However, I can’t seem to get past the 3rd step. When I try to download the registry fix it says: “Not all data was successfully written to the registry. Some keys are open by the system or other processes.” I then tried to do my own registry fix from one of your comments and got a message saying it couldn’t be imported and that there is “an error accessing the registry.” Please help!
In reply to Matt
Can you please try to run RKILL and then try to merge the registryfix…
Please download this version of RKILL – http://download.bleepingcomputer.com/grinler/rkill.scr
Next,follow the steps in the guide.
Waiting for your reply to tell me who everything works!:)
In reply to Stelian Pilici
Hi Stelian,
I followed what you daid and continued to RKILL then the next steps (malwarebytes and hitmanpro), which seemed to find and remove the malicious threats. I then rebooted and did an online ESET scan as well, which found 9 more threats. I’m not sure if they were removed or just found. My computer seems to be running ok and I can’t seem to find any trace of Live Platinum left, but ideally I want to remove all threats. What should I do now?
Thank you!
In reply to Matt
Hello Matt,
Yes,ESET Online scanner will remove automatically all the detected threats…so they’re all gone!
Stay safe!:)
Hi Stelian,
Help please! I went to safe mode with networking and used malwarebytes. It found and removed several items but the the live security platinum is still there in regular mode. I re ran malwarebytes again in safe mode but nothing was found this time. I tried going onto the Internet to download other software you’ve mentioned but it keeps redirecting me and now security shield came up which I think is a similar thing to live security platinum? Help please!!!!
N
In reply to Nancy
Hello Nancy,
Yes,Security Shield is similar to this rogue so you need to remove it as soon as possible… Please follow the below steps:
STEP 1. While in NORMAL MODE,download HitmanPro and then start this program in ForceBreach Mode
1.Here are the direct download links for HitmanPro,
– http://dl.surfright.nl/HitmanPro36.exe (For 32bit)
– http://dl.surfright.nl/HitmanPro36_x64.exe (For 64bit)
2.Hold down the left CTRL-key when you start HitmanPro and all non-essential processes are terminated, including this rogue malicious process
Here is a video that explains with graphic details how to do this : http://www.youtube.com/watch?v=m6eRWTv2STk
3. Let HitmanPro scan and remove the detected infections.
STEP 2: While in NORMAL MODE,download/Run Rkill and then run a scan with Malwarebytes
1.Download any re-named version of Rkill (direct download links bellow):
RKILL DOWNLOAD LINK #1
RKILL DOWNLOAD LINK #2
RKILL DOWNLOAD LINK #3
2.Next,please perform a scan with Malwarebytes and then do a RogueKiller and Unhide.exe scan as seen on the guide
STEP 3. Run a scan with ESET Online Scanner
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
Waiting for your reply to tell me how everything is working.. :) Good luck!
In reply to Stelian Pilici
Thanks Stelian! Looks like it did the trick since the Live Security Platinum box isn’t popping up in my regular mode anymore…
I was able to access the internet in Safe Mode with networking however it kept redirecting me to different sites. So I downloaded the programs you mentioned from another computer and put it on a USB to transfer it to the affectted computer. I was then unable to run Hitman Pro using the Force Breach mode in the regular mode so I tried running it in the Safe Mode, which it worked and I followed the rest of your steps there after.
Here’s my Eset Scan results: C:\Users\Lucas\AppData\Local\Temp\jar_cache1130105515261397219.tmp Java/TrojanDownloader.Agent.NEA trojan cleaned by deleting – quarantined
C:\Users\Lucas\AppData\Local\Temp\jar_cache2929406719678060418.tmp Java/Exploit.CVE-2012-0507.AN trojan deleted – quarantined
C:\Users\Lucas\AppData\Local\Temp\jar_cache565304576539688280.tmp multiple threats deleted – quarantined
C:\Users\Lucas\AppData\Local\Temp\jar_cache8792167532769200996.tmp Java/TrojanDownloader.Agent.NEB trojan cleaned by deleting – quarantined
C:\Users\Lucas\AppData\LocalLow\Sun\Java\Deployment\cache\6.0\29\48801dd-2dfebb0b a variant of Win32/Injector.UEZ trojan cleaned by deleting – quarantined
C:\Users\Lucas\AppData\LocalLow\Sun\Java\Deployment\cache\6.0\33\2050fca1-7c6dfbdd multiple threats deleted – quarantined
C:\Users\Lucas\AppData\Roaming\ncrsl.dll a variant of Win32/Medfos.BL trojan cleaned by deleting (after the next restart) – quarantined
Just to be on the safe side, how often should these scanners be run? Daily/weekly/monthly?
Should I install an anti virus program to prevent these from happening in he future? If so, is there one that you would recommend? I’ve read that AVG and Avast seems to be the popular ones..
Any advice you could provide would be much appreciated!
N
In reply to Nancy
Hello,
It’s good to see that you’ve manage to get rid of this virus. :)
You can use this software to run a scan with them once a week if you like.As far as your real time protection goes,I advise to install a security product to protect your computer.Below you can find some quick suggestions:
Free – Avast 7 Free version or COMODO Internet Security
Paid : Norton Internet Security 2012,Avast Internet Security 7,G-DATA Internet Security 2012 or ESET Smart Security 5.
Anyway ,you should really start a thread in our Security Configuration forum as you need to build a layerd security config: http://malwaretips.com/Forum-Security-Configuration-Wizard
Also it would very good if you took the time and read this article that I’ve wrote: http://malwaretips.com/blogs/how-to-easily-avoid-pc-infections/ .. If you follow it,then we’ll never meet again in this conditions:)
Hi Stelian
i did the safe mode step but i do not know how to get on the second one
]
STEP 2: Remove Live Security Platinum malicious proxy server
Live Security Platinum may add a proxy server which prevents the user from accessing the internet,follow the below instructions to remove the proxy.
Start the Internet Explorer browser and if you are using Internet Explorer 9 ,click on the gear icon [Image: IE gear icon] (Tools for Internet Explorer 8 users) ,then select Internet Options.
plz help me I beg u asap
thanks heaps
cheers
dany
In reply to dany
Hello,
If you internet connections is working then you can skip this step!:)
Good luck!
thanks your information. wish best for you.
THE BEST.
Thank you SO MUCH!!!
Thank you soooo much! i just finished doing as instructed and everything seems to be ok. Thank God there are people like you out there to help those who need it, if I had lost my computer, I would of lost alot of college work! THANK YOU!
Another satisfied customer of this great work. Going to email/post this great repository of free tools.
Just a suggestion-there is a ton of great info on optional stuff in the comments section; why not add a 7th step of optional steps if the first 6 aren’t successful about using ComboFix, RogueKiller, Avast, Emisoft, ESET Online scanner, etc.
In reply to Allan
Hello,
In most cases those tools aren’t need it… the people who are experiencing problems and actually need to run this tools , have other infections on their machine apart from this rogue software:)
Thank you for posting this process. However, I need to tell you that rebooting in “Safe Mode with Networking” does not work on a cellular modem. I had to run Windows in normal mode to accomplish all this.
In reply to JJ
What I did was download everything in “normal” mode, then I rebooted to “Safe Mode with Networking” (although the “networking” part was basically moot….), then I ran everything in the order listed.
In reply to JJ
Exact what I did
You are an absolute legend and should be knighted, THANK YOU :)