A contract notification can feel unusually important, especially when it carries a settlement number and asks for a signature. The formal wording makes hesitation seem costly.
Yet a polished document request can conceal more than it reveals. A few careful checks can separate genuine business paperwork from a dangerous imitation.
Overview
A Settlement Contract That Was Never Sent
The Contract Document To Review And Sign email scam impersonates an electronic signature service and claims a business agreement awaits the recipient.
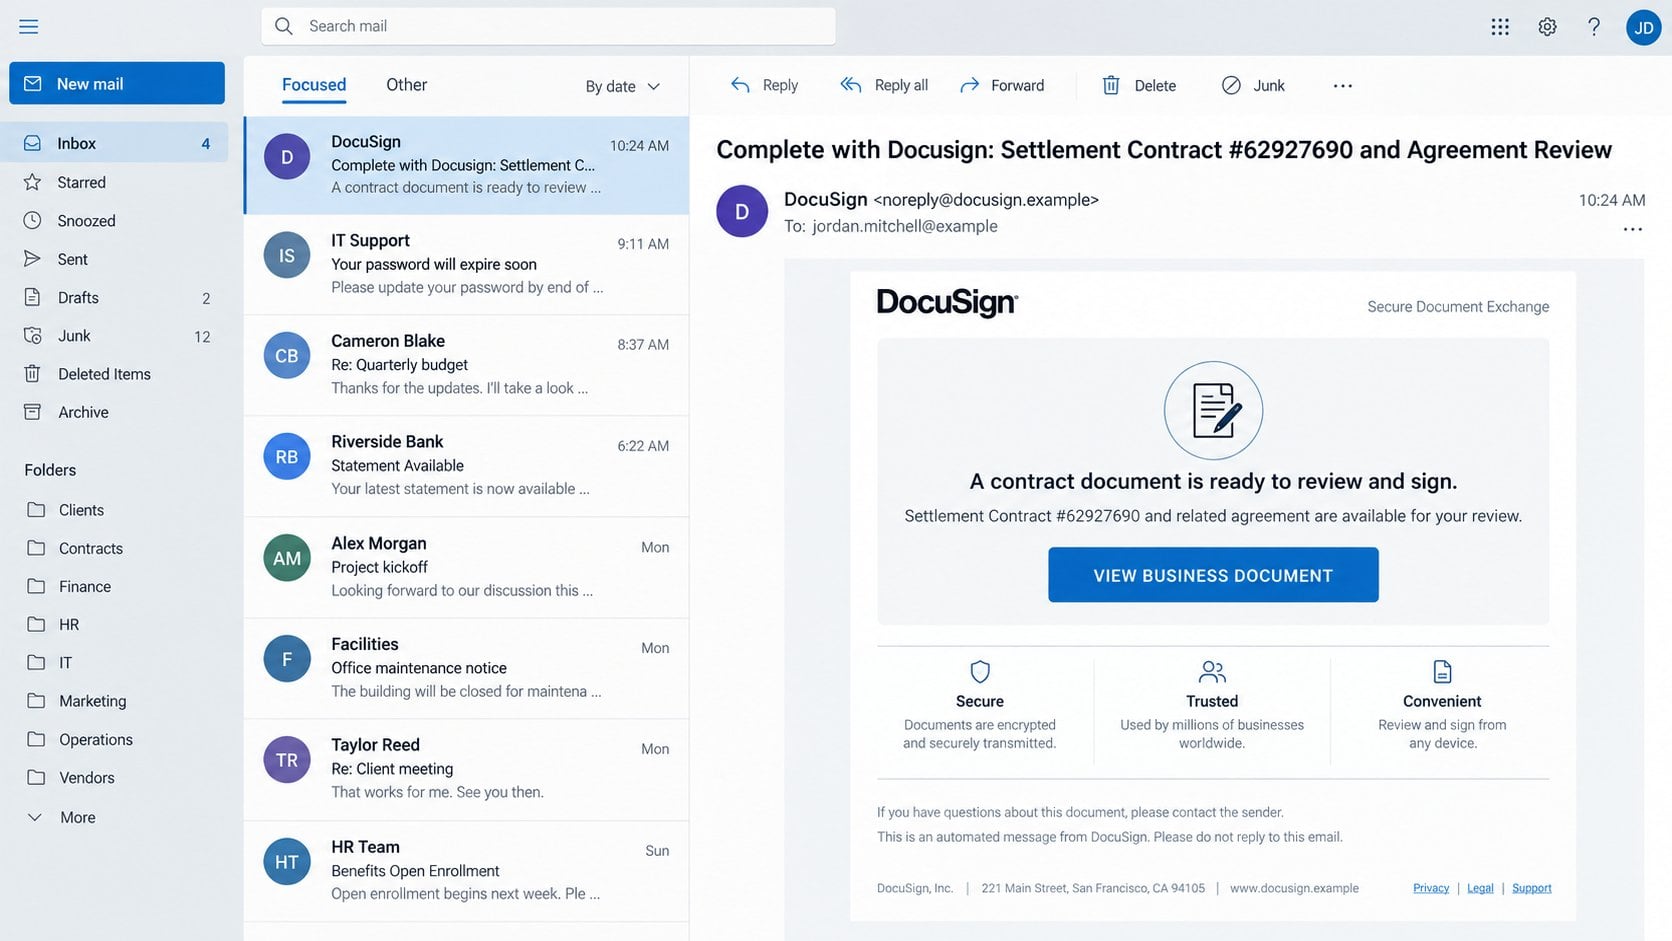
The examined subject read “Complete with Docusign: Settlement Contract #62927690 and Agreement Review.” That precise number makes the notice look tied to a real transaction.
Inside, a large “VIEW BUSINESS DOCUMENT” button promises access to the agreement. The message also refers to parties completing a purchase order for equipment.
Those details are invented. The button does not open a legitimate envelope, verified contract, or authentic signing session.
The Button Leads to a Password Trap
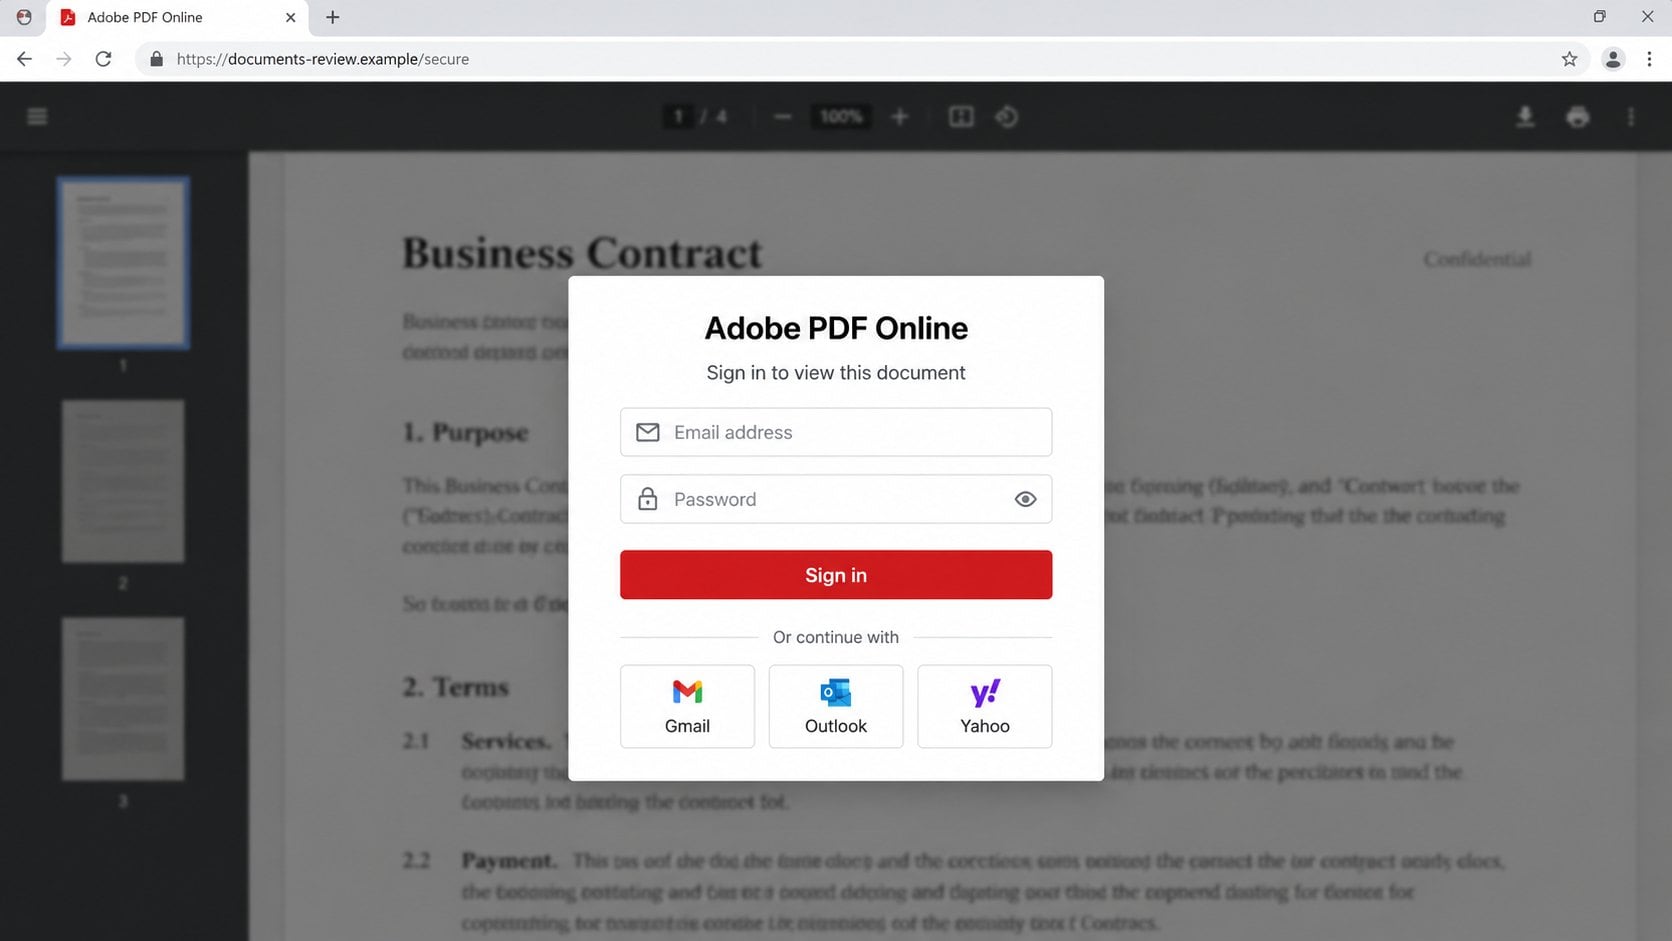
The email first directs visitors through an unrelated web address. Its path eventually displays a counterfeit “Adobe PDF Online” page.
A blurred contract appears behind a login box. The design suggests the document already exists and will become readable after authentication.
The email arrives without a recognized sender or prior negotiation.
The visible signing brand differs from the supposed PDF service.
The action button points to an unrelated website.
The page requests an email password before showing anything.
Provider logos are used to make the form feel compatible and safe.
The contract description supplies urgency but no verifiable business context.
Submitting the form gives criminals a mailbox credential. It does not unlock a protected PDF or confirm a signature.
Why a Stolen Mailbox Matters
Email accounts hold far more than conversations. They receive password resets, invoices, cloud invitations, identity records, and private business discussions.
An attacker can search for valuable exchanges, impersonate the owner, or quietly monitor future messages through hidden forwarding rules.
Work accounts are especially attractive. A compromised mailbox can support payment diversion, supplier impersonation, payroll fraud, and convincing attacks against colleagues.
This campaign is credential phishing. Simply viewing the email is not the central danger. Clicking and entering a password creates the immediate exposure.
How the Contract Document To Review And Sign Email Scam Works
Step 1: A Formal Contract Notice Arrives Unexpectedly
The campaign begins with an email designed to resemble an automated electronic signature notification. Its tone is restrained, professional, and deliberately ordinary.
A settlement reference gives the impression that a legal or commercial process is already underway. Recipients may worry that ignoring it could delay business.
The message does not establish who negotiated the agreement. Instead, it uses broad language that could fit a customer, vendor, employer, or unfamiliar partner.
That ambiguity is useful to the sender. The recipient is encouraged to open the document to discover why it supposedly concerns them.
Step 2: Equipment and Purchase-Order Details Add Credibility
The sample mentioned a mid-rise scissor lift purchase order. Specific industrial wording makes a random email resemble paperwork from a real procurement chain.
Scammers do not need to know whether the target buys that equipment. They only need the description to feel plausible to some percentage of recipients.
Employees who process invoices, facilities requests, legal documents, or purchasing records face constant paperwork. Routine volume can weaken careful inspection.
A genuine contract should connect to known negotiations, named parties, and an expected sender. Technical product language cannot replace that history.
Step 3: The Review Button Opens an Unrelated Website
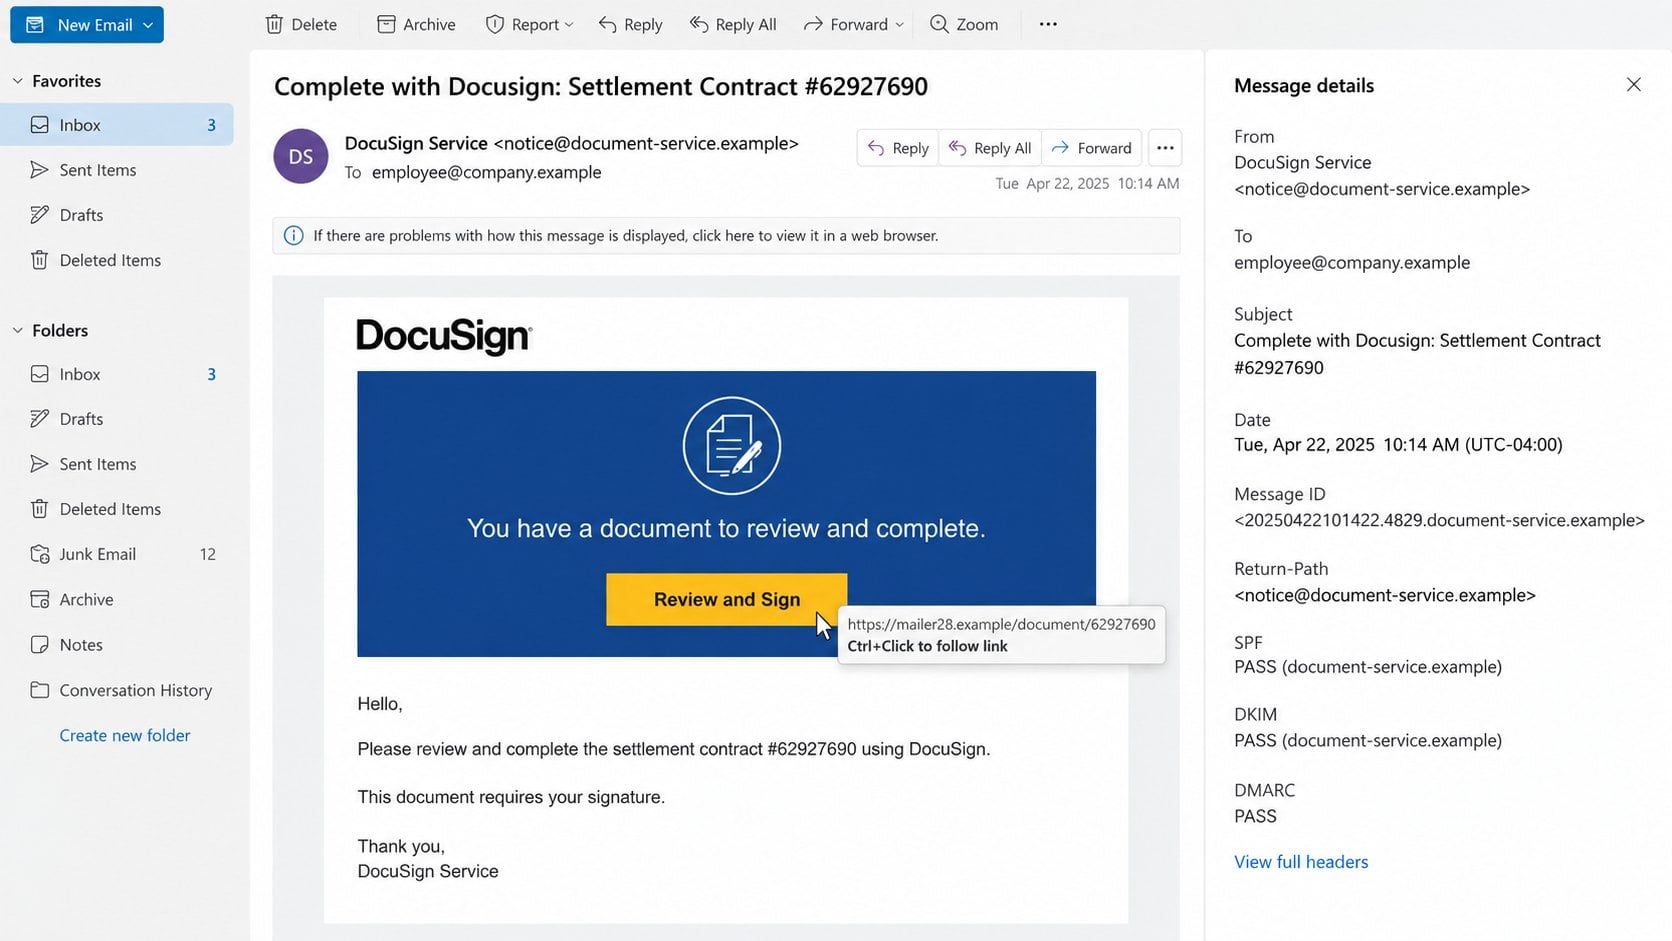
The “VIEW BUSINESS DOCUMENT” button looks like the normal next step. Its visible label reveals nothing about the actual destination.
In the analyzed path, the link used infrastructure unrelated to the signing service or the alleged parties. That mismatch is a decisive warning.
A familiar logo inside an email does not control where a button travels. The destination address is stronger evidence than the artwork surrounding it.
Redirects can also hide the final page from basic mail filters. Each intermediate site makes the route harder for recipients to understand.
Step 4: A Blurred PDF Creates an Authentication Excuse
The destination displays what appears to be a business contract, but its contents remain deliberately blurred. A centered form blocks the supposed document.
This visual arrangement is psychologically effective. It suggests the promised file is real, loaded, and only one familiar login away.
The page may offer Gmail, Outlook, or Yahoo choices. Those options are decorative cues, not proof that any provider authorized the site.
A document sender never needs the password to someone else’s email account. Authentication should occur only on the recipient’s established provider domain.
Step 5: The Counterfeit Form Records the Password
When a visitor enters an address and password, the page can transmit both values to the operator. It does not verify them safely.
Some phishing kits ask twice, claiming the first password was incorrect. That tactic captures alternate passwords from people who assume they mistyped.
Afterward, the site may show an error, display a harmless PDF, or redirect to a genuine service. None of those outcomes reverses the theft.
The criminal can test the credential quickly. Automated attempts may occur before the victim realizes that no meaningful contract appeared.
Step 6: The Compromised Account Supports a Second Attack
Successful access lets an intruder examine contacts, recent projects, payment conversations, and the language normally used by the account owner.
That information improves later impersonation. A fraudulent invoice sent within an existing thread can be much harder to recognize than the original lure.
Attackers may add inbox rules that hide security alerts or forward selected messages. Password changes alone may not remove those settings.
The original fake contract can also be sent from the compromised address to colleagues. A trusted internal sender makes the next recipient less suspicious.
How to Verify a Contract Notification Safely
Confirm the Agreement Through Existing Business Records
Search your calendar, contract system, procurement platform, and previous correspondence for the settlement number. Do not begin with the email button.
A legitimate signature request should follow some recognizable discussion. The parties, project, and purpose should not be mysteries resolved only after login.
If you work for an organization, ask the responsible legal or purchasing contact whether the envelope is expected. Share the message according to internal policy.
Inspect the Complete Sender and Destination
Expand the sender details instead of trusting the display name. Compare the address with earlier verified notices from the same signing platform.
Preview the button destination without opening it. A misspelled, newly introduced, or unrelated domain should stop the process immediately.
HTTPS does not prove ownership. A fraudulent site can encrypt traffic while collecting information for the person who operates it.
Reach the Signing Service Independently
Open the service through a saved bookmark, its official application, or an address already used by your organization. Check for the envelope there.
Do not paste an email password into a document viewer. Legitimate access may use a dedicated account, secure link, or company identity system.
If the contract is absent, contact the purported sender through a known number or established email thread. Avoid reply details supplied by the suspicious message.
Evaluate the Document Story, Not Just the Design
Ask whether the described purchase belongs to your role or company. An unfamiliar scissor lift order deserves verification before any digital action.
Check whether names, dates, reference numbers, and organizations agree with one another. Scammers often combine realistic fragments that lack a coherent relationship.
A genuine sender can explain the agreement without demanding your mailbox password. Pressure to authenticate before receiving basic context is not normal.
What to Do If You Fell Victim to the Contract Document Email Scam
Stay calm and respond according to what you entered or opened. Fast containment can greatly reduce the value of a stolen credential.
Close the phishing page and preserve the email.
Do not retry the form or experiment with another password. Save the original message, headers, destination, and approximate time of interaction.
Workplace users should notify their security team immediately. Administrators may need those details to find related messages across the organization.
Change the exposed password from a trusted route.
Open the genuine mail service directly and create a unique replacement. Never use a recovery link supplied by the suspicious message.
If that password protected other accounts, replace every reuse. Prioritize financial services, cloud storage, business systems, and social accounts.
Terminate sessions and strengthen authentication.
Review active devices, recent logins, recovery addresses, application passwords, and connected applications. Remove anything you do not recognize.
Enable multifactor authentication with a passkey, authenticator application, or security key when available. Save recovery codes somewhere protected.
Check the mailbox for hidden changes.
Inspect forwarding addresses, filters, inbox rules, delegates, sent mail, and deleted folders. Undo unauthorized settings before normal use resumes.
Look for security notifications that may have been hidden. A rule targeting words like “password” or “invoice” can reveal deliberate persistence.
Warn people exposed through the account.
Tell colleagues or contacts if suspicious messages were sent. Include the subject and timing, but do not forward a live phishing button.
Ask finance teams to verify bank-detail changes independently. An intruder may use known conversations to redirect legitimate payments.
Scan any downloaded content.
This documented path focused on password theft, but related campaigns can deliver harmful files. Run a complete Malwarebytes scan after opening an unexpected download.
AdGuard can block many known phishing and advertising domains. Keep it enabled as an added layer, while still verifying every unexpected contract.
Report losses and suspicious access.
Use the mail provider’s phishing report feature and follow workplace incident procedures. Record dates, actions, and support case numbers.
If money or identity documents were exposed, contact the relevant bank and fraud-reporting authority promptly. Ask what protective measures apply locally.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Anti-Malware Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
Adware — the cause of those annoying pop-ups
Browser hijackers — unwanted redirects and changed homepages
Trojans and spyware — hidden programs stealing your data
Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The whole process takes about 5 minutes.
Malwarebytes for WindowsMalwarebytes for MacMalwarebytes for Android
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
(The link opens in a new page where your download will start)
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.
Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.
Malwarebytes will now install on your device. This usually takes under a minute.
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.
On the final screen, click Open Malwarebytes to launch the program.
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.
In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.
Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take several minutes. Feel free to do something else — just check back occasionally to see the progress.
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.
Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, your PC is clean and you can continue with the next steps in this guide.
When the scan finishes, click Quarantine to remove everything Malwarebytes found. That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If your current antivirus allowed this malicious program on your computer, you may want to consider purchasing Malwarebytes Premium to protect against these types of threats in the future. If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.
When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.
Once the scan is done, remove every threat it detected. Your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If your current antivirus allowed a malicious program on your computer, you might want to consider purchasing the full-featured version of Malwarebytes Anti-Malware to protect against these types of threats in the future. If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.
When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options. This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue. Tap on “Got it” to proceed to the next step. Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue. Tap on “Allow” to permit Malwarebytes to access the files on your phone.
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.
Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
After the scan, tap Remove Selected to delete all detected threats. Your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If your current antivirus allowed a malicious app on your phone, you may want to consider purchasing the full-featured version of Malwarebytes to protect against these types of threats in the future. If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
Contracts carry natural authority. They imply deadlines, obligations, and decisions that may involve managers, customers, or legal teams.
The scam exploits uncertainty rather than making an outrageous promise. A recipient clicks because they want context, not because they expect a reward.
Electronic signature notices are also common. Familiarity trains people to move from inbox to browser with little conscious inspection.
A long reference number reinforces the appearance of an established workflow. Random digits feel administrative even when they match no internal record.
The blurred document completes the illusion. The visitor sees enough structure to believe a file exists but not enough information to verify it.
Teams can reduce this risk by establishing predictable contract channels. Employees should know which platforms, domains, and internal contacts handle signatures.
Business Protections That Limit the Damage
Mail filtering helps, but business procedures matter just as much. A single stolen account should not authorize a payment or contractual change.
Require secondary confirmation for new bank details, unusual purchases, and sensitive documents. Use a known telephone number, not contact data inside the request.
Restrict automatic forwarding where practical. Alerts for new rules, unfamiliar logins, and impossible travel can expose compromised mailboxes sooner.
Modern authentication reduces password-only attacks. Passkeys and security keys are harder for a counterfeit form to capture and reuse.
Employees need a quick reporting method. A suspicious email should be easy to submit without fear that asking for help will cause delay or criticism.
Security teams can search for the same subject, sender infrastructure, and button destination. Removing copies protects people who have not opened them.
Legal and procurement staff should publish the expected signature process. Consistency gives employees concrete details to compare with unexpected notices.
External partners should be told how changes are communicated. A verified onboarding message prevents a surprise domain from appearing legitimate later.
Organizations should also monitor compromised-account indicators. Outbound contract lures, unusual forwarding, and repeated login failures deserve prompt investigation.
These controls turn one employee’s moment of uncertainty into a manageable event. They also stop credential theft from becoming payment fraud.
Frequently Asked Questions
Is the Settlement Contract #62927690 real?
The number appeared in a phishing campaign and did not identify a verified agreement. Confirm any similarly numbered contract through your own business records.
Are DocuSign or Adobe responsible for this email?
No. Criminals copied familiar document language and branding. The legitimate companies do not control the unrelated phishing websites used in the campaign.
Can opening the message alone steal my password?
The primary documented risk begins after following the button and submitting credentials. Reading the email does not automatically reveal your password.
Why does the fake page offer several email providers?
Provider choices make the trap appear universal and trustworthy. They route visitors into counterfeit forms rather than protected provider authentication.
What if I clicked but entered nothing?
Close the page and clear any downloaded files. A password change is generally unnecessary unless credentials were entered or another suspicious event occurred.
Should I reply and ask whether the contract is genuine?
Do not reply to the questionable message. Contact the alleged sender through an established conversation, known telephone number, or verified business directory.
The Bottom Line
The Contract Document To Review And Sign email is a credential trap disguised as routine electronic paperwork. Its button leads to a counterfeit password form.
Verify the agreement outside the email, inspect the destination, and never give a document viewer your mailbox password. That pause prevents the entire chain.
10 Rules to Avoid Online Scams
Here are 10 practical safety rules to help you avoid malware, online shopping scams, crypto scams, and other online fraud. Each tip includes a quick “if you already got hit” action.
Stop and verify before you click, log in, download, or pay.
Most scams win by creating urgency. Verify using a trusted method: type the website address yourself, use the official app, or call a known number (not the one in the message).
If you already clicked: close the page, do not enter passwords, and run a malware scan.
Keep your operating system, browser, and apps updated.
Updates patch security holes used by malware and malicious ads. Turn on automatic updates where possible.
If you saw a scary “update now” pop-up: close it and update only through your device settings or the official app store.
Use layered protection: antivirus plus an ad blocker.
Antivirus helps block malware. An ad blocker reduces scam redirects, phishing pages, and malvertising.
If your browser is acting weird: remove unknown extensions, reset the browser, then run a full scan.
Install apps, software, and extensions only from official sources.
Avoid cracked software, “keygens,” and random downloads. During installs, choose Custom/Advanced and decline bundled offers you do not recognize.
If you already installed something suspicious: uninstall it, restart, and scan again.
Treat links and attachments as untrusted by default.
Phishing often impersonates delivery services, banks, and popular brands. If it is unexpected, do not open attachments or log in through the message.
If you entered credentials: change the password immediately and enable 2FA.
Shop safely: research the store, then pay with protection.
Be cautious with brand-new stores, “closing sale” stories, and prices that make no sense. Prefer credit cards or PayPal for dispute options. Avoid wire transfers, gift cards, and crypto payments.
If you already paid: contact your card issuer or PayPal quickly to dispute the transaction.
Crypto rule: never pay a “fee” to withdraw or recover money.
Common patterns include fake profits, then “tax,” “gas,” or “verification” fees. Another is a “recovery agent” who demands upfront crypto.
If you already sent crypto: stop paying, save evidence (wallet addresses, TXIDs, chats), and report the scam to the platform used.
Secure your accounts with unique passwords and 2FA (start with email).
Use a password manager and unique passwords for every account. Enable 2FA using an authenticator app when possible.
If you suspect an account takeover: change passwords, sign out of all devices, and review recent logins and recovery settings.
Back up important files and keep one backup offline.
Backups protect you from ransomware and device failure. Keep at least one backup on an external drive that is not always connected.
If you suspect infection: do not connect backup drives until the system is clean.
If you think you are a victim: stop losses, document evidence, and escalate fast.
Move quickly. Speed matters for disputes, account recovery, and limiting damage.
Stop payments and contact: do not send more money or respond to the scammer.
Call your bank or card issuer: block transactions, replace the card if needed, and start a dispute or chargeback.
Secure your email first: change the email password, enable 2FA, and remove unfamiliar recovery options.
Secure other accounts: change passwords, enable 2FA, and log out of all sessions.
Scan your device: remove suspicious apps or extensions, then run a full malware scan.
Save evidence: screenshots, emails, order pages, tracking pages, wallet addresses, TXIDs, and chat logs.
Report it: to the payment provider, marketplace, social platform, exchange, or wallet service involved.
These rules are intentionally simple. Most online losses happen when decisions are rushed. Slow down, verify independently, and use payment methods and account controls that give you recourse.
Hello! I'm Lapain Epuran, your go-to source for detailed and honest product reviews. From tech gadgets to miracle cures, I provide insights to help you make informed choices. Join me as we discover what's truly worth your time and money.