Protect reused accounts. Replace the same or similar password anywhere else, beginning with banking, cloud storage, and workplace systems.
Scan the device with Malwarebytes. A phishing page usually steals data, but Malwarebytes can find unwanted downloads or malware introduced during the visit.
Notify administrators and contacts. Business security teams can review logs, while contacts should ignore suspicious messages sent from the compromised account.
Review financial exposure. Check password-reset emails, purchases, transfers, and saved payment services for actions you did not authorize.
Block repeat phishing attempts. AdGuard can filter many malicious advertising links, tracking redirects, and known scam pages before they open.
Report the original email. Use the provider’s phishing-report function, preserve headers, then remove the message from the inbox.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Anti-Malware Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
Adware — the cause of those annoying pop-ups
Browser hijackers — unwanted redirects and changed homepages
Trojans and spyware — hidden programs stealing your data
Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The whole process takes about 5 minutes.
Malwarebytes for WindowsMalwarebytes for MacMalwarebytes for Android
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
(The link opens in a new page where your download will start)
Install Malwarebytes
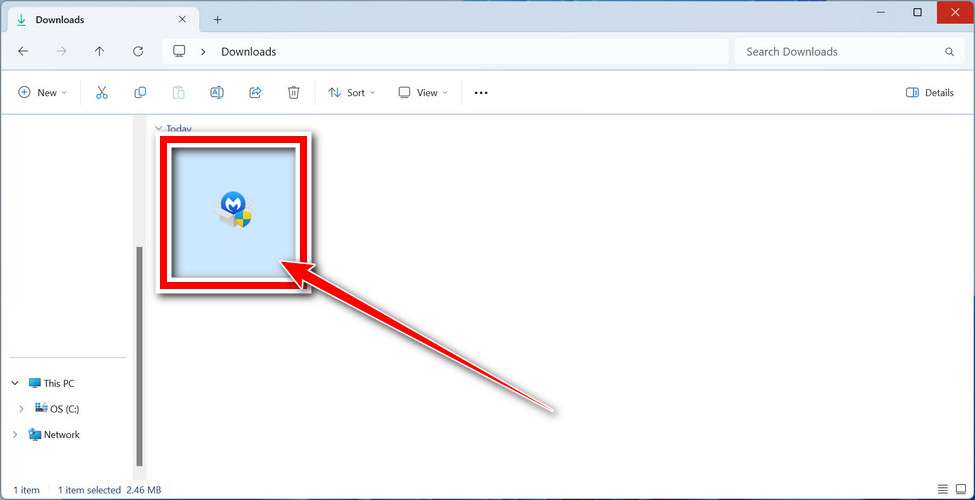
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.
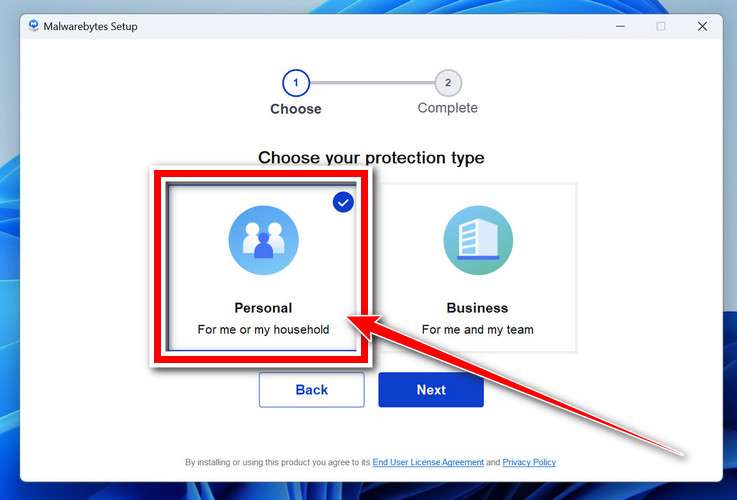
Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.
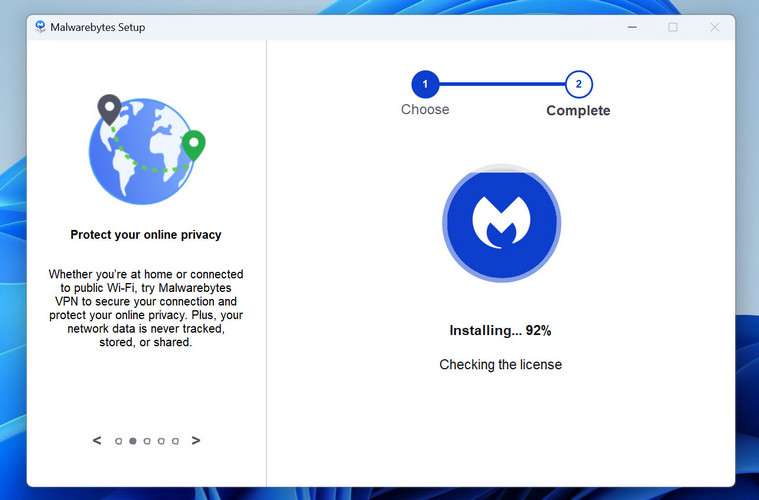
Malwarebytes will now install on your device. This usually takes under a minute.
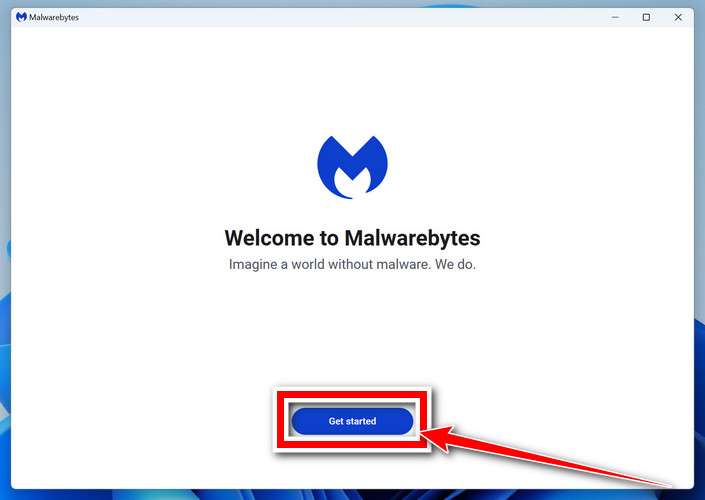
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.
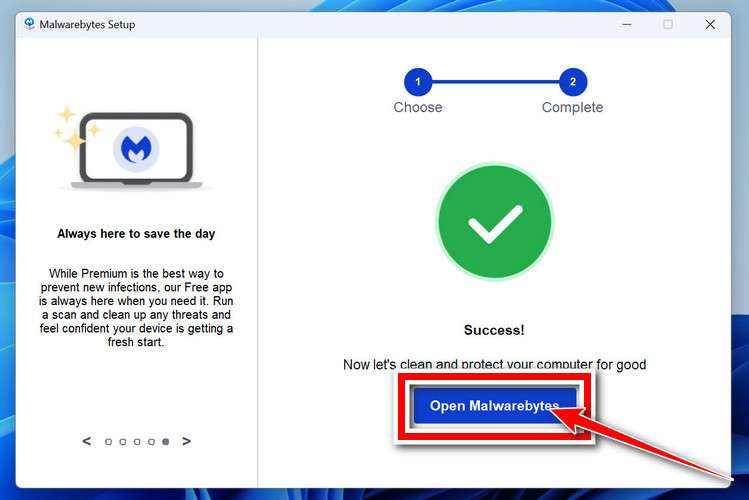
On the final screen, click Open Malwarebytes to launch the program.
Enable “Scan for Rootkits”
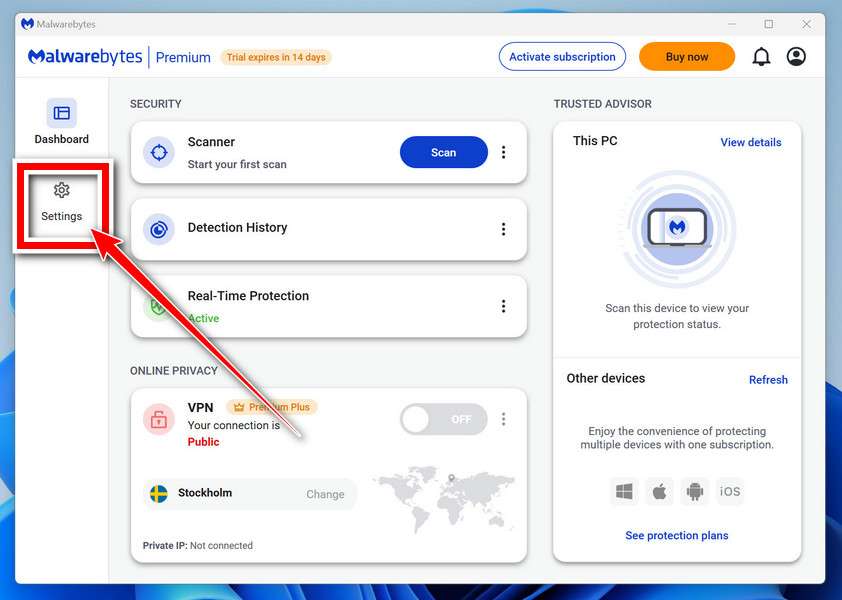
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.
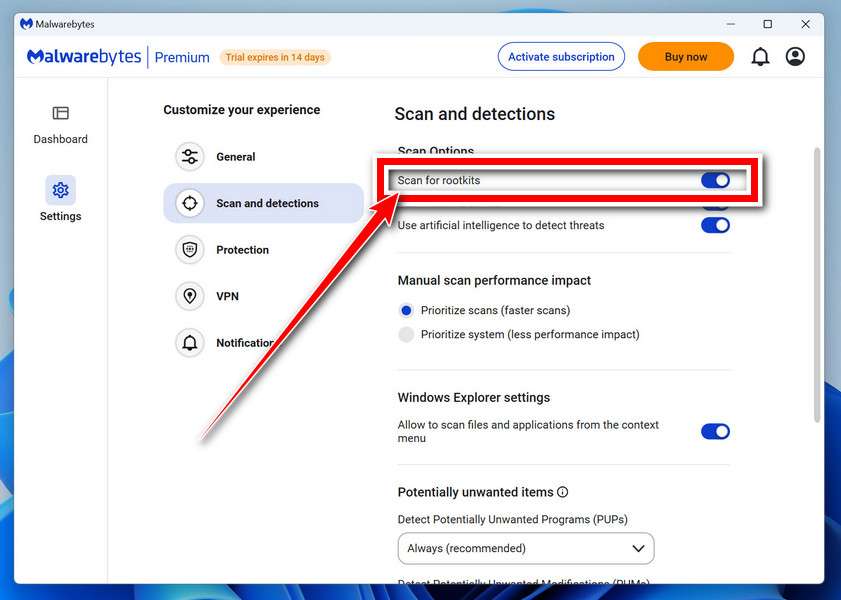
In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.
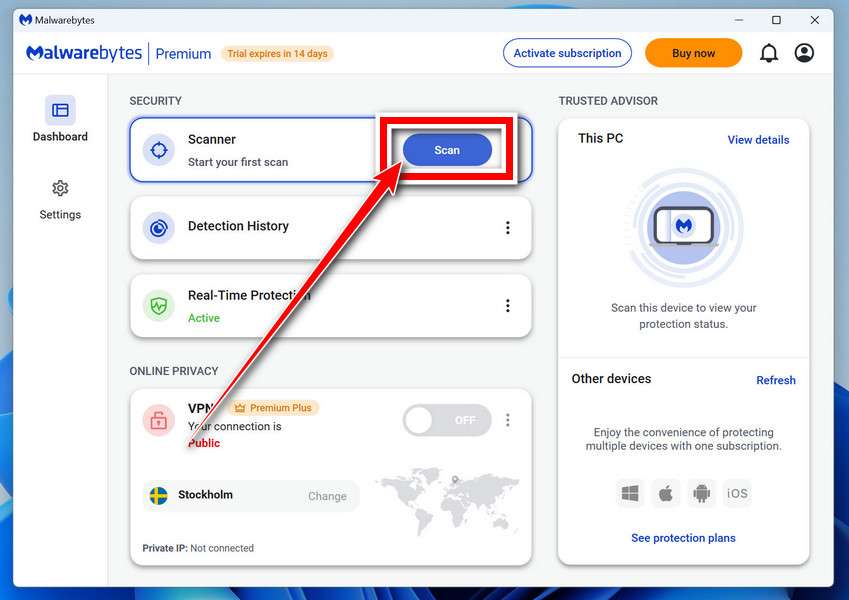
Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
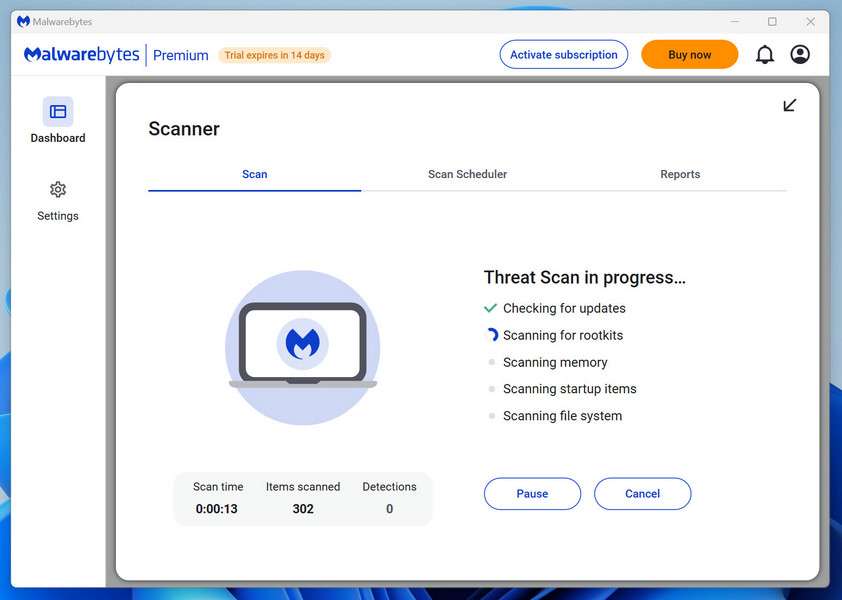
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take several minutes. Feel free to do something else — just check back occasionally to see the progress.
Quarantine the Detected Threats
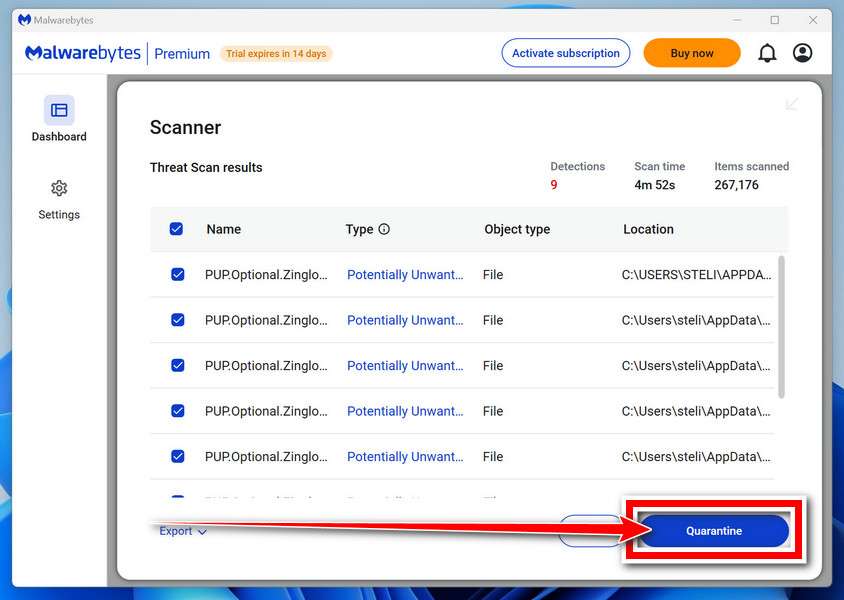
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.
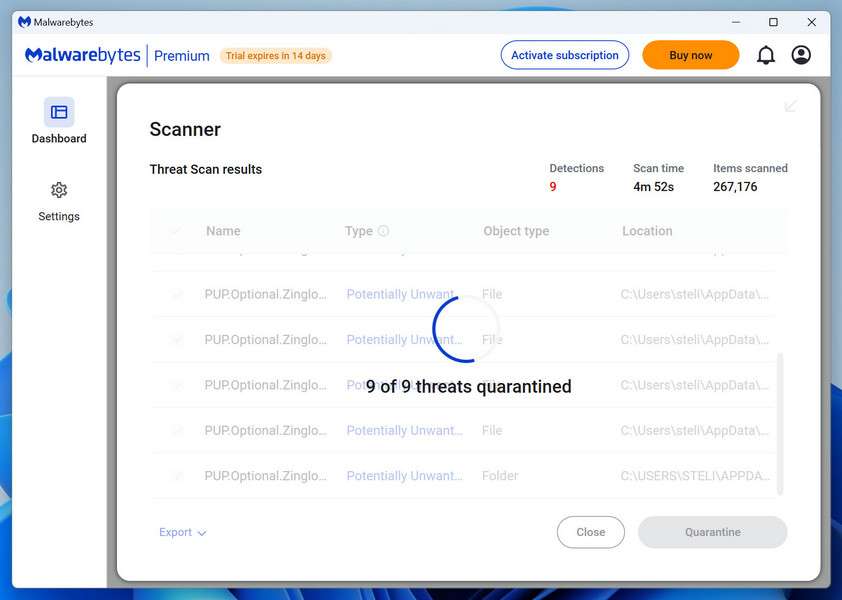
Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.
Restart Your Computer
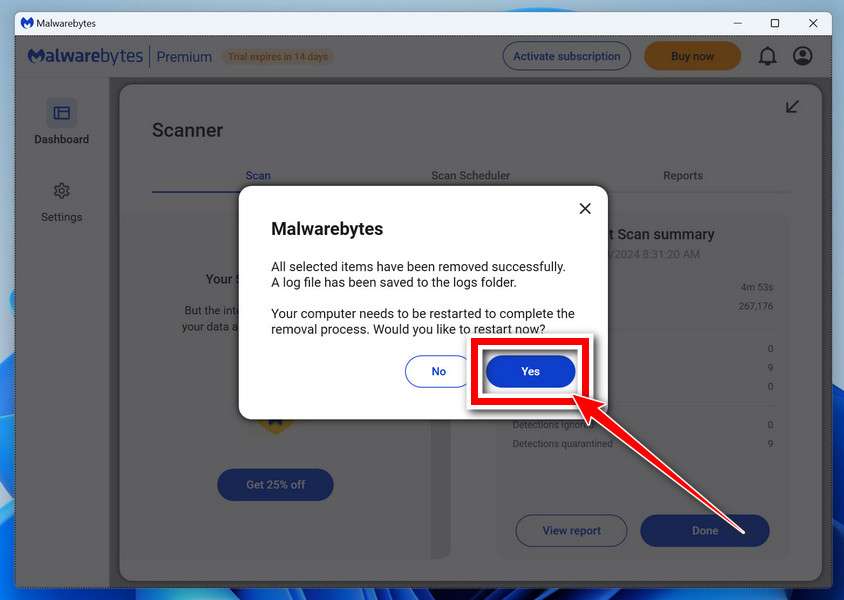
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, your PC is clean and you can continue with the next steps in this guide.
When the scan finishes, click Quarantine to remove everything Malwarebytes found. That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If your current antivirus allowed this malicious program on your computer, you may want to consider purchasing Malwarebytes Premium to protect against these types of threats in the future. If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
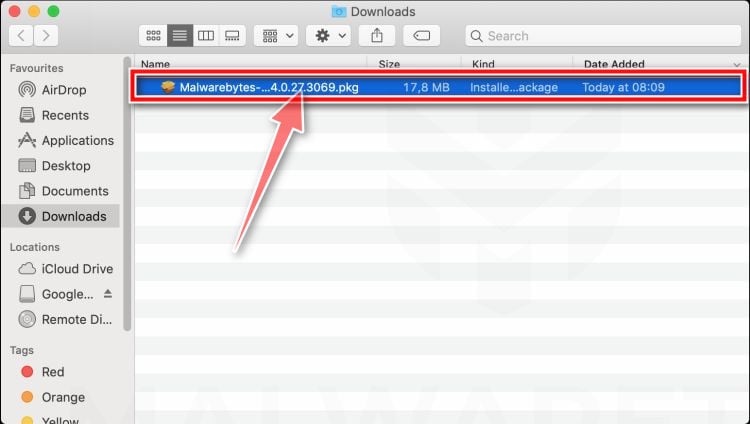
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.
Follow the On-Screen Prompts to Install Malwarebytes
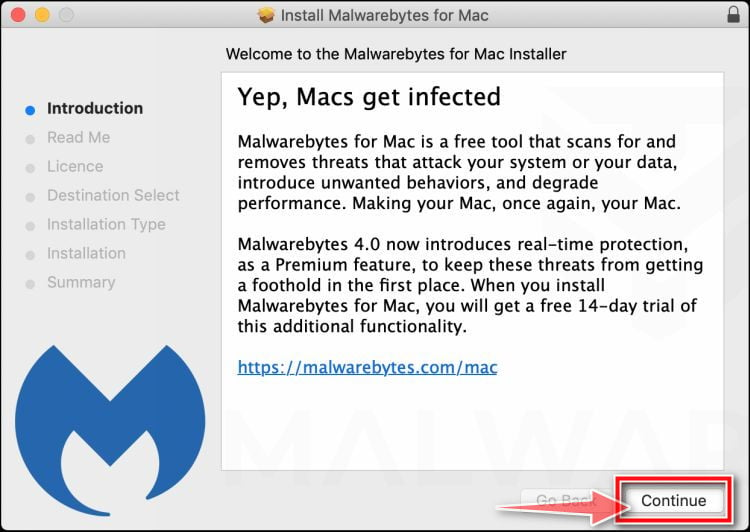
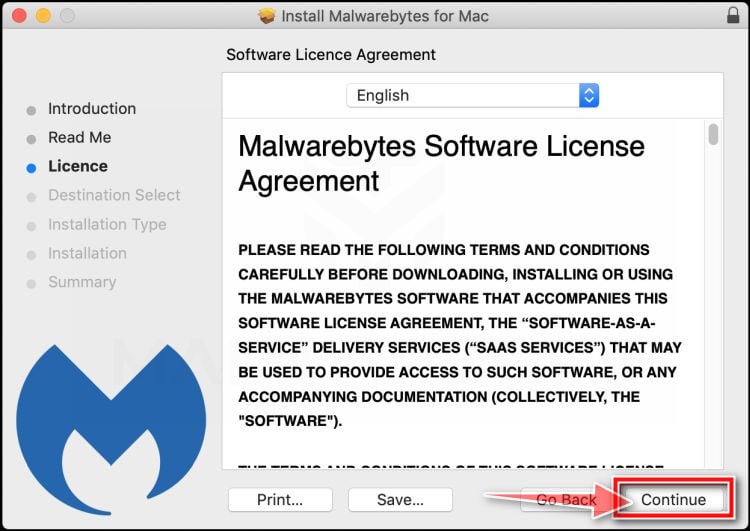
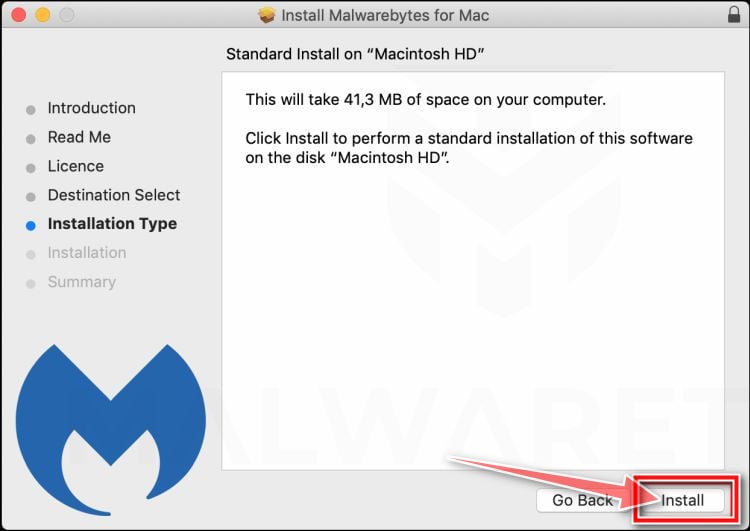
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.
When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
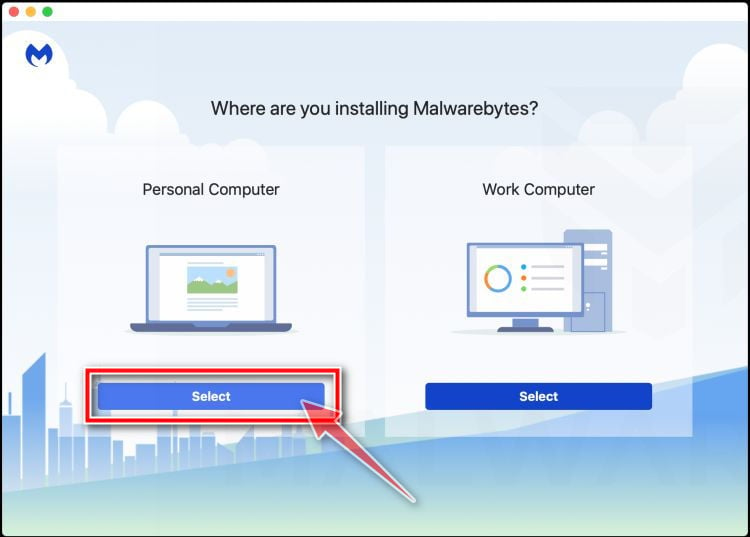
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.
Start the Scan
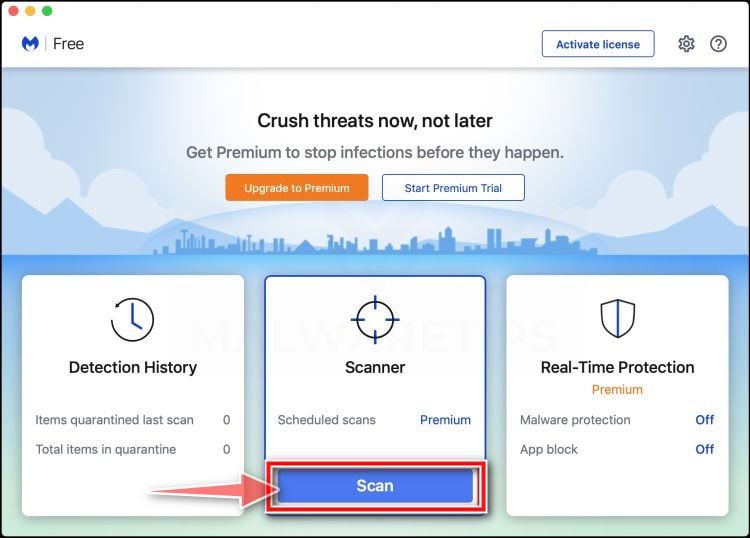
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.
Wait for the Scan to Finish
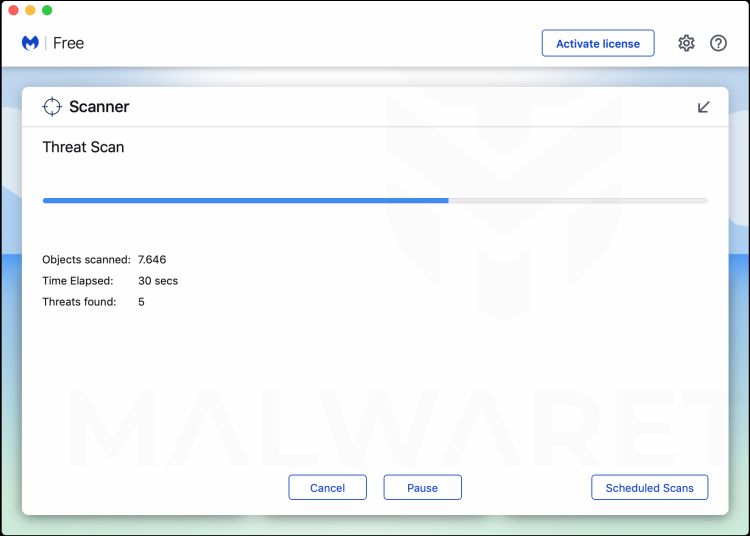
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.
Quarantine the Detected Threats
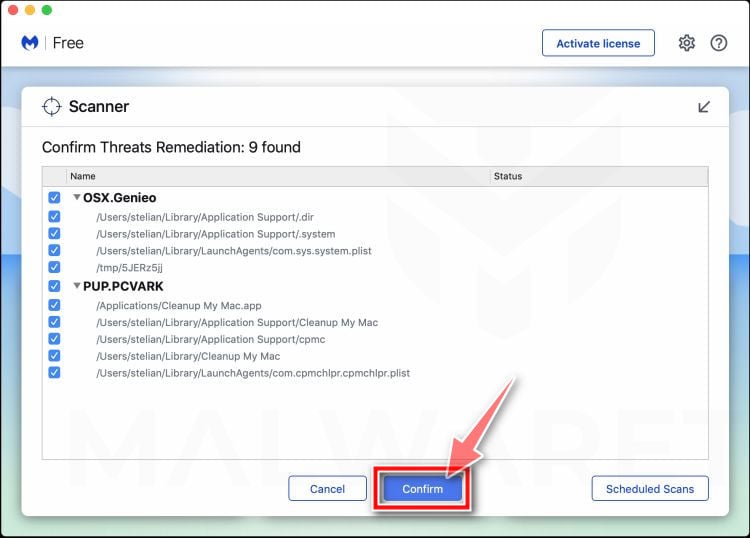
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.
Restart Your Mac
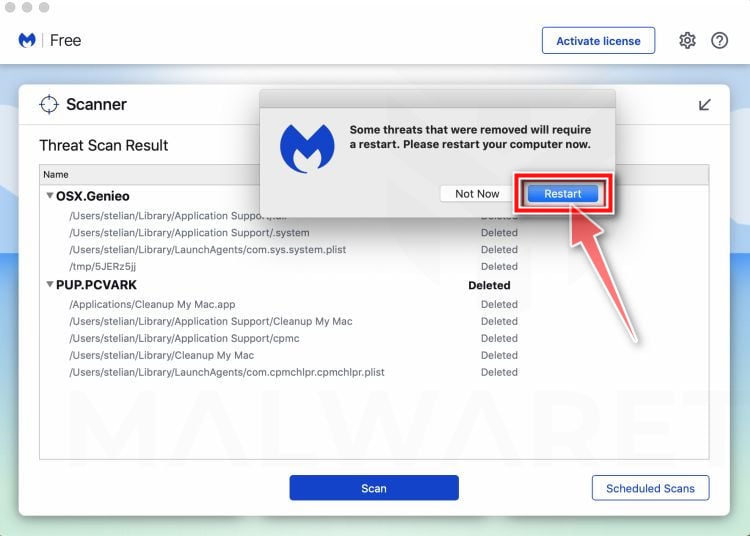
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.
Once the scan is done, remove every threat it detected. Your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If your current antivirus allowed a malicious program on your computer, you might want to consider purchasing the full-featured version of Malwarebytes Anti-Malware to protect against these types of threats in the future. If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
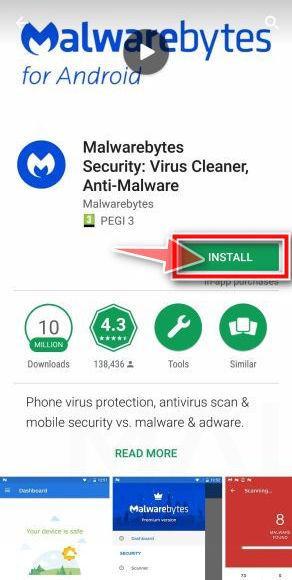
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.
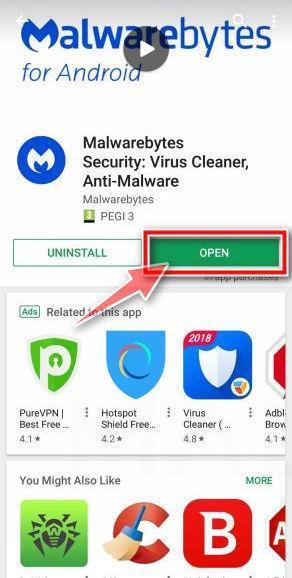
When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.
Follow the on-screen prompts to complete the setup process
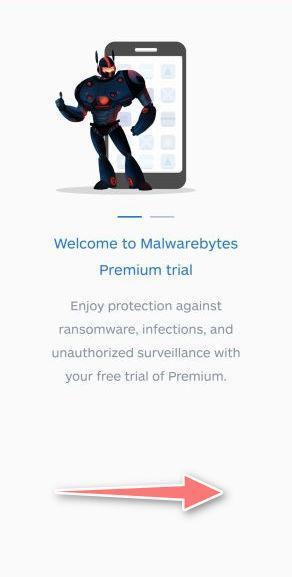
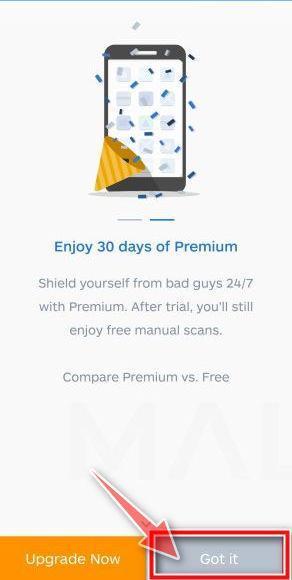
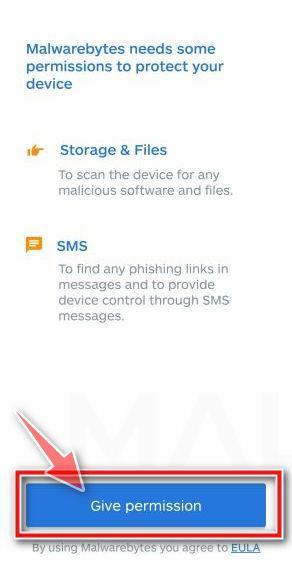
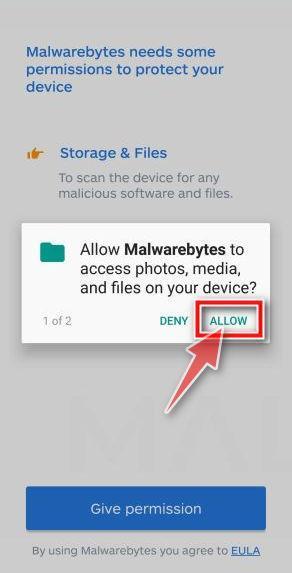
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options. This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue. Tap on “Got it” to proceed to the next step. Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue. Tap on “Allow” to permit Malwarebytes to access the files on your phone.
Update database and run a scan with Malwarebytes for Android
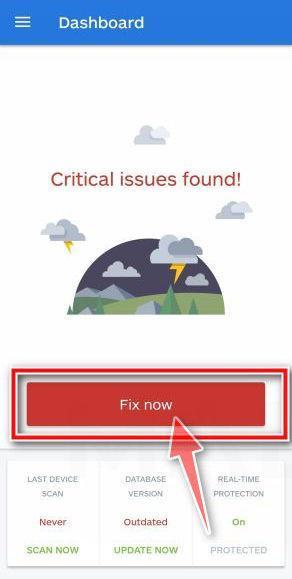
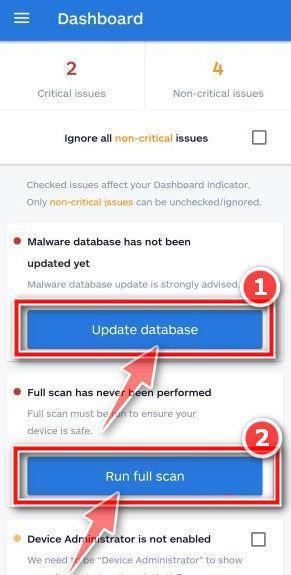
You will now be prompted to update the Malwarebytes database and run a full system scan.
Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.
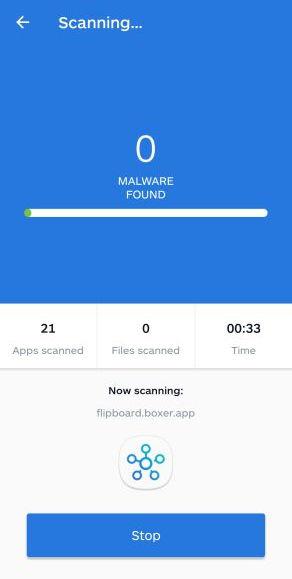
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.
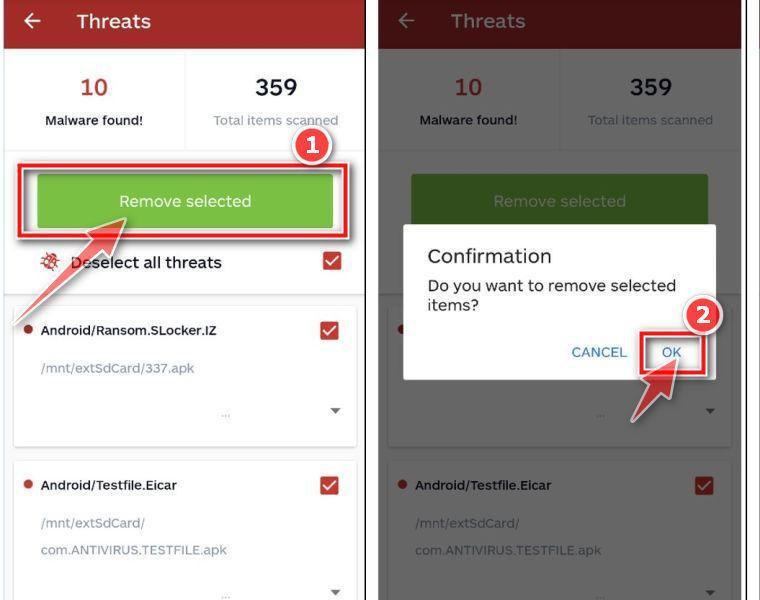
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
After the scan, tap Remove Selected to delete all detected threats. Your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If your current antivirus allowed a malicious app on your phone, you may want to consider purchasing the full-featured version of Malwarebytes to protect against these types of threats in the future. If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
When expected mail is missing, contact the sender through a known phone number or separate conversation.
Ask whether the message bounced and request the exact error returned by their mail system.
Check spam, quarantine, blocked-sender lists, storage usage, and filtering rules from the genuine mailbox settings.
Business users can ask administrators to trace the message identifier through server logs.
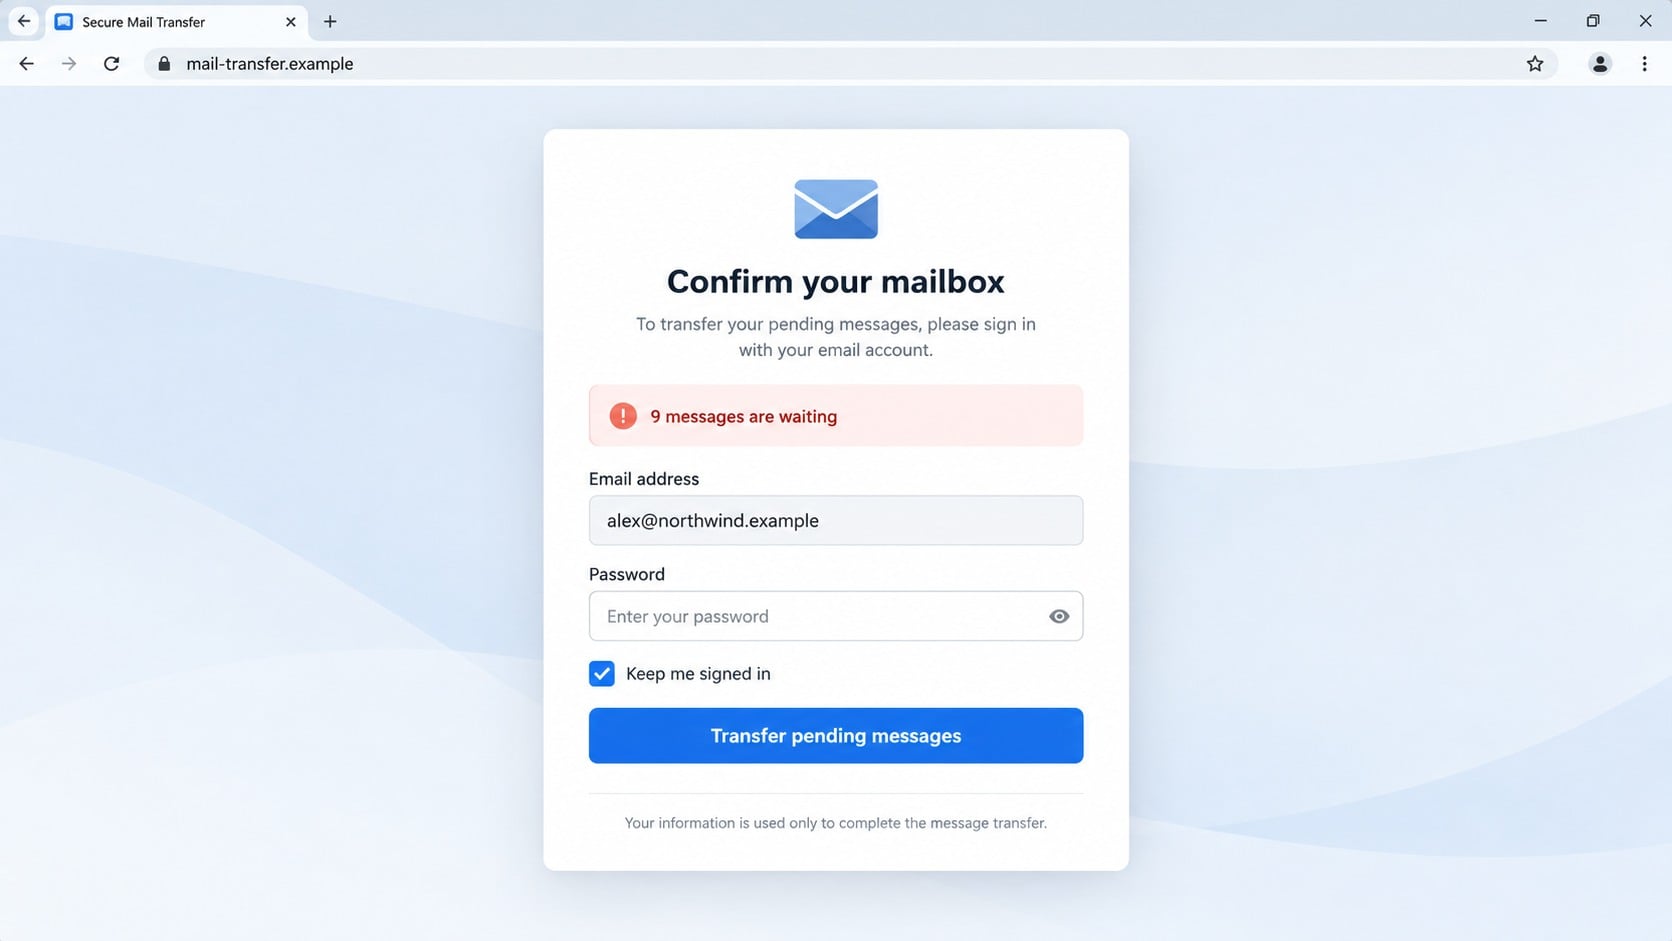
Real providers do not need your password again through a link to release individual incoming messages.
A service can ask you to sign in, but you should navigate there independently rather than following unsolicited email controls.
Read the address bar before entering credentials, including every character before the first slash.
Password managers provide a useful warning because they generally refuse to autofill credentials on an unrelated domain.
Pause when a message withholds essential details while demanding urgent action.
Legitimate operations can survive an independent verification call. Phishing depends on preventing one.
If the Stolen Password Was Reused Elsewhere
Assume every account using the same password is exposed, even when no suspicious activity has appeared yet.
Begin with the recovery email, financial services, cloud storage, shopping accounts, social networks, and employer systems.
Create a different replacement for each service instead of making one new password and repeating the mistake.
A password manager can generate and store long unique credentials without relying on memorable patterns.
Check breach notifications and login histories for automated attempts that began shortly after the phishing submission.
Remove unknown devices and refresh backup codes wherever an account supports multifactor protection.
Continue watching for reset messages because criminals sometimes return days later after testing a stolen credential list.
Tell your workplace security team if any reused password belonged to a company system or remote-access service.
Frequently Asked Questions
Are nine messages actually waiting for transfer?
No evidence supports that claim. The count is part of the lure and does not come from the recipient’s real mail server.
Can opening the email alone steal my password?
Normally, the dangerous step is clicking and submitting information. Remote images may still confirm that an address is active.
What if the login page showed my email address already?
Phishing links can include the address as a parameter. Prefilled information does not prove that the page belongs to your provider.
Does a padlock make the transfer page safe?
No. Encryption protects data traveling to the site, including data sent securely to a criminal-controlled server.
Why would scammers want an ordinary email account?
Mailboxes support password resets, identity research, contact impersonation, invoice fraud, and access to linked cloud services.
Should I scan if I only typed my password?
Secure the account first. A scan remains sensible if the page downloaded anything, requested permissions, or behaved unexpectedly.
The Bottom Line
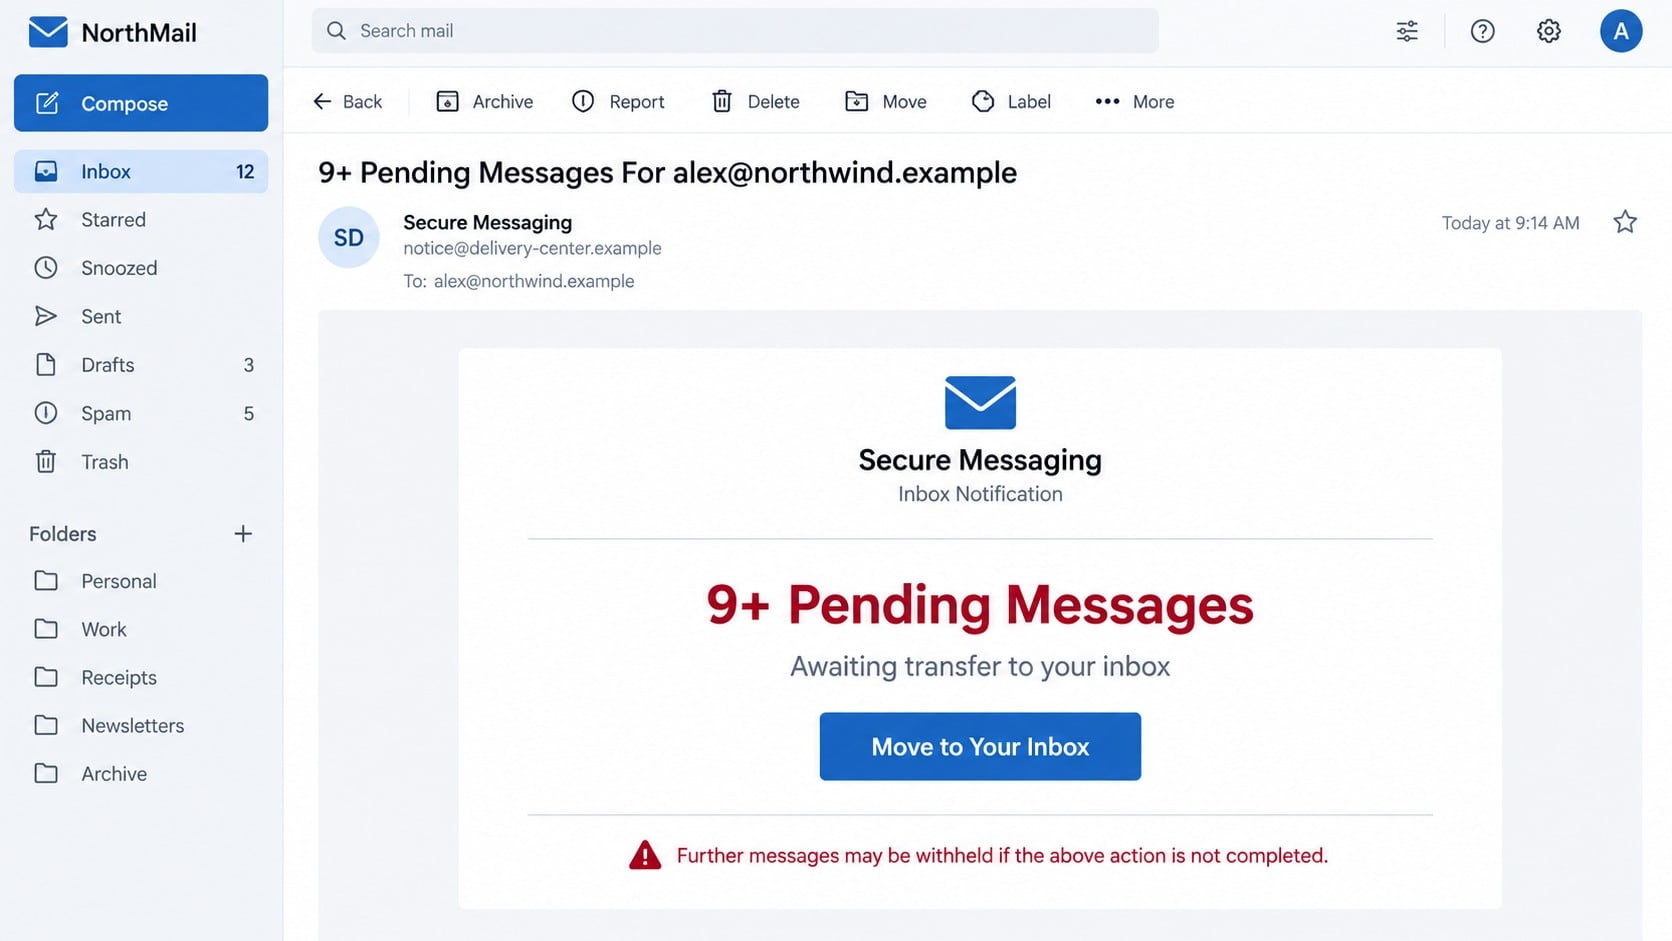
The Pending Messages Awaiting Transfer email invents an invisible queue so a fake delivery button can lead recipients into credential theft.
Verify mail problems inside the official account, never through the alert, and act quickly if any password was entered.
10 Rules to Avoid Online Scams
Here are 10 practical safety rules to help you avoid malware, online shopping scams, crypto scams, and other online fraud. Each tip includes a quick “if you already got hit” action.
Stop and verify before you click, log in, download, or pay.
Most scams win by creating urgency. Verify using a trusted method: type the website address yourself, use the official app, or call a known number (not the one in the message).
If you already clicked: close the page, do not enter passwords, and run a malware scan.
Keep your operating system, browser, and apps updated.
Updates patch security holes used by malware and malicious ads. Turn on automatic updates where possible.
If you saw a scary “update now” pop-up: close it and update only through your device settings or the official app store.
Use layered protection: antivirus plus an ad blocker.
Antivirus helps block malware. An ad blocker reduces scam redirects, phishing pages, and malvertising.
If your browser is acting weird: remove unknown extensions, reset the browser, then run a full scan.
Install apps, software, and extensions only from official sources.
Avoid cracked software, “keygens,” and random downloads. During installs, choose Custom/Advanced and decline bundled offers you do not recognize.
If you already installed something suspicious: uninstall it, restart, and scan again.
Treat links and attachments as untrusted by default.
Phishing often impersonates delivery services, banks, and popular brands. If it is unexpected, do not open attachments or log in through the message.
If you entered credentials: change the password immediately and enable 2FA.
Shop safely: research the store, then pay with protection.
Be cautious with brand-new stores, “closing sale” stories, and prices that make no sense. Prefer credit cards or PayPal for dispute options. Avoid wire transfers, gift cards, and crypto payments.
If you already paid: contact your card issuer or PayPal quickly to dispute the transaction.
Crypto rule: never pay a “fee” to withdraw or recover money.
Common patterns include fake profits, then “tax,” “gas,” or “verification” fees. Another is a “recovery agent” who demands upfront crypto.
If you already sent crypto: stop paying, save evidence (wallet addresses, TXIDs, chats), and report the scam to the platform used.
Secure your accounts with unique passwords and 2FA (start with email).
Use a password manager and unique passwords for every account. Enable 2FA using an authenticator app when possible.
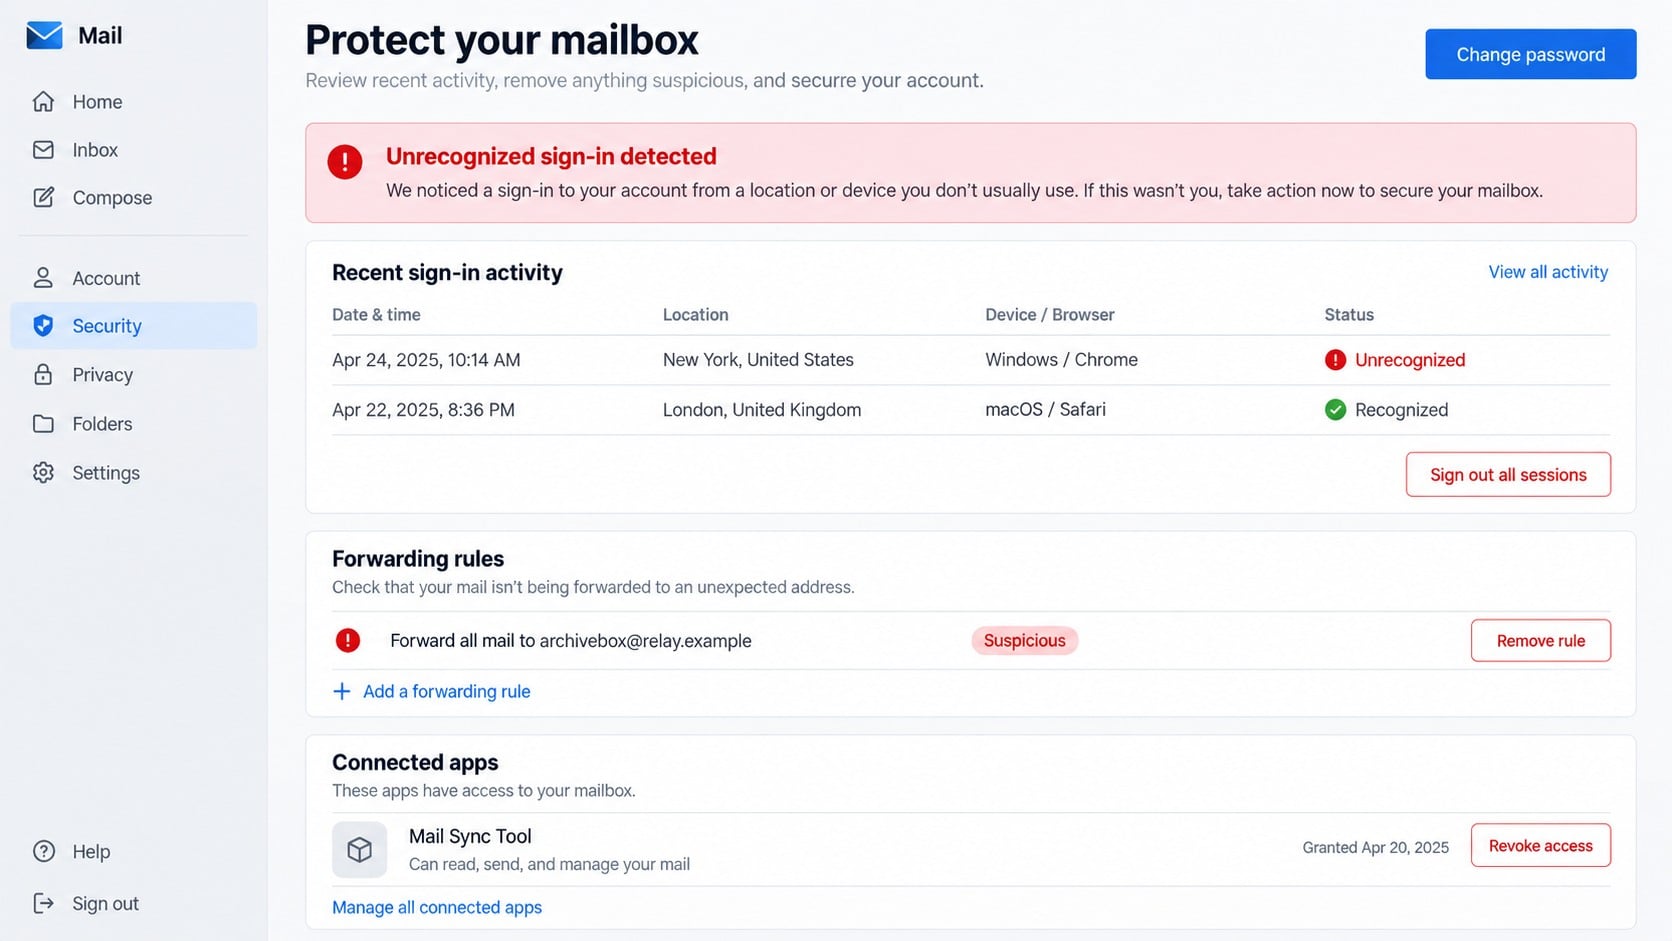
If you suspect an account takeover: change passwords, sign out of all devices, and review recent logins and recovery settings.
Back up important files and keep one backup offline.
Backups protect you from ransomware and device failure. Keep at least one backup on an external drive that is not always connected.
If you suspect infection: do not connect backup drives until the system is clean.
If you think you are a victim: stop losses, document evidence, and escalate fast.
Move quickly. Speed matters for disputes, account recovery, and limiting damage.
Stop payments and contact: do not send more money or respond to the scammer.
Call your bank or card issuer: block transactions, replace the card if needed, and start a dispute or chargeback.
Secure your email first: change the email password, enable 2FA, and remove unfamiliar recovery options.
Secure other accounts: change passwords, enable 2FA, and log out of all sessions.
Scan your device: remove suspicious apps or extensions, then run a full malware scan.
Save evidence: screenshots, emails, order pages, tracking pages, wallet addresses, TXIDs, and chat logs.
Report it: to the payment provider, marketplace, social platform, exchange, or wallet service involved.
These rules are intentionally simple. Most online losses happen when decisions are rushed. Slow down, verify independently, and use payment methods and account controls that give you recourse.
Hello! I'm Lapain Epuran, your go-to source for detailed and honest product reviews. From tech gadgets to miracle cures, I provide insights to help you make informed choices. Join me as we discover what's truly worth your time and money.