

An email says a payment has cleared, with a remittance document ready to view. For an accounts team, that sounds like routine reconciliation.
Then the document takes an unexpected detour. Before following its instructions, look closely at what it wants your computer to do.
Overview
A settlement notice aimed at everyday finance work
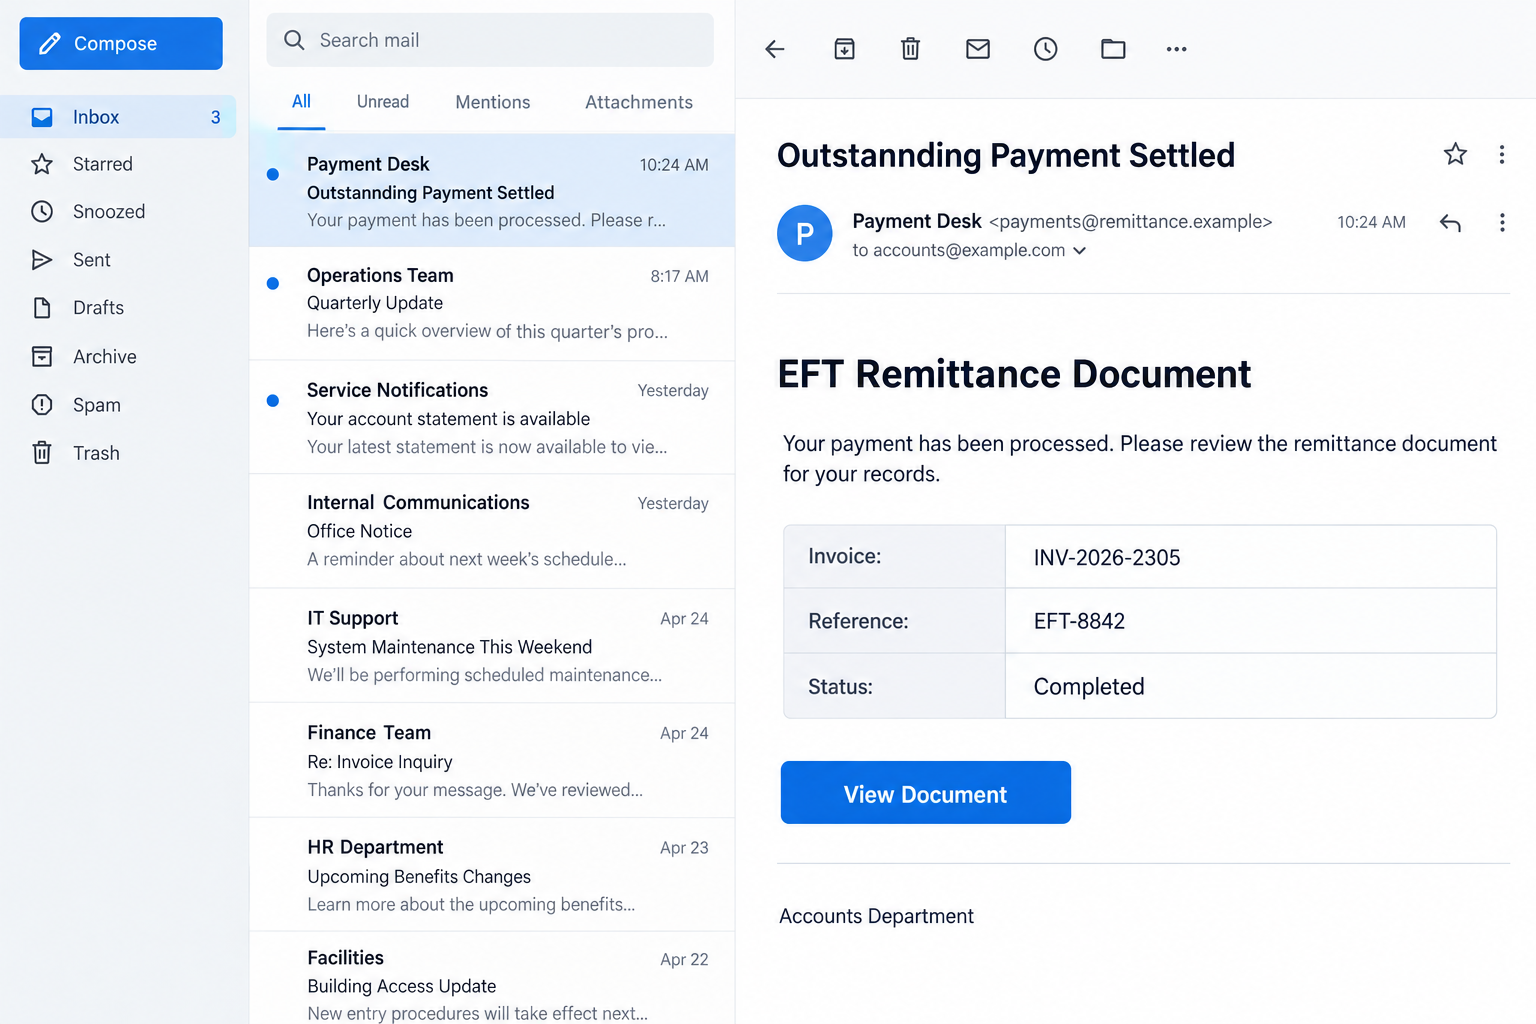
The EFT Remittance Document email virus campaign disguises malicious software delivery as a payment notification. The message invites recipients to view supporting paperwork for a settled payment.
A reported version borrows the RemitPay name and uses the subject “Outstannding Payment Settled.” It includes invoice and transfer references to resemble an accounts-receivable record.
The image above illustrates that kind of message with fictional contact details. It is not an original recipient’s email or evidence of a real payment.
The document becomes an alleged Adobe update
Instead of simply opening remittance information, the link leads to a page claiming Adobe Acrobat Reader needs updating. A download is presented as the way forward.
The reported file is Adobe Installer Latest Version 2.01.bat. Despite its reassuring name, a Windows batch file contains executable instructions, not a viewable payment document.
This is a malware-delivery lure. The specific malware family has not been established here, so claims about a particular stealer, ransomware strain, or confirmed theft would be speculation.
Where the risk changes
- Receiving the email does not mean a payment exists or malware has run.
- Following the document link exposes you to an untrusted update prompt.
- Saving a batch file is different from executing its instructions.
- Running it, approving elevation, or following additional commands can create a serious device incident.
- RemitPay and Adobe branding does not establish either company’s involvement in the attack.
The safe decision is to stop at the unexpected software requirement. Verify the payment separately and obtain any genuine Reader update through a trusted Adobe route.
What a Remittance Notice Actually Tells You
Remittance advice normally helps a business match money received to the invoices it covers. It can include invoice numbers, a payment date, deductions, or transfer references.
Those details are useful for bookkeeping, but an email displaying them does not prove that money reached the bank. The account record remains the financial check.
The campaign’s reported sample uses invoice reference INV-2026-2305 and payment reference EFT-8842. Such identifiers can look organized without corresponding to anything in your ledger.
Ask whether the named customer owes your business money, whether the invoice exists, and whether the amount and timing fit an actual outstanding balance.
Even a convincing match is not permission to install software from the message. Attackers sometimes obtain real invoice details or hijack existing conversations.
Finance staff should be able to verify incoming funds without changing the computer’s security posture. A document that suddenly requires an installer deserves a separate check.
How the EFT Remittance Document Malware Lure Works
Step 1: A completed payment creates a practical reason to click
The opening claim is welcome rather than frightening: an outstanding payment has supposedly been settled. The reader is encouraged to retrieve the details and finish the accounting task.
This can catch someone who has been chasing an overdue invoice. A message that appears to resolve a problem may receive less scrutiny than one demanding money.
The finance-themed wording gives the button a purpose. You are not being asked to install anything yet, only to inspect a document related to normal work.
A misspelled subject is a warning sign, but it is not the whole test. A corrected spelling would leave the later executable-file demand just as dangerous.
Likewise, the sending address needs context. A familiar display name or provider domain does not show that the claimed payment business authorized the message.
Check known customer records rather than using the email’s own reply address as your only source of reassurance.
Step 2: The document link introduces a false viewing problem
After the recipient selects the document button, the journey changes. A page presents an Adobe Acrobat Reader update as necessary to continue.
The explanation supplies an answer to an obstacle the page itself created. You wanted payment paperwork, and now the supposed solution is a software download.
Real PDF readers do receive updates. That familiar fact makes the story plausible, particularly if you have previously installed Reader to open business documents.
But a webpage does not become your software administrator because it mentions Adobe. You can close it and check the installed application independently.
Adobe’s Reader installation instructions direct users to its own download route. A surprise remittance page is not a substitute for that trusted source.
On a managed computer, the appropriate route may be your employer’s software portal or IT team. Do not bypass that process to speed up reconciliation.
Step 3: An installer label hides a runnable script
The advertised filename ends in .bat. On Windows, that extension identifies a batch script whose lines can be processed as commands when executed.
Words such as installer, Adobe, latest, and version describe what the sender wants you to believe. They do not establish a publisher or validate the file’s contents.
A document icon can be misleading too. Pay attention to the actual file type rather than assuming a familiar-looking icon means you received a PDF.
Windows may hide known filename extensions in some configurations. Viewing full extensions helps expose a script disguised with an impressive name or a misleading document reference.
If the file type remains unclear, leave it closed and ask your administrator. Do not rely on the visible name being complete.
There is no need to run the file to discover whether it is legitimate. The unexpected transition from payment record to batch-script installer is sufficient reason to stop.
Do not upload a business attachment to random online services for reassurance. It could contain confidential information, and an unknown verdict is not approval to execute it.
Step 4: The instructions persuade the recipient to authorize execution
The reported delivery instructions encourage running the file, accepting a User Account Control prompt, and allowing PowerShell activity to finish.
That is the important escalation. The recipient is no longer reading information; they are allowing software instructions to act on the computer.
A Windows permission prompt asks whether you authorize an action. It does not certify that the request is necessary, safe, or genuinely connected to Adobe.
PowerShell is a legitimate Windows tool used by administrators. Attackers can abuse legitimate tools, so seeing its name neither proves safety nor identifies a particular malware strain.
Once untrusted code runs, the consequences depend on what it does and which permissions it obtains. The lack of an obvious error does not settle that question.
For this campaign, an exact payload has not been independently analyzed here. Treat execution seriously without pretending that every affected machine has suffered the same outcome.
Separate the Fake Payment From the Device Incident
The bank record answers the payment question
Open your banking or payment service through its usual route. Compare the actual transaction with the invoice, payer, date, and amount already recorded by your business.
If no corresponding funds appear, ask the real customer through an existing contact channel. Do not accept a screenshot supplied by the suspicious sender as settlement proof.
A pending, scheduled, or initiated transfer may not be completed funds. Follow your normal accounting process rather than changing it to match the email’s wording.
Do not ship goods, issue a refund, or change an invoice’s status solely because the message says the transfer succeeded.
The computer needs a different investigation
If the file ran, checking the bank is not enough. Your organization needs to determine what executed, what it contacted, and which accounts were exposed.
Useful details include the approximate execution time, original filename, download location, security alerts, and whether an administrator prompt appeared.
You do not need to reproduce the event to give IT those details. Avoid running the script again, opening its links, or experimenting with additional permissions.
The Microsoft phishing guidance flags unexpected requests to install applications or change security settings. Those requests deserve scrutiny even when the surrounding email sounds routine.
Do not let a missing symptom reassure you
Malicious software does not always produce an obvious pop-up, slow computer, or ransom demand. Some activity is deliberately quiet.
On the other hand, simply receiving the email is not proof of infection. The response should follow what happened, not the most frightening possible outcome.
That distinction helps a responder prioritize. A deleted message, an unopened download, and an executed elevated script are three different situations.
What to Do if You Have Fallen Victim to This Scam
Stop following the update instructions. Close the payment page and do not approve further prompts. If the download is still untouched, leave it unopened.
Record the filename and where it came from. At work, ask IT how to preserve or remove it without circulating a live copy to colleagues.
If the script ran, separate the device from normal work. Disconnect its network connection where practical and promptly notify your IT or security team.
Use another trusted device or established phone contact to report the incident. Do not keep using the affected computer for banking while waiting for visible symptoms.
Give the responder a clear timeline. Explain when you opened the link, whether you executed the batch file, and whether you approved administrator access.
Include any antivirus alert or unexpected command window you remember. An honest timeline is more useful than guessing which malware family might be involved.
Check the system using trusted tools. On a personal device, use Malwarebytes obtained through a known legitimate route and follow appropriate detection and quarantine guidance.
An executed unknown script may need deeper investigation or a trusted reinstall. A clean scan alone cannot certify that all consequences have been reversed.
Secure accounts from a clean environment. Tell IT which work, banking, or password-management accounts were accessible while the untrusted program ran.
Follow its advice on password changes, session revocation, and recovery checks. Do not type replacement credentials into a computer that may still be monitored.
Verify the alleged payment independently. Compare your finance records with actual incoming funds. Contact the known payer if the invoice or settlement cannot be matched.
Escalate any real unauthorized transfer to the bank or payment provider immediately. The email’s reference number does not create a refund or recall guarantee.
Report the lure and reduce repeat exposure. Preserve the original email for IT or your mail provider’s phishing-report process, then remove it from normal workflow.
AdGuard can help reduce some malicious advertising and web exposure. Keep browser and operating-system protections enabled; never disable them to make a document open.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
How Accounts Teams Can Avoid the Same Detour
Create a simple boundary between reading payment information and changing software. An accounts employee should not need to make installation decisions inside a customer’s remittance journey.
If a genuine file cannot be opened, the next action is to ask IT or request another format through a verified contact. It is not to improvise.
Make that rule practical by providing an approved document viewer and a familiar way to report suspicious messages. A safe process must work during a busy payment run.
Managers should also avoid rewarding speed at the expense of verification. Staff need permission to pause a questionable settlement notice without feeling they are delaying revenue.
For shared finance mailboxes, tell colleagues when a lure has arrived. Otherwise, someone else may pick up the same unread message and repeat the attempted download.
A short warning can identify the actual trap: a payment email proposing a batch-script Adobe update. That is more useful than telling everyone that all remittance emails are malicious.
Frequently Asked Questions
Is the EFT Remittance Document email proof that I was paid?
No. Confirm funds through your existing bank or payment service and match them to your records. Invoice numbers inside an email are not settlement evidence.
Is Adobe Installer Latest Version 2.01.bat a PDF?
No. The .bat extension denotes a Windows batch script. A familiar product name does not turn executable commands into a payment document.
Which malware does this email install?
The payload is unspecified in the available case details. It would be misleading to identify a particular ransomware, banking trojan, or password stealer without analyzing the actual file.
Am I infected if I only downloaded the file?
Downloading and executing are different events. Do not open it. Tell IT what occurred, especially if you are unsure whether the browser or another application ran it.
Does approving a Windows prompt make the installer trustworthy?
No. The prompt requests permission for an action. It is not an endorsement of the website, the publisher claim, or the reason you were told to install.
Should I remove Adobe Acrobat Reader?
The legitimate Reader application is not the attack described here. Stop using the suspicious installer and update genuine software through Adobe or your organization’s approved process.
The Bottom Line
Do not run the batch file offered by this EFT Remittance Document email. Payment paperwork is being used to steer you into an untrusted software installation.
If you executed it, isolate the device and seek appropriate security help. Verify the money separately, and secure exposed accounts from a trusted environment.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.