

You open an ordinary page, read a few lines, and move on. The advertisement beside the story barely registers, let alone gets a click.
That unremarkable moment is at the center of AdFection, a spyware-delivery technique that changes what it means to avoid suspicious advertising.
Overview
AdFection can turn an ad impression into an attack opportunity
AdFection is the name used for spyware delivery through targeted advertising without requiring the person to click the ad. The advertisement is the entry route, not a purchase.
Citizen Lab linked targeted attacks at Al Jazeera to this technique with high confidence. At least 45 devices were targeted, which is not a claim that all 45 were infected.
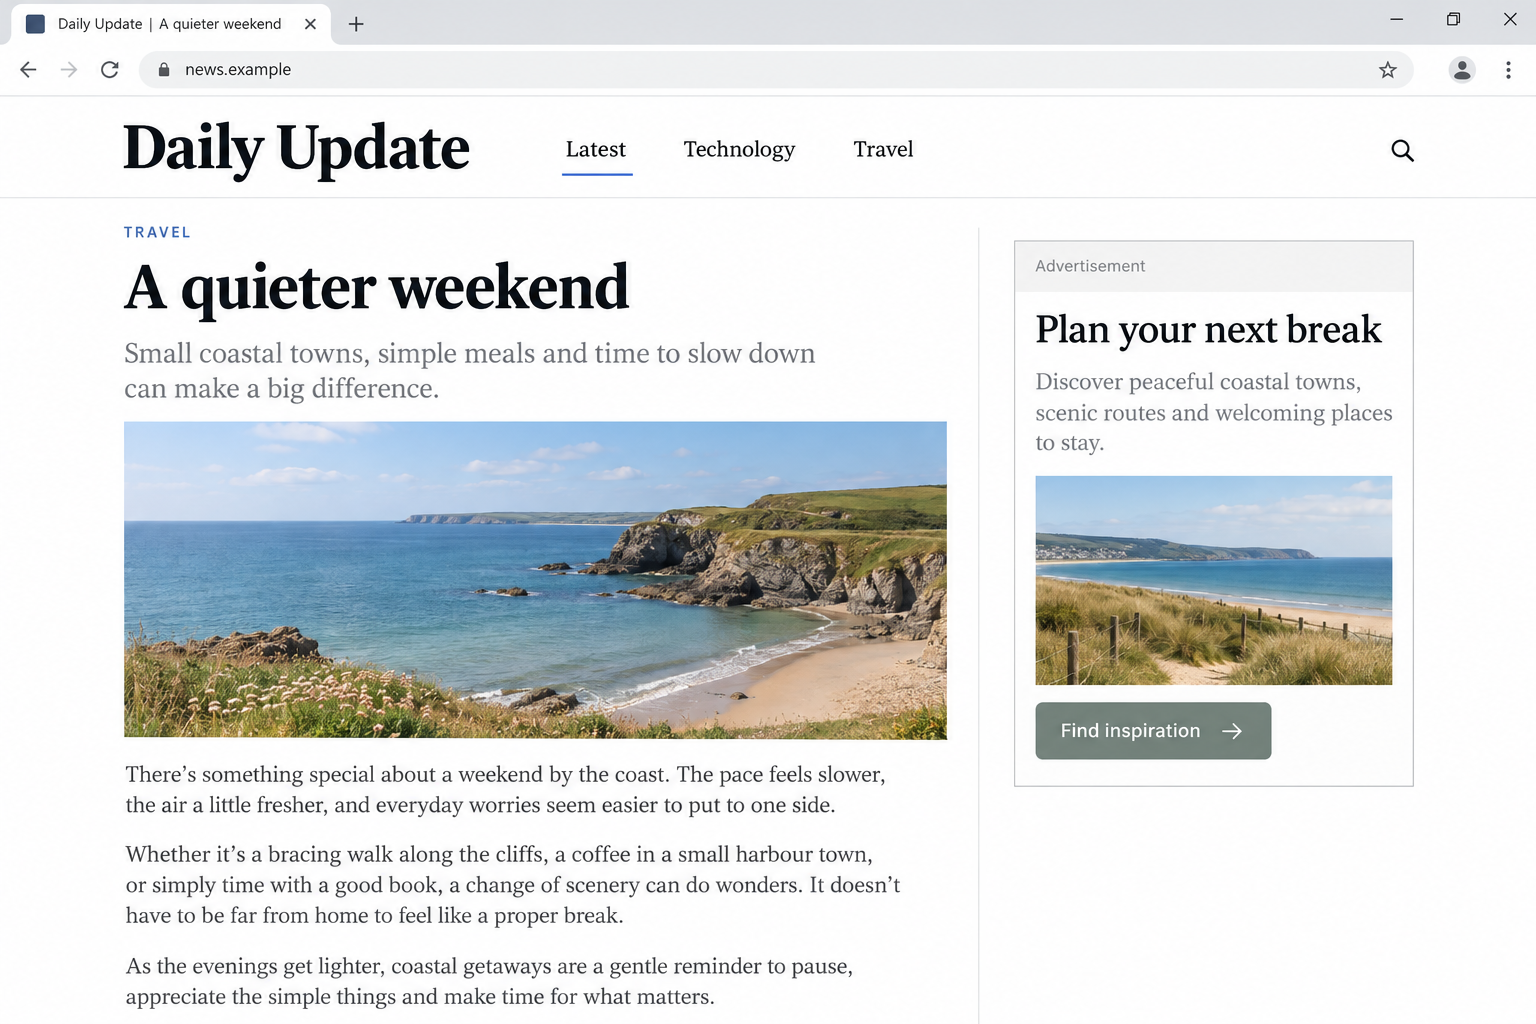
The fictional news page above illustrates an ordinary ad placement. It does not reproduce a malicious advertisement or show a particular publisher participating in the campaign.
Targeting, profiling and infection are different stages
A device contacting advertising infrastructure is not automatically a device running spyware. Reports describing millions of contacts must not be turned into millions of confirmed infections.
The distinction matters to anyone worried after seeing the headline. Exposure can justify protective measures, but an individual diagnosis needs more than remembering an advertisement.
- Keep supported operating systems, apps, and browsers current.
- Reduce unnecessary advertising and tracking exposure.
- Treat credible vendor threat notifications seriously.
- Seek specialist help when your work or circumstances make targeted surveillance plausible.
The practical response is protection, not panic
You cannot identify a zero-click exploit by deciding whether the visible ad looks trustworthy. Use technical protections and a response suited to your actual level of risk.
Do not buy an emergency spyware-cleaning service from a pop-up. If you have a credible alert, preserve it and contact a trusted security team.
Why an Advertisement Is More Than a Picture
What you see in a banner may be a static image. What the browser loads to display it can involve scripts and connections to several other systems.
Those systems help choose the ad, measure its appearance, and report activity. The visible advertiser is only one part of a longer delivery chain.
A familiar publisher may therefore display material supplied through outside advertising infrastructure. Trust in the surrounding article is not the same as control over every ad component.
That does not mean the publisher deliberately distributes spyware. Responsibility for a compromised advertising path needs investigation rather than guilt by placement.
For readers, the useful distinction is between the image and the behavior behind it. An attractive landscape cannot tell you what network requests accompanied its display.
A banner saying nothing alarming may be less noticeable than an obvious virus warning. A targeted delivery route does not need the victim to recognize an offer at all.
This is why don’t-click advice remains useful but incomplete. It addresses actions after seeing an ad, not every process involved in loading one.
What the Researchers Actually Established
Citizen Lab’s investigation identifies Discover-Tech as a bridge between advertising infrastructure and spyware delivery, including activity linked to Candiru. The report distinguishes broad profiling from targeted attacks.
Confiant’s parallel technical work examined a sophisticated advertising script framework. Its analysis describes device fingerprinting, selection checks, and a mechanism for receiving further instructions.
Those findings help explain how two visitors can encounter the same-looking ad yet receive different underlying behavior. A scanner may not be treated like an intended target.
However, the presence of a script feature does not mean it can access everything on a device. Browser context and permission boundaries still matter.
Confiant specifically notes restrictions affecting capabilities inside an ad frame. It would be wrong to turn a list of possible functions into proof of unrestricted access everywhere.
Nor does the research establish that every advertisement, website visit, or phone is affected. The documented technique is serious without exaggerating its reach.
Readers should keep the finding attached to the specific reported operation. The fact that an unrelated app uses advertisements does not make it a spyware product.
How an AdFection Attack Can Unfold
Step 1: Advertising systems place an ad on a device
The person opens a page or application that carries advertising. The opportunity begins when an ad is delivered, not when the person deliberately visits a suspicious destination.
This makes the route different from a fake download button. Teaching people to recognize misleading buttons cannot by itself address an attack that needs no button press.
Step 2: The delivery chain evaluates the visitor
The underlying framework can collect device and browser characteristics. Those details may help distinguish an intended target from other visitors or automated inspection.
A targeted decision also explains why someone else opening the same page later may see nothing unusual. Their experience does not reconstruct what the first device received.
That is a technical selection process, not proof that ordinary personalization always contains an exploit. Keep legitimate advertising behavior separate from its documented abuse.
Step 3: A selected device may receive an exploitation attempt
In a zero-click delivery path, the next malicious stage does not require a person to knowingly install an application or approve a normal download.
Whether an attempt succeeds depends on the target and available attack capabilities. Exposure to the delivery infrastructure alone does not settle that outcome.
A claim that an attack is zero-click describes the missing user interaction. It is not a claim that every device is vulnerable to the same method.
Step 4: Investigators distinguish attempted delivery from continuing compromise
Specialists look at relevant device artifacts and network activity to assess what happened. A screenshot of the advertisement cannot answer that question on its own.
If continuing access is found, the response must protect the person and their information, not merely close the webpage where the chain began.
That can involve a safer communication device, account protection, evidence preservation, and a deliberate recovery plan. The right order depends on the circumstances.
What This Means for an Ordinary Reader
Seeing an ad is not a diagnosis. If this article is your only reason for concern, begin with routine protective maintenance rather than treating your device as confirmed compromised.
Install available security updates through built-in settings. A pending update is worth addressing even when the device seems to work normally.
Use software that still receives security support. Check the vendor’s support information rather than assuming an old device remains protected because it can browse the web.
Review unnecessary apps and browser extensions. Removing something you no longer use reduces the amount of software and permissions you need to keep track of.
Advertising and tracking controls can reduce exposure, but no single switch is a guarantee. Keep them as one layer alongside updates and sensible account protection.
Do not spend hours trying to recognize the exact banner described in a technical report. Advertising changes, and visual similarity would not establish that you received an exploit.
If you remember a concerning event, note the date and app before clearing history. Useful details are more valuable to a responder than a confident guess about the cause.
When the Risk Deserves Specialist Attention
A journalist protecting sources faces a different situation from someone who simply read a frightening headline. Threat response should reflect what is at stake.
Credible targeting indicators may include an independently verified vendor warning or evidence supplied by a qualified incident-response team. Treat those differently from generic pop-up claims.
People handling sensitive reporting, legal cases, activism, or organizational information should involve their existing security contacts early rather than publishing suspected indicators in an open forum.
A public request can expose sources, work patterns, or travel information. Share necessary details through a channel agreed with the responder.
Access Now’s Digital Security Helpline offers assistance to eligible civil-society users, including journalists and human-rights defenders. Locate its contact details independently.
If another person may be monitoring your communications, consider the device used to seek help. A trusted separate device can be safer than continuing the discussion on the suspect one.
Do not confront a suspected operator or deliberately revisit infrastructure to gather evidence. Professional assistance should not require you to recreate an attack against yourself.
What to Do If You Suspect Ad-Delivered Spyware
-
Separate a real alert from an advertisement. Record who issued the warning and where it appeared. A webpage claiming to have scanned your phone is not a vendor notification.
For an Apple threat notification, verify it through the Apple account route described in Apple’s official guidance. Do not use a link supplied by an unexpected caller.
-
Use a trusted contact route for urgent help. Contact your organization’s security team or an appropriate specialist from a safer device if targeting appears credible.
Describe the concern, the device, and any verified alert. Ask how to preserve evidence before factory-resetting, deleting apps, or repeatedly changing the device’s state.
-
Apply available protections with the right expectations. For ordinary risk reduction, update the operating system, browser, and relevant apps through their established settings.
Apple offers Lockdown Mode for people who may face highly sophisticated targeted attacks. Review its official explanation and practical restrictions before deciding whether it fits your situation.
A hardening feature is a preventive layer, not a certificate that an earlier attack failed or an already-compromised device has been cleaned.
-
Reduce unnecessary ad and tracker delivery. A reputable tool such as AdGuard can help block supported advertising and tracking paths, depending on platform and configuration.
Check the actual publisher, requested permissions, and coverage. A browser extension does not necessarily cover advertisements inside every other app on the device.
Do not install a lookalike blocker promoted by an alarming pop-up. More permissions do not automatically mean better protection.
-
Use malware checks where the platform supports them. Malwarebytes can help detect common threats on supported systems. Obtain it through a known genuine source.
Do not interpret a clean consumer scan as a forensic clearance for sophisticated mercenary spyware. Mobile-platform restrictions and attack-specific techniques can limit what a tool can establish.
A specialist may need a different examination. Tell the responder about scans already run and keep their results rather than assuming the work must start from memory.
-
Protect sensitive accounts and communications deliberately. From a trusted environment, review important sessions, recovery settings, and multifactor authentication with the responder’s guidance.
Agree on a recovery or replacement plan before returning to sensitive work. If compromise is confirmed, account changes and endpoint recovery must be coordinated.
Keep the people who depend on the device informed through safe channels. Avoid sharing confidential case details with unsolicited recovery businesses.
What Ad Blockers, VPNs and Encryption Do Not Prove
It is tempting to look for one product that makes the issue disappear. That is exactly the temptation an emergency-cleanup advertisement can exploit.
An ad blocker can stop some requests before they load. Its effectiveness depends on the supported environment, filters, permissions, and how the application delivers advertising.
A VPN changes how traffic reaches its destination. It does not automatically inspect and neutralize everything a browser or app receives through that connection.
Encrypted messaging protects communications in transit under its design. It cannot make a compromised endpoint a trustworthy place to read or compose sensitive information.
These tools can still be useful. The problem is treating the presence of one tool as proof that no other security work is necessary.
Ask a provider to explain its actual scope, not just whether it uses a security-related label. Do not accept a blanket guarantee against every spyware technique.
Do Not Turn Large Exposure Numbers Into a Personal Diagnosis
Threat reports often contain several populations: devices that saw an ad, devices profiled, selected targets, attempted infections, and confirmed compromises. They should not be added together casually.
A broad infrastructure contact count describes reach. A targeted-device count describes selection. Confirmation of an implant requires more specific evidence.
For your own situation, ask what evidence connects the device to an actual harmful event. A headline with a large number cannot provide that connection.
The same restraint helps organizations respond effectively. Label records by what they show instead of marking every matching network event as a successful infection.
Careful counting helps security teams find the people who need urgent assistance. Everyone else can improve protection without treating ordinary browsing as a confirmed infection.
For a newsroom or civil-society group, agree in advance on a private reporting route. Staff should not need to decide whom to trust while a warning is frightening them.
A short plan can name the security contact, safer communication method, and information to preserve. It should also explain which details must never enter a public support thread.
Preparedness is especially useful here because the person may have done nothing visibly wrong. A calm response should protect them, not blame them for failing to spot an invisible stage.
Frequently Asked Questions
Can spyware arrive without clicking an ad?
Yes, the reported AdFection technique uses ad delivery without requiring a click. That does not mean every advertisement or device is affected.
Were millions of people confirmed infected?
No. Broad contacts with profiling or delivery infrastructure must not be described as a count of confirmed spyware infections.
Can I identify the attack from the banner’s appearance?
No. The visible creative does not reveal all underlying delivery behavior. Similar-looking banners can accompany different technical activity.
Will AdGuard guarantee protection?
No tool provides that blanket assurance. Blocking supported advertising paths can reduce exposure, but coverage varies and should be combined with other protections.
Does a clean antivirus scan settle a targeted-spyware concern?
Not necessarily. A credible targeting alert deserves specialist assessment even when an ordinary consumer scan finds nothing.
Should everyone factory-reset after reading this?
No. Apply routine protections if you have no specific indicators. If targeting is credible, seek advice before actions that could destroy evidence.
The Bottom Line
Do not rely on avoiding clicks as your only defense against malicious advertising. Keep software current, reduce unnecessary ad delivery, and reject instant-cleanup guarantees.
If a credible warning suggests targeted spyware, contact a trusted specialist from a safer device. Preserve the evidence and follow a recovery plan suited to the actual risk.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.