

The message looks like something you would expect from a real security team.
It has a case ID. It names an “APPLE STORE” location. It mentions Apple Pay pre-authorization and “temporarily blocked” activity. Then it offers a simple fork in the road that feels reassuring: if the activity is familiar, do nothing. If it is not, call Apple Support immediately.
That second option is the whole scam.
Because the moment you call the number in the text, you are no longer dealing with Apple. You are dealing with a scripted, professional-sounding fraud operation that is built to keep you anxious, keep you talking, and eventually steer you into handing over access, money, or both.
This “Unverified Apple Pay Usage” alert is designed to feel urgent, but not chaotic. It is meant to catch you when you are busy, and make the safest choice feel like making a phone call.
In reality, the safest choice is almost always the opposite.
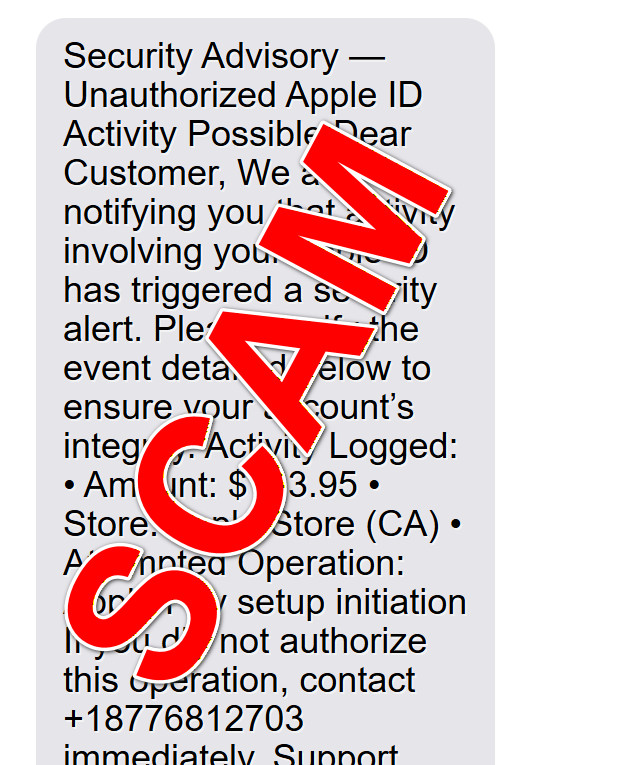
Scam Overview
“Unverified Apple Pay Usage” scam texts are a form of impersonation and tech support fraud. They pretend to be an Apple security notification, claiming suspicious Apple Pay activity, multiple sign-in attempts, and blocked setup requests from unknown devices. The message usually adds a pending charge with a specific dollar amount, often something like $287.99, tied to a recognizable location such as “APPLE STORE, Orlando, FL.”
The point is not accuracy. The point is emotional plausibility.
It is supposed to make you think, “I did not do that,” and then immediately hand you a way to fix it. That fix, calling the phone number, is how scammers move you from a harmless text into an interactive con.
What makes this scam feel believable
A lot of scam texts fail because they look lazy. This one is built differently.
It borrows several credibility signals that real security alerts often use:
- A formal subject line like “Unverified Apple Pay Usage”
- A case ID to imply a tracking system
- A pending charge described as “Apple Pay Pre-Authorization”
- Multiple “blocked” events, like sign-in attempts and setup requests
- A calm, official-sounding tone that avoids obvious spelling errors
- A familiar support flow, “If this is familiar, no action is required”
That last line is a psychological trick.
It makes the message sound fair, like it is not trying to force you. It lowers resistance. It encourages you to treat the message as a genuine notification that simply offers help.
Then it adds the pressure sentence: contact Apple Support immediately, and it provides a phone number.
That number is the baited hook.
Why Apple Pay is such a powerful theme for scammers
Apple Pay sits right at the intersection of identity and money.
When someone hears “Apple Pay setup requests from unknown devices,” it triggers a specific fear. Not just “a charge might happen,” but “someone might be trying to add my card to their phone.”
That feels like a direct threat to your finances, and it feels time-sensitive. People assume that if a wallet setup succeeds, the scammer can make instant purchases.
Scammers choose Apple Pay because it creates urgency without needing technical explanations. They can say:
- “Your Apple Pay is being activated on another device.”
- “Your wallet is being cloned.”
- “A pre-authorization charge is pending.”
Most victims are not sure how Apple Pay provisioning works, so they are more likely to defer to an “expert” on the phone.
The charge amount is carefully chosen
Amounts like $287.99 are not random.
Scammers usually avoid very small charges, because those are easy to ignore. They also avoid huge amounts, because those trigger skepticism and immediate bank contact.
A mid-range number hits the sweet spot:
- High enough to feel serious
- Low enough to feel plausible
- Specific enough to feel real
They also pair it with a store location because it gives the brain a picture. A place. A scene. “Orlando, FL” feels like a real Apple Store, and that familiarity creates false confidence.
“Pre-authorization” is used because it sounds technical and urgent
Pre-authorization language is common in payment systems. Hotels, car rentals, and some retail purchases can trigger pending authorizations.
Scammers use this term because it helps them control the narrative:
- “It is pending, so we can stop it, but only if you act quickly.”
- “It is under investigation, but you must verify now.”
- “If you do nothing, it will proceed within 24 hours.”
That 24-hour window is another psychological lever. It gives you a countdown without looking like a countdown. It makes waiting feel risky.
The “Apple Security Division” sign-off is a tell
Apple does not sign text messages as “Apple Security Division.”
Scammers love to invent department names that sound plausible, but are just vague enough to avoid verification. Real Apple communications tend to be consistent in branding and phrasing, and they rarely introduce themselves as a dramatic security division in consumer texts.
The real goal: get you into a live conversation
This scam is not primarily a link scam.
Yes, it includes a link to a real Apple support page, such as getsupport.apple.com. That can be legitimate, but scammers often include real links to make the message look trustworthy.
The phone number is the actual trap.
Once you call, they can:
- Keep you on the line and prevent you from thinking clearly
- Tailor the script to your reactions
- Extract personal information gradually
- Push you into high-risk actions, like installing remote access tools
- Pressure you into irreversible payment methods
This is why tech support scams have survived for so long. The human voice is persuasive. It is harder to ignore than a text. It can sound confident, caring, and urgent all at once.
What happens during the call
Victims often report a familiar pattern.
The person who answers may:
- Claim to be Apple Support, Apple Billing, or Apple Security
- Ask for basic “verification” details like your name and email
- Confirm the case ID from the text to make it feel official
- Describe your account as “flagged” or “under investigation”
- Warn that your Apple Pay wallet is being provisioned on an unknown device
Then the scammer moves toward control.
They may ask you to:
- Confirm codes sent to your phone or email
- Share your Apple ID login or reset it while on the phone
- Install a remote access app like AnyDesk or TeamViewer on a computer
- Enable screen sharing or accessibility permissions
- Open your bank app “to verify the pending pre-authorization”
- Perform steps that feel like protection but actually grant access
This is the danger zone, because the scammer is no longer relying on a fake message. They are guiding you through a sequence of actions that can be used to take over accounts or steal money.
Common variations of the “Unverified Apple Pay Usage” scam
Once you recognize the structure, you will notice it shows up with small changes.
Common variations include:
- Different amounts, often between $200 and $600
- Different Apple Store locations, often large cities or tourist areas
- “Multiple unauthorized sign-in attempts” added for extra fear
- “Your account will be locked in 24 hours” threats
- “Reply Y to confirm” or “Reply NO to stop” prompts
- “Your iCloud is compromised” claims
- Instructions to download an app or visit a site, followed by a call
The details change, but the funnel stays the same: panic, urgency, phone call, control.
Who gets targeted and why you might receive it
You do not need to have Apple Pay enabled to receive this scam text.
Scammers blast these messages to huge lists of numbers, and they rely on volume. Even a tiny response rate can be profitable.
You might be targeted because:
- Your phone number was part of a data leak
- You entered your number on a site that was later compromised
- You posted your number publicly or used it in business listings
- A marketer or broker sold lists that include your region and device type assumptions
- It was simply random
The scam works even if you are not an iPhone user, because many people will still call to “check.” Once you call, the scammer can adapt, and pivot to “your credit card has been used with Apple Pay,” even if you do not use Apple devices.
The biggest red flags in the message
If you are scanning quickly, look for these signs:
- The message tells you to call a phone number to resolve a security issue
- It uses urgency, “immediately,” “within 24 hours,” “responding quickly”
- It includes a “case ID” to create false legitimacy
- It claims Apple Pay setup requests from unknown devices, but you did not initiate anything
- It implies that doing nothing will allow the charge to proceed
- It signs off with an invented department name
Any one of these should be enough to slow down. Several together are a strong indicator you are looking at a scam.
What scammers want from you
The outcomes usually fall into a few buckets:
- Apple ID takeover
They try to capture your login, trick you into approving a login prompt, or get verification codes. - Financial theft
They steer you into sending money through methods that are hard to reverse, including wire transfers, instant payment apps, or gift cards. - Remote access
They get control of your computer, then pivot into banking and identity theft. - Identity harvesting
Even if you do not pay, they may collect your name, address, email, and phone details for later fraud.
The most important thing to understand is that the scam is designed to escalate. The first request might seem harmless. The later requests are where the damage happens.
How the Scam Works
Below is the most common step-by-step flow. Not every victim sees every step, but the pattern stays consistent. The scam is built like a funnel, and each stage is designed to push you deeper.
1) The text arrives with a believable security narrative
The scammer sends a message that reads like an internal incident report.
It includes:
- A case ID
- A pending charge
- A store location
- A list of “flagged” actions like sign-in attempts and Apple Pay setup requests
- A reassurance line that makes it feel legitimate
- A phone number presented as Apple Support
The goal is to make you feel that the situation is already underway, and that you are seeing it just in time.
2) You call the number, and they create instant authority
When you call, they usually answer quickly.
They may use a scripted greeting like:
- “Apple Support, how may I assist you?”
- “Apple Security Division, case verification, may I have your case ID?”
They will often ask for the case ID shown in the message. That is not for security. That is a prop.
When they repeat it back to you, it triggers a feeling of legitimacy. You think, “They have my case open.” In reality, they are reading what you told them.
3) They widen the threat, from one charge to full account compromise
Next, they shift the story.
It stops being about a single $287.99 charge and becomes:
- “Multiple devices attempted to access your Apple ID”
- “Your Apple Pay wallet is being set up on an unknown device”
- “We see a high-risk login attempt”
- “Your iCloud could be compromised”
This escalation is strategic.
A single charge can be disputed with a bank. A compromised Apple ID feels bigger and scarier. It also makes people more willing to follow instructions that they would normally reject.
4) They push you into “verification” steps that collect data
Now the scammer starts asking questions.
They frame it as standard security verification, but it is really information gathering.
You might be asked for:
- Your full name and billing ZIP code
- Your Apple ID email address
- Your phone number, if you called from a different line
- Whether you have cards saved to your Apple account
- Whether you use Apple Pay, and which bank you use
- Your device model and iOS version
Each answer helps them tailor the next part of the script.
If you seem cautious, they will become more reassuring. If you seem panicked, they will push urgency. If you say you do not use Apple Pay, they may pivot to “your card is being used in Apple Pay.”
5) They introduce a “secure process” that keeps you on the phone
A major goal is to keep you engaged.
They often say things like:
- “Please do not hang up, this is time sensitive.”
- “If we disconnect, the case may be delayed.”
- “I will guide you through a secure procedure.”
This is about preventing you from stopping to think, or contacting your bank, or checking Apple’s official channels.
The scam thrives on uninterrupted attention.
6) The control move: remote access or code capture
This is where many victims get trapped.
The scammer may push one of these routes:
Remote access on a computer
- They tell you to install AnyDesk or similar software.
- They claim it is needed to “scan” your system or “remove unauthorized devices.”
- Once installed, they can view your screen, sometimes control it, and guide you into banking or password resets.
Verification codes and login prompts
- They ask you to read out codes sent to your phone.
- They claim the code is to “cancel the charge” or “block the setup.”
- In reality, those codes may be for logging into your Apple ID or email account.
Apple ID reset while they watch
- They instruct you to reset your Apple ID password with them on the line.
- If they can intercept codes or watch the reset, they can take over the account.
Even if they never fully control your device, they can manipulate you into doing the dangerous parts yourself.
7) The money extraction, framed as protection or reversal
Once they have you in a fear state, they introduce the “solution.”
This can look different depending on the script, but common outcomes include:
- “We will reverse the $287.99 charge, but we need to verify the billing source.”
- “We need to secure your wallet by placing a refundable authorization.”
- “We must create a security hold on your funds.”
- “We require a verification payment that will be refunded.”
Then the pressure ramps up.
If they go the gift card route, it often sounds like:
- “Purchase Apple Gift Cards to validate ownership.”
- “This is a secure token, not a payment.”
- “Read the codes so we can apply them to the case.”
If they go the bank route, it might be:
- “Move money to a safe account to prevent further fraud.”
- “Your bank account may be compromised.”
If they go the fake refund route:
- They claim they refunded too much.
- They pressure you to send back the difference quickly.
- They create fear of legal trouble or account lock.
No matter the path, the end goal is the same: get money out of your control and into theirs.
8) They attempt to cover tracks and set up future access
If the scammer succeeds, they often try to reduce the chance you reverse it.
They might tell you to:
- Delete the text message and call history
- Avoid contacting your bank for 24 hours
- Keep remote access software installed for “monitoring”
- Ignore legitimate fraud alerts by claiming they are “automated”
They may also target you again later.
Victims sometimes receive follow-up calls from “senior Apple security” or “the fraud department,” claiming they can help recover losses. Those are frequently additional scammers.
Scam Message Text and Common Variants
Below is the exact scam text you shared, followed by common real-world variants scammers use. The wording changes, but the goal stays the same: push you to call a fake “Apple Support” number and panic you into acting fast.
The exact message text (example)
“Unverified Apple Pay Usage
Your Apple ID (Case ID: 649182) has triggered a security warning. A pending $287.99 charge at “APPLE STORE – Orlando, FL” was detected via Apple Pay Pre-Authorization. Additionally, multiple unauthorized sign-in attempts and Apple Pay setup requests from unknown devices have been flagged. These actions are temporarily blocked, and the charge is under investigation.
If this activity is familiar, no action is required, and the transaction will proceed within 24 hours. If not, contact Apple Support immediately at +1-888-574-3705 for assistance.
Need Assistance?
Apple Support: +1-888-574-3705 Billing Help: https://getsupport.apple.com/
Responding quickly can help prevent further issues.
Stay secure, Apple Security Division”
Possible variants you may see
Variant 1: “Security Warning” style
“Apple Security Warning
Unverified Apple Pay activity detected on your Apple ID. A pending $287.99 transaction at APPLE STORE (Orlando, FL) is under review. If you do not recognize this charge, call Apple Support now at +1-888-574-3705 to stop the transaction.”
Variant 2: “Apple Pay Setup Attempt” style
“Apple Pay Setup Attempt Blocked
We detected Apple Pay setup requests from an unknown device linked to your Apple ID. A pending $287.99 authorization has been placed at APPLE STORE Orlando. If this was not you, contact Apple Support immediately: +1-888-574-3705.”
Variant 3: “Multiple Login Attempts” style
“Apple ID Alert
Multiple unauthorized sign-in attempts were detected on your Apple ID. Apple Pay access has been temporarily suspended. Pending charge: $287.99 at APPLE STORE, Orlando FL. Call Apple Support at +1-888-574-3705 if you did not authorize.”
Variant 4: “Case ID” and “Investigation” style
“Case Update: Apple ID Security
Case ID: 649182
Your Apple ID has triggered a high-risk security warning. Apple Pay pre-authorization of $287.99 is under investigation. If this was not you, call Apple Support now at +1-888-574-3705.”
Variant 5: “24 hours” pressure style
“Immediate Action Required
A pending $287.99 Apple Pay charge has been detected at APPLE STORE Orlando, FL. If you do not respond within 24 hours, this transaction will be completed. Contact Apple Support: +1-888-574-3705.”
Variant 6: “Account locked” threat style
“Apple ID Compromised
Unauthorized Apple Pay activity detected. Your account will be restricted unless verified. Pending transaction: $287.99. Call Apple Support immediately at +1-888-574-3705.”
Variant 7: “Suspicious device” style
“Unknown Device Detected
An unknown device attempted to add Apple Pay to your Apple ID. Pending $287.99 at APPLE STORE Orlando. If you did not request this, call Apple Support: +1-888-574-3705.”
Variant 8: “Billing department” style
“Apple Billing Notice
A pending Apple Pay authorization for $287.99 was placed at APPLE STORE Orlando, FL. If you do not recognize this, contact Apple Billing Support: +1-888-574-3705.”
Variant 9: “Verification code” bait style
“Apple Verification Required
We detected unverified Apple Pay usage on your Apple ID. To prevent a pending $287.99 charge, contact Apple Support at +1-888-574-3705 to verify your identity.”
Variant 10: “Your card has been added” style
“Urgent: Apple Pay Wallet Update
Your card may have been added to Apple Pay on a new device. Pending authorization: $287.99 at APPLE STORE Orlando, FL. If you did not authorize, call Apple Support immediately at +1-888-574-3705.”
Quick note about what stays the same across variants
Even when the wording changes, most versions include:
- A scary Apple Pay or Apple ID claim
- A pending charge amount, often between $200 and $600
- A time-pressure line like “within 24 hours”
- A phone number they want you to call right away
- Sometimes a real Apple link mixed in for credibility
What To Do If You Fell Victim to This Scam
If you called the number, shared information, installed software, or sent money, you can still take control back. The key is to move quickly and methodically, without panic.
Follow these steps in order.
- Stop contact immediately
Hang up. Do not call back. Do not respond to texts. If they keep calling, block the number. Any continued conversation gives them more opportunities to manipulate you. - If you installed AnyDesk or remote access software, remove it right now
Uninstall AnyDesk, TeamViewer, or any remote access tool you installed during the call.
On a computer, also check:
- Installed programs you do not recognize
- Browser extensions you did not add
- Download history for anything added during the call
If you are not sure what was installed, treat the device as potentially compromised until you scan it.
- Run a trusted security scan, and clean up unwanted software
Use reputable tools to scan and remove threats:
- Malwarebytes for malware, unwanted programs, and potentially risky software
- AdGuard to reduce exposure to malicious ads, scam pages, and redirect traps that often lead to fake alerts
If Malwarebytes finds anything, follow its remediation steps. After cleanup, restart the device and run another scan.
- Secure your Apple ID from a trusted device
Do not use a device the scammer accessed if you can avoid it.
- Change your Apple ID password to a strong, unique password.
- Review your trusted devices and remove any you do not recognize.
- Verify that two-factor authentication is enabled.
- Review your Apple ID account information, including phone numbers and recovery options.
- Check for any new payment methods, subscriptions, or changes you did not authorize.
- Secure your email account immediately
Email is where password resets and verification codes land. If scammers get into your email, they can take over other accounts even if you change passwords later.
- Change your email password.
- Enable two-factor authentication on email.
- Check for forwarding rules, filters, and recovery email changes.
- Review recent login activity and sign out of other sessions.
- Contact your bank or card issuer and report potential fraud
If you shared card details, opened your bank app while on the call, sent a transfer, or purchased gift cards, contact your bank’s fraud department.
Ask about:
- Freezing or replacing cards
- Blocking suspicious transactions
- Reviewing recent activity for unauthorized charges
- Adding extra verification requirements
- Stopping transfers if they are still pending
If you see a charge you did not authorize, dispute it through your bank, not through a phone number in a text.
- If you bought gift cards, report it immediately with receipts
If you provided gift card codes, contact the gift card issuer as quickly as possible. Some issuers can freeze remaining balance if the code has not been fully redeemed.
Keep:
- Photos of the card front and back
- The receipt
- The store location and time of purchase
- Any messages or call logs related to the scam
- Change passwords for any accounts you accessed during the call
If you logged into banking, email, Apple ID, or shopping accounts while the scammer was on the line or watching your screen, change those passwords too.
Prioritize:
- Apple ID
- Bank and payment apps
- Main shopping accounts with saved cards
- Password manager accounts
Use unique passwords, and enable two-factor authentication wherever possible.
- Watch for follow-up scams and “recovery” fraud
Scammers often circle back.
Be cautious of:
- Calls claiming to be Apple “escalation”
- People offering to recover your money for a fee
- Messages claiming your “case” is still open
If you need Apple support, initiate it yourself through official Apple channels you locate independently.
- Document everything and report it
Write down:
- The phone number you called
- The date and time
- What information you shared
- What software you installed
- Any payments or gift cards involved
Save screenshots of the scam message. Documentation helps your bank, helps with disputes, and helps you stay organized under stress.
How to Remove Unwanted Apps and Malware
If a pop-up scam tricked you into downloading an unwanted program — or you suspect your device is infected — follow the free, step-by-step removal guide below to clean it completely.
Please follow the steps in order. If you get stuck or have doubts at any point, stop and ask for help in our free support forum — our team will guide you personally.
 Remove Unwanted Apps and Malware from Windows
-
 Remove Unwanted Apps and Malware from Mac
 Remove Unwanted Apps and Malware from Android
- Remove Unwanted Apps and Malware from iPhone and iPad
Remove Unwanted Apps and Malware from Windows
- STEP 1: Uninstall malicious programs from Windows
- STEP 2: Reset browsers back to default settings
- STEP 3: Use Malwarebytes Anti-Malware to remove malware and unwanted programs
- STEP 4: Use HitmanPro to scan your computer for badware
- STEP 5: Use AdwCleaner to remove adware and malicious browser policies
STEP 1: Uninstall malicious programs from Windows
In this first step, we will manually check if any unknown or malicious programs are installed on the computer. Sometimes adware and browser hijackers can have a usable Uninstall entry that can be used to remove them.
-
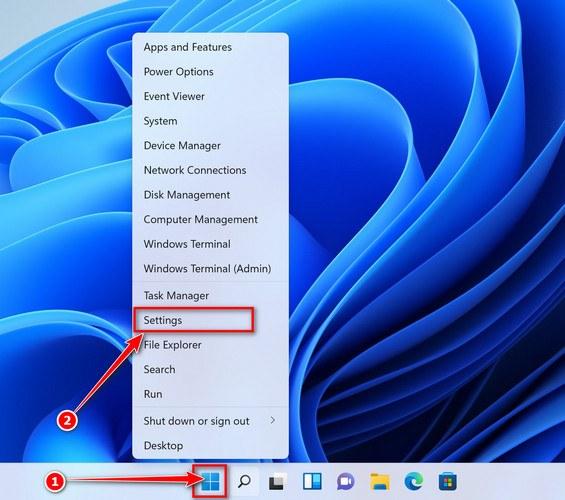
Open the Settings app
Press Windows + I on your keyboard to open Settings. Alternatively, right-click the Start button and select “Settings” from the menu.
-
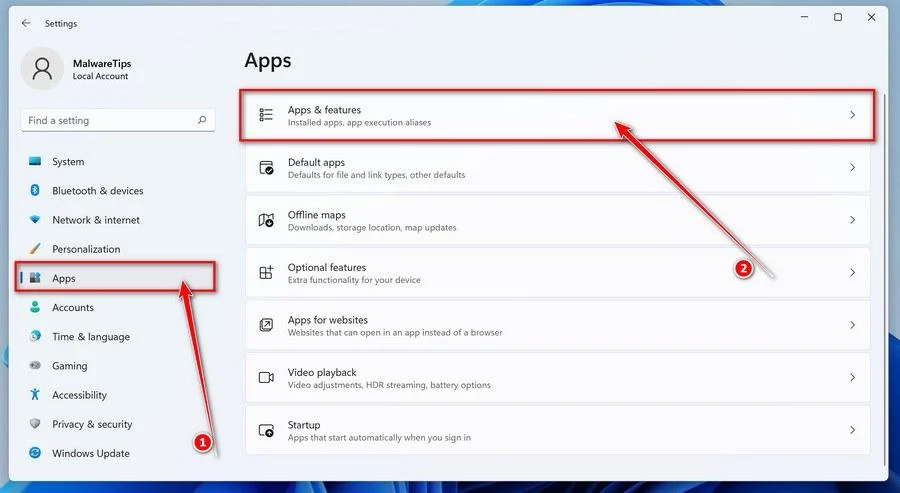
Go to “Apps & Features”
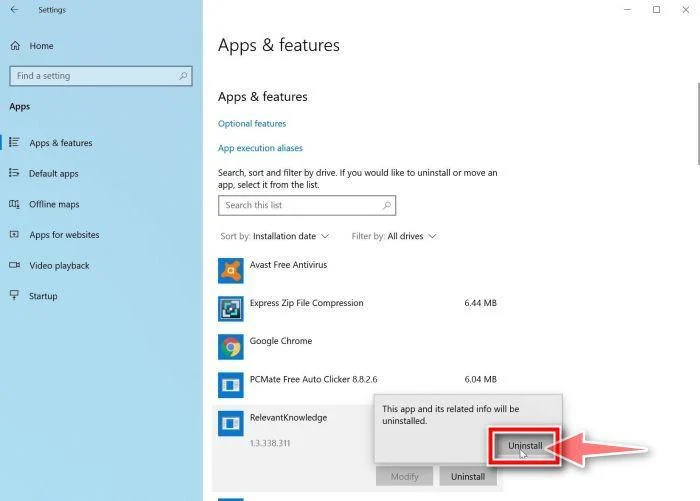
In the Settings window, click “Apps” in the sidebar, then select “Apps & Features“.
-
Find and uninstall the malicious program
Scroll through the list of installed apps and look for anything suspicious — a program you don’t remember installing, or one with a strange or generic name.
Quick tip: click “Sort by” and choose “Install date“. Malware is usually one of the most recently installed programs, so it will appear near the top.
When you find the malicious program, click the three dots next to it and select “Uninstall“.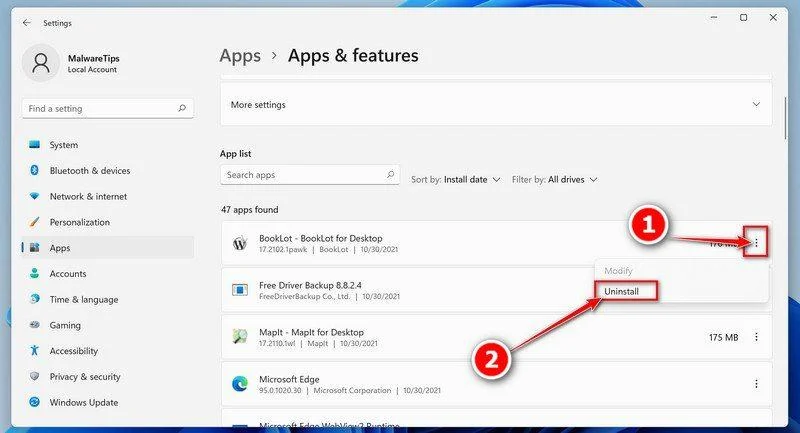 Didn’t find any suspicious programs? That’s fine — not all infections install visible apps. Just continue with the next step in this guide.
-
Complete the uninstall
Confirm by clicking Uninstall in the message box, then follow the remaining prompts.
Read each prompt carefully — some malicious programs use confusing wording or pre-ticked boxes hoping you’ll click through without looking.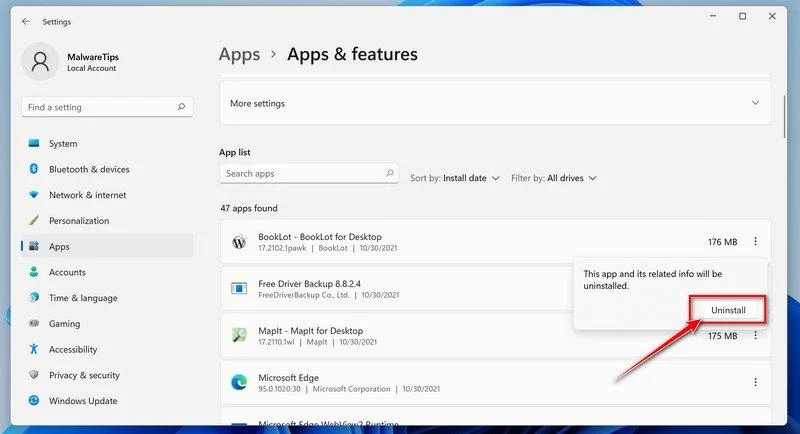
-
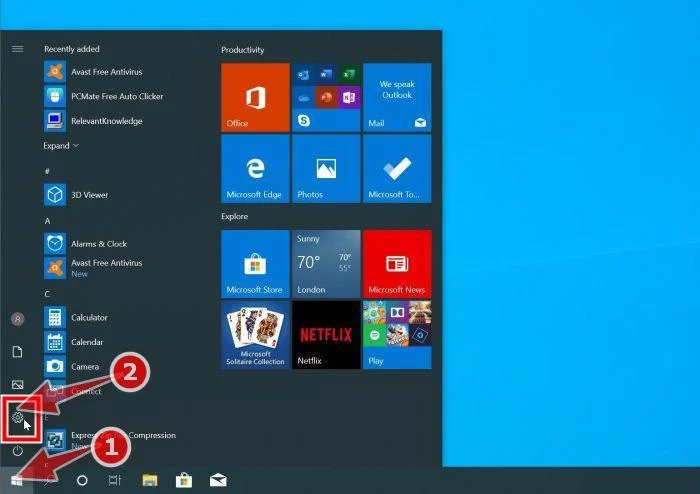
Open the Settings app
Press Windows + I on your keyboard to open Settings. Alternatively, click the Start button on the taskbar and select “Settings” (the gear icon).
-
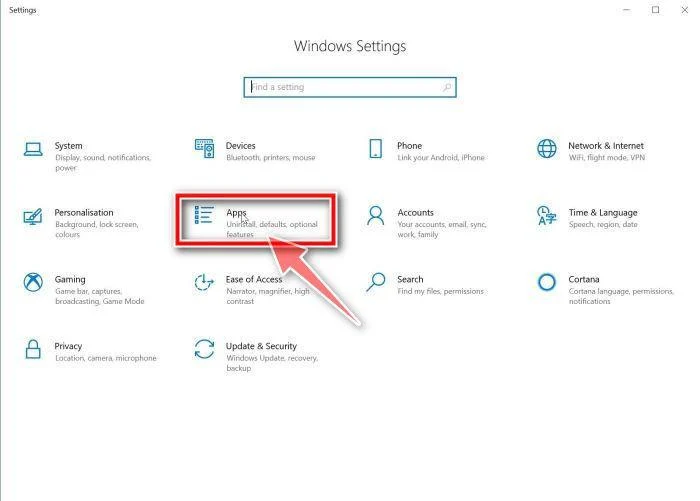
Click on “Apps”
In the “Windows Settings” window, click “Apps“. The “Apps & Features” section should open by default — if it doesn’t, select it from the list on the left.
-
Find and uninstall the malicious program
Scroll through the list of installed apps and look for anything suspicious — a program you don’t remember installing, or one with a strange or generic name.
Quick tip: click “Sort by” and choose “Install date“. Malware is usually one of the most recently installed programs, so it will appear near the top.
When you find the malicious program, click on it and select “Uninstall“.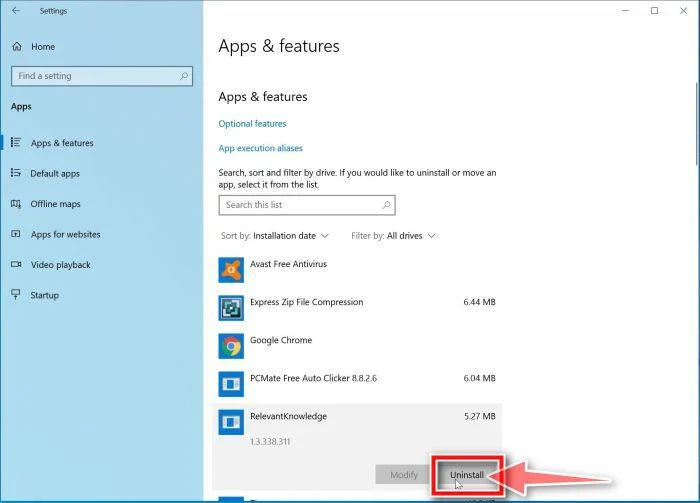 Didn’t find any suspicious programs? That’s fine — not all infections install visible apps. Just continue with the next step in this guide.
-
Complete the uninstall
Confirm by clicking Uninstall in the message box, then follow the remaining prompts.
Read each prompt carefully — some malicious programs use confusing wording or pre-ticked boxes hoping you’ll click through without looking.
-
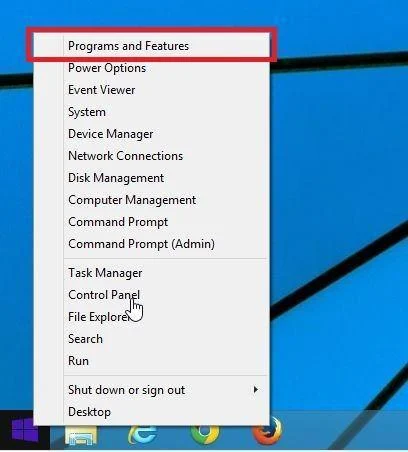
Open “Programs and Features”
Right-click the Start button in the taskbar, then select “Programs and Features“. This takes you straight to the list of installed programs.
-
Find and uninstall the malicious program
Scroll through the list of installed programs and look for anything suspicious — a program you don’t remember installing, or one with a strange or generic name. Click to highlight it, then click the “Uninstall” button.
Didn’t find any suspicious programs? That’s fine — not all infections install visible apps. Just continue with the next step in this guide.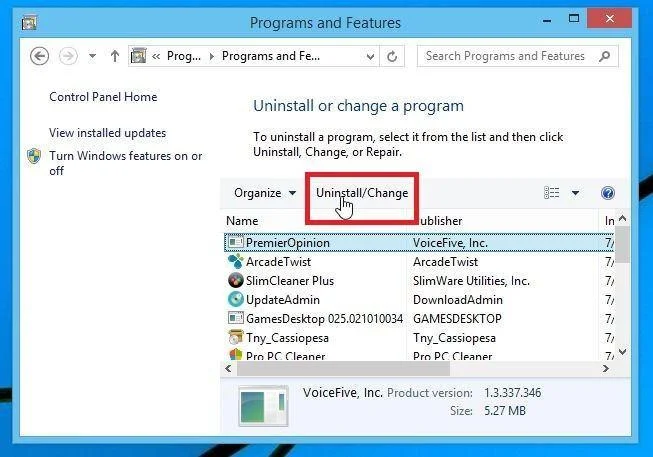
-
Complete the uninstall
Confirm by clicking Yes in the message box, then follow the remaining prompts. Read each prompt carefully — some malicious programs use confusing wording or pre-ticked boxes hoping you’ll click through without looking.
-
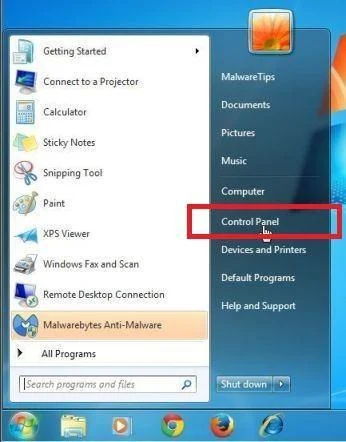
Open the Control Panel
Click the “Start” button, then click “Control Panel“.
-
Click on “Uninstall a Program”
In the Control Panel, click “Uninstall a Program” under the Programs category.
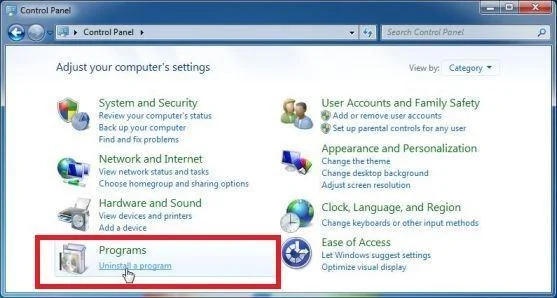
-
Find and uninstall the malicious program
Scroll through the list of installed programs and look for anything suspicious — a program you don’t remember installing, or one with a strange or generic name. Click to highlight it, then click the “Uninstall” button.
Didn’t find any suspicious programs? That’s fine — not all infections install visible apps. Just continue with the next step in this guide.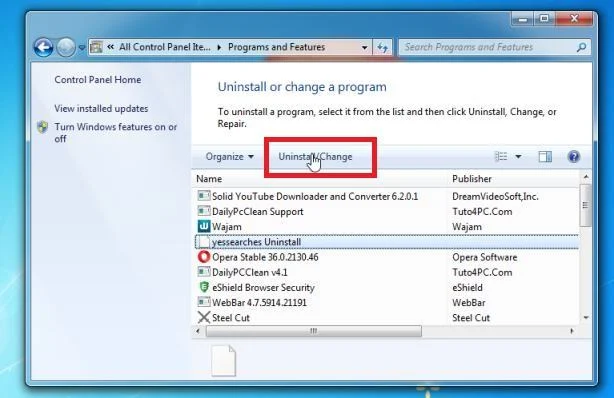
-
Complete the uninstall
Confirm by clicking Yes in the message box, then follow the remaining prompts. Read each prompt carefully — some malicious programs use confusing wording or pre-ticked boxes hoping you’ll click through without looking.
With the malicious programs removed, you’re ready for the next step in this guide.
STEP 2: Reset browsers back to default settings
In this step, we will remove spam notifications, malicious extensions, and change to default any settings that might have been changed by malware.
Please note that this method will remove all extensions, toolbars, and other customizations but will leave your bookmarks and favorites intact. For each browser that you have installed on your computer, please click on the browsers tab below and follow the displayed steps to reset that browser.
Reset Chrome for Windows to default settings
We will now reset your Chrome browser settings to their original defaults. This will reset your startup page, new tab page, search engine, and pinned tabs. It will also disable all extensions and clear temporary data like cookies. Your favorites, history, and saved passwords will not be cleared.
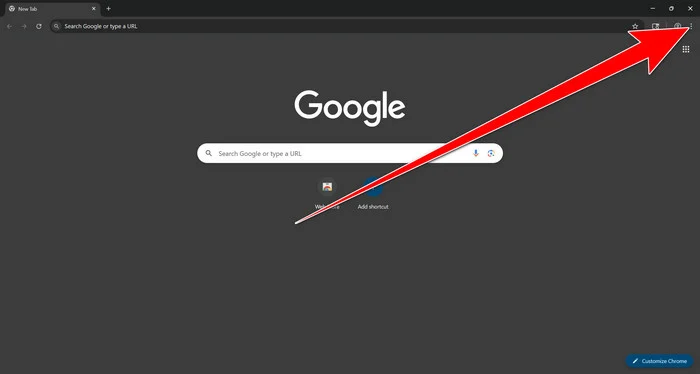
Open the Chrome menu
Open Google Chrome and click the three-dot (⋮) icon in the top-right corner.
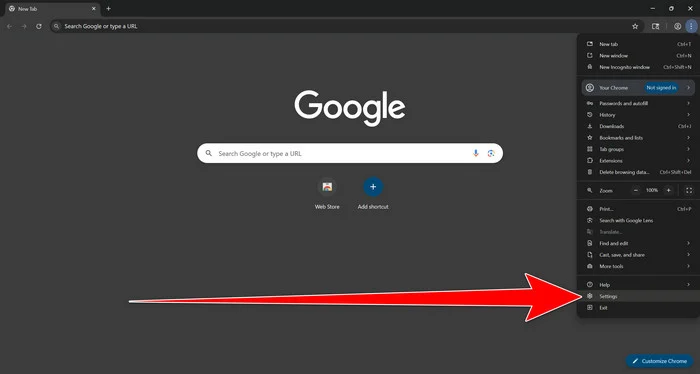
Open Chrome Settings
Select Settings from the Chrome menu.
Select “Reset settings”
Look at the menu on the left side of the Settings page. Scroll down and click Reset settings.
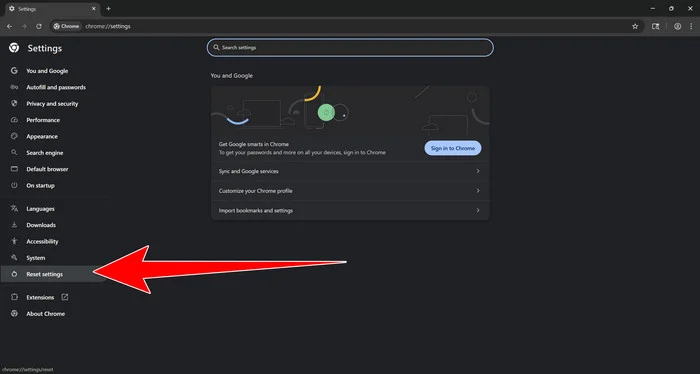
Restore Chrome’s original settings
Click Restore settings to their original defaults.
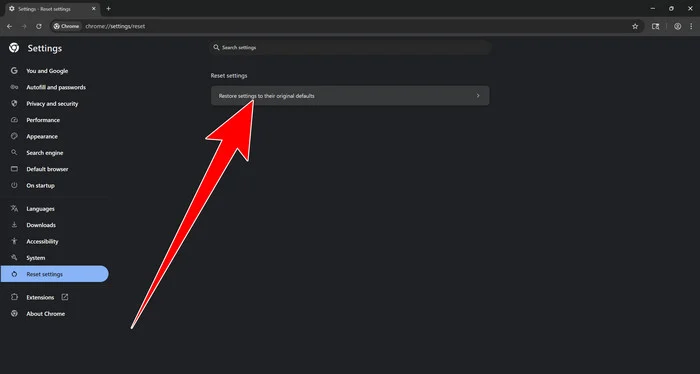
Confirm the Chrome reset
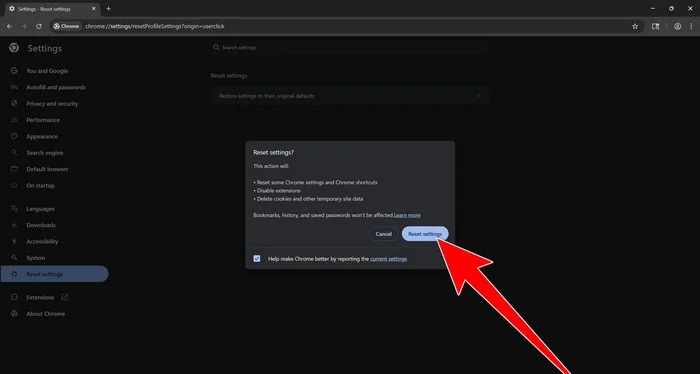
A confirmation window will appear. Click Reset settings.
This will:
- Restore the default search engine, homepage, and new tab page
- Reset startup pages and pinned tabs
- Disable installed extensions
- Clear temporary cookies and website data
Don’t worry: Chrome will not delete your bookmarks, browsing history, or saved passwords.
Restart Chrome and perform a test search. If your searches now open normally in Google, you can stop here.
If searches are still redirected through shady domains complete the additional step below.
Remove persistent search hijacker data
Only complete this step if the redirect continues after resetting Chrome.
Some browser hijackers hide inside Chrome’s local search-engine database. A standard Chrome reset may not remove this database, which is why searches can continue to pass through shady sites.
The following procedure creates a backup of the affected database and allows Chrome to build a new, clean version. This is safer and less disruptive than deleting the entire Chrome profile.
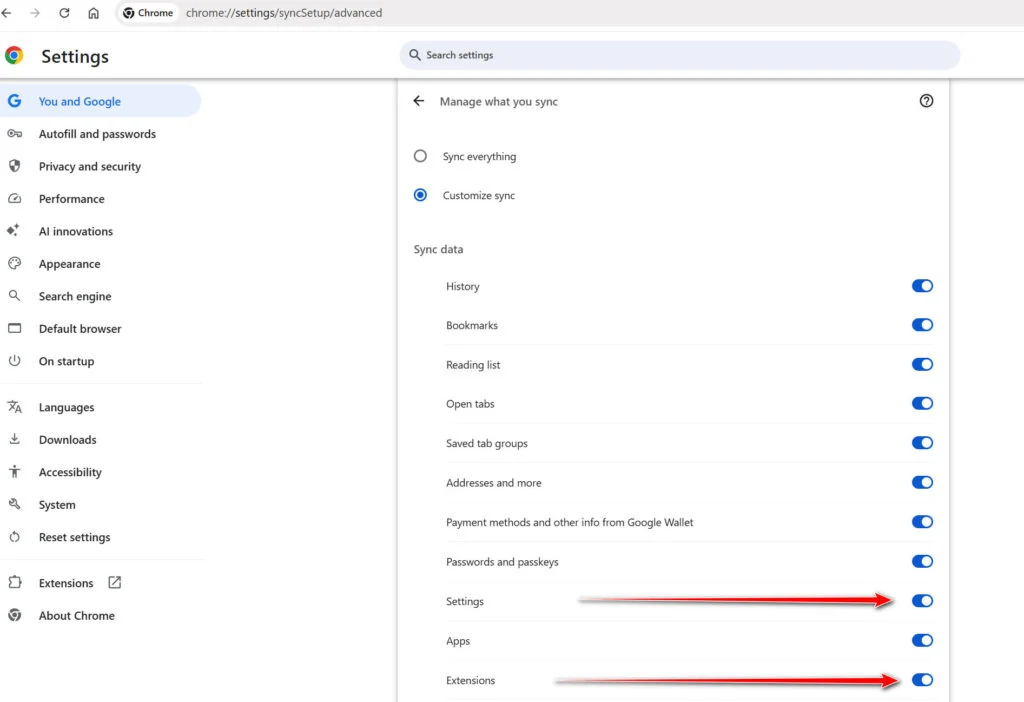
First, prevent Chrome Sync from restoring the hijacked settings:
- Open a new Chrome tab.
- Copy the following address, paste it into Chrome’s address bar, and press Enter:
chrome://settings/syncSetup/advanced - Under Manage what you sync, select Customize sync.
- Turn off Settings and Extensions.
- You can leave Bookmarks and Passwords enabled so your important data remains synchronized.
Note: Some newer Chrome versions may automatically redirect this address to the Google Account settings page. If that happens, locate the list of synchronized Chrome data and turn off Settings and Extensions there.
Now save anything you are working on and close every Chrome window.
Run the cleanup command:
- Press the Windows key on your keyboard.
- Type PowerShell.
- Open Windows PowerShell. Administrator access is not required.
- Copy the entire command shown below.
- Right-click inside the PowerShell window to paste the command, then press Enter.
- If Windows warns you about pasting multiple lines, select the option to continue.
$stamp = Get-Date -Format "yyyyMMdd-HHmmss"

Get-Process chrome -ErrorAction SilentlyContinue |
 Stop-Process -Force

$root = "$env:LOCALAPPDATA\Google\Chrome\User Data"

if (Test-Path $root) {
 $profiles = Get-ChildItem $root -Directory |
 Where-Object {
 $_.Name -eq "Default" -or
 $_.Name -match "^Profile \d+$"
 }

 foreach ($profile in $profiles) {
 foreach ($name in @(
 "Web Data",
 "Web Data-journal",
 "Web Data-wal",
 "Web Data-shm"
 )) {
 $file = Join-Path $profile.FullName $name

 if (Test-Path $file) {
 $backup = "$file.search-hijacker-backup-$stamp"
 Move-Item -LiteralPath $file -Destination $backup
 Write-Host "Backup created: $backup"
 }
 }
 }
}

Write-Host ""
Write-Host "Chrome search data has been cleaned."
Write-Host "You can now reopen Chrome."
Wait until PowerShell displays the following message:
Chrome search data has been cleaned.
You can now reopen Chrome.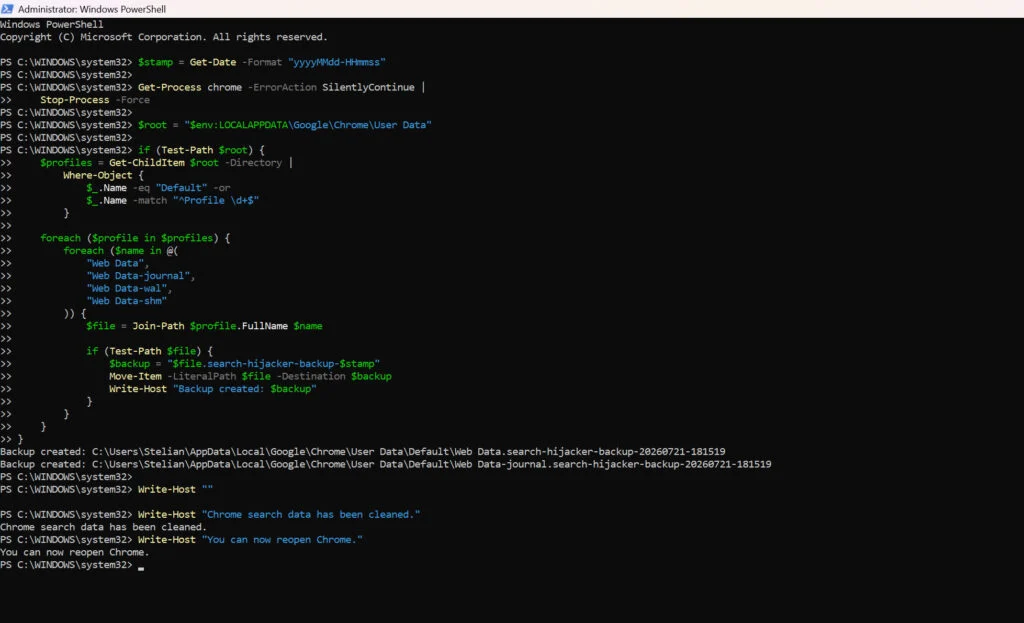
Close PowerShell and reopen Google Chrome. Chrome will automatically create a clean search database for every local profile.
Next, copy the following address, paste it into Chrome’s address bar, and press Enter:
chrome://settings/searchEnginesMake sure Google is selected as the default search engine. Test several searches from the address bar and confirm that they no longer pass through shady search engines.
Your important Chrome data is protected: the PowerShell cleanup does not remove bookmarks, saved passwords, browsing history, cookies, or installed extensions. However, it may reset locally stored Autofill addresses and form suggestions.
The original search database is not deleted. PowerShell renames it and adds
search-hijacker-backupto its filename so it can be recovered if necessary.Keep Settings and Extensions synchronization disabled while testing Chrome. Do not enable every extension at once. Enable only the extensions you recognize, one at a time, and test Chrome after each one.
If the redirect returns after enabling a particular extension, remove that extension immediately.
Reset Firefox for Windows to default settings
We will now reset your Firefox browser settings to their default. The reset feature fixes many issues by restoring Firefox to its factory default state while saving your essential information like bookmarks, passwords, web form auto-fill information, browsing history, and open tabs.
-
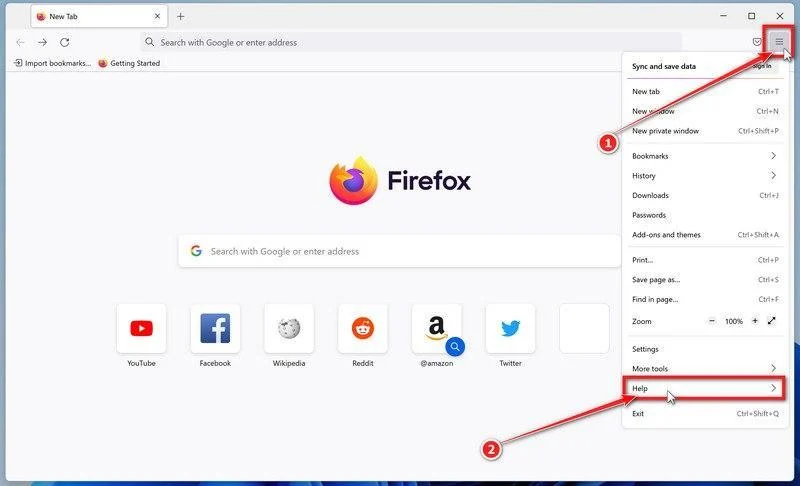
Open the Firefox menu and click “Help”
Click the three horizontal lines in the top-right corner of Firefox to open the main menu, then select “Help“.
-
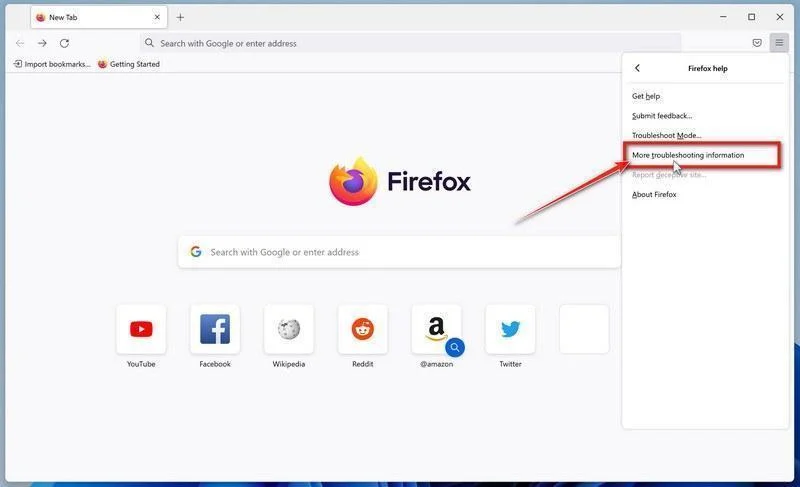
Click “More troubleshooting information”
In the Help menu, click “More troubleshooting information“.
-
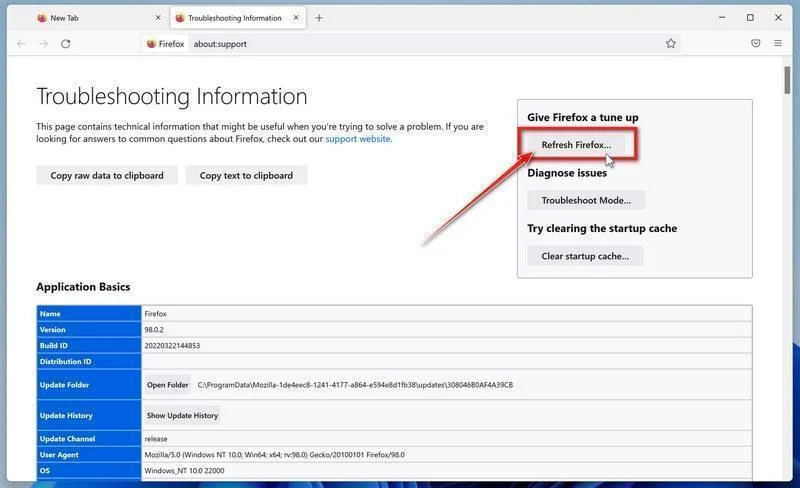
Click “Refresh Firefox”
On the “Troubleshooting Information” page, click the “Refresh Firefox” button in the top-right area of the page.
-
Confirm the refresh
In the confirmation window, click “Refresh Firefox” again. This removes extensions, themes, and customized settings — the usual hiding places for browser hijackers — while keeping your bookmarks, history, and saved passwords safe.
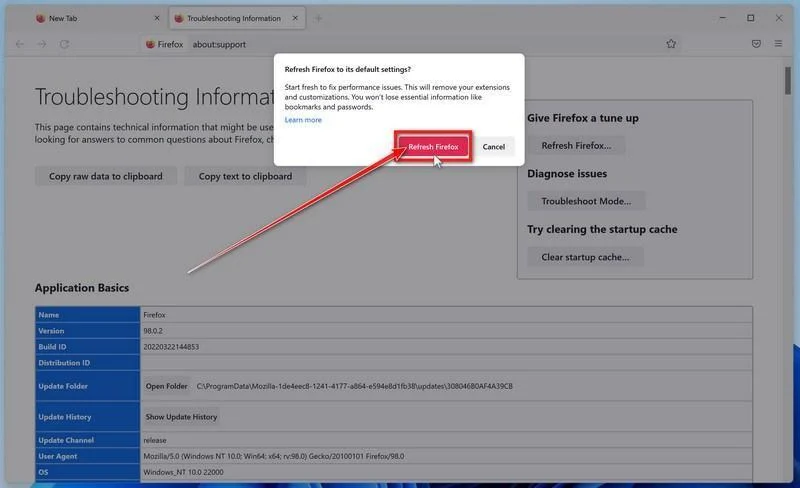
-
Click “Finish”
Firefox will close, reset itself to default settings, and reopen with a window listing the information that was restored. Click “Finish” — your Firefox is now clean.
About the “Old Firefox Data” folder: Firefox saves a copy of your old profile on your desktop. If something you need is missing after the reset, you can recover it from this folder. Otherwise, delete the folder — it contains sensitive data like passwords and cookies, and may also still hold the malicious files you just removed.
Reset Microsoft Edge to default settings
We will now reset your Microsoft Edge browser settings to their default. This will reset your startup page, new tab page, search engine, and pinned tabs. It will also disable all extensions and clear temporary data like cookies. Your favorites, history, and saved passwords will not be cleared.
Updated for Microsoft Edge on Windows 10 and Windows 11 — July 2026.
-
Open the Edge menu and click “Settings”
Open Microsoft Edge. In the top-right corner, click the three-dot (…) icon, then click Settings.
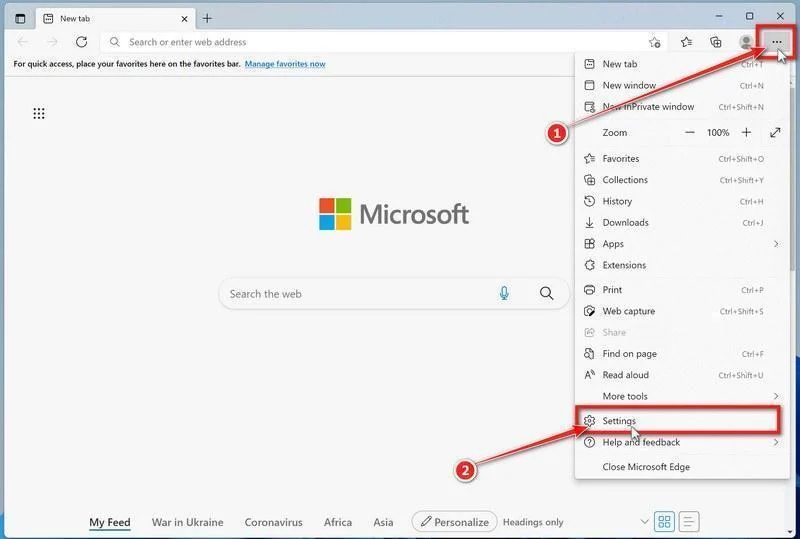
-
Prevent the unwanted settings from returning through Edge Sync
If you are signed in to Microsoft Edge, a bad setting or extension may be stored in your Microsoft account and return after the reset.
Copy the following address, paste it into the Edge address bar, and press Enter:
edge://settings/profiles/syncOn the Sync page, turn off these two options:
- Settings
- Extensions
You can leave Favorites and Passwords turned on.
If Edge says that sync is already off, simply continue to the next step.
Important: Edge Sync settings are separate for each profile. If you use more than one Edge profile, switch to each affected profile and repeat this step.
You do not need to sign out of your Microsoft account or delete the Edge profile.
-
Open “Reset settings”
In the left sidebar, click Reset settings.
You can also open the reset page directly. Copy the following address, paste it into the Edge address bar, and press Enter:
edge://settings/reset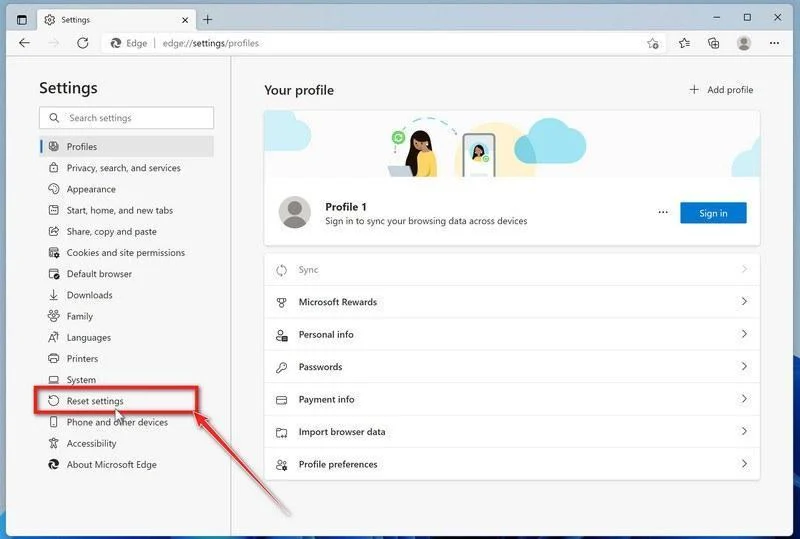
-
Click “Restore settings to their default values”
Click Restore settings to their default values.
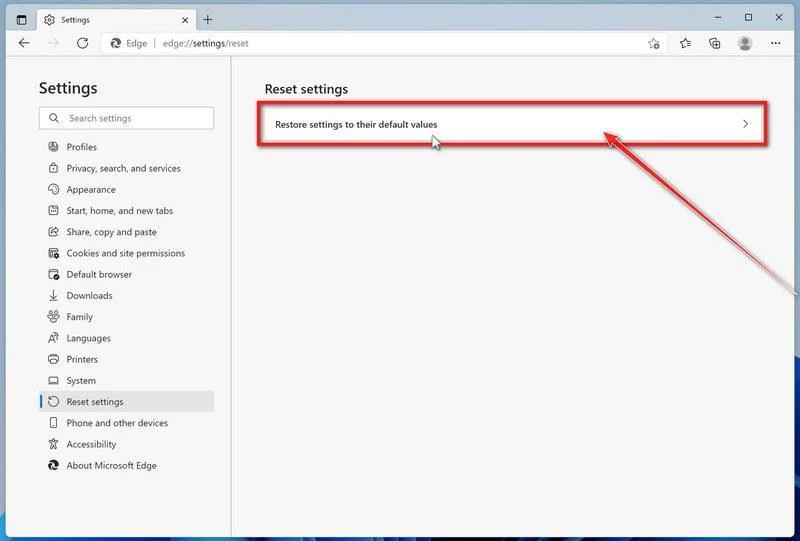
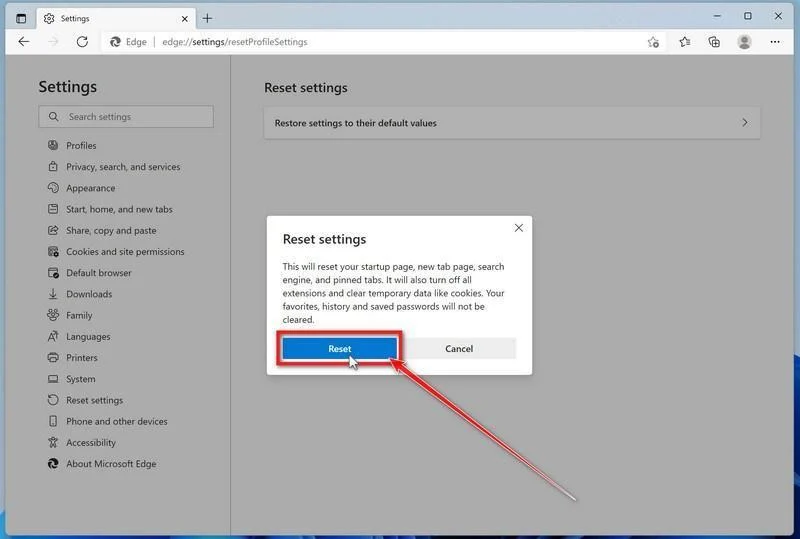
-
Confirm the reset
In the confirmation dialog, click Reset.
This resets the startup page, new tab page, search engine, and pinned tabs. It also disables all extensions and clears temporary site data, such as cookies.
Don’t worry: your favorites, browsing history, and saved passwords will not be deleted.
-
Check your extensions before turning them back on
Copy the following address, paste it into the Edge address bar, and press Enter:
edge://extensionsRemove any extension you do not recognize or no longer use. Pay particular attention to extensions related to search, coupons, shopping, PDF conversion, browser protection, new tabs, or video downloading.
Do not turn all extensions back on at the same time. Enable only the extensions you recognize and trust.
-
Select a trusted search engine
Copy the following address, paste it into the Edge address bar, and press Enter:
edge://settings/searchEnginesSelect Bing, Google, DuckDuckGo, or another search provider you trust and make it the default.
Remove any unknown search engines, especially providers with strange names or addresses that you did not add yourself.
Restart Edge and perform a search from the address bar. If searches are no longer redirected, you can stop here.
-
If the redirect remains, clean the corrupted search data without deleting the Edge profile
Use this additional step only if Edge continues to redirect searches after the normal reset.
This command cleans the search-engine database from every local Edge profile while keeping your favorites, saved passwords, browsing history, cookies, and profiles.
Before continuing: save anything you are working on because the command will close Microsoft Edge.
- Open the Windows Start menu.
- Type PowerShell.
- Open Windows PowerShell. Administrator access is not required.
- Copy the entire command below.
- Paste it into PowerShell and press Enter.
$stamp = Get-Date -Format "yyyyMMdd-HHmmss"
$root = Join-Path $env:LOCALAPPDATA "Microsoft\Edge\User Data"

Get-Process -Name msedge -ErrorAction SilentlyContinue |
    Stop-Process -Force -ErrorAction SilentlyContinue

Start-Sleep -Seconds 2

if (-not (Test-Path -LiteralPath $root)) {
    Write-Host "The Microsoft Edge profile folder was not found:"
    Write-Host $root
    return
}

$profiles = Get-ChildItem -LiteralPath $root -Directory |
    Where-Object {
        $_.Name -eq "Default" -or
        $_.Name -match "^Profile \d+$"
    }

$movedFiles = 0

foreach ($profile in $profiles) {
    foreach ($name in @(
        "Web Data",
        "Web Data-journal",
        "Web Data-wal",
        "Web Data-shm"
    )) {
        $file = Join-Path $profile.FullName $name

        if (Test-Path -LiteralPath $file) {
            $backup = "$file.search-reset-backup-$stamp"

            try {
                Move-Item -LiteralPath $file -Destination $backup -ErrorAction Stop
                Write-Host "Cleaned: $($profile.Name)\$name"
                $movedFiles++
            }
            catch {
                Write-Warning "Could not clean: $file"
            }
        }
    }
}

Write-Host ""

if ($movedFiles -gt 0) {
    Write-Host "Microsoft Edge search data has been cleaned." -ForegroundColor Green
    Write-Host "You can now reopen Microsoft Edge."
}
else {
    Write-Host "No Edge search database files were found." -ForegroundColor Yellow
}
The command does not permanently delete the original files. It renames them as backup files, and Edge creates a clean search database when it starts again.
Note: this additional cleanup may also reset saved form-fill suggestions, saved addresses, and manually added search engines. It does not delete favorites, passwords, or browsing history.
-
Reopen Edge and test the browser
Open Microsoft Edge again, visit edge://settings/searchEngines, and select your preferred search engine.
Perform several searches from the address bar to confirm that the redirect is gone.
Keep synchronization for Settings and Extensions turned off until you are certain that the computer and extensions are clean. If you enable them again, turn them on one at a time and test Edge after each change.
-
If Edge still redirects your searches
Open edge://policy. If this is your personal computer and Edge displays unknown policies such as ExtensionInstallForcelist or DefaultSearchProvider, the hijacker may be installed outside the browser profile.
In that situation, continue with the next malware-removal steps and run a complete antivirus scan. If the computer belongs to a company or school, contact its IT administrator before changing any policies.
Reset Internet Explorer to default settings
We will now reset your Internet Explorer browser settings to their default. You can reset Internet Explorer settings to return them to the state they were in when Internet Explorer was first installed on your computer.
-
Go to “Internet Options”.
Open Internet Explorer, click on the gear icon in the upper-right part of your browser, then select “Internet Options“.
-
Select the “Advanced” tab, then click “Reset”
In the “Internet Options” dialog box, select the “Advanced” tab, then click on the “Reset” button.
-
Click on “Reset”.
In the “Reset Internet Explorer settings” section, select the “Delete personal settings” checkbox, then click on the “Reset” button.
-
Click on “Close”.
When Internet Explorer has completed its task, click on the “Close” button in the confirmation dialogue box.
Close your browser and then you can open Internet Explorer again.
STEP 3: Use Malwarebytes Anti-Malware to remove malware and unwanted programs
In this third step, we will install Malwarebytes to scan and remove any infections, adware, or potentially unwanted programs that may be present on your computer.
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

STEP 4: Use HitmanPro to scan your computer for badware
In this next step, we will scan the computer with HitmanPro to ensure that no other malicious programs are installed on your device.
HitmanPro is a second-opinion scanner — it’s designed to catch what your main antivirus might have missed. Instead of relying on a single detection engine, it checks the behavior of files in the locations where malware usually hides. Anything suspicious gets sent to the cloud, where it’s analyzed by two of the best antivirus engines available: Bitdefender and Kaspersky.
Good news: scanning is completely free, with no limits. You only need a license when it’s time to remove what was found — and even then, you can activate a free one-time 30-day trial to clean your PC at no cost. (A full license is $24.95 per year for 1 PC.)
-
Download HitmanPro
Click the button below to download HitmanPro. Remember — the scan is free, so you have nothing to lose by checking your PC.
Download HitmanProFree scan. Removing threats needs the free 30-day trial. Opens the official HitmanPro page in a new tab. HitmanProSecond-opinion malware scanner from Sophos
-
Install HitmanPro
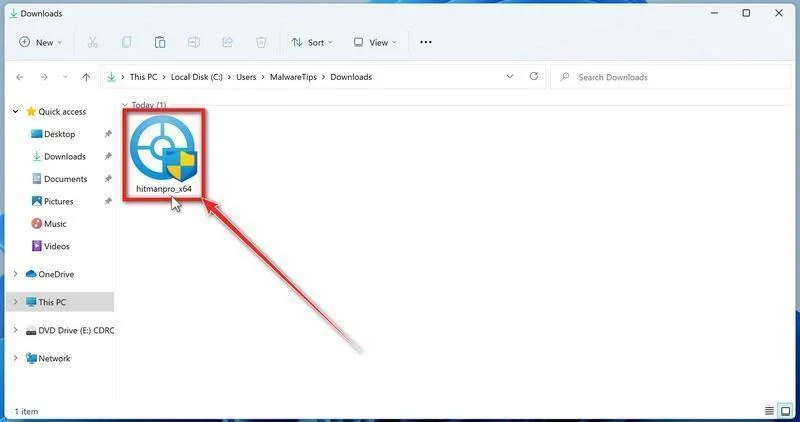
When the download finishes, open your Downloads folder and double-click the file: “hitmanpro.exe” on 32-bit Windows, or “hitmanpro_x64.exe” on 64-bit Windows.
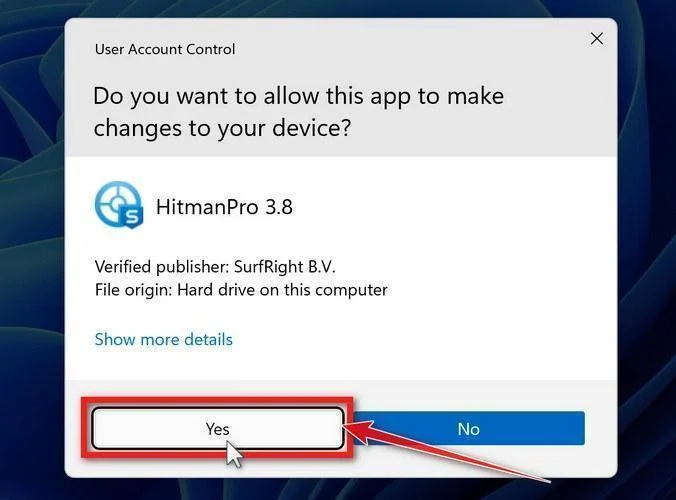
If a User Account Control pop-up asks whether HitmanPro can make changes to your device, click “Yes” to continue.
-
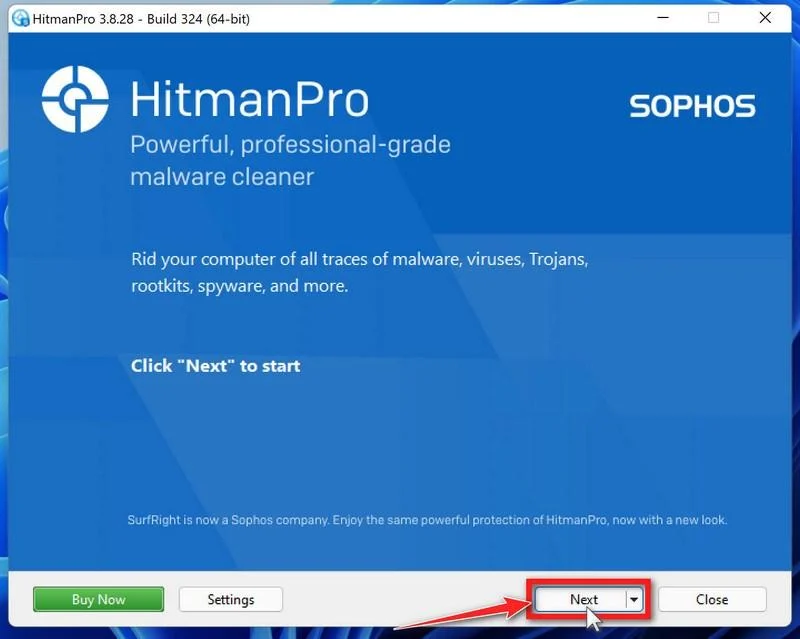
Follow the On-Screen Prompts
On the HitmanPro start screen, click “Next” to begin the system scan. No lengthy setup required — it goes straight to work.
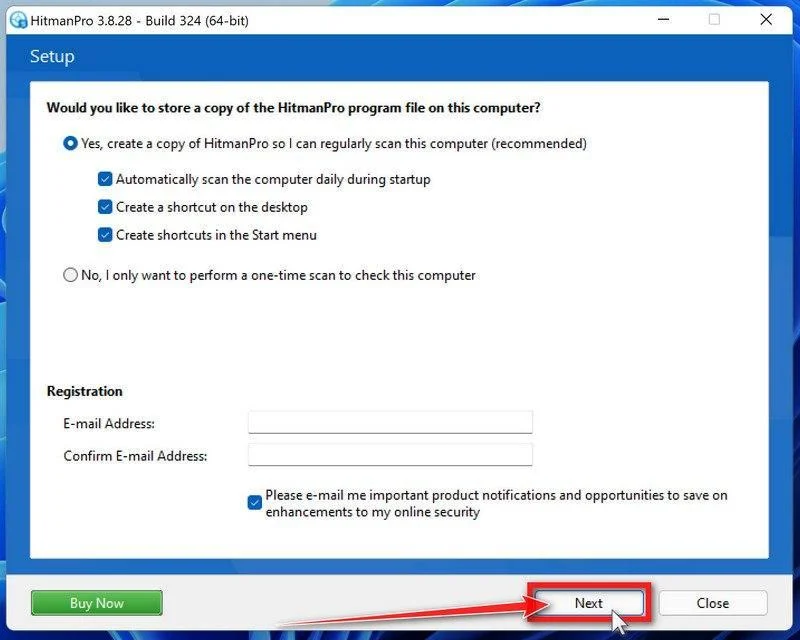
-
Wait for the Scan to Finish
HitmanPro will now check your computer for malicious programs. This usually takes just a few minutes thanks to its cloud-based scanning.
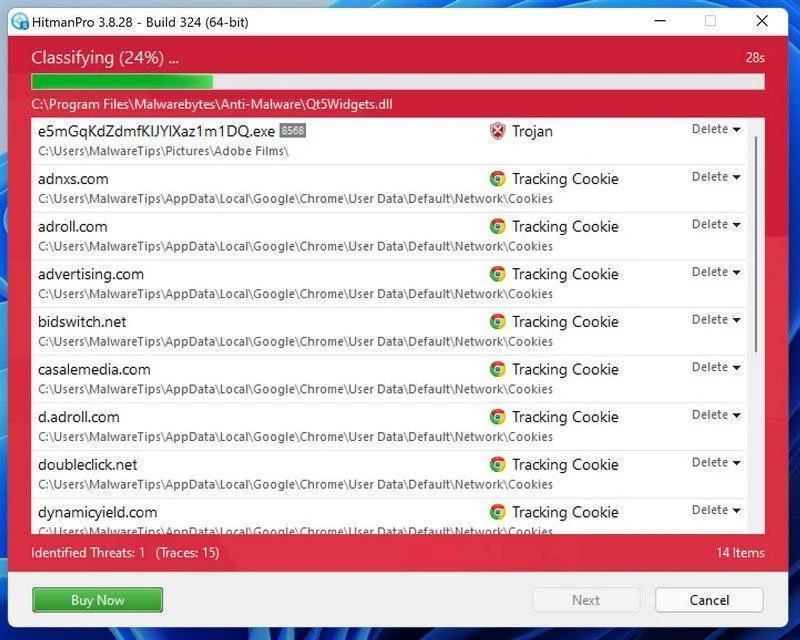
-
Review the Results and Click “Next”
When the scan is done, HitmanPro will show you everything it found. Click “Next” to remove the detected threats.
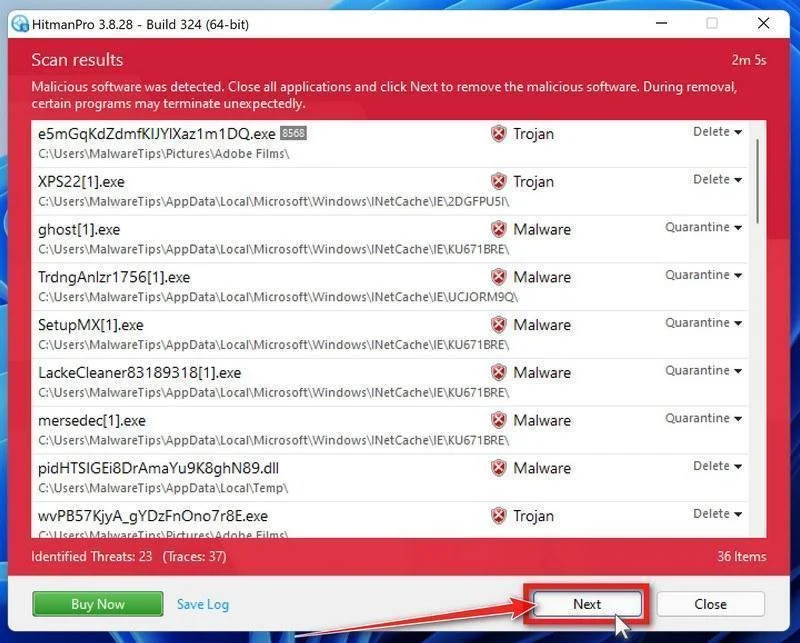
-
Click “Activate Free License”
To remove the malicious files, click the “Activate free license” button. This starts your free 30-day trial — no payment details needed — and unlocks the full cleanup.
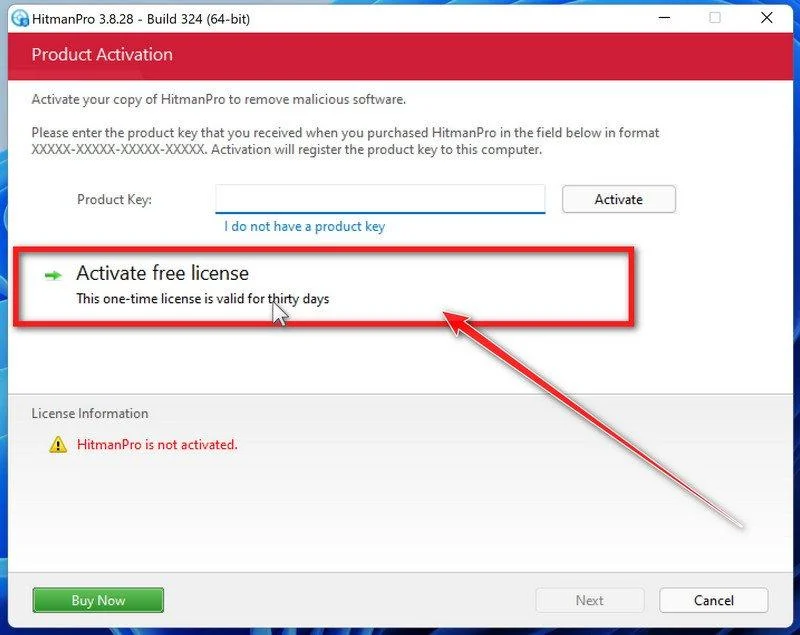
When the removal is complete, HitmanPro will show a summary of everything it cleaned. Click Next, then click Reboot if prompted. If there’s no reboot prompt, just click Close — your PC is clean.
STEP 5: Use AdwCleaner to remove adware and malicious browser policies
In this final step, we will use AdwCleaner to remove the malicious browser policies that were set by browser hijackers on your computer and delete malicious browser extensions.
AdwCleaner is a free on-demand scanner that specializes in adware, browser hijackers, and unwanted toolbars — the exact threats that mainstream antivirus programs often miss. It also includes tools that repair the damage malware leaves behind, like hijacked browser settings and malicious policies. It’s a quick scan that’s well worth running.
-
Download AdwCleaner
Click the button below to download AdwCleaner — it’s free, portable, and requires no installation.
Download AdwCleanerOpens the official download page in a new tab. Malwarebytes AdwCleanerRemoves adware and unwanted programs at no cost
-
Run AdwCleaner
Open your Downloads folder and double-click the file named “adwcleaner.exe“. There’s no installation — the program starts right away.
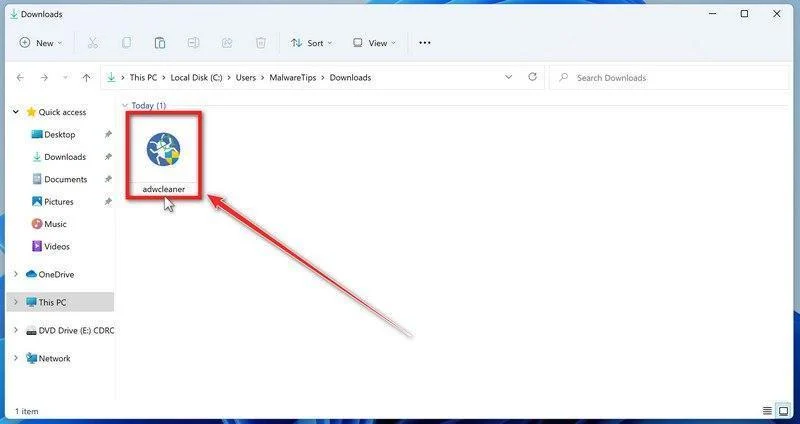
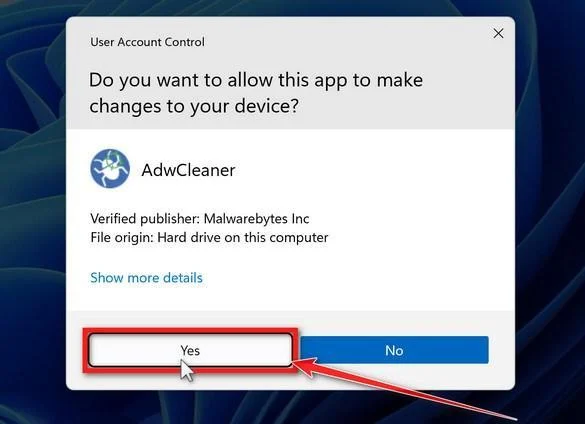
If Windows asks whether you want to allow AdwCleaner to run, click “Yes“. When the license agreement appears, click I agree to continue.
-
Enable “Reset Chrome policies”
This setting removes malicious browser policies — a trick malware uses to lock your browser settings so you can’t change them back. Click “Settings” on the left side of the window, then turn on “Reset Chrome policies“.
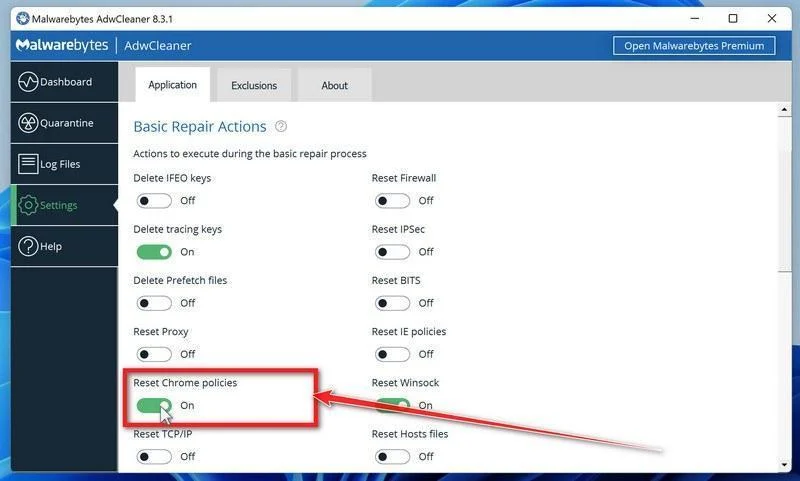
-
Start the Scan
Click “Dashboard” on the left side of the window, then click the “Scan” button.
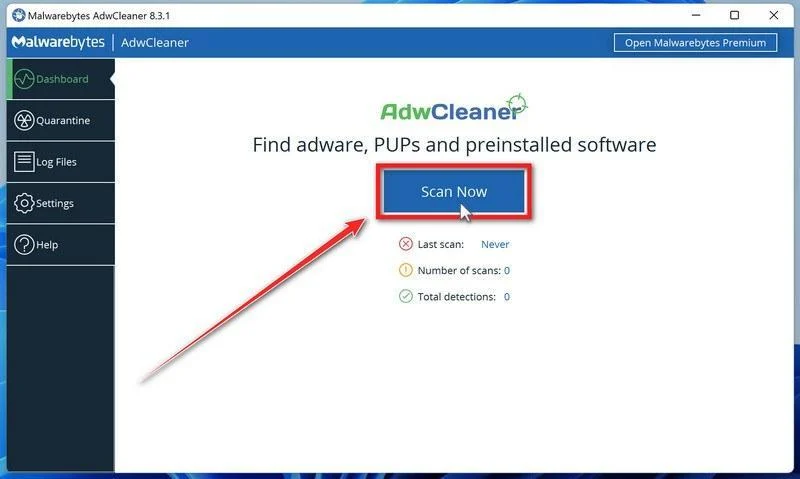
-
Wait for the Scan to Finish
AdwCleaner will now check your computer for adware and other malware. This usually takes only a few minutes — it’s one of the fastest scanners around.
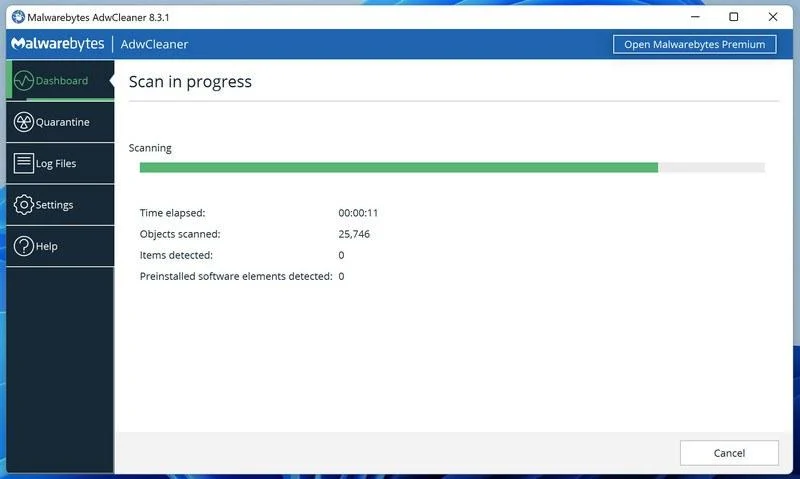
-
Quarantine the Detected Threats
When the scan finishes, AdwCleaner will list everything it found. Click the “Quarantine” button to remove all the malicious items at once.
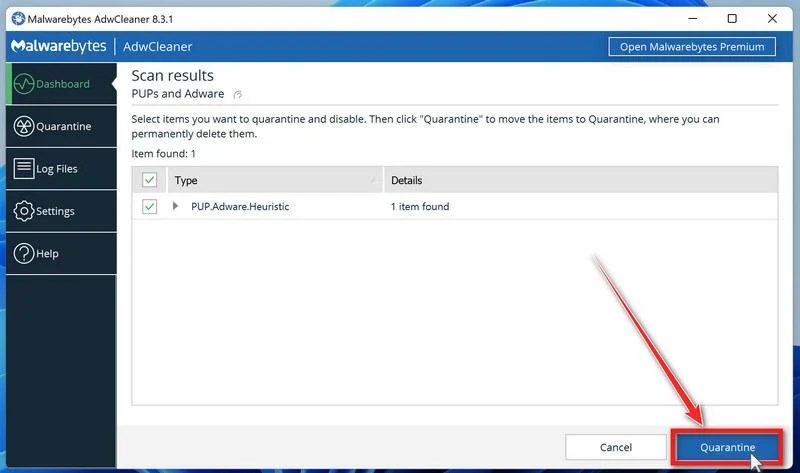
-
Click “Continue” to Finish the Cleanup
Save any open work first — AdwCleaner needs to close your open programs before it can clean. When you’re ready, click the “Continue” button.
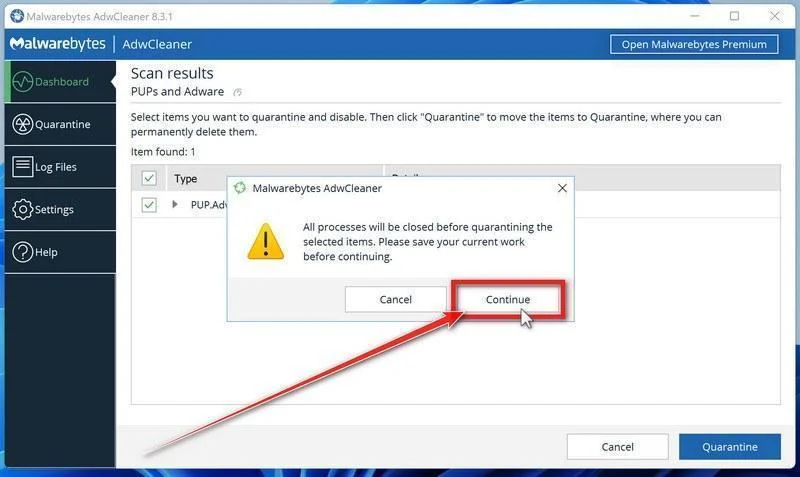
AdwCleaner will now delete all detected malware from your computer. If it asks you to restart your PC, allow it — your computer will be clean when you log back in.
That’s it — your Windows computer is now clean. The unwanted apps, adware, and any other malware have been removed.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Remove Unwanted Apps and Malware from Mac
- STEP 1: Remove malicious profiles
- STEP 2: Delete malicious apps
- STEP 3: Reset browsers back to default settings
- STEP 4: Run a scan with Malwarebytes for Mac to remove malware
STEP 1: Remove malicious profiles
Profiles are used by IT admins in businesses to control the behavior of their Macs. These profiles can configure a Mac to do many different things, some of which are not otherwise possible.
When it comes to home users, adware and browser hijackers are using the configuration profile to prevent users from removing malicious programs from the computer. This also prevents the user from changing that behavior in the browser’s settings.
In this first step, we will check your computer to see if any configuration profiles are installed. To do this, follow the below steps:
-
Open “System Settings”
From the Apple menu () in the top-left corner of the screen, select System Settings. (On macOS Monterey and earlier, this is called System Preferences.)
-
Look for “Profiles”
In the System Settings window, search for Profiles — on newer macOS versions you’ll find it under Privacy & Security, or you can type “Profiles” in the search box.
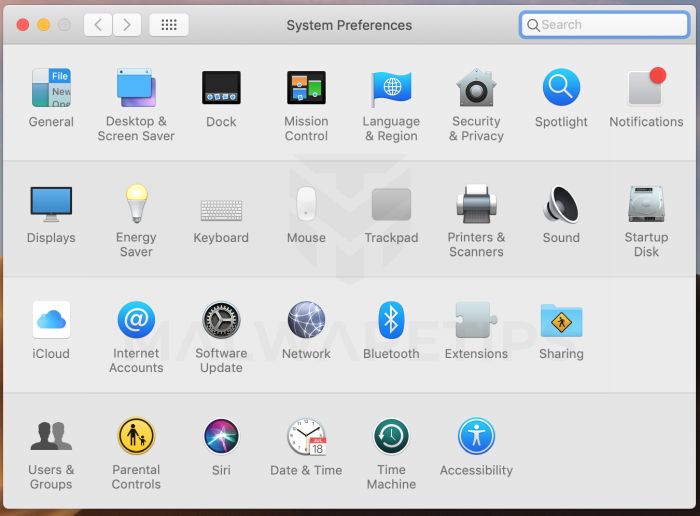 No Profiles section? Good news — that means no profiles are installed on your Mac, which is completely normal. Skip ahead to the next step of this guide.
-
Remove the malicious profiles
Malware uses configuration profiles to lock your browser settings — forcing a fake search engine or homepage on you and preventing you from changing it back. If you see a profile you don’t recognize (and your Mac isn’t managed by your workplace or school), select it, press the − (minus) button, and click Remove to confirm.
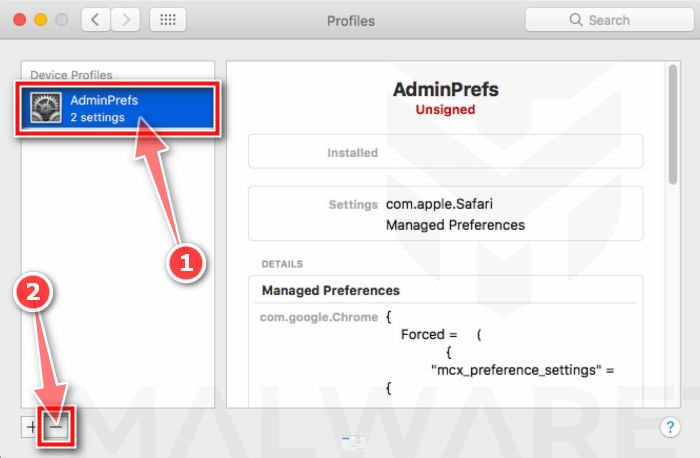
STEP 2: Delete malicious apps
In this second step, we will try to identify and remove any malicious apps and files that might be installed on your computer. Sometimes redirects or adware programs can have usable Uninstall entries that can be used to remove these programs.
-
Quit the malicious programs
Check the Apple menu bar in the top-right corner of your screen. If you see an icon you don’t recognize, click it and select Quit. This stops the malware from running so it can’t interfere while we remove it.
-
Open “Finder”
Click the Finder icon in your dock.
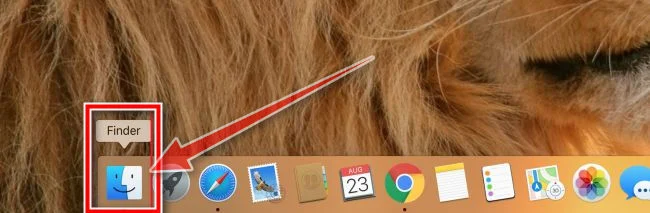
-
Click on “Applications”
In the Finder sidebar, click “Applications“.
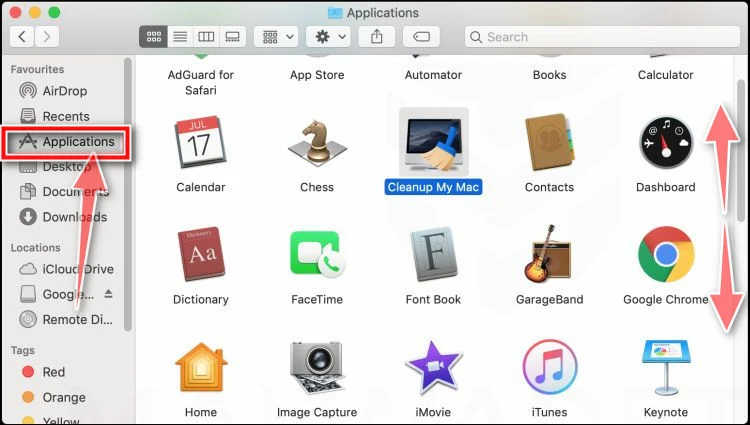
-
Find and remove the malicious app
Scroll through the list of installed apps and look for anything suspicious — an app you don’t remember installing, or one with a strange or generic name. When you find it, right-click it and select “Move to Trash“.
Some known malicious programs to look for: SearchMine, TakeFresh, TopResults, FeedBack, ApplicationEvents, GeneralOpen, PowerLog, MessengerNow, ImagePrime, GeneralNetSearch, Reading Cursors, GlobalTechSearch, PDFOnline-express, See Scenic Elf, MatchKnowledge, Easy Speedtest, and WebDiscover. The names change constantly, though — so treat any app you can’t account for as suspect.
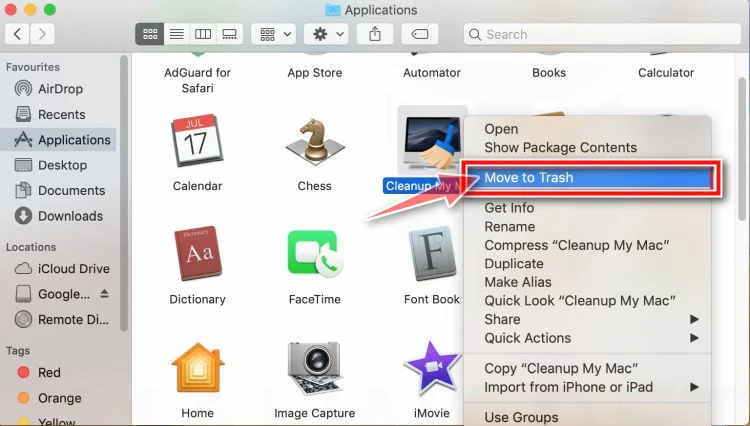
-
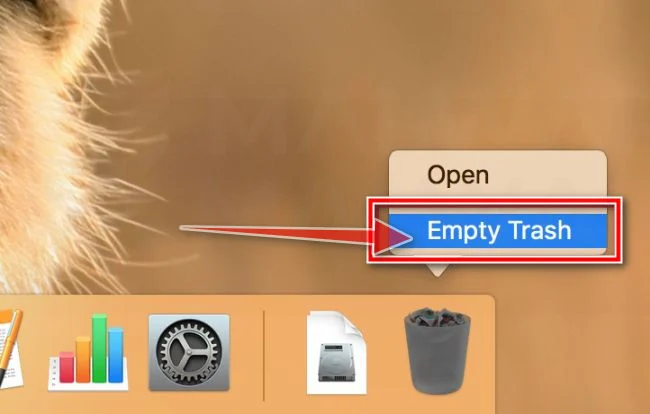
Empty the Trash
Right-click the Trash icon in your dock and select “Empty Trash“. This permanently deletes the malicious app you just removed — until you do this, the malware is still on your Mac.
Find and remove the malicious files
Malware on Mac uses launch agents and launch daemons — small files that automatically restart the malware every time you boot your Mac. We’ll check the four folders where they hide:
- Click the desktop to make sure you’re in Finder, then open the “Go” menu and click “Go to Folder“.
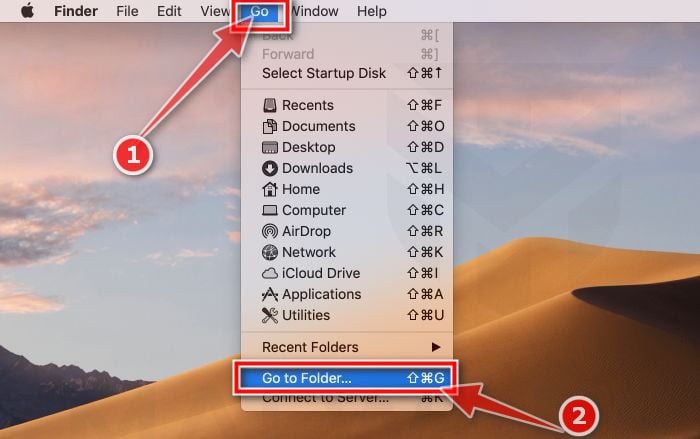
- Copy and paste each of the paths below into the window, one at a time, and click Go after each:
- /Library/LaunchAgents
- ~/Library/LaunchAgents
- /Library/Application Support
- /Library/LaunchDaemons
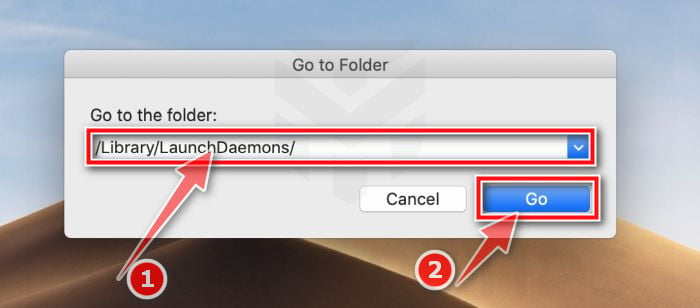
- In each folder, look for suspicious .plist files — typically named after the malware or with odd, random-looking names. Some known examples: “com.adobe.fpsaud.plist”, “installmac.AppRemoval.plist”, “myppes.download.plist”, “mykotlerino.ltvbit.plist”, and “com.myppes.net-preferences.plist”. When you find a malicious file, move it to the Trash — then empty the Trash again when you’re done.
Be careful: these folders also contain files belonging to legitimate apps — especially /Library/Application Support, where programs like Adobe, Google, and Microsoft store their data. Only delete files you’re confident are malicious. If you’re unsure about a file, search its exact name online first — or skip it; the Malwarebytes scan in the next step will catch what you miss.
- Click the desktop to make sure you’re in Finder, then open the “Go” menu and click “Go to Folder“.
STEP 3: Reset browsers back to default settings
In this third step, we will remove spam push notifications and malicious extensions, and change to default any settings that might have been changed by malware.
For each browser that you have installed on your computer, please click on the tab below and follow the displayed steps to reset that browser.
Remove malicious extensions and settings from Safari
To remove malware from Safari we will check if there are any malicious extensions installed on your browser and what settings have been changed by this malicious program.
-
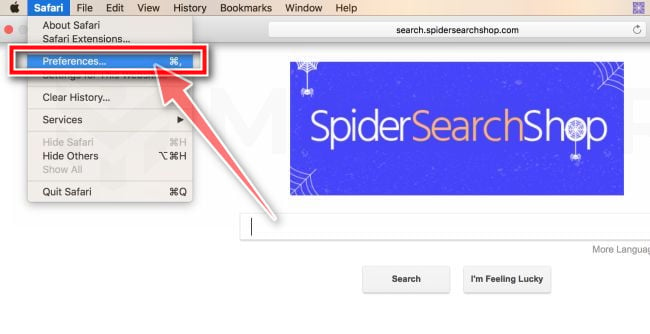
Go to Safari’s “Preferences”.
On the menu bar, click the “Safari” menu and select “Preferences”.
-
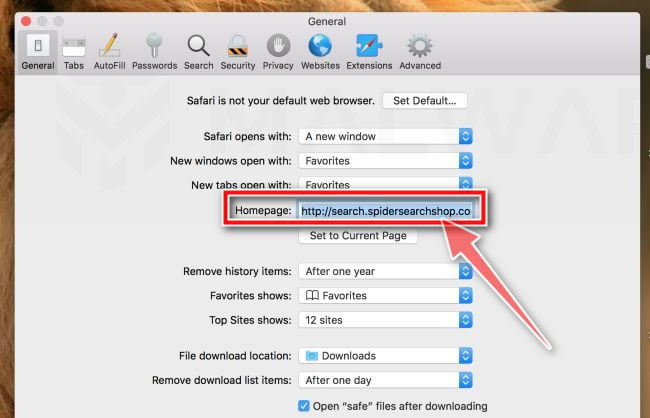
Check Homepage.
This will open a new window with your Safari preferences, opened to the “General” tab. Some browser hijackers may change your default homepage, so in the Homepage field make sure it’s a web page you want to use as your start-up page.
-
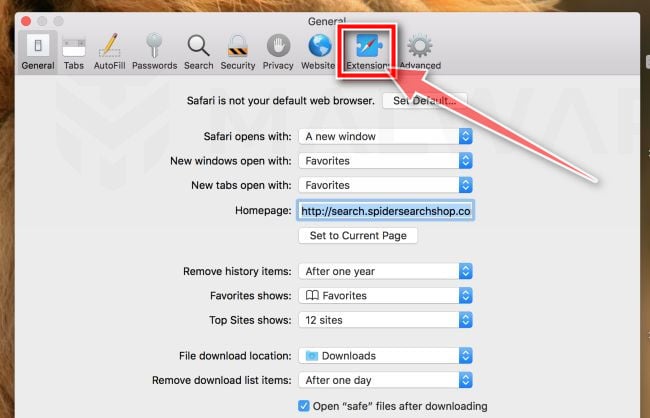
Click “Extensions”
Next, click on the “Extensions” tab.
-
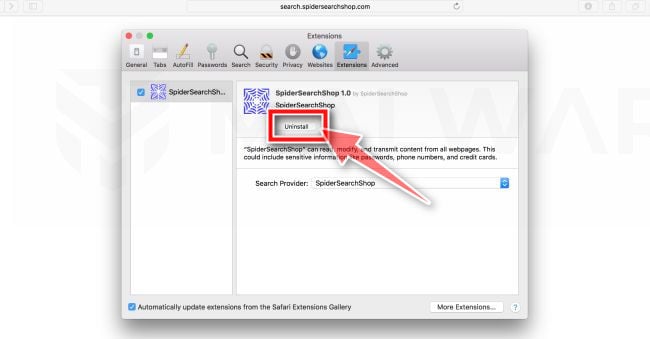
Find and uninstall malicious extensions.
The “Extensions” screen will be displayed with a list of all the extensions installed on Safari. Look out for any suspicious browser extension that could be behind all the drama – anything you don’t remember downloading or that doesn’t sound like a genuine extension. By default, there are no extensions installed on Safari so it’s safe to remove an extension
-
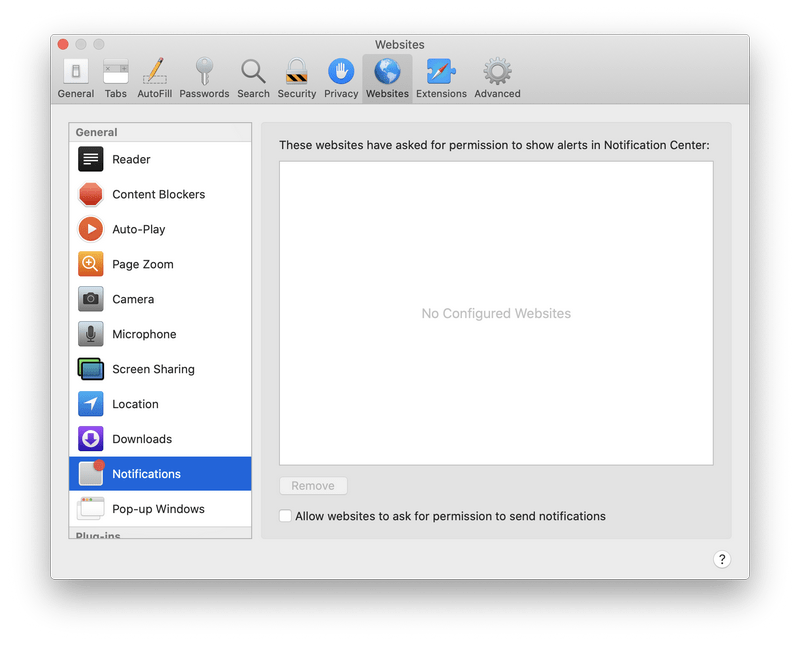
Remove spam notifications ads
Click Preferences, click Websites, then click Notifications. Deselect “Allow websites to ask for permission to send push notifications”.
-
Remove all data stored by websites on your computer.
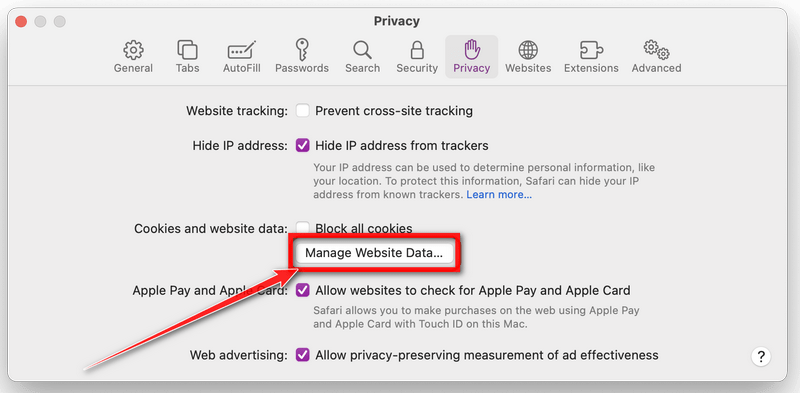
In the Safari menu, choose “Preferences…”, select “Privacy” at the top of the new window that appears, and then click the “Manage Website Data” button.
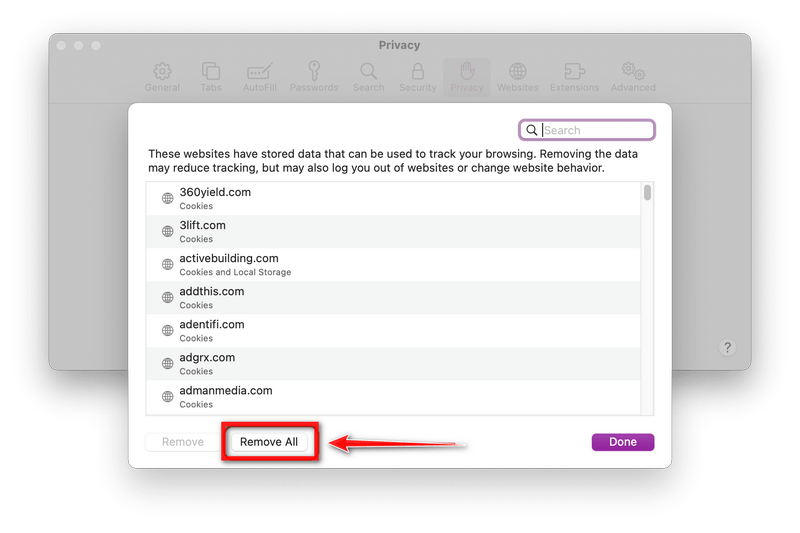
In the next dialog box, click “Remove All“. It will ask you if you are sure you want to remove all data stored by websites on your computer. Select “Remove Now” to clear data that could be used to track your browsing.
-
Empty Safari Caches.
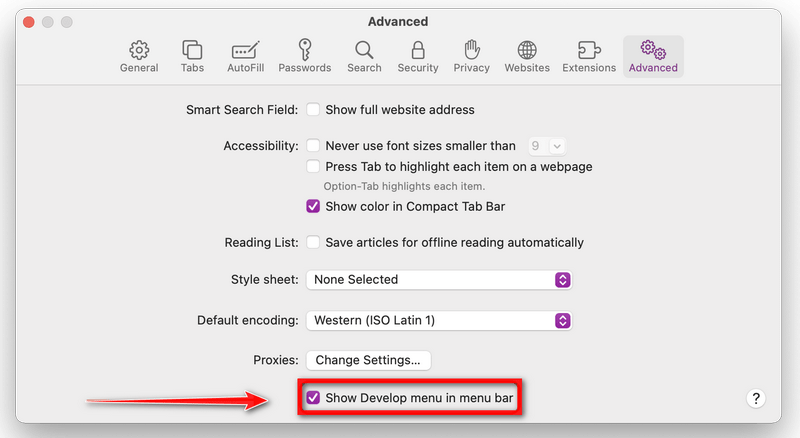
From your Safari menu bar, click Safari and select Preferences, then select the Advanced tab. Enable the checkbox to “Show Develop menu in menu bar“.
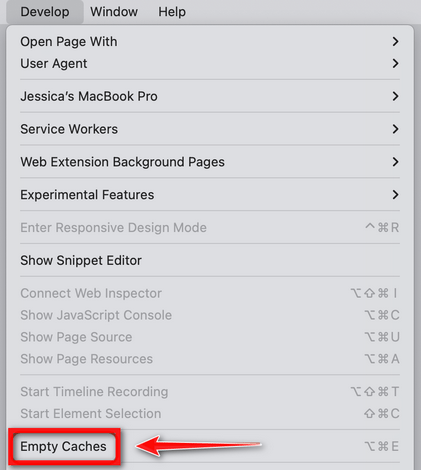
From the menu bar select Develop, then click on Empty Caches as seen in the image below.
Remove malware from Chrome for Mac
To remove malware from Chrome for Mac we will reset the browser settings to their default. Doing these steps will erase all configuration information from Chrome such as your home page, tab settings, saved form information, browsing history, and cookies. This process will also disable any installed extensions. All of your bookmarks, though, will be preserved.
-
Click on the three dots at the top right and go to Settings.
Click on Chrome’s main menu button, represented by three dots at the top right corner. Now click on the menu option labeled Settings as shown by the arrow in the picture below, which will open the basic settings screen.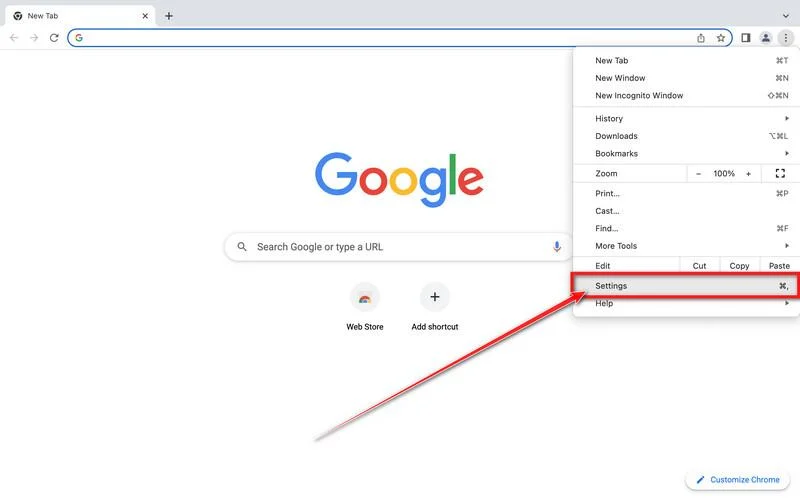
-
In the left sidebar, click on the “Reset and Cleanup” option.
In the left sidebar, click on “Reset and clean up“.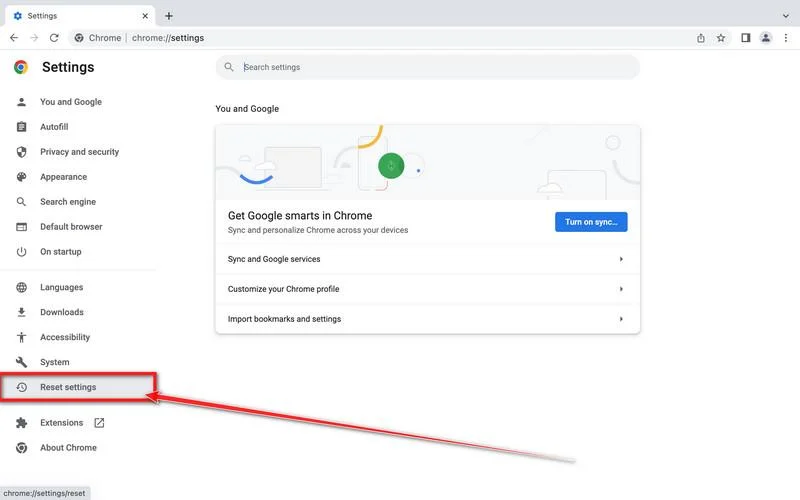
-
Click “Reset settings to their original defaults”.
Now click on the “Reset settings to their original defaults”. link as shown in the image below.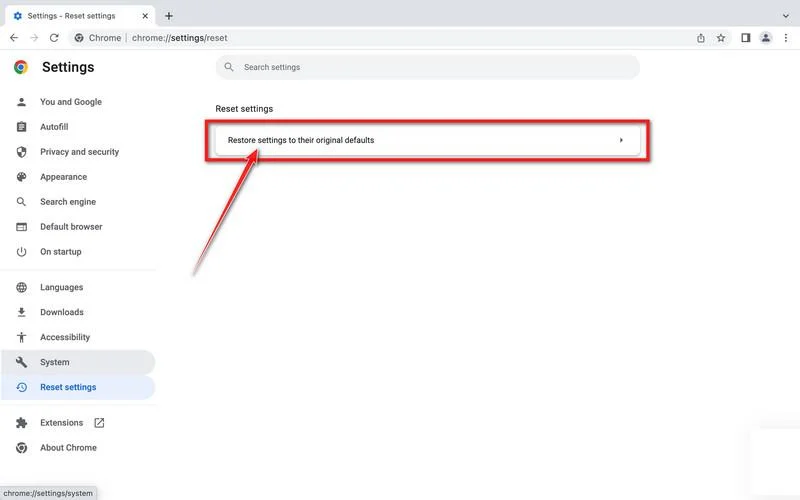
-
Click “Reset Settings” button.
A confirmation dialog should now be displayed, detailing the components that will be restored to their default state should you continue with the reset process. To complete the restoration process, click on the “Reset Settings” button.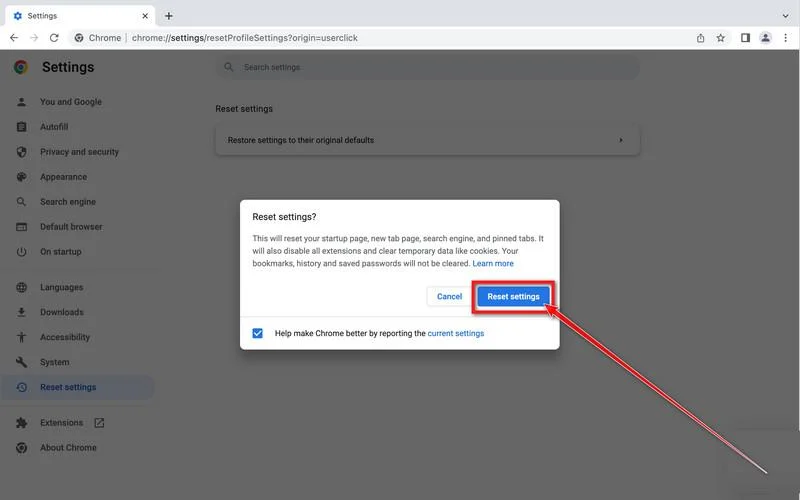
-
(Optional) Reset Chrome Data Sync.
In case a malicious extension reinstalls itself even after performing a browser reset, you have an additional option to reset the data sync for your browser. To do this, navigate to chrome.google.com/sync and click on the Clear Data button.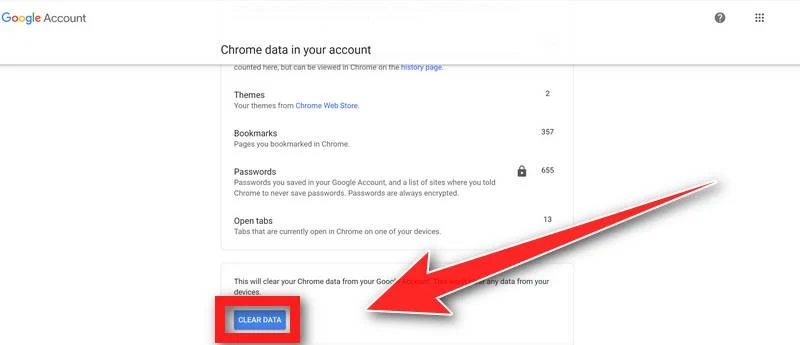
Remove malware from Firefox for Mac
To remove malware from Firefox for Mac we will reset the browser settings to its default. The reset feature fixes many issues by restoring Firefox to its factory default state while saving your essential information like bookmarks, passwords, web form auto-fill information, browsing history, and open tabs.
-
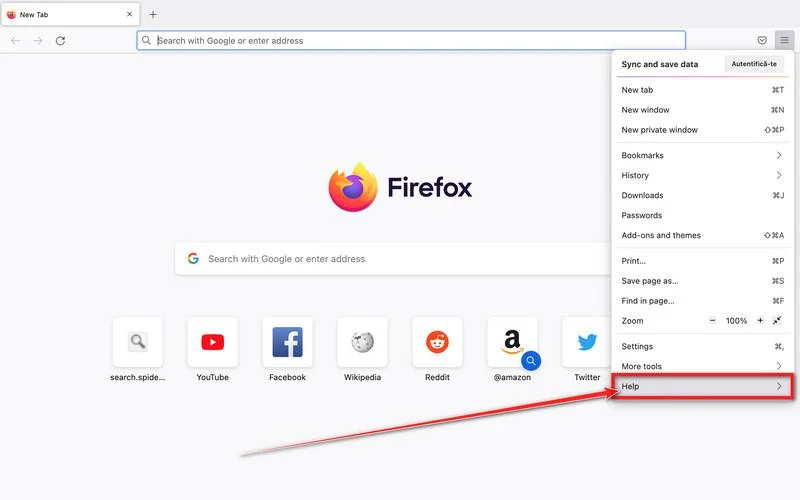
Go to the “Help” menu.
Click on Firefox’s main menu button, represented by three horizontal lines. When the drop-down menu appears, select the option labeled “Help“.
-
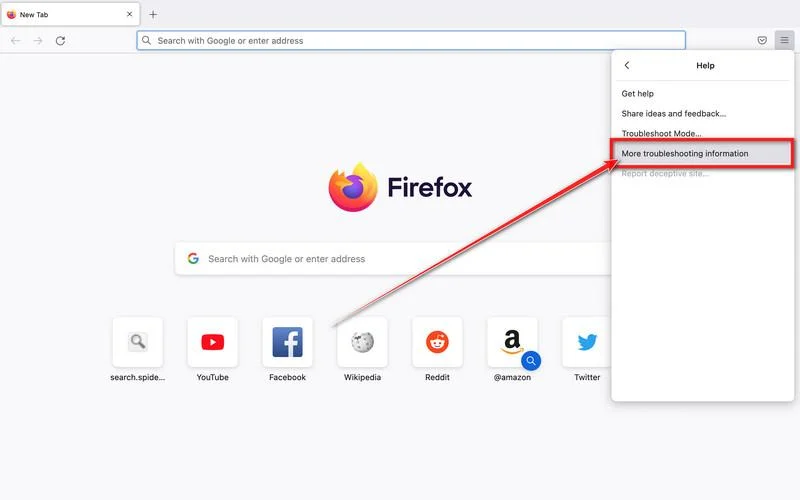
Click “Troubleshooting Information”.
Next click on the “Troubleshooting Information” option as indicated by the arrow in the image below. This will bring you to a Troubleshooting page.
-
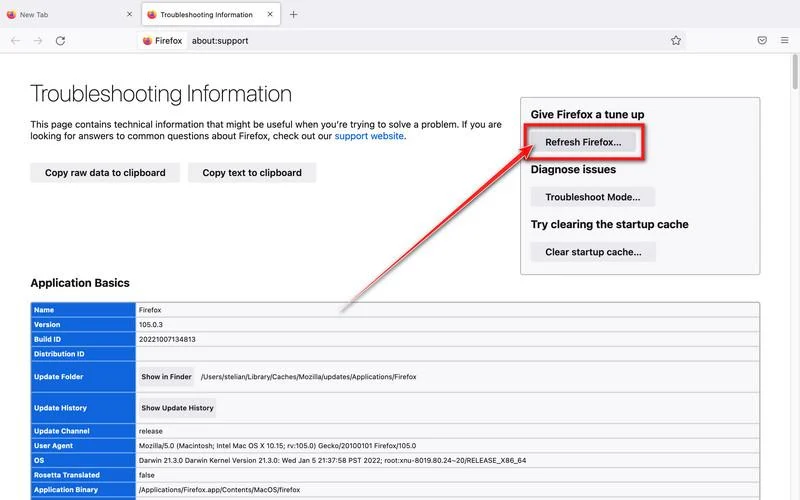
Click on “Refresh Firefox”
Click the “Refresh Firefox” button in the upper-right corner of the “Troubleshooting Information” page.
-
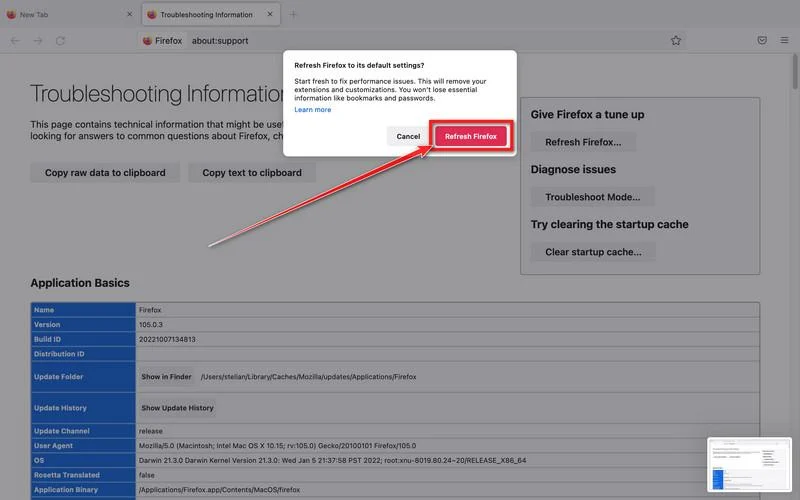
Confirm.
To continue, click on the “Refresh Firefox” button in the new confirmation window that opens.
-
Click on “Finish”.
Firefox will close itself and will revert to its default settings. When it’s done, a window will list the information that was imported. Click on the “Finish“.
STEP 4: Run a scan with Malwarebytes for Mac to remove malware
In this final step, we will scan the computer with Malwarebytes for Mac to find and remove any malicious programs that might be installed on your Mac.
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now clean. The unwanted apps, adware, and any other malware have been removed.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Remove Unwanted Apps and Malware from Android
- STEP 1: Uninstall malicious apps
- STEP 2: Reset browsers back to default settings
- STEP 3: Use Malwarebytes for Android to remove malicious apps
STEP 1: Uninstall malicious apps
In this first step, we will check if any malicious apps are installed on your phone. Sometimes browser hijackers or adware apps can have usable Uninstall entries that can be used to remove these apps.
-
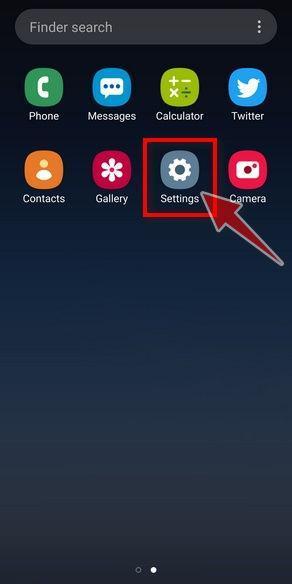
Open the “Settings” menu.
Tap on the “Settings” app from your phone menu or home screen.
-
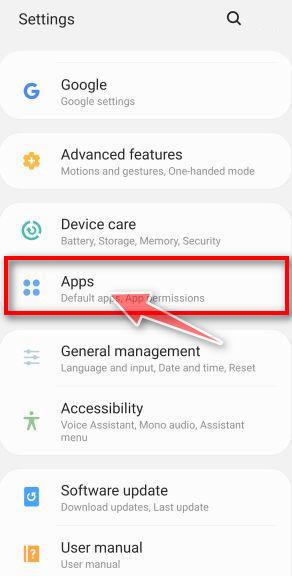
Tap on “Apps”.
When the “Settings” menu opens, tap on “Apps” (or “App Manager”) to see all the installed applications on your phone.
-
Find the malicious app.
The “Apps” screen will be displayed with a list of all the applications that are installed on your phone. Scroll through the list and look out for any suspicious app that could be behind all the drama – anything you don’t remember downloading or that doesn’t sound like a genuine program.
Most often, cyber criminals hide malware inside video or photo editing apps, weather apps, and camera apps.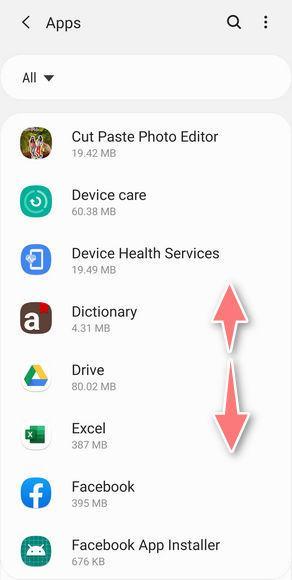
-
Uninstall the malicious app
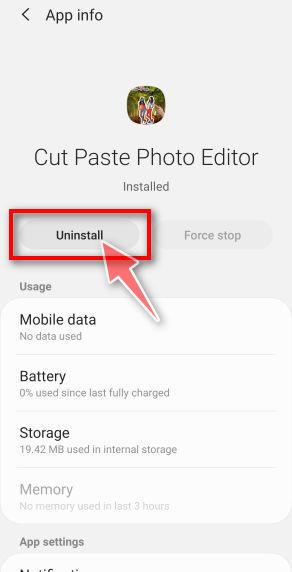
When you find a suspicious or malicious app, tap on it to uninstall it. This won’t start the app but will open up the app details screen. If the app is currently running press the “Force stop” button, then tap on “Uninstall”.
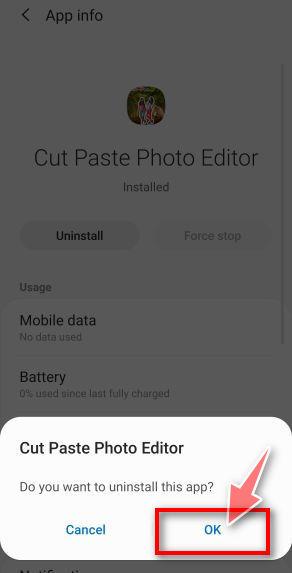
A confirmation dialog should be displayed to confirm you want to uninstall the app, tap on “OK” to remove the malicious app from your phone.
STEP 2: Reset browsers back to default settings
In this second step, we will reset your browser to its default settings to remove spam notifications, unwated search redirects, and restore its factory settings
Resetting the browser settings to their default it’s an easy task on Windows or Mac computers; however, when it comes to Android, this can’t be done directly because it’s not an option built-in into the browser settings. Restoring the browser settings on Android can be done by clearing the application data. This will remove all the cookies, cache, and other site settings that may have been saved. So let’s see how we can restore your browser to its factory settings.
Remove malware from Chrome for Android
To reset Chrome for Android to its default settings, follow the below steps:
-
Open the “Settings” menu.
Tap on the “Settings” app from your phone menu or home screen.
-
Tap on “Apps”.
When the “Settings” menu opens, tap on “Apps” (or “App Manager”) to see all the installed applications on your phone.
-
Find and tap on Chrome.
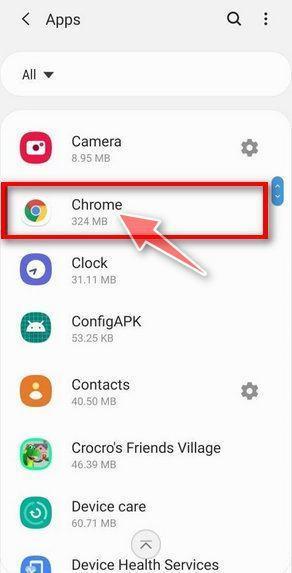
The “Apps” screen will be displayed with a list of all the apps installed on your phone. Scroll through the list until you find the Chrome app, then tap on it to open the app’s details.
-
Tap “Storage”.
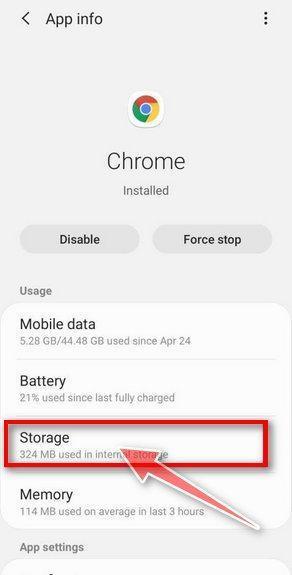
When Chrome’s app info menu is displayed, tap on “Storage“.
-
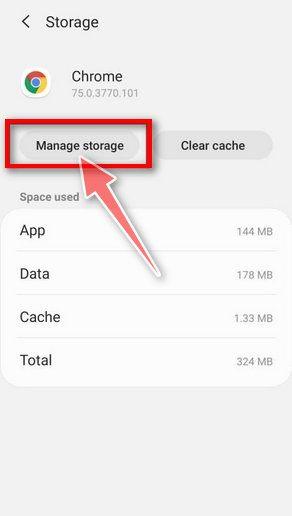
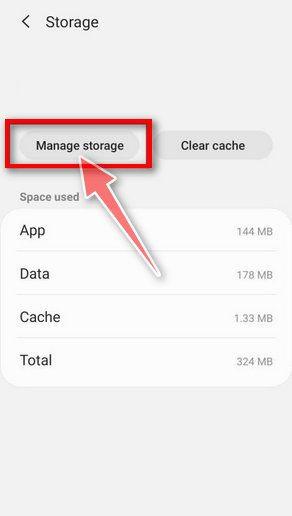
Tap “Manage Space”.
Under the storage settings, you will get two options — Manage Space and Clear Cache. Tap on “Manage Space“.
-
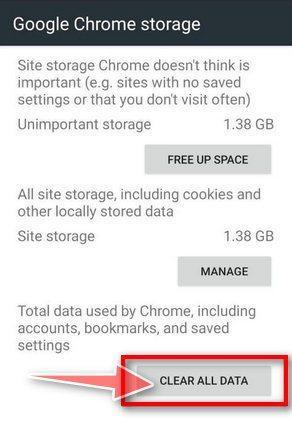
Tap “Clear all data”.
Tap “Clear all data” to delete all Chrome’s data including accounts, bookmarks, and your settings to reset the default settings.
-
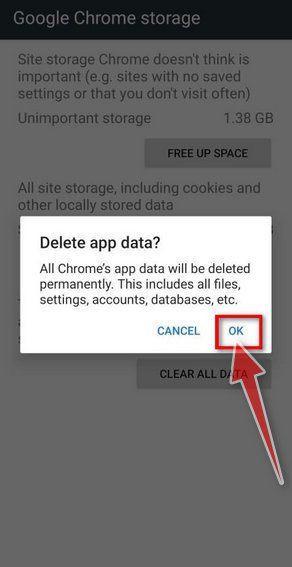
Confirm by tapping “Ok”.
A confirmation dialog should now be displayed, detailing the components that will be restored to their default state should you continue with the reset process. To complete the restoration process, tap “Ok“.
Remove malware from Firefox for Android
To reset Firefox for Android to its default settings, follow the below steps:
-
Open the “Settings” menu.
Tap on the “Settings” app from your phone menu or home screen.
-
Tap on “Apps”.
When the “Settings” menu opens, tap on “Apps” (or “App Manager”) to see all the installed applications on your phone.
-
Find and tap on Firefox.
The “Apps” screen will be displayed with a list of all the apps installed on your phone. Scroll through the list until you find the Firefox app, then tap on it to open the app’s details.
-
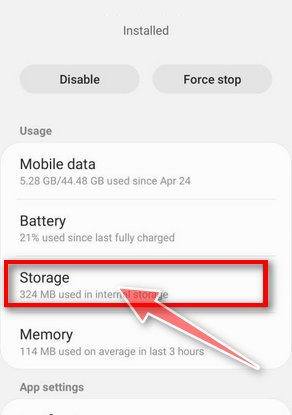
Tap “Storage”.
When Firefox’s app info menu is displayed, tap on “Storage“.
-
Tap “Manage Space”.
Under the storage settings, you will get two options — Manage Space and Clear Cache. Tap on “Manage Space“.
-
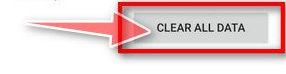
Tap “Clear all data”.
Tap “Clear all data” to delete all Firefox data including accounts, bookmarks, and your settings to reset the default settings.
-
Confirm by tapping “Ok”.
A confirmation dialog should now be displayed, detailing the components that will be restored to their default state should you continue with the reset process. To complete the restoration process, tap “Ok“.
Remove malware from the Opera browser
To reset the Opera browser to its default settings, follow the below steps:
-
Open the “Settings” menu.
Tap on the “Settings” app from your phone menu or home screen.
-
Tap on “Apps”.
When the “Settings” menu opens, tap on “Apps” (or “App Manager”) to see all the installed applications on your phone.
-
Find and tap on Opera.
The “Apps” screen will be displayed with a list of all the apps installed on your phone. Scroll through the list until you find the Opera app, then tap on it to open the app’s details.
-
Tap “Storage”.
When Opera’s app info menu is displayed, tap on “Storage“.
-
Tap “Manage Space”.
Under the storage settings, you will get two options — Manage Space and Clear Cache. Tap on “Manage Space“.
-
Tap “Clear all data”.
Tap “Clear all data” to delete all Opera’s data including accounts, bookmarks, and your settings to reset the default settings.
-
Confirm by tapping “Ok”.
A confirmation dialog should now be displayed, detailing the components that will be restored to their default state should you continue with the reset process. To complete the restoration process, tap “Ok“.
Remove malware from Samsung Internet Browser
To reset the Samsung Internet Browser to its default settings, follow the below steps:
-
Open the “Settings” menu.
Tap on the “Settings” app from your phone menu or home screen.
-
Tap on “Apps”.
When the “Settings” menu opens, tap on “Apps” (or “App Manager”) to see all the installed applications on your phone.
-
Find and tap on Samsung Internet Browser.
The “Apps” screen will be displayed with a list of all the apps installed on your phone. Scroll through the list until you find the Samsung Internet Browser app, then tap on it to open the app’s details.
-
Tap “Storage”.
When the Samsung Internet Browser’s app info menu is displayed, tap on “Storage“.
-
Tap “Manage Space”.
Under the storage settings, you will get two options — Manage Space and Clear Cache. Tap on “Manage Space“.
-
Tap “Clear all data”.
Tap “Clear all data” to delete all Samsung Internet Browser’s data including accounts, bookmarks, and your settings to reset the default settings.
-
Confirm by tapping “Ok”.
A confirmation dialog should now be displayed, detailing the components that will be restored to their default state should you continue with the reset process. To complete the restoration process, tap “Ok“.
Remove malware from Microsoft Edge for Android
To reset the Microsoft Edge for Android to its default settings, follow the below steps:
-
Open the “Settings” menu.
Tap on the “Settings” app from your phone menu or home screen.
-
Tap on “Apps”.
When the “Settings” menu opens, tap on “Apps” (or “App Manager”) to see all the installed applications on your phone.
-
Find and tap on Microsoft Edge.
The “Apps” screen will be displayed with a list of all the apps installed on your phone. Scroll through the list until you find the Microsoft Edge app, then tap on it to open the app’s details.
-
Tap “Storage”.
When the Microsoft Edge’s app info menu is displayed, tap on “Storage“.
-
Tap “Manage Space”.
Under the storage settings, you will get two options — Manage Space and Clear Cache. Tap on “Manage Space“.
-
Tap “Clear all data”.
Tap “Clear all data” to delete all Microsoft Edge’s data including accounts, bookmarks, and your settings to reset the default settings.
-
Confirm by tapping “Ok”.
A confirmation dialog should now be displayed, detailing the components that will be restored to their default state should you continue with the reset process. To complete the restoration process, tap “Ok“.
STEP 3: Use Malwarebytes for Android to remove malicious apps
In this final step, we will install Malwarebytes for Android to scan and remove malicious apps from your phone or tablet.
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android device is now clean. The malicious apps, adware, and browser redirects have been removed.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Remove Unwanted Apps and Malware from iPhone and iPad
STEP 1: Clean your browser
First, we’ll clean Safari using the built-in “Clear History and Website Data” feature. This removes your browsing history, cookies, and cached data — including the stored data that scam sites use to keep showing you pop-ups and redirects. Don’t worry: this won’t delete your photos, apps, or saved passwords.
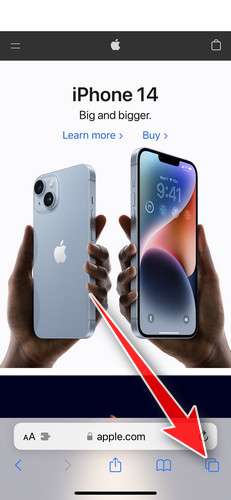
- Don’t tap anything inside the scam page or pop-up — the buttons are designed to trick you. Instead, tap the tabs icon in the lower-right corner of Safari, as shown below.
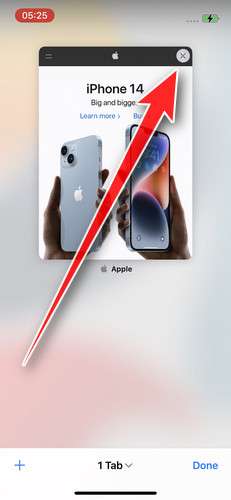
- Tap the X on the malicious tab (or swipe it up) to close it safely.
- Open the Settings app.
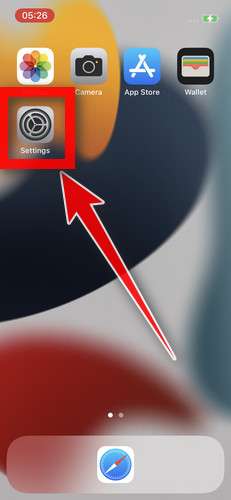
- Turn on Airplane Mode. This temporarily disconnects your iPhone from the internet, so the scam site can’t load anything while we clean up. We’ll turn it back off at the end.
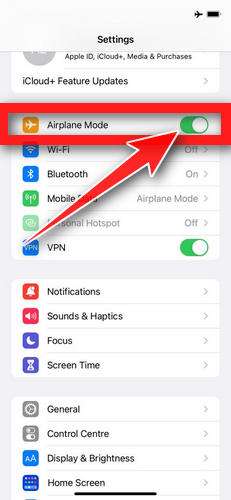
- Scroll down and tap Safari.
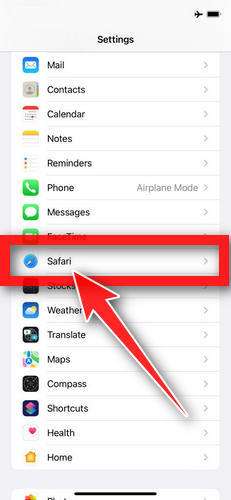
- Tap Clear History and Website Data.
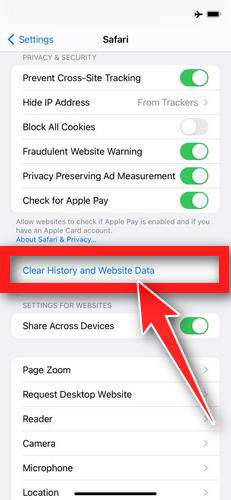
- Confirm by tapping “Clear History and Data” in the pop-up.
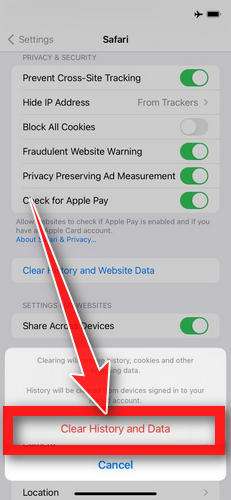
- While you’re still in Safari settings, turn on Block Pop-ups and Fraudulent Website Warning. These two switches stop most scam pages before they can even load.
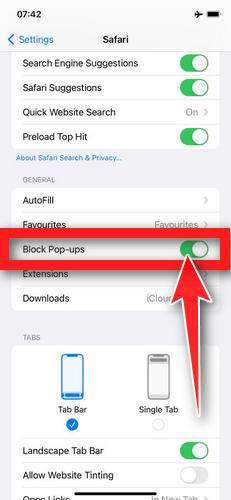
- Tap Settings in the upper-left corner to return to the main Settings menu.
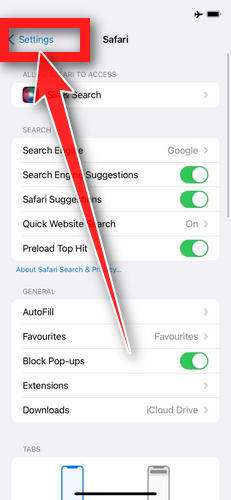
- Turn Airplane Mode back off to reconnect your iPhone to the internet.
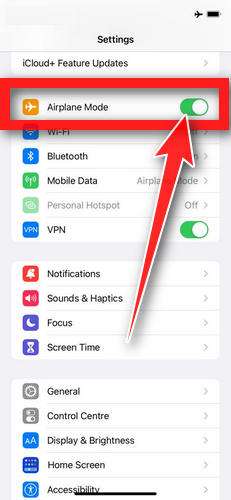
STEP 2: Delete unwanted apps
Next, we’ll remove any suspicious apps from your iPhone. If a shady website redirected you to the App Store and you installed an app — or you spot an app you don’t remember downloading — delete it now:
-
On the home screen, tap and hold the unwanted app’s icon until the icons start to wiggle.
-
Tap the minus (–) badge in the corner of the app icon, then tap Delete App. (On older iOS versions, this badge appears as an “X”.)
-
Confirm by tapping “Delete“.
That’s it — your iPhone is now clean and safe to use.
To stop these scam pages from coming back, we recommend installing an ad blocker like AdGuard. It blocks the malicious ads and redirects that cause these pop-ups in the first place.
Still having issues after completing these steps? Try one of the following:
- Run a scan with Malwarebytes for iOS
- Ask for help in our free Mobile Malware Removal Help & Support forum — our team will assist you personally.
That’s it — your iPhone or iPad is now clean.
The Bottom Line
The “Unverified Apple Pay Usage” text is not a helpful Apple security alert. It is a carefully written tech support scam designed to push you into calling a fake support number. The case ID, the pending $287.99 charge, and the Apple Store location are there to make the threat feel real and urgent.
The danger starts when you call. That is where scammers try to gain control through remote access tools, steal verification codes, take over accounts, and pressure victims into sending money or gift card codes.
If you receive one of these messages, do not call the number. Verify your Apple ID and your payment activity directly through official settings and your bank.
If you already engaged, act quickly but calmly. Remove remote access tools, scan with Malwarebytes, add protection like AdGuard, secure your Apple ID and email, and involve your bank’s fraud team. Step by step, you can shut the scam down, reduce your risk, and make it much harder for them to try again.
FAQ
What is the “Unverified Apple Pay Usage” scam?
It’s a fake Apple security alert sent by scammers through text messages or emails. The message claims your Apple ID triggered a security warning and that a pending Apple Pay charge, like $287.99 at an Apple Store location, was detected. The real goal is to get you to call a fake “Apple Support” phone number so scammers can pressure you into giving up access or sending money.
Is the $287.99 “APPLE STORE, Orlando, FL” charge real?
Usually not. In most cases it’s a made-up number designed to trigger panic. Sometimes scammers reuse real city names and “Apple Store” wording to make it feel authentic. The only safe way to confirm charges is to check your bank or card statement directly, and review Apple purchase history inside your Apple account, not by calling the number in the text.
Why does the message mention “Apple Pay pre-authorization”?
Because it sounds technical and urgent. “Pre-authorization” implies the charge is pending and can still be stopped if you act fast. That creates pressure. Scammers use payment terms people have heard before, but do not fully understand, to make their story feel legitimate.
The message includes a real Apple link to getsupport.apple.com. Does that mean it’s legitimate?
No. Scammers often include real Apple links to make the message look trustworthy. A real link does not validate the phone number or the rest of the message. The scam is the instruction to call the number, not the presence of an official-looking URL.
Will Apple ever text me and tell me to call a phone number “immediately” for Apple ID security?
No. Apple does not handle Apple ID security incidents by sending unsolicited texts that instruct you to call a number provided in the message. If you need help, you should contact Apple through official channels you find yourself, not the contact details in the text.
What happens if I call the number in the scam text?
You reach a fake tech support center. They often claim your Apple ID is being hacked, your Apple Pay is being set up on another device, or your account is “under investigation.” Then they try to keep you on the line while they extract personal information, get you to share verification codes, or convince you to install remote access software.
Why do scammers ask victims to install AnyDesk or remote access tools?
Remote access lets scammers see your screen and guide you through actions that reveal sensitive information. They may try to capture one-time passcodes, email logins, banking logins, or trick you into authorizing transfers. Legitimate Apple support will not ask you to install random remote access tools because of a text message.
What are the biggest red flags that prove it’s a scam?
Common red flags include:
- A demand to call a phone number right away
- Pressure language like “immediately” or “within 24 hours”
- A “case ID” meant to look official
- Claims of unknown Apple Pay setup requests
- Threats that the charge will “proceed” unless you act
- A sign-off like “Apple Security Division”
- Any request for gift cards, crypto, or money transfers
What should I do if I received the text but did not call?
You can ignore it, but it’s smart to do a quick verification on your own terms:
- Check your bank or card app for any real pending charge
- Review Apple purchase history and subscriptions in your account
- Review your Apple ID trusted devices and security settings
Do not call the number and do not reply to the text.
I called, but I didn’t give them anything. Am I still at risk?
If you only called and hung up quickly, your risk is low. But if you shared your Apple ID email, confirmed personal details, or stayed on the line while they “checked your account,” expect more scam attempts. Keep an eye on your accounts and be cautious about follow-up calls pretending to be “senior support.”
What if I shared my Apple ID email, password, or verification codes?
Treat it as an account takeover risk:
- Change your Apple ID password immediately
- Enable or confirm two-factor authentication
- Review and remove unknown trusted devices
- Secure your email account next, because it controls password resets
If you suspect your Apple ID was accessed, consider contacting Apple through official support channels you navigate to yourself.
What if I installed AnyDesk, allowed screen sharing, or let them see my device?
Take immediate steps:
- Uninstall AnyDesk or any remote tool you installed
- Run a full scan with Malwarebytes
- Check for unknown browser extensions or suspicious installed apps
- Change passwords from a clean device, starting with email and Apple ID
- Contact your bank if you opened banking apps while they were watching
Why do these scams often end with gift card requests?
Because gift cards are fast, irreversible, and easy to resell. No legitimate company uses gift cards to “verify” identity, “secure” an account, or “process a refund.” If the conversation turns to gift cards, it is 100% a scam.
Can I get my money back if I sent gift card codes or made a transfer?
It depends on speed and the payment method. If you used gift cards, contact the gift card issuer immediately and keep your receipts. If you made a bank transfer, call your bank’s fraud department right away and ask if it can be stopped or recalled. Even if recovery is uncertain, reporting quickly improves your chances.
Should I use Malwarebytes and AdGuard after this scam?
Yes, especially if you installed anything, clicked unknown links, or allowed remote access.
- Malwarebytes helps detect and remove malware and unwanted programs.
- AdGuard helps block malicious ads, scam sites, and redirect pages that often lead to these alerts.
How can I verify whether Apple Pay is actually being used on my account?
Use official, direct checks:
- Review your card transactions in your bank app
- Check your Apple ID security settings for trusted devices
- Review Apple purchase history and subscriptions inside your account
If anything looks suspicious, contact your bank using the number on the back of your card, and contact Apple through official channels you find independently.
How do I report the “Unverified Apple Pay Usage” scam text?
You can:
- Mark it as spam or junk in your messaging app
- Block the sender
- Report the phone number to your carrier or local consumer protection channels
If you lost money, also file a fraud report with your bank and document the messages and call details.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.