

A new and deeply troubling extortion scam has emerged through spam emails, where scammers claim to have infected devices with Cobalt Strike malware called “Beacon” and obtained private videos and data. The email threatens to leak this information publicly unless a ransom is paid in bitcoin.
Known as the Cobalt Strike Beacon email scam, this scheme aims to trick victims by sounding technically legitimate. However, the threats are entirely fabricated with the goal of extorting money through fear. This article will provide an in-depth analysis of how this scam works, red flags to watch for, and recommended actions if you receive this scam.
Overview of the Cobalt Strike Beacon Email Scam
The Cobalt Strike Beacon email scam claims to have infected devices with real malware and obtained private videos and data. Here are the key components that make up this scam:
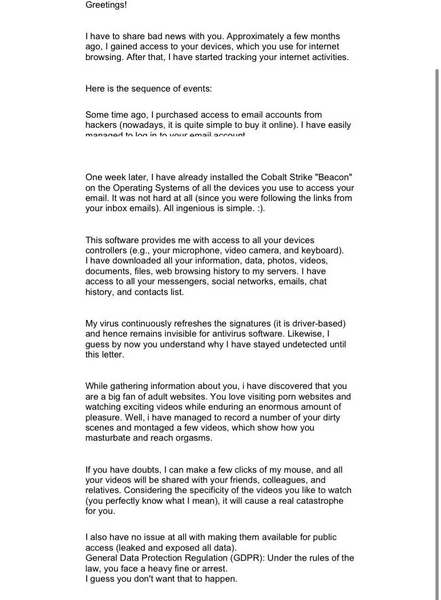
Here is how the Cobalt Strike Beacon email scam usually reads:
Greetings!
I have to share bad news with you. Approximately a few months ago, I gained access to your devices, which you use for internet browsing. After that, I have started tracking your internet activities.
Here is the sequence of events:
Some time ago, I purchased access to email accounts from hackers (nowadays, it is quite simple to buy it online). I have easily managed to log in to your email account
One week later, I have already installed the Cobalt Strike “Beacon” on the Operating Systems of all the devices you use to access your email. It was not hard at all (since you were following the links from your inbox emails). All ingenious is simple. :).
This software provides me with access to all your devices controllers (e.g., your microphone, video camera, and keyboard).
I have downloaded all your information, data, photos, videos, documents, files, web browsing history to my servers. I have access to all your messengers, social networks, emails, chat history, and contacts list.My virus continuously refreshes the signatures (it is driver-based) and hence remains invisible for antivirus software. Likewise, I guess by now you understand why I have stayed undetected until this letter.
While gathering information about you, i have discovered that you are a big fan of adult websites. You love visiting porn websites and watching exciting videos while enduring an enormous amount of pleasure. Well, i have managed to record a number of your dirty scenes and montaged a few videos, which show how you **** and reach orgasms.
If you have doubts, I can make a few clicks of my mouse, and all your videos will be shared with your friends, colleagues, and relatives. Considering the specificity of the videos you like to watch (you perfectly know what I mean), it will cause a real catastrophe for you.
I also have no issue at all with making them available for public access (leaked and exposed all data).
General Data Protection Regulation (GDPR): Under the rules of the law, you face a heavy fine or arrest.
I guess you don’t want that to happen.Let’s settle it this way:
You transfer 2.4 Bitcoin to me and once the transfer is received, I will delete all this dirty stuff right away. After that, we will forget about each other. I also promise to deactivate and delete all the harmful software from your devices. Trust me. I keep my word.
That is a fair deal, and the price is relatively low, considering that I have been checking out your profile and traffic for some time by now. If you don’t know how to purchase and transfer Bitcoin – you can use any modern search engine.
You need to send that amount here Bitcoin wallet:
bc1qh5aex028jj339vdjkj5u3k37a72rkr33kqkars(The price is not negotiable).
You have 5 days in order to make the payment from the moment you opened this email.Do not try to find and destroy my virus! (All your data is already uploaded to a remote server).
Do not try to contact me. Various security services will not help you; formatting a disk or destroying a device will not help either, since your data is already on a remote server.This is an APT Hacking Group. Don’t be mad at me, everyone has their own work.
I will monitor your every move until I get paid.
If you keep your end of the agreement, you won’t hear from me ever again.Everything will be done fairly!
One more thing. Don’t get caught in similar kinds of situations anymore in the future!
My advice: keep changing all your passwords frequently.
Let’s break down this email scam:
1. Use of Real Cybersecurity Terms
The email establishes credibility by mentioning “Cobalt Strike” and “Beacon”, which are real forms of malware. This makes the message sound legitimate.
2. Claim of Total Device Compromise
The message asserts that this fictional malware allows complete access to all your devices, files, accounts, webcam, microphone, and more. This sets an eerie tone.
3. Threats to Leak Intimate Videos
The email states compromising videos were recorded of you in intimate situations. It threatens to share these videos publicly to all your contacts.
4. Demands Untraceable Ransom Payment
The sender demands ransom payment in bitcoin within a short timeframe, based on its anonymous nature. Failing to comply supposedly triggers video leaks.
5. Applies Pressure Tactics
The email warns that the sender can monitor all your activity, creating a sense of powerlessness and inability to seek help.
By manipulating fear and technical terms, the scam email aims to obtain ransom funds. But analyzing its methods allows one to discern the deception.
How the Cobalt Strike Beacon Email Scam Works
The Cobalt Strike Beacon scam email utilizes various sophisticated social engineering and pressure tactics to manipulate and deceive victims. Here is how it operates, step-by-step:
- The email will have an alarming or urgent subject line designed specifically to entice opening and reading. Examples include “URGENT: Your Account Security Compromised” or “ACTION REQUIRED: Unauthorized Access Detected.”
- The opening line aims to immediately establish a threatening tone, often stating “I have gained full access to your devices” or “I have been secretly monitoring your activities.” This sparks a sense of fear and vulnerability right away.
- The email cites real cybersecurity terms like “Cobalt Strike” and “Beacon malware” to sound far more technically sophisticated and legitimate. Most recipients are unlikely to be familiar with these specific terms.
- The message asserts total compromise and control over all your connected devices, files, accounts, webcams, microphones, and more. This aims to project complete infiltration of your digital life.
- One of the centerpieces of the scam is claiming to have recorded you in compromising adult situations through remote access to your webcam. This inspires immense feelings of fear, shame, and embarrassment.
- The email threatens to leak these fabricated intimate videos by sharing them with all your contacts including friends, family, colleagues, etc. This weaponizes the fear of public humiliation to coerce compliance.
- Payment of an untraceable ransom in bitcoin is demanded within a short, pressing timeframe while warning of dire consequences for non-compliance. This applies urgency.
- The message disallows contacting authorities for assistance and claims removal of data will be impossible after the deadline has passed. This pressures victims against seeking external help.
- The email is sent from your own compromised email account to establish credibility and make the supposed hacking seem real. But this tactic can be mimicked.
- Ongoing monitoring of the email account is mentioned to spark a sense of powerlessness in victims, as if the scammer will know if attempts are made to seek help or advice regarding the threats.
By thoroughly examining each psychological trigger and technical deception method used in the scam email, we can discern how it overrides critical thinking with urgency and emotional manipulation. But awareness of these precise tactics is key to logically rejecting the threats.
How to Spot This Scam Email
Here are some tips to identify and avoid the Cobalt Strike Beacon extortion scam email:
- Watch for urgent subject lines about account or security compromises to grab attention.
- Be suspicious of claims that your device was hacked and activities monitored.
- Look for specific terms like “Cobalt Strike” and “Beacon malware” used in a threatening context. These are real cybersecurity tools.
- Question claims that your entire digital life was infiltrated and controlled via malware.
- Watch for threats to leak fabricated adult videos of you from your webcam.
- Be wary of demands for quick untraceable ransom payment in bitcoin.
- Note warnings not to contact authorities or claims that data removal will be impossible. These discourage seeking help.
- Consider whether the message could have been spoofed and sent from your own email.
- Spot check for poor grammar, spelling errors and urgent tones revealing non-native English speakers.
- Verify alarming claims by contacting supposed senders through known legitimate channels rather than replying.
- Check the email address as scams often come from unfamiliar or randomized accounts.
- Educate yourself on the latest malware and sextortion scam tactics to recognize patterns.
- Ensure your devices have updated antivirus software and malware protection.
With vigilance, caution and awareness, you can identify key indicators in unsolicited emails that may signal extortion scams and prevent compromise.
What to Do If You Receive This Scam Email
If the alarming Cobalt Strike malware email arrives in your inbox, stay calm and take the following steps:
1. Ignore Ransom Payment Demands
No matter how threatening the email may seem, never pay the ransom amount. The scammers do not actually have compromising videos.
2. Scan Devices for Malware
Run antivirus scans on your devices to check for malware, just as a precaution. Use trusted software from leading cybersecurity firms.
3. Change All Account Passwords
Reset passwords on your email, banking, and other online accounts in case of a breach. Enable two-factor authentication as well.
4. Watch for Suspicious Activity
Carefully monitor financial statements and online accounts over the next few weeks for any unauthorized access attempts.
5. Alert Contacts About Scam
Kindly warn your friends and family about this scam email in case they also receive it. This prevents the scam spreading further.
6. Report Email as Phishing
Report the scam email to your email provider as phishing so they can block the source. Delete the message also.
7. Learn How to Identify Similar Scams
Research other tech support and sextortion scams to recognize the same manipulation tactics in the future.
Rest assured, this scam email does not actually have compromising information about you. Ignore the empty threats and educate yourself on cyber extortion schemes.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
What is the Cobalt Strike Beacon email extortion scam?
This scam sends emails claiming to have infected your device with Cobalt Strike “Beacon” malware that recorded embarrassing videos of you. The email threatens to leak the videos publicly unless a ransom is paid.
What are Cobalt Strike and Beacon malware?
Cobalt Strike and Beacon are real malware, often used by cybercriminals. But the claims of infecting you are fabricated in this scam.
Can the scammers actually leak videos of me?
No, the scammers do not actually have any private videos of you. The threats are completely fabricated to manipulate victims into paying.
Should I pay the ransom amount demanded?
No, you should never pay the ransom demand. The threats are fake and you will lose your money in this scam.
Why do they want payment in bitcoin?
Bitcoin offers anonymity to scammers, making it impossible for victims to trace them. It also attracts less scrutiny for money laundering.
What precautions should I take after getting this email?
Scan devices for malware, reset account passwords, monitor financial statements, report the email as phishing, and learn to identify similar scams.
Can I track down the scammers behind this email?
It’s very difficult to trace cyber extortion scammers since they mask their digital footprints. But you can report them to the FBI’s Internet Crime Complaint Center.
How can I spot similar scam emails in future?
Look for emails demanding quick anonymous payment, threats of leaking fabricated videos, and warnings not to tell others.
Who should I contact if I have other concerns?
Reach out to your email provider or local law enforcement if you have additional questions. The FBI’s IC3 also accepts scam reports.
The Bottom Line
The Cobalt Strike Beacon email scam uses real cybersecurity terms and threats of leaking videos to try extorting money through fear. But a closer look reveals sheer manipulation.
Stay alert for emails demanding quick anonymous payment in bitcoin to keep fabricated videos private. Report them as phishing, but never respond or open attachments. Through education, we can logically reject cyber extortion scams rather than reacting emotionally.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.