


Scammers are aggressively using the Evri name to send phishing text messages and emails aimed at stealing personal and financial information from unsuspecting victims. These sophisticated scams convince recipients to share confidential details under the guise of a missed parcel delivery or other shipping-related issue that requires urgent attention.
This in-depth article will uncover how the Evri scams operate, red flags to watch for, and most critically, how to protect yourself from being deceived.
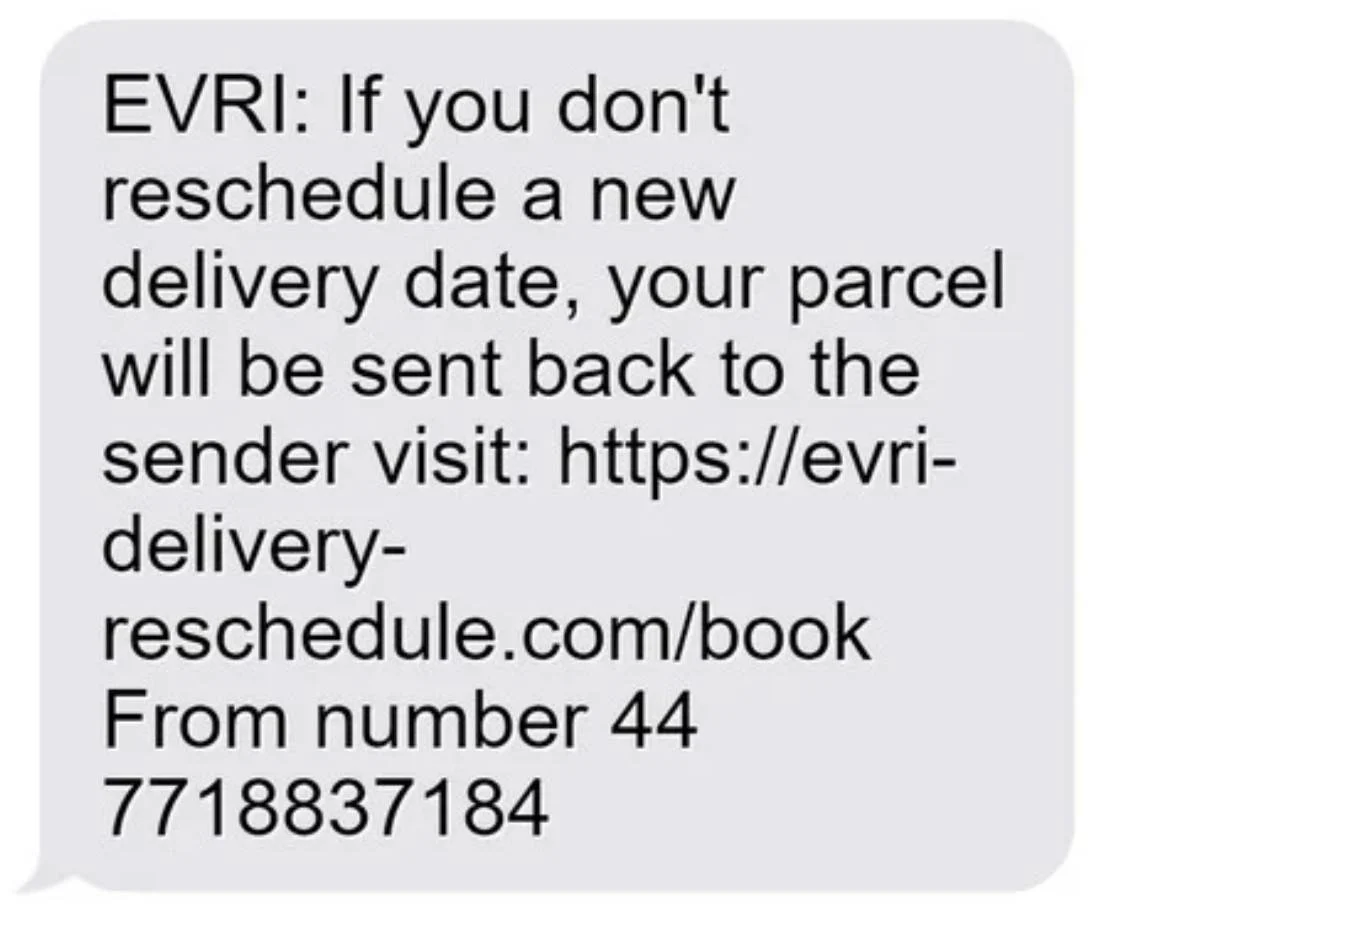
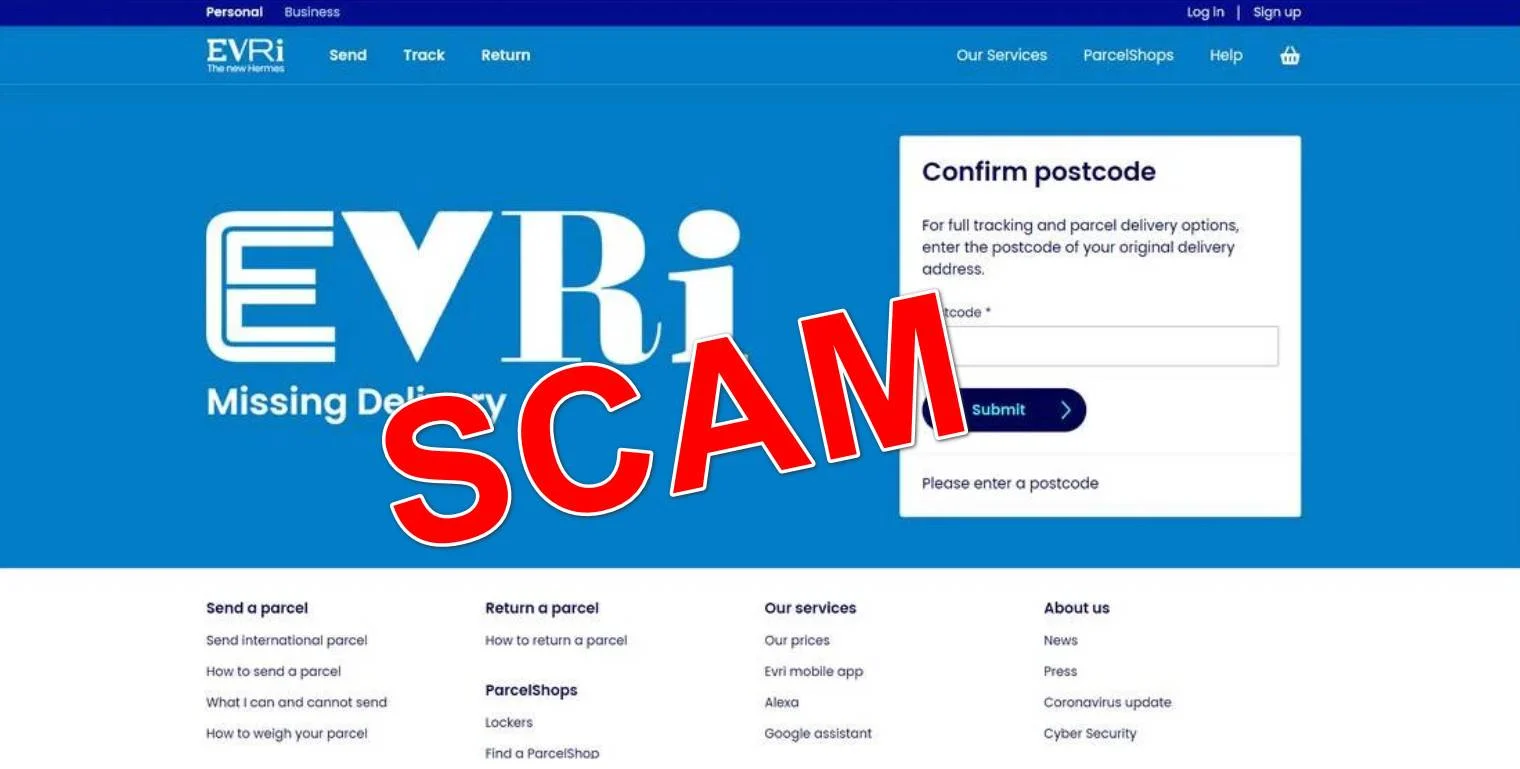
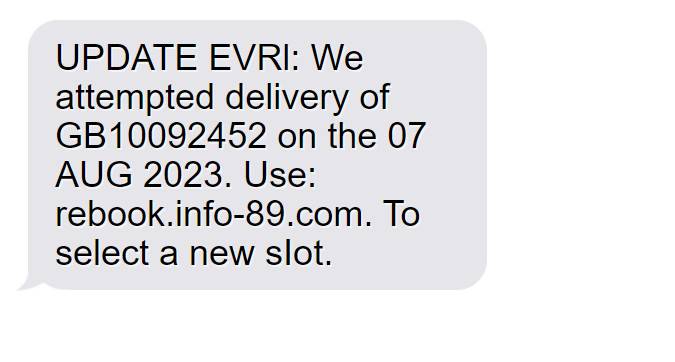
Overview of the Evri Scam
This scam involves fraudulent text messages or emails that appear to come from Evri about issues with a package delivery or customs fees. The messages mimic Evri branding and messaging style.
Some variant of the following shipping-related issues are typically cited:
- A parcel is stuck in customs and fees must be paid
- There is a pending delivery you must confirm
- Your package delivery address needs to be validated
- Your shipment has shipping issues that require payment
No matter the story, the scammers posing as Evri then provide a phone number to call or link to click so the problem can supposedly be resolved. Their ultimate aim is to steal financial and personal information or infect devices with malware.
This scam surged during the pandemic as more people shopped online and anxiously awaited courier deliveries. Victims expect parcels and don’t suspect notifications from Evri are fraudulent.
The sophistication varies. Some scams have typos and inconsistencies, while others can appear very credible, replicating official Evri fonts, colors and logos. Evri has posted warnings on its website about the scams.
Key things to know about the scam:
- Uses real Evri branding – The texts and emails looks like authentic Evri communications. This fools many people.
- Pressures urgent action – Messages often say immediate payment is required or penalties will be incurred. This rushes victims into clicking without thinking.
- Directs victims to fake sites – The links and numbers go to convincing sham Evri pages where users enter personal or financial data.
- May include parcel numbers – Fake parcel IDs and details make the scam more believable and personalized.
- Originates from burner phones/accounts – Texts come from constantly changing cell numbers and disposable accounts are used for emails.
- Seeks sensitive information – Whether through fake sites or calls, the scammers want personal info, bank logins, credit card details, etc.
- Preys on parcel anticipation – People expecting a delivery are more likely to fall for notifications about shipping problems from the courier.
This scam has infiltrated many regions as more citizens fall victim. But awareness of how to spot fraudulent Evri communications will curb deception.
How the Evri Scam Works
Evri scammers operate through text messages or emails. Here are the step-by-step details on how both versions of the scam unfold:
Evri SMS Scam
- A text message is sent from a phone number disguised as an official notice from Evri. The number changes regularly to avoid blocking.
- The message claims there is an urgent issue with a package delivery using Evri branding and messaging. Common reasons given are customs fees owed or address confirmation needed.
- A link is embedded in the text to supposedly address the delivery problem. The link goes to a fake website impersonating the real Evri site.
- On the phony site, victims are instructed to enter personal information like name, address, ID number, phone, etc. to confirm delivery details. In other cases, financial account info is sought.
- The scammers now possess the victim’s sensitive data, either using it directly for identity theft or selling it online. If bank details are given, accounts can be drained.
- With the confidential information acquired, the criminals disappear. The temporary number and website leave virtually no trail. The victim’s data is now in the hands of scammers.
Evri Email Scam
- An email is sent to recipients spoofing the legitimate email and website of Evri. The “From” address mimics Evri but goes to the scammer.
- The email claims the recipient has a pending delivery, but there is a problem needing urgent action. Customs charges, address confirmation, redelivery fees, and shipping issues are commonly cited.
- A link within the email leads to a fake Evri website seeking personal information when entered by victims. In other cases, it may download malware onto the user’s device.
- The scam email prompts entry of bank account data, credit card numbers, photo ID, etc. to pay fictional fees – allowing immediate account access.
- Along with potential bank theft and malware installation, the scammers obtain personal data like name, phone, ID numbers, address, etc. to facilitate identity fraud.
- As with the text scam, the criminals have now acquired sensitive user details through the sham emails and sites. The disposable accounts used make the scammers difficult to trace.
Red Flags of the Scam:
- Spelling and grammar mistakes
- Threatening urgent calls to action
- Requests for financial account information
- Links to odd URLs or domain names
- Requests to download software
- Phone numbers from outside your region
- Lack of specific user and shipment details
Here is a detailed section on how to spot Evri delivery text message scams using examples:
How to Identify Evri Text Message Scams
Evri scammers use text messages to fool victims about delivery issues. Here are tips to spot fraudulent texts with examples:
Analyze the Sender’s Number
- Evri’s official short code is 73757. Other numbers are likely scams.
- Example: “Parcel issue, call 01234555 immediately or fees applied. Click: [OddLink]”
Inspect Links Thoroughly
- Hover over links to preview the URL without clicking. Fake sites have odd links.
- Example: “Urgent – address confirmation needed for your Evri parcel today: [ShadyLink].”
Watch for Threatening Messages
- Evri won’t threaten you over text. Scare tactics about fees/penalties are red flags.
- Example: “Failed delivery yesterday – redelivery fee must be paid in 30 minutes or further £50 penalties charged.”
Verify Unexpected Requests
- Pause if a text out of nowhere asks for sensitive information or payment. Verify first.
- Example: “Please confirm your Evri account details now to schedule redelivery: [SketchyLink]”
Check for Missing Details
- No parcel number, order references or your address suggests a scam.
- Example: “You have a pending Evri delivery. Provide your address and credit card details now: [FishyLink]”
Trust your instincts if a text seems suspicious. Verify directly with Evri before clicking links or providing information.
How to Spot Evri Delivery Scam Emails
Evri imposters also use fraudulent emails to target victims. Here are tips to recognize scam emails with examples:
Examine the Sender’s Email Address
- Emails from odd addresses pretending to be Evri are scams.
- Example: Sender “EvriSupport@evrim4il.com” – typo is a red flag.
Analyze the Links in Emails
- Hover over hyperlinks to preview the actual destination URL without clicking.
- Example: “Click here to pay redelivery fee” points to shady “evrilogisticss.com”
Watch for Spelling/Grammar Errors
- Poor writing suggests an amateur scammer, not a real Evri email.
- Example: “Parcel attempt failed. Must pay outstanding balence immediately.”
Verify Threats of Fees or Penalties
- Evri won’t threaten penalties in emails. These urgent claims aim to pressure victims.
- Example: “You must pay £75 customs fee in 1 hr or delivery will be canceled and further fines applied.”
Check for Lack of Details
- No order number, tracking ID or your address is suspicious.
- Example: “Your Evri parcel awaits delivery. Please click link to update information.”
Go slowly and use scrutiny before clicking email links or attachments. When in doubt, contact Evri directly to verify legitimacy first.
What to Do if You Have Fallen Victim to the Scam
If you suspect you have been targeted or already fallen victim to an Evri text or email scam, take these recommended steps:
1. Contact your bank and credit card issuer.
If any financial information was shared, immediately contact your bank and card issuer. They can freeze accounts and block fraudulent charges. The quicker you notify them, the better.
2. Change any compromised passwords.
If you entered login credentials on fake sites or downloaded malware, rapidly change passwords for your email, bank accounts, social media, and other critical accounts. Enable two-factor authentication if possible.
3. Scan devices for malware.
Use quality antivirus software like Malwarebytes to scan all involved devices for viruses and malware. Remove any infections detected.
4. Place fraud alert on your credit.
Contact credit bureaus to declare fraud alerts for your file. This flags any new activity for review, making it harder for scammers to open accounts in your name.
5. Monitor accounts and credit reports.
Watch bank statements, credit reports, and online logins closely for signs of misuse of your information in the months following the scam targeting you. Proactive monitoring helps.
6. Report the scam.
Alert Evri about both scam texts and emails by filing a complaint on their website. Also report SMS scams directly to your mobile operator.
7. Document details as evidence.
Retain records like screenshots of scam texts, emails, and sites as proof for claims and investigations. Note relevant dates, phone numbers, messages, losses, etc.
8. Wipe devices completely if severe infection.
For serious malware attacks, fully reset infected devices to factory default settings. This cleans out embedded malware. Reinstall apps afterwards.
9. Seek further help if identity theft occurs.
If scammers misuse your stolen data, file an identity theft report and contact agencies like the Identity Theft Resource Center for extended fraud resolution guidance.
Falling prey to the Evri scam can create substantial personal and financial troubles. But taking quick and thorough actions can help curb damages and prevent further negative impacts going forward.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions About Evri Scams
What are Evri scams?
They are fake text messages and emails sent by scammers impersonating Evri delivery company. They claim issues with deliveries to trick people into providing personal and financial information.
How do I recognize Evri scams?
Watch for odd links, urgent threats, spelling/grammar errors, requests for sensitive data, non-Evri numbers, missing order details, and other red flags. Verify any suspicions directly with Evri.
What do the scammers want?
Their aim is to steal identities, drain bank accounts, and install malware using the fraudulent shipping communications. Posing as Evri lets them elicit sensitive data.
What should I do if I get a suspicious message?
Do not click links, provide information, make payments, or call numbers provided. Report scam emails to Evri and text scams to 7726.
What if I already provided information or clicked a link?
Quickly contact your bank, scan devices for malware, enable two-factor authentication on accounts, place fraud alerts with credit bureaus, monitor your credit, and report the scam.
How can I avoid Evri scams?
Analyze messages closely, look for red flags, contact Evri to verify concerns, avoid opening attachments/links, and never provide personal or financial data to unconfirmed sources.
How common are these scams?
These scams have surged along with e-commerce and delivery volumes. Scammers increasingly pretend to be Evri hoping victims anxiously await parcels.
Who is responsible for these scams?
Individual scammers and organized cybercrime rings in the UK and abroad run these cons. They are difficult to trace as they use burner phones and fake accounts.
What risks do I face if I provide my information?
Identity theft, bank account draining, credit damage, and device malware infections. Scammers exploit leaked personal and financial data.
Can Evri help if I’m scammed?
Unfortunately Evri is not liable, but can provide information to authorities to aid investigations. You must file claims and reports regarding any losses from scams.
How can I protect myself from these scams?
Be vigilant inspecting parcel communications, contact Evri to verify odd requests, avoid opening attachments/links, and never provide personal or financial information to unconfirmed sources.
The Bottom Line
Scam texts and emails impersonating Evri are a growing threat that citizens should be vigilant against. These fraudulent shipping notifications are designed to harvest users’ personal details and money.
By learning the scam tactics, recognizing warning signs, and acting fast if targeted, individuals can protect themselves from the havoc of identity theft and bank account draining. The insights provided here offer the awareness needed to avoid becoming another victim of these parcel delivery and customs scams.
Stay alert for questionable digital communications claiming to be from Evri. Verify any delivery issues directly with them. Follow prudent cyber security habits regarding links, downloads, and providing sensitive information to unconfirmed sources. With proper scam awareness, these frauds can be contained. But it requires an informed public that examines messages critically and understands this threat. Use the knowledge in this article to identify and evade Evri scams.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.