

Apple has released emergency security updates to address two zero-day vulnerabilities that were being actively exploited by NSO Group’s Pegasus spyware to hack into fully updated iPhones.
Pegasus Used BLASTPASS Exploit Chain to Deploy Spyware
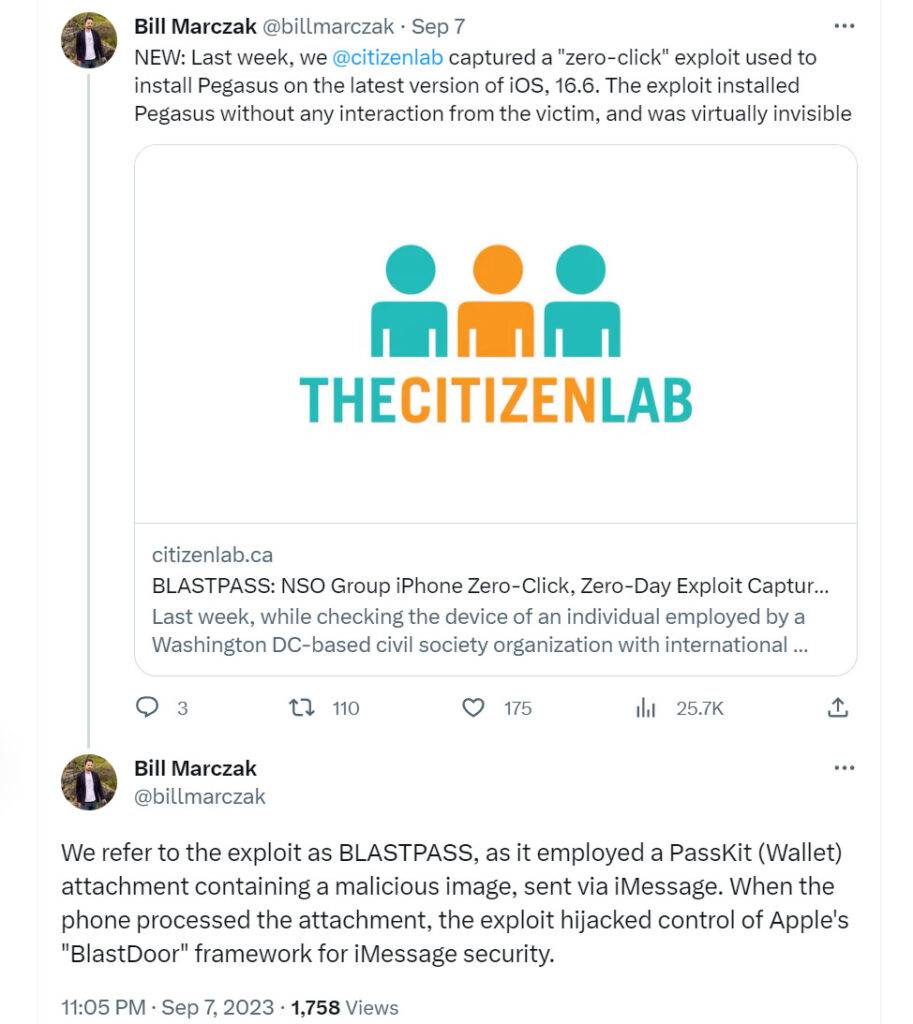
According to research by Citizen Lab, the two vulnerabilities – CVE-2023-41064 and CVE-2023-41061 – were exploited via a zero-click attack chain dubbed BLASTPASS to deploy Pegasus onto iPhones running latest iOS 16.6.
The exploit chain involved sending malicious PassKit attachments containing weaponized image files to victims through iMessage. Once opened, the images triggered the vulnerabilities enabling remote code execution and installation of the Pegasus malware without any user interaction.
Zero-Days Allowed Complete iPhone Takeover
Both the flaws resided in core iPhone components – Image I/O and Wallet frameworks. CVE-2023-41064 was a buffer overflow triggered during processing of specially crafted images. CVE-2023-41061 stemmed from a validation issue that could be leveraged using malicious attachments.
Together, the vulnerabilities gave attackers full control over targeted devices to extract sensitive data including messages, emails, photos and location history.
Update iPhones, iPads and Macs Immediately
Apple has addressed the zero-days in iOS 16.6.1, iPadOS 16.6.1, macOS Ventura 13.5.2, and watchOS 9.6.2 by improving memory handling and input validation.
Users are strongly advised to install the latest updates on all iPhones, iPads, Macs and Apple Watch models urgently. Those at high risk of spyware attacks should enable Lockdown Mode for additional protection.
Pegasus Devastating for Journalists, Activists and Dissidents
Pegasus is marketed by NSO Group as a tool for government surveillance of criminals and terrorists. However, it has been consistently misused to hack journalists, human rights activists, lawyers, diplomats and dissidents worldwide.
The spyware infects both iPhones and Android devices, enabling unfettered access to messages, emails, calls, photos, location data and even microphone and camera control.
Multiple Zero-Days Used in Targeted iPhone Attacks This Year
Apple has patched 13 zero-days so far in 2023, with many being actively exploited in the wild to compromise up-to-date iPhones and Macs:
- July – CVE-2023-37450 and CVE-2023-38606
- June – CVE-2023-32434, CVE-2023-32435, CVE-2023-32439
- May – CVE-2023-32409, CVE-2023-28204, CVE-2023-32373
- April – CVE-2023-28206, CVE-2023-28205
- February – CVE-2023-23529
The growing number of in-the-wild iPhone exploits highlights the need for rapid patching and vigilance, especially for high-risk users.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.