


Trojan:BAT/Bancos.B is a family of trojans that is created/generated by kits known as “Zeus”; these kits are bought and sold on the cyberworld black market.
Trojan:BAT/Bancos.B was created to steal data from victim’s system, such as account login names and passwords, online banking passwords and other sensitive data, then relays the captured information to the attacker. Most Win32/Bancos variants target customers of Brazilian banks, though some variants target customers of banks in other locations.
Trojan:BAT/Bancos.B spreads mostly via email but can also utilize auto run capabilities of removable media, or install via a drive-by infection when the user visits a compromised or malicious webpage. Once the infected binary file is installed to a machine it connects to a command and control server, and also monitors for internet activity and uploads stolen data.
Some variants of the Trojan:BAT/Bancos.B will monitor open Web-browser windows looking for bank names in the title bar or bank URLs in the address bar. The Trojans may also log keystrokes to record credentials that a user enters at banking Web sites. To assist in capturing banking credentials, Trojan:BAT/Bancos.B may also replace or supplement legitimate bank Web pages with fake Web pages disguised to look like the original.
Trojan:BAT/Bancos.B send the captured banking credentials to the attacker by e-mail, or uploading to an attacker’s FTP site, or posting the stolen credentials to a web site.
Trojan:BAT/Bancos.B may copy itself to various folders on the infected computer, such as the %windir% or , and also drop other files there. The Trojan executable file name may contain the string ‘cartao’, which is Portuguese for the English word ‘card’. Some variants of Trojan:BAT/Bancos.B may also configure itself to run automatically each time Windows starts, for example by creating entries in registry keys such as HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run , and may also try to disable security-related software such as antivirus and firewall software
Most antivirus products can detect this threat as :
BAT/Disabler.E.dropper (AVG)
TR/Proxy.Banker.O.33 (Avira)
BAT/Spy.Banker.AB trojan (ESET)
Trojan.BAT.DNSChanger.b (Kaspersky)
PWS-Banker!hdv (McAfee)
Troj/DNSChan-NG (Sophos)
TROJ_SPNR.03G312 (Trend Micro)
STEP 1: Remove Trojan:BAT/Bancos.B infection with Kaspersky TDSSKiller
As part of its self defense mechanism, Trojan:BAT/Bancos.B will install a rootkit on the infected computer.In this first step, we will run a system scan with Kaspersky TDSSKiller to remove this rookit.
- Please download the latest official version of Kaspersky TDSSKiller.
Download TDSSKillerYour download starts right away. - Before you can run Kaspersky TDSSKiller, you first need to rename it so that
you can get it to run. To do this, right-click on the TDSSKiller.exe icon and select Rename.
Edit the name of the file from TDSSKiller.exe to iexplore.exe, and then double-click on it to launch. - Kaspersky TDSSKiller will now start and display the welcome screen and we will need to click on Change Parameters.
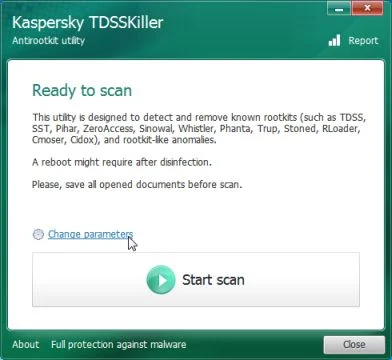
- In the new open window,we will need to enable Detect TDLFS file system, then click on OK.
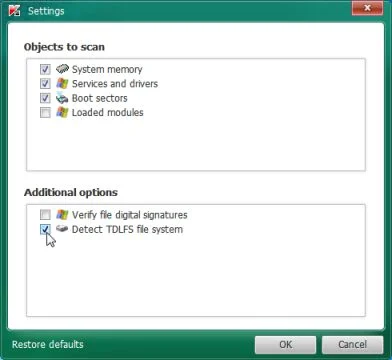
- Next,we will need to start a scan with Kaspersky, so you’ll need to press the Start Scan button.
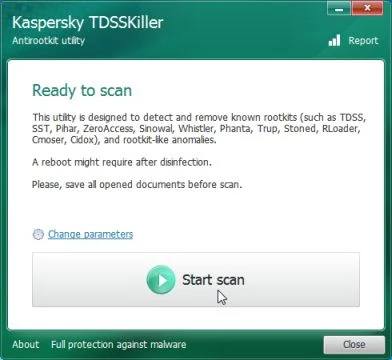
- Kaspersky TDSSKiller will now scan your computer for Trojan:BAT/Bancos.B infection.
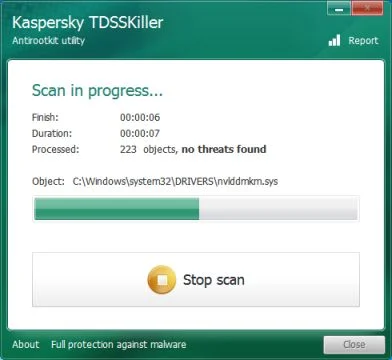
- When the scan has finished it will display a result screen stating whether or not the infection was found on your computer. If it was found it will display a screen similar to the one below.
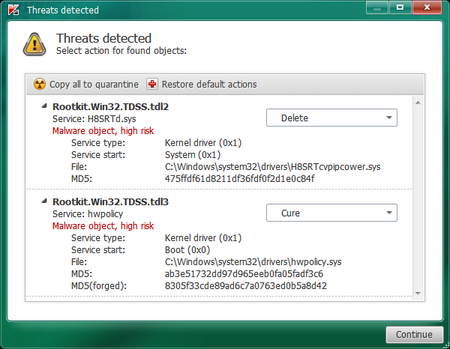
- To remove the infection simply click on the Continue button and TDSSKiller will attempt to clean the infection.A reboot will be require to completely remove any infection from your system.
STEP 2: Remove Trojan:BAT/Bancos.B malicious files with Malwarebytes Anti-Malware
Malwarebytes Chameleon technologies will allow us to install and run a Malwarebytes Anti-Malware scan without being blocked by Trojan:BAT/Bancos.B.
- Download Malwarebytes Chameleon from the below link and extract it to a folder in a convenient location.
Download Malwarebytes ChameleonOpens the download page in a new tab. - Make certain that your infected computer is connected to the internet and then open the Malwarebytes Chameleon folder and double-click on svchost.exe.

IF Malwarebytes Chameleon will not open, double-click on the other renamed files until you find one will work, which will be indicated by a black DOS/command prompt window. - Follow the onscreen instructions to press a key to continue and Chameleon will proceed to download and install Malwarebytes Anti-Malware for you.
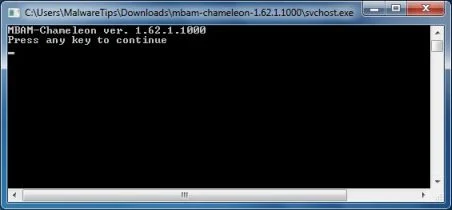
- Once it has done this, it will update Malwarebytes Anti-Malware, and you’ll need to click OK when it says that the database was updated successfully.
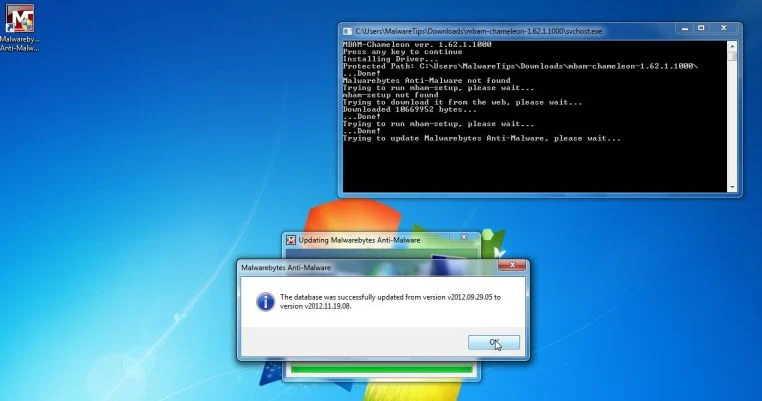
- Malwarebytes Anti-Malware will now attempt to kill all the malicious process associated with Trojan:BAT/Bancos.B.Please be aware that this process can take up to 10 minutes, so please be patient.
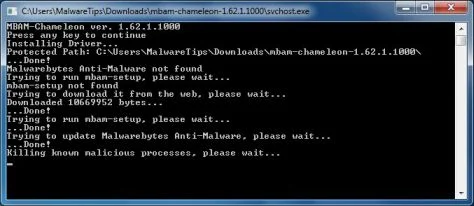
- Next, Malwarebytes Anti-Malware will automatically open and perform a Quick scan for Trojan:BAT/Bancos.B malicious files as shown below.
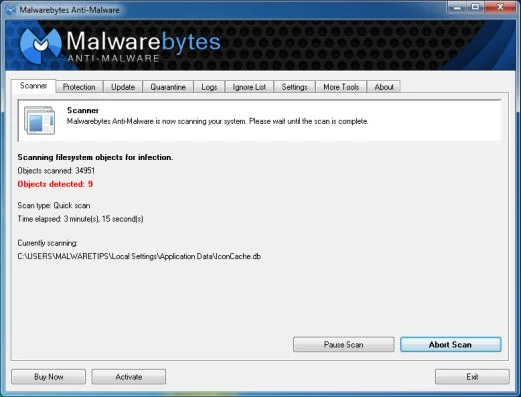
- Upon completion of the scan, click on Show Result
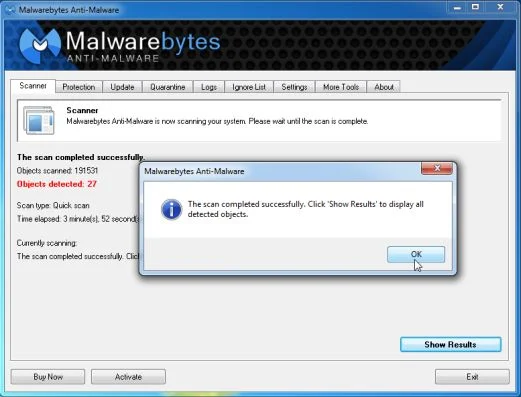
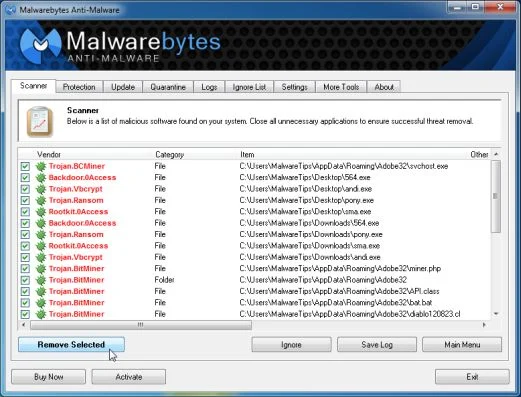
- You will now be presented with a screen showing you the malware infections that Malwarebytes Anti-Malware has detected.
Make sure that everything is Checked (ticked),then click on the Remove Selected button.
- After your computer restarts, open Malwarebytes Anti-Malware and perform a Full System scan to verify that there are no remaining threats

STEP 3 : Remove the malicious registry keys added by the Trojan:BAT/Bancos.B
Trojan:BAT/Bancos.B has added some malicious registry keys to your Windows installation,to remove them we will need to perform a scan with RogueKiller.
- You can download RogueKiller from the below link.
Download RogueKillerOpens the download page in a new tab. - Double click on RogueKiller.exe to start this utility and then wait for the Prescan to complete.This should take only a few seconds and then you can click the Start button to perform a system scan.
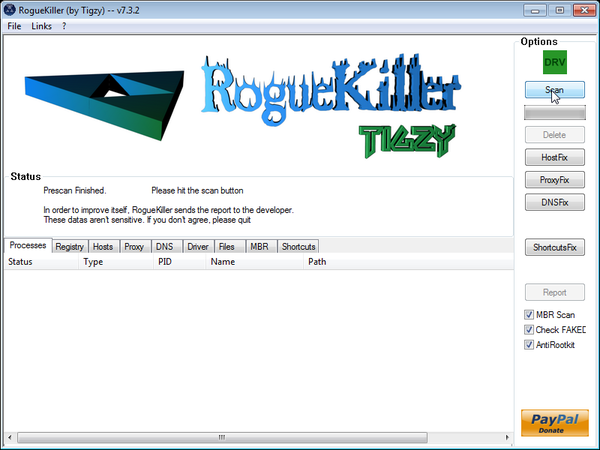
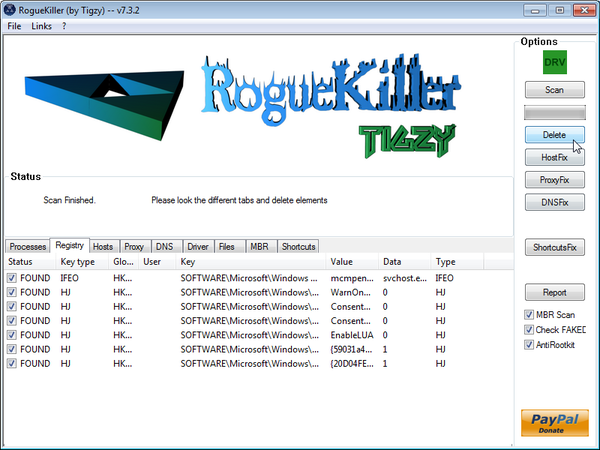
- After the scan has completed, press the Delete button to remove any malicious registry keys.
STEP 4: Remove Trojan:BAT/Bancos.B rootkit with HitmanPro
- you can download HitmanPro from the below link,then double click on it to start this program.
Download HitmanProOfficial Sophos download. Free scan, free 30-day trial to remove threats.
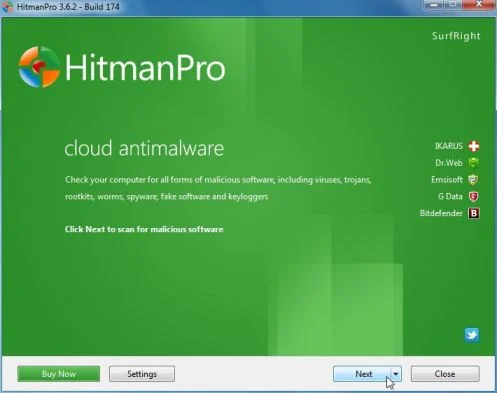
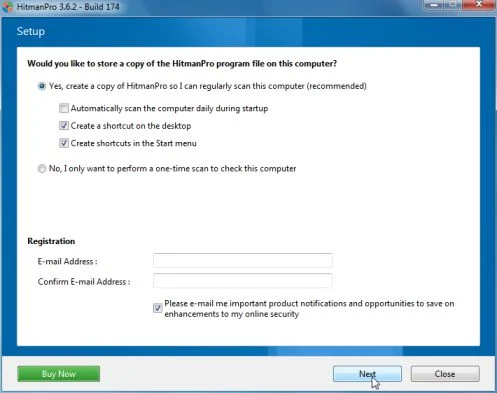
IF you are experiencing problems while trying to start HitmanPro, you can use the Force Breach mode.To start HitmanPro in Force Breach mode, hold down the left CTRL-key when you start HitmanPro and all non-essential processes are terminated, including the malware process. (How to start HitmanPro in Force Breach mode – Video) - HitmanPro will start and you’ll need to follow the prompts (by clicking on the Next button) to start a system scan with this program.
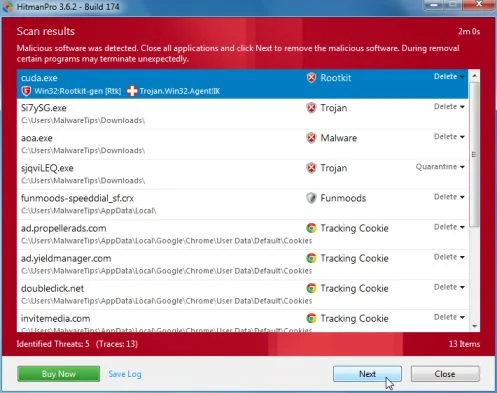
- HitmanPro will start scanning your computer for Trojan:BAT/Bancos.B malicious files as seen in the image below.
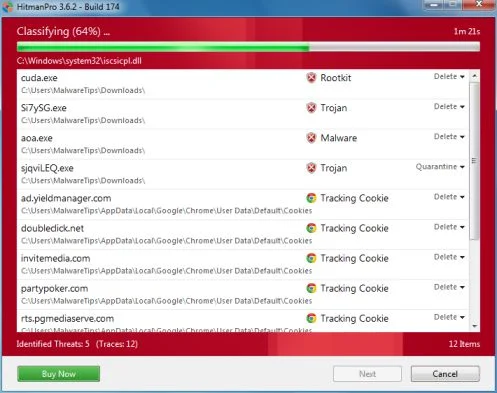
- Once the scan is complete,you’ll see a screen which will display all the infected files that this utility has detected, and you’ll need to click on Next to remove this malicious files.
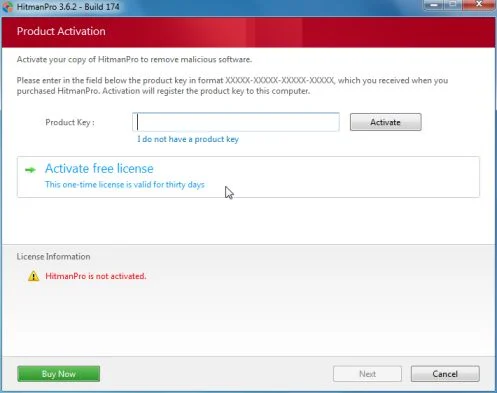
- Click Activate free license to start the free 30 days trial and remove all the malicious files from your computer.
STEP 5: Double check for any left over infections with Emsisoft Emergency Kit
- You can download Emsisoft Emergency Kit from the below link,then extract it to a folder in a convenient location.
Download Emsisoft Emergency KitOpens the download page in a new tab. - Open the Emsisoft Emergency Kit folder and double click EmergencyKitScanner.bat, then allow this program to update itself.
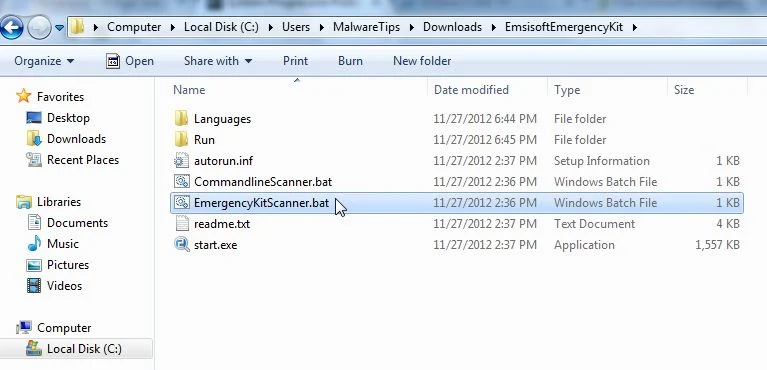
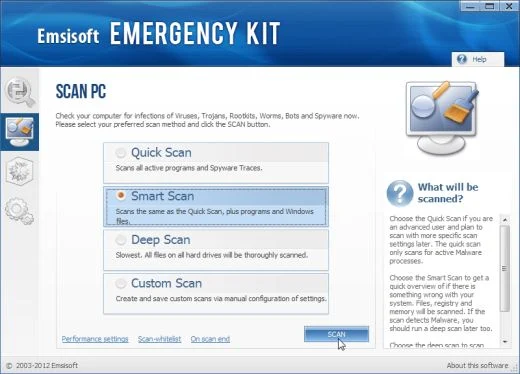
- After the Emsisoft Emergency Kit has update has completed,click on the Menu tab,then select Scan PC.
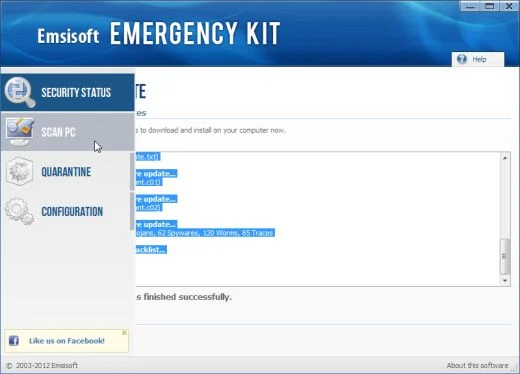
- Select Smart scan and click on the SCAN button to search for Trojan:BAT/Bancos.B malicious files.
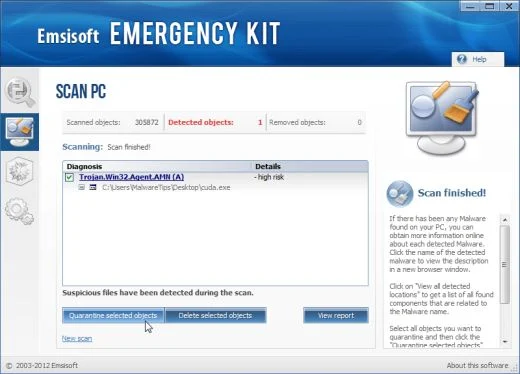
- When the scan will be completed,you will be presented with a screen reporting which malicious files has Emsisoft detected on your computer, and you’ll need to click on Quarantine selected objects to remove them.
Next,we will remove the tools that we’ve used in our malware removal process.
Kaspersky TDSSKiller and RogueKiller can be removed by deleting the utilities.
We strongly recommend that you keep Malwarebytes Anti-Malware and HitmanPro installed on your machine and run regular scans with this tools.If you however,wish to remove them,you can go into the Add or Remove programs and uninstall this two on-demand scanners.
Because this trojan is designed to steal your personal information, we recommend that you change your passwords for your online accounts and if you have used your credit card(s) while Trojan:BAT/Bancos.B was on your computer,you should contact your bank and let them know that you might be be victim of a phishing attack.

Join the discussion
2 commentsShare your experience or ask a question about this article.
Your progress
Did these steps help?
Let us know how the guide worked for you.
Describe what you see and the step you reached. Keep passwords and other private information out.
Discussion
First of all thank you for these instructions. I have Malwarebytes, avast! & Spybot installed. avast! runs 24/7. The Banker trojan showed up about a year ago & has been with me ever since. Malwarbytes finds it & removes it every time I run a scan (1 x month, more or less). The Banker is there EACH & EVERY time. So if I go through all the steps you’ve outlined, download this, download that, change the name, etc., will that finally sink the Banker? That’s a loaded question, isn’t it. I’ll put it another way — Is it a high percentage kill rate with the steps you have given?
In reply to Roxie English
Hello Roxie,
Yes, HitmanPro and RogueKiller should remove this infection…..Perform the scans and post back with the results….. If this won’t work, you always have our Malware Removal Assistance forum. :D