

If you are reading this article than you’re most likely trying to find out, what Live Security Platinum is and how you can get rid of this virus.
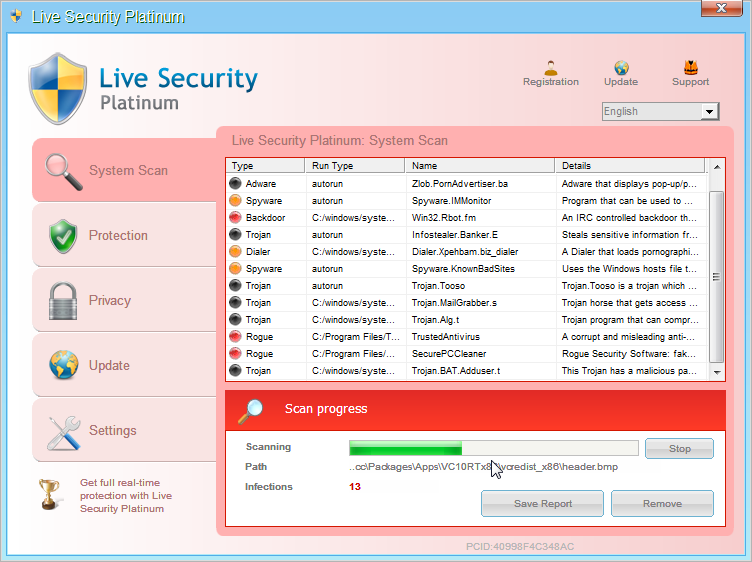
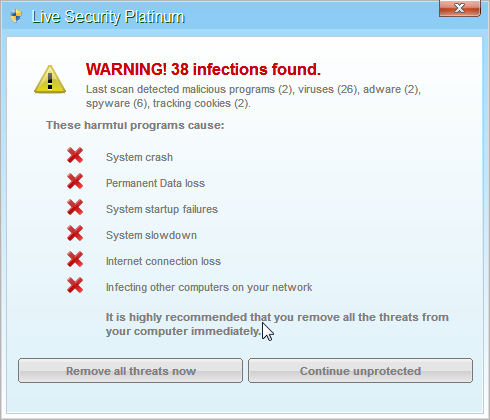
As you’ve probably realized by now,Live Security Platinum is a malicious software (rogue security software) that is displaying bogus antivirus alerts in an attempt to scare you into buying this fake security product.
Live Security Platinum is also blocking you from running programs and is causing browser redirects and slowing down your PC.
Live Security Platinum Images
Below you can see some images of Live Security Platinum.
Registration codes for Live Security Platinum
As an optional step,you can use the following license key to register Live Security Platinum and stop the fake alerts.
AA39754E-715219CE
Please keep in mind that entering the above registration code will NOT remove Live Security Platinum from your computer , instead it will just stop the fake alerts so that you’ll be able to complete our removal guide more easily.
Live Security Platinum Removal Instructions
STEP 1 : Start your computer in Safe Mode with Networking
- Remove all floppy disks, CDs, and DVDs from your computer, and then restart your computer.
- Press and hold the F8 key as your computer restarts.Please keep in mind that you need to press the F8 key before the Windows start-up logo appears.
Note: With some computers, if you press and hold a key as the computer is booting you will get a stuck key message. If this occurs, instead of pressing and holding the “F8 key”, tap the “F8 key” continuously until you get the Advanced Boot Options screen. - On the Advanced Boot Options screen, use the arrow keys to highlight Safe Mode with Networking , and then press ENTER.


STEP 2: Remove Live Security Platinum malicious proxy server
Live Security Platinum may add a proxy server which prevents the user from accessing the internet,follow the below instructions to remove the proxy.
- Start the Internet Explorer browser and if you are using Internet Explorer 9 ,click on the gear icon
 (Tools for Internet Explorer 8 users) ,then select Internet Options.

- Go to the tab Connections.At the bottom, click on LAN settings.
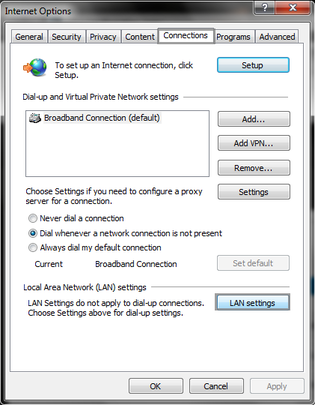
- Uncheck the option Use a proxy server for your LAN. This should remove the malicious proxy server and allow you to use the internet again.

 (Tools for Internet Explorer 8 users) ,then select Internet Options.


If you are a Firefox users, go to Firefox(upper left corner) → Options → Advanced tab → Network → Settings → Select No Proxy
STEP 3: Repair your Windows Registry from Live Security Platinum malicious changes.
Smart Fortress 2012 has changed your Windows registry settings so that when you try to run a executable file (ending with .exe ) , it will instead launch the infection rather than the desired program.
- Download the registryfix.reg file to fix the malicious registry changes from Live Security Platinum.
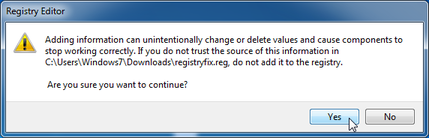
Download RegistryFix.regOpens the download page in a new tab. - Double-click on registryfix.reg file to run it. Click “Yes” for Registry Editor prompt window,then click OK.
STEP 4: Run RKill to terminate known malicious processes associated with Live Security Platinum.
RKill is a program that will attempt to terminate all malicious processes associated with Live Security Platinum,so that we will be able to perform the next step without being interrupted by this malicious software.
Because this utility will only stop Live Security Platinum running process, and does not delete any files, after running it you should not reboot your computer as any malware processes that are configured to start automatically will just be started again.
- While your computer is in Safe Mode with Networking ,please download the latest official version of RKill.Please note that we will use a renamed version of RKILL so that Live Security Platinum won’t block this utility from running.
Download RKillYour download starts right away. - Double-click on the iExplore.exe icon in order to automatically attempt to stop any processes associated with Live Security Platinum.

- RKill will now start working in the background, please be patient while the program looks for various malware programs and tries to terminate them.

IF you are having problems starting or running RKill, you can download any other renamed versions of RKill from here. - When Rkill has completed its task, it will generate a log. You can then proceed with the rest of the guide.
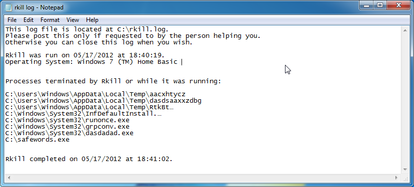


WARNING: Do not reboot your computer after running RKill as the malware process will start again , preventing you from properly performing the next step.
STEP 5: Remove Live Security Platinum malicious files with Malwarebytes Anti-Malware FREE
- Download the latest official version of Malwarebytes Anti-Malware FREE.
Download MalwarebytesFree official installer. Your download starts right away. - Start the Malwarebytes’ Anti-Malware installation process by double clicking on mbam-setup file.

- When the installation begins, keep following the prompts in order to continue with the setup process. Do not make any changes to default settings and when the program has finished installing, make sure you leave both the Update Malwarebytes’ Anti-Malware and Launch Malwarebytes’ Anti-Malware checked. Then click on the Finish button. If Malwarebytes’ prompts you to reboot, please do not do so.

- Malwarebytes Anti-Malware will now start and you’ll be prompted to start a trial period , please select ‘Decline‘ as we just want to use the on-demand scanner.

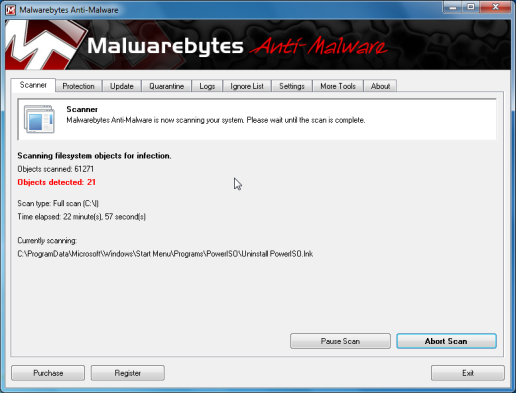
- On the Scanner tab,select Perform full scan and then click on the Scanbutton to start scanning your computer.

- Malwarebytes’ Anti-Malware will now start scanning your computer for Live Security Platinum malicious files as shown below.
- When the scan is finished a message box will appear, click OK to continue.
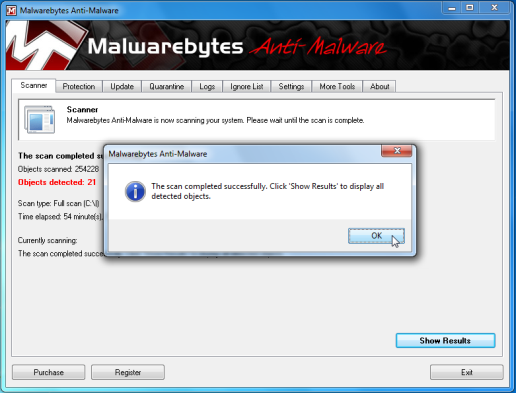
- You will now be presented with a screen showing you the malware infections that Malwarebytes’ Anti-Malware has detected.Please note that the infections found may be different than what is shown in the image.Make sure that everything is Checked (ticked) and click on the Remove Selectedbutton.
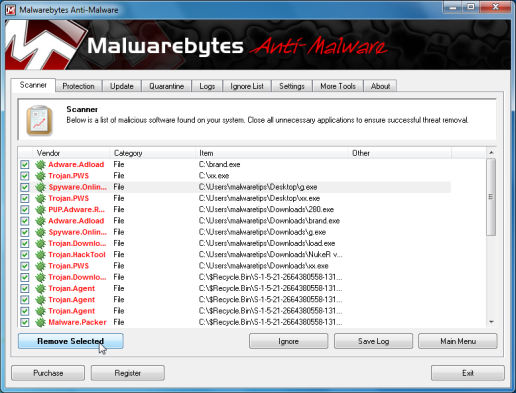
- Malwarebytes’ Anti-Malware will now start removing the malicious files.After completing this task it will display a message stating that it needs to reboot,please allow this request and then let your PC boot in Normal mode.


STEP 6: Double check your system for any left over infections with HitmanPro
- This step can be performed in Normal Mode ,so please download the latest official version of HitmanPro.
Download HitmanProOfficial Sophos download. Free scan, free 30-day trial to remove threats. - Double click on the previously downloaded fileto start the HitmanPro installation.

IF you are experiencing problems while trying to starting HitmanPro, you can use the “Force Breach” mode.To start this program in Force Breach mode, hold down the left CTRL-key when you start HitmanPro and all non-essential processes are terminated, including the malware process. (How to start HitmanPro in Force Breach mode – Video) - Click on Next to install HitmanPro on your system.

- The setup screen is displayed, from which you can decide whether you wish to install HitmanPro on your machine or just perform a one-time scan, select a option then click on Next to start a system scan.

- HitmanPro will start scanning your system for malicious files. Depending on the size of your hard drive, and the performance of your computer, this step will take several minutes.

- Once the scan is complete,a screen displaying all the malicious files that the program found will be shown as seen in the image below.After reviewing each malicious object click Next.

- Click Activate free license to start the free 30 days trial and remove the malicious files.
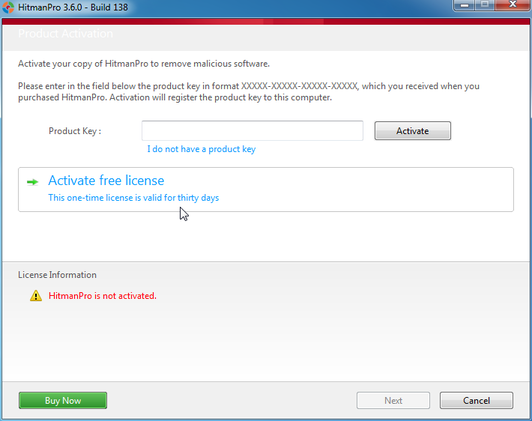
- HitmanPro will now start removing the infected objects, and in some instances, may suggest a reboot in order to completely remove the malware from your system. In this scenario, always confirm the reboot action to be on the safe side.


Join the discussion
311 commentsShare your experience or ask a question about this article.
Community experiences
Did this happen to you?
Your experience could help someone recognize the same scam. Submit a private report for our team to review.
I experienced this tooReports are reviewed before publication. Sharing publicly is always your choice.
Discussion
Hello,
First of all, thank you for providing this info. I tried to get my computer to go into “Safe Mode with Networking.” I tap F8 and I get to the right screen. I select the correct option but then it will not put me into Safe Mode with Networking. What can I do?
Chris
In reply to Chris
Hello,
Please follow the below steps…
STEP 1. While in NORMAL MODE,download HitmanPro and then start this program in ForceBreach Mode
1.Here are the direct download links for HitmanPro,
– http://dl.surfright.nl/HitmanPro36.exe (For 32bit)
– http://dl.surfright.nl/HitmanPro36_x64.exe (For 64bit)
2.Hold down the left CTRL-key when you start HitmanPro and all non-essential processes are terminated, including this rogue malicious process
Here is a video that explains with graphic details how to do this : http://www.youtube.com/watch?v=m6eRWTv2STk
3. Let HitmanPro scan and remove all the detected threats.
STEP 2: While in NORMAL MODE,download/Run Rkill and then run a scan with Malwarebytes
1.Download any re-named version of Rkill (direct download links bellow):
RKILL DOWNLOAD LINK #1
RKILL DOWNLOAD LINK #2
RKILL DOWNLOAD LINK #3
2.Next,please perform a scan with Malwarebytes as seen on the guide.
STEP 3. Run a scan with ESET Online Scanner
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
Waiting for your reply to tell me how everything is working.. :) Good luck!
HI,
My laptop working on safe mode.
This is my ESET SCAN THREATS
C:\Archivos de programa\BringMeSports_1c\bar\1.bin\1cdatact.dll a variant of Win32/Toolbar.MyWebSearch.A application Win32/Adware.Yontoo.B application
ETC…..
C:\WINDOWS\system32\drivers\5ef0cac4b951a0ef.sys a variant of Win32/Rootkit.Kryptik.MN trojan
Now I start my computer in Normal mode.
Please reply me as soon as possible.
Thanks
In reply to Girish
Ok….Did you run the HitmanPro and Malwarebytes scans?
How is your compute running in Normal Mode?Any problems?
In reply to Girish
Hi,
Thanks for help me. I run Hitmanpro, but its after scan there is no facility for free licence activation.
After scan with Malwarebytes no threats there.
Now My laptop working in Normal mode, but some time my internet exporer stop automatically. This is problem of threats.
And should i remove Hitaman pro?
In reply to Girish
I’ll contact the HitmanPro developers and let them know about the missing activation button…..
In the mean time please run a scan with RogueKiller.
ROGUEKILLER DOWNLOAD LINK (This link will automatically download RogueKiller on your computer)
NEXT,
Download Windows Repair by Tweaking.com to your desktop. Use the direct download link for the Portable version of Windows Repair by Tweaking.com
Note: When asked if you would like to create a restore point. It is recommended just in-case something does not go as planned.
Note: Leave everything else unchecked
Next,reset Internet Explorer settings:
Let me know how everything is running.As a personal opinion , you should really switch your browser to Google Chrome or Mozilla Firefox as Internet Explorer is a very targeted browser by the cyber criminals.
I can do all the things but I can not download rkill. And hitaman pro also not free. Please reply me now what I do. Now my computer is good but some time internet explorer stop automatically. I already removed Live security platinum, so why this happened?
Hi,
First thank you for your effort, i did all but i couldnt terminate the whole processes to start hitmanpro, please help me.
In reply to meme
Hello meme,
Please run a scan with RogueKiller.
ROGUEKILLER DOWNLOAD LINK (This link will automatically download RogueKiller on your computer)
NEXT,download HitmanPro and then start this program in ForceBreach Mode
1.Here are the direct download links for HitmanPro,
– http://dl.surfright.nl/HitmanPro36.exe (>> For 32bit)
– http://dl.surfright.nl/HitmanPro36_x64.exe (>> For 64bit)
2.Hold down the left CTRL-key when you start HitmanPro and all non-essential processes are terminated, including this rogue malicious process
Here is a video that explains with graphic details how to do this : http://www.youtube.com/watch?v=m6eRWTv2STk
3. Let HitmanPro scan and remove all the detected threats.
NEXT, run a s can with ESET Online Scanner
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
Waiting for your reply to tell me how everything is working.. :) Good luck!
In reply to Stelian Pilici
thanks for your replay, i tried to download RogueKiller but i couldnt
[Windows cannot access the specified file, You may not have permissions to access tjhe items]
please help
In reply to meme
Please run HitmanPro in ForceBreach mode as seen in my previous reply,and remove any malicious files detected.
NEXT,download any re-named version of Rkill (direct download links bellow):
RKILL DOWNLOAD LINK #1
RKILL DOWNLOAD LINK #2
RKILL DOWNLOAD LINK #3
2.Next,please perform a scan with Malwarebytes as seen on the guide.
After you have completed this scan, please run a RogueKiller and ESET Scan.
thanks very much
I did it as your tutorial. Thanks so much! God bless you! :D
hi, i cannot access the internet in safe mode, can i follow your instructions in normal mode, regards john
In reply to john
Hello John!
Hello,
STEP 1. While in NORMAL MODE,download HitmanPro and then start this program in ForceBreach Mode
1.Here are the direct download links for HitmanPro,
– http://dl.surfright.nl/HitmanPro36.exe (For 32bit)
– http://dl.surfright.nl/HitmanPro36_x64.exe (For 64bit)
2.Hold down the left CTRL-key when you start HitmanPro and all non-essential processes are terminated, including this rogue malicious process
Here is a video that explains with graphic details how to do this : http://www.youtube.com/watch?v=m6eRWTv2STk
3. Let HitmanPro scan and remove the detected threats.
Step 2: While in NORMAL MODE,download/Run Rkill and then run a scan with Malwarebytes
1.Download any re-named version of Rkill (direct download links bellow):
http://download.bleepingcomputer.com/grinler/WiNlOgOn.exe
http://download.bleepingcomputer.com/grinler/uSeRiNiT.exe
http://download.bleepingcomputer.com/grinler/rkill.scr
2.Next,please follow the guide starting with the Malwarebytes scan.
Let me know , how everything goes.
In reply to Stelian Pilici
Hi hello, many thanks hitman pro worked fine but cannot run rkill, i get an installation failed and a dos screen flashes briefly, seem to have remove the malware though?, thanks again
In reply to john
HitmanPro should have remove the malware so RKILL isn’t need it anymore….however please run a scan with Malwarebytes just to see if that got all the malicious files.
Next,run a scan with ESET Online Scanner
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
Hello, I tried following the above instructions but can’t start internet explore in safe mode or normal mode to be able to make the recommend downloads, looks like its disabled IE all together regardless of the mode I run in. How do i get to the next steps without being able to download the recommend softwares?
Help… Claudio
In reply to Claudio
Do you have any other browsers installed?
Did you try to use the license key on the post?
Lets try this trick:
Hold down the WINDOWS key and press the R key,this should brind up the Run box…. In it, please type the below content…
iexplore.exe http://download.bleepingcomputer.com/grinler/WiNlOgOn.exeLet the program run,until a log its produced (5 – 10 minutes max)
Next, hold down the WINDOWS key and press the R key,this should brind up the Run box…. In it, please type the below content…
iexplore.exe http://www.malwarebytes.org/mbam-download-exe.phpUpdate and Run a full system scan with Malwarebytes as seen on the above guide.
Let me know how everything goes…
In reply to Stelian Pilici
Hi stelian,
I’m having the same problem as claudio. I can not run Internet explorer or google chrome and when I did the first stage the LAN setting was already unchecked. How can I fix this without being able to download any software?
Cheers Wes
In reply to Wes
Get a USB stick and copy on it Combofix, then transfer it to the infected computer and perform the following steps:
Please read and follow all the steps very carefully.
Download ComboFix from one of the following locations:
COMBOFIX DOWNLOAD LINK #1 (This link will automatically download Combofix on your computer)
COMBOFIX DOWNLOAD LINK #2 (This link will automatically download Combofix on your computer)
VERY IMPORTANT !!! Save as Combo-Fix.exe during the download. ComboFix must be renamed before you download to your Desktop
———————————————————–
———————————————————–
———————————————————–
Notes:
I want to know how the heck does one infected with this? I haven’t downloaded or installed anything. Isn’t some kind of user interaction necessary?
In reply to drape
If you say that you didn’t run any file than you’re most likely the victim of a drive-by or exploit.
Here are some other common points of infections: http://malwaretips.com/blogs/from-where-did-my-pc-got-infected/
Anyway I strongly recommend that you check-up your PC security configuration in our Security Configuration Wizard forum because a decent antivirus should have prevent this infection.
It would be beneficial also to read this article: http://malwaretips.com/blogs/how-to-easily-avoid-pc-infections/ … :)
Stay safe!
In reply to Stelian Pilici
Hi Stellan,
I read the link you sent me to about malware and have come to the conclusion my computer was infected by the Live Security Platinum malware from the way I closed a pop-up. The information was helpful, however I am still unclear as to how to remove this from my computer?
I removed Norton Antivirus from my computer because it was slowing my laptop down, but if I re-install Norton, will Norton get rid of Live Security Plus?
In reply to Amber
Please read carefully the advice from my previous reply and scan with the recommended software as you need to remove this infection as soon as possible!
Hi,
I have made it successfully to the “RKill” step, however, everytime I attempt to download Rkill, the black screen pops up saying “preparing rkill” then it just disappears. The rkill log never comes up. I have tried the other options to download rkill, but it doesn’t seem to work. Please help!
In reply to Amber
Hello,
STEP 1. While in NORMAL MODE,download HitmanPro and then start this program in ForceBreach Mode
1.Here are the direct download links for HitmanPro,
– http://dl.surfright.nl/HitmanPro36.exe (For 32bit)
– http://dl.surfright.nl/HitmanPro36_x64.exe (For 64bit)
2.Hold down the left CTRL-key when you start HitmanPro and all non-essential processes are terminated, including this rogue malicious process
Here is a video that explains with graphic details how to do this : http://www.youtube.com/watch?v=m6eRWTv2STk
3. Let HitmanPro scan and remove the detected threats.
Step 2: While in NORMAL MODE,download/Run Rkill and then run a scan with Malwarebytes
1.Download any re-named version of Rkill (direct download links bellow):
http://download.bleepingcomputer.com/grinler/WiNlOgOn.exe
http://download.bleepingcomputer.com/grinler/uSeRiNiT.exe
http://download.bleepingcomputer.com/grinler/rkill.scr
2.Next,please follow the guide starting with the Malwarebytes scan.
Let me know , how everything goes.
In reply to Amber
Nevermind the previous comment, I realized I was reading the wrong comment. I am going to try the hitman pro option and go from there.
Thank you for all your help.
In reply to Amber
It worked like a charm!! Thanks, Stelian, you’re a rockstar!!
Got hit with this pesky virus but thanks to your tutorial was able to follow your advice and thankfully all seems to be working properly again.
Much appreciate your help. Thank you.
You are actually a life saver! Live security removed , thank you so so much!
Thank you. You are wonderful people.
So grateful. Platinum virus removed. Would have been lost without your efforts.
Your efforts are appreciated.
If I delete the hitmanpro will the thing come back?
In reply to Bob
HitmanPro is a legit software….If you want to remove it , just go to the Add/Remove Programs in Windows… :_)
Stay safe!
In reply to Stelian Pilici
I think he’s asking if he deletes hitman pro will the Live Security Platinum come back? In which case I would think the answer is no, unless you do again what you did to let it on in the first place
In reply to marc
Yes,that’s right…If you removed the detected infections by HitmanPro then Live Platinum Security should be gone. :)
Hi,
Thank you so much. The original instructions above were all I needed to seemingly remove Live Security Platinum from my desktop (except I didn’t install the hitman pro. Running Malwarebytes again in regular mode, then Symantec. Lucky that this didn’t seem to include a rootkit… had a nasty one last fall….. worse infection ever!
Thank you so much for your guide! It worked well… the first time. I had removed it this past Wednesday evening using your guide, except I didn’t run Hitmanpro. I ran symantec instead. Then it happened again Friday morning and ran through your guide again, using hitmanpro this time. But all of a sudden my programs shut down just now. It came back AGAIN. I’m glad there’s a way to get rid of it… but is there a way to keep it away for GOOD? I don’t even know where I’m picking this up from. Hope to hear back from you soon, thanks!
In reply to Sarah
Hello,
Please re-run a scan with Malwarebytes.
Next,please run a scan with ESET Online Scanner
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
Hi
Thank you so much for all your help i carried out your instructions and it seems to have worked, but i was wondering if you could help with something all the scans seemed to have worked but on my taskbar it still has live security platinium 3.5.7 listed as an option to add to my taskbar, is this just an icon or is it still installed on my computer?? Help would be much appreciated.
Thanks Clare
In reply to clare
Its most likely ,just a left over icon :)
Anyway please run a scan with ESET Online Scanner
ESET Online Scanner Download Link (This link will automatically download ESET Online Scanner on your computer.)
In reply to Stelian Pilici
Hi
Heres the results from the ESET scan you asked me to run sorry there seems to be a fair few:
C:\Program Files (x86)\BabylonToolbar\BabylonToolbar\1.5.3.17\BabylonToolbarApp.dll a variant of Win32/Toolbar.Babylon application cleaned by deleting – quarantined
C:\Program Files (x86)\BabylonToolbar\BabylonToolbar\1.5.3.17\BabylonToolbarEng.dll Win32/Toolbar.Babylon application cleaned by deleting – quarantined
C:\Program Files (x86)\BabylonToolbar\BabylonToolbar\1.5.3.17\BabylonToolbarsrv.exe probably a variant of Win32/Toolbar.Babylon application cleaned by deleting – quarantined
C:\Program Files (x86)\BabylonToolbar\BabylonToolbar\1.5.3.17\BabylonToolbarTlbr.dll Win32/Toolbar.Babylon application cleaned by deleting – quarantined
C:\Program Files (x86)\BabylonToolbar\BabylonToolbar\1.5.3.17\bh\BabylonToolbar.dll Win32/Toolbar.Babylon application cleaned by deleting – quarantined
C:\Users\clare\AppData\Local\Temp\YontooSetup-S.exe probably a variant of Win32/Adware.SLITAT application cleaned by deleting – quarantined
C:\Users\clare\AppData\Local\Temp\BabylonToolbar\BabylonToolbar\1.5.3.17\BabylonToolbar4ie.exe Win32/Toolbar.Babylon application cleaned by deleting – quarantined
C:\Users\clare\AppData\Local\Temp\is1754315082\ezLooker-S-Setup_Suite1.exe probably a variant of Win32/Adware.DFJFHGU application cleaned by deleting – quarantined
C:\Users\clare\AppData\Local\Temp\is1754315082\MyBabylonTB.exe Win32/Toolbar.Babylon application cleaned by deleting – quarantined
C:\Users\clare\AppData\LocalLow\Sun\Java\Deployment\cache\6.0\50\7becc332-36586cd0 a variant of Win32/Injector.TNC trojan cleaned by deleting – quarantined
Thanks
Clare
In reply to clare
Looks good!How is your computer behaving?On which browser do you have problems?
YOU ARE A GENIUS. Thank you so freakin’ much! I didn’t have problems removing it thanks to this tutorial! :D
Thanks for your help! With this article’s advice & one other free anti virus program, hopefully I have ridden my computer. It sucks that someone would create a program to do so much harm & frustration