

Getting a text about a missed USPS delivery is stressful enough. Getting one with a PDF attachment feels even more official.
That is exactly why this scam works.
The USPS scam text PDF attachment is a phishing scheme where scammers send a fake delivery message claiming there is a problem with your package. Instead of only including a suspicious link in the text, the message may attach a PDF that looks like an official shipping notice, delivery form, or address update document.
But the PDF is not proof that the message is real. In many cases, it is just another layer of deception designed to make the scam look safer and more believable.
What Is the USPS Scam Text PDF Attachment?
The USPS scam text PDF attachment is a mobile phishing scam, also known as smishing. The message pretends to come from the United States Postal Service and usually claims that a package cannot be delivered because of an incomplete address, unpaid postage, a failed delivery attempt, or a missing confirmation.
The twist is the PDF attachment.
Instead of asking you to click a link directly in the text, the scam may tell you to open a PDF file. Inside that PDF, there may be a button, tracking notice, QR code, or “Update Address” link that sends you to a fake USPS website.
The U.S. Postal Inspection Service warns that USPS-related smishing messages often claim a delivery requires action and are designed to steal personal or financial information. USPS also says it does not send customers text messages or emails unless the customer first requests the service with a tracking number, and those official messages will not contain a link.
This means a random text with a PDF attachment about a USPS delivery should be treated as suspicious by default.
Why Scammers Use PDF Attachments
PDFs feel professional. People receive PDFs from banks, employers, shipping companies, schools, government offices, and online stores. Because of that, many users assume a PDF is safer than a normal link.
Scammers exploit that trust.
Security researchers at Zimperium reported a USPS impersonation campaign that used malicious PDF files targeting mobile users. The PDFs were designed to steal credentials and sensitive information, and researchers found more than 20 malicious PDF files and 630 phishing pages connected to the campaign.
The danger is not only the file itself. The PDF may contain a hidden or disguised link. On a phone, it is harder to inspect where a button or link really goes before tapping it. That gives scammers a major advantage.
How the USPS PDF Text Scam Works
1. You Receive a Fake USPS Text
The message usually arrives from an unknown number, email-to-text address, or strange sender. It may say something like:
“USPS: Your package cannot be delivered due to incomplete address information. Please open the attached notice and update your details.”
Other versions may claim:
- Your package is on hold
- Your delivery failed
- You owe a small redelivery fee
- Your shipping address needs confirmation
- Your parcel will be returned if you do not act quickly
The FTC warns that fake delivery texts often claim there is a problem such as unpaid postage, missed delivery, or shipping preferences that must be updated. The goal is to push you toward a link or fake website where your information is collected.
2. The PDF Looks Like an Official USPS Notice
Once opened, the PDF may show USPS-style colors, a tracking number, a barcode, a delivery failure message, or an “Update Now” button.
This is the psychological trick. The scammer wants the PDF to feel like an official document rather than a random scam link.
But PDFs can contain embedded links, buttons, scripts, and other interactive elements.
3. The PDF Sends You to a Fake USPS Website
If you tap the button or link inside the PDF, you may land on a page that looks like USPS.com. The fake site may use the USPS logo, postal colors, fake tracking details, and official-sounding wording.
But the domain will not be the real USPS website.
The fake page usually asks you to enter:
- Full name
- Home address
- Phone number
- Email address
- Date of birth
- Credit or debit card number
- CVV code
- Billing ZIP code
4. The Scam Asks for a Small “Redelivery Fee”
Many USPS phishing scams ask for a tiny payment, often less than $1, to make the request feel harmless.
That small charge is bait.
The real goal is not the fee. The goal is your card number, CVV, billing details, address, and identity information. Once scammers have that data, they may attempt fraudulent charges, sell the information, use it for identity theft, or target you with more scams.
The Postal Inspection Service warns that scammers seek personally identifiable information such as usernames, passwords, Social Security numbers, birth dates, card numbers, PINs, and other sensitive data that can be used for financial fraud.
How the USPS Scam Texts Look
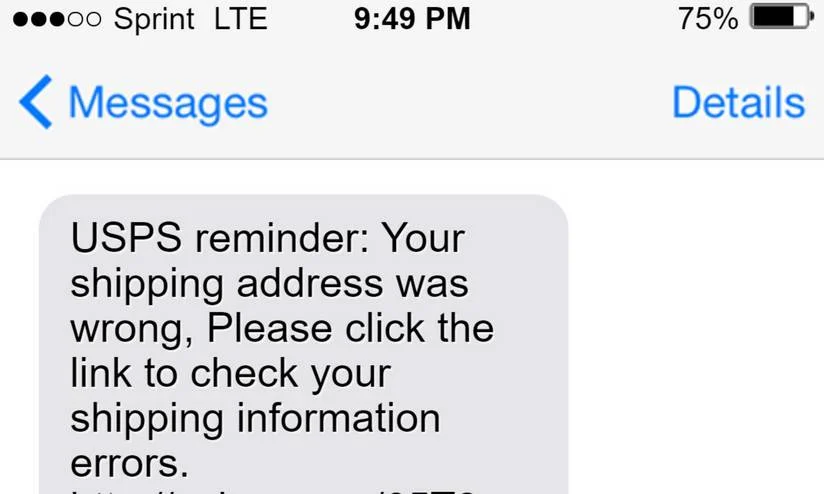
USPS scam texts usually look short, urgent, and official enough to make people panic. The message often claims there is a problem with a package and tells the recipient to open a PDF attachment or click a link to fix the issue.
A typical scam text may look like this:
USPS Notice: Your package could not be delivered because the address information is incomplete. Please open the attached delivery notice and update your details.
Another version may say:
USPS: Your parcel is on hold due to missing delivery information. Review the attached PDF and confirm your address within 24 hours to avoid return.
Some messages are even more direct:
Your USPS package has failed delivery. Open the attached document to reschedule delivery.
The PDF attachment may have a name that sounds official, such as:
USPS_Delivery_Notice.pdfPackage_Update_Form.pdfUSPS_Redelivery_Request.pdfShipping_Address_Confirmation.pdfDelivery_Problem_Notice.pdf
Inside the PDF, scammers may include USPS-style branding, fake tracking numbers, barcodes, QR codes, or buttons that say:
- “Update Delivery Address”
- “Confirm Package”
- “Pay Redelivery Fee”
- “Track My Parcel”
- “Reschedule Delivery”
The goal is to make the attachment feel safer than a normal suspicious link. Instead of placing the phishing link directly in the text, scammers hide it inside the PDF where many people are less cautious.
The message may also include urgency, such as:
- “Your package will be returned today”
- “Action required within 12 hours”
- “Delivery attempt failed”
- “Final notice”
- “Your parcel is suspended”
These are pressure tactics. Real delivery problems should always be checked directly through the official USPS website or the retailer where the order was placed, not through a random text message or PDF attachment.
Red Flags of the USPS Scam Text PDF Attachment
The message is likely fake if:
- You did not request USPS text tracking for that package
- The message comes from a random phone number or email address
- It includes a PDF attachment you were not expecting
- It asks you to open a file to update delivery information
- It creates urgency or threatens package return
- It asks for a small payment to release or redeliver a package
- It asks for your card number, CVV, or personal details
- The PDF contains a clickable button or QR code
- The website address is not the real USPS domain
- The wording feels awkward, generic, or overly urgent
A real USPS tracking update should not require you to open a random PDF from an unsolicited text.
Is Opening the PDF Dangerous?
Opening the PDF may not automatically mean your money or identity has been stolen, but it is still risky.
The highest risk comes if you:
- Tap a link inside the PDF
- Scan a QR code inside it
- Enter personal information
- Enter payment card details
- Download another file from the linked page
- Give the page permission to install anything
USPS and USPIS guidance warns that phishing and smishing messages may contain fake URLs or files designed to steal personal information, and some files may infect a device if clicked or opened. (USPS)
If you only opened the PDF but did not tap anything or enter information, delete the message, update your phone, and monitor for suspicious activity. If you clicked the link or typed anything into the fake page, treat it as a higher-risk incident.
What To Do If You Received the USPS PDF Text
Do not open the attachment again.
Do not click links inside the PDF.
Do not reply to the text.
Do not call any number listed in the message.
Instead, check your delivery status directly by going to the official USPS website or the retailer account where you placed the order.
You should also report the message. The Postal Inspection Service says USPS-related smishing can be reported by emailing spam@uspis.gov, attaching a screenshot, including the sender number and date, and forwarding the smishing text to 7726.
What To Do If You Clicked the Link or Entered Information
If you clicked the link inside the PDF but did not submit anything, close the page immediately. USPIS still recommends notifying your financial institution if you interacted with the URL, even if you did not click submit.
If you entered card details, act quickly:
- Contact your bank or card issuer and report the card as compromised.
- Ask for a replacement card.
- Dispute any unauthorized charges.
- Monitor your account for small test charges.
- Change passwords for accounts using the same email or phone number.
- Enable two-factor authentication where possible.
- Watch for follow-up scam texts, calls, or emails.
- Consider placing a fraud alert or credit freeze if you shared sensitive identity information.
If you entered your Social Security number, date of birth, or other identity details, report the incident to the FTC and monitor your credit closely.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
FAQ
What is the USPS scam text PDF attachment?
The USPS scam text PDF attachment is a phishing scam where scammers send a fake delivery text pretending to be from USPS. The message includes a PDF attachment that may look like an official shipping notice, but it usually contains a link or QR code leading to a fake USPS website.
Is the USPS PDF text message real?
Usually, no. A random text message with a PDF attachment claiming to be from USPS should be treated as suspicious. Scammers often use fake delivery alerts to steal personal information, credit card numbers, and login details.
Why does the scam include a PDF file?
Scammers use PDFs because they look more professional and official than a normal link. Many people trust PDF files, so the attachment makes the scam feel more believable.
Can opening the PDF infect my phone?
Simply opening the PDF may not always infect your phone, but it is still risky. The bigger danger is tapping a link, scanning a QR code, downloading another file, or entering personal or payment information on the fake website.
What happens if I click the link inside the PDF?
The link may take you to a fake USPS website that asks you to update your address, confirm delivery, or pay a small redelivery fee. Any information you enter can be stolen by scammers.
Does USPS send PDF attachments by text?
USPS does not normally send random PDF attachments by text asking customers to fix delivery problems or pay fees. If you receive a message like this unexpectedly, do not trust it.
What should I do if I received a USPS text with a PDF?
Do not open the attachment, click any links, reply to the message, or call any phone number listed inside it. Check your package directly through the official USPS website or the retailer where you placed your order.
What should I do if I entered my credit card information?
Contact your bank or card issuer immediately. Ask them to block or replace the card, monitor your account for unauthorized charges, and dispute any fraudulent transactions.
How can I report the USPS PDF scam text?
You can forward the suspicious text to 7726 and report USPS-related phishing or smishing messages to the U.S. Postal Inspection Service. You can also report the scam to the FTC.
How can I avoid USPS text scams?
Do not click links in unexpected delivery messages. Track packages only through official websites or apps, check the sender carefully, avoid opening suspicious attachments, and never enter payment details after clicking a link from a random text.
The Bottom Line
The USPS scam text PDF attachment is a more deceptive version of the classic fake delivery text. Scammers know many people are suspicious of random links, so they hide the link inside a PDF that looks official.
That does not make it safe.
USPS does not randomly text customers with PDF attachments asking them to fix delivery problems, pay redelivery fees, or confirm personal information. If you receive one, do not open the file, do not click anything inside it, and do not enter payment information.
Check your package directly through USPS or the retailer you ordered from. Report the message, delete it, and warn others before they fall for the same trick.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.