

The new file endings are bad enough. Then a note suggests your databases could be sold, turning a computer problem into a much more personal worry.
If Zynex ransomware appears in your folders, you need two clear answers: what happened to the files, and what the attacker can actually prove.
Overview
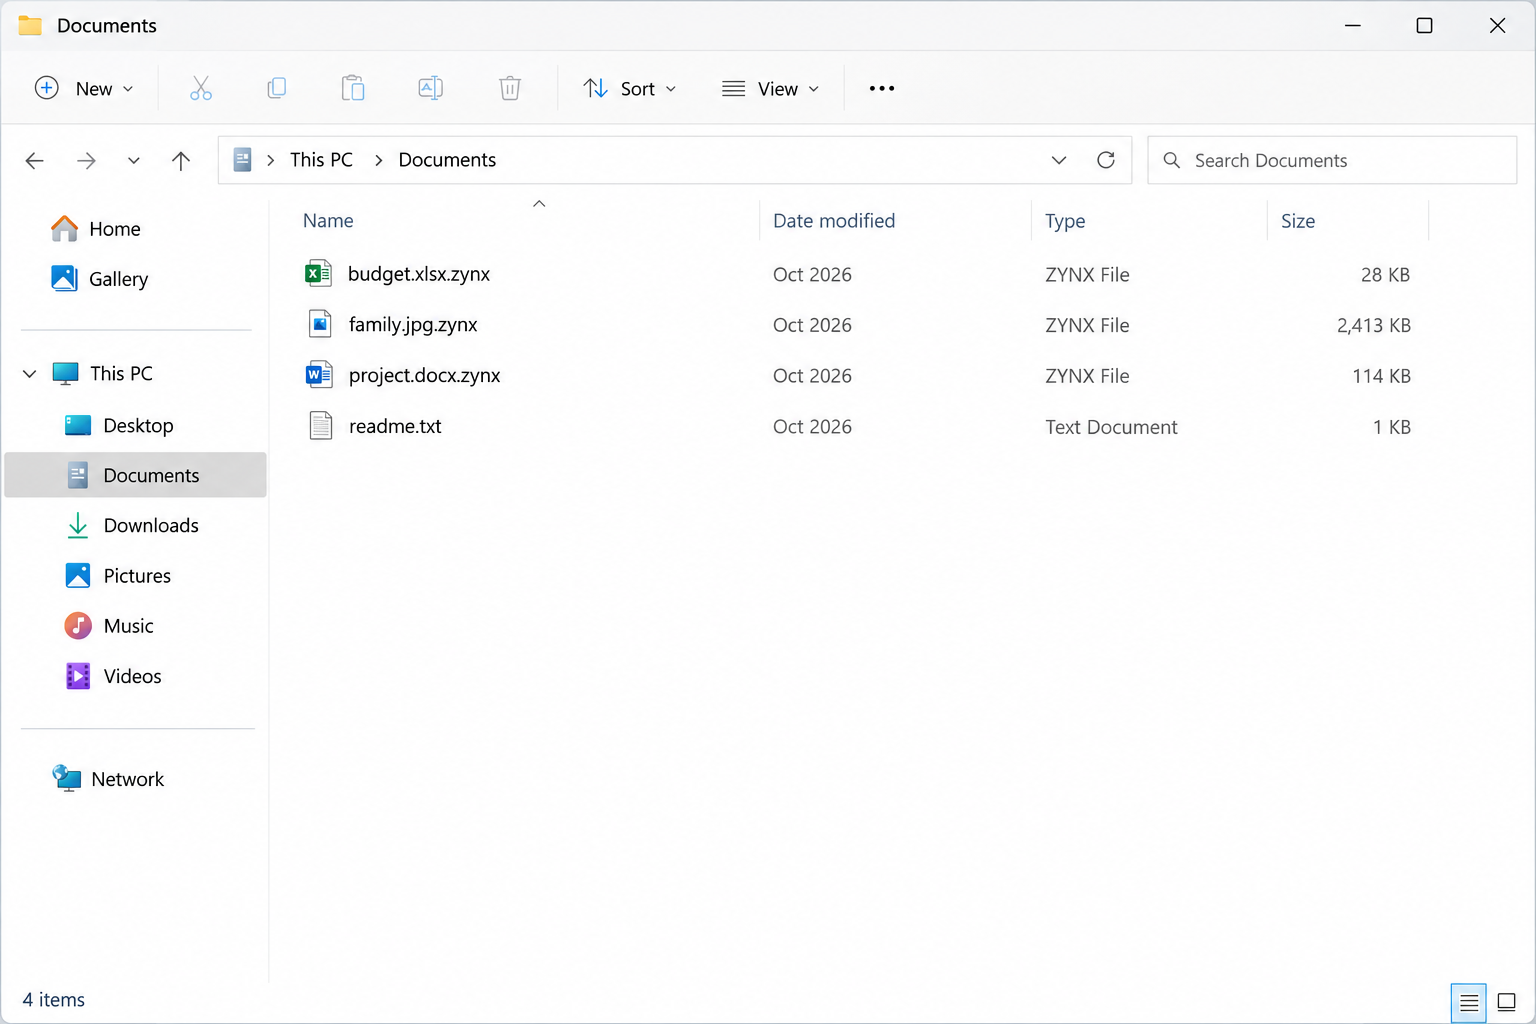
The .zynx suffix and readme.txt
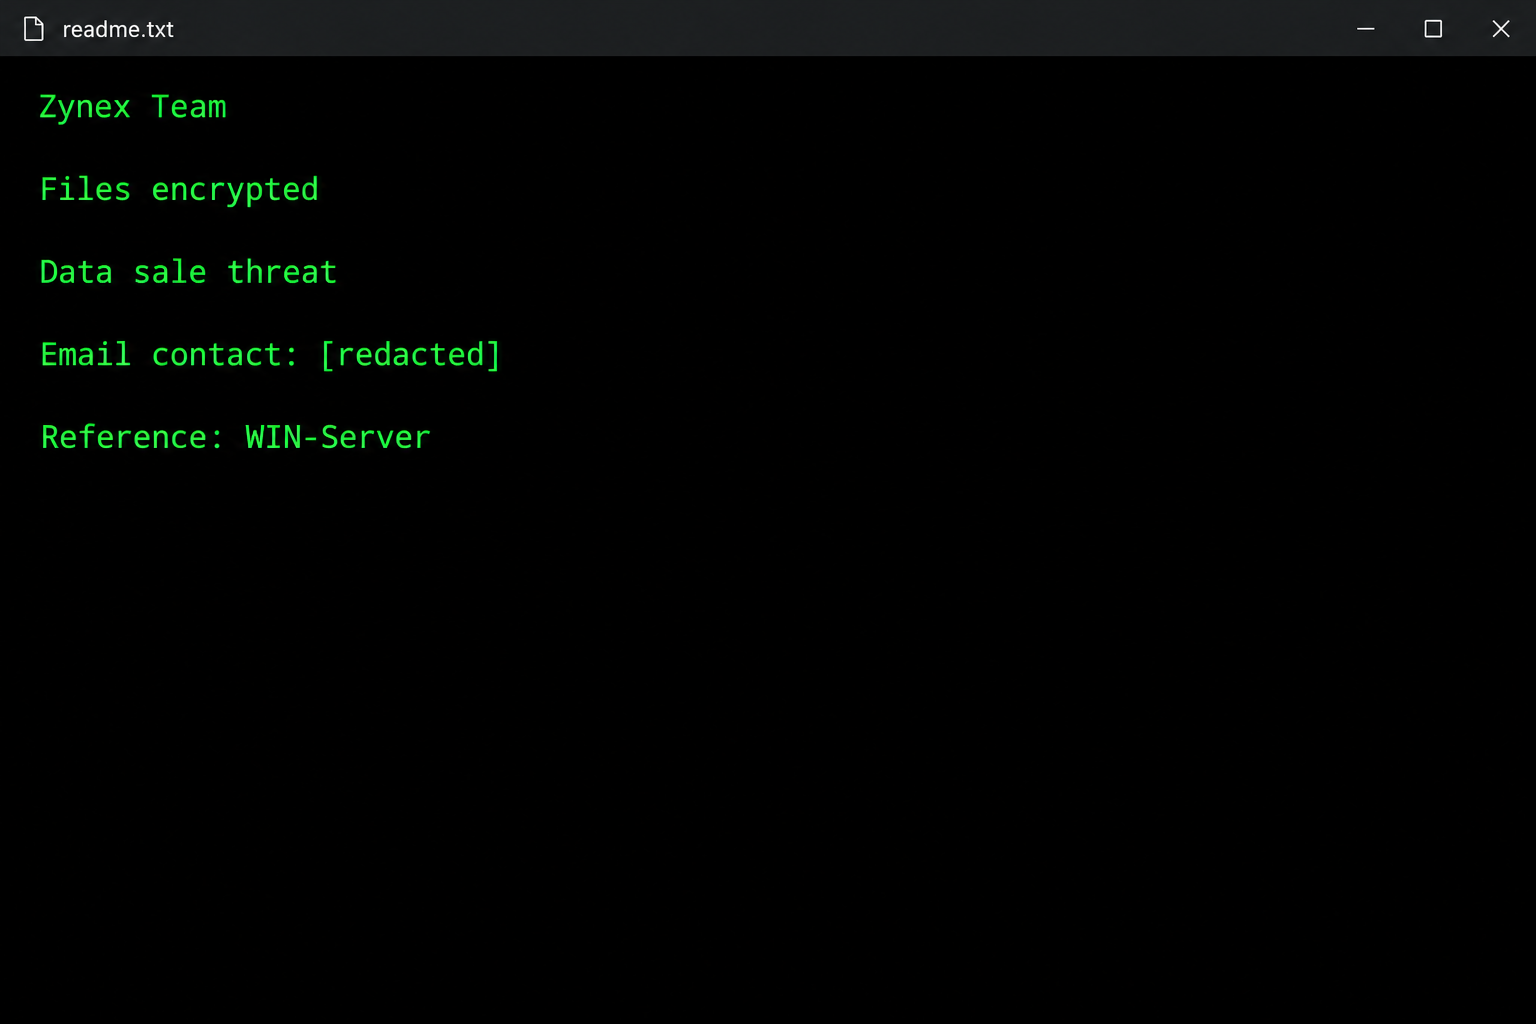
The documented Zynex ransomware specimen adds .zynx to filenames and leaves a ransom note called readme.txt.
For example, an affected file might look like accounts.xlsx.zynx. Its continued presence in a folder does not mean its original contents remain readable.
This article concerns the ransomware identification pattern, not unrelated websites or businesses with similar names.
- Added .zynx endings on inaccessible files.
- A readme.txt ransom demand.
- Claims about stolen files and databases.
- A proposed email conversation and decryption demonstration.
A theft allegation requires a separate investigation
The note claims data was uploaded and threatens to sell it. That is evidence of an extortion threat, not independent proof of successful theft.
Nevertheless, sensitive information deserves attention. A business should investigate possible exposure while working to restore unavailable systems.
A working backup could solve an availability problem without answering a confidentiality problem. Those are distinct parts of the response.
The current recovery position
No verified public tool specifically supporting Zynex was located in the decryption catalog reviewed on October 6, 2026. Similar family labels do not establish compatibility.
Preserve encrypted copies, investigate intact backups, and obtain help appropriate to the data involved. Do not let a sales threat rush you into irreversible decisions.
Paying would not provide independently verifiable proof that copied information had been deleted. That remains true even if some files were successfully decrypted.
Reading the Data-Sale Threat Without Accepting It as Fact
Ransom notes are designed to influence decisions. Their authors have a financial reason to make the incident sound as broad and urgent as possible.
Ask what the actual evidence shows. Have unfamiliar exports appeared? Are there unusual outbound transfers? Did an unauthorized account access the database?
Those questions belong with your responder, not an argument in the attacker’s inbox. A note cannot replace a review of logs and access records.
The illustrations use fictional documents and shortened note content to show the visible pattern. They are not evidence that a particular organization’s data was uploaded.
How Zynex Ransomware Works
Step 1: Unauthorized access creates an opportunity to damage data
File encryption requires access to the relevant storage. That access can come from malicious code running locally or from a broader intrusion.
The entry route for your incident needs evidence. A ransomware brand does not tell you which password, download, or exposed service was involved.
A responder should trace the first suspicious activity, not simply start at the time readme.txt became visible.
Step 2: Files become unavailable and acquire .zynx endings
The reported specimen alters data and appends .zynx. An application then encounters encrypted contents rather than the document structure it expects.
Rename operations cannot restore that structure. Keep filenames intact and work on duplicates during any approved recovery test.
Record actual affected locations. The note’s claim about an entire network should not be substituted for a verified inventory.
Step 3: The note introduces another source of pressure
Alongside denied access, the attacker describes a possible sale of stolen information. This raises concerns that a backup alone cannot resolve.
It may also push a victim to negotiate before evaluating whether the theft assertion is supported.
The right response is neither automatic belief nor automatic dismissal. Preserve logs and let qualified investigators assess what information may have been accessed.
Step 4: Email contact makes the demand feel procedural
The documented note lists WeAreZynex@tutamail.com and Getyourdata@onionmail.org, with WIN-Server as the requested subject. These are identification clues, not recommended contacts.
Recognizable mail services do not authenticate the person using them. A functioning inbox can belong to someone committing extortion.
If a responder preserves correspondence, keep the original messages and headers. Do not publicly post confidential exchanges or privately supplied organization details.
Step 5: A demonstration and early-contact incentive encourage a deal
The offer of a limited decryption test is meant to make payment seem practical. It cannot guarantee complete recovery of a damaged database or archive.
Likewise, an early-contact incentive is a negotiating device. It does not show that restoring files will become technically impossible when a clock runs out.
Keep the two promises separate: access to files and treatment of allegedly copied data. Neither creates a dependable contract with the attacker.
What a Business Needs to Check Beyond the Encrypted Folder
Availability: what cannot currently be used?
List the interrupted functions, not just file totals. A small inaccessible database can matter more than thousands of replaceable downloads.
Assign restoration priorities with the people who understand those systems. Avoid bringing a damaged application back online merely because its files have been copied somewhere.
Access: who could still enter the environment?
Review compromised accounts, remote sessions, shared credentials, and unexpected administrative access. Restoring documents while leaving the entry point available risks another interruption.
Do not make unplanned global account changes yourself during a coordinated investigation. Your response team should sequence containment and credential recovery.
Confidentiality: which data may have been exposed?
Identify potentially affected records and their owners. Involve privacy, legal, or compliance support where sensitive business or personal information is present.
Notification duties depend on the facts and jurisdiction. An attacker email cannot tell you whether a legal threshold has been met.
What to Do If You Find Zynex Ransomware
Disconnect affected devices and notify the incident-response lead. Protect backups and preserve system evidence before attempting mass cleanup.
Keep readme.txt and a representative set of .zynx filenames. Document where they were found and which applications stopped working.
Open separate workstreams for restoration and possible data exposure. Do not let a successful backup restore close the confidentiality investigation prematurely.
Use malware-removal tools such as Malwarebytes within a planned cleanup process. A scanner result alone cannot verify that all network access has been revoked.
Report the extortion and retain transaction records if payment occurred. Get qualified advice before responding to further demands or purported recovery intermediaries.
Remove Zynex and Investigate Related Access
Contain the incident before running cleanup tools
Disconnect the affected computer from Wi-Fi and wired networks. Unplug external storage and leave backup drives disconnected while you assess what happened.
Pause synchronization from a clean device where possible. Otherwise, encrypted versions may replace usable cloud copies while you are trying to rescue them.
At work, contact your IT or incident-response team immediately. A ransomware screen on one computer may be the visible part of a larger intrusion.
Keep the ransom note, filenames, discovery time, and any security alerts. A specialist may need disk or memory evidence before cleanup changes the machine.
If you cannot isolate a computer and encryption is visibly continuing, seek immediate assistance about shutting it down. Powering off can lose volatile evidence.
Do not repeatedly restart, reinstall, or experiment with utilities. Those actions can overwrite recovery evidence without addressing the underlying access problem.
Use trusted scanners on an isolated personal computer
For a home computer, arrange cleanup after preserving the evidence you need. Obtain security tools through their official websites using an unaffected system.
Malwarebytes can scan for malicious programs and related unwanted software. It is an infection-removal tool, not a way to decrypt already encrypted documents.
Install a current copy, update its detection data when safely possible, and run the available comprehensive scan. Review detections before applying the recommended quarantine actions.
Keep the scan report. It can help distinguish the ransomware payload from another infection, a suspicious installer, or a remote-access program.
Windows Security also provides scan options. Microsoft Defender Offline restarts into an offline scanning environment, so save your work before starting it.
Follow Microsoft’s ransomware protection guidance rather than instructions in the criminal’s note. A note telling you to disable protection is not trustworthy advice.
If Windows will not start or the scanners cannot operate, stop improvising. Use reputable technical assistance instead of downloading a supposed one-click emergency decryptor.
Do not upload the executable to unfamiliar recovery websites or run it elsewhere for testing. A second execution can create another incident.
Verify the environment before restoring anything
A completed scan is useful, but it cannot establish that every account, remote session, or networked computer is safe.
Check for unauthorized remote-access software, suspicious accounts, changed security settings, and unknown scheduled tasks. Business environments require coordinated investigation beyond this home-computer checklist.
Change exposed passwords from a clean device. Prioritize email, cloud storage, administrator access, and any account whose credentials were saved on the affected system.
Enable multifactor authentication where supported and revoke suspicious sessions. Simply changing the password may leave an existing signed-in session active.
A trusted reinstall may be appropriate when system integrity remains uncertain. Preserve recoverable data first, and reinstall from authentic installation media.
AdGuard can help reduce exposure to malicious advertising during future browsing. It neither cleans an infected system nor reverses file encryption.
Keep backup media offline until cleanup and access checks are complete. Reconnecting your only good copy too early can turn a recovery opportunity into another loss.
Restore Files Without Losing the Incident Evidence
Make a recovery copy, not another damaged original
Keep an untouched copy of the encrypted data whenever practical. Include the ransom note and retain the original directory structure.
Use a separate destination for recovery experiments. Never let a utility overwrite your only encrypted copy or replace an intact backup.
Before sharing samples, consider their sensitivity. Choose an ordinary, nonconfidential file and ask the service about handling rules if business or personal information is involved.
The note’s name, complete filename suffix, and contact details can help identify a variant. An extension alone is not enough to establish decryption compatibility.
For example, two infections can use the same suffix while generating different keys. A familiar family name can also hide a newer, unsupported version.
Record the exact error or result from each attempt. Keep a simple checklist so another helper does not repeat risky tests on the same files.
Check recognized decryption projects
Visit the No More Ransom decryption catalog from a clean browser. Look for the actual variant and read the tool’s requirements carefully.
A tool for a related family does not automatically unlock your files. Some decryptors support only older versions, certain keys, or specific encryption mistakes.
Download through the catalog’s trusted vendor link, not a sponsored search result or an unsolicited message offering guaranteed recovery.
Test only a duplicate sample first. Successful decryption should produce a usable document or image, not merely remove the added extension.
If the utility reports an unsupported file or key, stop. Changing the filename to resemble a supported variant does not change its encrypted contents.
When no compatible tool is available, preserve your encrypted archive. Researchers sometimes release new tools later, but future recovery cannot be promised.
Look for copies that existed before encryption
Check disconnected drives, backup software, cloud version history, another computer, and files previously sent to trusted contacts. You may have more copies than you remember.
Cloud synchronization is not automatically a backup. Confirm that an earlier usable version survives and that the account itself has not been compromised.
Restore into a cleaned environment. Open a selection of documents, photos, and project files before assuming the recovered collection is complete.
Compare important dates and contents. An older spreadsheet might open perfectly while still missing the transactions you needed to recover.
Windows Previous Versions or existing snapshots may offer additional copies. Availability depends on prior configuration and whether those snapshots survived the incident.
Do not create new restore points expecting them to contain yesterday’s files. Recovery depends on copies that already existed before the damage.
Deleted-file recovery utilities are a different category. They may locate unencrypted originals in some circumstances, but they do not mathematically decrypt overwritten data.
If you want a specialist to investigate that possibility, minimize writes to the affected storage. Continued installations can overwrite remnants that might otherwise be recoverable.
Evaluate recovery offers without surrendering control
Be wary of anyone who contacts you first, claims exclusive access to a secret decryptor, or requests an advance payment in cryptocurrency.
Ask a recovery provider what method it intends to use, what evidence supports success, and whether it would negotiate with the attacker.
Get the scope, fee, privacy terms, and limitations in writing. A legitimate assessment should distinguish a possibility from a demonstrated recovery result.
Do not provide remote administrator access to an unknown helper. Recovery desperation can make a second scam feel like the only remaining option.
If you already paid, retain receipts, transaction references, wallet addresses, and correspondence. Contact the payment provider promptly and report the extortion.
Recovery is sometimes partial. Prioritize irreplaceable files, verify them individually, and keep your evidence archive until the investigation and restoration decisions are settled.
Frequently Asked Questions
Is .zynx the same as the name Zynex?
.zynx is the filename suffix associated with the documented ransomware specimen. Zynex is the threat name; keep both details when seeking identification help.
Does readme.txt prove my database was stolen?
No. It establishes that the attacker made the claim. Evidence from access records, transfers, and other incident artifacts is needed to assess actual exposure.
Will a backup eliminate the data-sale risk?
A usable backup can restore availability. It cannot erase a copy someone else may possess or answer whether information left the environment.
Are the listed email providers responsible for Zynex?
The addresses describe channels used in the demand. They do not establish that a mail provider participates in or endorses the extortion.
Can three restored test files guarantee database recovery?
No. A limited demonstration does not test every file, database consistency, missing data, or the safety of a subsequently supplied utility.
Should a company report Zynex even if it has backups?
Yes, report the criminal intrusion and assess any additional obligations with qualified support. Restoring operations does not make the attack irrelevant.
The Bottom Line
Zynex ransomware combines a visible file-locking pattern with allegations of data theft. Treat the damage seriously without presenting the note’s threats as established forensic facts.
Contain access, preserve evidence, restore from verified copies, and investigate possible exposure separately. The attacker’s promise of silence is not a measurable recovery guarantee.








