

Two important messages are supposedly waiting somewhere behind your inbox. A newly announced administration policy is blamed for holding them back.
The notice offers a quick way to restore delivery before time expires. That ordinary workplace problem hides a much more serious risk.
Overview
The email invents a delivery problem
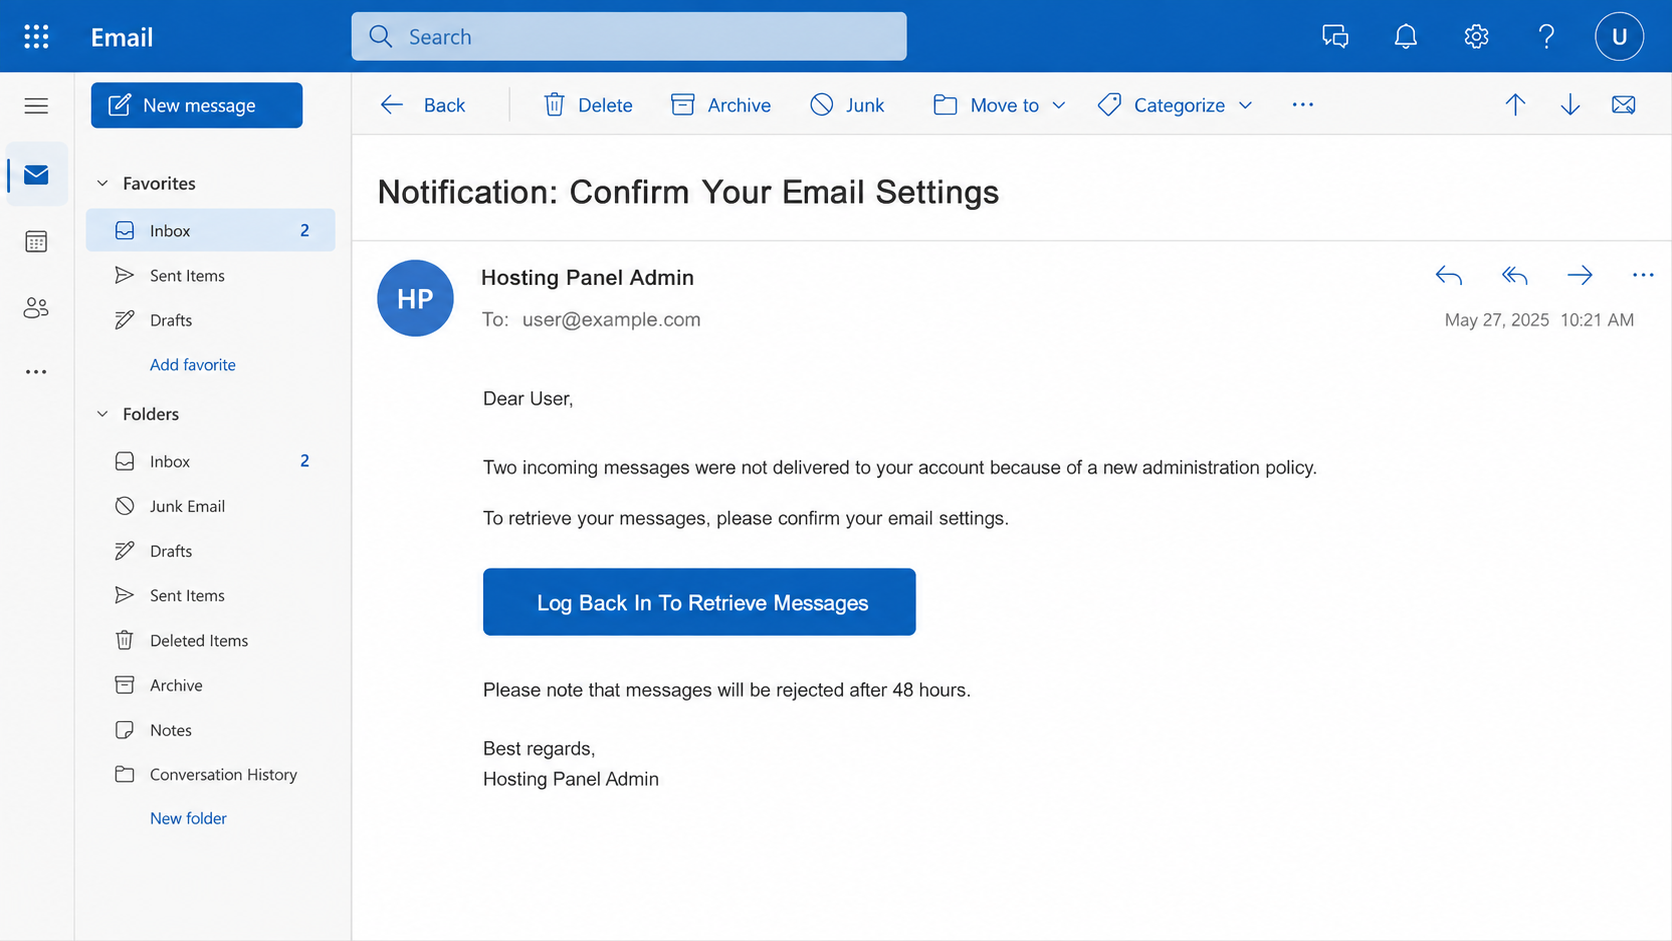
The message claims two incoming emails were not delivered because the recipient’s hosting panel adopted a new administration policy.
It says restoration can take 48 hours unless the user signs in immediately to retrieve the messages.
Nothing in the notice identifies the held senders, subjects, message IDs, or actual server event.
That vagueness lets one template target many domains, providers, employees, and mailbox systems.
The cPanel name supplies borrowed authority
cPanel is legitimate hosting-management software. Criminals use the familiar name because website owners recognize it from authentic administration tasks.
The campaign is not evidence that cPanel sent the notice or that its systems were compromised.
A display name, footer, or copyright line can be copied into any email. The destination link and sender authentication matter far more.
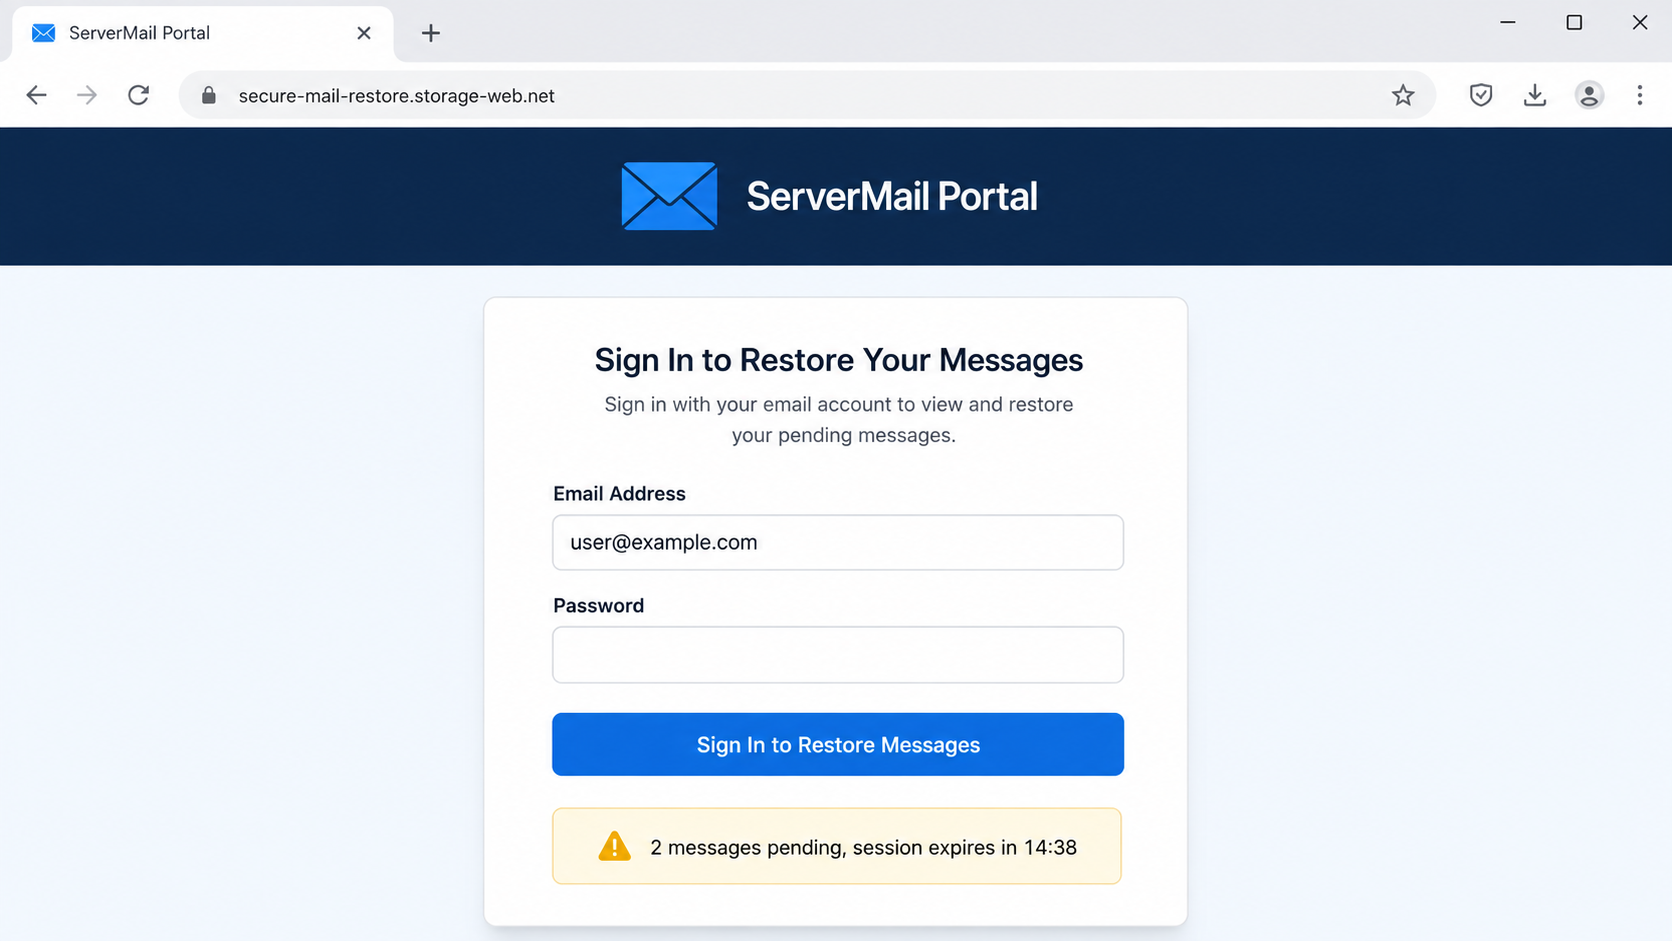
In the examined campaign, the link led away from the recipient’s real provider to a credential-harvesting page.
The stolen mailbox is the valuable prize
The fake page requests an email address and password. Submitted information goes to the phishing operator, not a legitimate mail administrator.
A business inbox can expose invoices, password resets, client conversations, cloud invitations, supplier records, and internal documents.
Warning signs include:
- An unexplained “new policy” with no administrator announcement.
- Exactly two held messages but no identifying details.
- A 48-hour rejection threat designed to create urgency.
- A button that does not lead to the known webmail domain.
- A sender address unrelated to the hosting provider.
- A login page hosted on storage or cloud infrastructure.
- A prefilled email address used to make the page feel personalized.
- No support ticket, server hostname, or verifiable policy reference.
What the Message Actually Says
The subject is commonly styled as “Notification: Confirm Your Email Settings.” It sounds procedural rather than overtly threatening.
The body says a panel policy prevented correct delivery. Awkward wording may be present, but polished variants can use flawless English.
Recipients are offered two apparent choices: wait through restoration or log back in and retrieve the messages immediately.
The first choice is framed as risky because unretrieved mail will supposedly be rejected after the deadline.
The second choice is visually easy. A prominent link or button carries the victim to the impostor page.
This design exploits office curiosity. A missing customer order or urgent executive request feels more costly than a routine login.
The attacker never needs to know which messages matter. The victim supplies their own imagined reason to click.
Generic greetings are another clue, although personalized campaigns can use names gathered from websites or previous breaches.
Real mail administrators can identify a quota issue, rejected message, sending server, or policy rule with technical detail.
They also provide support through known portals. An unexpected email should not redefine where an employee normally signs in.
Why a Stolen Email Password Causes Wider Damage
Email is often the recovery channel for other accounts. Control of one inbox can unlock many unrelated services.
The attacker may search for invoices, payroll records, tax documents, reservation details, contracts, and cryptocurrency discussions.
They can create forwarding rules that quietly copy future messages to an outside address.
Inbox rules can hide replies from the legitimate owner, helping an invoice-diversion scheme continue unnoticed.
A criminal can enter an existing supplier conversation and replace bank instructions shortly before payment.
Messages sent from a familiar account are more persuasive than new phishing emails. Trust spreads the compromise to colleagues and clients.
If the same password was reused, automated login attempts may reach hosting, social media, file storage, and financial services.
Some phishing pages request a multifactor code after the password. A real-time relay can use that code before it expires.
Session cookies may also be targeted. Stealing an authenticated session can bypass the need to know the password later.
Fast containment therefore matters even when no unusual sent messages appear immediately.
How the New cPanel Administration Policy Email Scam Works
Step 1: Criminals send a reusable mailbox warning
The campaign reaches addresses collected from websites, leaked lists, business directories, or automated domain guesses.
The template refers to generic “messages” and an “administration policy,” so it does not require knowledge of the recipient’s actual setup.
A cPanel reference increases relevance for domains that use hosting services, even when the mailbox runs elsewhere.
Step 2: The message creates an invisible loss
Unlike a fake invoice, this lure does not claim money already disappeared. It suggests important communication is being withheld.
Because the missing mail cannot be seen, the recipient imagines the most urgent possibility.
The 48-hour limit prevents a calm discussion with the hosting provider or internal administrator.
Step 3: The link opens an imitation webmail page
The destination copies colors, icons, and sign-in language from popular mail systems.
In the examined example, fraudulent content was hosted on ordinary cloud storage infrastructure rather than the recipient’s known webmail server.
A reputable hosting platform can unknowingly serve abusive files. Its presence does not authenticate the page.
Step 4: Personalization makes the form feel legitimate
The address may already appear in the username field because it was passed inside the phishing URL.
Seeing a correct address reassures users, although the attacker already knew it when sending the email.
The page requests a password and may reject the first entry, prompting a second submission to capture common alternatives.
Step 5: Credentials are transmitted to the attacker
Submitting the form sends the entered data to a collection script, messaging bot, or remote server.
The page may display an error or redirect to a genuine provider afterward. That handoff can make the failure appear harmless.
The victim may assume the messages were restored and never report the incident.
Step 6: The mailbox is tested and quietly prepared
Attackers attempt the credentials against the email provider and related services.
Once inside, they review recent threads, add forwarding rules, register recovery methods, or create application passwords.
They may wait for a valuable payment conversation rather than acting immediately.
Step 7: Business contacts receive trusted fraud
The compromised account sends document lures, payment changes, or new mailbox warnings to people who recognize the sender.
That second wave can be more damaging because it inherits real signatures and conversation history.
Organizations may discover the breach only after a supplier, guest, or customer reports an unexpected request.
How to Check a Suspected Mail Policy Alert
Do not press the embedded button. Open your usual webmail bookmark or type the known provider address yourself.
Check whether messages, quota notices, or administrative alerts appear inside the authenticated account.
Ask the person or team that manages the domain whether any policy changed. Use contact details already stored internally.
Hover over the link without opening it. Compare the real destination with the expected mail or hosting domain.
On a phone, long-pressing may reveal the address, but avoid accidental navigation.
Inspect the sender’s complete address, reply-to field, and headers. Display names can be written freely.
SPF, DKIM, and DMARC results can help administrators evaluate origin. A passing result authenticates a domain, not the truth of every claim.
Look for a specific server name, policy identifier, ticket number, and provider documentation.
Call support through the hosting dashboard. Never use telephone numbers presented only inside the suspicious email.
Report the message as phishing so filters can protect other recipients on the same organization.
Controls That Can Stop This Campaign Earlier
Organizations should teach employees that mail-delivery repairs begin inside established portals, not surprise messages.
A simple reporting button gives uncertain users a safer action than clicking, forwarding casually, or replying to the sender.
Secure email gateways can rewrite and inspect links, although newly created pages may evade initial reputation checks.
Domain-based authentication reduces simple spoofing. It cannot stop every lookalike domain or a compromised legitimate mailbox.
Conditional access can block logins from impossible locations, unknown devices, anonymous networks, or countries outside normal operations.
Risk-based controls should challenge unusual sessions without training users to approve every unexpected prompt.
Phishing-resistant security keys sharply reduce the usefulness of captured passwords because authentication remains bound to the genuine domain.
Legacy protocols should be disabled where possible. They can bypass modern authentication protections and provide quiet entry points.
Administrators should alert on new forwarding rules, mass downloads, recovery changes, and suspicious application consent.
Shared mailboxes need clear ownership and audit trails. Every user should know how legitimate quota or policy notices arrive.
External-sender banners can help, but employees often stop noticing them. Training must focus on destination verification and independent confirmation.
Browser password managers provide a useful clue. They normally refuse to autofill credentials on an unrelated phishing domain.
That clue is not absolute, but users should pause whenever the expected saved login does not appear.
Backups protect messages from deletion, not account impersonation. Incident plans must address both data restoration and trusted-contact notification.
Logging retention should cover enough time to investigate delayed misuse. Criminals may observe an inbox before launching payment fraud.
Security teams should search for the same subject, link, sender, and recipient pattern across the organization after one report.
Removing a message from every inbox can prevent later clicks by employees returning from leave or another time zone.
After containment, teams should explain exactly which clue exposed the lure. Specific feedback builds better judgment than a generic warning.
Review nearby alerts for the same recipient. Multiple failed sign-ins may show that credentials were tested before anyone reported the message.
Mail servers should retain original authentication results and delivery paths. Forwarded copies can remove details investigators need.
Help desks can publish examples of genuine quota and policy notices inside the authenticated support portal.
Employees then have a stable reference when a surprise message claims the process changed overnight.
Administrators should register lookalike domains defensively when practical and monitor certificates created for deceptive variations.
No single control catches every campaign. Layered prevention combines user judgment, filtering, authentication, access policy, and rapid response.
Measure training by reporting speed, not only click rate. Someone who reports immediately can prevent organization-wide exposure.
Do not punish honest mistakes. Fear causes employees to hide clicks until damage becomes visible.
Credential phishing is an incident even when the account login initially fails. The password may unlock another service.
Record which password was exposed without storing it in a ticket. Ask the user where else it was reused.
Review privileged hosting accounts separately because an email compromise can support password resets and domain changes.
Check DNS records and registrar access when the mailbox controls the domain. Unauthorized changes can redirect both web traffic and future email.
Document the final scope before closing the incident. A restored inbox does not prove every connected account remained untouched.
Company, Address, and Fulfillment Checks
Separate cPanel from the sender
cPanel is a real software company, but the brand name inside this message does not establish involvement.
Verify notices through the genuine account portal or established administrator, never through the message itself.
Check the claimed administrator
A legitimate internal policy has an owner, effective date, help channel, and documented scope.
If nobody managing the domain recognizes it, the alert’s central claim collapses.
Identify the actual web host
Cloud-storage and hosting providers merely supply infrastructure. Criminals can abuse reputable services for short-lived phishing pages.
Report the exact URL to the provider, but do not describe that provider as the scam operator without evidence.
Trace where credentials were delivered
For email phishing, “fulfillment” is the credential route. Administrators should preserve URLs, headers, DNS data, and access logs.
Those records help identify affected users, malicious logins, forwarding changes, and other recipients.
What to Do if You Have Fallen Victim to This Scam
- Change the mailbox password immediately. Use the real provider portal from a clean device. Make the new password unique and unrelated to the old one.
- End active sessions. Sign out other devices, revoke remembered browsers, application passwords, and third-party access tokens.
- Enable stronger multifactor authentication. Prefer a security key or authenticator application over codes delivered to the same compromised mailbox.
- Review account settings. Inspect forwarding addresses, inbox rules, delegates, recovery details, filters, and automatic replies for unauthorized changes.
- Contact the administrator. Business users should notify IT or their hosting provider quickly so logs and organization-wide indicators can be checked.
- Protect reused accounts. Replace the exposed password anywhere else it was used. Start with hosting, financial, storage, and social accounts.
- Inspect recent activity. Look for unfamiliar locations, sent mail, deleted messages, password-reset notices, and payment conversations.
- Scan the device. Run Malwarebytes if anything was downloaded or installed, or if the browser behaved unexpectedly after the click.
- Block repeat destinations. AdGuard can stop many known phishing and advertising domains, but account recovery remains necessary after disclosure.
- Warn affected contacts. Tell colleagues, customers, and suppliers to distrust recent links or changed payment instructions from the mailbox.
- Preserve the original email. Export headers and retain the message, URL, screenshots, and security alerts for investigation.
- Report the page. Notify the hosting provider, domain registrar, email provider, CISA or local cyber authority, and the impersonated organization.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Did cPanel send the New Administration Policy email?
The examined message was phishing. Confirm any real cPanel communication through official support and your established hosting account.
Are two messages really being held?
The number is part of the lure. Check your genuine mailbox and provider dashboard rather than trusting the email.
Why is the phishing page hosted in the cloud?
Public cloud services are fast and familiar. Their infrastructure can be abused without the provider endorsing the content.
Is viewing the page enough to compromise me?
Usually the main risk is entering credentials. Downloads, browser exploits, notification permissions, and extensions can create additional exposure.
What if I entered the wrong password?
Treat it as exposed if it is valid anywhere. Phishing pages often collect multiple attempts deliberately.
Can my hosting account also be at risk?
Yes, especially if credentials were reused or the mailbox controls hosting resets. Secure both services and review logs.
The Bottom Line
The New cPanel Administration Policy email invents held messages and a 48-hour deadline to steal mailbox credentials.
Ignore its login route. Verify delivery problems through your normal provider, and act quickly if any password reached the fake page.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.